Google Cloud Key Management allows users to manage encryption keys on Google Cloud.
N/A
IBM Vault
Score9.1 out of 10
N/A
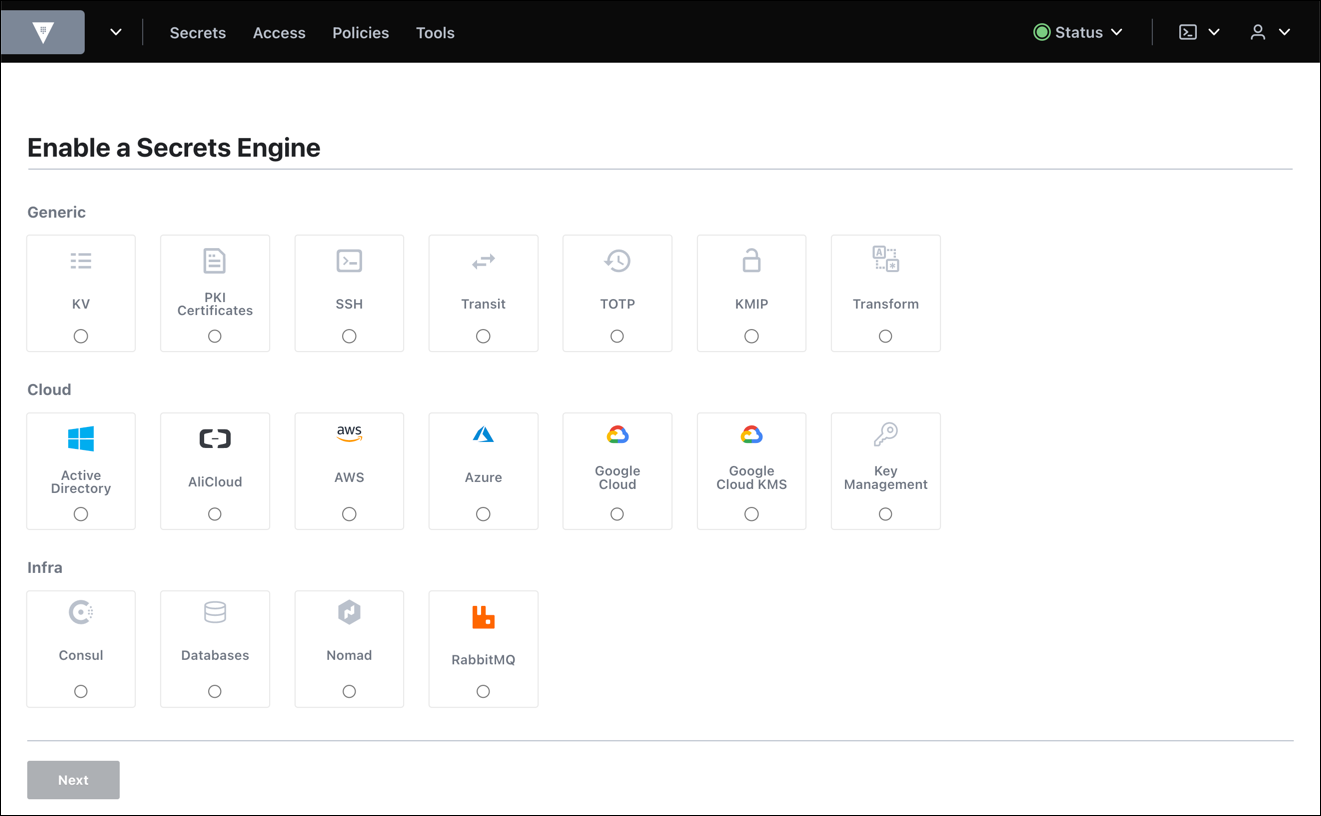
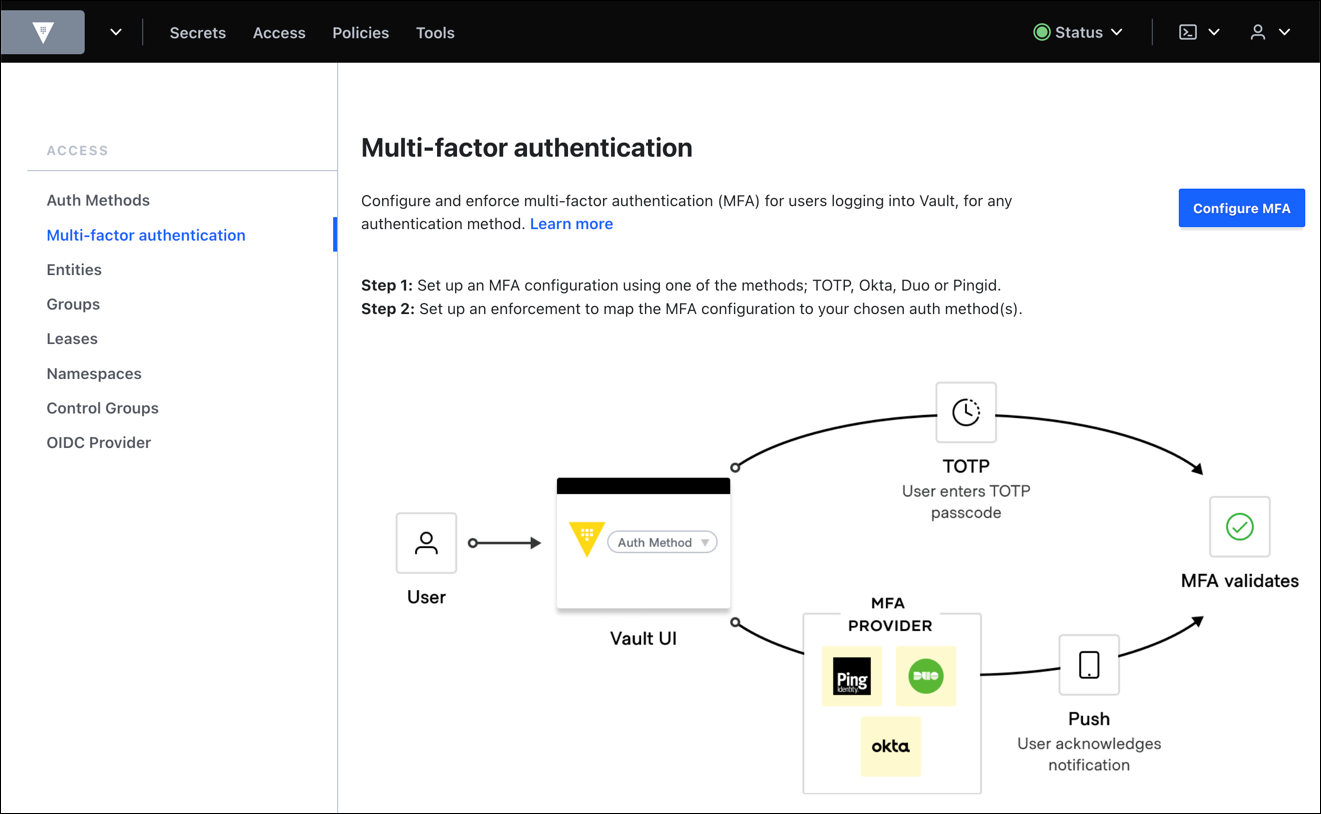
IBM Vault (formerly Hashicorp Vault) is an encryption tool for managing secrets including credentials, passwords and other secrets, providing access control, audit trail, and support for multiple authentication methods. It is available open source, or under an enterprise license.
Use for most types of cloud SQL services. Excellent modern-day encryption technologies. If a customer wants to manage their keys then Google Cloud Platform is well suited for those people if it matters. Able to divide workloads and pipelines. Customer managed encryption keys support for Data fusion, Data Proc, Cloud SQL, and GKE. We use Cloud EKM: key use operations $0.03 per 10,000 operations for our day to day operations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Vault is well-suited for all software application development. It does a great job of ensuring you have full visibility and traceability into your credentials and who checks them out. The integration is the key enabler that makes Vault a differentiator. Some of the new agent capabilities are going to be a good value-add.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It doesn't have an interface. This isn't entirely bad because of the purpose it serves, but it does make the barrier to entry a little difficult.
Unlike many other HashiCorp products, the documentation feels like it leaves some steps out. Step by step documentation lowers the barriers to entry a little bit, and going through even the installation documentation and setup leaves a little bit of the caveats out.
It needs a fair bit of supporting infrastructure. You cannot just have a Vault instance. Having a HashiCorp Vault instance means also having a consul cluster for the backend.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
HashiCorp Vault is the best there is out there, and it has become critical to our secret management use cases. It would be difficult to find anything that would suit our needs better and that would be beneficial for us to switch over to.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Most, if not all companies would have a use for Vault, from basic secret storage and retrieval to dynamic Cloud credentials, database management, etc., and they are all easily configurable to the specific needs/use cases of your specific company. If you can afford it/have it in your budget, Vault is definitely something worth checking out and at least demoing the open-source version.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
As with all other products provided by HashiCorp, the effort and attention that the company has in creating a complete solution ecosystem for the DevOps universe are fully apparent. Several technical lectures about products on YouTube are presented by the company's CEO.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The UI / UX, first of all, is night and day difference. The main attraction after the services were this: It's user friendly. It welcomes new users and properly guides them on what to do and what you can expect. Honestly, I had a very bad experience with Microsoft Azure in 2018, so I think the Google Cloud Key Management service is best for me for now and I may give the new Azure a try later.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
HashiCorp Vault integrates with a lot of tools and systems, and the documentation was pretty robust with a lot of community help. Because HashiCorp Vault is also older than other solutions, it is already well developed with a lot of features you need for storing secrets and configuration. HashiCorp Vault is also friendlier towards application build and is focused in providing security and a lot of customization for almost any use case scenario. Bitwarden is more limited to password management of enterprise accounts, but for application usage is not that great or easy to integrate. It does not scale well also. AWS Secrets Manager on the other hand is really good but more limited to AWS applications and vendor lock is problematic as well for such a critical piece of infrastructure.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info