TrustRadius: an HG Insights company

Google Threat Intelligence (Mandiant) vs. Imperva Attack Analytics

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    Google Threat Intelligence (Mandiant)

    Score10 out of 10
    Enterprise companies (1,001+ employees)
    Google Threat Intelligence, based on the expertise and service of Mandiant, aims to accelerate security and risk decision making – operational as well as strategic – and to enable security teams to focus on threats that matter to them.N/A

    Imperva Attack Analytics

    Score9.4 out of 10
    N/AImperva Attack Analytics, (formerly ThreatRadar), is a threat intelligence service relying on research from Imperva's Application Defense Center (ADC), integratable into Imperva's WAF solutions and able to be fed into enterprise security data.N/A
    Pricing
    Google Threat Intelligence (Mandiant)Imperva Attack Analytics
    Editions & Modules
    No answers on this topic
    No answers on this topic
    Offerings
    Pricing Offerings
    Google Threat Intelligence (Mandiant)Imperva Attack Analytics
    Free Trial
    YesNo
    Free/Freemium Version
    YesNo
    Premium Consulting/Integration Services
    YesNo
    Entry-level Setup FeeOptionalNo setup fee
    Additional DetailsPriced by company size—
    More Pricing Information
    Community Pulse
    Google Threat Intelligence (Mandiant)Imperva Attack Analytics
    Considered Both Products
    Google
    No answer on this topic
    Imperva, a Thales company
    No answer on this topic
    Key User Insights
    Would buy again
    100%
    Would buy again
    17 Answers
    No answers on this topic
    Delivers good value for the price
    100%
    Delivers good value for the price
    14 Answers
    No answers on this topic
    Happy with the feature set
    100%
    Happy with the feature set
    17 Answers
    No answers on this topic
    Lived up to sales and marketing promises
    80%
    Lived up to sales and marketing promises
    8 Answers
    No answers on this topic
    Implementation went as expected
    100%
    Implementation went as expected
    14 Answers
    No answers on this topic
    Features
    Google Threat Intelligence (Mandiant)Imperva Attack Analytics
    Endpoint Security
    Comparison of Endpoint Security features of Google Threat Intelligence (Mandiant) and Imperva Attack Analytics
    Feature
    Google Threat Intelligence (Mandiant)
    7.2
    6 Ratings
    0% below category average
    Imperva Attack Analytics
    -
    Ratings
    Infection Remediation7.26 Ratings00 Ratings
    Threat Intelligence
    Comparison of Threat Intelligence features of Google Threat Intelligence (Mandiant) and Imperva Attack Analytics
    Feature
    Google Threat Intelligence (Mandiant)
    7.8
    10 Ratings
    8% above category average
    Imperva Attack Analytics
    -
    Ratings
    Network Analytics7.79 Ratings00 Ratings
    Threat Recognition7.89 Ratings00 Ratings
    Vulnerability Classification7.510 Ratings00 Ratings
    Automated Alerts and Reporting8.09 Ratings00 Ratings
    Threat Analysis7.510 Ratings00 Ratings
    Threat Intelligence Reporting8.210 Ratings00 Ratings
    Automated Threat Identification7.99 Ratings00 Ratings
    User Ratings
    Google Threat Intelligence (Mandiant)Imperva Attack Analytics
    Likelihood to Recommend
    7.8
    (18 ratings)
    9.4
    (3 ratings)
    Usability
    7.6
    (18 ratings)
    -
    (0 ratings)
    User Testimonials
    Google Threat Intelligence (Mandiant)Imperva Attack Analytics
    Likelihood to Recommend
    Google
    Usually SOC leverages Intel from mutiple sources. The scenarios are: 1.Suitable: In large scale SOC where more than 5000 devices are being monitored and the tech stack is wide, Mandiant will play an excellent role in that scenario. 2.Not Suitable: In small scale SOCs wherein limited devices belonging to the same tech stack is being used then the analysts can rely on OSINT and it is not useful to buy the solution.
    Incentivized
    Read full review
    Imperva, a Thales company
    I have found the solution to be flexible, adaptable and responsive which enables the implementation of risk management principles and security best practices. It provides visibility into cloud application usage, including what data has been accessed, when and by whom that help detect behavioral anomalies with app usage and alert on suspicious events
    Incentivized
    Read full review
    Pros
    Google
    • accelerated threat response feature, prioritizing threats according to requirement.
    • Optimization of the threat intelligence , and can be integrated with 3rd party tools.
    • Features like - Breach ,Adversary, Machine and Operational Intelligence.
    • Mandiant dynamic host and the malware views along with indicators.
    Incentivized
    Read full review
    Imperva, a Thales company
    • It quickly shows us the statistics graphically.
    • It gives us a super grainy detail of the attack.
    • The board is very friendly.
    • It is always constantly updated.
    Incentivized
    Read full review
    Cons
    Google
    • Paywalls exist throughout the data set and can halt an investigation without the right model
    • Some data was incomplete or broken up between pay tiers
    • Navigation through the data lacked a definitive trail or breadcrumbs to retrace steps during investigations
    Incentivized
    Read full review
    Imperva, a Thales company
    • The UI does not feel intuitive
    • The support documentation sometimes is lacking or unclear
    • API integration seems a little more complicated than need be.
    Incentivized
    Read full review
    Usability
    Google
    Mandiant Advantage Threat Intelligence has a very usable platform, with well-differentiated sections for the analyst, as well as the possibility of cross-searching to obtain the desired results. All this is presented with an interface that is easy on the eye and not very messy, which increases productivity and the speed with which work is done.
    Incentivized
    Read full review
    Imperva, a Thales company
    No answers on this topic
    Alternatives Considered
    Google
    It gives more ways to analyze threats and options to fixed it. This device gives more visibility on vulnerability detection and its analysis. It provides detailed reports to have more information of all malwares which help us to increase overall security of our current organization
    Incentivized
    Read full review
    Imperva, a Thales company
    We chose Imperva Attack Analytics for its ability to monitor and audit database activities and its ability to scale and meet demands of the distributed environment. The solution is simple, straightforward and transparent for colleagues, and provides real-time event monitoring, audit analysis and customisable reports.
    Incentivized
    Read full review
    Return on Investment
    Google
    • Improved incident response time
    • Specific investigations that have reduced the attack surface
    • Technical reports on threats not controlled by the bank's local team
    Incentivized
    Read full review
    Imperva, a Thales company
    • We gain in reputation as our website has never been down.
    • We gain credibility as we are protected with the best security tool.
    • We gain trust, our clients know that their accounts are well protected.
    Incentivized
    Read full review
    ScreenShots

    Google Threat Intelligence (Mandiant) Screenshots
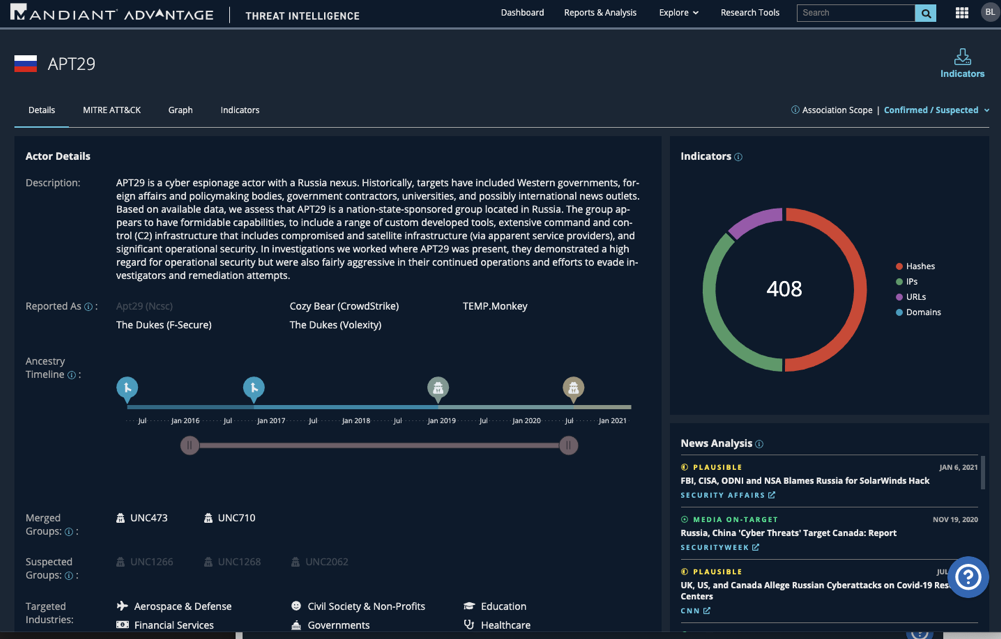
    Screenshot of Mandiant Advantage DashboardScreenshot of Mandiant Advantage Actor DetailsScreenshot of Mandiant Advantage Actor Graph
