TrustRadius: an HG Insights company

Google Threat Intelligence (Mandiant) vs. Splunk Cloud Platform

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    Google Threat Intelligence (Mandiant)

    Score10 out of 10
    Enterprise companies (1,001+ employees)
    Google Threat Intelligence, based on the expertise and service of Mandiant, aims to accelerate security and risk decision making – operational as well as strategic – and to enable security teams to focus on threats that matter to them.N/A

    Splunk Cloud Platform

    Score8 out of 10
    N/ASplunk Cloud Platform is a data platform service thats help users search, analyze, visualize and act on data. The service can go live in as little as two days, and with an IT backend managed by Splunk experts.N/A
    Pricing
    Google Threat Intelligence (Mandiant)Splunk Cloud Platform
    Editions & Modules
    No answers on this topic
    No answers on this topic
    Offerings
    Pricing Offerings
    Google Threat Intelligence (Mandiant)Splunk Cloud Platform
    Free Trial
    YesNo
    Free/Freemium Version
    YesNo
    Premium Consulting/Integration Services
    YesNo
    Entry-level Setup FeeOptionalNo setup fee
    Additional DetailsPriced by company size—
    More Pricing Information
    Community Pulse
    Google Threat Intelligence (Mandiant)Splunk Cloud Platform
    Considered Both Products
    Google
    No answer on this topic
    Cisco
    No answer on this topic
    Key User Insights
    Would buy again
    100%
    Would buy again
    17 Answers
    100%
    Would buy again
    15 Answers
    Delivers good value for the price
    100%
    Delivers good value for the price
    14 Answers
    92%
    Delivers good value for the price
    11 Answers
    Happy with the feature set
    100%
    Happy with the feature set
    17 Answers
    100%
    Happy with the feature set
    15 Answers
    Lived up to sales and marketing promises
    80%
    Lived up to sales and marketing promises
    8 Answers
    91%
    Lived up to sales and marketing promises
    10 Answers
    Implementation went as expected
    100%
    Implementation went as expected
    14 Answers
    100%
    Implementation went as expected
    13 Answers
    Features
    Google Threat Intelligence (Mandiant)Splunk Cloud Platform
    Endpoint Security
    Comparison of Endpoint Security features of Google Threat Intelligence (Mandiant) and Splunk Cloud Platform
    Feature
    Google Threat Intelligence (Mandiant)
    7.2
    6 Ratings
    0% below category average
    Splunk Cloud Platform
    -
    Ratings
    Infection Remediation7.26 Ratings00 Ratings
    Threat Intelligence
    Comparison of Threat Intelligence features of Google Threat Intelligence (Mandiant) and Splunk Cloud Platform
    Feature
    Google Threat Intelligence (Mandiant)
    7.8
    10 Ratings
    8% above category average
    Splunk Cloud Platform
    -
    Ratings
    Network Analytics7.79 Ratings00 Ratings
    Threat Recognition7.89 Ratings00 Ratings
    Vulnerability Classification7.510 Ratings00 Ratings
    Automated Alerts and Reporting8.09 Ratings00 Ratings
    Threat Analysis7.510 Ratings00 Ratings
    Threat Intelligence Reporting8.210 Ratings00 Ratings
    Automated Threat Identification7.99 Ratings00 Ratings
    Security Information and Event Management (SIEM)
    Comparison of Security Information and Event Management (SIEM) features of Google Threat Intelligence (Mandiant) and Splunk Cloud Platform
    Feature
    Google Threat Intelligence (Mandiant)
    -
    Ratings
    Splunk Cloud Platform
    8.2
    20 Ratings
    3% above category average
    Centralized event and log data collection00 Ratings9.019 Ratings
    Correlation00 Ratings8.419 Ratings
    Event and log normalization/management00 Ratings9.220 Ratings
    Deployment flexibility00 Ratings7.220 Ratings
    Integration with Identity and Access Management Tools00 Ratings7.718 Ratings
    Custom dashboards and workspaces00 Ratings8.920 Ratings
    Host and network-based intrusion detection00 Ratings8.217 Ratings
    Data integration/API management00 Ratings7.310 Ratings
    Behavioral analytics and baselining00 Ratings7.28 Ratings
    Rules-based and algorithmic detection thresholds00 Ratings8.210 Ratings
    Response orchestration and automation00 Ratings7.48 Ratings
    Reporting and compliance management00 Ratings8.810 Ratings
    Incident indexing/searching00 Ratings8.711 Ratings
    Best Alternatives
    Google Threat Intelligence (Mandiant)Splunk Cloud Platform
    Small Businesses
    No answers on this topic
    No answers on this topic
    Medium-sized Companies
    No answers on this topic
    IBM Security QRadar SIEM
    Score8.9 out of 10
    Enterprises
    No answers on this topic
    SolarWinds Security Event Manager (SEM)
    Score8 out of 10
    All AlternativesView all alternativesView all alternatives
    User Ratings
    Google Threat Intelligence (Mandiant)Splunk Cloud Platform
    Likelihood to Recommend
    7.8
    (18 ratings)
    8.8
    (21 ratings)
    Likelihood to Renew
    -
    (0 ratings)
    9.1
    (1 ratings)
    Usability
    7.6
    (18 ratings)
    8.4
    (7 ratings)
    Support Rating
    -
    (0 ratings)
    7.2
    (4 ratings)
    User Testimonials
    Google Threat Intelligence (Mandiant)Splunk Cloud Platform
    Likelihood to Recommend
    Google
    Usually SOC leverages Intel from mutiple sources. The scenarios are: 1.Suitable: In large scale SOC where more than 5000 devices are being monitored and the tech stack is wide, Mandiant will play an excellent role in that scenario. 2.Not Suitable: In small scale SOCs wherein limited devices belonging to the same tech stack is being used then the analysts can rely on OSINT and it is not useful to buy the solution.
    Incentivized
    Read full review
    Cisco
    Splunk is excellent when all your data is in one location. Its ability to correlate all that data is intuitive (once the hurdle of learning the query language is overcome). It is also easy to standardize the presentation of information to the company. When data is siloed/standalone, other systems can be cheaper and faster to implement.
    Incentivized
    Read full review
    Pros
    Google
    • accelerated threat response feature, prioritizing threats according to requirement.
    • Optimization of the threat intelligence , and can be integrated with 3rd party tools.
    • Features like - Breach ,Adversary, Machine and Operational Intelligence.
    • Mandiant dynamic host and the malware views along with indicators.
    Incentivized
    Read full review
    Cisco
    • This SIEM consolidates multiple data points and offers several features and benefits, creating custom dashboards and managing alert workflows.
    • Splunk Cloud provides a simple way to have a central monitoring and security solution. Though it does not have a huge learning curve, you should spend some time learning the basics.
    • Splunk Cloud enables me to create and schedule statistical reports on network use for Management.
    Incentivized
    Read full review
    Cons
    Google
    • Paywalls exist throughout the data set and can halt an investigation without the right model
    • Some data was incomplete or broken up between pay tiers
    • Navigation through the data lacked a definitive trail or breadcrumbs to retrace steps during investigations
    Incentivized
    Read full review
    Cisco
    • The SPL programming language that the queries are built in is not very intuitive.
    • There should be a better repository of pre-built queries for what I would think of as common Active Directory usage monitoring.
    • I would like to see more free training/familiarization information made available.
    Incentivized
    Read full review
    Likelihood to Renew
    Google
    No answers on this topic
    Cisco
    Ease of use and have all the features we need
    Incentivized
    Read full review
    Usability
    Google
    Mandiant Advantage Threat Intelligence has a very usable platform, with well-differentiated sections for the analyst, as well as the possibility of cross-searching to obtain the desired results. All this is presented with an interface that is easy on the eye and not very messy, which increases productivity and the speed with which work is done.
    Incentivized
    Read full review
    Cisco
    Splunk AI Assistant for SPL is good tool, as I said, it is really useful for educational purpose, taking in its hands small and simple tasks (ex:small query dashboard,...), but it's not a ten because the contextual memory for complex issues/dashboarding/reports etc can be limited, and can sometime suggets none optimized query which are not always checked by teammates and can cause issue on the long term.
    Incentivized
    Read full review
    Support Rating
    Google
    No answers on this topic
    Cisco
    Splunk Cloud support is sorely lacking unfortunately. The portal where you submit tickets is not very good and is lacking polish. Tickets are left for days without any updates and when chased it is only sometimes you get a reply back. I get the feeling the support team are very understaffed and have far too much going on. From what I know, Splunk is aware of this and seem to be trying to remedy it.
    Incentivized
    Read full review
    Alternatives Considered
    Google
    It gives more ways to analyze threats and options to fixed it. This device gives more visibility on vulnerability detection and its analysis. It provides detailed reports to have more information of all malwares which help us to increase overall security of our current organization
    Incentivized
    Read full review
    Cisco
    Vs elastic: - SPL's statistical functions superior to KQL for complex correlations - Better enterprise support, less operational overhead - Splunk Cloud Platform's detection engineering more mature vs Sentinel: - SPL more powerful than KQL for custom analytics - Better cross-platform visibility (non-Azure environments) vs Datadog - SPL enables deeper forensic Investigations - Superior compliance/audit capabilities
    Incentivized
    Read full review
    Return on Investment
    Google
    • Improved incident response time
    • Specific investigations that have reduced the attack surface
    • Technical reports on threats not controlled by the bank's local team
    Incentivized
    Read full review
    Cisco
    • End-end visibility across your departmental silos
    • Strengthen the overall global monitoring posture
    • Move from Reactive to Proactive Monitoring
    • Highly secure environment at your finger-tips
    • Takes you away from managing infrastructure/administration, allows saving time & money. Reduce the overall TCO (Total Cost of Ownership)
    Incentivized
    Read full review
    ScreenShots

    Google Threat Intelligence (Mandiant) Screenshots
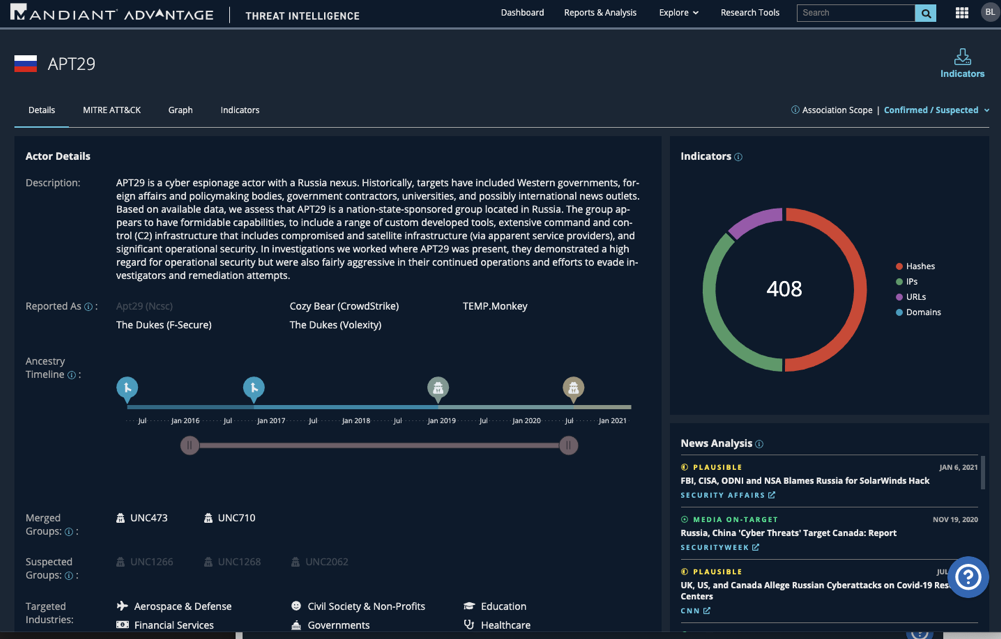
    Screenshot of Mandiant Advantage DashboardScreenshot of Mandiant Advantage Actor DetailsScreenshot of Mandiant Advantage Actor Graph
