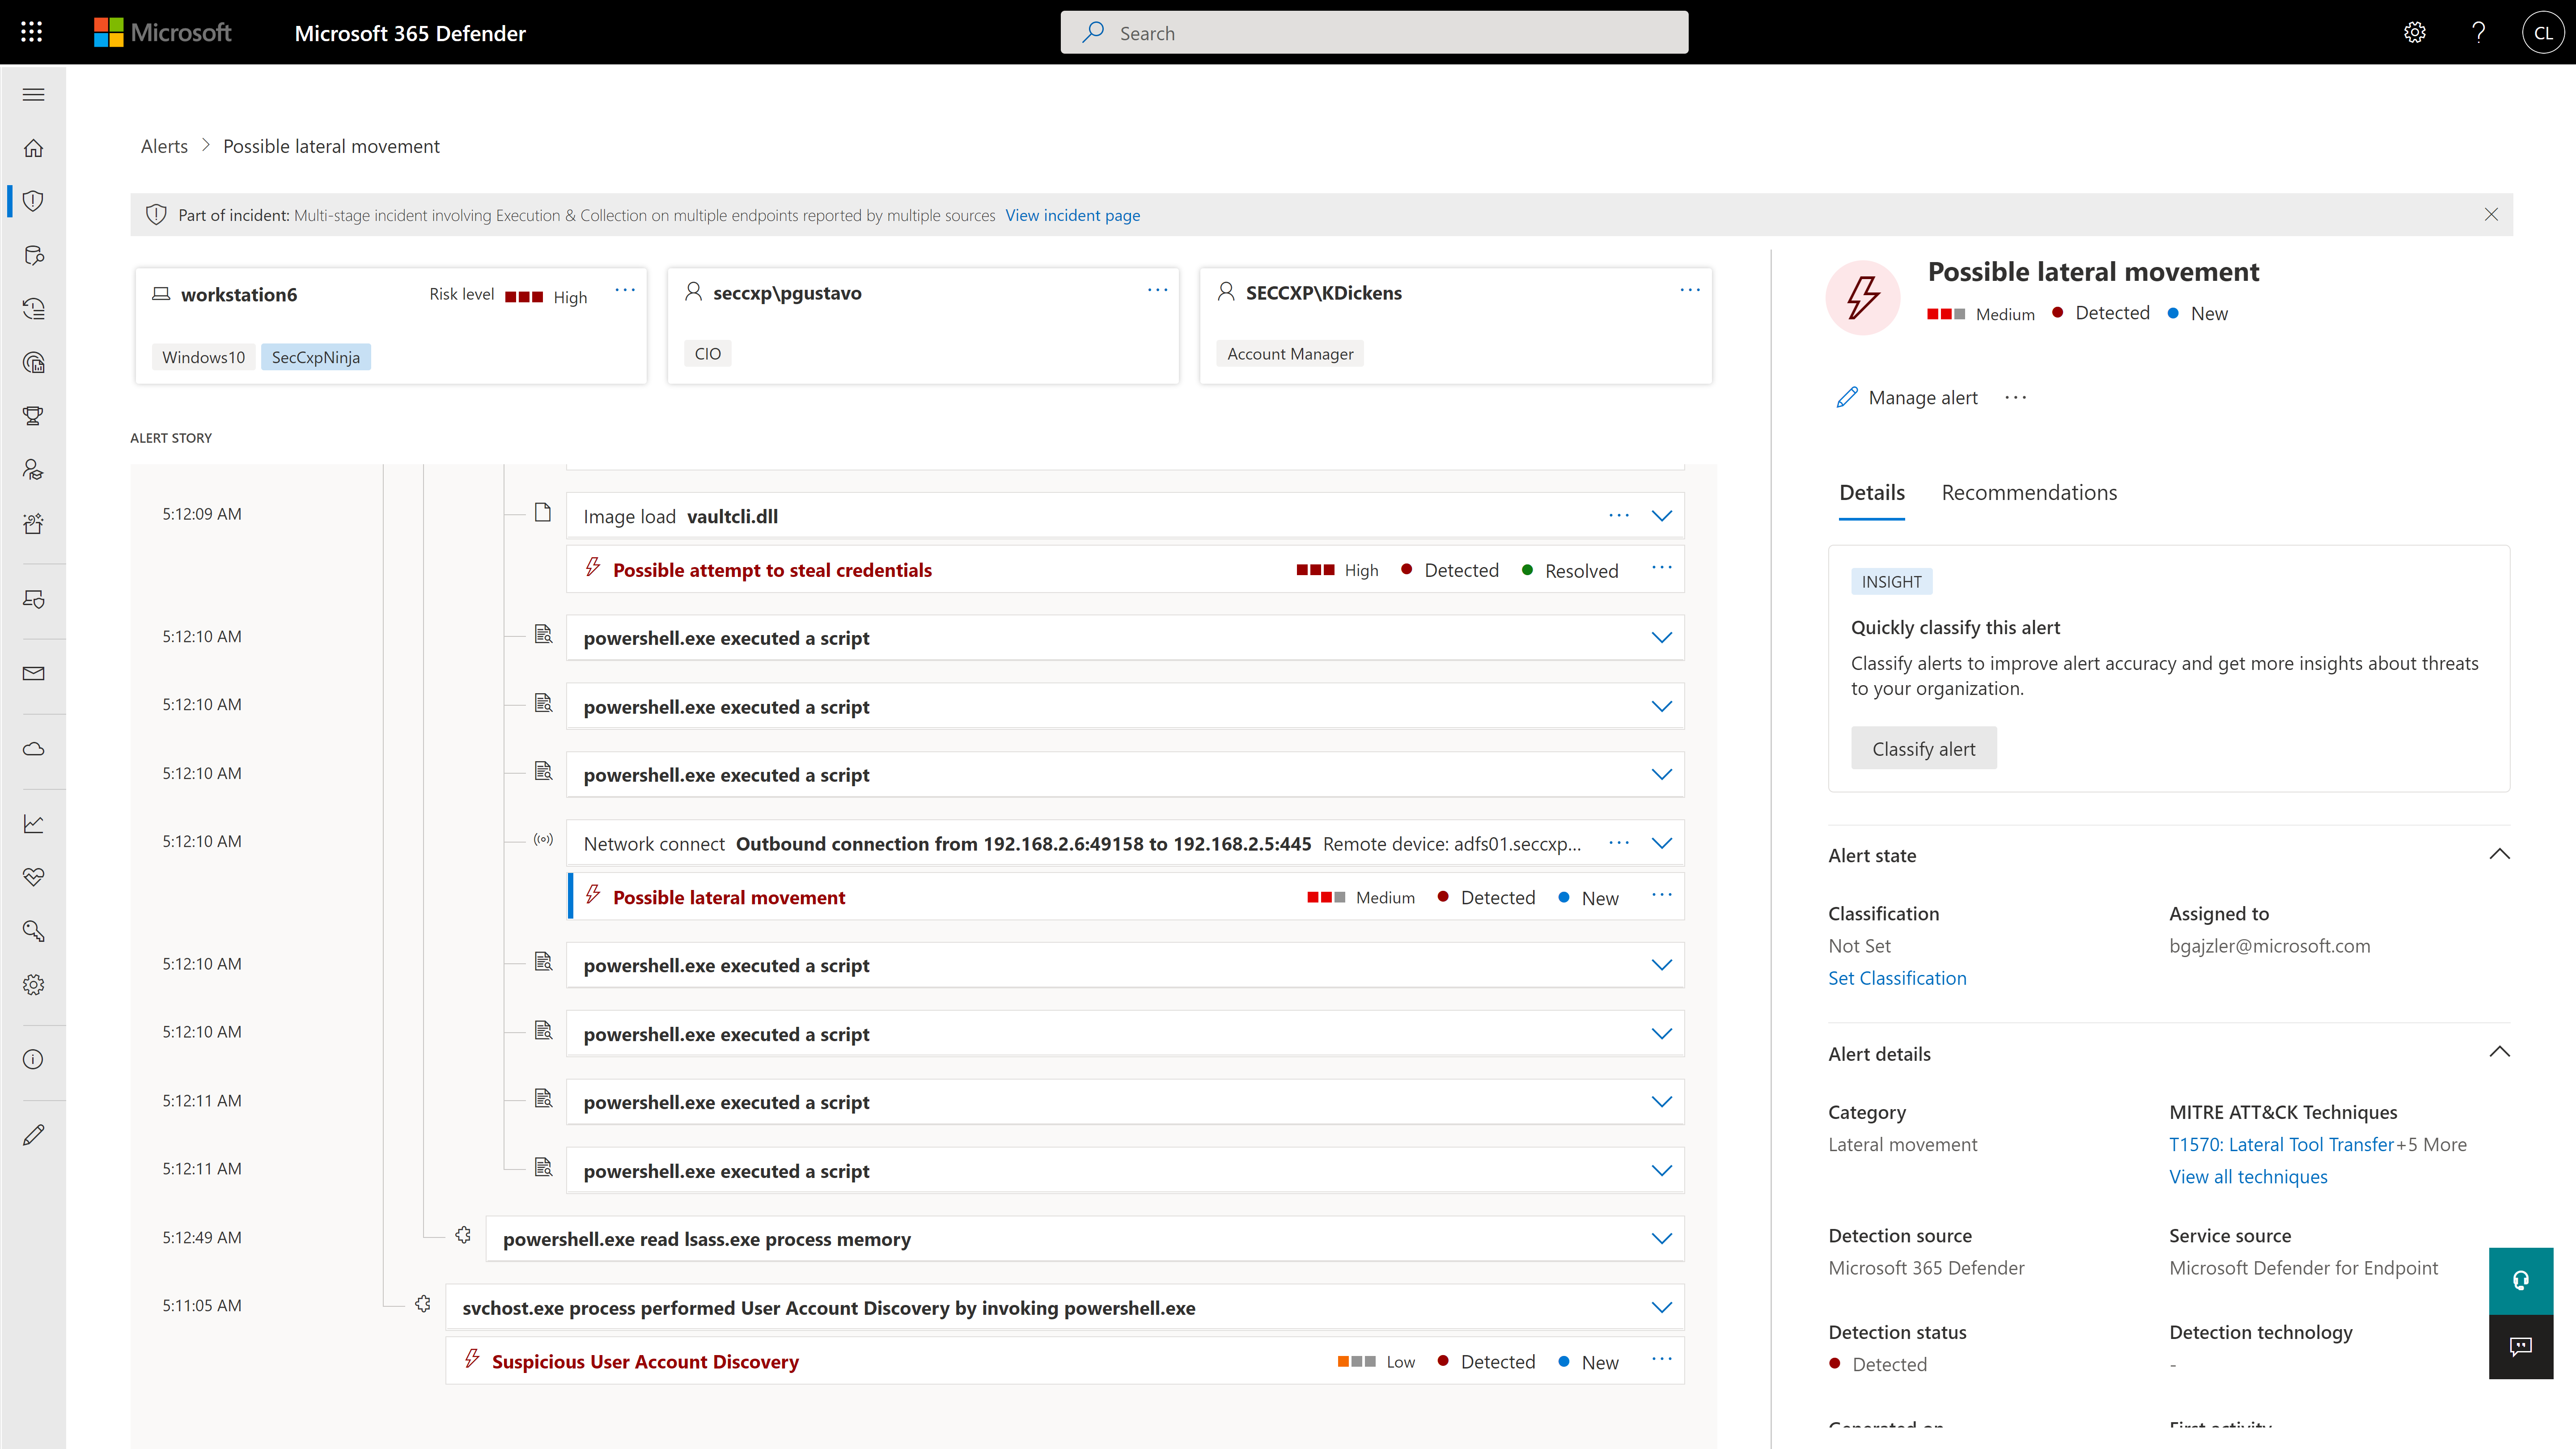
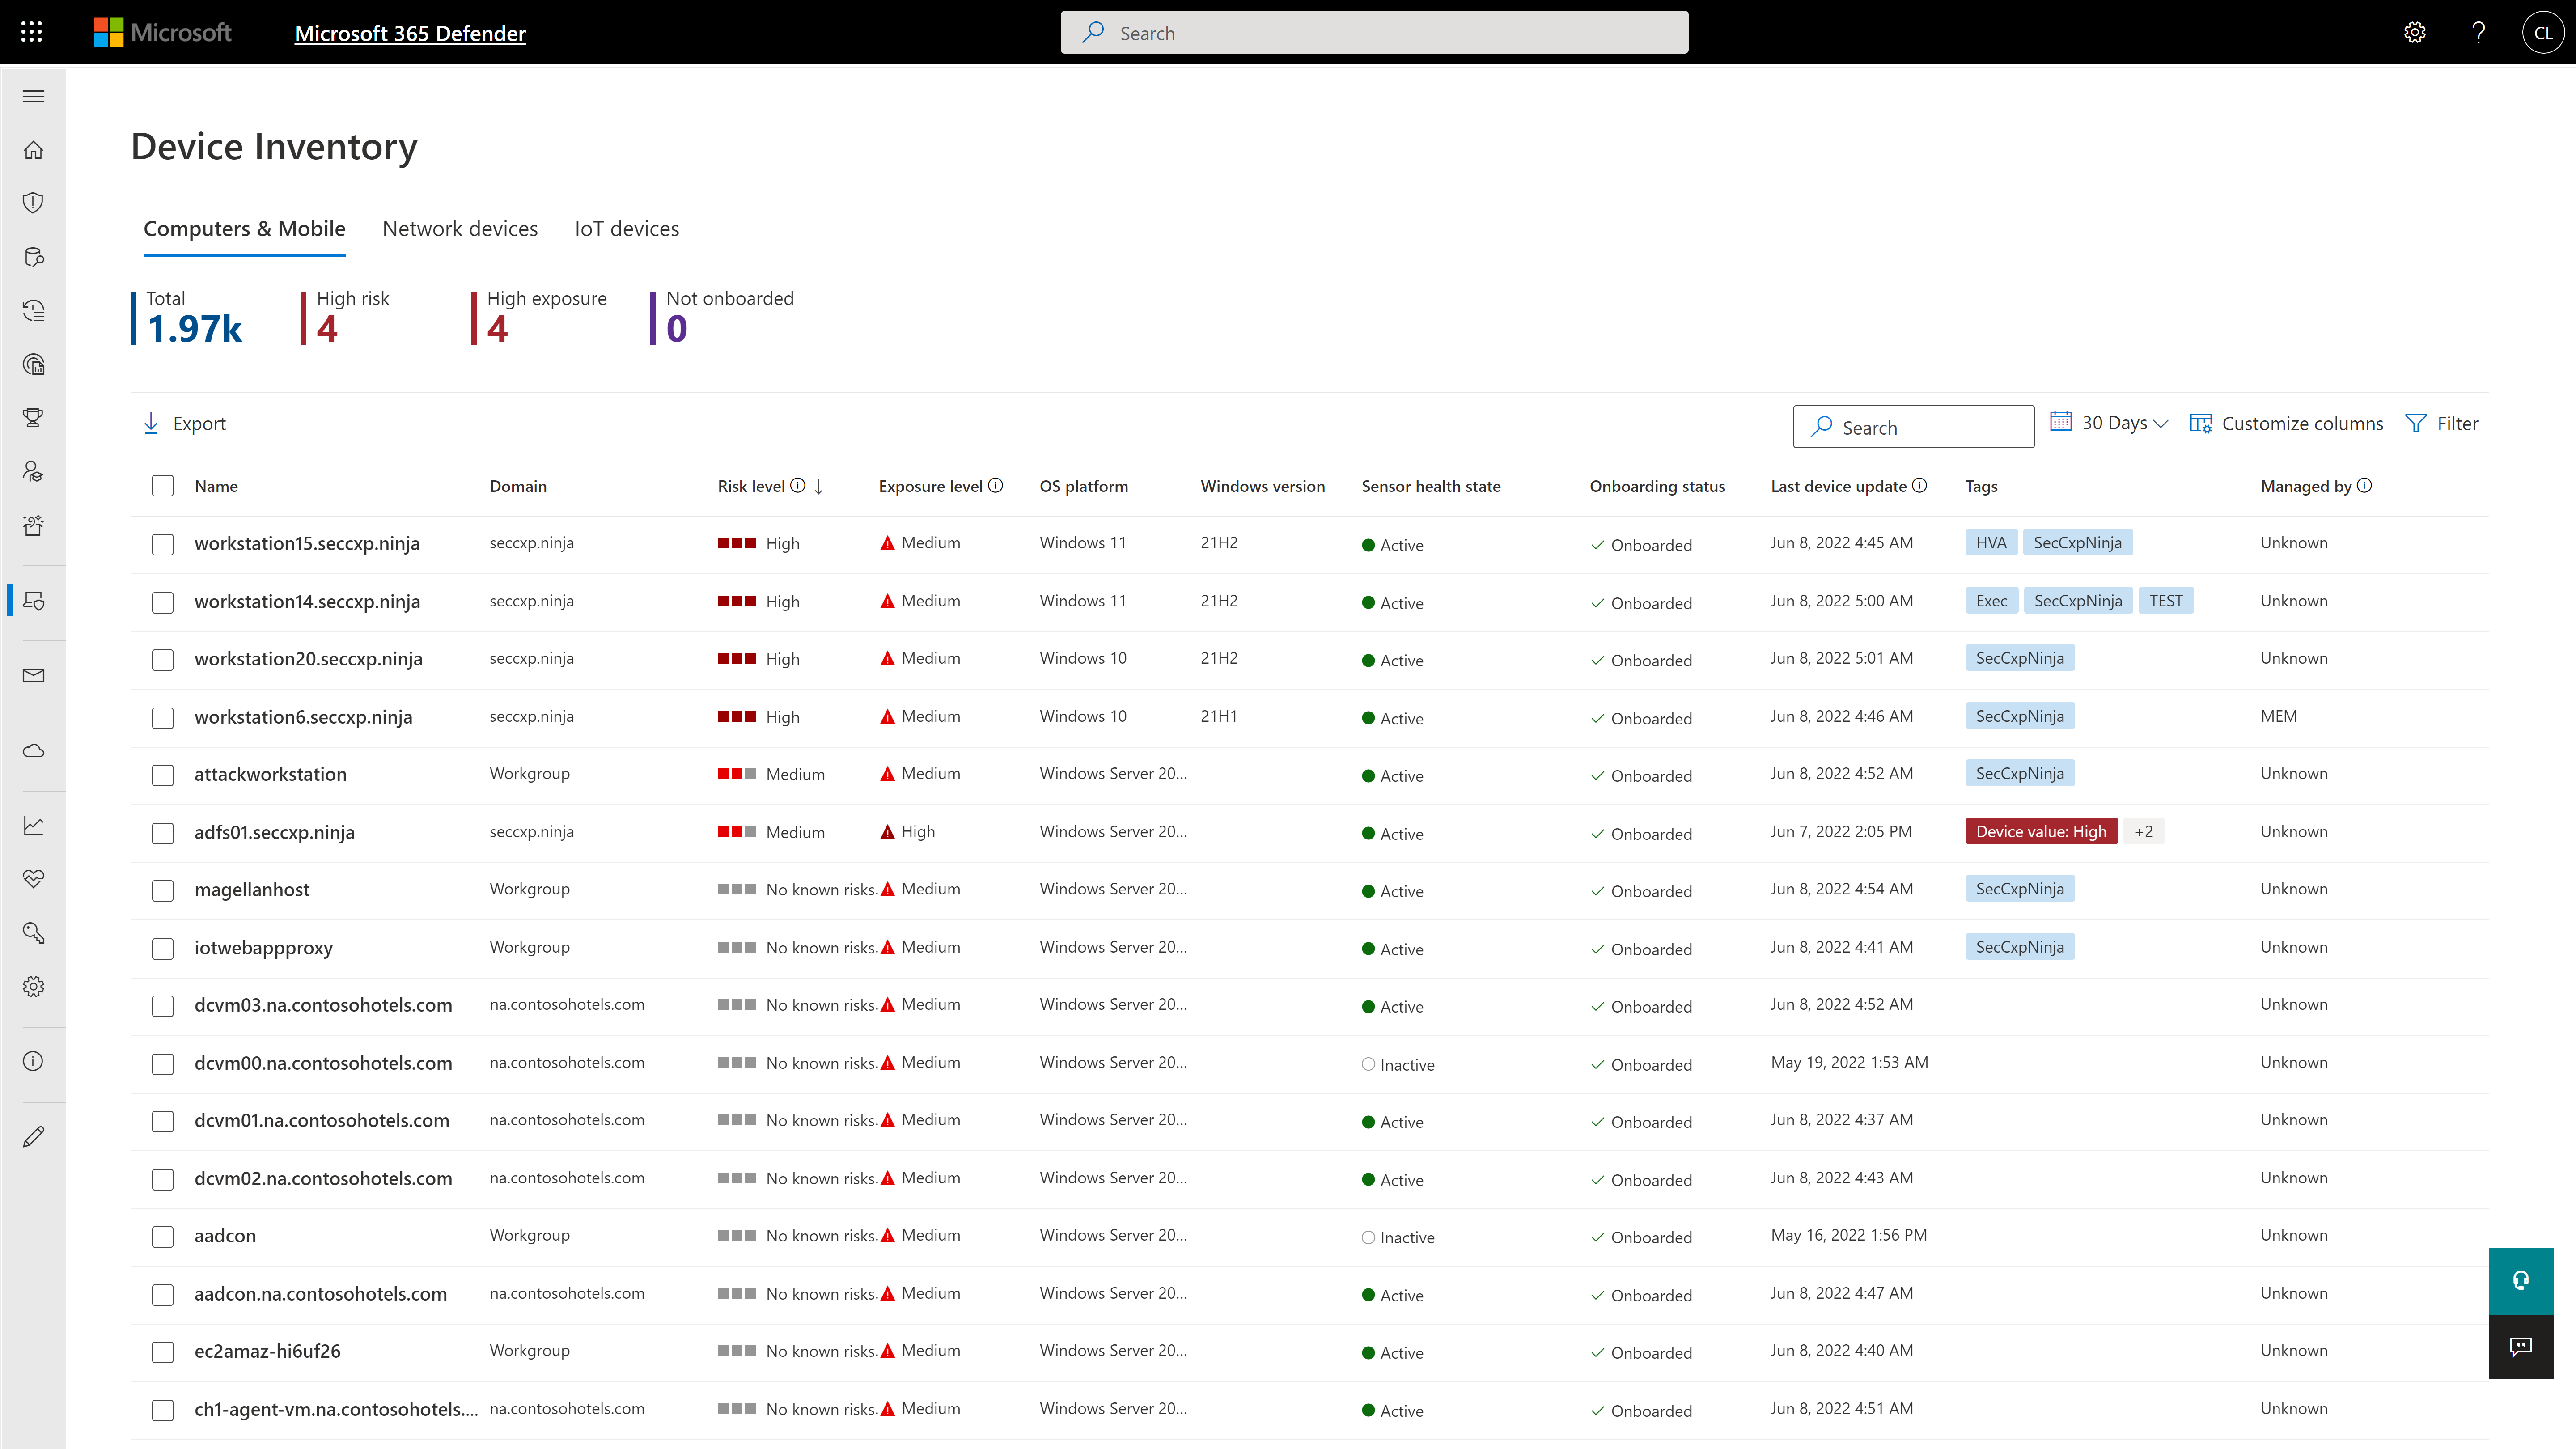
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
Nmap
Score8.7 out of 10
N/A
Nmap is a free, open source network discovery, mapper, and security auditing software. Its core features include port scanning identifying unknown devices, testing for security vulnerabilities, and identifying network issues.
$49,980
one-time fee
Pricing
Microsoft Defender for Endpoint
Nmap
Editions & Modules
Academic
$2.50
per user/per month
Standalone
$5.20
per user/per month
Nmap OEM Small/Startup Company Redistribution License - Quarterly Term Maintenance Fee
$7,980
Every Three Months per license
Nmap OEM Mid-Sized Company Redistribution License - Quarterly Term Maintenance Fee
$11,980
Every Three Months per license
Nmap OEM Enterprise Redistribution License - Quarterly Term Maintenance Fee
$13,980
Every Three Months per license
Nmap OEM Small/Startup Company Redistribution License - Annual Maintenance Fee
$14,980
per year per license
Nmap OEM Mid-Sized Company Redistribution License - Annual Maintenance Fee
All perpetual licenses include a six-month trial period during which you can cancel for any reason and receive a full refund of all money paid (including maintenance). The term license is only a 3-month commitment and cal also be terminated with full refund during the first 30 days of the initial quarter.
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
If you're a sysadmin, or anyone who's had to deploy network services, you've almost certainly had to use Nmap at some point or other. Need to see what devices are on your LAN? Nmap can tell you that. Want to check which ports your web server has open to the internet? Nmap is your friend.
Nmap is a powerful command-line tool and has many options that require some reading of documentation to get the best out of (although generally straightforward). If the thought of working at the command-line scares you (presumably not if you're reading this review), then you may want a much simpler tool, or at least check out Zenmap GUI.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
NMap provides a very fast and a very thorough network "sweep" that allows you to quickly map out exactly what's on your network.
NMap is highly configurable. The "canned" choices are very good in most instances, but using various switches and options, you can create a very specific scan and get exactly the results you're looking for.
NMap is easy to use. Even a new administrator will be able to use the graphical version (Zenmap) with efficiency right away.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The GUI version on Nmap could use some improvement with the options that are available to do scans. For example, they could make it easier to select options for the different types of scanning for people who are beginners
There are no abilities to schedule a scan in the Nmap tool.
An intensive scan sometimes takes too much time to complete.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Nmap uses are very practical and I don't think there is a better tools for what Nmap does. It is open-sources that therefore there is no cost to use it. It offers a number of benefits, including but not limited to network mapping, port scanning and more. It is very reliable as a network scanning tool.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
There is a very large support community and a robust selection of add-ons and scripts. Once you get the use down this is one of the most powerful tools and you can find anything you are looking for as far as examples on the web. While not having official support its not lacking by any means.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Alternatives to Nmap (other IP scanners) are often much more limited in what they can do; They often only allow you to scan a specific subset of ports or a limited number of IP addresses in one command. Nmap is unrestricted in that regard. What makes Nmap stand out above the rest, is the complete network analysis package you get with it. It allows IP scanner, network deep-dives, hardware analysis, vulnerability analysis, encryption detailing, and so much more, in one free application
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info