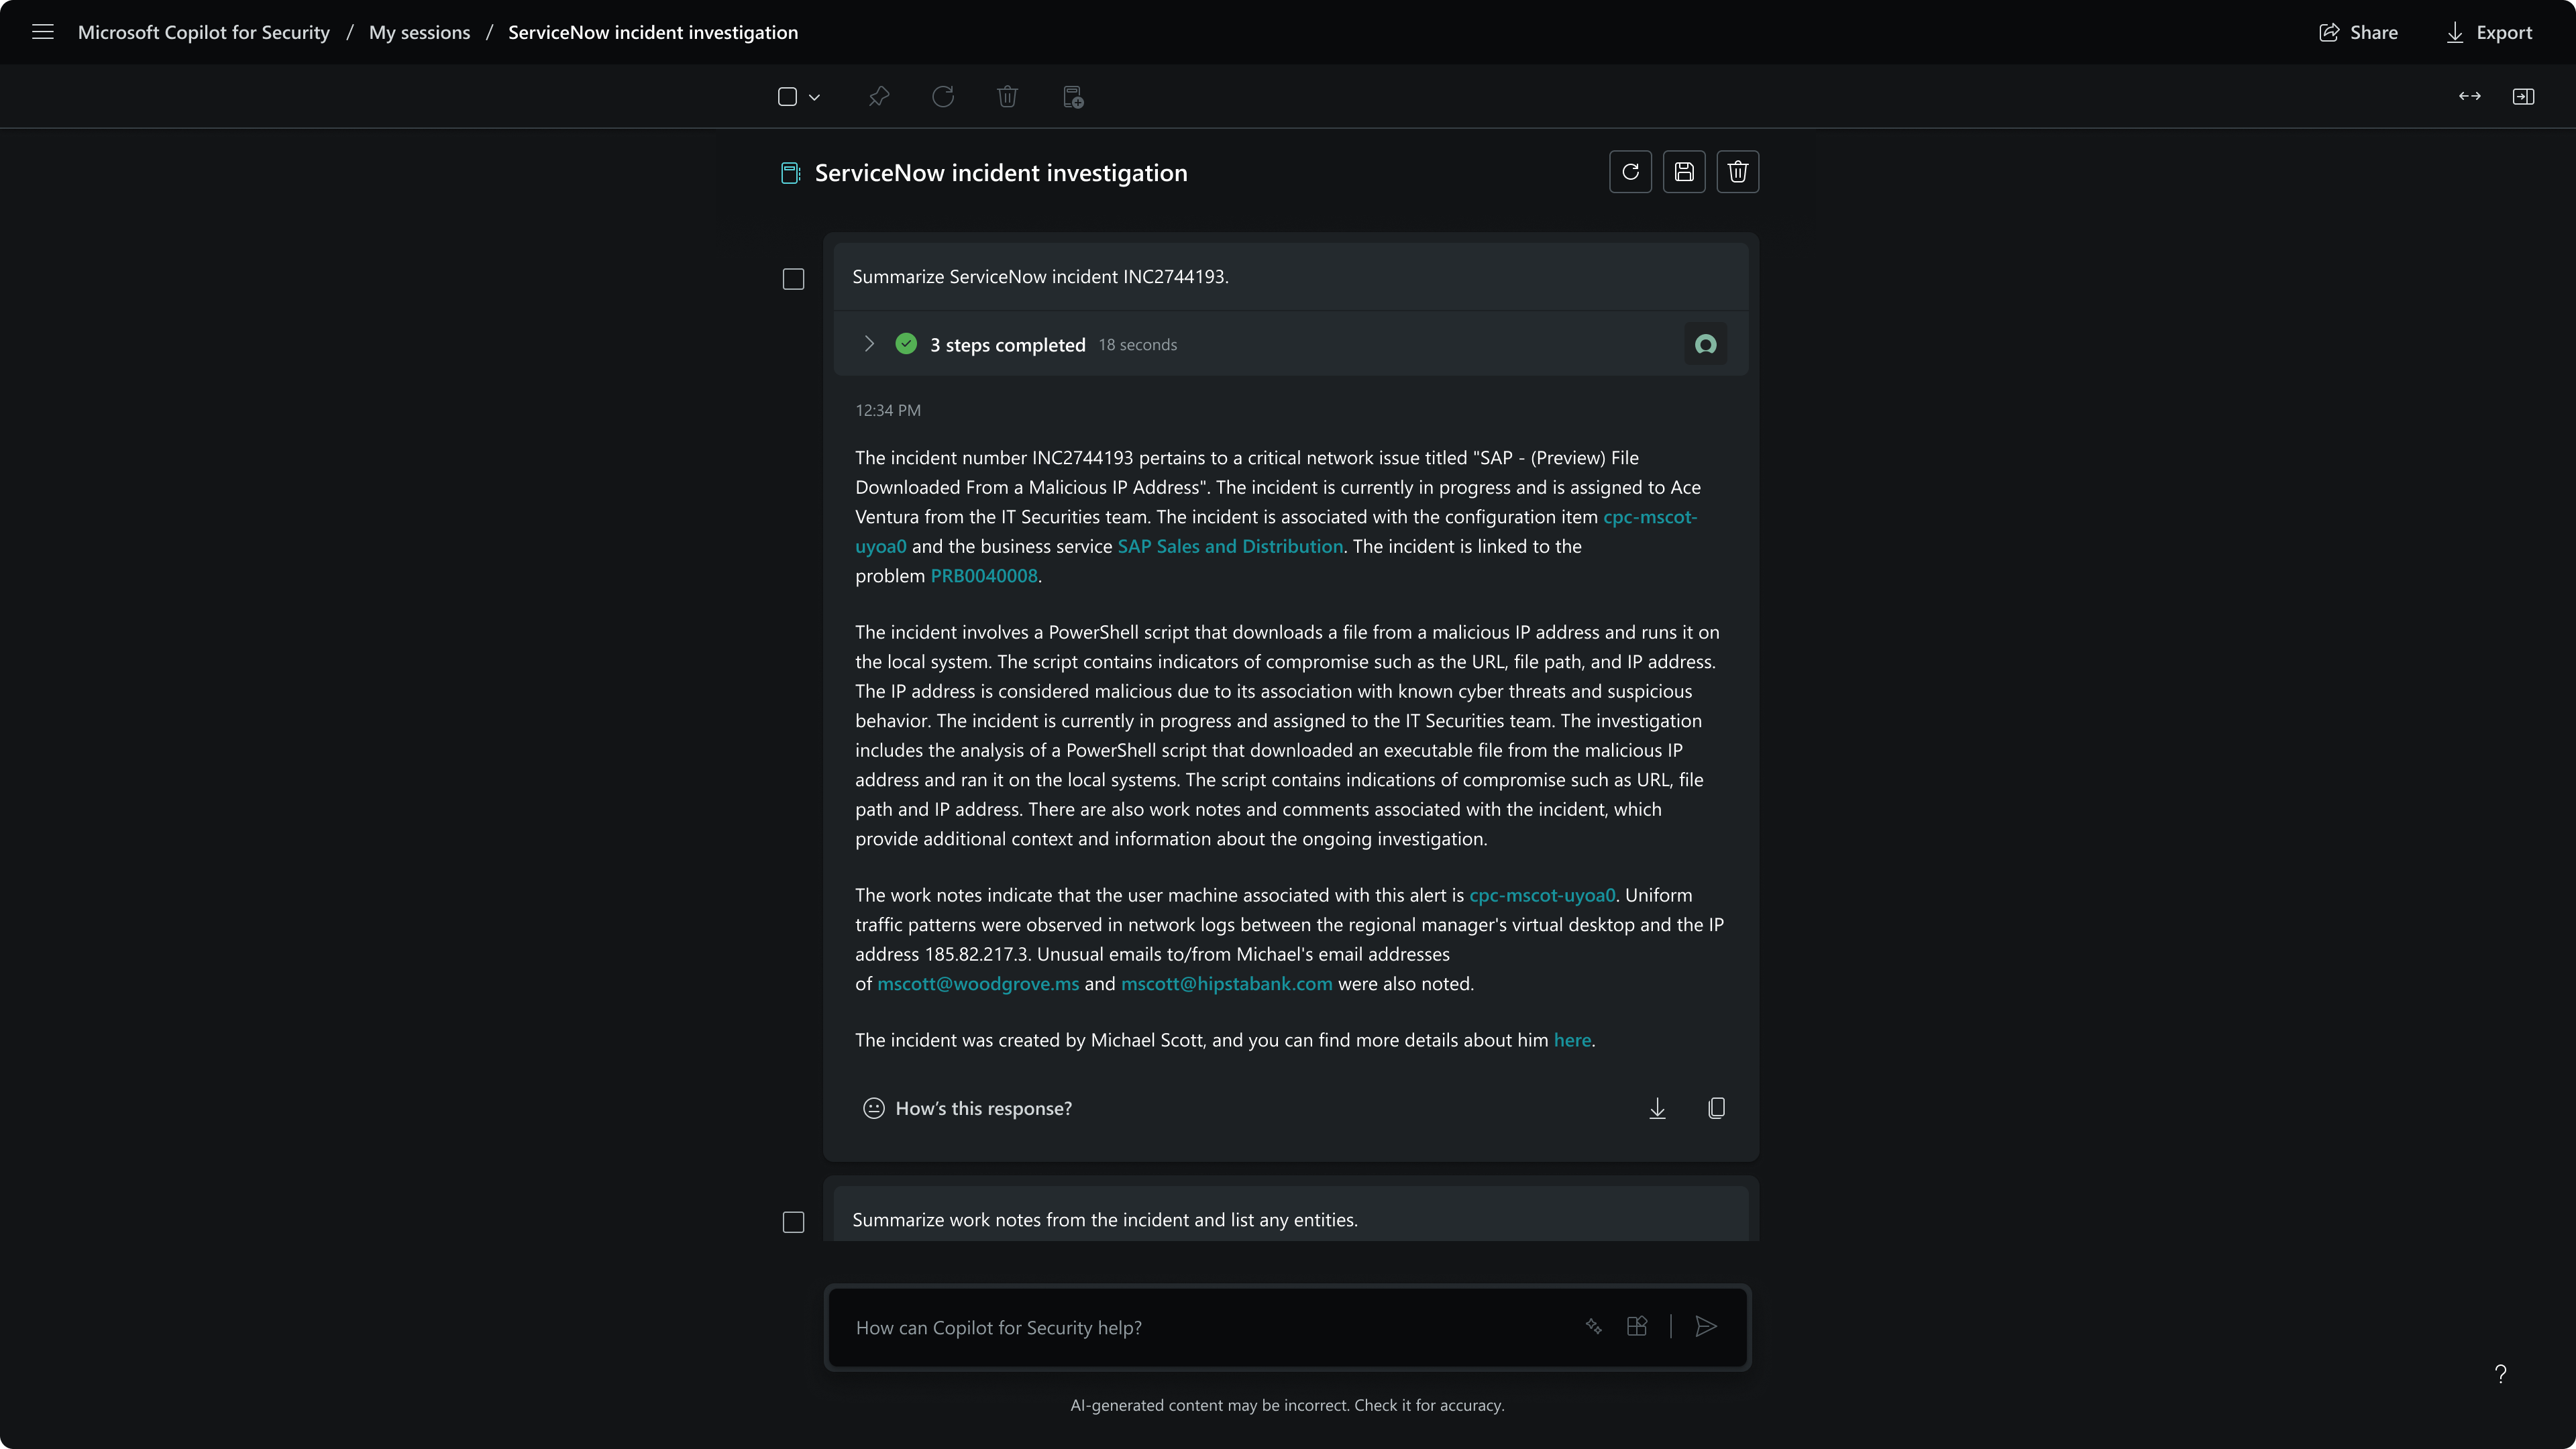
Microsoft Security Copilot helps security and IT teams to protect organizations at the speed and scale of AI. It is available in a standalone experience or embedded into other Microsoft Security products.
N/A
Splunk Enterprise Security
Score8.5 out of 10
N/A
Splunk Enterprise Security is an analytics-driven SIEM that helps to combat threats with actionable intelligence and advanced analytics at scale.
It's easy to integrate with other tools because it's a native Microsoft solution for generating OAuth tokens and handling other integrations. But as far as querying for data, using the LLM to analyze it and find that needle in the haystack, whatever, I feel it's terrible. In my experience, it just takes so much manipulation to get it to actually do what you want it to do.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Splunk ES is great for organizations with complex IT environments, and real-time visibility into their infrastructure is critical. We use it as the central platform to sort through alerts, run diagnostics, and respond to incidents. We have integrated it with SOAR and automations; both help keep our security posture up to date.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Sometimes people don't know how to do a certain feature, especially in Excel, for example. It's a little bit more complex and a community for certain people. And with just a couple of questions about using Microsoft Security Copilot, they can get their answers ready, not having to get support from IT, right? So it eliminates multiple tickets and support from personnel on our team, and they can get the response themselves via this assistant.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Writes Powerful Queries: The queries that can be written using the Splunk Query Language are very powerful and highly customizable to meet every need. Ex: Writing queries to search the intersection of two different sources like Network and Endpoint Logs.
Offers Dashboard Abilities: Helps build complex panels for Dashboards in addition to providing several out-of-the-box panels. Ex: creating panels to calculate the performance of analysts in a given timezone.
Helpful Search Aids: It helps to set up complex custom alerts very easily. The interesting fields section is very helpful while threat hunting. Ex: It shows all the users and the frequency of each in a failed login event. The user list on the interesting fields is useful to look for suspicious logins.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I don't have that as of yet. I do like the product for now. I'm sure that as I use it more, I will find things that can be improved. Just understanding how it integrates with the Microsoft ecosystem, it works just fine for what I use it for.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Improved User Interface Customization: While the interface is generally intuitive, providing more options for users to customize their dashboards and views would enhance the overall user experience. Tailoring the interface to specific roles or use cases could be a valuable addition.
Simplified Alert Management: Streamlining the process of managing alerts, such as grouping or categorizing them based on severity or type, would make it easier for security teams to prioritize and respond to incidents effectively.
Expanded Threat Intelligence Feeds: Increasing the variety and sources of threat intelligence feeds available within ES would provide a broader context for identifying and mitigating emerging threats, ensuring a more comprehensive defense against evolving attack vectors.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We are not going to stop using M365 and our environment is large enough that there is not enough in-house expertise to handle all aspects of security, even with the help of a MSSP. Security Copilot helps us shore up the knowledge gap and keep our organization's security posture tight.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Anyone can use it. Easy to prompt, also capabilities to become advance with custom agents. It can become custom to your workflow. Many people will have their unique experiences to share and results are generally positive. This is a growth in the product from the effect of community and adoption/usage.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I gave it a 6/10 because it's a perfect tool for experienced Splunk users. It's very difficult to add people to the Splunk team due to the complexity of the solutions. It took weeks to write useful SPL queries and even more time to be independent of the solution.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It takes a long time for items to load if you are just generally searching through logs. It is best to use the data models which load faster but can be strange in terms of what is coming from which logs where. Yes, you can look it up, but this also requires familiarity with where things are and how to look them up.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's good when it's responsive, but I've had times where I had to wait quite a while for a response. But these are typically the exceptions rather than the rule. When you do get a response it is always well-informed and appropriate. I would say they've been trending better over time with this.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I experienced only on-line training, but the trainers were very professional and competent. Maybe it could be more useful if they also have an experience in projects because sometimes they didn't have a real project experience to communicate to the students. Anyway, it was very interesting and I learned many thing that's very difficoult (or maybe impossible!) to have by myself, aven if I have more than 10 years of Splunk activity experience.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It was very interesting and I learned many thing that's very difficoult (or maybe impossible!) to have by myself. The only problem was that, when I worked with the Splunk Professional Services, I found some difference between the training contents and the information from PS. In addition is required a long experience on Splunk Enterprise for the data ingestion part, in other words I'm able to work with ES because I'm worling on Splunk since 11 years, otherwise I'd some problem.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
My usage of other products is based on SIEM tools. So far, Microsoft Security Copilot is the only product I've seen that works across multiple technologies/products to provide full visibility into security tooling using AI. I know other vendors are working towards this, but Microsoft has definitely taken a lead.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Splunk enterprise is the only solution that we’ve been able to identify that provides risk based alerting, which allows our SOC to reduce analyst fatigue which would be a huge problem without it. Before RBA, there were thousands of alerts a day and it was impossible to review all of them
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
for my exterience, unit pricing and billing frequency are correct. As I already said, I hint to have more discount flexibility, expecially with new customers, because there are competitors less expensive and very aggressive that are dangerous. In addition the possibility to don't pay the license for the development period could be a very interesting feature for the final customers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
- 8 out of 10 and took 2 for the data pipeline and administration part. Even if you'd like to improve yourself or your team, you have to pay a lot of money and it could be more than GIAC education + cert. - Normalization for Data models and CPU-based searches can be a problem sometimes.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I had a fantastic experience with Splunk Professional Services: they worked with us in our last SON project (a SOC migration for a very large customer) and helped to build a multi tenent environment even if ES isn't a multi tenant platform. Th Splunk PS was a very professional and competent people, he is italian and was able to speak with our italian customers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say it was initially negative because it took us time to learn it and understand how to build the workflow around it. But since then, we've been able to speed up and adjust and adapt and move a lot faster. So it's overall.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We have a 100% success rate on all our ES implementations due to the amazing documentation and Splunk enablement on the subject.
Our Splunk ES business has grown 100% YoY for the last 3 years.
In terms of long term management and maintenance, ES has been highly stable and predictable, reducing our overhead on costly services team for ad hoc maintenance work.