OpenText™ ALM/Quality Center, formerly from Micro Focus, serves as the single pane of glass for software quality management. It helps users to govern application lifecycle management activities and implement rigorous, auditable lifecycle processes.
N/A
SonarQube
Score8.7 out of 10
N/A
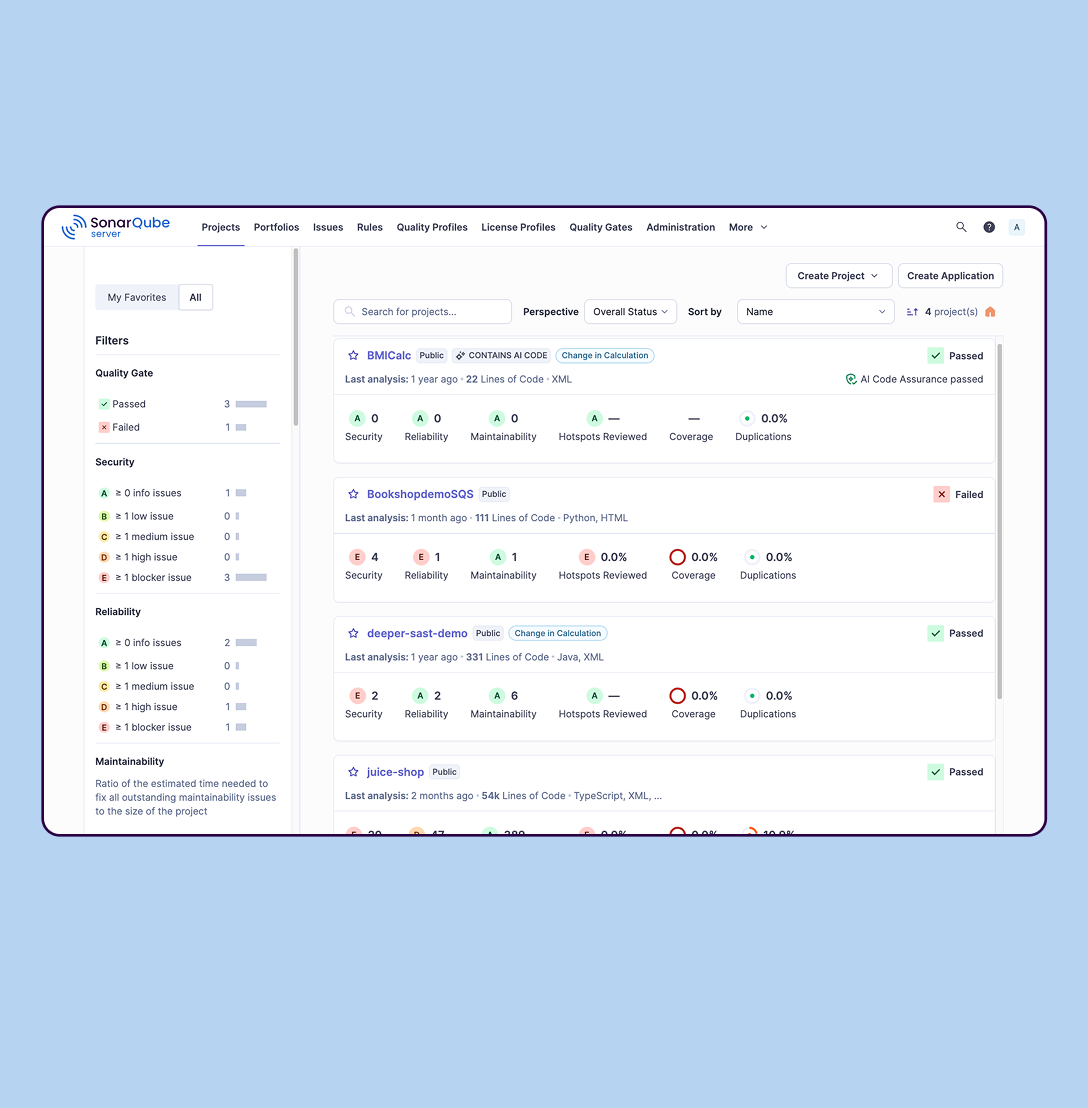
SonarQube is an automated code review solution, serving as the verification layer for code quality and SDLC security. SonarQube is used to ensure that code is secure, reliable, and maintainable. It is available through SaaS or self-managed deployment.
For an organisation that has completely adopted SAFe structure including naming terminology, it is less appropriate and apart from that. It can suit any organisation out there, and it can solve all your problems one way or another by customising it. It is a robust and highly scalable solution to support all the business needs. It improves a lot of productivity and visibility.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is excellent if you start using it at the beginning when developing a new system, in this situation you will be able to fix things before they become spread and expensive to correct. It’s a bit less suitable to use on existing code with bad design as it’s usually too expensive to fix everything and only allows you to ensure the situation doesn’t get worse.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you have a mix of automation & manual test suites, HPALM is the best tool to manage that. It definitely integrates very well with HP automation tools like HP Unified Functional Testing and HP LoadRunner. Automated Suites can be executed, reports can be maintained automatically. It also classifies which test suites are manual & which are automated & managers can see the progress happening in moving from manual to automated suites. In HPA ALM all the functional test suites, performance test suites, security suites can be defined, managed & tracked in one place.
It is a wonderful tool for test management. Whether you want to create test cases, or import it, from execution to snapshot capturing, it supports all activities very well. The linking of defects to test runs is excellent. Any changes in mandatory fields or status of the defect triggers an e-mail and sent automatically to the user that the defect is assigned to.
It also supports devops implementation by interacting with development tool sets such as Jenkins & GIT. It also bring in team collaboration by supporting collaboration tools like Slack and Hubot.
This tool can integrate to any environment, any source control management tool bringing in changes and creates that trace-ability and links between source control changes to requirements to tests across the sdlc life-cycle.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
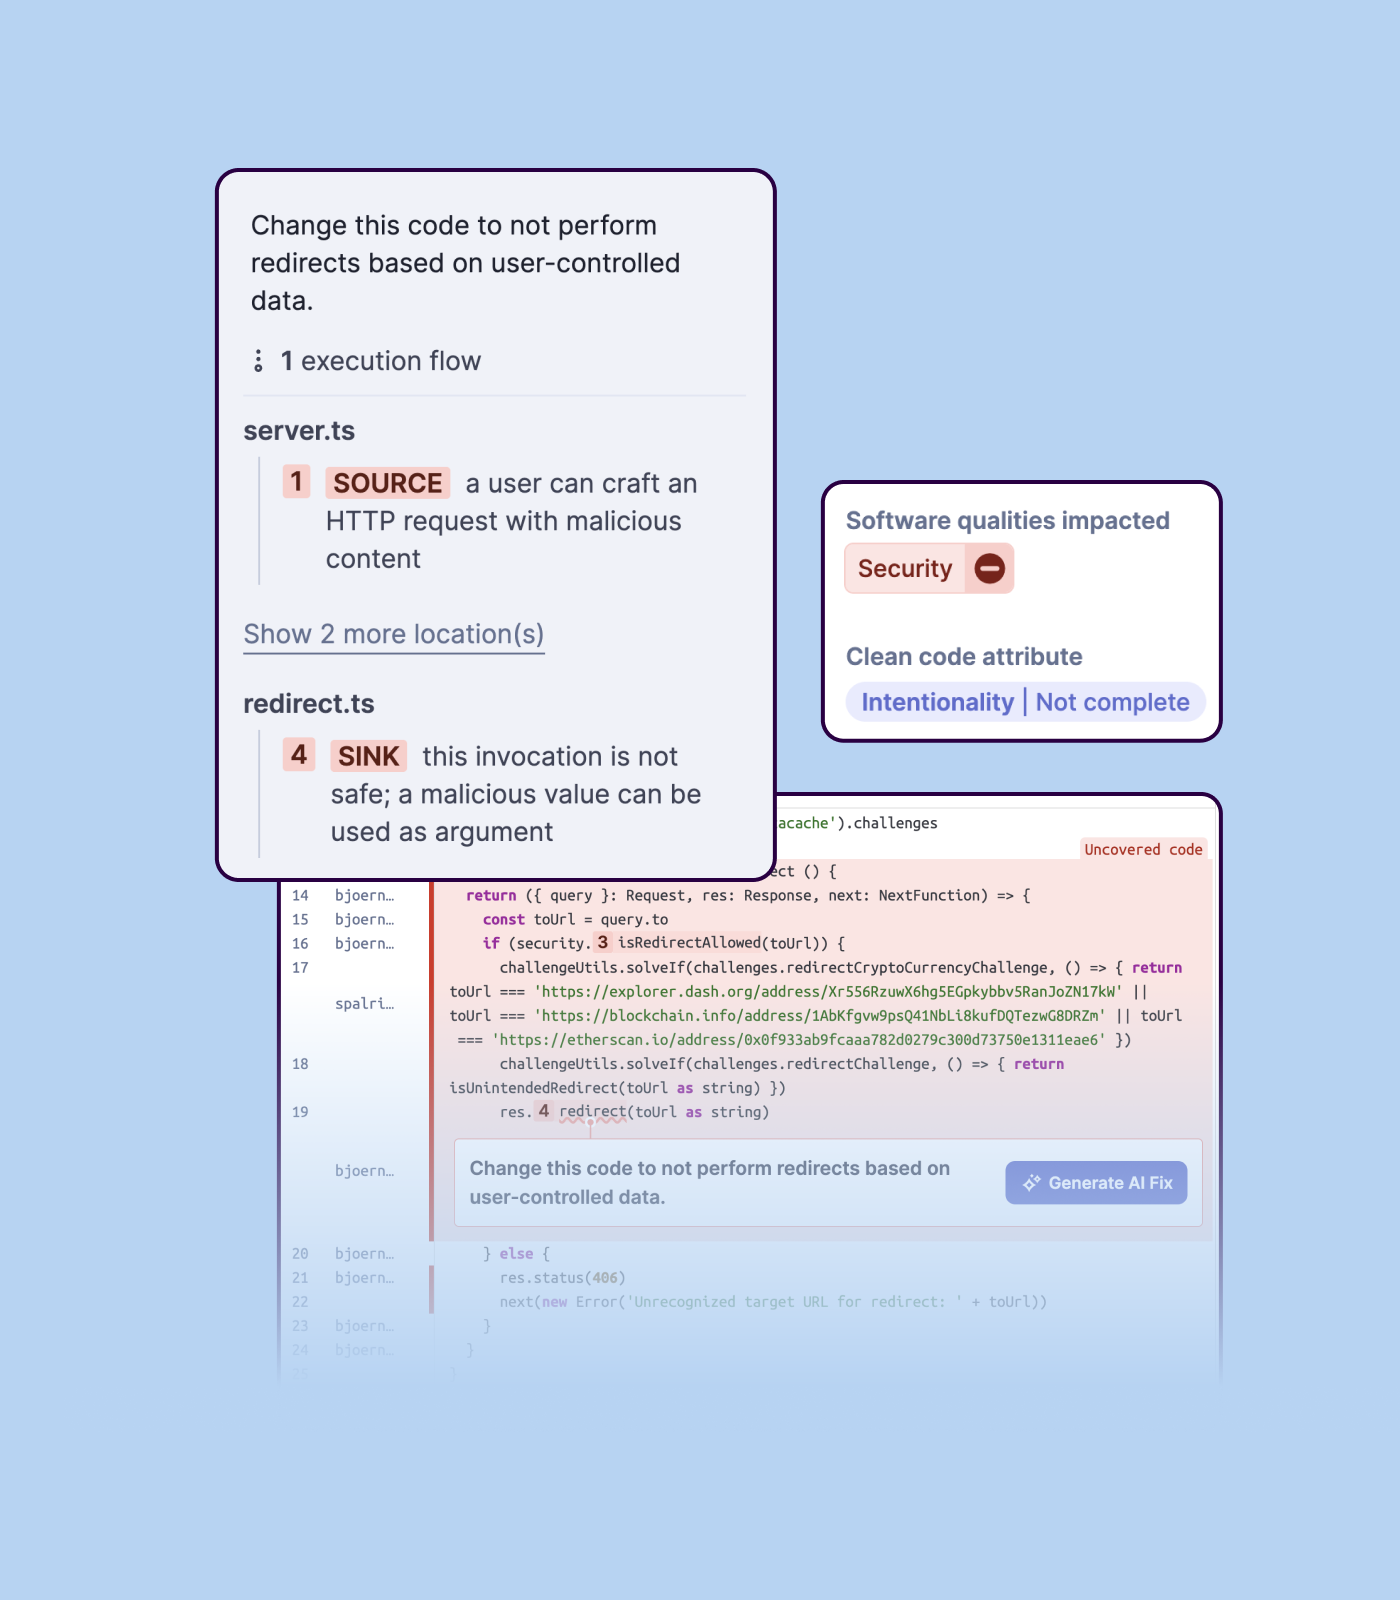
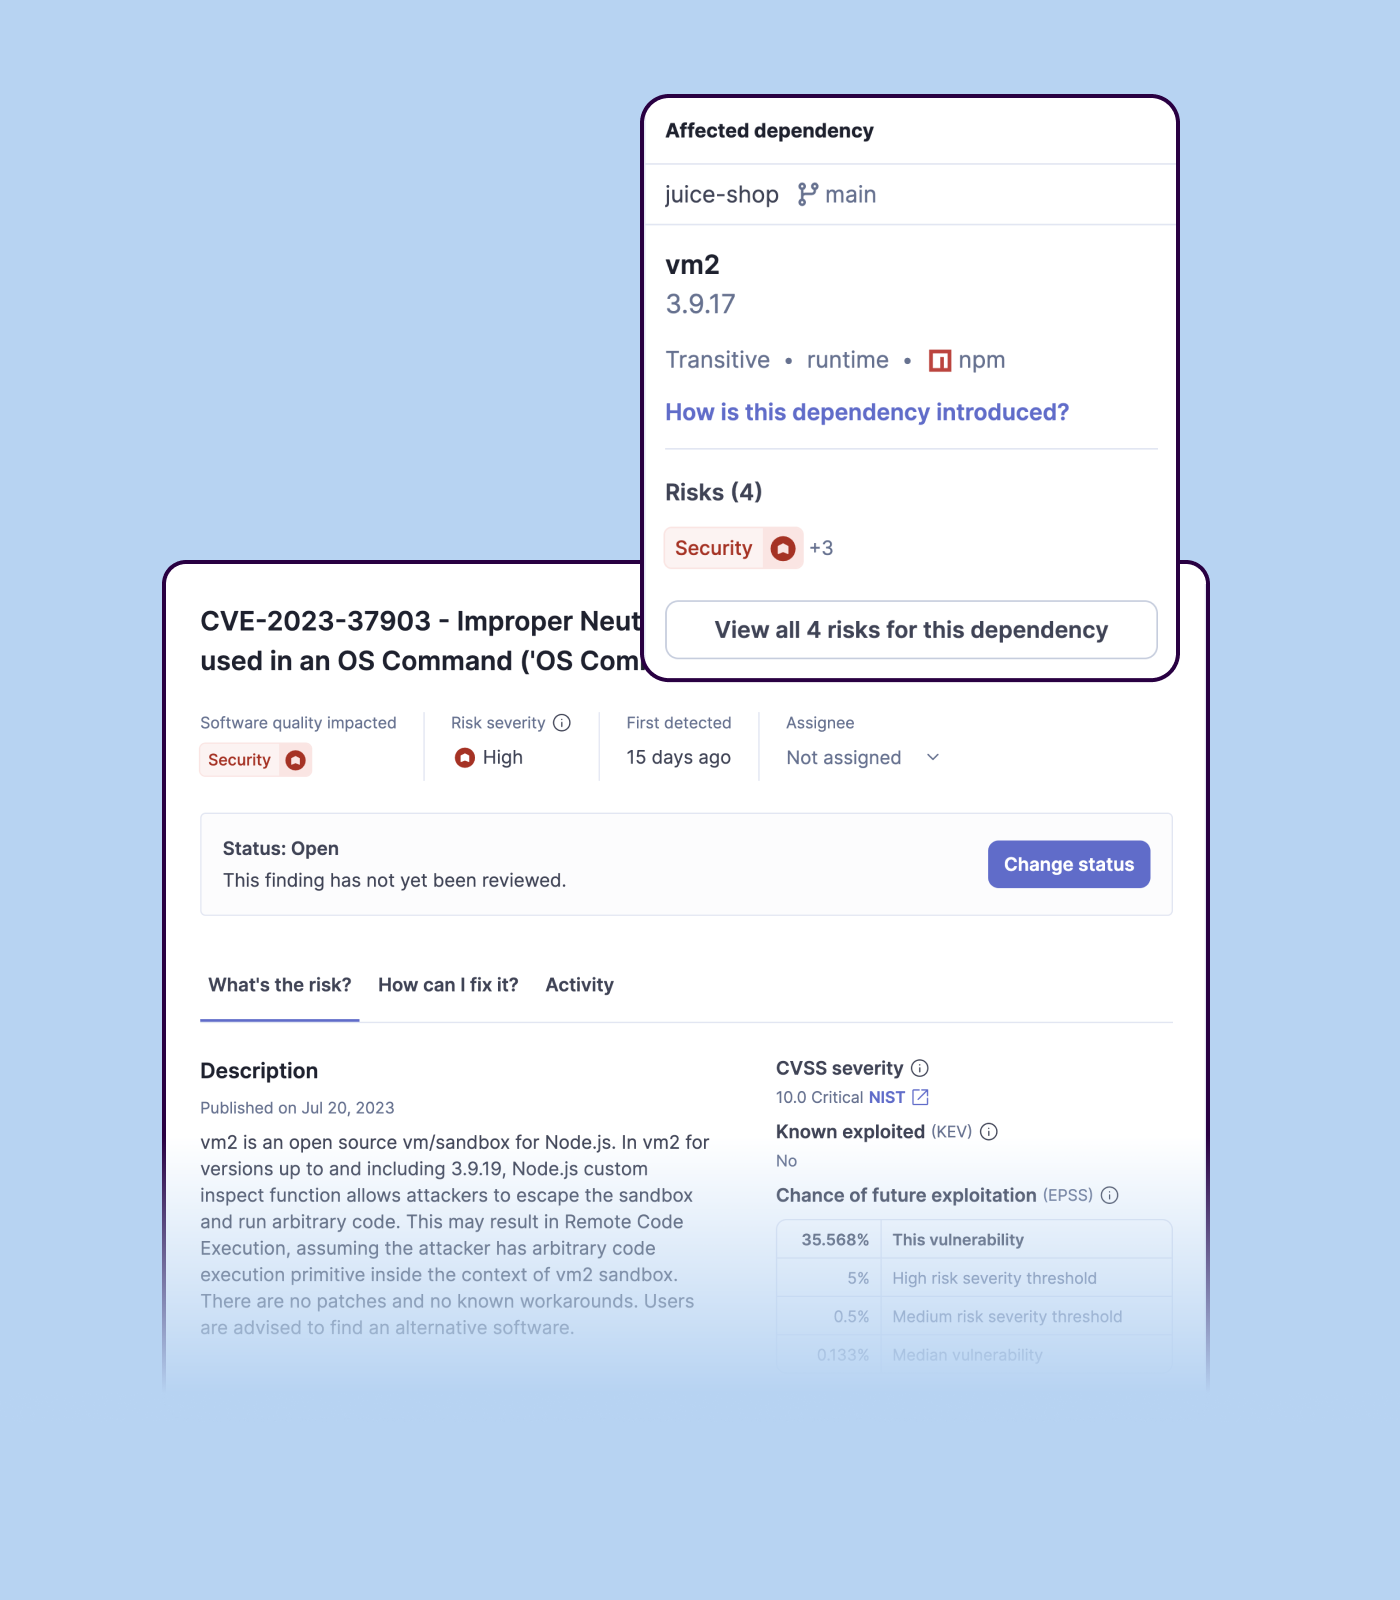
Detecting bugs and vulnerabilities: SonarQube can identify a wide range of bugs and vulnerabilities in code, such as null pointer exceptions, SQL injection, and cross-site scripting (XSS) attacks. It uses static analysis to analyze the code and identify potential issues, and it can also integrate with dynamic analysis tools to provide even more detailed analysis.
Measuring code quality: SonarQube can measure a wide range of code quality metrics, such as cyclomatic complexity, duplicated code, and code coverage. This can help teams understand the quality of their code and identify areas that need improvement.
Providing actionable insights: SonarQube provides detailed information about issues in the code, including the file and line number where the issue occurs and the severity of the issue. This makes it easy for developers to understand and address issues in the code.
Integrating with other tools: SonarQube can be integrated with a wide range of development tools and programming languages, such as Git, Maven, and Java. This allows teams to use SonarQube in their existing development workflow and take advantage of its powerful code analysis capabilities.
Managing technical debt: SonarQube provides metrics and insights on the technical debt on the codebase, enabling teams to better prioritize issues to improve the quality of the code.
Compliance with coding standards: SonarQube can check the code against industry standards like OWASP, CWE and more, making sure the code is compliant with security and coding standards.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The requirements module is not as user friendly as other applications, such as Blue Bird. Managing requirements is usually done in another tool. However, having the requirements in ALM is important to ensure traceability to tests and defects.
Reporting across multiple ALM repositories is not supported within the tool. Only graphs are included within ALM functionality. Due to size considerations, one or two projects is not a good solution. Alternatively, we have started leveraging the template functionality within ALM and are integrating with a third party reporting tool to work around this issue.
NET (not Octane) requires a package for deployment to machines without administrative rights. Every time there is a change, a new package must be created, which increases the time to deploy. It also forces us to wait until multiple patches have been provided before updating production.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Importing a new custom quality profile on SonarQube is a bit tricky, it can be made easier
Every second time when we want to rerun the server, we have to restart the whole system, otherwise, the server stops and closes automatically
When we generate a new report a second time and try to access the report, it shows details of the old report only and takes a lot of time to get updated with the details of the new and fresh report generated
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it lets me track the test cases with detailed scenarios and is clearly separated in folders. Also the defect filter helps me filter only the ones that have been assigned to a particular area of interest. The availability of reports lets me see the essentials fields which I might be missing the data on and helps me to work on these instead of having to go through everything.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is a great tool, however, it got this rating because there is a lot of learning that takes a lot longer than other tools. There are no mobile versions of ALM even with just a project summary view. I believe ALM is well capable of integration with other analytics tools that can help business solutions prediction based on current and past project data. This is Data held in ALM but with no other use apart from human reading and project progress. ALM looks like a steady platform that I believe can handle more dynamic functionality. You could add an internal communication platform that is not a third party. Limit that communication tool to specific project members.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We we easily able to integrate the SonarQube steps into our TFS process via the Microsoft Marektplace, we didn't have the need to call SonarQube support. We've used their online documentation and community forum if we ran into any issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have other tools in our organization like Atlassian JIRA and Microsoft Team Foundation Server, which are very capable tools but very narrow in their approach and feature set and does not come even close to the some of the core capabilities of HP ALM. HP ALM is the "System of Record" in our organization. It gives visibility for an artifact throughout the delivery chain, which cut downs unnecessary bottlenecks and noise during releases.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is an open-source. It's a scalable product. The costs for this application, for the kind of job it does, are pretty descent. Pipeline scan is more secured in SonarQube. Its a very good tool and its support multiple languages. Its main core competency is of static code analysis and that is why SonarQube exists and it does it exceedingly well. The quality of scan on code convention, best practices, coding standards, unit test coverage etc makes them one of the best competent tool in the market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive ROI from the standpoint of flagging several issues that would have otherwise likely been unaddressed and caused more time to be spent closer to launch
Slightly positive ROI from time-saving perspective (it's an automated check which is nice, but depending on the issues it finds, can take developers time to investigate and resolve)