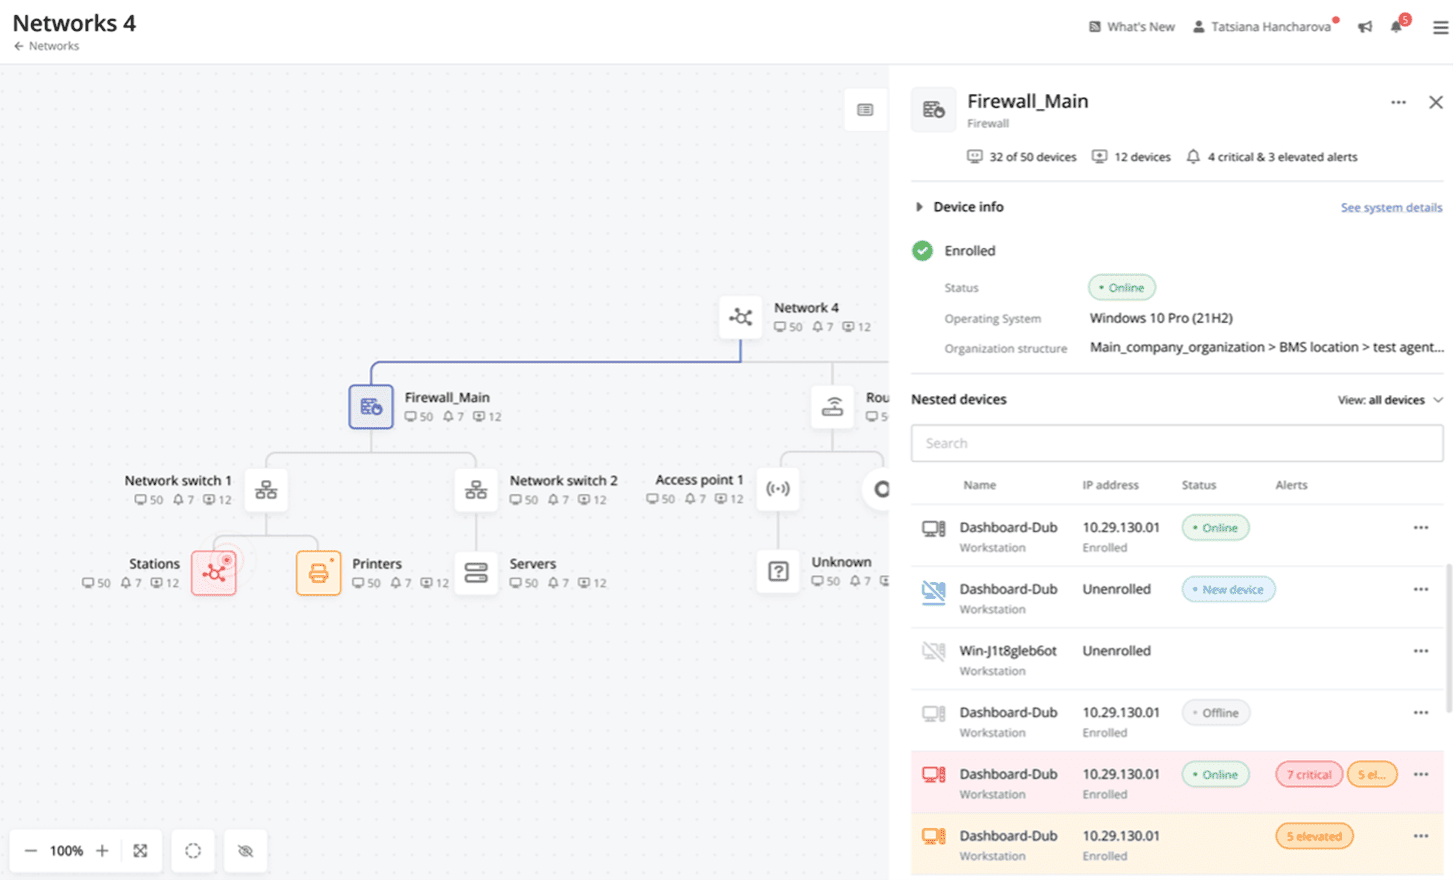
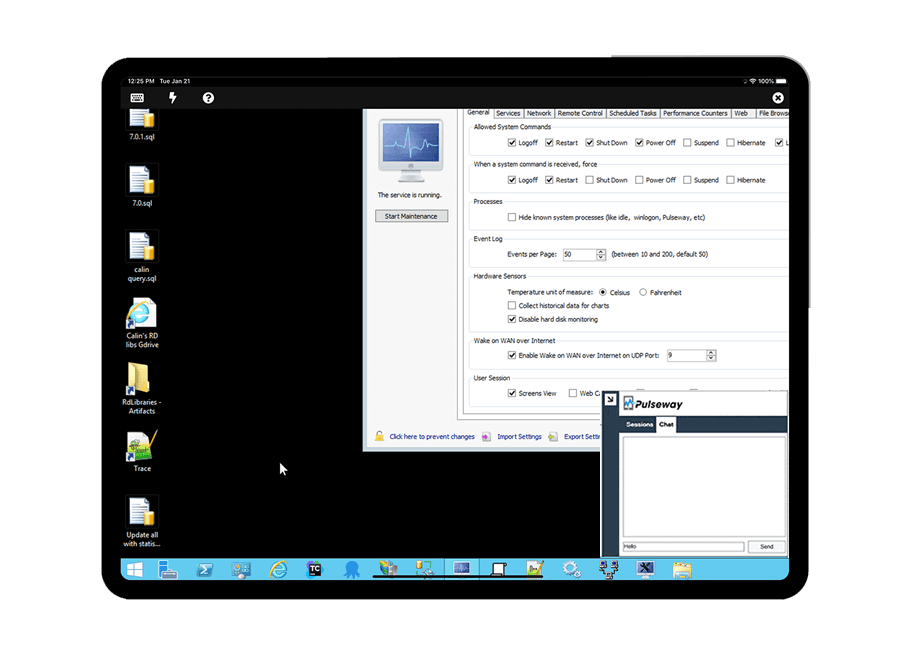
Pulseway is an IT monitoring and management solution that enables users to monitor, manage and control all systems and servers from a smartphone, tablet or browser. For system administrators, Pulseway sends a notification, so they can see an issue and sort it in seconds. Pulseway features: Automation: Auto-remediation workflows, so that IT issues are fixed before users even notice them. Mobile Access: Customers can monitor, manage, connect with…
$0.80
per month per installation
Symantec Content & Malware Analysis
Score8.3 out of 10
N/A
Symantec Content & Malware Analysis is an application which provides advanced threat detection and threat hunting through advanced machine learning, based on intelligence gathered from ProxySG, threat intelligence services, and other sources.
N/A
Pricing
Pulseway
Symantec Content & Malware Analysis
Editions & Modules
Enterprise
$0.80
per month per installation
No answers on this topic
Offerings
Pricing Offerings
Pulseway
Symantec Content & Malware Analysis
Free Trial
Yes
No
Free/Freemium Version
Yes
No
Premium Consulting/Integration Services
Yes
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
No hidden fees or contracts. Term-based discounts.
If you have to manage a large number of computers, especially spread over multiple clients or a large physical area. This is one of the main products that allows us to act as a Managed Service Provider (MSP) and actually manage our clients devices and not just react to issues as clients call them in. Clients really love the proactive approach it allows us to take. Sadly as we became more familiar with options out there we found this area lacking and what was actually holding us back.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you have Symantec based environment including Symantec proxy and endpoints, Content and Malware Analysis is the obvious choice. You can't run the CAS-MAS as a standalone deployment, you need proxies or ICAP supported devices capable to send the files/URLS. It's not a network security device where you can flow/direct the traffic to C/MAS. It does not have UBA, NBA or NTR features, it is just working for analyzing files as expected.
It monitors computers and notifies us of any issues with any computer.
It allows remote control of computers, such as requesting a computer to reboot itself.
It is very highly configurable to monitor exactly what we need to monitor. For example, on server, we can have it notify us any time the server is shutdown or rebooted. On the other hand, for a desktop computer, we don't have to be bothered with notifications when a user decides to reboot his computer.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The tool is easy to use however it is can be daunting with the amount of features available in it. Last I checked, their knowledge base was not very expansive and they relied a lot on the changelog for how to do some stuff. This can make it hard to learn how to do some more advanced things like the automation.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I have never had to use the support for Pulseway. However, when initially starting out, we would receive emails every so often asking how we are doing and if there is any support that they can provide. I would imagine that any request would be supplied with the same great support!
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Pulseway has the most features, the best looking app with the best design and better usability than any others we evaluated. We liked the uniformity of the app design across all platforms (Windows, Android, Apple) and the notifications displayed on each platform. The price was a major contributor to our selection of Pulseway compared to the competition.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have been using many solutions even tested nearly all available 0day sandbox solutions in the market. We choose Symantec CMA as we have already Symantec endpoint protection/EDR on the client, Symantec proxy for the web access, SCMA fits our environment. We have a big bargain when we puchase lots of equipment from the Symantec. Detection and prevention is very good at SCMA but some constant issues; like the product is not designed for heterogeneous environments, we can not integrate the SCMA with WAFs, it's lacking in api and request/reply calls. There's no file scanning, discover the option. SIEM integration is not smooth. I can not run some of the SOAR playbooks through the SCMA.
Problems can be dealt with more rapidly because I have access to systems from anywhere. I don't have to carry a computer with me nor do I have to find a location with potentially non-secure wifi to gain access to my systems.
I can handle 99% of my system admin tasks using Pulseway and never have to touch a system or connect to the console.
Pulseway gives so much control over a system that I don't need to spend extra money on other software to perform management tasks.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
As the SSL is inspected and analyzed at Bluecoat proxy servers, hidden threats, malicous files are passed to SCMA to be analyzed.
Getting full visibility at file trajectory level
As it's a full proxy and ICAP integration, we are sure that the files are to analyzed and scanned for malicious activity. This is a big plus compared to NGFW analyze concept, as the NGFWs have special failsafe mechanisms allowing bypass of file analysis. SCMA fully catches the hidden threats.
Flawless integration with Bluecoat systems is a big plus, customers are getting the same type of messages within their browsers.
A negative impact is the standardization when I deploy SCAM to one of our locations. Then the auditors demand the same coverage within other areas and it comes with the cost. Especially maintaining these devices on premise environment has a significant cost.