VMware Salt is an Infrastructure Automation & Configuration Management platform that provisions, configures, deploys, and manages infrastructure components at scale. The solution utilizes an event-driven automation engine to enforce compliant software states across virtual machines, servers, containers, and network devices.
The VMware Salt solution is comprised of software components from both VMware and the open-source Salt Project While the Salt Masters and Salt Minions are a part of the open…
N/A
SonarQube
Score8.5 out of 10
N/A
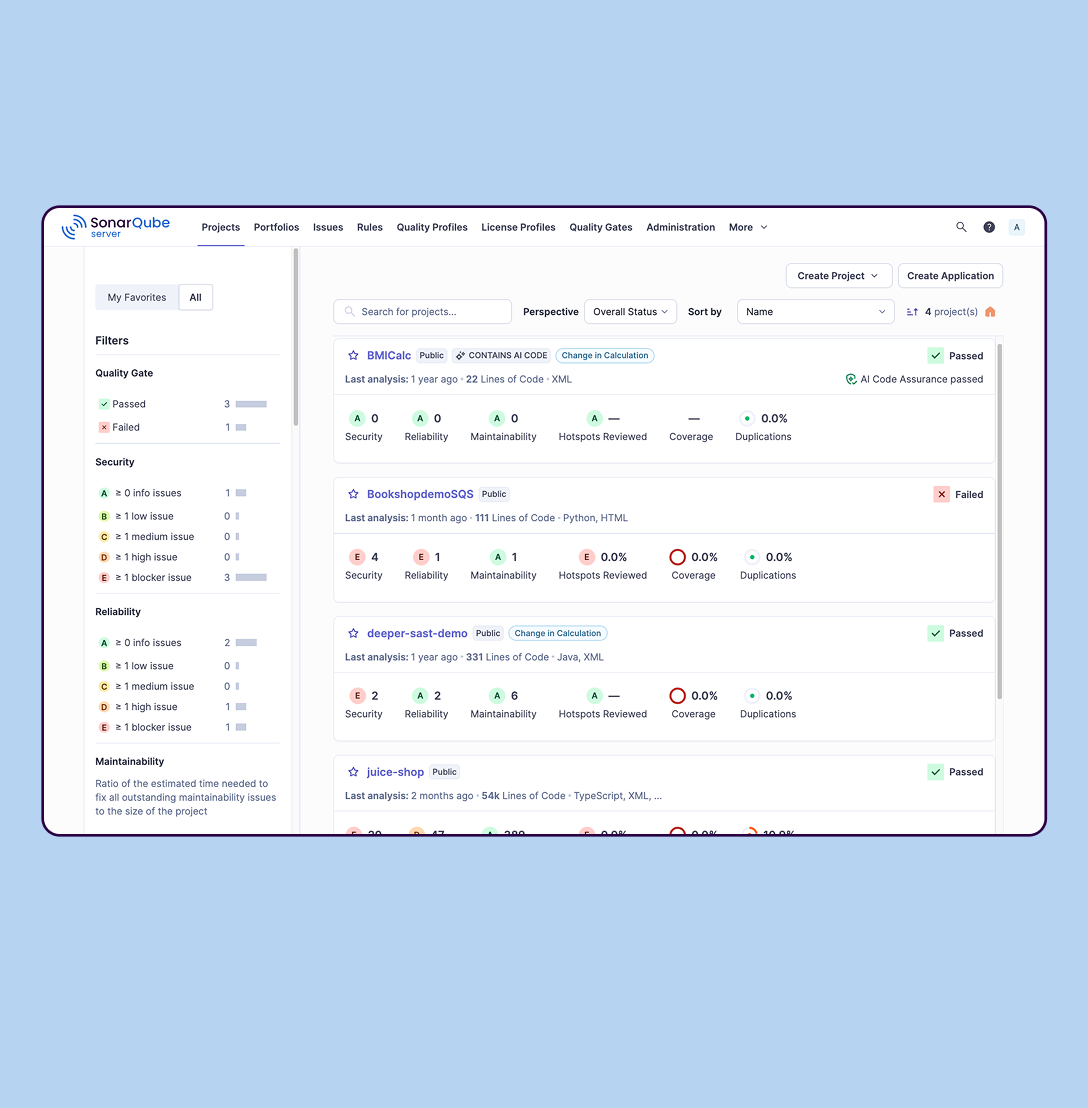
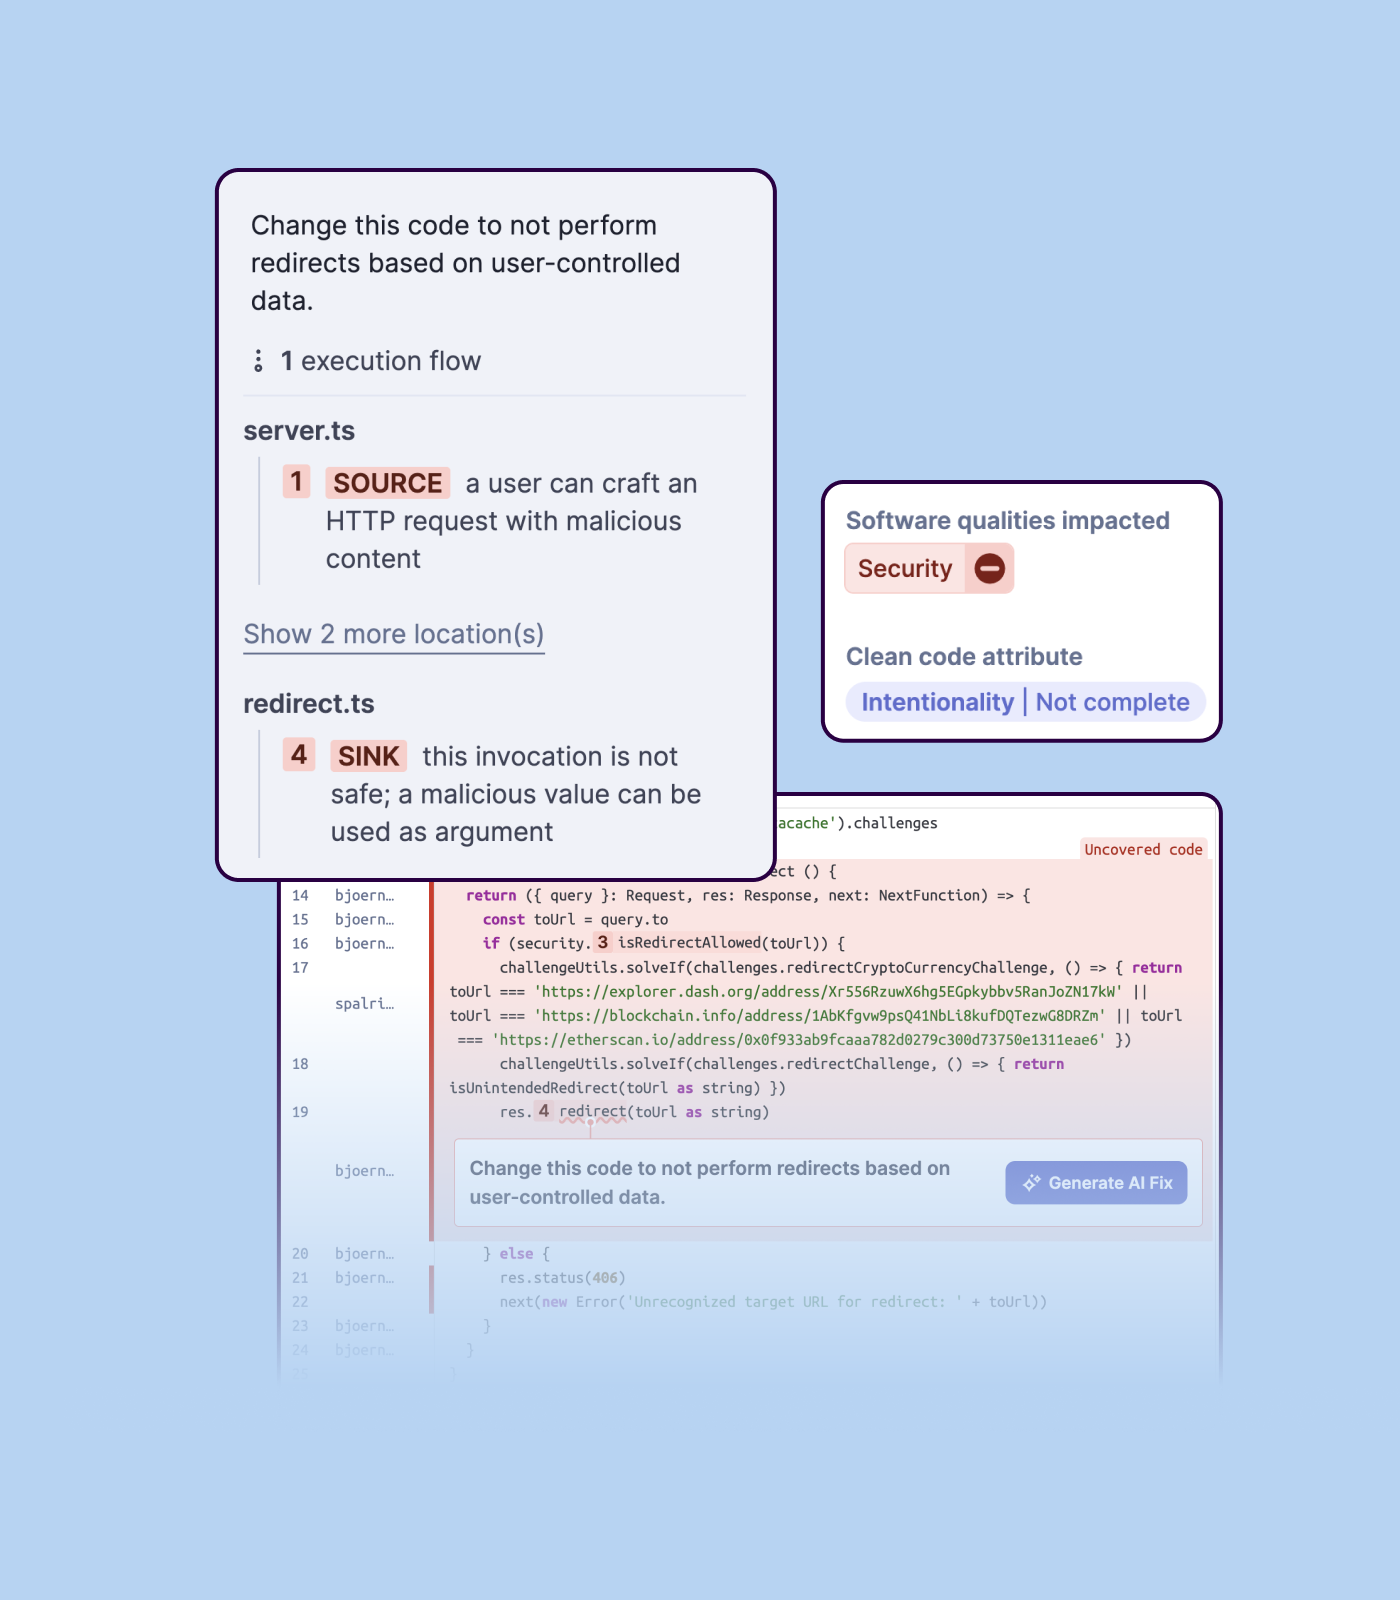
SonarQube is an automated code review solution, serving as the verification layer for code quality and SDLC security. SonarQube is used to ensure that code is secure, reliable, and maintainable. It is available through SaaS or self-managed deployment.
SaltStack is a very well architected toolset and framework for reliably managing distributed systems' complexity at varied scale. If the diversity of kind or number of assets is low, or the dependencies are bounded and simple, it might be overkill. Realization that you need SaltStack might come in the form of other tools, scripts, or jobs whose code has become difficult, unreliable, or unmaintainable. Rather than a native from-scratch SaltStack design, be aware that SaltStack can be added on to tools like Docker or Chef and optionally factor those tools out or other tools into the mix.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is excellent if you start using it at the beginning when developing a new system, in this situation you will be able to fix things before they become spread and expensive to correct. It’s a bit less suitable to use on existing code with bad design as it’s usually too expensive to fix everything and only allows you to ensure the situation doesn’t get worse.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Targeting is easy and yet extremely granular - I can target machines by name, role, operating system, init system, distro, regex, or any combination of the above.
Abstraction of OS, package manager and package details is far advanced beyond any other CRM I have seen. The ability to set one configuration for a package across multiple distros, and have it apply correctly no matter the distrospecific naming convention or package installation procedure, is amazing.
Abstraction of environments is similarly valuable - I can set a firewall rule to allow ssh from "management", and have that be defined as a specific IP range per dev, test, and prod.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Detecting bugs and vulnerabilities: SonarQube can identify a wide range of bugs and vulnerabilities in code, such as null pointer exceptions, SQL injection, and cross-site scripting (XSS) attacks. It uses static analysis to analyze the code and identify potential issues, and it can also integrate with dynamic analysis tools to provide even more detailed analysis.
Measuring code quality: SonarQube can measure a wide range of code quality metrics, such as cyclomatic complexity, duplicated code, and code coverage. This can help teams understand the quality of their code and identify areas that need improvement.
Providing actionable insights: SonarQube provides detailed information about issues in the code, including the file and line number where the issue occurs and the severity of the issue. This makes it easy for developers to understand and address issues in the code.
Integrating with other tools: SonarQube can be integrated with a wide range of development tools and programming languages, such as Git, Maven, and Java. This allows teams to use SonarQube in their existing development workflow and take advantage of its powerful code analysis capabilities.
Managing technical debt: SonarQube provides metrics and insights on the technical debt on the codebase, enabling teams to better prioritize issues to improve the quality of the code.
Compliance with coding standards: SonarQube can check the code against industry standards like OWASP, CWE and more, making sure the code is compliant with security and coding standards.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Importing a new custom quality profile on SonarQube is a bit tricky, it can be made easier
Every second time when we want to rerun the server, we have to restart the whole system, otherwise, the server stops and closes automatically
When we generate a new report a second time and try to access the report, it shows details of the old report only and takes a lot of time to get updated with the details of the new and fresh report generated
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We haven't had to spend a lot of time talking to support, and we've only had one issue, which, when dealing with other vendors is actually not that bad of an experience.
We we easily able to integrate the SonarQube steps into our TFS process via the Microsoft Marektplace, we didn't have the need to call SonarQube support. We've used their online documentation and community forum if we ran into any issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We moved to SaltStack from Puppet about 3 years ago. Puppet just has too much of a learning curve and we inherited it from an old IT regime. We wanted something we could start fresh with. Our team has never looked back. SaltStack is so much easier for us to use and maintain.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is an open-source. It's a scalable product. The costs for this application, for the kind of job it does, are pretty descent. Pipeline scan is more secured in SonarQube. Its a very good tool and its support multiple languages. Its main core competency is of static code analysis and that is why SonarQube exists and it does it exceedingly well. The quality of scan on code convention, best practices, coding standards, unit test coverage etc makes them one of the best competent tool in the market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We manage two complex highly available self-healing (all infrastructure and systems) environments using SaltStack. Only one person is needed to run SaltStack. That is a HUGE return on investment.
Building tooling on top of SaltStack has allowed us to share administrative abilities by role - e.g. employee X can deploy software Y. No need to call a sysadmin and etc.
Recovery from problems, or time to stand-up new systems is now counted in minutes (usually under eight) rather than hours. This is a strategic advantage for rolling out new services.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive ROI from the standpoint of flagging several issues that would have otherwise likely been unaddressed and caused more time to be spent closer to launch
Slightly positive ROI from time-saving perspective (it's an automated check which is nice, but depending on the issues it finds, can take developers time to investigate and resolve)