TrustRadius: an HG Insights company

ManageEngine Log360

Score8.4 out of 10

15 Reviews and Ratings

What is ManageEngine Log360?

Log360 is a unified SIEM solution with integrated DLP and CASB capabilities that detects, prioritizes, investigates, and responds to security threats.

Read more details.

Media

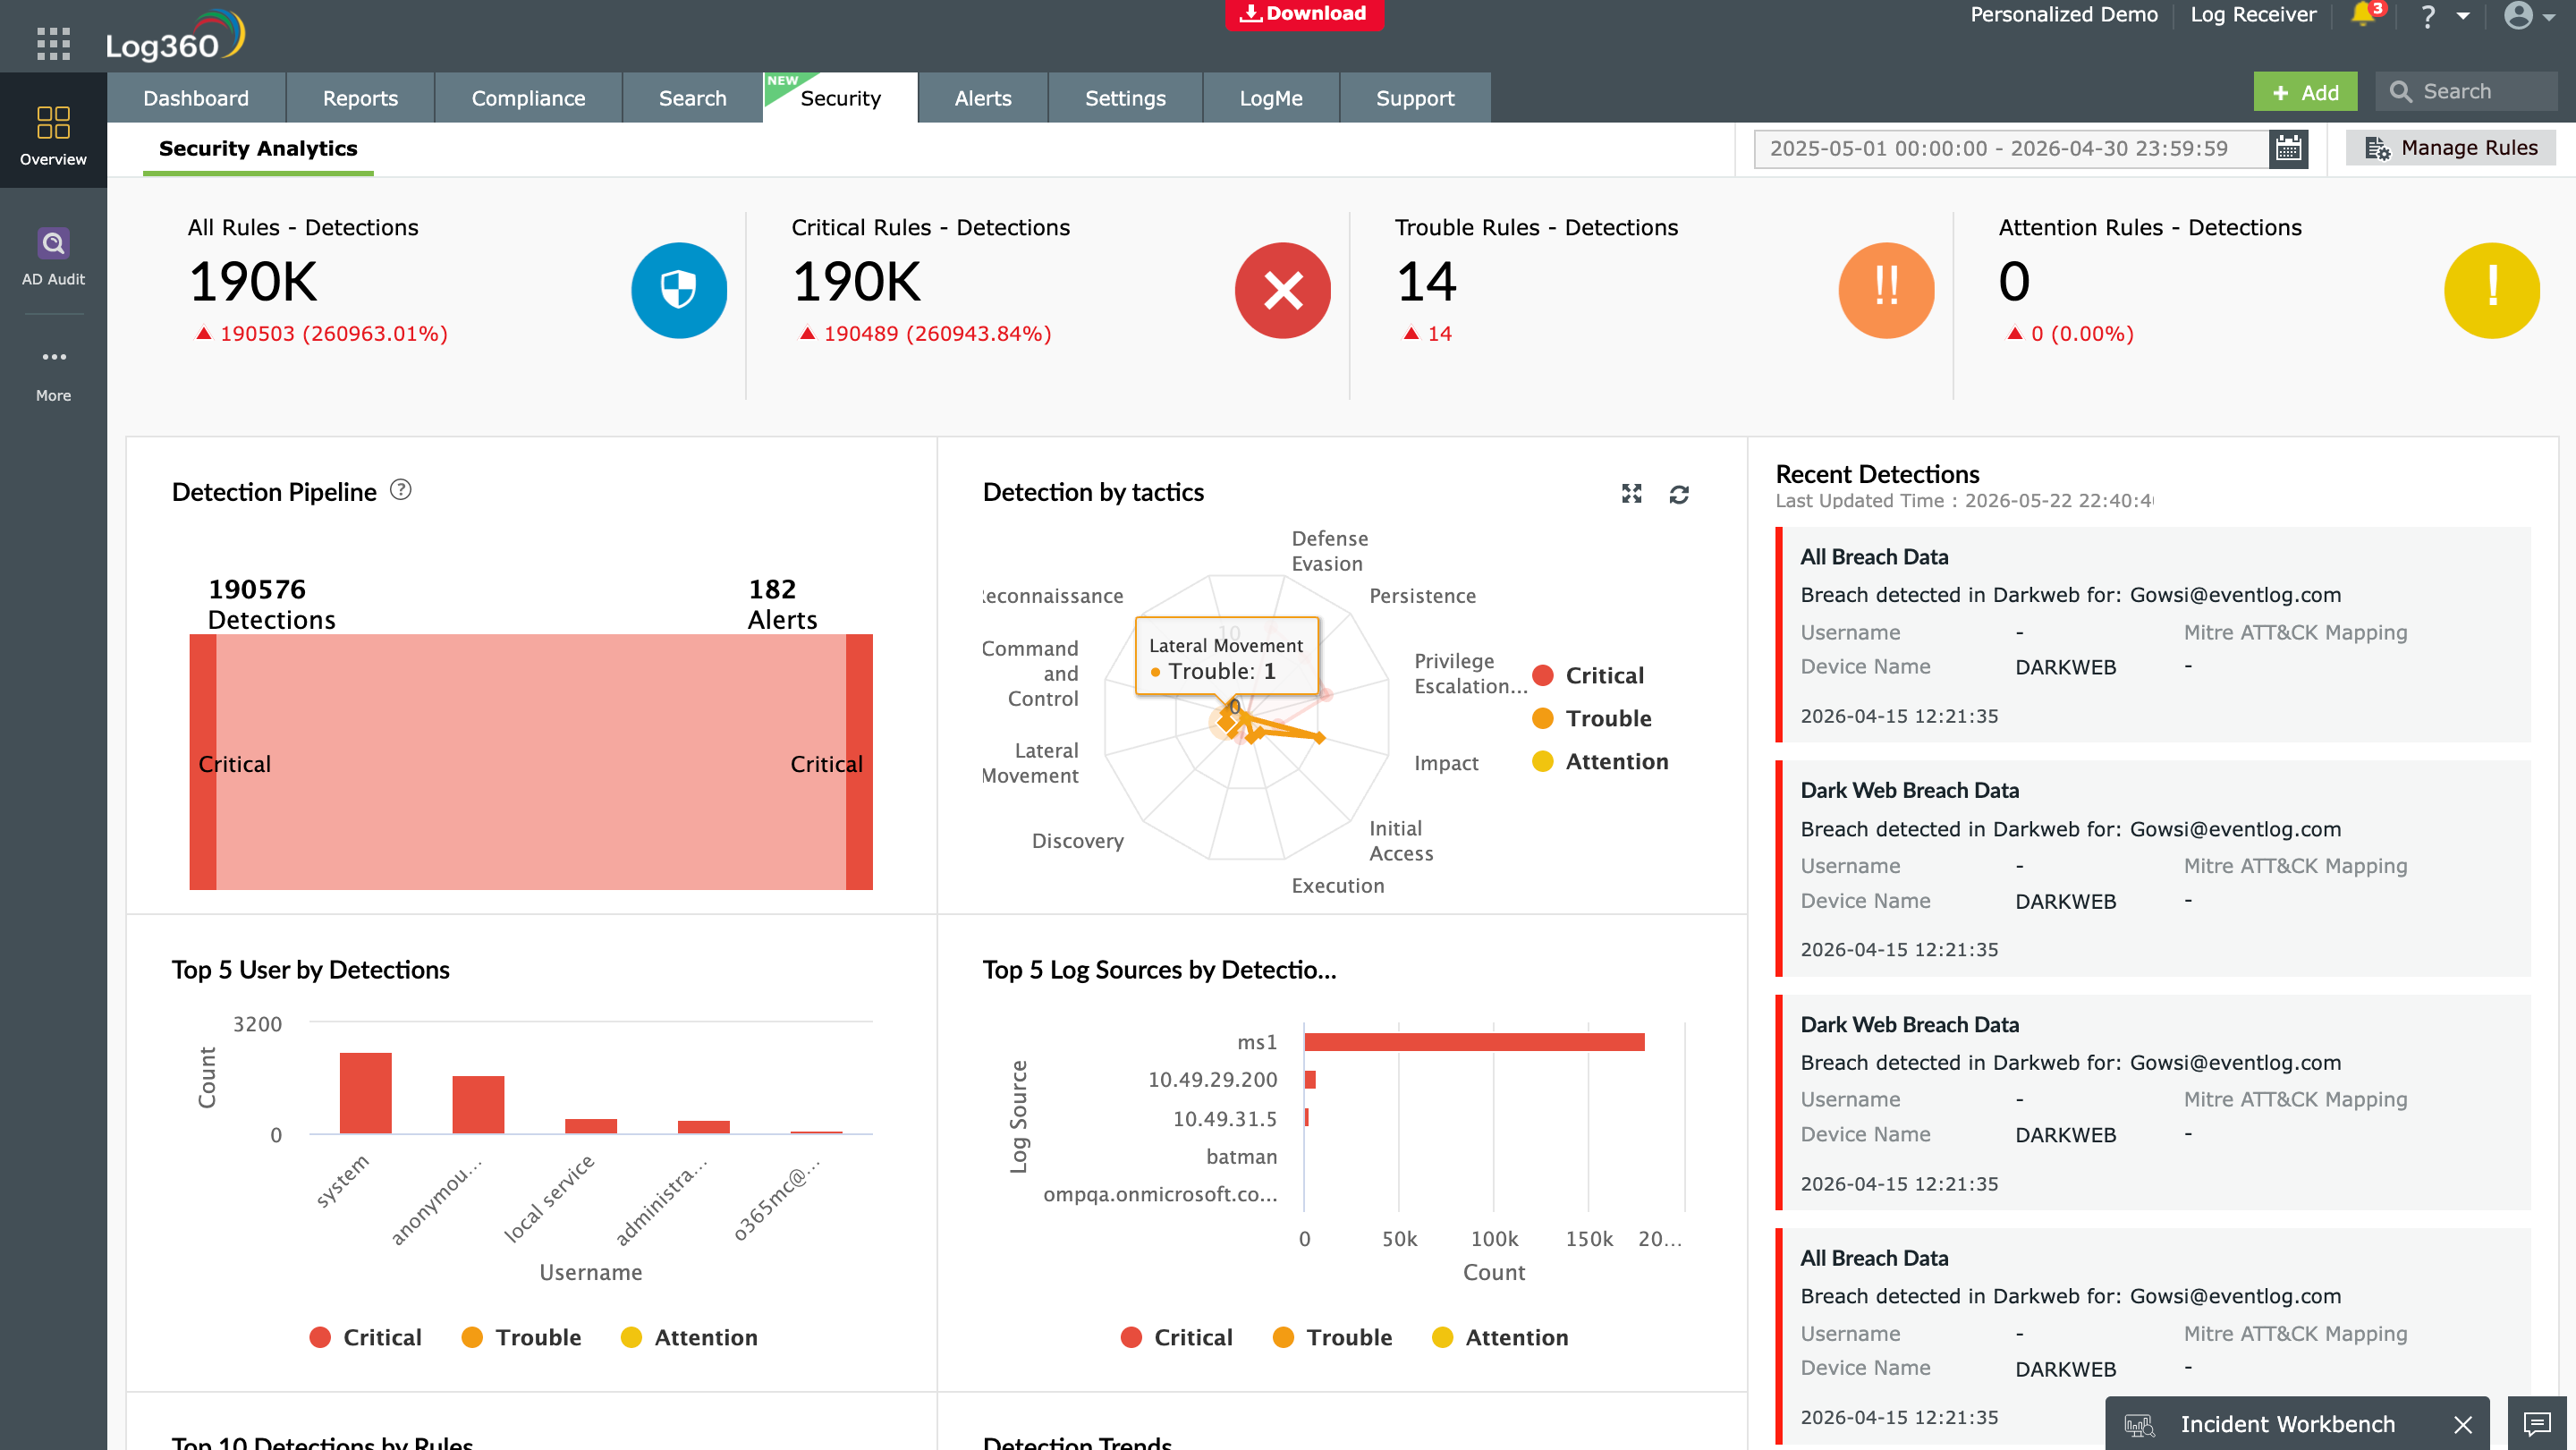
Screenshot of Security Analytics Dashboard: Provides a centralized view of security events, threat trends, attack severity, and MITRE ATT&CK mapped detections to help SOC teams monitor threats in real time.
Screenshot of Dark Web Monitoring: Detects compromised credentials and exposed assets using dark web intelligence feeds.
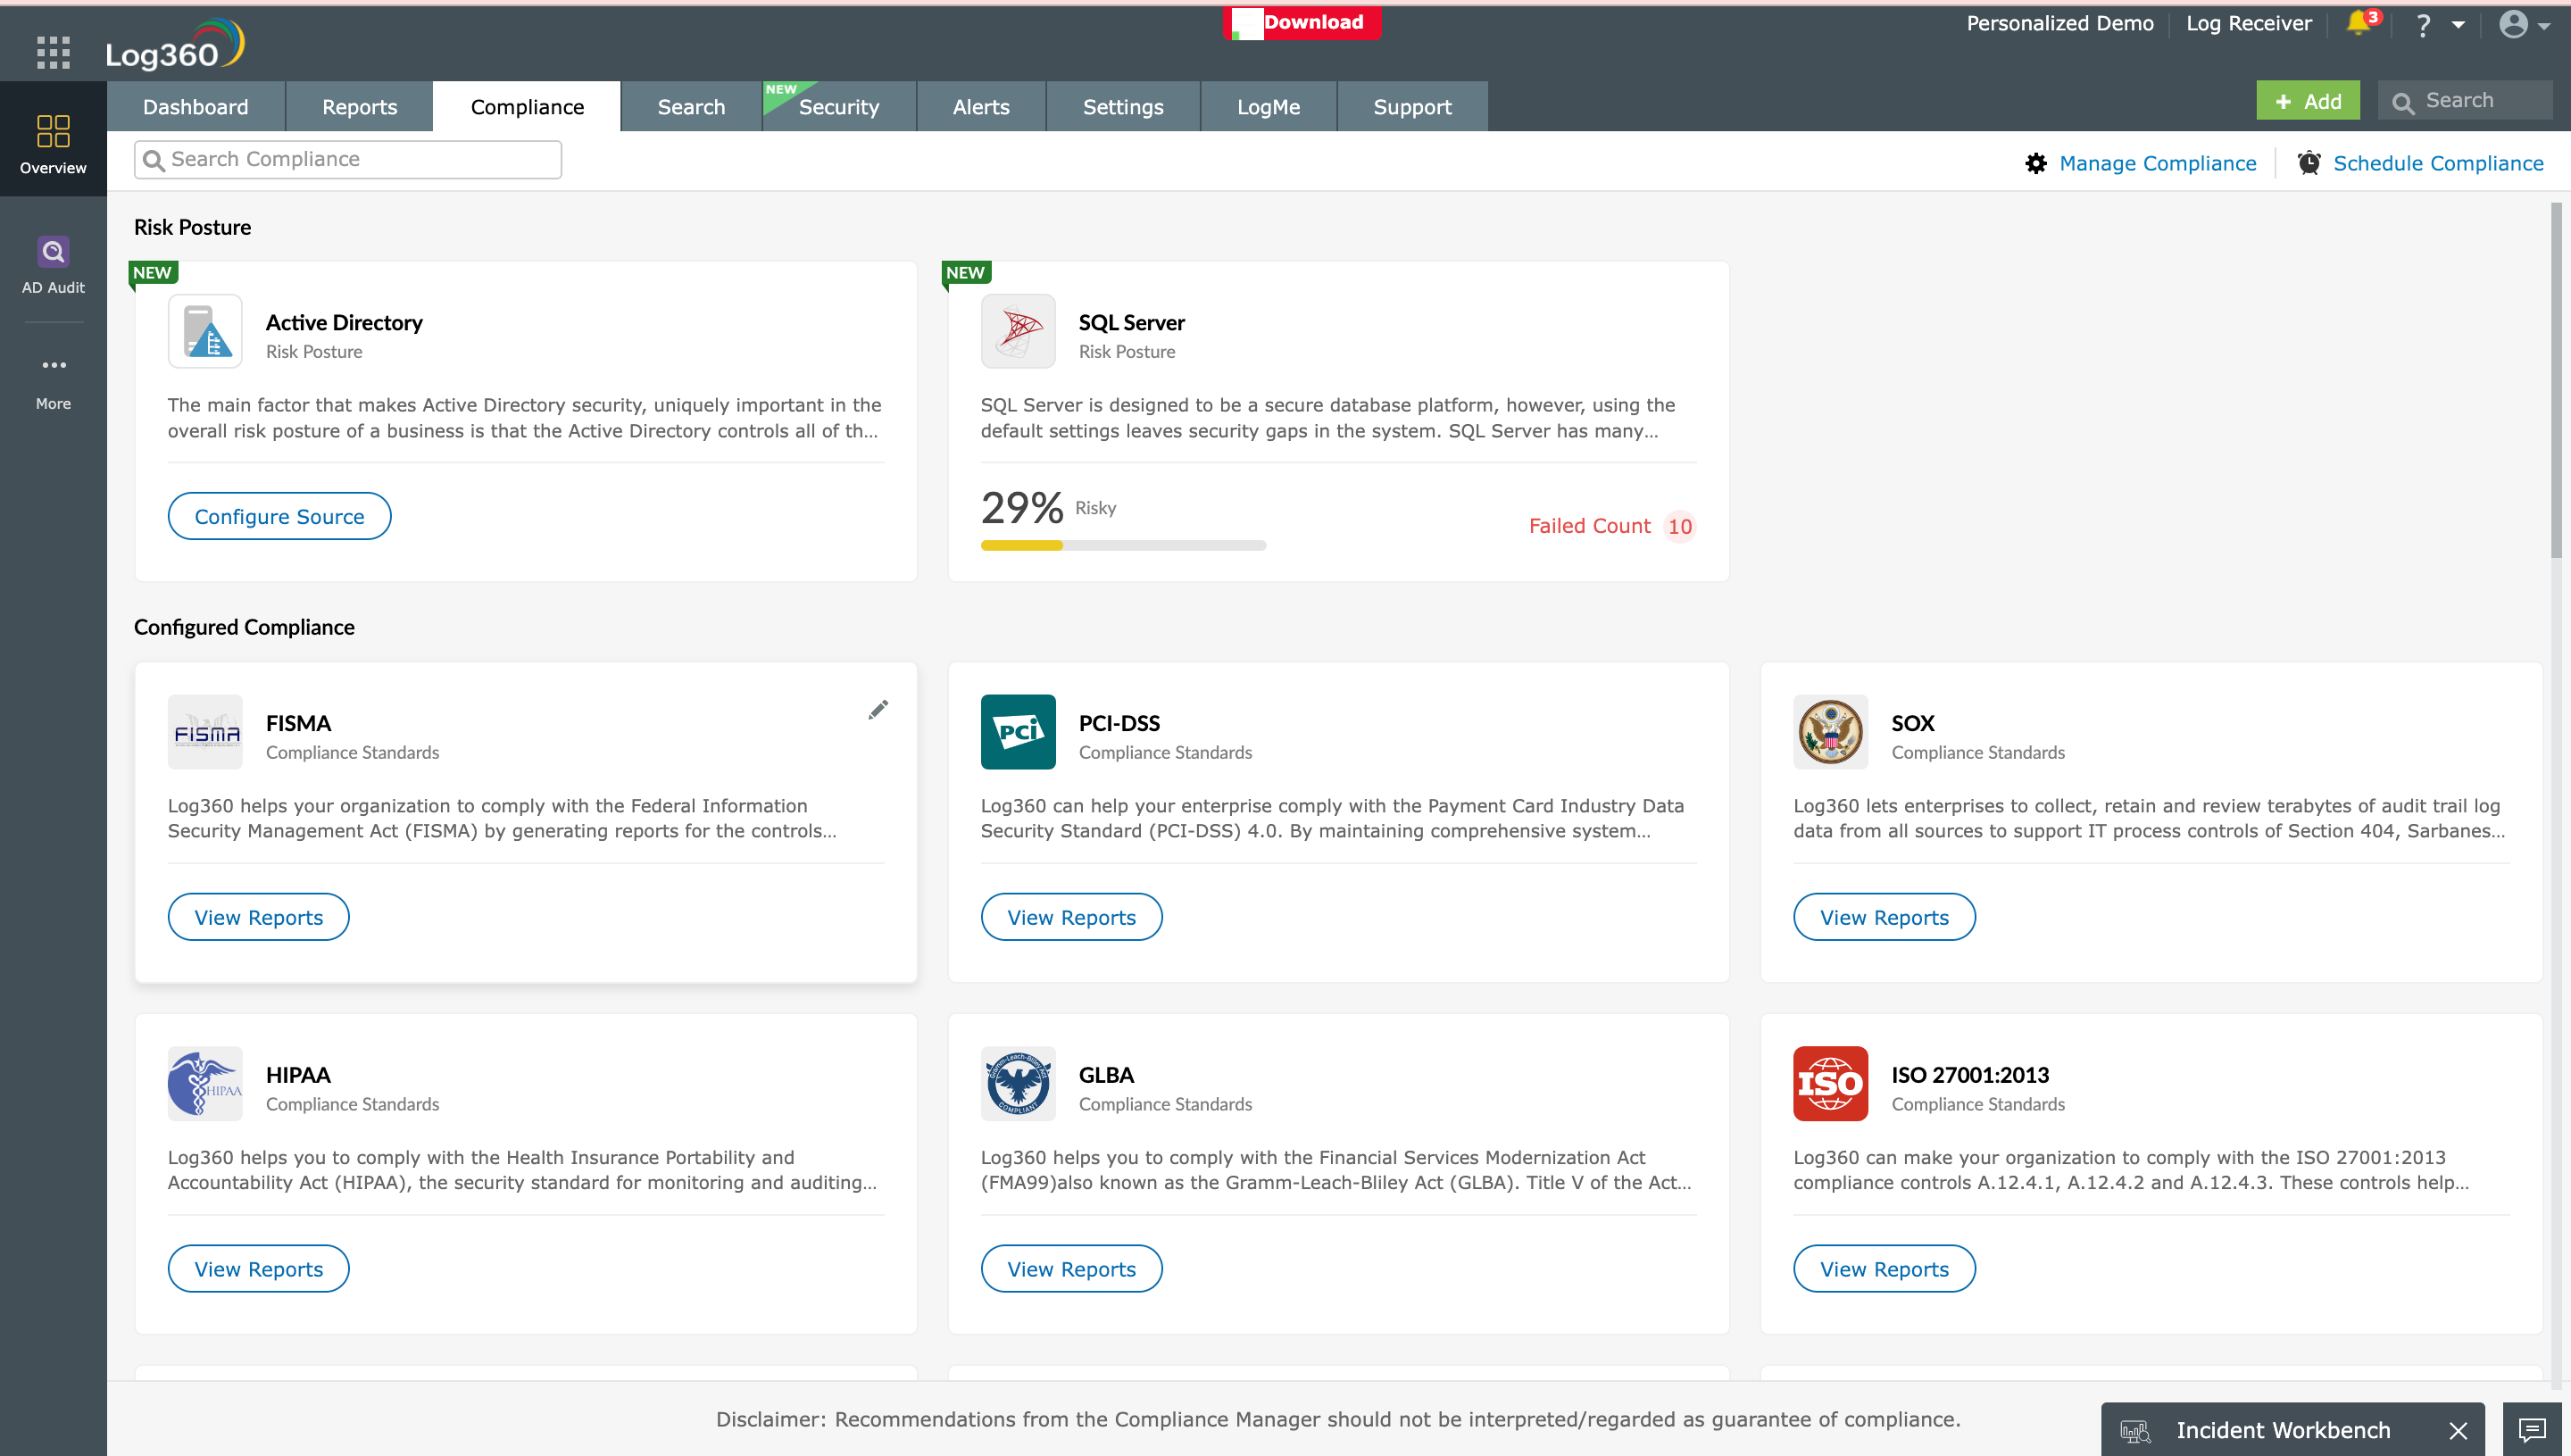
Screenshot of Compliance Reporting: Provides audit-ready reports and predefined templates for standards such as PCI DSS, HIPAA, GDPR, ISO 27001, SOX, and more.
Screenshot of Forensic Search and Log Search: Allows security teams to perform advanced log searches, event filtering, and forensic investigations across collected data sources.
Screenshot of Real-Time Alert Console: Monitor security events as they happen with a real-time alert console that displays triggered alerts with severity levels, assigned risk scores, and MITRE ATT&CK technique mappings for immediate context.
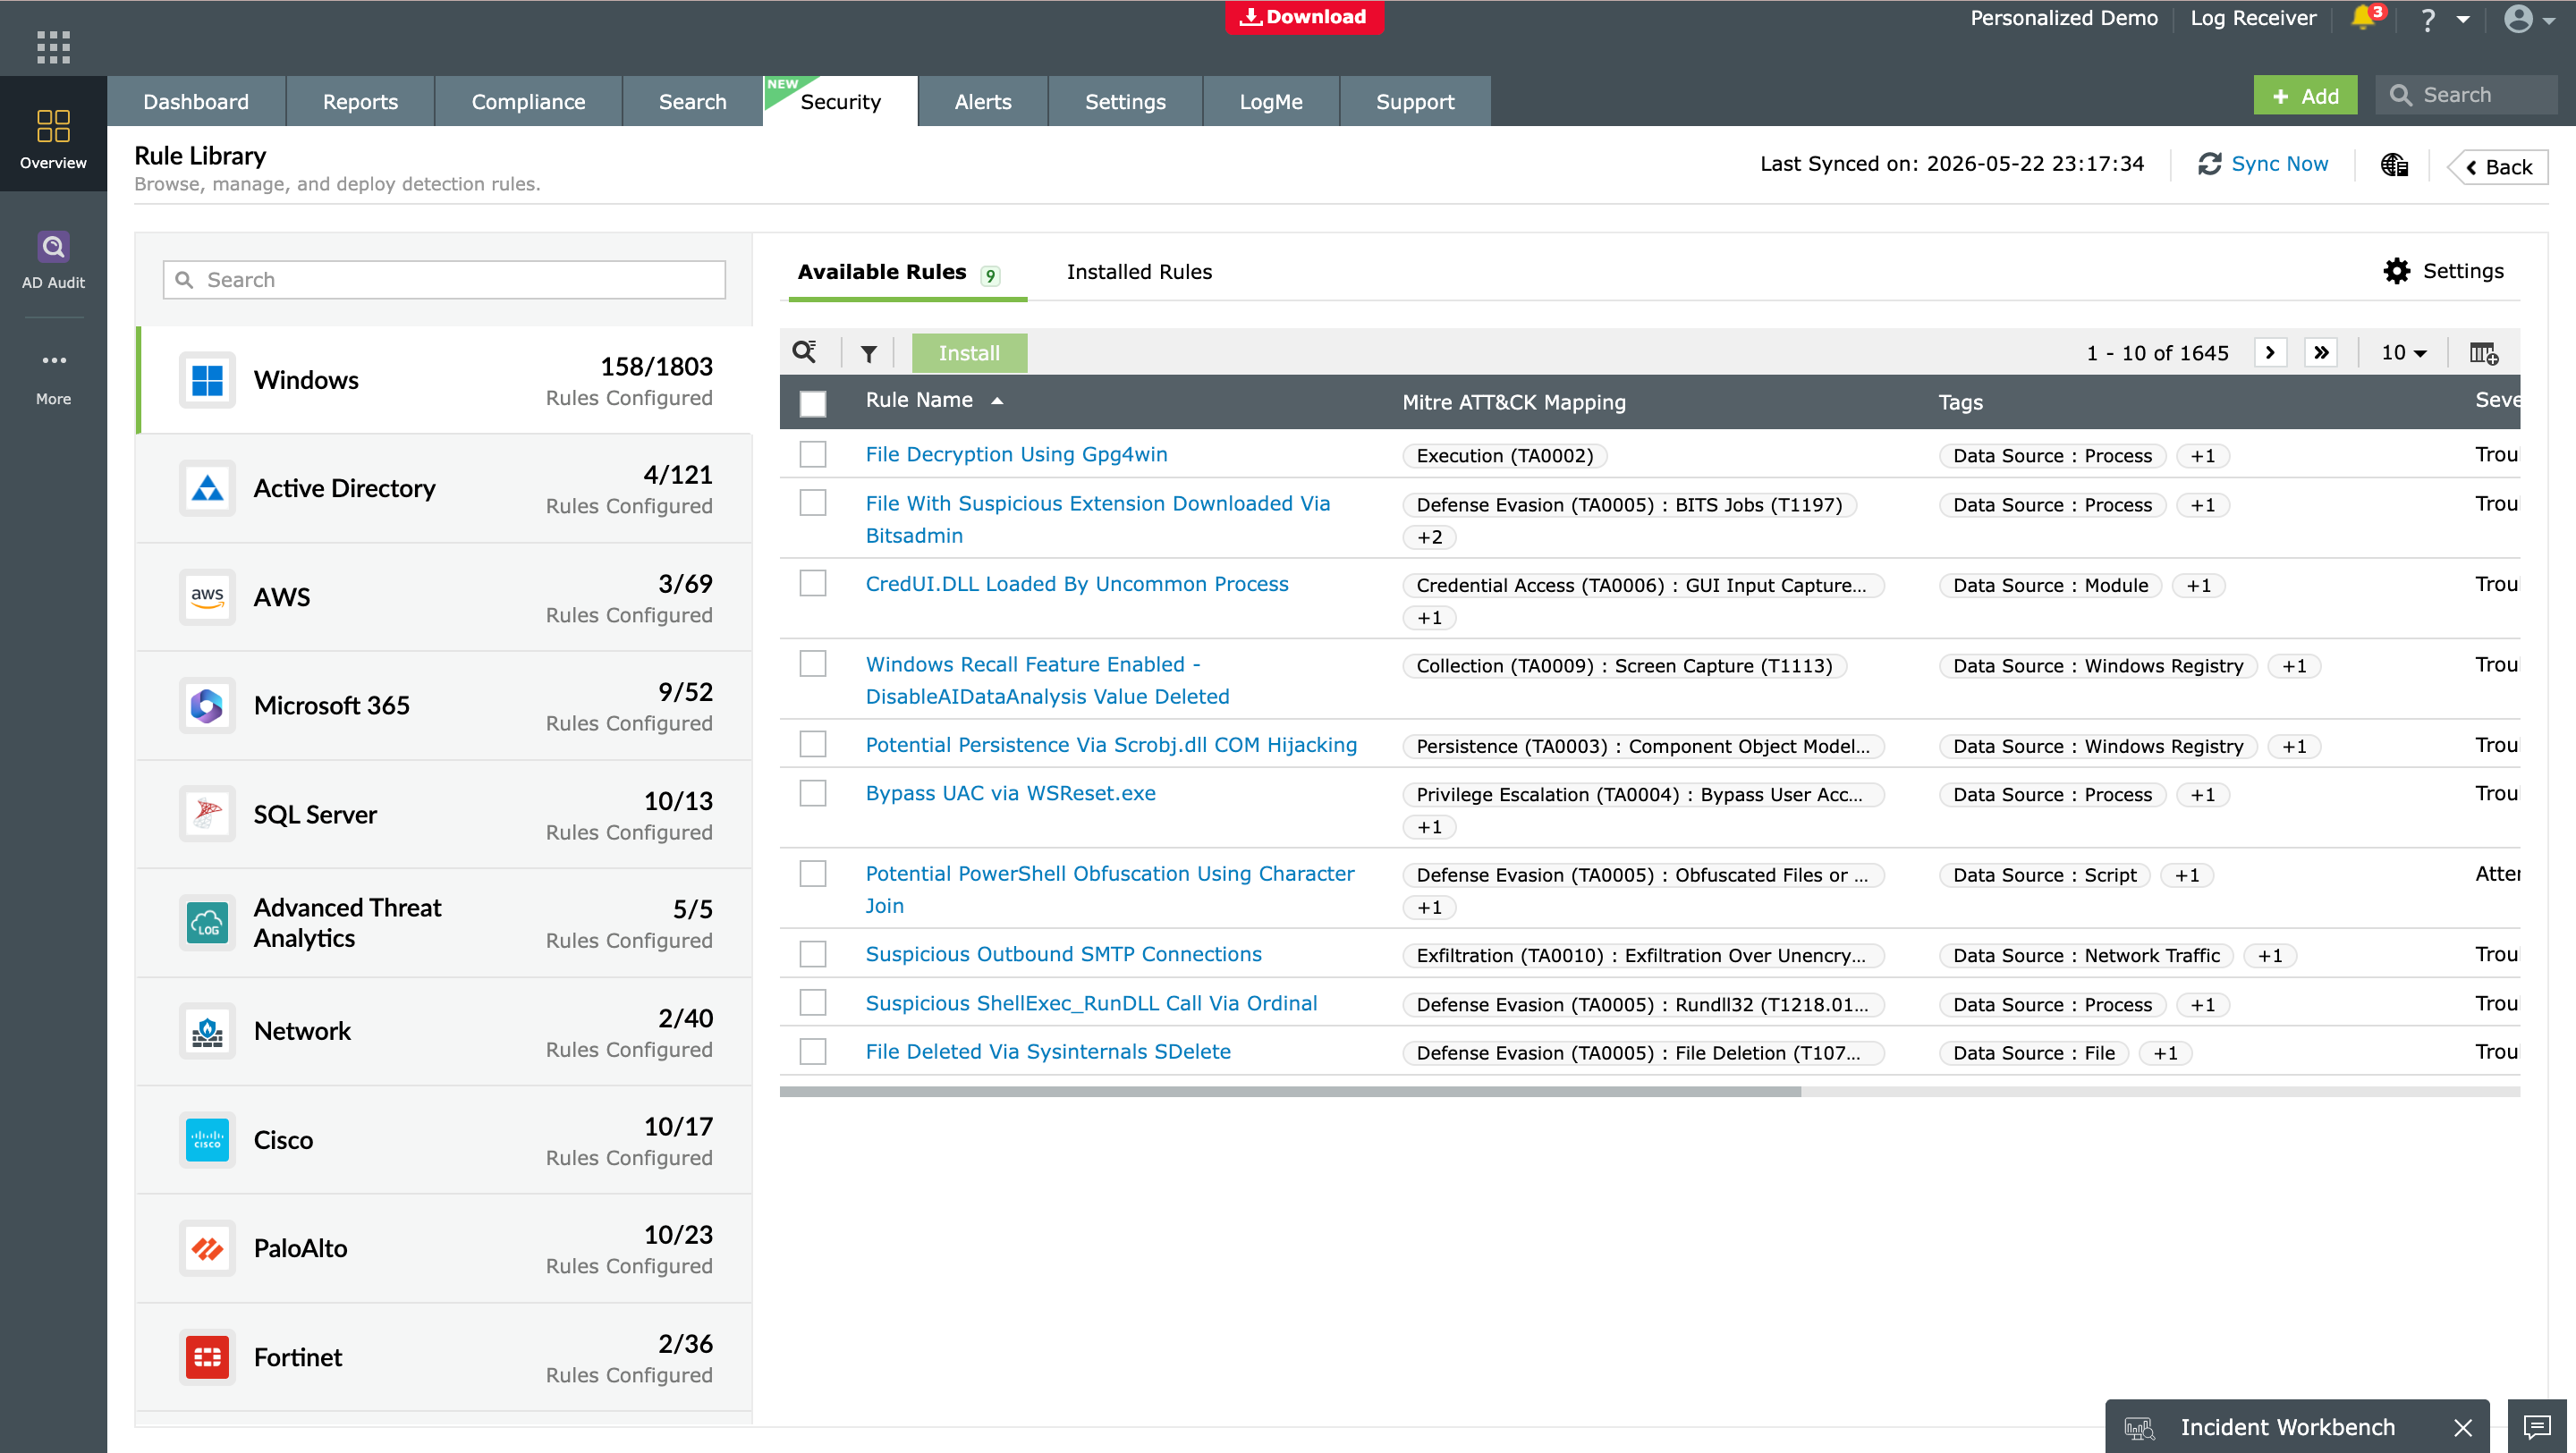
Screenshot of Rule Library: Includes 2,000+ predefined detection rules for identifying threats, anomalies, and suspicious activities.

1 / 6

Screenshot of Security Analytics Dashboard: Provides a centralized view of security events, threat trends, attack severity, and MITRE ATT&CK mapped detections to help SOC teams monitor threats in real time.

Top Performing Features

  • Centralized event and log data collection

    Effectiveness of real-time centralized event and log data collection

    Category average: 8.9

  • Behavioral analytics and baselining

    How effectively activity and behavior baselines are established and maintained

    Category average: 8.6

  • Response orchestration and automation

    Quality of built-in response orchestration and automation in Next-Gen SIEM

    Category average: 8.4

Areas for Improvement

  • Event and log normalization/management

    Ability to normalize event syntax so that logs can be compared and are machine-understandable

    Category average: 8.7

  • Data integration/API management

    Ease and quality of data integrations between SIEM and other systems

    Category average: 8.3

  • Correlation

    Correlation of logs and events to pinpoint significant threats

    Category average: 8.4

ManageEngine Log360 Best for Small Business Where ISO 27001 is Required

Use Cases and Deployment Scope

We have been using ManageEngine Log360 Cloud for the last 3 years. We started using this tool to comply with our audit requirements, specifically ISO 27001: 2022.
It covers our Centralized Logging solution, Threat detection, Compliance reporting, and alerting for our on-prem data center devices.
Support of this platform help to configure our initail requirement and now we can manage by our self because interface of the application is user friendly. We are facing some challenges with custom reporting to get specific time and date logs.

Pros

  • Centralized logging for on-prem Devices like switches, Windows servers, and Linux machines.
  • Compliance reporting specifically for ISO-required controls.
  • Therate detection is a very useful feature that provides valuable information.

Cons

  • Integration with other Security software so we can get all reports and alerts on one platform, like integration with Antivirus Endpoint solutions
  • Custom log search needs some improvement and needs to update the search web page with some graphical controls.

Return on Investment

  • We achieved our business requirement with this product, so it is highly recommended for a small setup. Most of the team work is coverd by this tool

Usability

Alternatives Considered

Datadog

Other Software Used

Datadog, MontyCloud DAY2