TrustRadius: an HG Insights company

What is Venvera?

Venvera is a cloud-based Governance, Risk & Compliance platform developed by Atlant Security that automates regulatory compliance, cross-framework control mapping, and risk management for organizations operating under complex regulatory mandates.

Read more details.

Media

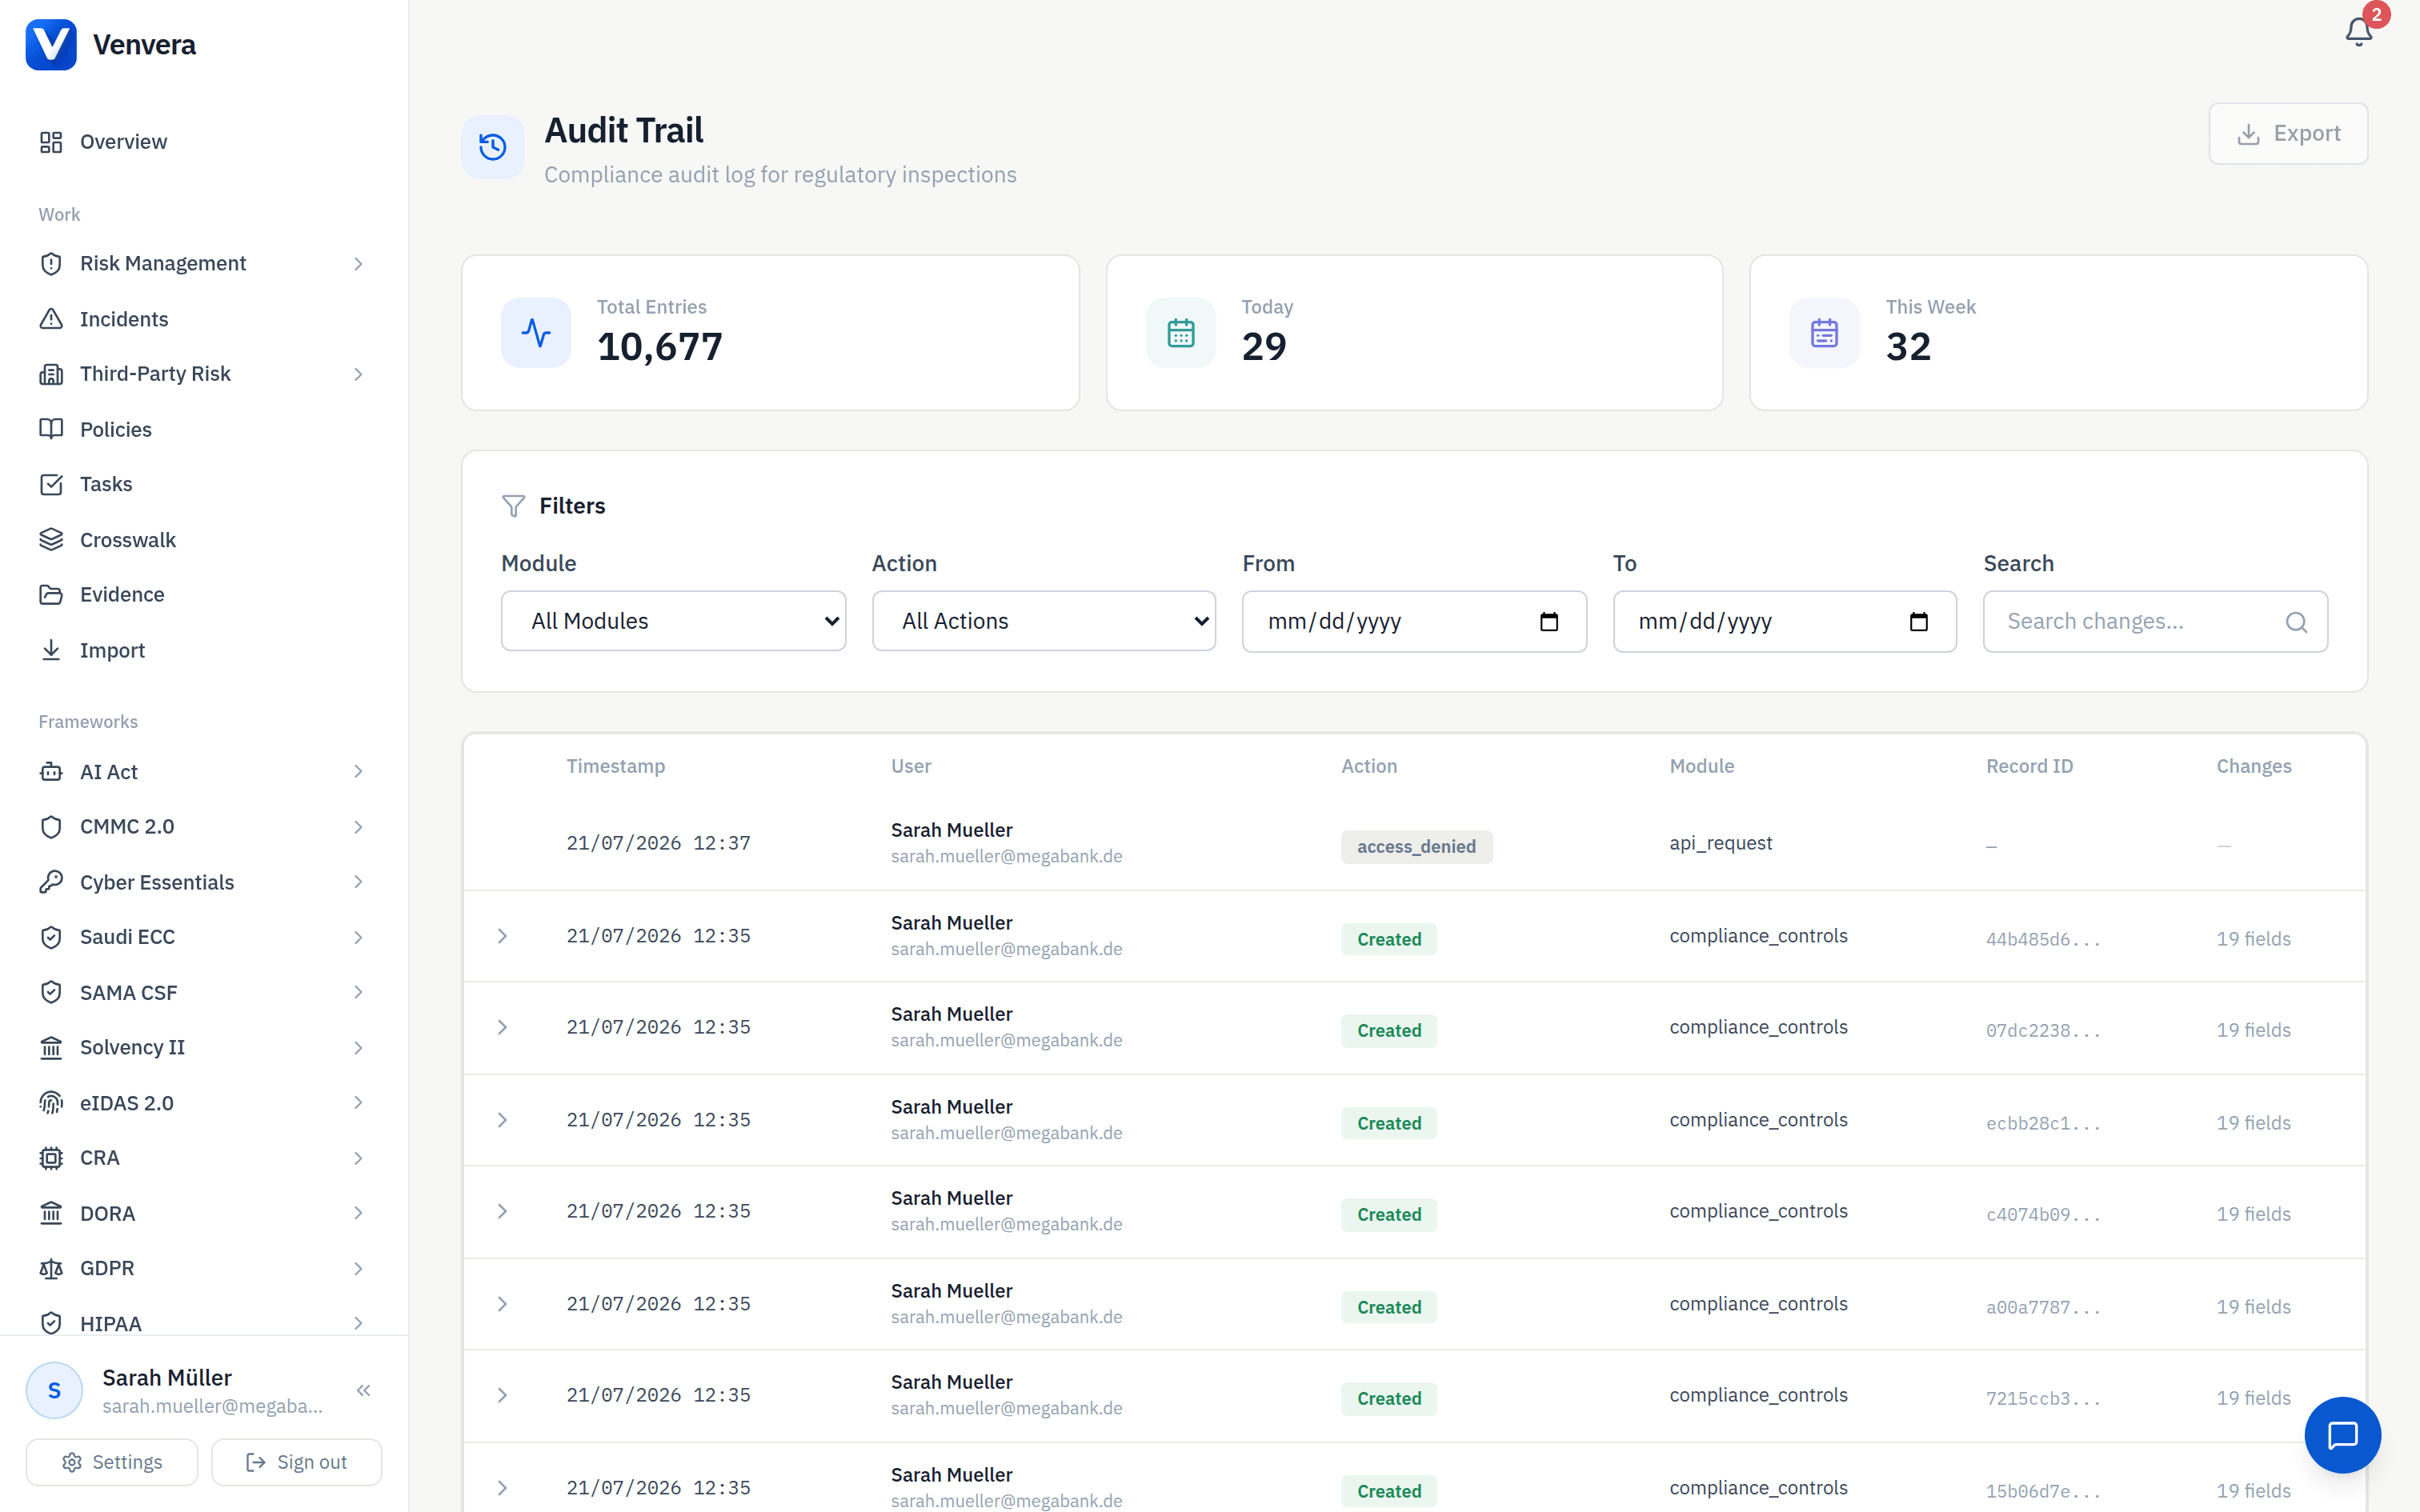
Screenshot of Compliance officers get a tamper-evident, filterable log of every platform action — 10,677 entries spanning all modules — so regulators and auditors see exactly who did what and when. Exportable for DORA, GDPR, and ISO 27001 inspections.
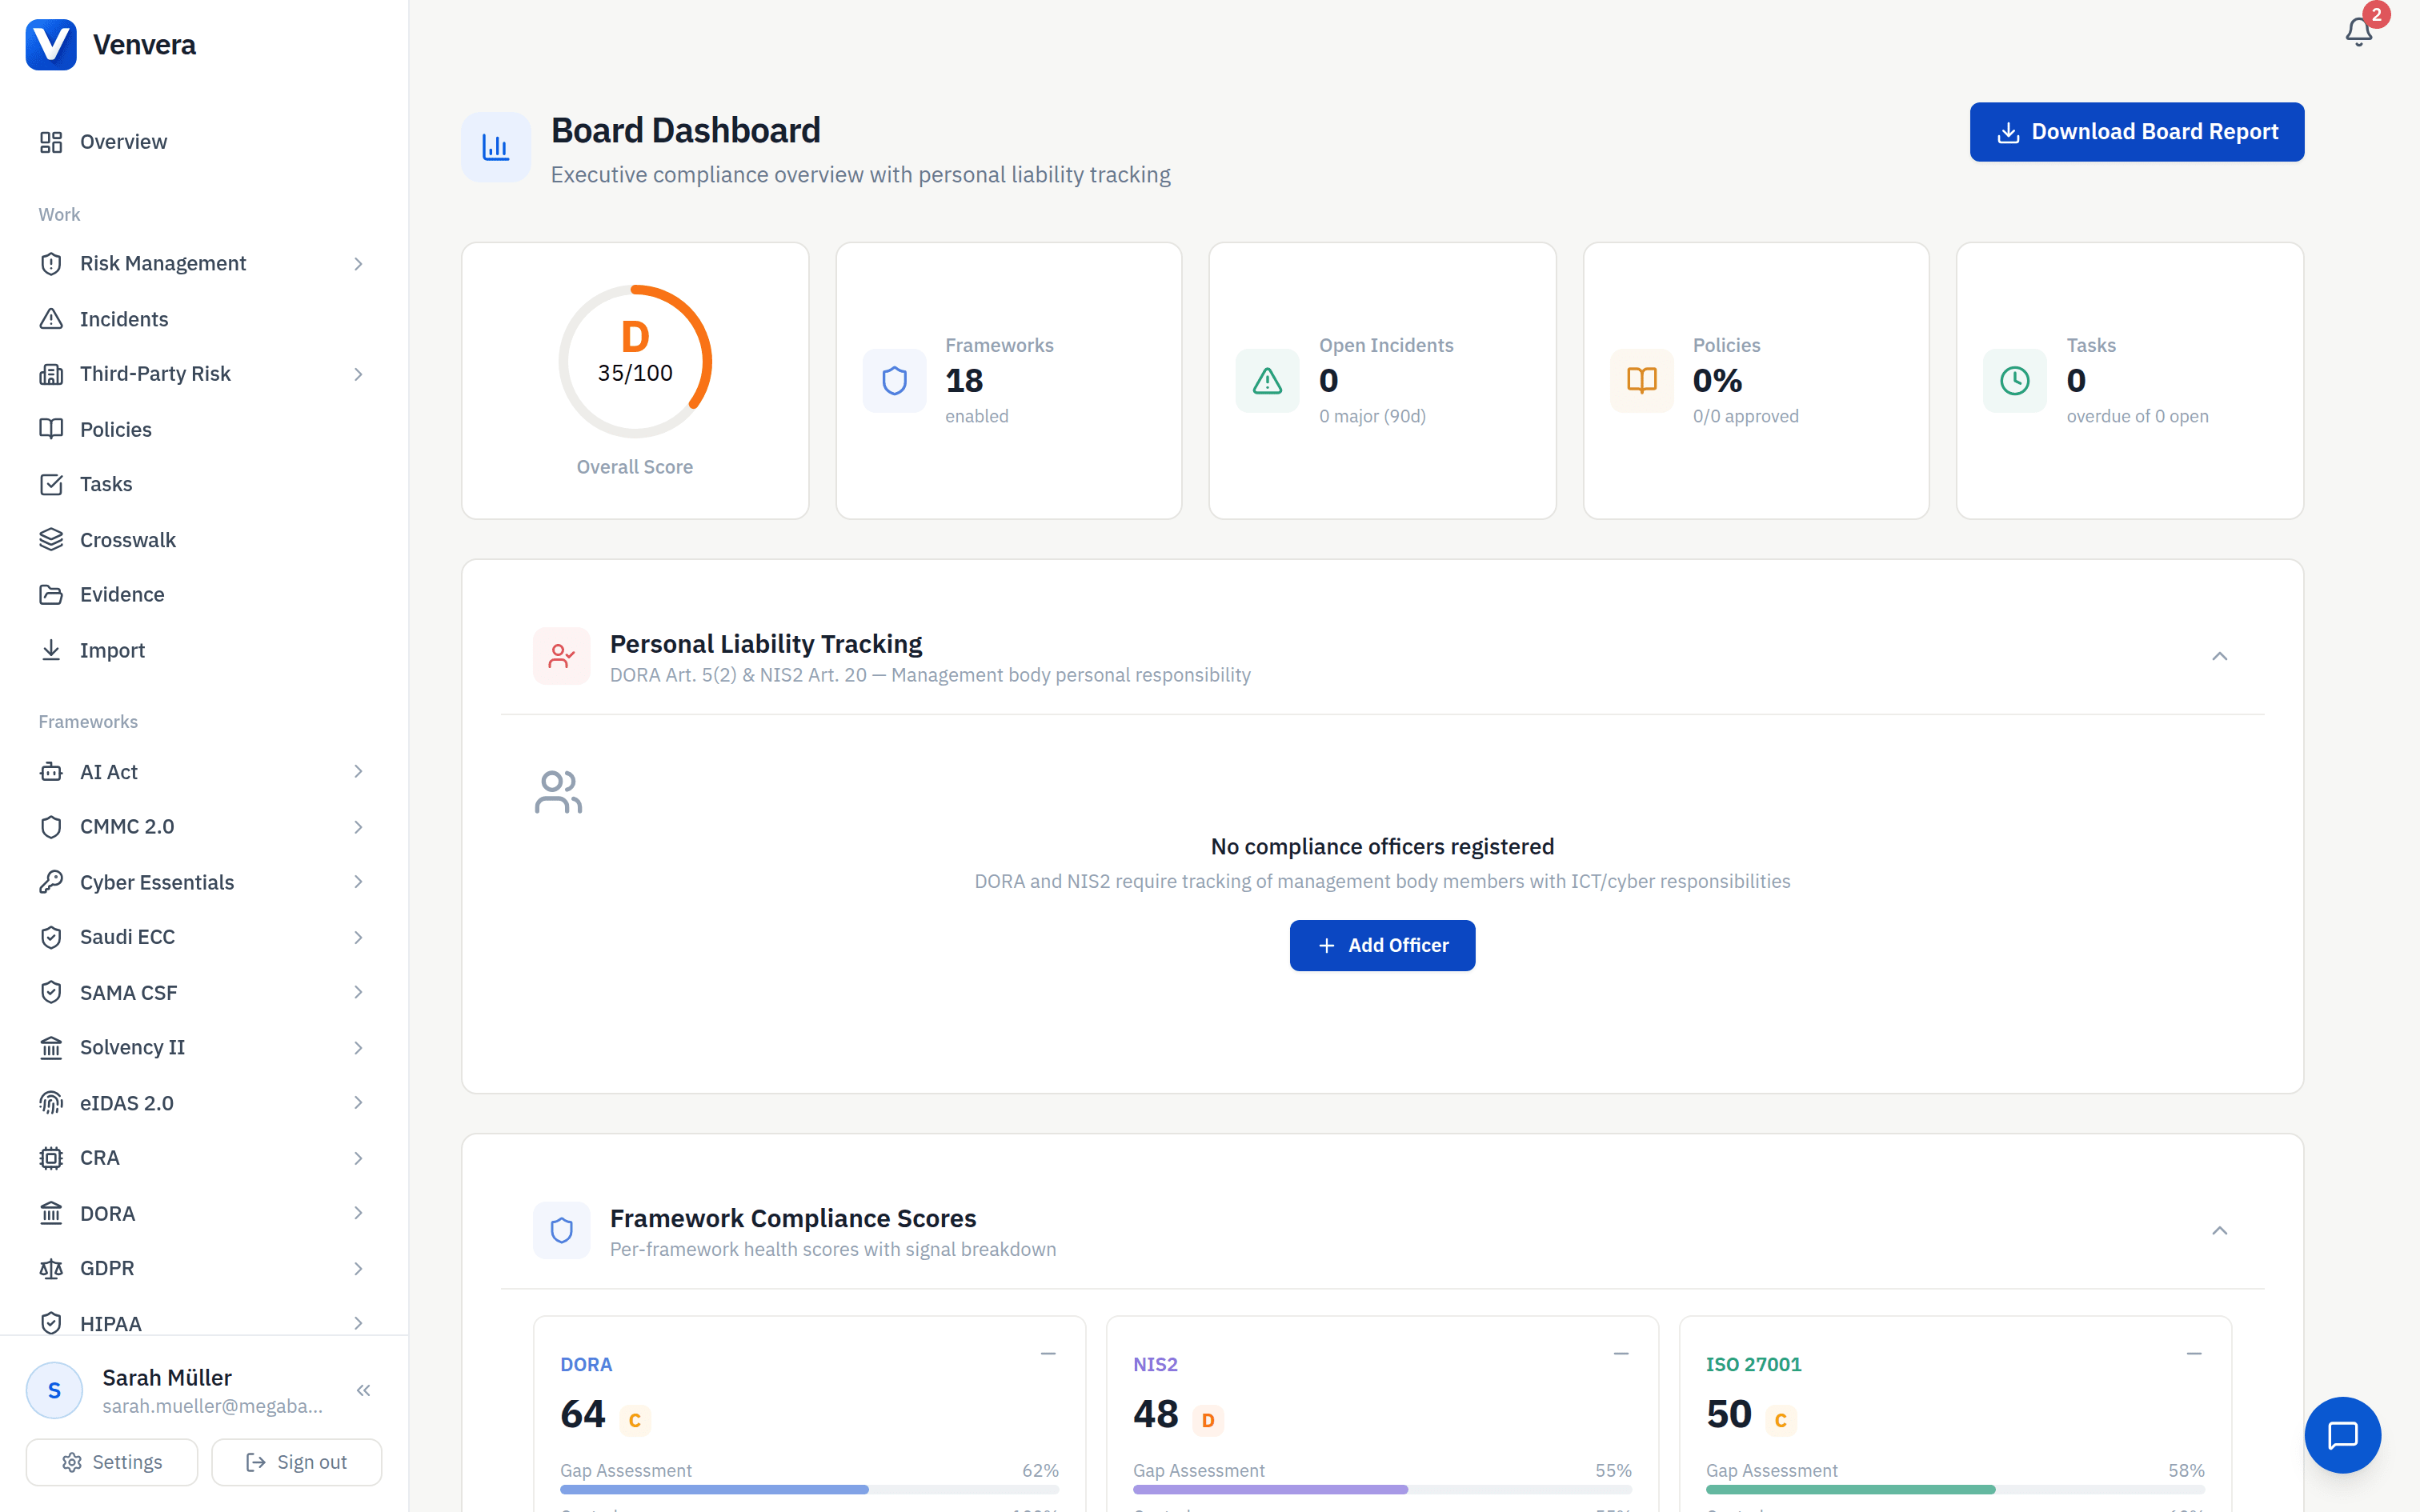
Screenshot of Boards and CISOs get an at-a-glance compliance posture — overall score, active frameworks, open incidents, and per-framework health scores for DORA, NIS2, and ISO 27001 — plus personal liability tracking mapped to DORA Art. 5(2) and NIS2 Art. 20. A one-click export delivers a board-ready PDF report from live data.
Screenshot of Compliance teams see exactly where one control satisfies many frameworks at once: per-framework scores (DORA at 83%, NDPA at 79%) sit alongside a domain-level matrix showing compliant, partial, and gap status across 17 frameworks simultaneously. Six gap domains become the day's priority list.
Screenshot of Compliance officers see their posture across 18 active frameworks at a glance — from DORA and NIS2 to HIPAA and CMMC — with per-framework scores and gap-assessment percentages surfaced instantly. Teams can spot which frameworks need urgent attention and drill into any dashboard to act, without switching tools.
Screenshot of Compliance teams track every open incident against DORA ITS deadlines — initial notification (4h), intermediate report (24h), and final report (72h) — with overdue timelines flagged inline. Major incidents like AML service degradation surface a "72h OVERDUE" alert instantly, so regulators are never missed.
Screenshot of Risk managers see residual ratings, control effectiveness, and inherent-vs-residual shift side by side, so they can prove to auditors that 48 active risks are covered and that severe exposure has been driven to zero. KRI RAG status and 6-month trend sit below, turning the dashboard into a live brief for the board.

1 / 6

Screenshot of Compliance officers get a tamper-evident, filterable log of every platform action — 10,677 entries spanning all modules — so regulators and auditors see exactly who did what and when. Exportable for DORA, GDPR, and ISO 27001 inspections.