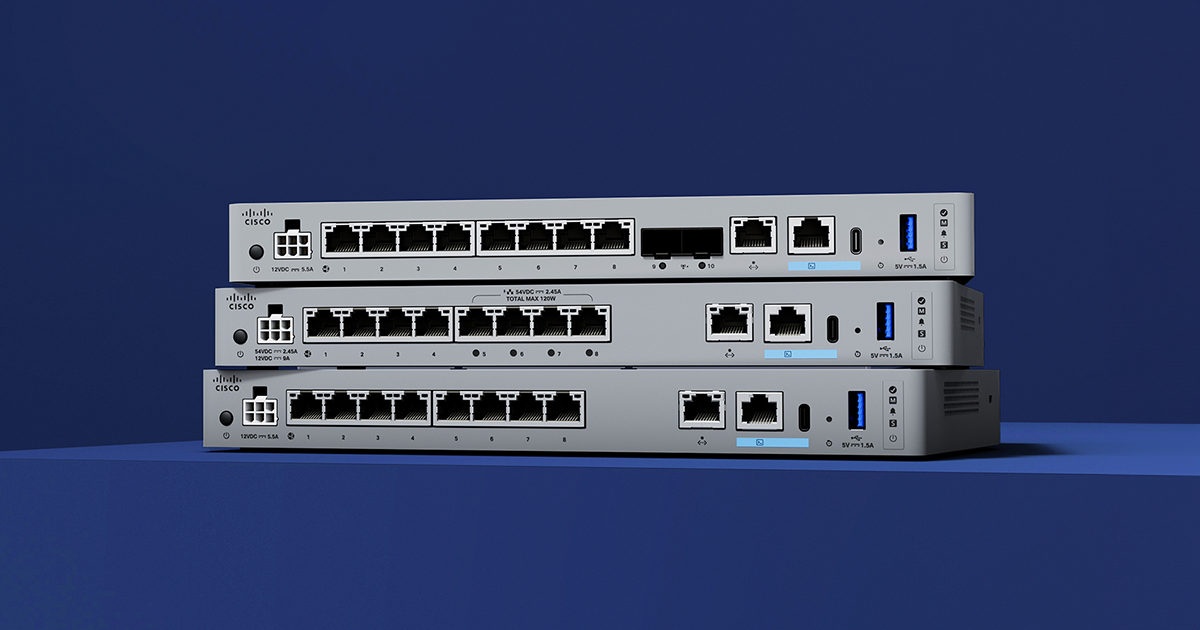
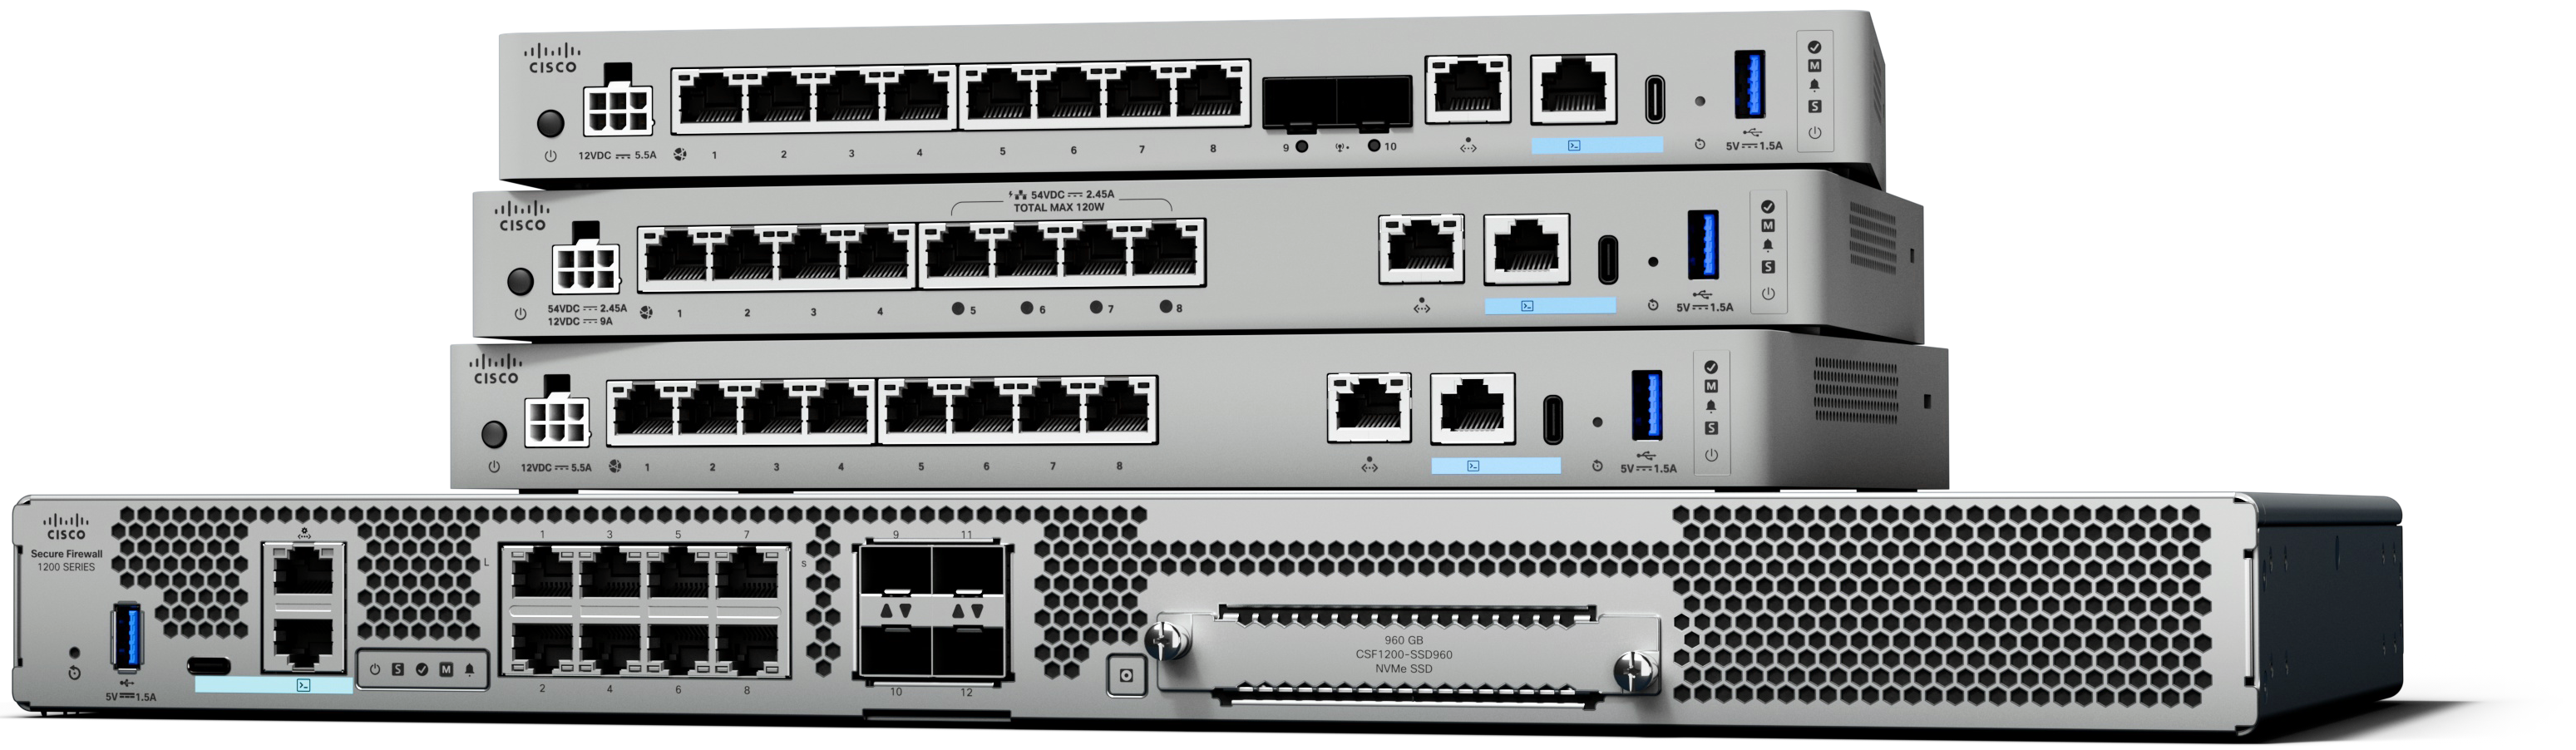
Cisco's Catalyst is one of that company's brand of network switches.
N/A
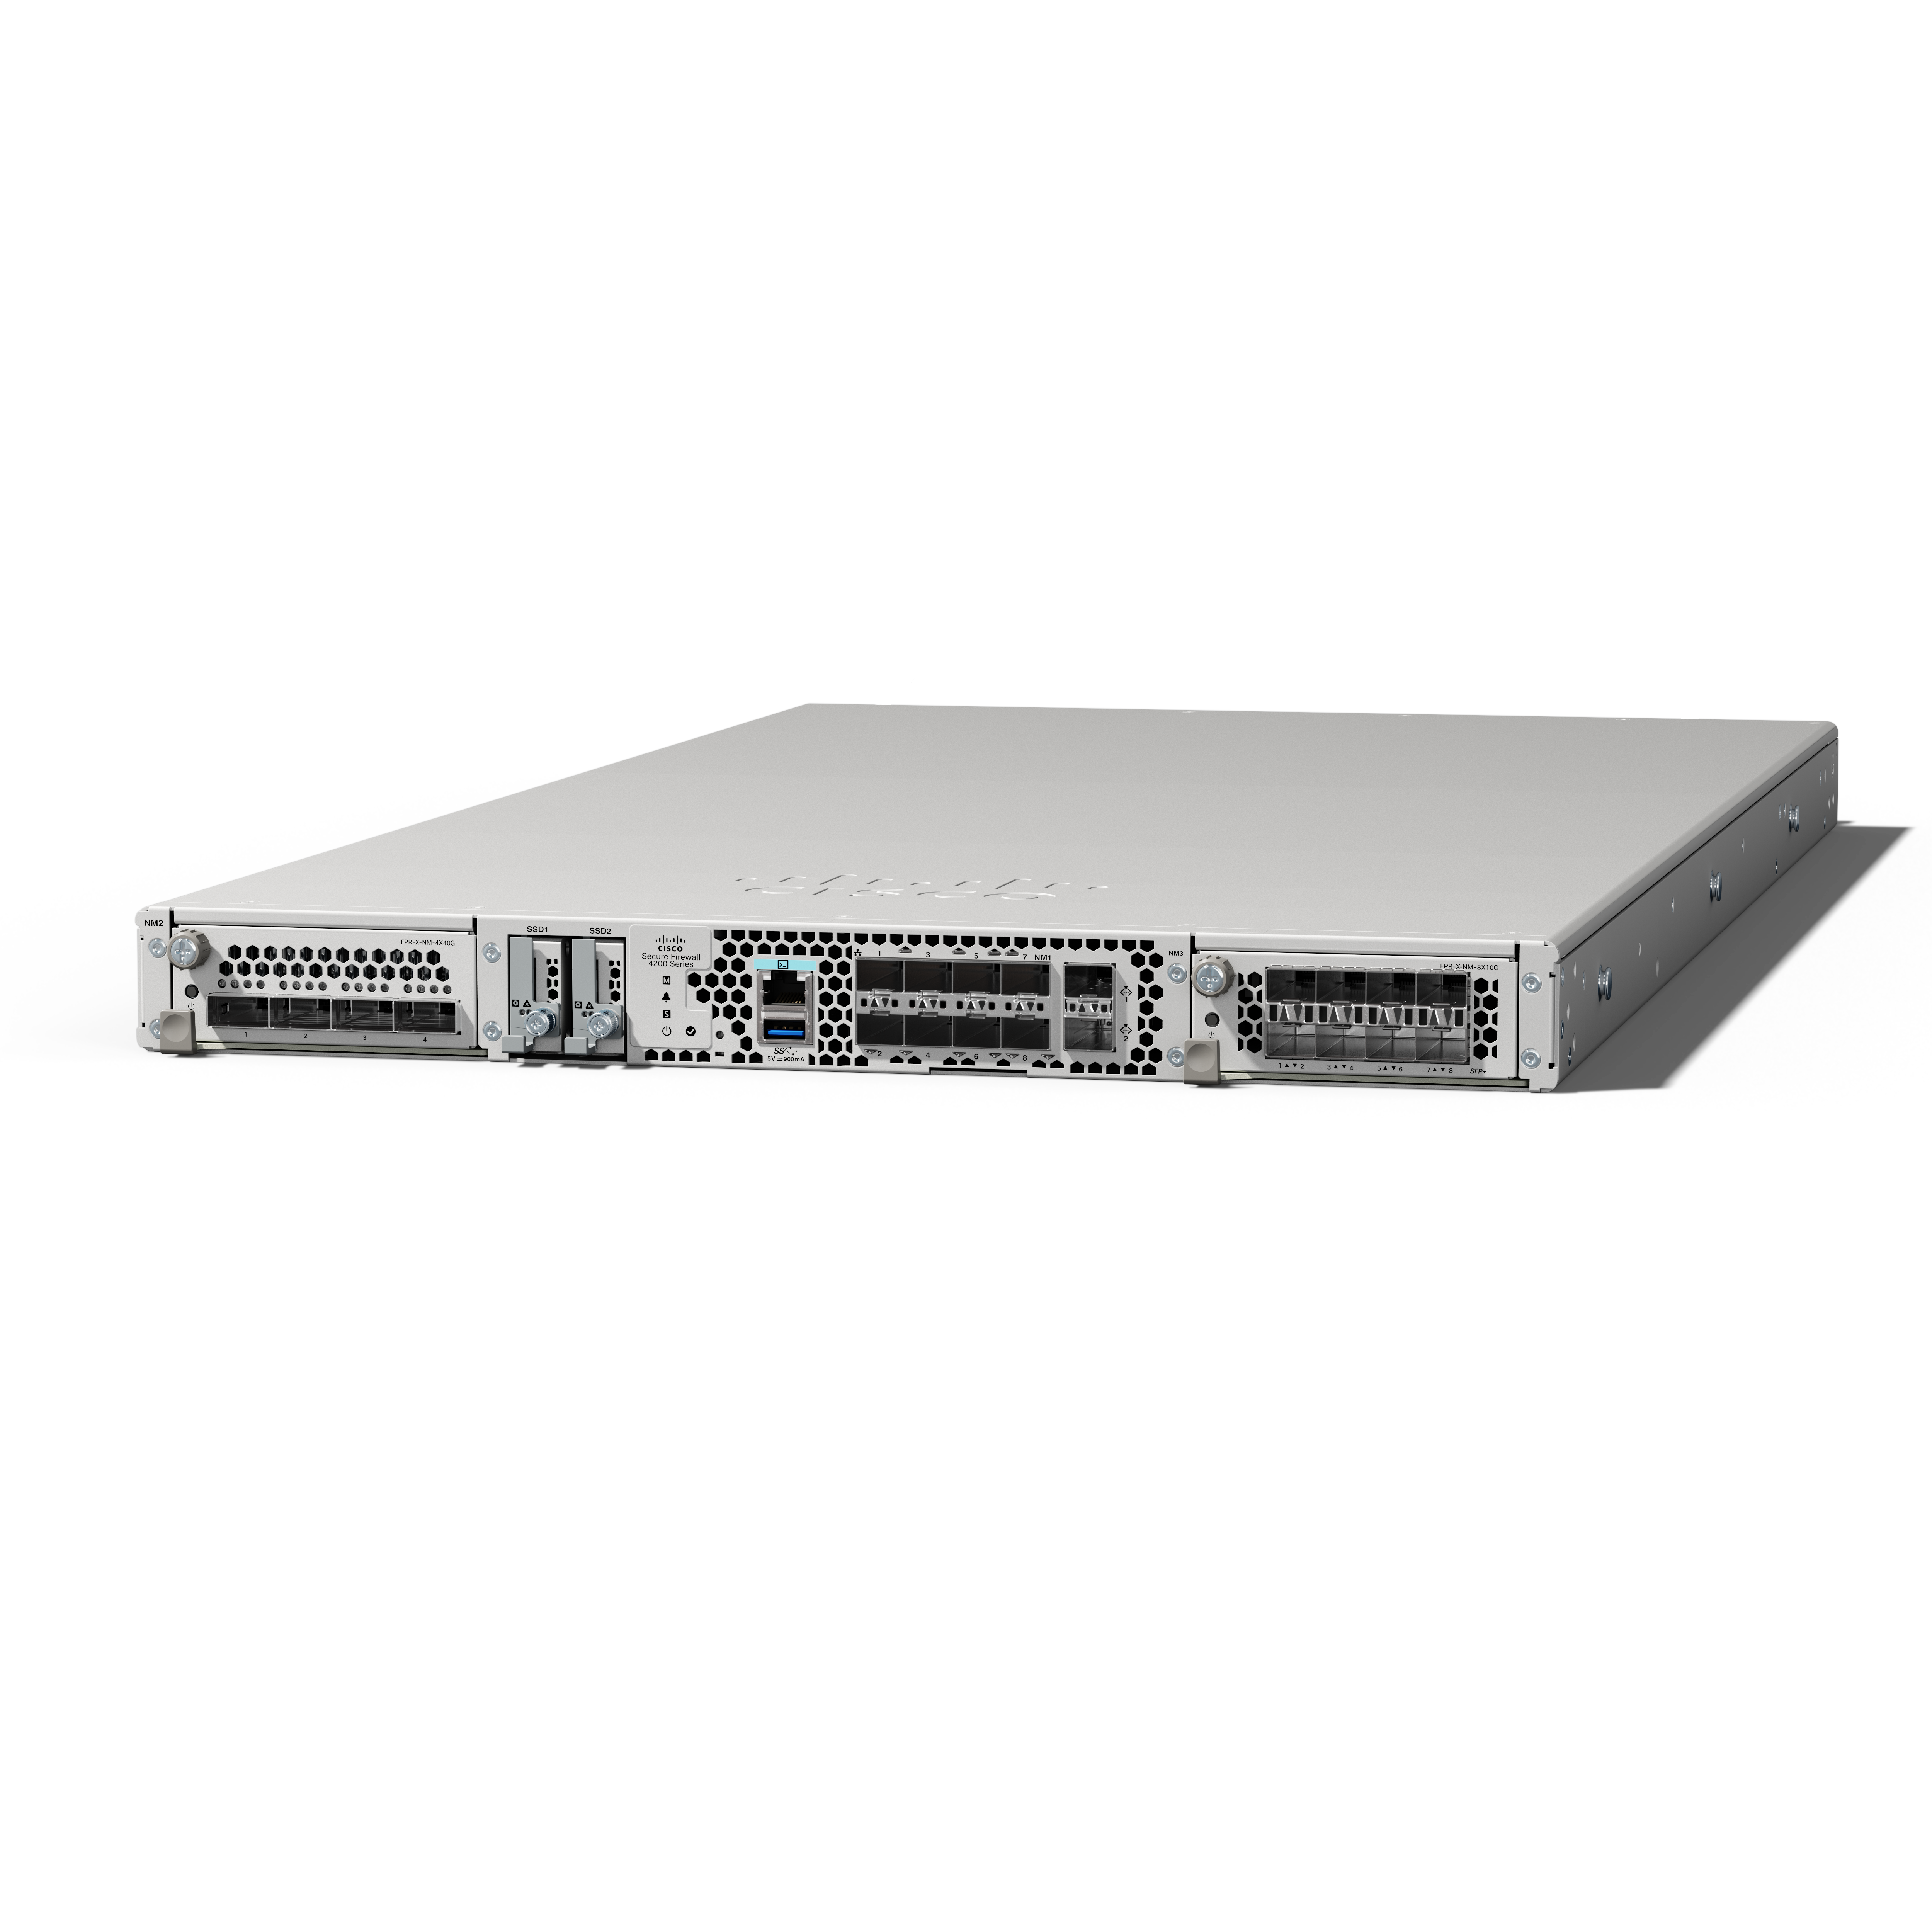
Cisco Secure Firewall
Score8.4 out of 10
N/A
Cisco Secure Firewall delivers comprehensive threat protection for modern, distributed networks. Built to support hybrid workforces and multicloud environments, it enables Zero Trust access, application visibility, and secure remote connectivity. With integration across the Cisco Secure portfolio, including SecureX and Talos threat intelligence, the firewall powers organizations to detect and stop more sophisticated threats. Centralized management simplifies policy enforcement, orchestration,…
N/A
pfSense
Score8.5 out of 10
N/A
pfSense is a firewall and load management product available through the open source pfSense Community Edition, as well as a the licensed edition, pfSense Plus (formerly known as pfSense Enterprise). The solution provides combined firewall, VPN, and router functionality, and can be deployed through the cloud (AWS or Azure), or on-premises with a Netgate appliance. It as scalable capacities, with functionality for SMBs. As a firewall, pfSense offers Stateful packet inspection, concurrent…
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco
Verified User
Chose Cisco Secure Firewall
The Cisco Secure Firewall is more advanced and provides more visibility into possible issues across the network.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Cisco Secure Firewall
The other products do well with simplifying some of the tasks such as rule creation where it would create rules based on a zone.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Cisco Secure Firewall
It's more reliable and the level of Cisco support can not be compared.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Sr Team Leader in Information Technology at Dish TV (Information Technology & Services, 1001-5000 employees)
Chose Cisco Secure Firewall
pfsence is a very complicated firewall and there is lots of documentation available on Cisco website for help. The configuration is very difficult and less documentation available. Cisco Secure Firewall provides us all the security features in low cost and this is very easy to …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Well-suited for big companies like mine, where we have a lot of users that we have to connect together. Getting all the switches into one big stack that you can just manage all at one time is fantastic for ease of use. Not suited for maybe smaller mom and pop shops or smaller companies that don’t have as many. They could probably go with something much easier to manage.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I can't think of scenarios where it is less appropriate, unless we are talking about real tiny businesses. More businesses will find Cisco Secure Firewall an outstanding tool to use, love, and trust from a reputable Network giant vendor. It is a must for businesses that want to focus on what they are doing, and leaving the network security for the pros.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I believe PFSense is well suited for both home lab environments as well as up to small to mid-size business environments on a tight budget. However, I would implore that anything in production requires the use of the authorized hardware that PFSense sells to receive support. However, in my experience, PFSense is a solid set-and-forget firewall solution.
Easy-to-use management interfaces. The CLI commands go across the whole Cisco Catalyst Switches 9000 series, so it makes it easy, the code being the same on the 9000 series. Just being able to do port channels, trunks, and connecting up edge switches to it with the Cisco Catalyst Switches 9000 Series.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cisco's firewall actually does its job of blocking what it is supposed to block. We had an old Firewall that led to slippages. Cisco catches 97% of malware and vulnerabilities during testing. For Coitiar, that means an engineer who clicks a link with malware is handled quickly.
We actually tested if failovers would affect running sessions. We pulled our primary unit during a certification submission period. The firewall just switched, and the connection kept running.
The AI assistant in policy management is excellent, and for our lean team, it makes the whole process easy and efficient. I don't have to audit 200 policies manually; the AI steps in and does its thing.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Easy to use. Good user interface design! Easy to understand and easy to set up.
Lower hardware requirement. 3 years ago, we used an old PC to run it. Now, we have changed to a router device with Celeron CPU and 8GB RAM. It runs smoothly with a 1000G commercial broadband.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One thing is that these, every time Cisco gets a new switch, they just make an amendment to the power supply, so they'll just put a knob on it. So let's say if you lose any power supply unit, you'll have to purchase another one, which costs a lot of extra money because we have a lot of another power supply units from the redundant, which we can use, but we can't now because they have just tweaked the modeling of that. Which makes no sense, particularly to me because it's an extra money making machine kind of a thing. But that's fine.
Another thing is these ports, I believe they are a bit less of, if I can say the quality of the oldest switches, they were quite sturdy. As I said earlier, the new switches, they're very light and when you lift them you feel it. So that's one thing, which I think the quality or the material which we are using has gone down.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I mean I think a lot of the technology with managing them is getting better. There's a few cons to the new firewall management console. You can't sort through routes or I think you can with interfaces now, but there's a few caveats that they haven't really worked out yet, but they're implementing AI into it, so it's getting to be a lot easier to use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I did kind of mention a Con in the Pro section with OpenVPN.
When I create a config for an employee other employees are able to login to that config.
I could be doing something wrong when I am making it - I am not afraid to admit that as I am pretty new to all of this, but it seems like it builds a key and I would think the key would be unique in some way to each employee, but I could be wrong.
I actually do not have a lot of Con's for this software - I did not get to set this up on our work network so I am not sure of any downfalls when installing.
I installed this on my personal machine in a Hyper-V environment to get a feel for it before I started working on it at work and it seemed pretty smooth. I didn't run into any issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
They are consistently reliable and this switch in particular is a very affordable solution. We can place the Cisco Catalyst 1000 Series Switches gear in areas that we normally would not place a switch because it is affordable enough to make it justifiable. And because it is a reliable solution, we are confident it will continue to provide service over the long haul.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It works really well. We can do most anything we want or need to with it, and you don’t have to have a doctorate or multiple certs to necessarily figure it out. The thing that would probably have to happen to make us switch would be if we just got priced out - Cisco’s more powerful and higher bandwidth models cost a pretty penny.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cisco by and far does a great job with the Catalyst line. From a layer 2 dumb switch all the way up to ISP carrier grade switching within the Catalyst portfolio. The best part about it is command parity among the various tiers of product. The only differences are going to lie in what features are available per switch.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
i think overall after ALOT of tac cases it works allright now. But still have alot of issues if you use cloud based mangement. fx, if you open 2 windows of access policys, both of the pages, rules starte to jump form side to side. if you then open one more list, its start to jump even faster. if you close the 2 of them, its back to normal. ALSO the extended access lists for VPN, SUCKS. Its the tiniest window when opening the editor, and you are not able to give the rules names, Which means finding and editing rules SUCKS, its a horrible experience, and eveytime we have to we want to yell :P
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The pfSense UI is easy to navigate and pretty go look at. It is much better than some high dollar firewalls that just throw menus you you. The pfSense UI is quick and responsive and makes sense 99% of the time. Changes are committed quickly and the hardware rarely requires a reboot. It just runs.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have very few is any outages due to a Cisco hardware failure. Some of our gear is exposed to some pretty harsh environments, and they keep on ticking!
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
No, the packets flow. Sometimes you will see collisions and broadcast storms can happen which will slow performance but that can be fixed and the packets will flow.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have not had any performance issues with Cisco Secure Firewall, even with DPI and IPS enabled, we have not seen a performance hit. Emoployes have not complained about any slow network speeds that could have been attributed to the secure firewall it has always been something else within the office network.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We rarely have issues with the product. I have only had to contact support one time since we put it in and that was to see if another vendor was giving me accurate information on an issue I was having.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I rarely get the support I need in the time I need it. Often, while they are "looking at packet captures and going to get back to me" I fix the problem on my own. If you were to look at my TAC cases over the past year, you would see some very lengthy cases that usually ended with me contacting the TAC person and telling them to just close the case
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cisco Networking Academy partners with many local Colleges and High Schools to provide great hands-on training. You do need to drive to learn the topic. The in-class session only go so far. You really need to apply this to the real world. Cisco makes it easy for business to connect via CLC or Cisco Learning Credits.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
was a good training but questions was answered not so good. Training was "Fundamentals of Cisco Firewall Threat Defense and Intrusion Prevention (SFWIPF)".
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The implementation of the Cisco Catalyst 1000 Series Switches is fairly seamless, especially if you are familiar with Cisco products. We have had Brocade switch gear in place too, and the differences between the manufacturers [are] not a major issue.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Our initial implementation was aided by Cisco's professional services and was excellent. The engineer was very knowledgeable and helped us work through issues while building out our new internet security edge Part of this involved tools to migrate the firewall configuration from old to new.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
2960s, 9200s, 9400s, 3650s, 3800s. I think that this product is a lot better. I know I just complained about the noise, but it’s still much quieter than our other ones. So we do have a couple of public deployments, and once we swap these out, they complained less. Sometimes we have small offices that get the gear in with them, and these sound less like a jet engine. And yeah, these are a lot easier to manage as well. Everything in the same family. It’s a lot.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cisco Secure Firewall works better with the Cisco ecosystem when we can utilize it and feels beefy enough when we utilize it in the data center. The Fortinet we have found are great, small cost boxes for remote offices with a better UI then Cisco Secure Firewalls. The feature set included with the firewalls feels similar from a security point of view.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Meraki has a unified management login for all devices, which is nice. It also has decent content filtering, both areas where pfSense is weaker. Where pfSense far ouclasses Meraki is in the ease of use and the other width of features. These include features such as better VPN interoperability, non-subscription based pricing, auditability, not relying on the infrastructure of a third party, more transparency of what's actually going on, easier to deploy replacements if hardware fails. Additionally, the NAT management for pfSense seems to be a bit better, as you can NAT between any network segment and not just the LAN segments out the WAN interfaces.
A solid, realistic rating most people give for Cisco Secure Firewall pricing is 7 or 8 out of 10 (because the product is strong but licensing can be a bit complex)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We are exclusive Cisco at our organization. In truth part of the reason is, with one type of switch and one manufacturer, it is easier to support. It is also easier to give consistent training to our staff in our tech department
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco Secure Firewall has never given us any trouble, it has stayed up at all times, upgrading the appliance has also become much simpler. We operate the appliance in a HA pair, so 0% downtime within our organisation. During switchover while upgrading, not a single packet seems to get lost, so this has been a very valuable asset to our company.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
pfSense can be installed on commodity hardware with no licensing fees. With a simple less than 10 minute restore time, on most hardware, it's an extremely inexpensive way to achieve the same results that some of the more expensive vendors provide.
The easy to use interface has allowed configuration management to be preformed by lower level technicians with quick and easy training.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info