CrowdStrike offers the Falcon Endpoint Protection suite, an antivirus and endpoint protection system emphasizing threat detection, machine learning malware detection, and signature free updating. Additionally the available Falcon Spotlight module delivers vulnerability assessment with no performance impact, no additional agents, hardware, scheduled scans, firewall exceptions or admin credentials.
$59.99
per endpoint/month (minimum number of endpoints applies)
Microsoft Defender for Cloud
Score8.7 out of 10
N/A
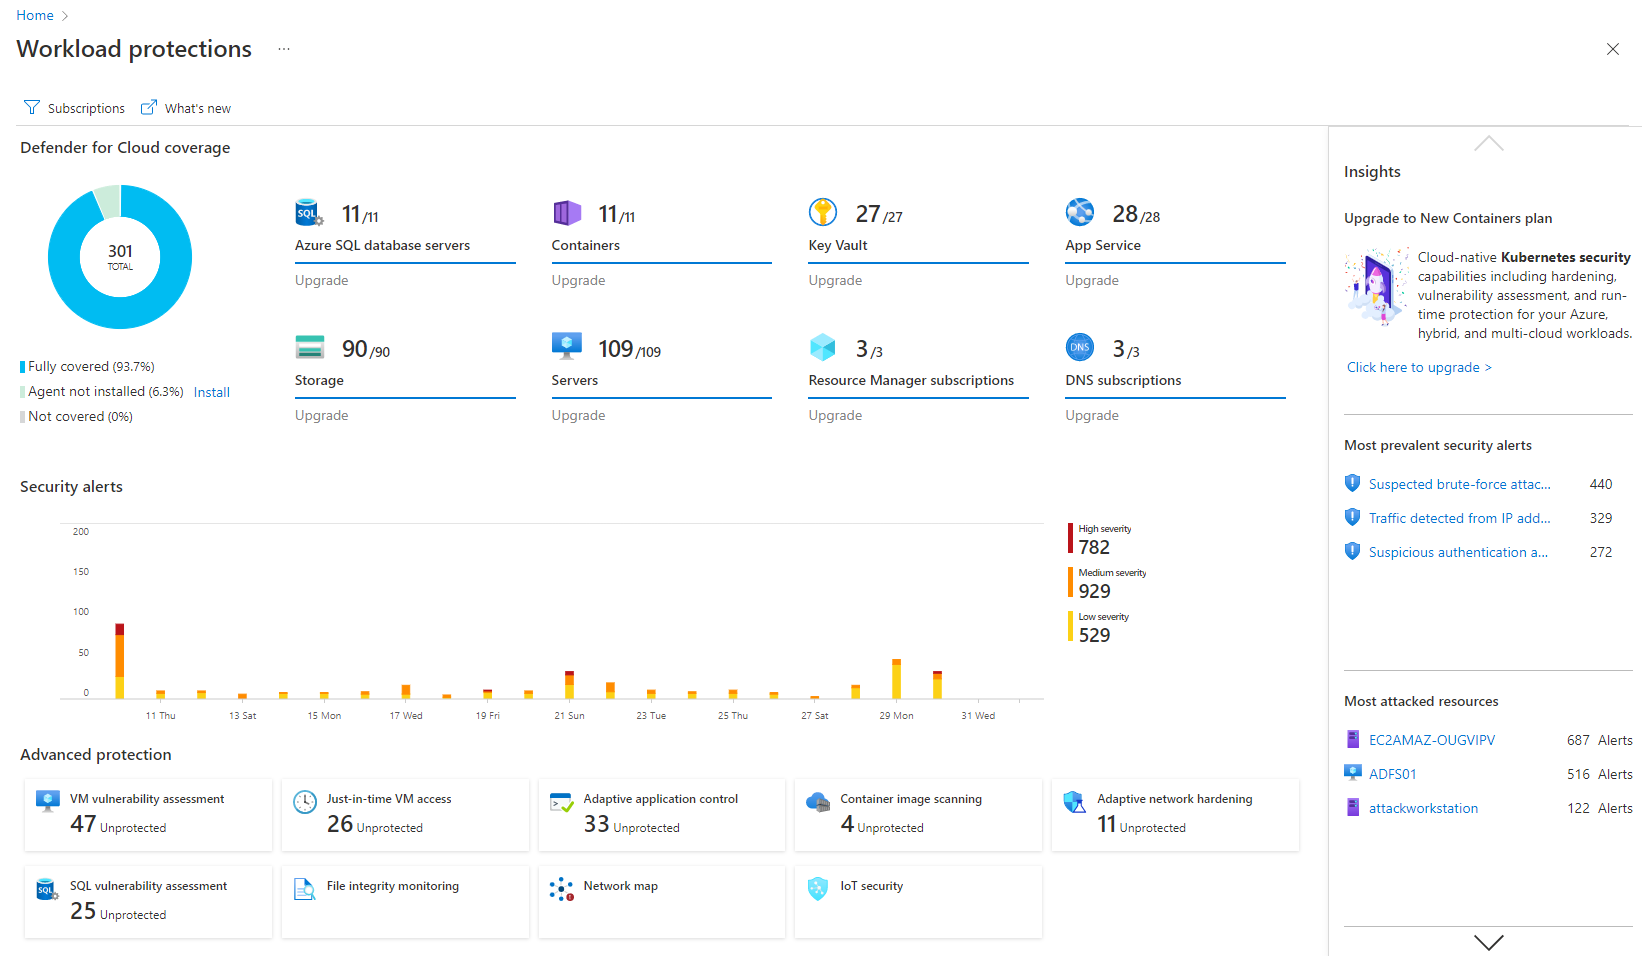
Microsoft Defender for Cloud is a Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platform (CWPP) for Azure, on-premises, and multicloud (Amazon AWS and Google GCP) resources.
N/A
Pricing
CrowdStrike Falcon
Microsoft Defender for Cloud
Editions & Modules
Falcon Go (Small Business)
$59.99
per endpoint/month (minimum number of endpoints applies)
Falcon Go (Small Business)
$59.99
Falcon Pro
$99.99
per endpoint/month (for 5-250 endpoints, billed annually)
Falcon Enterprise
$184.99
per endpoint/month (minimum number of endpoints applies)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Microsoft
Verified User
Chose Microsoft Defender for Cloud
Because we do a profound review of functionalities, configurations, and security operations from our soft team's perspective. The best one that adapts to our actual architecture, and I mean it's so negative for us because we are more prone to Microsoft products, was Microsoft …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender for Cloud
I believe Microsoft Defender for Cloud stacks up well against the other tools we looked at. It is native to the Azure platform and provides the same insights as the other tools. We selected Microsoft Defender for Cloud because it integrates well with the Azure resources and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Cloud
Microsoft Defender for Cloud offered a more integrated and comprehensive solution for our multi-cloud environment, integrating well with our security and compliance needs
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
System Integration Consultant in Engineering at JLL (Computer Software, 10,001+ employees)
Chose Microsoft Defender for Cloud
There is the several ways to protect the applications and lot more tools available in the market. Most commonly we used Crowd strike Falcon for endpoint detection and response capabilities. McAfee endpoint protection also provide broad range of security features. Best …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Crowdstrike is a unified platform for monitoring endpoint devices, whether they're workstations, servers, cloud-native machines, or even mobile devices. It uses AI/ML to monitor anomalies and suspicious behavior, including zero-day attacks. It is suitable for large organizations but may be costlier or less appropriate for smaller organizations, those who want an on-prem EDR setup, and those who need custom scanning based on compliance requirements.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think it's good for cloud-native companies. A company that, from day zero, they're like, "We're going cloud, and this is how we're going to do it." They get it. It works well for them. Smaller organizations that are under X amount of resources- I don't know what that X might mean- but I feel like it plays well in smaller, more nimble organizations. If you're an older organization or if you're extremely large, it starts becoming a little difficult to manage at scale. And you have to sometimes throw bodies at the problem. Maybe not the most eloquent way of saying it, but that's what it feels like.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It's really well laid out, with an easy-to-use, accessible UI.
With Microsoft Defender for Cloud, it has everything you need with the Safelink attachment, the Safelink emails for URL, the way it scans those URLs and attachments within the product, and you're seeing the results. And that adds an extra layer of security for the user, so you feel comfortable knowing the product monitors those. That's something I really like about that product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Integrations with on-premise workloads can sometimes be challenging. Needs improvement and well standardised integration points
Vulnerability categories can be difficult to understand. It should allow teams to focus on critical findings and help them keep aside low-severity or suppressed vulnerabilities
Pricing can be improved as it can be over-priced for smaller businesses and would potentially affect their ROI due to the small scale
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Crowdstrike has a large suite of tools built for helping the engineers triage and respond to security event whenever identified. The ability to customize the security policies and implement more granular policies to different devices based on the functionality is unmatched. Crowdstrike provides so much of ability in a decent budget which ascertains the value for money or ROI.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is a great product that integrates nicely when running an Azure platform and even multi-cloud environment. Not looking for point-solutions but a suite that answers most requirements. It is very comfortable being able to use KQL, workbooks and automation that is native to the azure platform
I think it is a complete and very trustful XDR platform, with very few False Positives. It is very well supported by highly skilled professionals on all levels: from pre-sales engineers, Customer Account Managers and support engineers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
My visibility is limited because I'm only doing very small pieces of what the overall org does. And also, we have limitations on what we're allowed to use. It's not like we get a new product as users or leadership level users, and everything is on, and we can just do whatever we want. We're very restricted in what we can use any tooling within the org because of the different levels of regulatory constraints we have, because of just the nature of who we are inherently. So that's why. I don't think it's necessarily the product. I think it's more or less of what we're able to do with the product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Any time we need to engage the Crowdstrike Falcon Complete Team, their response is switch, thorough, and they are sure to not close out any request until the customer confirms that they have provided an acceptable resolution. If I ever need anything from the account team related to the product, I also get a response from them within minutes typically to address my question. Top notch customer service!
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
There is limited amount of learning that can be completed in an in-person training available. In my opinion, the self-paced learning provided by Falcon portal is more useful over in-person training. The support from Falcon is great and useful to overcome difficulties, if any.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The training provided by Crowdstrike Falcon is complete in terms of the depth of technical knowledge and teaches the users about going through with the platform. There are lots of jargons for different tools that Crowdstrike Falcon has and this training teaches them all which helps in managing the platform better. Plus, the regular knowledge checks are also very helpful for the end user.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It was just a legacy AV program onboarded during initial setup days. As the org. As it expanded, its threat landscape also grew, and we needed a next-gen solution to protect against evolving threat vectors. Falcon EDR was the one that solved all these in a single place.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I believe Microsoft Defender for Cloud stacks up well against the other tools we looked at. It is native to the Azure platform and provides the same insights as the other tools. We selected Microsoft Defender for Cloud because it integrates well with the Azure resources and gives the needed insight, security alerts and recommendations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
CrowdStrike Falcon's proactive threat mitigation has significantly reduced the risk of successful cyber attacks, resulting in tangible savings related to potential data breaches or system compromises.
The cloud-native architecture and automated features have improved operational efficiency.
The platform's real-time visibility and threat hunting capabilities have drastically improved incident response times.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info