Forescout Technologies headquartered in San Jose actively defends the Enterprise of Things by identifying, segmenting and enforcing compliance of every connected thing. Forescout boasts a widely deployed, enterprise-class platform at scale across IT, IoT, and OT managed and unmanaged devices. Forescout arms customers with device intelligence, in order to allow organizations across every industry to classify risk, detect anomalies and quickly remediate cyberthreats without disruption of critical…
N/A
SolarWinds Engineer's Toolset
Score7.6 out of 10
N/A
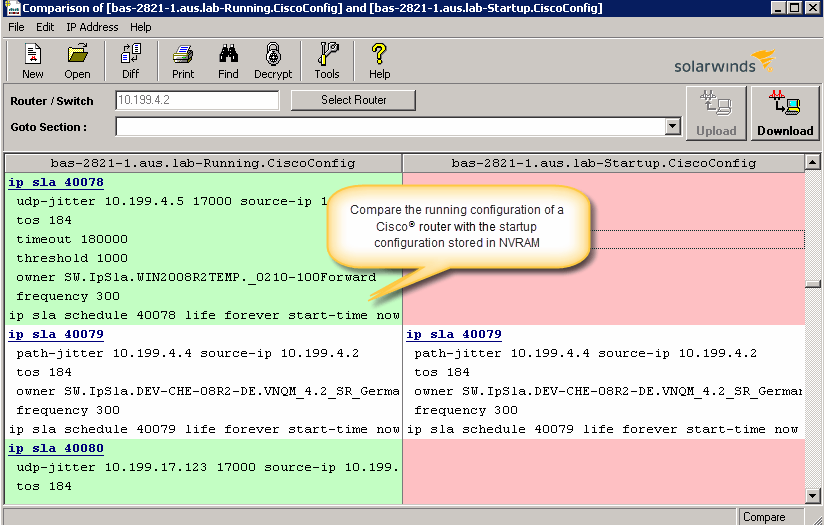
SolarWinds® Engineer’s Toolset (ETS) helps users monitor and troubleshoot a network with over 60 tools for network management. ETS allows users to monitor and receive alerts in real time on network availability and health, and perform network diagnostics for faster troubleshooting and resolution of complex
network issues. With ETS users can deploy an array of network discovery tools including Port Scanner, Switch Port Mapper or advanced Subnet Calculator, manage Cisco®
devices with specialized…
$1,585
Per Instance
Zscaler Private Access
Score9.4 out of 10
N/A
Zscaler Private Access™ (ZPA) gives users secure access to private apps and OT devices while enabling zero trust connectivity for workloads.
I strongly recommend using it in networks where many machines enter, it is essential to have a capture of all ids, mac etc to prevent and detect unauthorized machines.We are in the technological era and there is a lot of technological robotization looking for weak systems to enter.Invest in greater security and that does not happen to you.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I have found the toolset especially useful for scanning subnets to discover devices, and for setting up temporary real-time monitors when we are troubleshooting or setting up new connections. The most useful aspect has been the ability to apply the tools to help troubleshoot and pinpoint intermittent issues. More general tools like Orion often do not have the granularity to detect issues like intermittent packet loss which are especially impactful to applications like Voice. The toolset gives us another level of capability to dig into issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Zscaler Private Access works really well in environments setup for FQDNs and where you know what users should/shouldn't be accessing on what ports. You can use Zscaler Private Access to figure out these kinds of features but that doesn't always mean you'll be correct. It also provides a consistent experience for users as they can access their materials anywhere. It also makes the user the last line of defense. If a user's account is compromised then the attacker has access to everything they already did. It doesn't work great in OT environments or Server based environments. Flows have to be initiated from the client and not the server for stuff to behave properly.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Connecting users remotely with a secure connection. I am a service desk agent who works with end users, and if there is an issue due to ZPA, it's most likely due to configuration. A really good service.
Logging, I believe, works well as I troubleshoot end users and can gather extra details for my network admin. IP.zscaler.com, and the debug logs are nice. Additionally, I like how it shows the App policy assigned to the user's machine ECT.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The unifying component that is intended to be the initial interface to the tools seems clunky. I prefer to start the tools individually rather than using it.
The port scanner could use some improvements to make it easier to use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Needs an interface for Support Desk/Help Desk to more easily understand that the problem is a lack of an FQDN or access is not allowed due to policy, not because of a technical shortcoming in ZPA.
Documentation of the BC solution is not well-detailed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The environment feels more secure, and we are seeing that users are adapting to it fast. The fact that we have tools to assist the users with their day-to-day access helps, as we can hand it off to the helpdesk without any escalations to the Network team. It is a work in progress for our agency, but we are seeing the benefits from the solution.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
They are prompt in their response with a complete resolution once they have identified the problem. Other OEM's generally give stop-gap arrangements and then later come with new upgrade versions. This gives downtime tasks to customers often, which isn't appreciated. Given the criticality of this software, their support is prompt.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Better intergration with patch management tools. Forescount Platfform (CounterAct) is easily compatible with diverse network infrastructure to offer better service and efficiently ensure seamless operations. Its automation capabilities have also enabled us to depend less on the operations teams hence saving time as it's faster and also saving the operational cost of having people around in case of threats.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I haven't compared any tools similar to SolarWinds Engineer's Toolset. This might be because I'm pretty biased when it comes to monitoring, and reporting solutions. I've found that SolarWinds provides the biggest bang for the buck in my opinion. I'm sure there are other solutions on the market that compete, but I haven't tried any of them because I've been very satisfied with SolarWinds.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
ZPA is where the bulk of zero-trust access is found. While the functionality for ZIA is excellent, the policy we implement for internet access is more focused on threat prevention and not narrowly scoped access.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We used to get anywhere from 30 to 50 tickets surrounding our previous VPN solution every month. We now average 3-5 tickets regarding remote connectivity, and of those, only 1 or 2 are actual issues with ZPA.
Using ZPA Access Policies, we can now block endpoints that have outdated security software from ever connecting to our environment. This was simply not possible with our previous solution.
Some of our employee base skews older and had a harder time understanding the change from VPN to Zscaler.
There is significantly less downtime with ZPA when compared to other VPN solutions.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info