IBM Security QRadar is security information and event management (SIEM) Software.
N/A
Microsoft Defender for Endpoint
Score8.8 out of 10
N/A
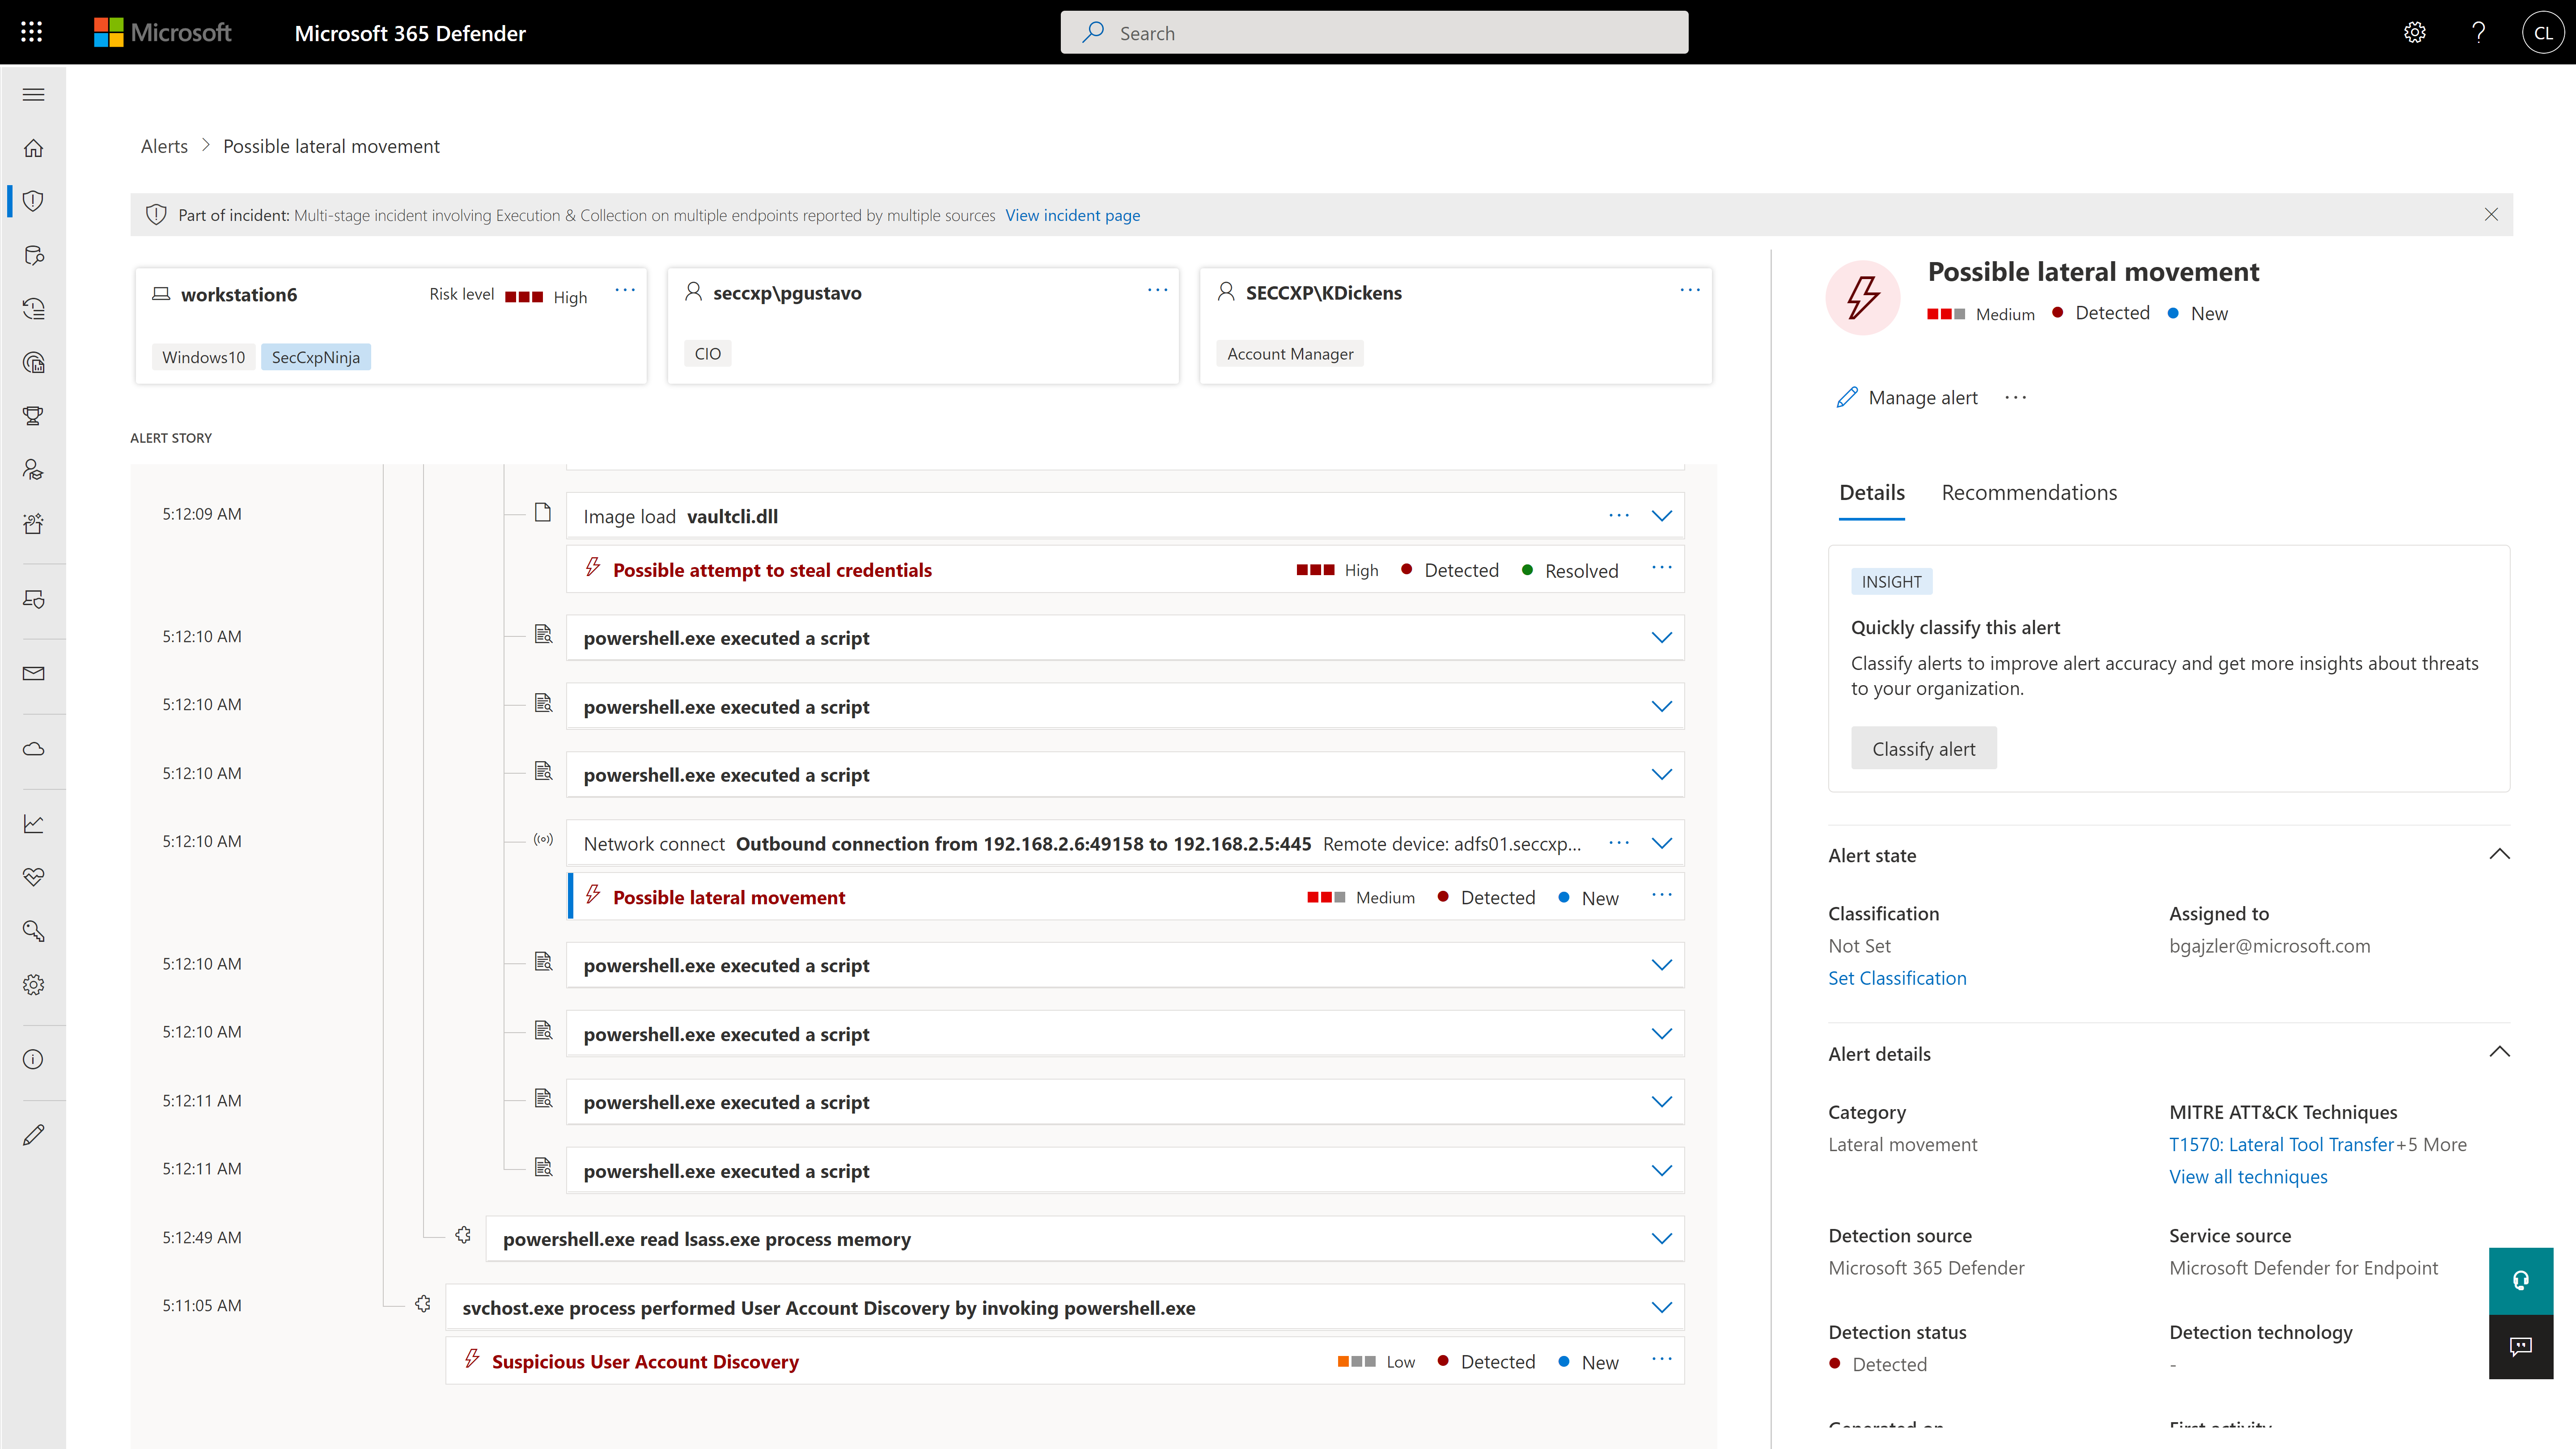
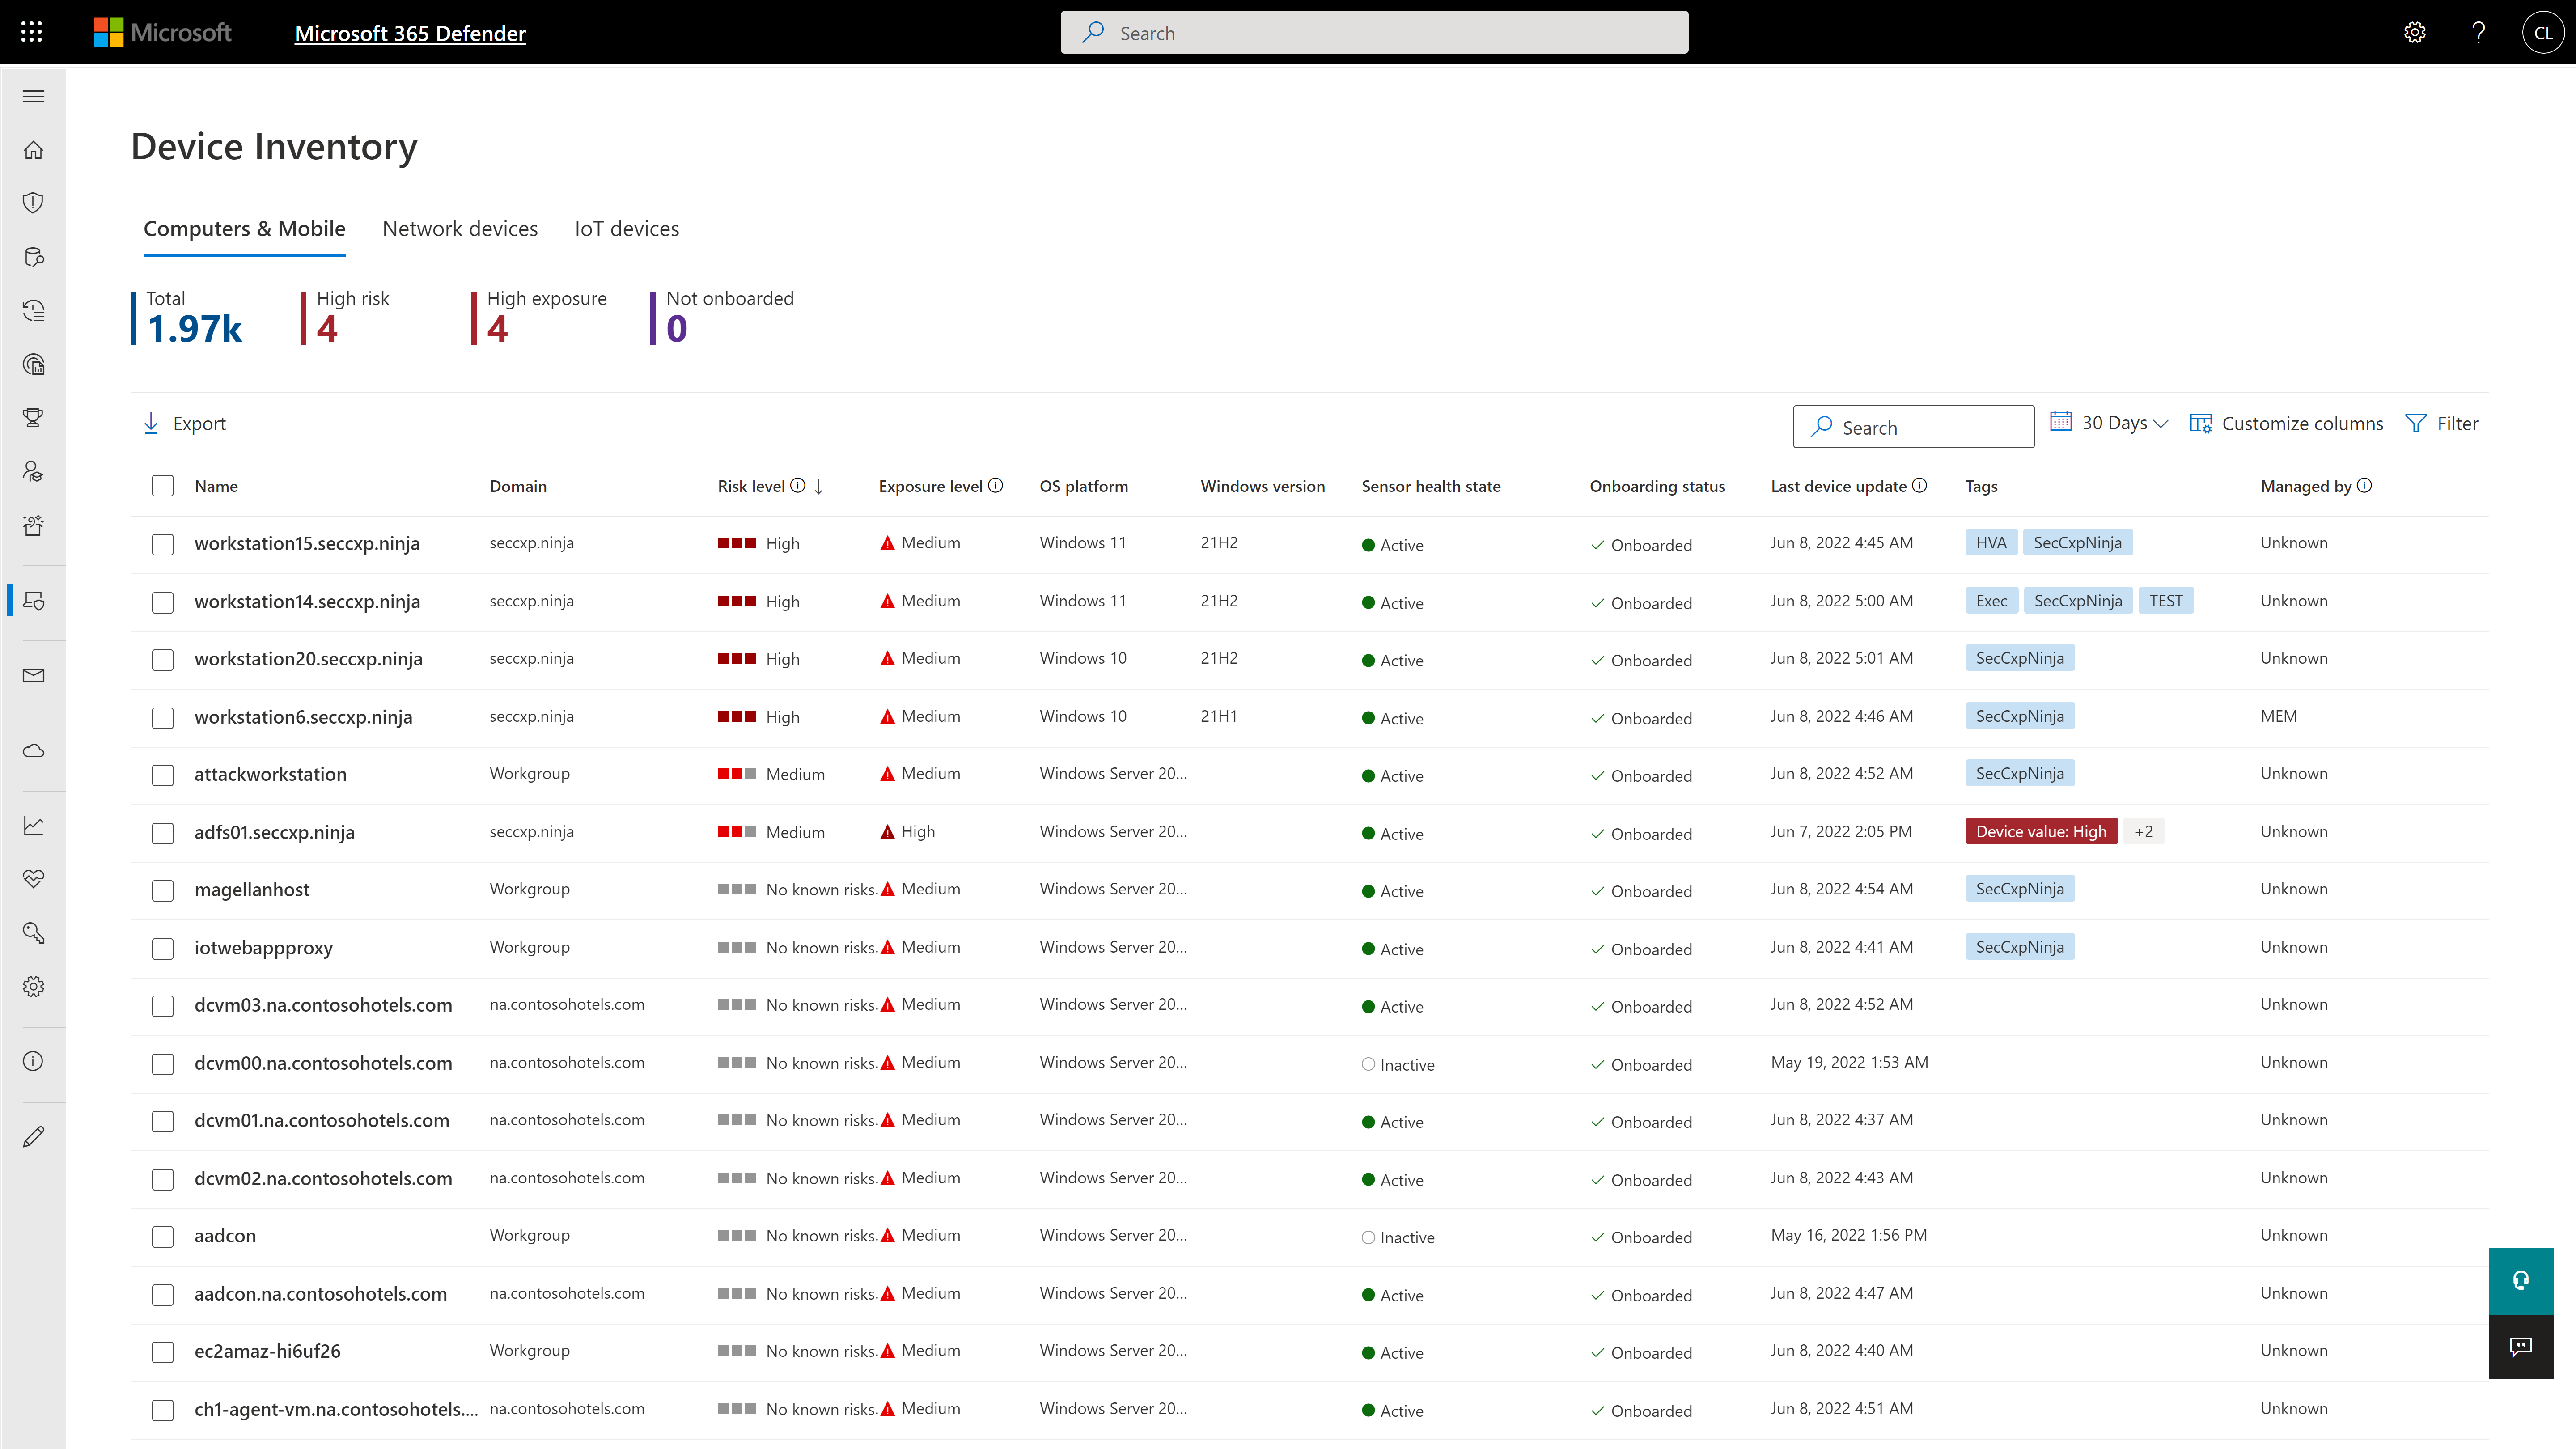
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
Microsoft Sentinel
Score8.6 out of 10
N/A
Microsoft Sentinel (formerly Azure Sentinel) is designed as a birds-eye view across the enterprise. It is presented as a security information and event management (SIEM) solution for proactive threat detection, investigation, and response.
/security Specialist in Information Technology at BANCO DO BRASIL S/A (Banking, 10,001+ employees)
Chose IBM Security QRadar SIEM
The QRadar licensing process is based on EPS (Events Per Second) and there are no limitations on event collection, regardless of the origin of the logs. This becomes an advantage as the price is agreed between the parties before purchase, so you have knowledge of what you can …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Security Solutions Architect in Information Technology at Tech Mahindra Ltd (Information Technology & Services, 10,001+ employees)
Chose IBM Security QRadar SIEM
I found that IBM Security QRadar SIEM has better threat detection methods and the identification of cyber kill chains followed by attackers. Analysis of the data gives visibility that other SIEM solutions need to improve. Integration in IBM Security QRadar SIEM is also better …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose IBM Security QRadar SIEM
IBM Qradar takes the best from its competitors. Reliable and stable but sometimes very expensive, the SIEM from IBM offers a wide range of scenarios in which the customers can suite and size their own infrastructures. IBM Qradar doesn't really needs to stack up againt its …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose IBM Security QRadar SIEM
IBM Qradar is cheaper and also easy to use. For splunk you need dedicated team of experts.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Information Technology Security Engineer in Information Technology at Yapı Kredi Teknoloji (Banking, 10,001+ employees)
Chose IBM Security QRadar SIEM
IBM is more user-friendly if we compare it with ELK stack and ArcSight. Much reliable, and have better Support. Onboarding data, creating correlation searches, and easier to integrate with 3rd party solutions as well. LogOps projects and less time-consuming products. Qradar …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft
Verified User
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint consistently showed better user experiences during scans due to the reduced amount of resources used on each system compared to our previous endpoint protection solutions. However, the main reason we chose Microsoft Defender for Endpoint is …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
It's very convenient and very well integrated with our environment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
IT Security Specialist in Information Technology at Oregon Judicial Department (Government Administration, 1001-5000 employees)
Chose Microsoft Defender for Endpoint
Before we switched to using Endpoint, we were using McAfee and we weren't getting the most use out of that, weren't super happy with it, and so we switched, got rid of that and switched to just using all the endpoint features.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Senior Manager-Cyber Security in Information Technology at Brookfield Renewable (Environmental Services, 1001-5000 employees)
Chose Microsoft Defender for Endpoint
Defender works better for my org. This may depend on your ecosystem, however for me, Defender is a clear winner. I like Defender's ability to utilize multiple sensors and data points to detect possible breaches. I like the built-in EDR functionality. I do not need to purchase a …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft
Verified User
Chose Microsoft Sentinel
These are all the Microsoft products. We have used Splunk. And again, I would say Microsoft Sentinel stacks up because it's a native tool that is more like an ecosystem. It's not a standalone tool. It's like if you're in the Microsoft stack, Microsoft Sentinel will stack up …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Sentinel
Most of our landscape, both on prem and cloude, is based in Microsoft technologies, while the unification of tools implies some risk, decreasing the vendor levels simplify integrations, and by scale, help us to reduce costs too. Yes, the tool itself is a good contender, but the …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
SOC Engineer in Engineering at Dell technology (Computer & Network Security, 10,001+ employees)
Chose Microsoft Sentinel
Microsoft Sentinel feels on another different level from these solutions , all in the cloud . No need for troubleshooting , deployment or upgrades. Constant updates from the vendor and good support
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
National Security Practice Manager in Sales at Data#3 (Information Technology & Services, 1001-5000 employees)
Chose Microsoft Sentinel
Splunk, Google, SecOps. I look at how it stacks up based on the fact that it's the primary solution that we sell. So I think it stacks up really well. Why do we select it? Well, we selected it primarily because we're a very large Microsoft partner. The technology is very good …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Sentinel
Elastic seems to have a much better interface for log search and is able to filter out noise. Microsoft Sentinel also appears to generate a lot of false positives.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Sentinel
Prior to using Sentinel, we were using Splunk specifically Splunk Enterprise Security and Splunk Cloud, so their on-prem and their cloud-based products. We switched originally for cost reasons, specifically cost control, but I have found that the ability to create reports, the …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Sentinel
The key advantage of using Sentinel lies in Microsoft already being a renowned name in cloud services. Hence, the Collection of data at the cloud scale across all users, devices, applications, and infrastructure, both on-premises and especially in the MS Cloud, is super easy. …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Sentinel
ArcSight is an on-prem solution that has a different approach than Sentinel.
In a basis this product is more complex to maintain and deploy. The query functionality in Sentinel is more powerful and easier to maintain. ArcSight has a much slower performance and an interface that …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Sentinel
Microsoft Sentinel really goes the extra mile when it comes to an SIEM that slowly improves toward a proper SOAR, this may be the best selling point of the entire solution. Highly scalable, cloud-based, and nearly perfect when dealing with Microsoft-based infrastructures, …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Comparison of Security Information and Event Management (SIEM) features of IBM Security QRadar SIEM and Microsoft Defender for Endpoint and Microsoft Sentinel
Feature
IBM Security QRadar SIEM
8.5
69 Ratings
6% above category average
Microsoft Defender for Endpoint
-
Ratings
Microsoft Sentinel
8.5
34 Ratings
6% above category average
Centralized event and log data collection
9.927 Ratings
00 Ratings
9.134 Ratings
Correlation
8.669 Ratings
00 Ratings
8.935 Ratings
Event and log normalization/management
9.527 Ratings
00 Ratings
8.435 Ratings
Deployment flexibility
7.827 Ratings
00 Ratings
8.333 Ratings
Integration with Identity and Access Management Tools
8.965 Ratings
00 Ratings
8.933 Ratings
Custom dashboards and workspaces
7.569 Ratings
00 Ratings
8.435 Ratings
Host and network-based intrusion detection
9.725 Ratings
00 Ratings
8.030 Ratings
Data integration/API management
9.07 Ratings
00 Ratings
8.433 Ratings
Behavioral analytics and baselining
7.648 Ratings
00 Ratings
9.031 Ratings
Rules-based and algorithmic detection thresholds
8.049 Ratings
00 Ratings
8.733 Ratings
Response orchestration and automation
7.75 Ratings
00 Ratings
8.232 Ratings
Reporting and compliance management
7.947 Ratings
00 Ratings
7.35 Ratings
Incident indexing/searching
8.97 Ratings
00 Ratings
8.733 Ratings
Endpoint Security
Comparison of Endpoint Security features of IBM Security QRadar SIEM and Microsoft Defender for Endpoint and Microsoft Sentinel
I would only recommend IBM Security QRadar SIEM in a few situations. For one, it's very easy to setup and use if all your log sources are generic from known vendors. It's also significantly cheaper than Splunk, which is nice if you're trying to save money or be more efficient. I would not recommend IBM Security QRadar SIEM for environments with a lot of custom logs and complicated detection requirements.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
What has really impressed me is how Microsoft Sentinel delivers centralised security monitoring across multiple data sources in our enterprise. It has reduced cost of handling large security logs by collecting and analyzing data without friction of managing traditional SIEM infrastructure. It is easy to work to integrate with Azure logs for quick data analysis.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The visual presentation of data is terrific, so including what we had prior to Microsoft Sentinel, it presents data in a much more usable way, so that's been quite refreshing. It's not quite as complex to understand what you're looking at.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Need to spend more time configuring the system to properly interpret and normalize different type of data collected from multiple resources.
While Rule creation QRadar uses that rules to detect security threats and generate alerts, but to creating and managing rules is bit complex & tedious work to complete.
IBM Security QRadar SIEM is excellent in handling large & complex systems that requires in-depth knowledge and extensive training to configure and maintain the system which includes upgrading, optimization of performance & issue troubleshooting.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One feature that I would like to see improved is probably the log parsing. I think one of the big things that Splunk does better than Microsoft Sentinel is that it makes it easy to bring in new log streams of arbitrary formats and parse them out into columns and tables. Microsoft Sentinel is a lot more involved, though. It takes a lot more manual work to bring in different log sources and parse them out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
QRadar is an established and stable product, we have been using it for many years and want to continue to focus on it. Anyone who has used the product and knows it knows how reliable it is and how it facilitates continuous monitoring of threats from outside and inside. it is an exceptional product that is very useful for us.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
As a grade I give 8 as QRadar is not easy to learn. It requires some time to master it. It also needs a team of people actively working on the product. Once you learn to use it the software works very well and it is easy to correlate and understand detected threats. It only takes time to learn how to use it well and configure it properly.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Mirosoft sentinel is easy to use once the inital setup is completed.The dashboard and centralized alerts make it simple to monitor security events and investigate incidents.Integration with other microsoft security tool is also helpful.Some advanced features and configurations can take time to understand, but overall it provides good, user-friendly security monitoring.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Customer support is Good of IBM, While Using IBM QRadar its deployment is to slow and suddenly stop working and crashed we have contacted IBM Support and Rised a Ticket within a few minute we get call back from customer support and Query Resolved by them Fast And Rapid Support of Ibm
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft support is one of the highest rated on the market. It has global and multilingual support. Calls can be made over the phone and the solution is virtually instantaneous with the help of Microsoft engineers. It's great!
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The training was very useful and the people who taught us were very knowledgeable. Although the software may initially seem difficult to learn they made things much easier for us.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Initial patience is required to learn how to use the product, and it takes a dedicated team to use it. One person is not enough, and it's not enough to just set it up and check it once in a while. It has to be used daily and kept under control to be used effectively
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
IBM Qradar takes the best from its competitors. Reliable and stable but sometimes very expensive, the SIEM from IBM offers a wide range of scenarios in which the customers can suite and size their own infrastructures. IBM Qradar doesn't really needs to stack up againt its competitors because it already sets an example in the SIEM world.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Compared to platforms such as Splunk, LogRhythm, and Devo, Microsoft Sentinel’s cloud‑native, consumption‑based pricing model and reduced infrastructure overhead tend to offer better overall cost efficiency. This is especially true for organizations already invested in the Microsoft ecosystem, where Sentinel can deliver strong capabilities with a lower total cost of ownership.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's probably neutral. We see value, but it's, again, tick that kind of expense stuff. We're getting more insight and value into what is going on in that cloud workspace, but just noting the cost. So it's probably neutral. I'm not directly responsible, so the full kind of return on investment kind of cycle, that's someone else's problem. I'm like the end user. It's my team that will look at the data and look at the output of Microsoft Sentinel. So the ROI, someone else can worry about that.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info