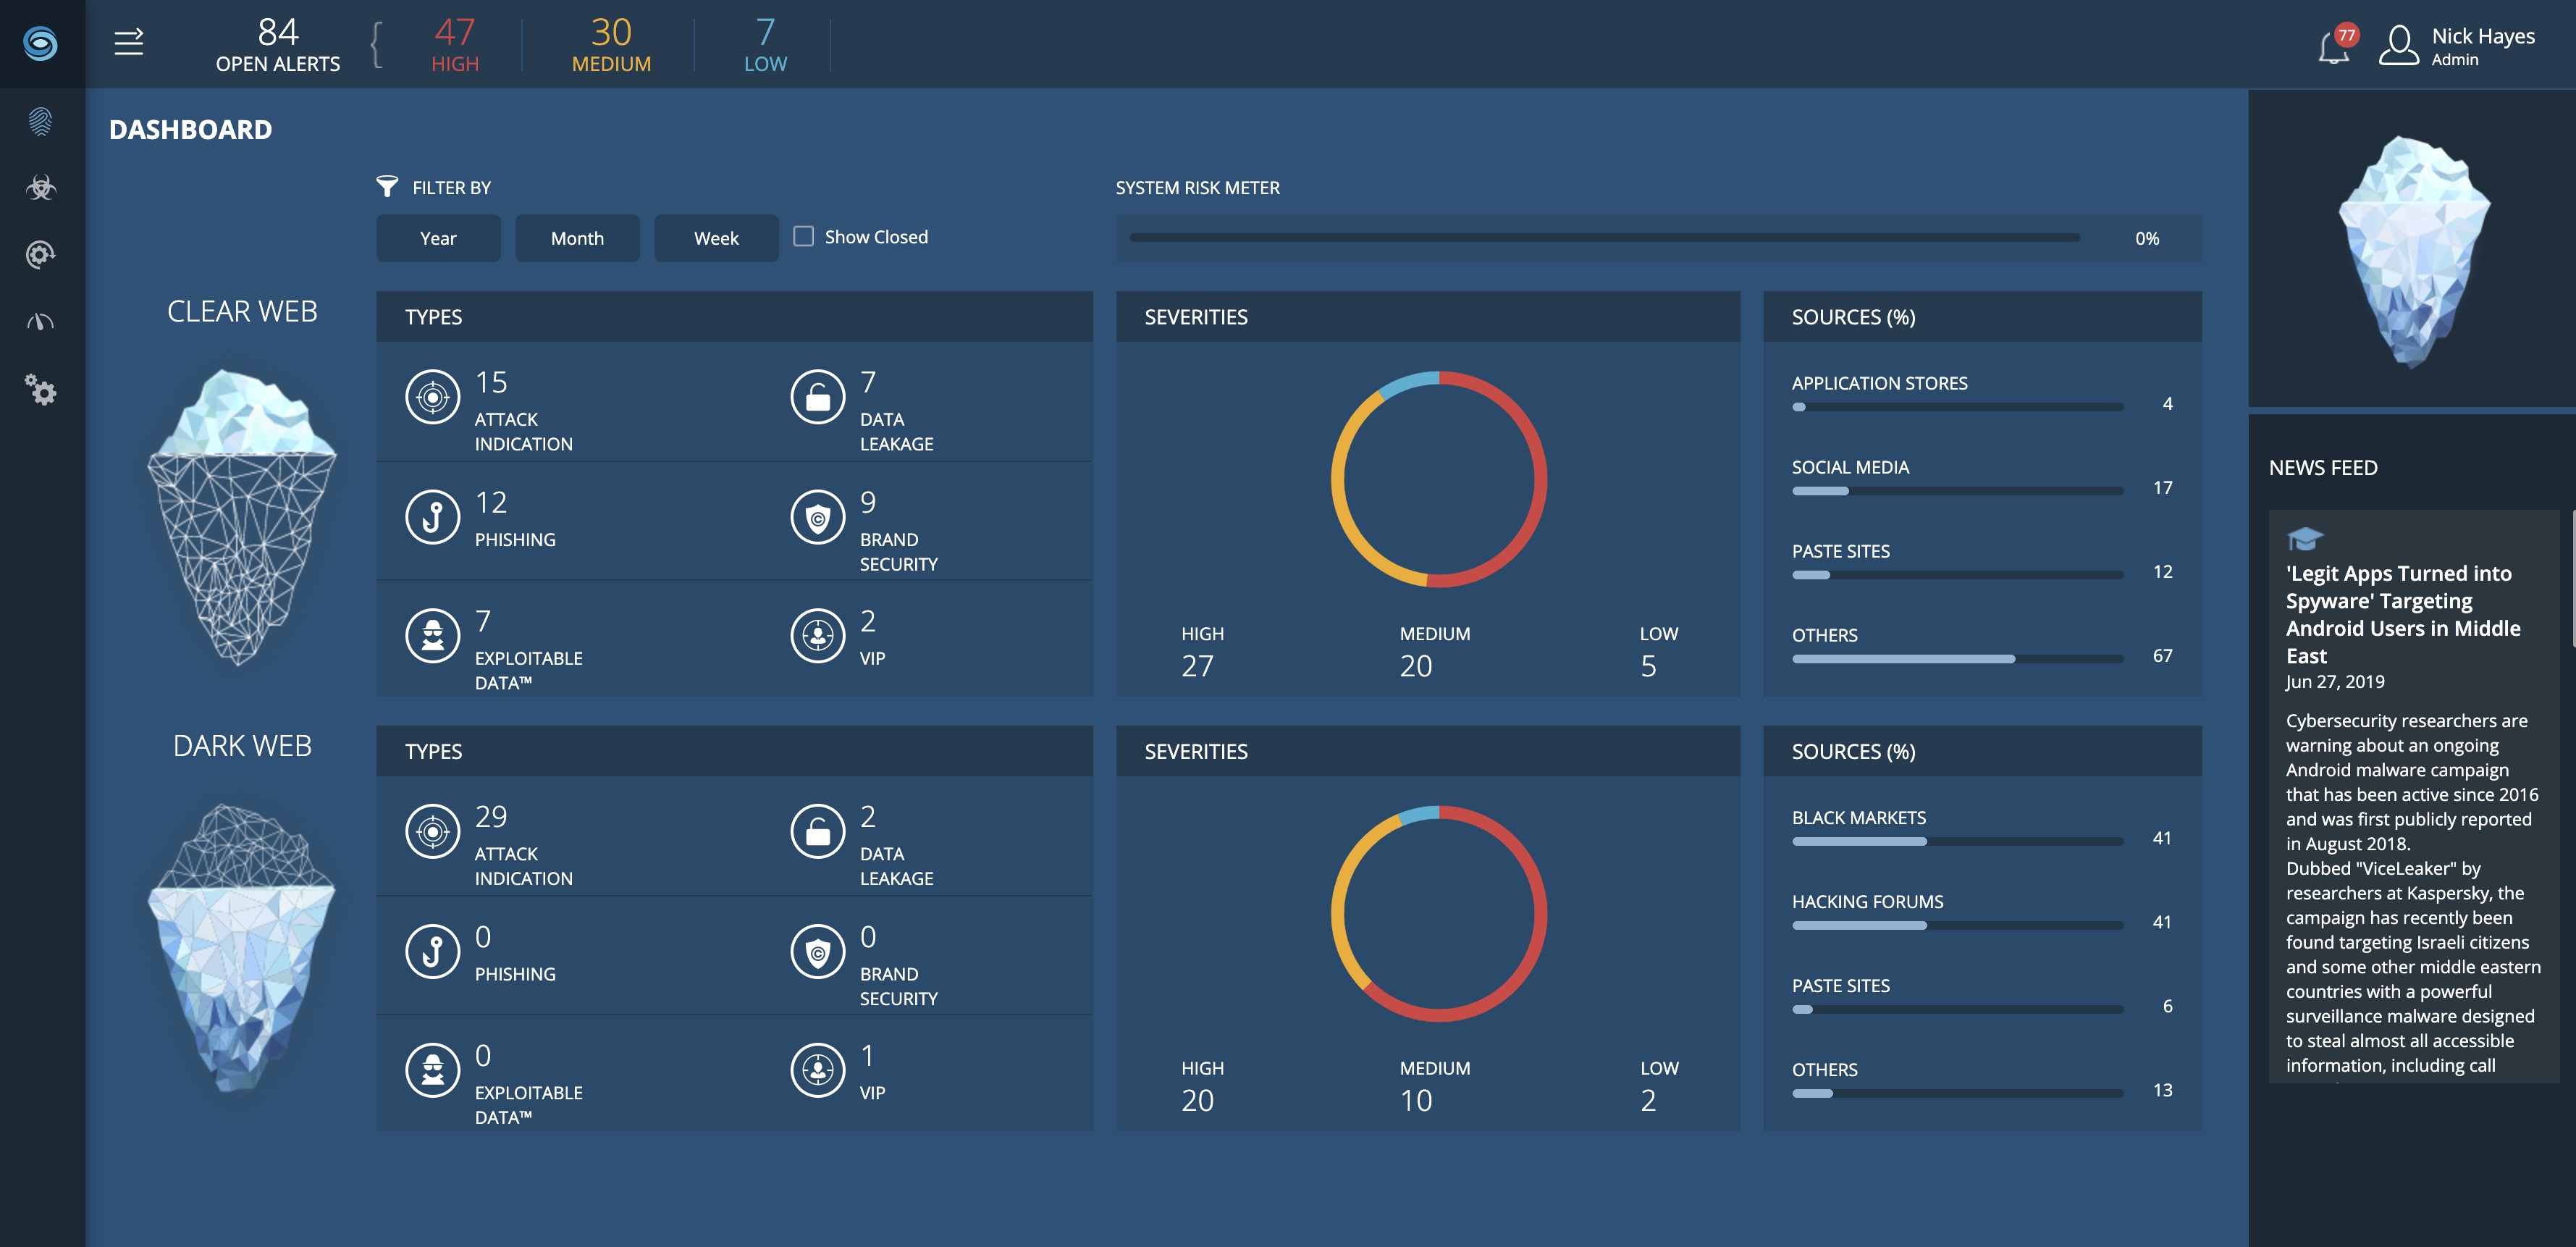
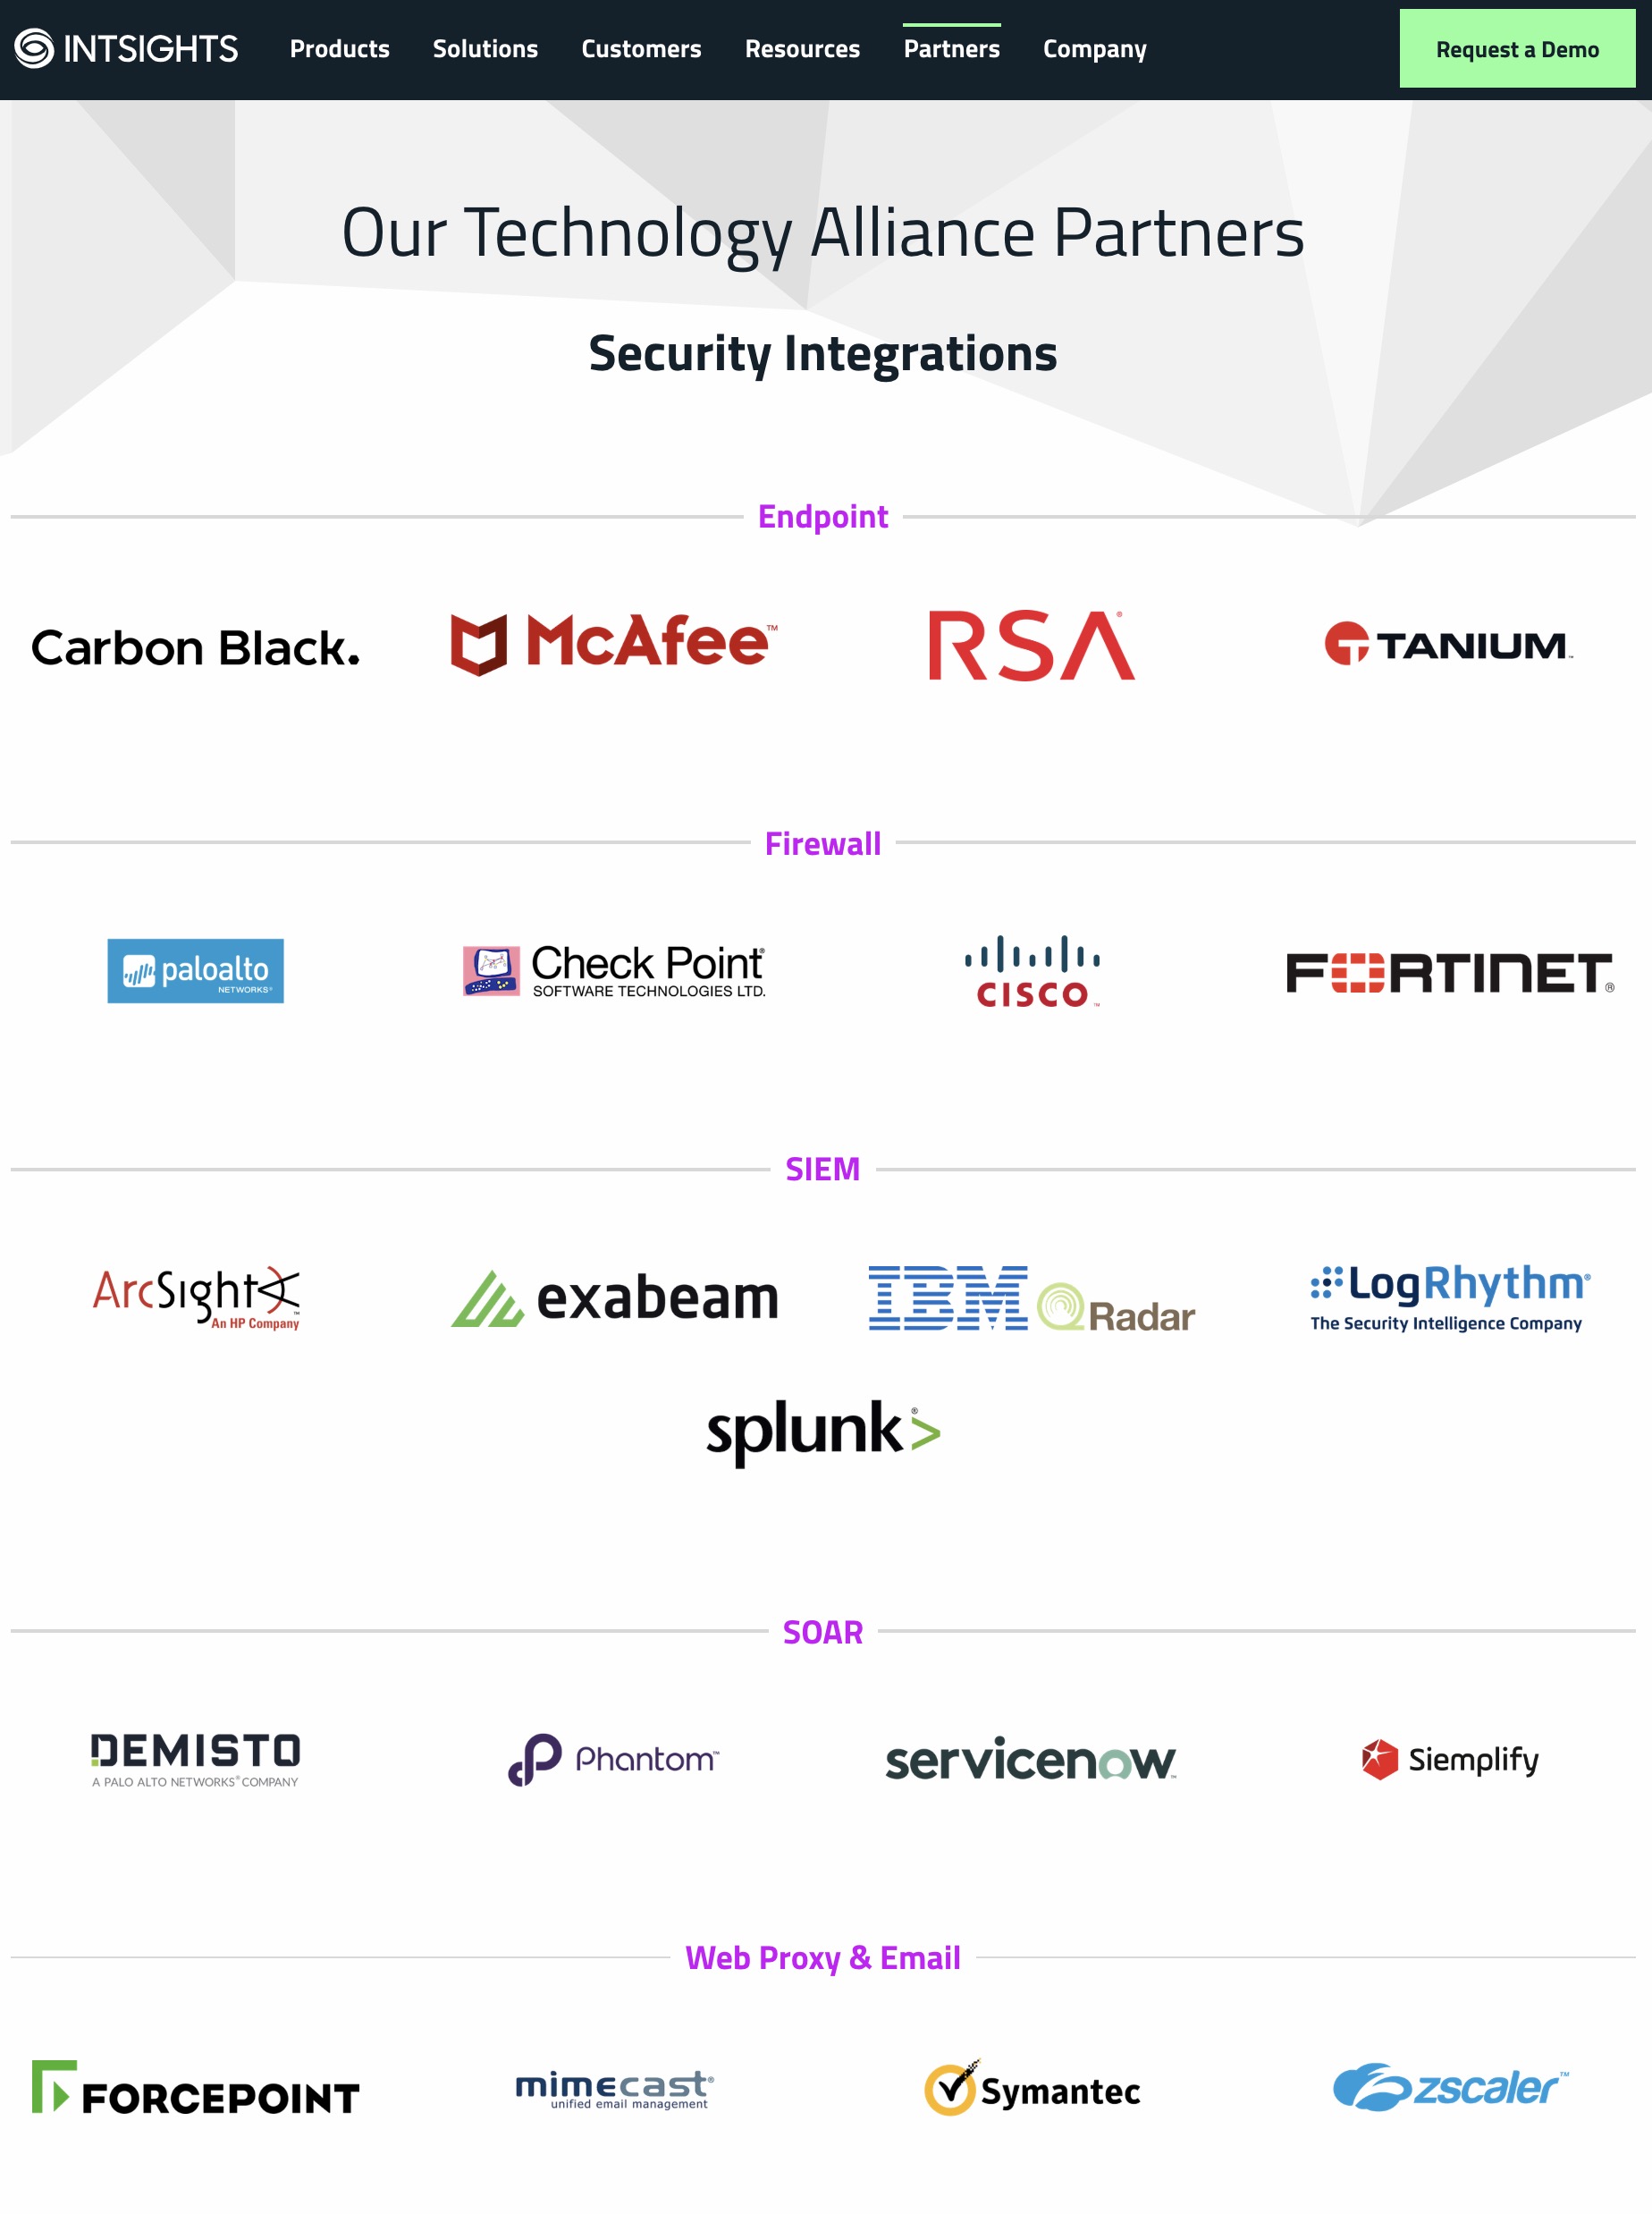
IntSights is an all-in-one external threat intelligence and protection platform, purpose-built to neutralize threats outside the wire. According to the vendor, it is the only solution of its kind. IntSights solution suite's goal is to equip cybersecurity teams worldwide to more effectively detect, assess, and mitigate threats externally from the source, well-before before they reach the perimeter. IntSights four core offerings are: Threat Command™ Threat Intelligence…
N/A
Zabbix
Score8.5 out of 10
N/A
Zabbix is an open-source network performance monitoring software. It includes prebuilt official and community-developed templates for integrating with networks, applications, and endpoints, and can automate some monitoring processes.
It has been a brilliant tool and we have harnessed it for so many applications - Threat intelligence, Risk Analysis, Automation, Endpoint protection, Vulnerability Management, Application Security, Protecting all our Cloud Applications. We love the fact that we only have to see those threats that are meaningful to us. We don't need clutter and endless dashboards with information that just gets in the way and makes things complicated. By having this full, crisp, easily discernible visibility, our decision-making is enhanced and we can see clearly what's happening in real time. We also love the fact that if a dashboard isn't proving to be productive, then we can go ahead and scrap it, and create another one. The tailor made/bespoke aspect of the Application is the thing that really sets it apart. By having all our dashboards aligned, our teams are all working from the same page and it means we are safe in the knowledge that our systems and applications are being monitored in the most effective and efficient ways. There haven't been any real scenarios where it has been ineffective. - perhaps just In-depth Risk Vulnerability Analytics are a bit lacking. However, I'm probably just picking hairs there.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Zabbix is great for monitoring your servers and seeing alerts when the system uses too much CPU or memory. This allowed the system Engineer to be proactive and add resources to these systems to avoid interrupting the services. Especially servers running operations applications and services. This is one of the best usages for Zabbix.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Collecting hardware data - CPU, Memory, Network, and Disk Metrics are collected and reported on.
Flexible design - It is very easy to build out even very large environments via the templating system. You can also start where you are - network monitoring, server monitoring, etc. and then build it out from there as time and resources permit.
Provides a "plugin architecture" (via XML templates) to allow end users to extend it to monitor all kinds of equipment, software, or other metrics that are not already added into the software already.
Very complete documentation. Almost every aspect of Zabbix has been documented and reported on.
Cost - Zabbix is FOSS software and always free. Support is reasonably priced and readily available.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is free. It didn't cost anything to implement (other than my time and the cost incurred for it) and it is filling a badly needed gap in our IT infrastructure. Support is available if we have issues and can be done annually or paid for on a per incident basis as needed. Expansion, updates, and all other future lifecycle activities are likewise free of cost, so as long as someone is able to implement/maintain the software (and the OSS project is maintained) then I imagine the company will never leave it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think every organization, especially the IT department, needs a tool like this. I know of another product like Zabbix that gives a similar or the same solution, but its range makes it very useful. You can see almost all the device info in one place: disk usage, disk space, network usage, etc.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The setup is the most time-consuming portion of using zabbix. It takes a lot of effort to shape it into a usable format and even then it can get very messy. It's not exactly intuitive and as mentioned the UI seems a bit antiquated. If I was to roll out a monitoring solution from scratch, I'd probably look for alternatives which are easier to use and maintain.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We are a mainly Windows environment, so it would be useful if we could have used Active Directory to deploy agents. As of version 4.2, Zabbix has announced a new agent MSI file to allow exactly that. Unfortunately, we didn't have that option. Also, for Linux and MAC deployments, there is no simple way to deploy that. Using remote scripts you may be able to create something, but most places will opt for either SNMP (agentless) or manual installation of agents to add to Zabbix. A way of deploying agents via discovery would go a long way to helping in the adoption of the tool.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
IntSights Cyber Intelligence, from Rapid7 was by far the clear winner, in terms of seamless integration with our exisitng systems, deployment, cleaner User Interface, ease of operation, better for monitoring Indicators of compromise and dark web information, having more features etc.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We're using the Solarwinds suite as our global monitoring standard, but it is very complex and its licensing model makes it difficult to monitor a wide range of technologies. So, we're using Zabbix as a complement on our monitoring process. Zabbix is a way more flexible and has free integrations to a wide range of technologies. It is also more 'user friendly' and easy to manage.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info