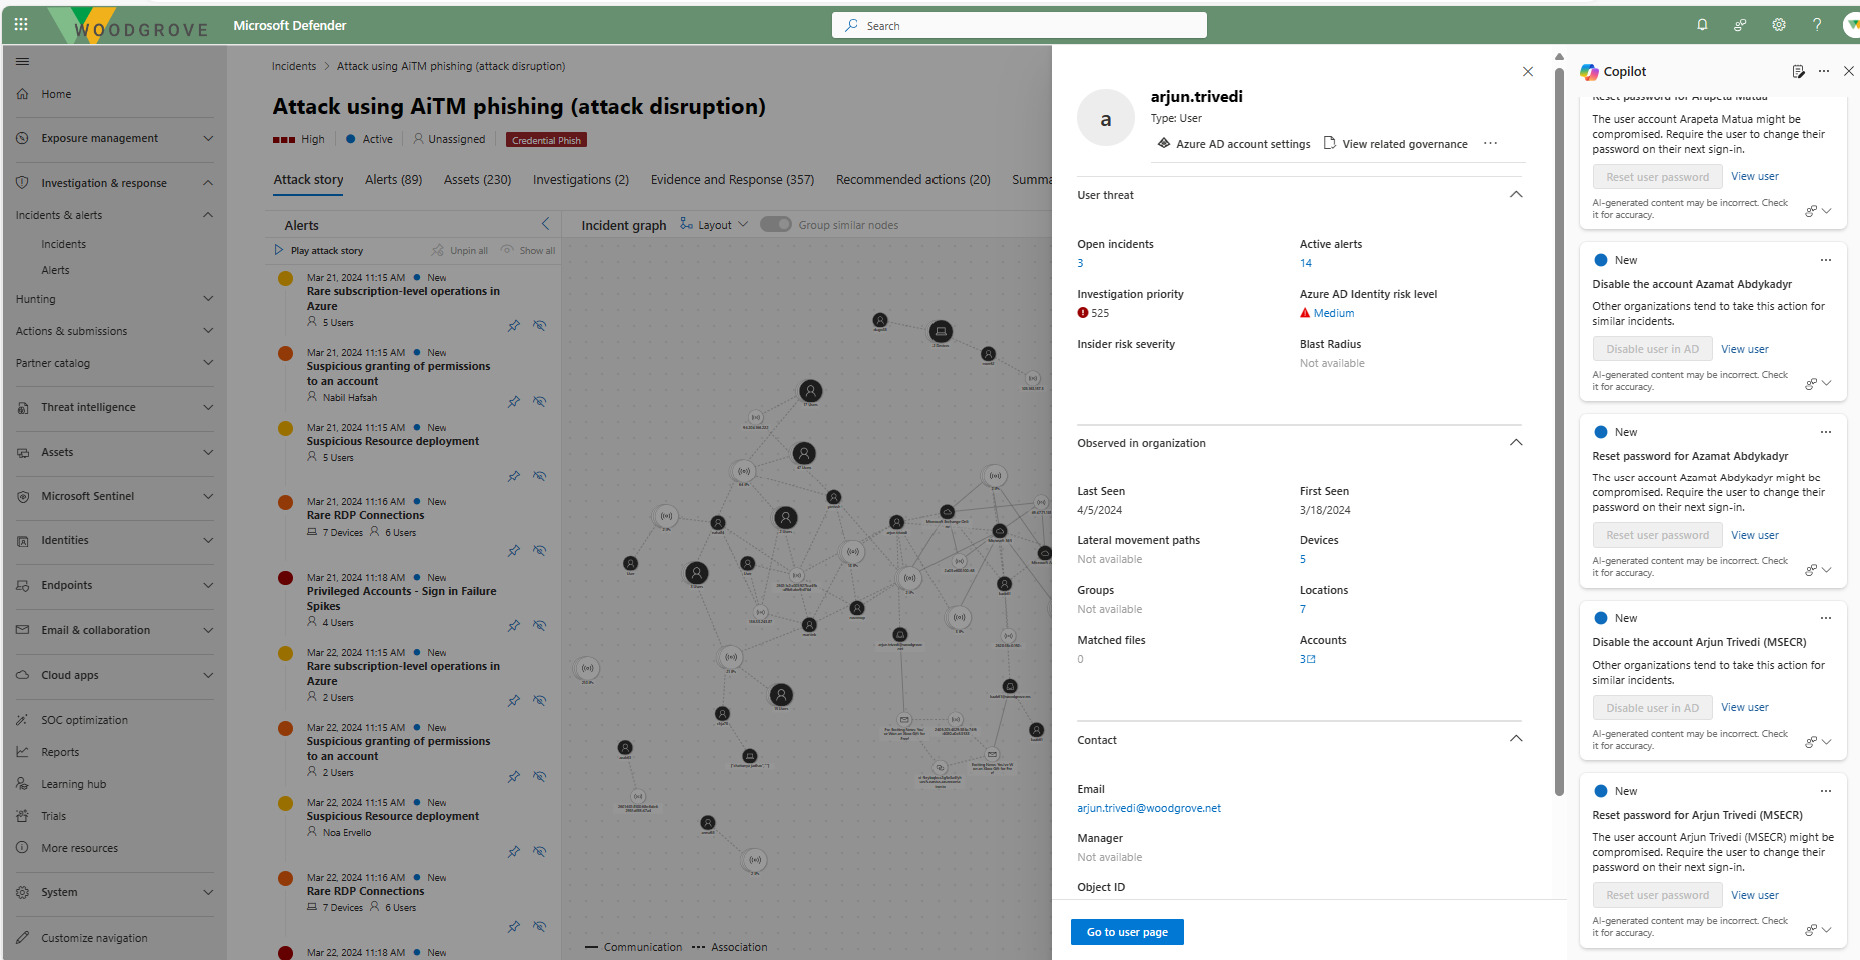
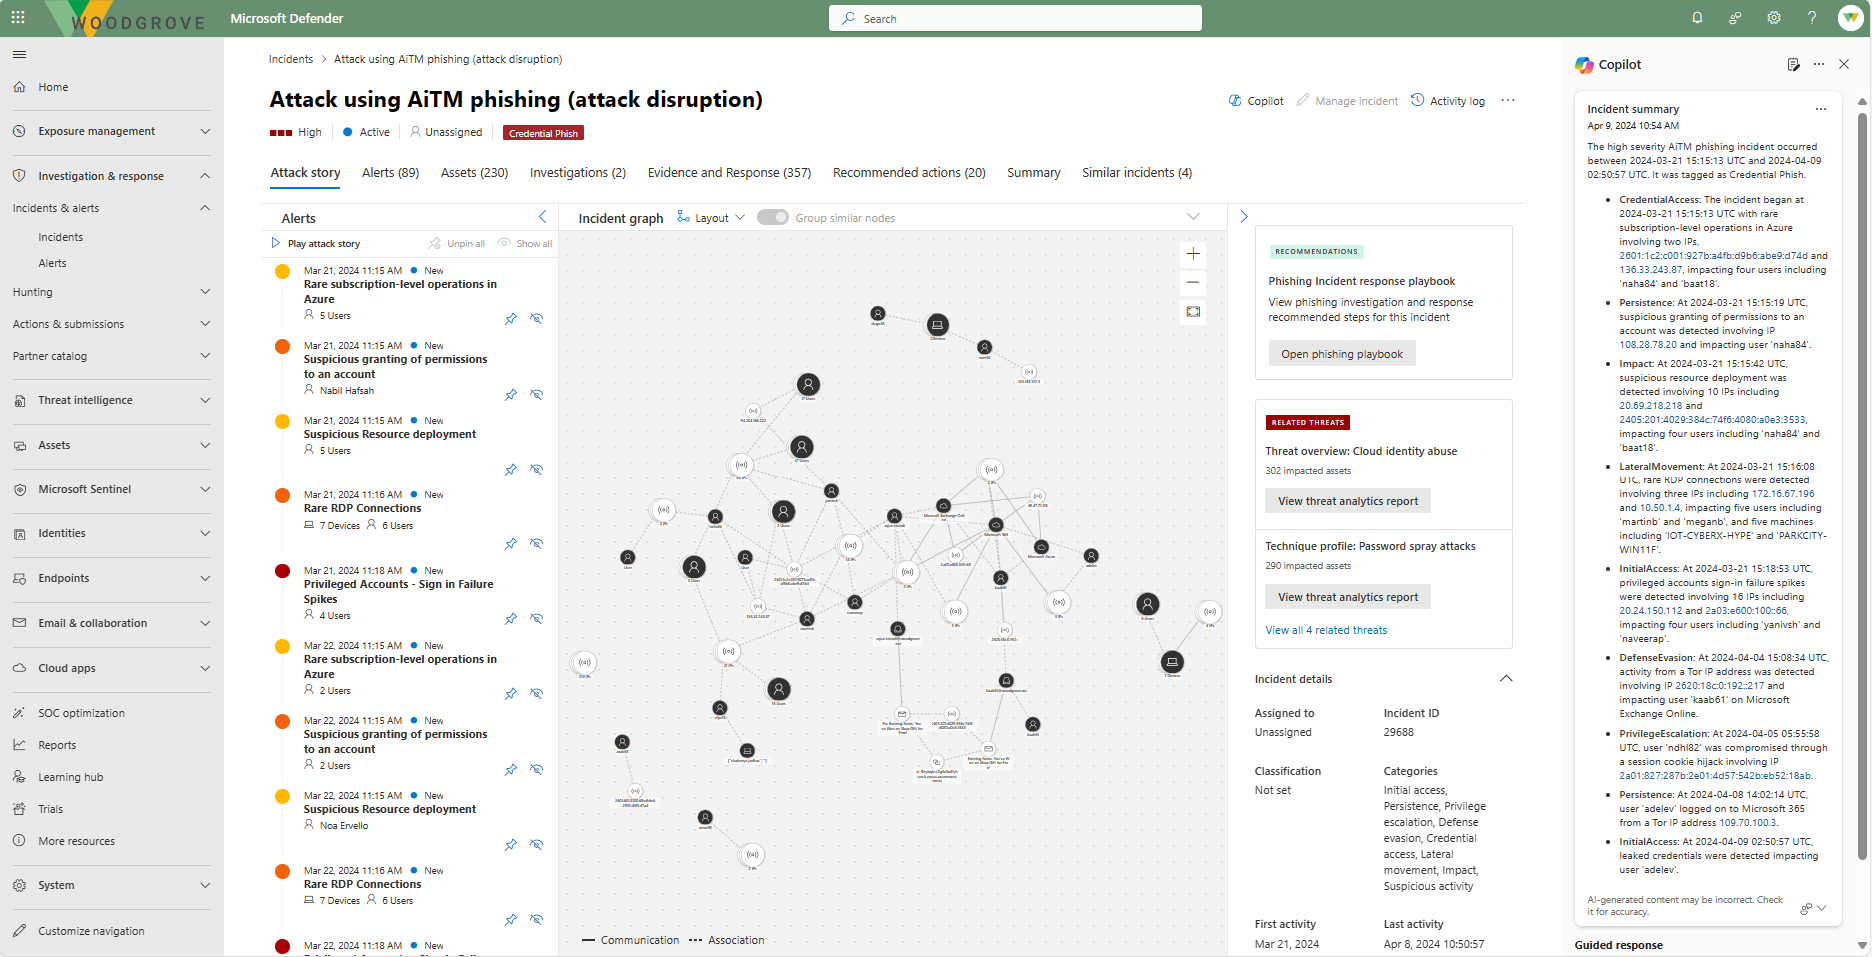
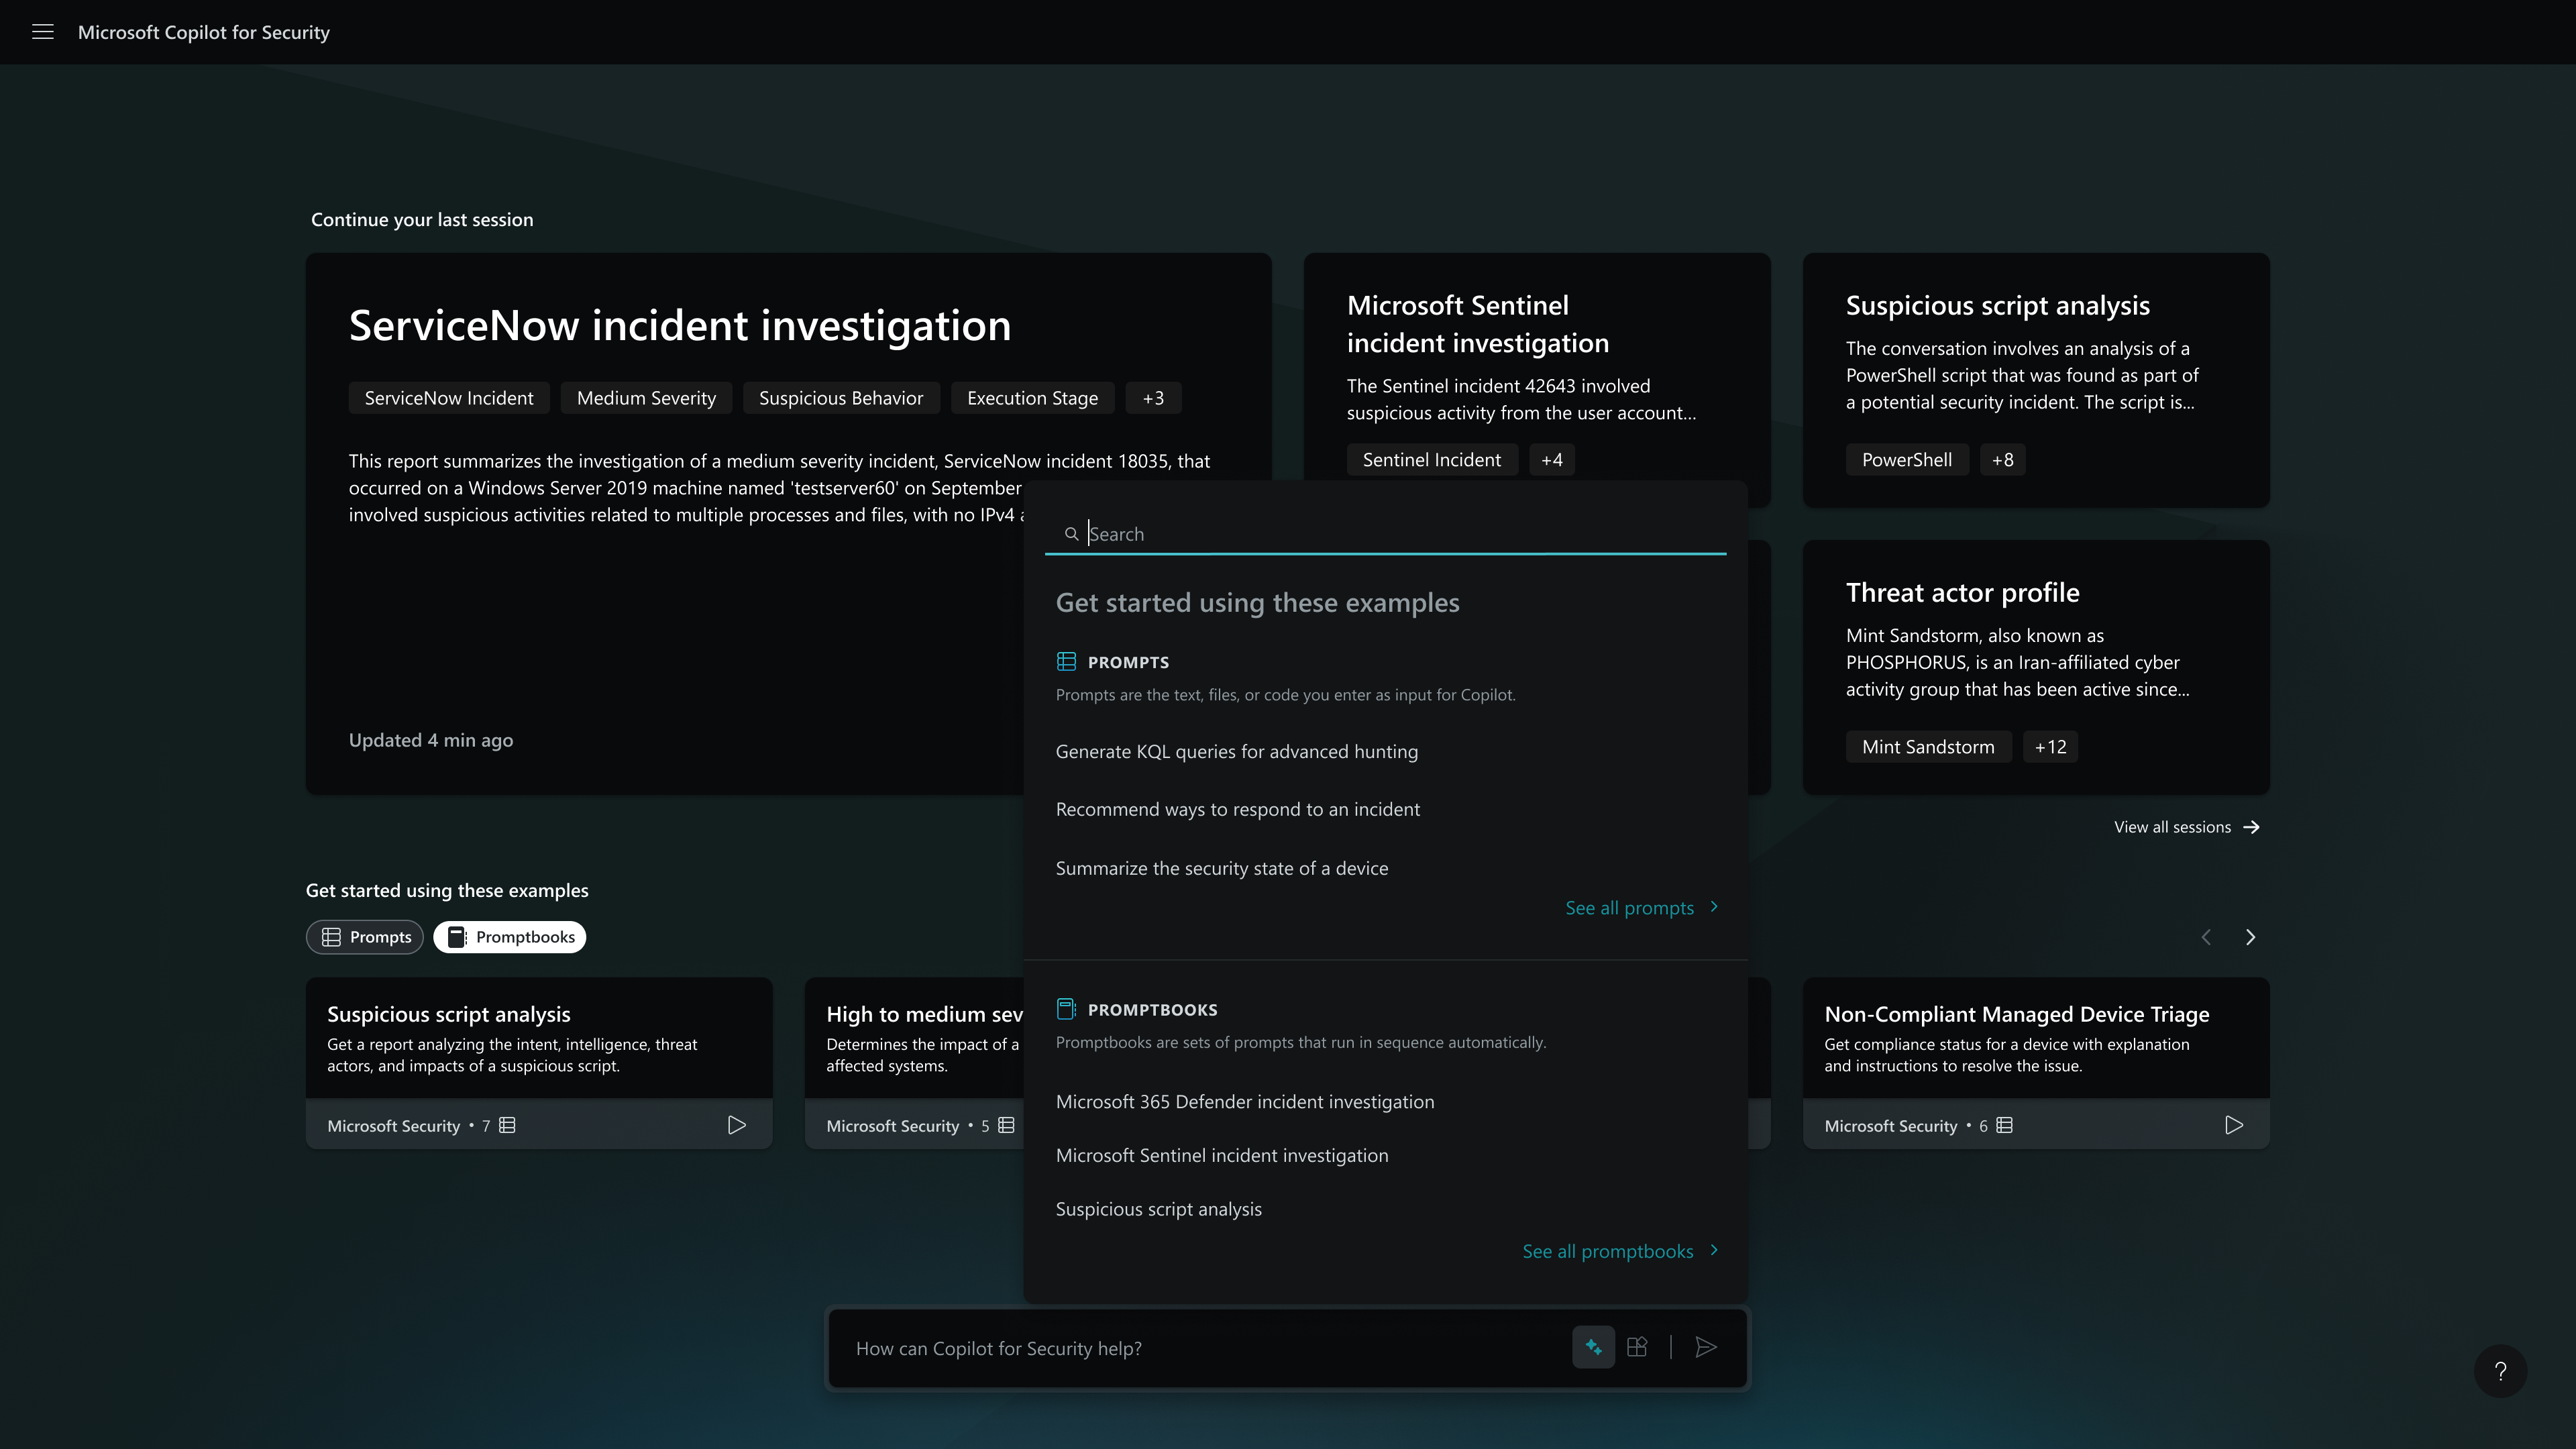
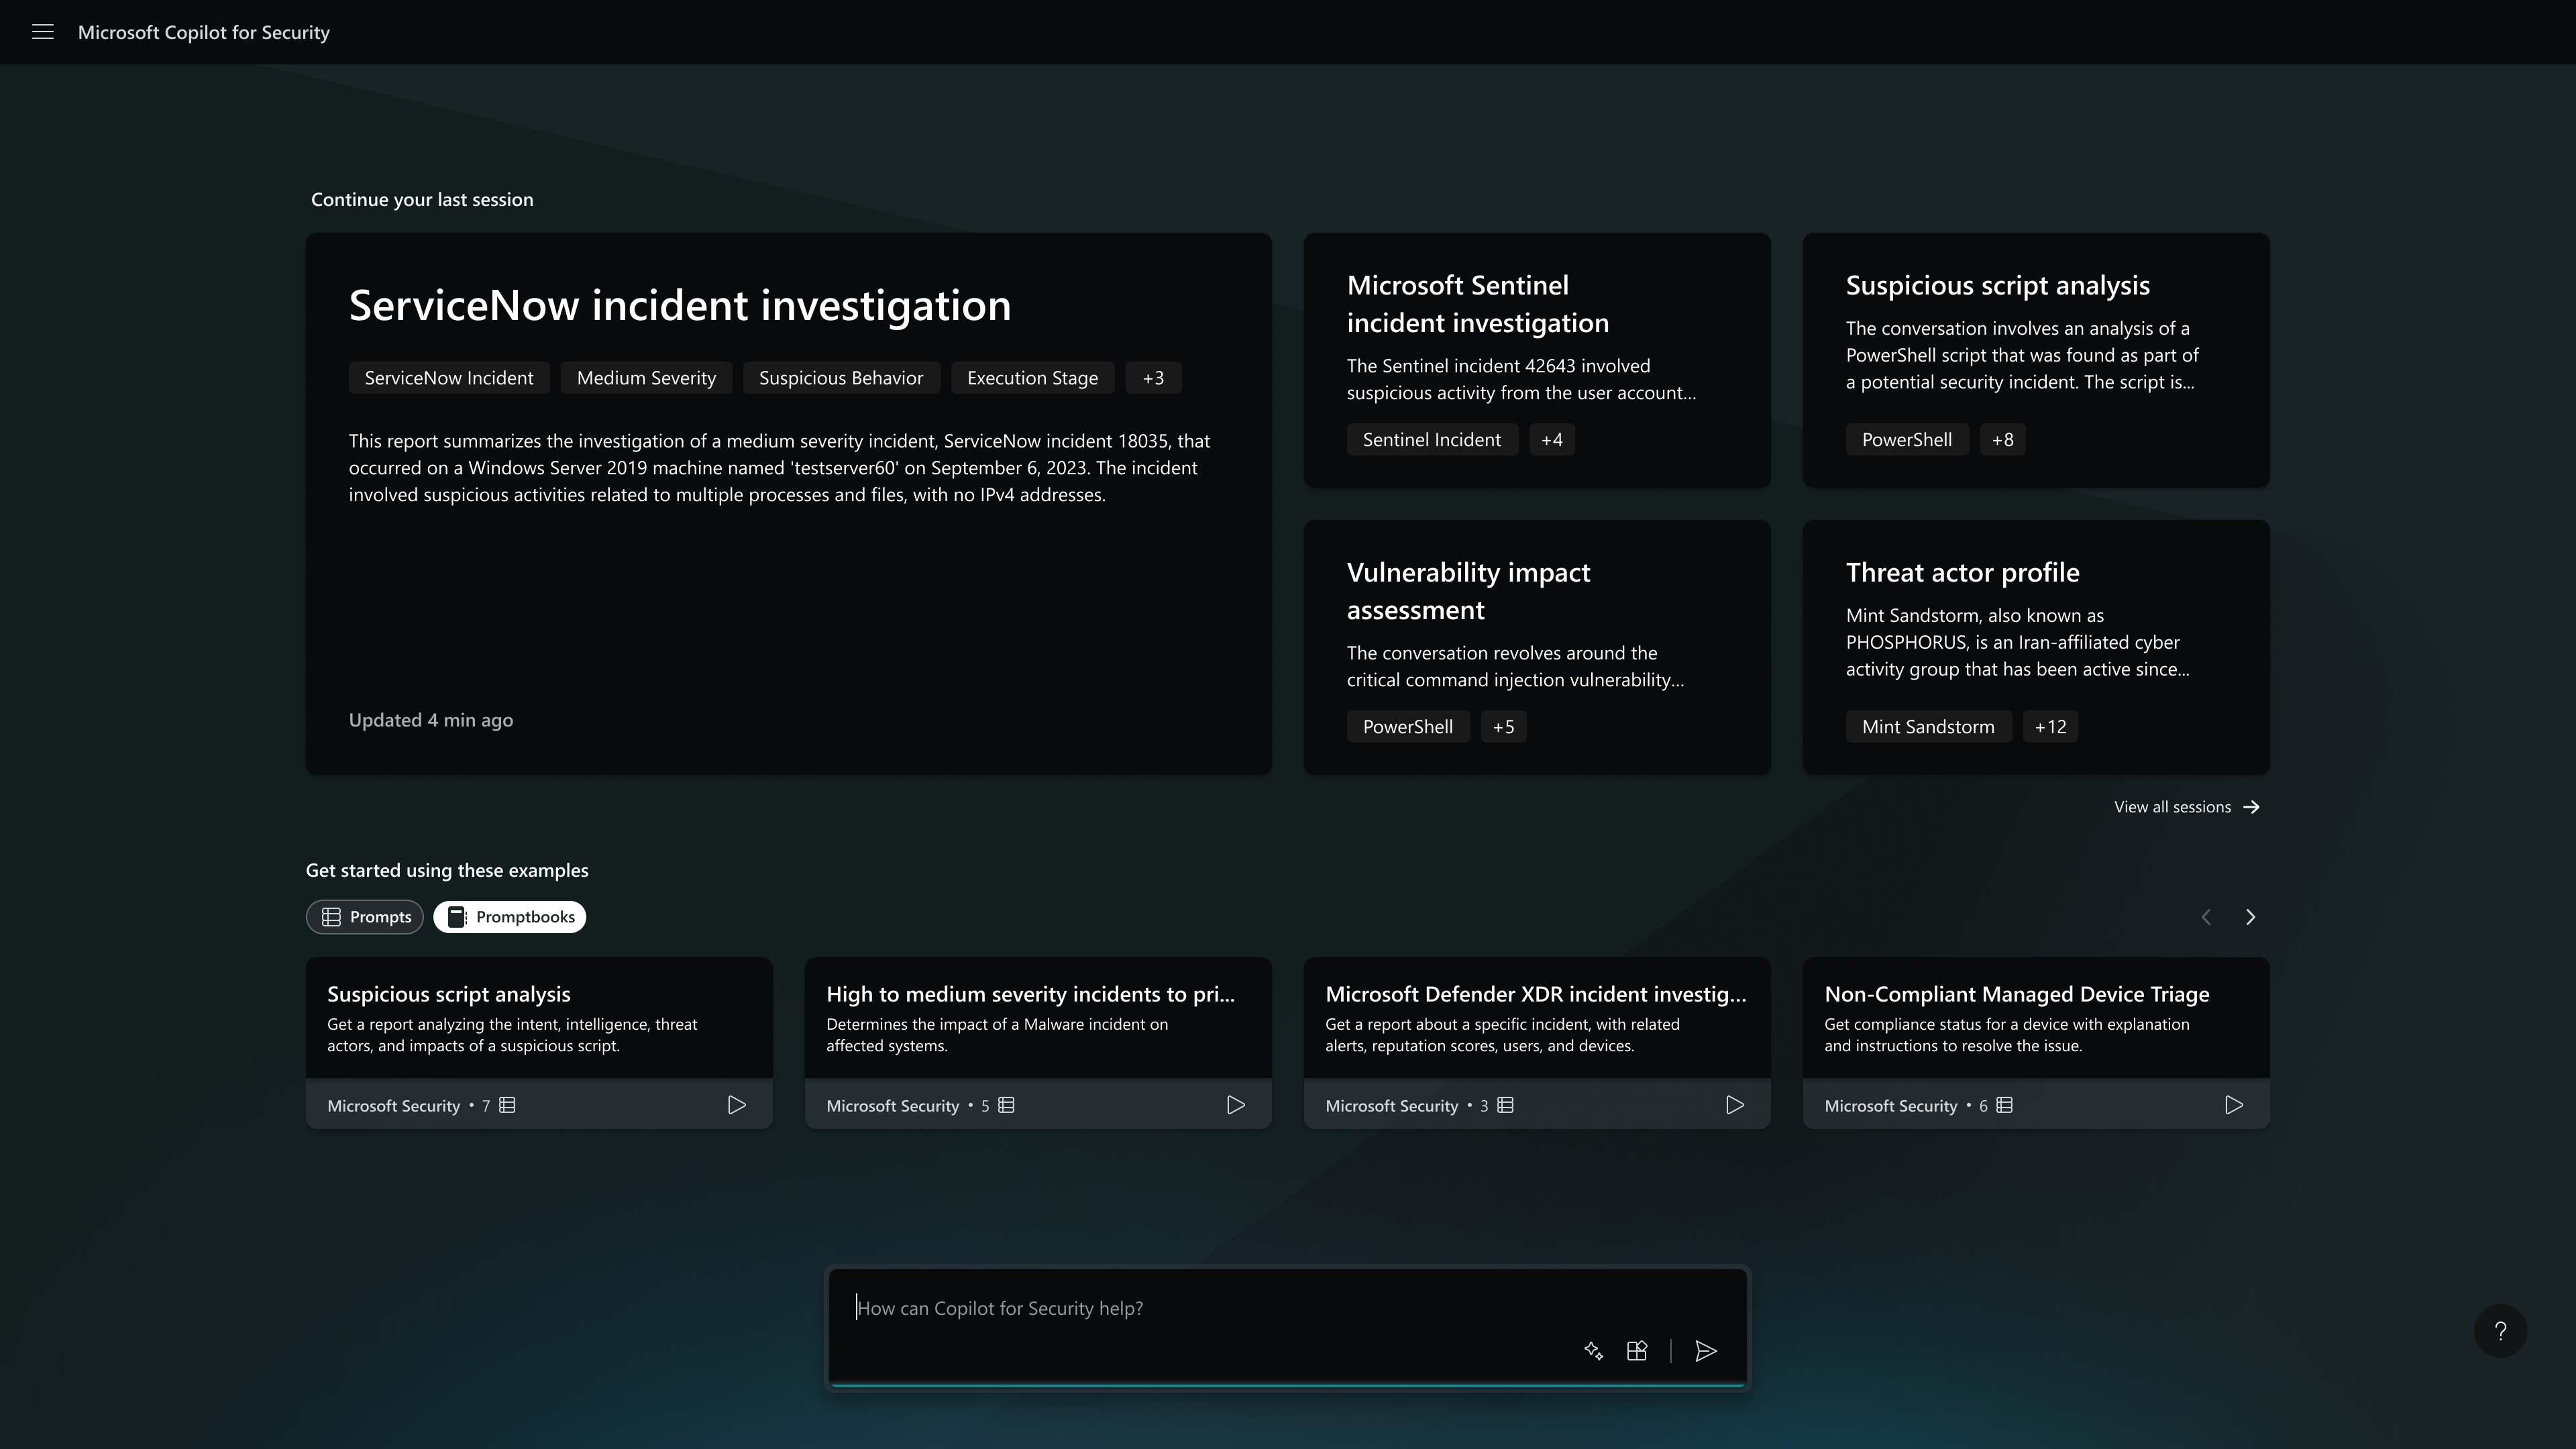
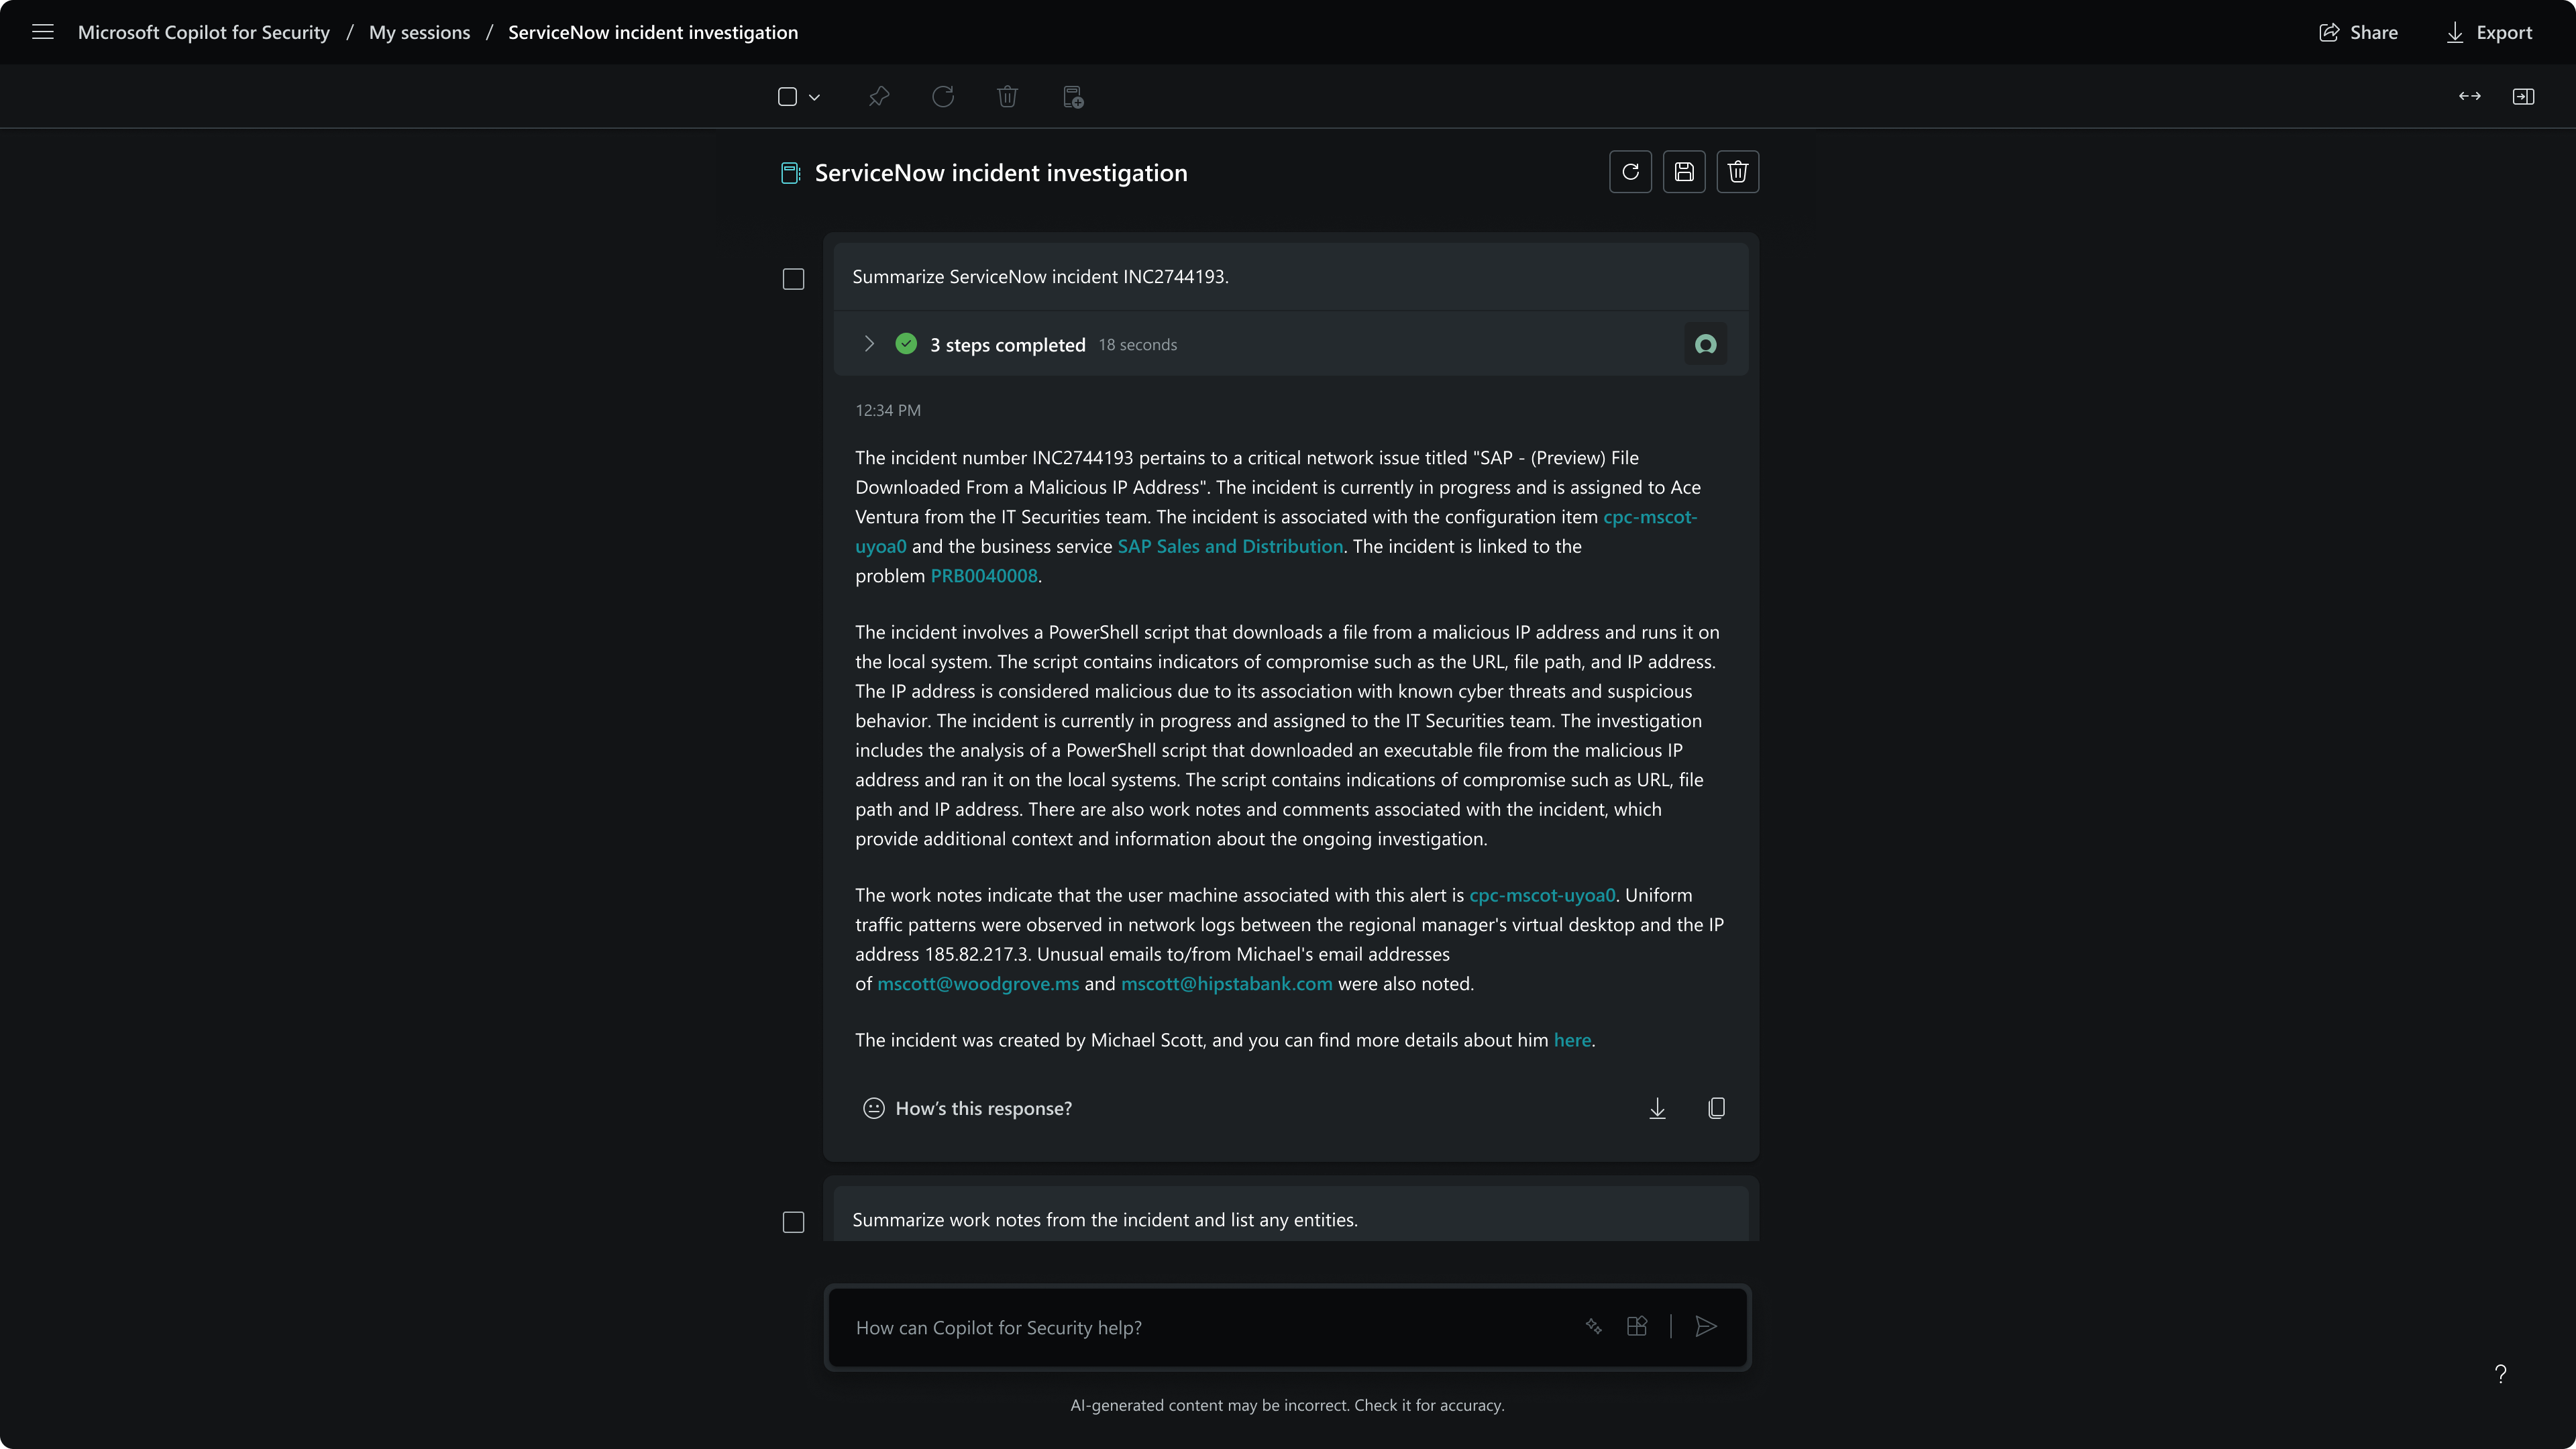
Microsoft Security Copilot helps security and IT teams to protect organizations at the speed and scale of AI. It is available in a standalone experience or embedded into other Microsoft Security products.
N/A
Splunk Enterprise
Score8.6 out of 10
N/A
Splunk is software for searching, monitoring, and analyzing machine-generated big data, via a web-style interface. It captures, indexes and correlates real-time data in a searchable repository from which it can generate graphs, reports, alerts, dashboards and visualizations.
It's easy to integrate with other tools because it's a native Microsoft solution for generating OAuth tokens and handling other integrations. But as far as querying for data, using the LLM to analyze it and find that needle in the haystack, whatever, I feel it's terrible. In my experience, it just takes so much manipulation to get it to actually do what you want it to do.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'm liking the newer products, and I'm looking forward to how they integrate with the overall product when they come together. Just log in and be able to query a large number of systems for similar issues or a unique one. That is a great fit for Splunk Enterprise, looking for a simple case or a simple String or something of that nature across multiple machines. It's a great fit for that to identify issues or particular software, whatever your scenario is, String, to find it across any particular server or group of servers, so that you can update or do a deployment or whatever it is you're looking to do.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sometimes people don't know how to do a certain feature, especially in Excel, for example. It's a little bit more complex and a community for certain people. And with just a couple of questions about using Microsoft Security Copilot, they can get their answers ready, not having to get support from IT, right? So it eliminates multiple tickets and support from personnel on our team, and they can get the response themselves via this assistant.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I don't have that as of yet. I do like the product for now. I'm sure that as I use it more, I will find things that can be improved. Just understanding how it integrates with the Microsoft ecosystem, it works just fine for what I use it for.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We are not going to stop using M365 and our environment is large enough that there is not enough in-house expertise to handle all aspects of security, even with the help of a MSSP. Security Copilot helps us shore up the knowledge gap and keep our organization's security posture tight.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We are using Splunk extensively in our projects and we have recently upgraded to Splunk version 6.0 which is quite efficient and giving expected results. We keep track of updates and new features Splunk introduces periodically and try to introduce those features in our day to day activities for improvement in our reporting system and other tasks.
Anyone can use it. Easy to prompt, also capabilities to become advance with custom agents. It can become custom to your workflow. Many people will have their unique experiences to share and results are generally positive. This is a growth in the product from the effect of community and adoption/usage.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
You can literally throw in a single word into Splunk and it will pull back all instances of that word across all of your logs for the time span you select (provided you have permission to see that data). We have several users who have taken a few of the free courses from Splunk that are able to pull data out of it everyday with little help at all.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Splunk maintains a well resourced support system that has been consistent since we purchased the product. They help out in a timely manner and provide expert level information as needed. We typically open cases online and communicate when possible via e-mail and are able to resolve most issues with that method.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The online course was simple clear and described the main capabilities of the solution. There is also an initial module that can be done for free so anyone can familiarize themselves with the functionality of this solution. On the other hand, however, there could be more free online courses. Maybe even with a certificate, this would broaden the group of people who are familiar with the platform while increasing familiarity with the solution itself.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
My usage of other products is based on SIEM tools. So far, Microsoft Security Copilot is the only product I've seen that works across multiple technologies/products to provide full visibility into security tooling using AI. I know other vendors are working towards this, but Microsoft has definitely taken a lead.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A lot of products have natively inside their own dashboards and or their own logging repositories. And each one is difficult to learn or they're too complex or they're not verbose in the sense that they're not easy to mine the data that you're looking for. So that could be anything from the native logging that you find in other Cisco products. It's easier to use Splunk to draw the data that you're looking for as opposed to going to the individual's products themselves to get the logs that you're looking for.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I'd say it was initially negative because it took us time to learn it and understand how to build the workflow around it. But since then, we've been able to speed up and adjust and adapt and move a lot faster. So it's overall.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Splunk has allowed developers to diagnose production issues when access of control was taken away from them to be allowed to view items in production environments and I believe that is invaluable.
At times some developers weren't super happy about using it, but it was more of the fact that they were used to having production access and not creating their splunk queries to get information.
Going one place to view logs was very beneficial to have.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info