A combined SIEM and SOAR, used to accelerate threat detection and response with holistic security analytics, native SOAR, and intelligent automation.
N/A
Sophos Intercept X
Score8.9 out of 10
N/A
Sophos Endpoint Protection (Sophos EPP) with Intercept X is an endpoint security product providing an antivirus / antimalware solution that when upgraded with Intercept X or Intercept X Advanced provides advanced threat detection and EDR capabilities.
$28
per year per user
Pricing
OpenText Threat Detection and Response
Sophos Intercept X
Editions & Modules
No answers on this topic
Intercept X Advanced
$28
per year per user
Intercept X Advanced with XDR
$48
per year per user
Sophos Managed Threat Response
$79
per year per user
Offerings
Pricing Offerings
OpenText Threat Detection and Response
Sophos Intercept X
Free Trial
No
No
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
—
Pricing is for a 3-year commitment. Government and Education pricing available.
In the current lot of hundreds of SIEM solutions out there in the market, ArcSight ESM is fairly less expensive with strong fundamentals in place. The log ingestion, correlation are very well performing and totally worth ROI. However, the tool has lost its way when it comes to staying abreast with current feature curve of SIEM technology and the evolution has not been done by MicroFocus. Search times are high and there is no major plug-in that has been introduced as part of the product life cycle.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
To be frank, this product is fairly expensive. So I would recommend this to companies that are mid-sized or larger to condone the cost of the purchase. It does save me a significant amount of time in my day - being able to glance at the dashboard and see if there are any outstanding issues that require my attention, as not much digging must be done to accomplish this. So for our company, with a short-staffed IT department, it's incredibly helpful to us. We also qualify for Educational pricing which brings the cost down - which helps tremendously
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Integration with smart logger and ESM to create rules and easy management of the same.
Easy integration with all end point security management tool(IPS/IDS, Firewall, Anti-Virus) and their consolidated output at a single place to effectively rectifying true and false positives.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sophos Intercept X is great at preventing malware infections and rolling back their effects. I have seen this happen hundreds of times since we installed it
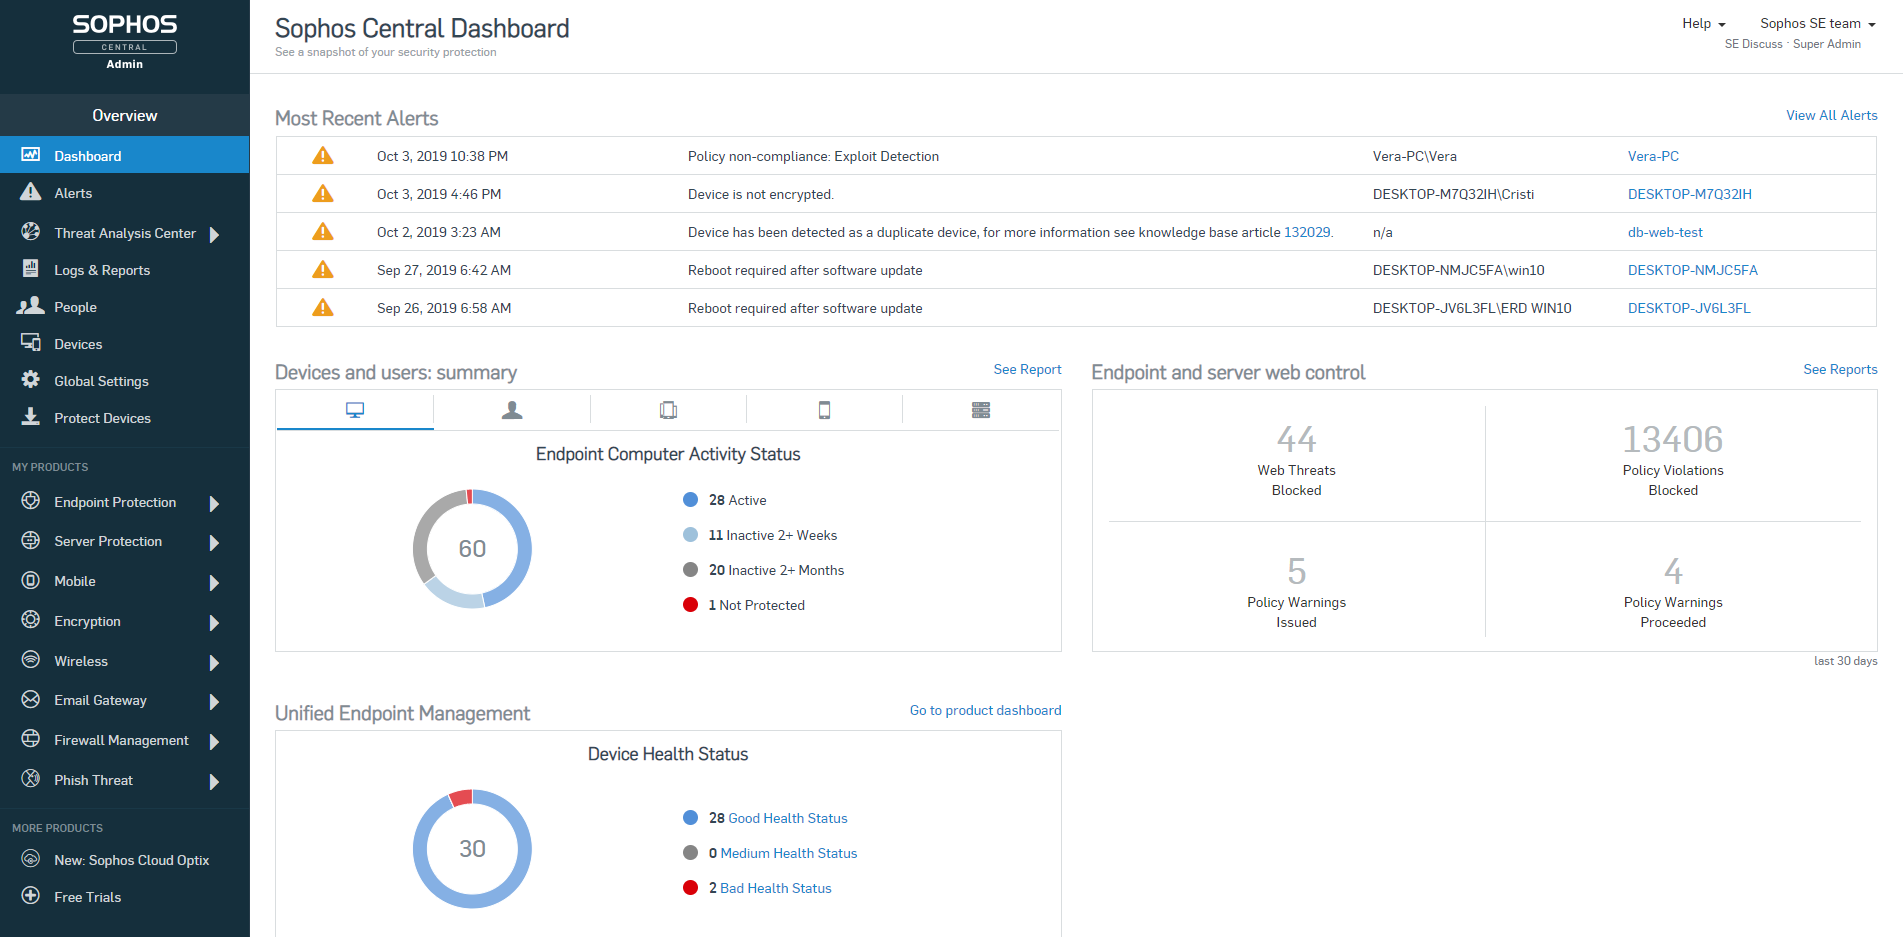
When combined with Sophos Central, you have an easy to use dashboard where you can manage all installations from a single pane of glass.
It's easy to deploy on machines and stays updated.
Good reporting features including alerts sent to the admin if there's ever something wrong with it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sophos OOTB policies are very strict and they don't offer anything less strict without you creating new custom policies. I'm sure this is deliberate because the product starts you out in the safest way possible but it means that you will have lots of calls to your tech support desk when you first deploy it unless you do somewhat extensive testing beforehand.
Sophos Intercept X is currently broken (at least the DLP component) by having secure boot turned on in the UEFI/BIOS. If any user wants to be able to write data to a USB drive or floppy from their PC (yes we still have a couple users who need to use floppies) we have to turn off secure boot on their PC, even if the DLP policy for that user/PC combination specifies that the user and PC are allowed to write to USB/floppy. This would be a very serious problem if it weren't for the fact that we have very few users who need to write files to USB. For us it's OK but I bet it would be a deal-breaker for others.
I don't see a whole lot of evidence that Intercept X is any different than any other anti-virus, so maybe their admin alerts just don't clearly identify when they have identified a zero-day threat or maybe we just haven't had any zero-day threats.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Overall, it is a good investment in order for an organization to stay compliant and stay secure from all the wild things happening. It is definitely a cost effective tool with some good features including correlation, log storage, reporting and dashboards. If a customer is looking for advanced set of features, then I would highly not recommend this.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The usability has never been a problem. Sophos Intercept X is a program you can install and let protect your company without much intervention. Apart from a few policies, Sophos will keep you protected better than most any product on the market. Sophos Intercept X works quite well when you are looking to "tighten your grip" on user's access to websites, programs, and add-ons.
I personally haven't reached the support team, however, the engineers never complained about the Arcsight support team. We had some issues with the tool in the past but every time we reached the support, all issues were resolved in a timely manner.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Most of the support reps are fantastic. There have been a few though that have had to be escalated via Account Manager when they haven't followed up but this is a rare instance, and often followed up by the Support Manager for APAC.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Multiple platforms are already supported by Arcsight. Support is good. Scripts can be used to get data from multiple threat intel sources & the same can be used in correlation rules to detect any suspicious activity. Reporting features are good & you can check any backdated information within new clicks.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Webroot Endpoint Protection is not even in the same league as Sophos Intercept-X. I have tested and compared both sides by side, run simulations and it's not even close. Plus the Sophos central management is so much better. Easier to view user activities and apply policies and remediate threats. Sophos is the clear winner between these two products.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Logger helps us to decrease incident response times.
It also decreased our project times with the man/day calculations. Before this solution, it may take up to 10 men/days to do something. After this, it becomes nearly half of the time.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Once our technical and commercial areas got certified, the ROI over the time spent, is great. Actual customers, and/or new ones with other tools, feel safe and advised, once they get in touch with us.
When Sophos EndPoint is being compared against Web Management Tools (competitors), we have failed to deliver, nevertheless, there is a version of Sophos Central (Cloud) which achieves this requirement at 100% and more, since is Cloud Based (on AWS).
We are grateful to be on Sophos "Radar" as a Platinum Partner, and "The Americas" valued partner, we have seen our business grow, thanks to this kind of technology, throughout the years.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info