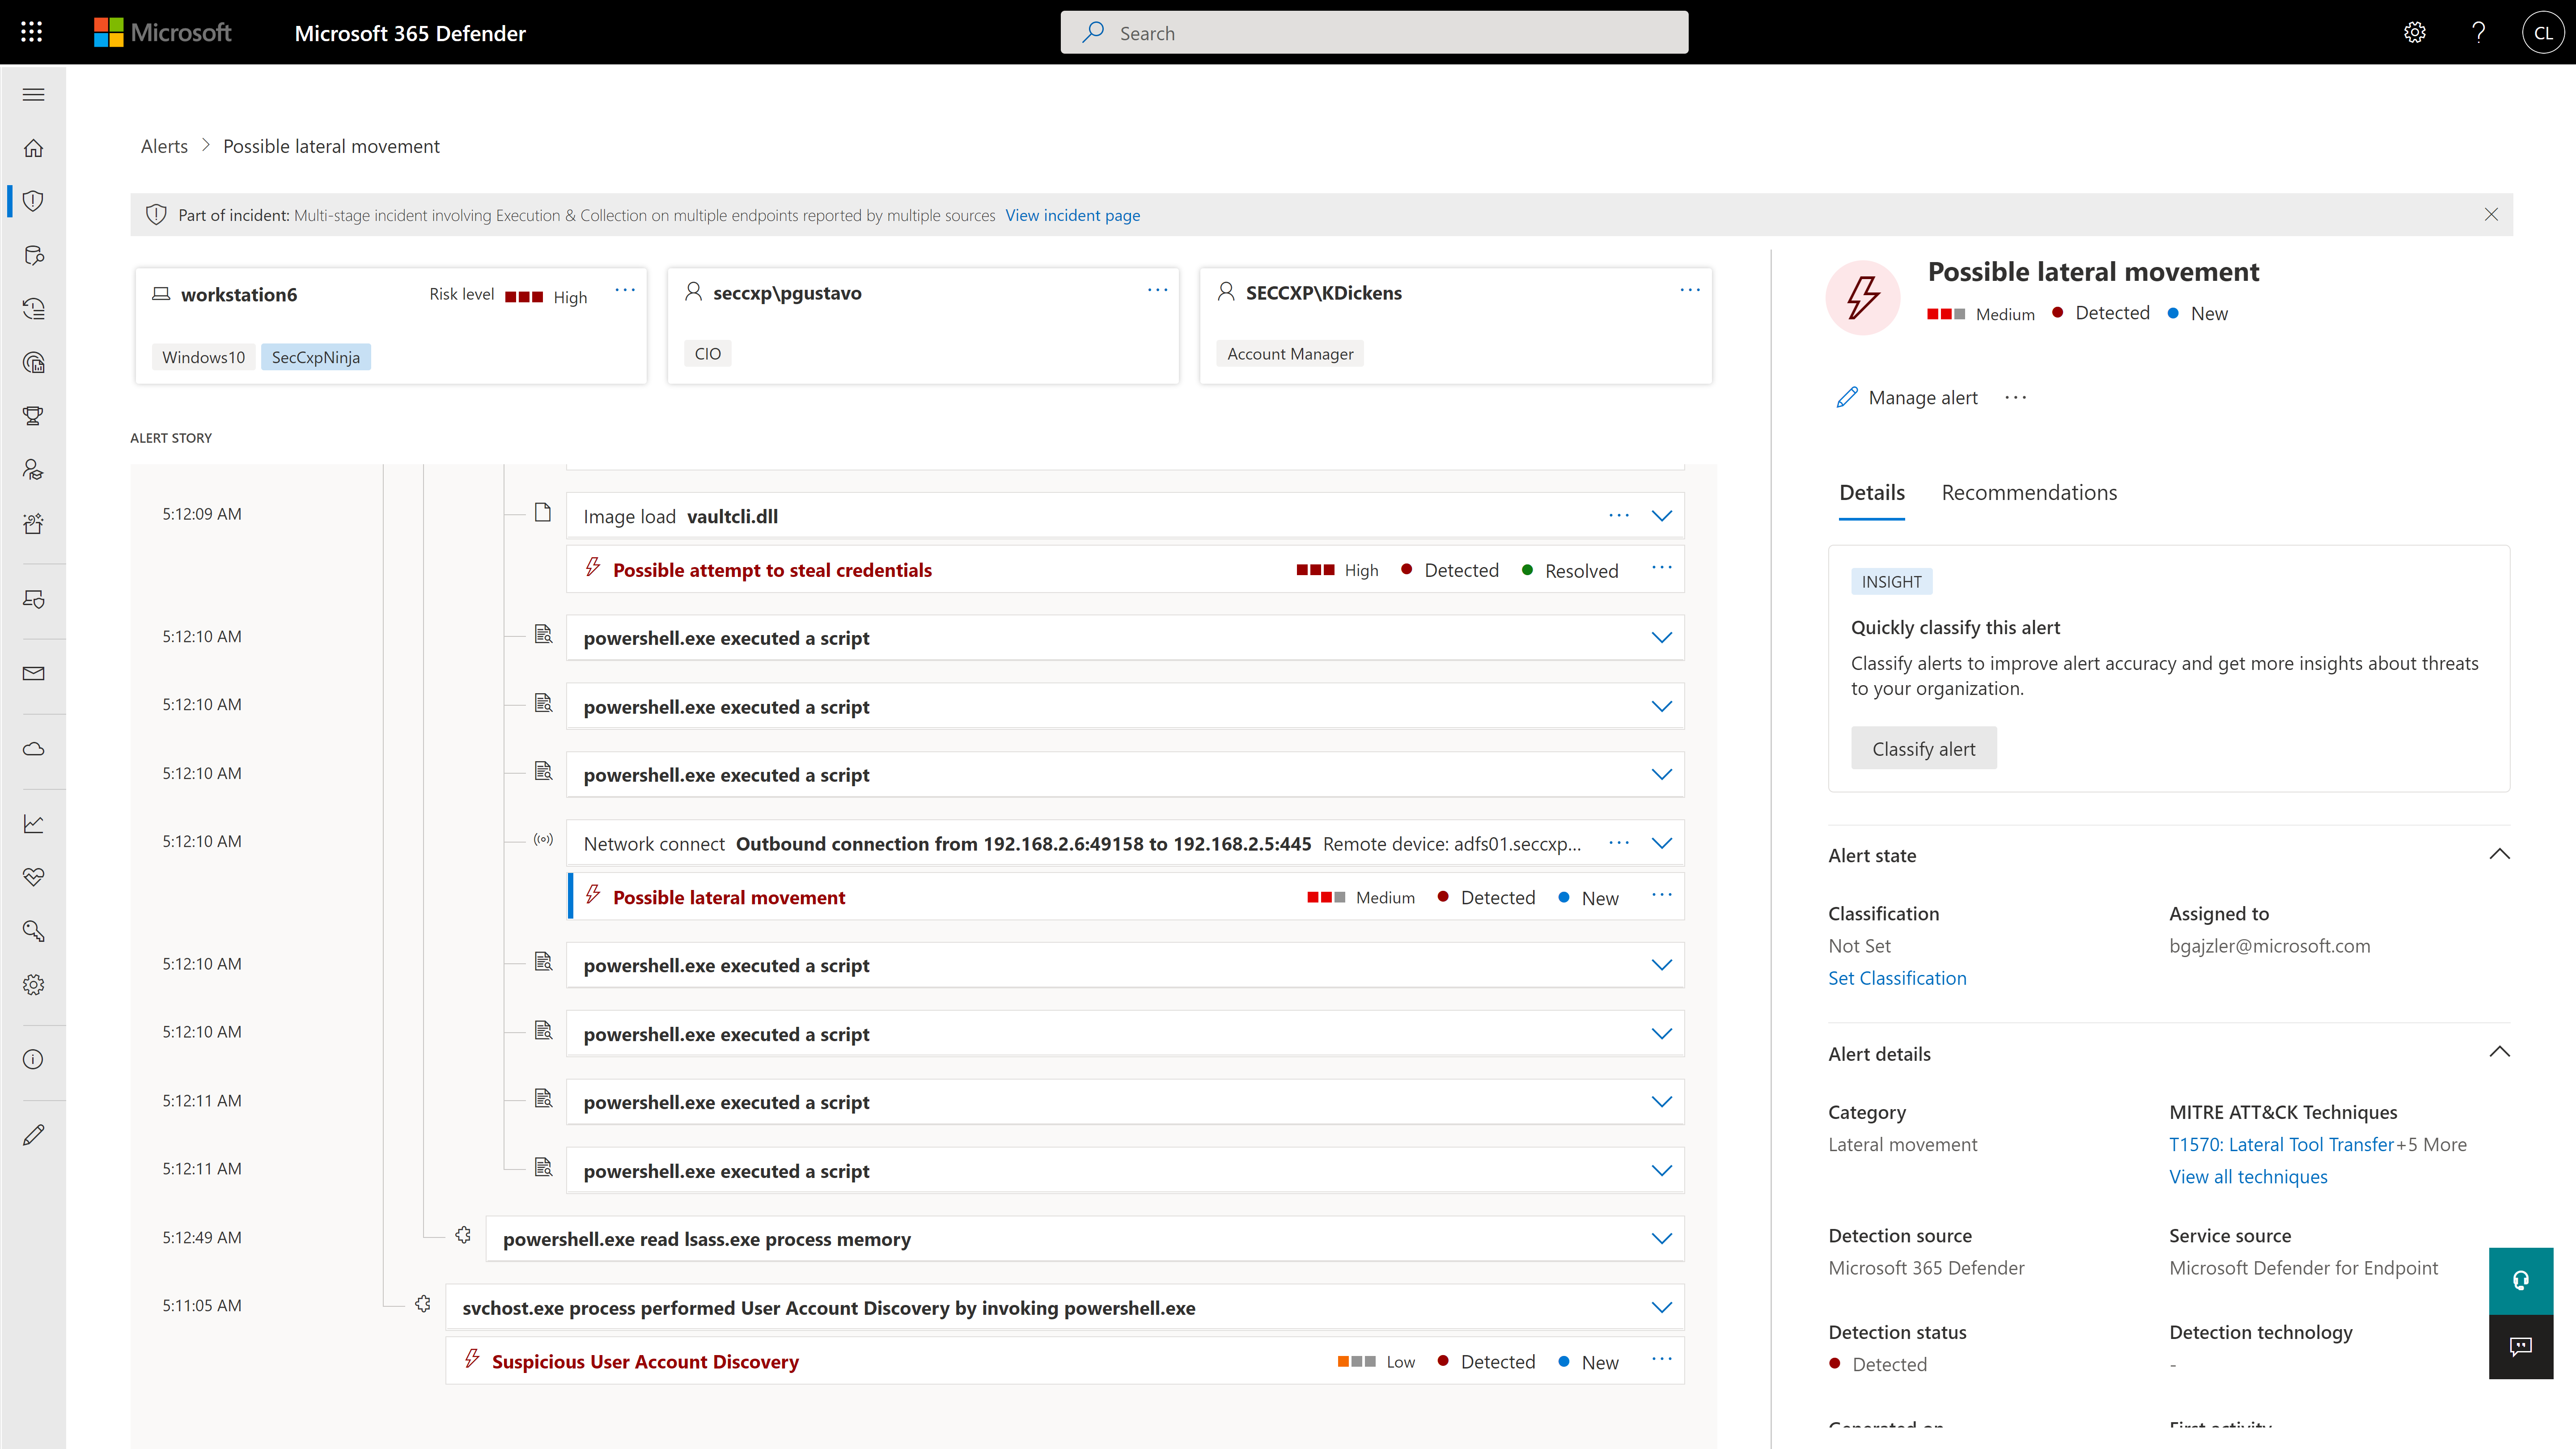
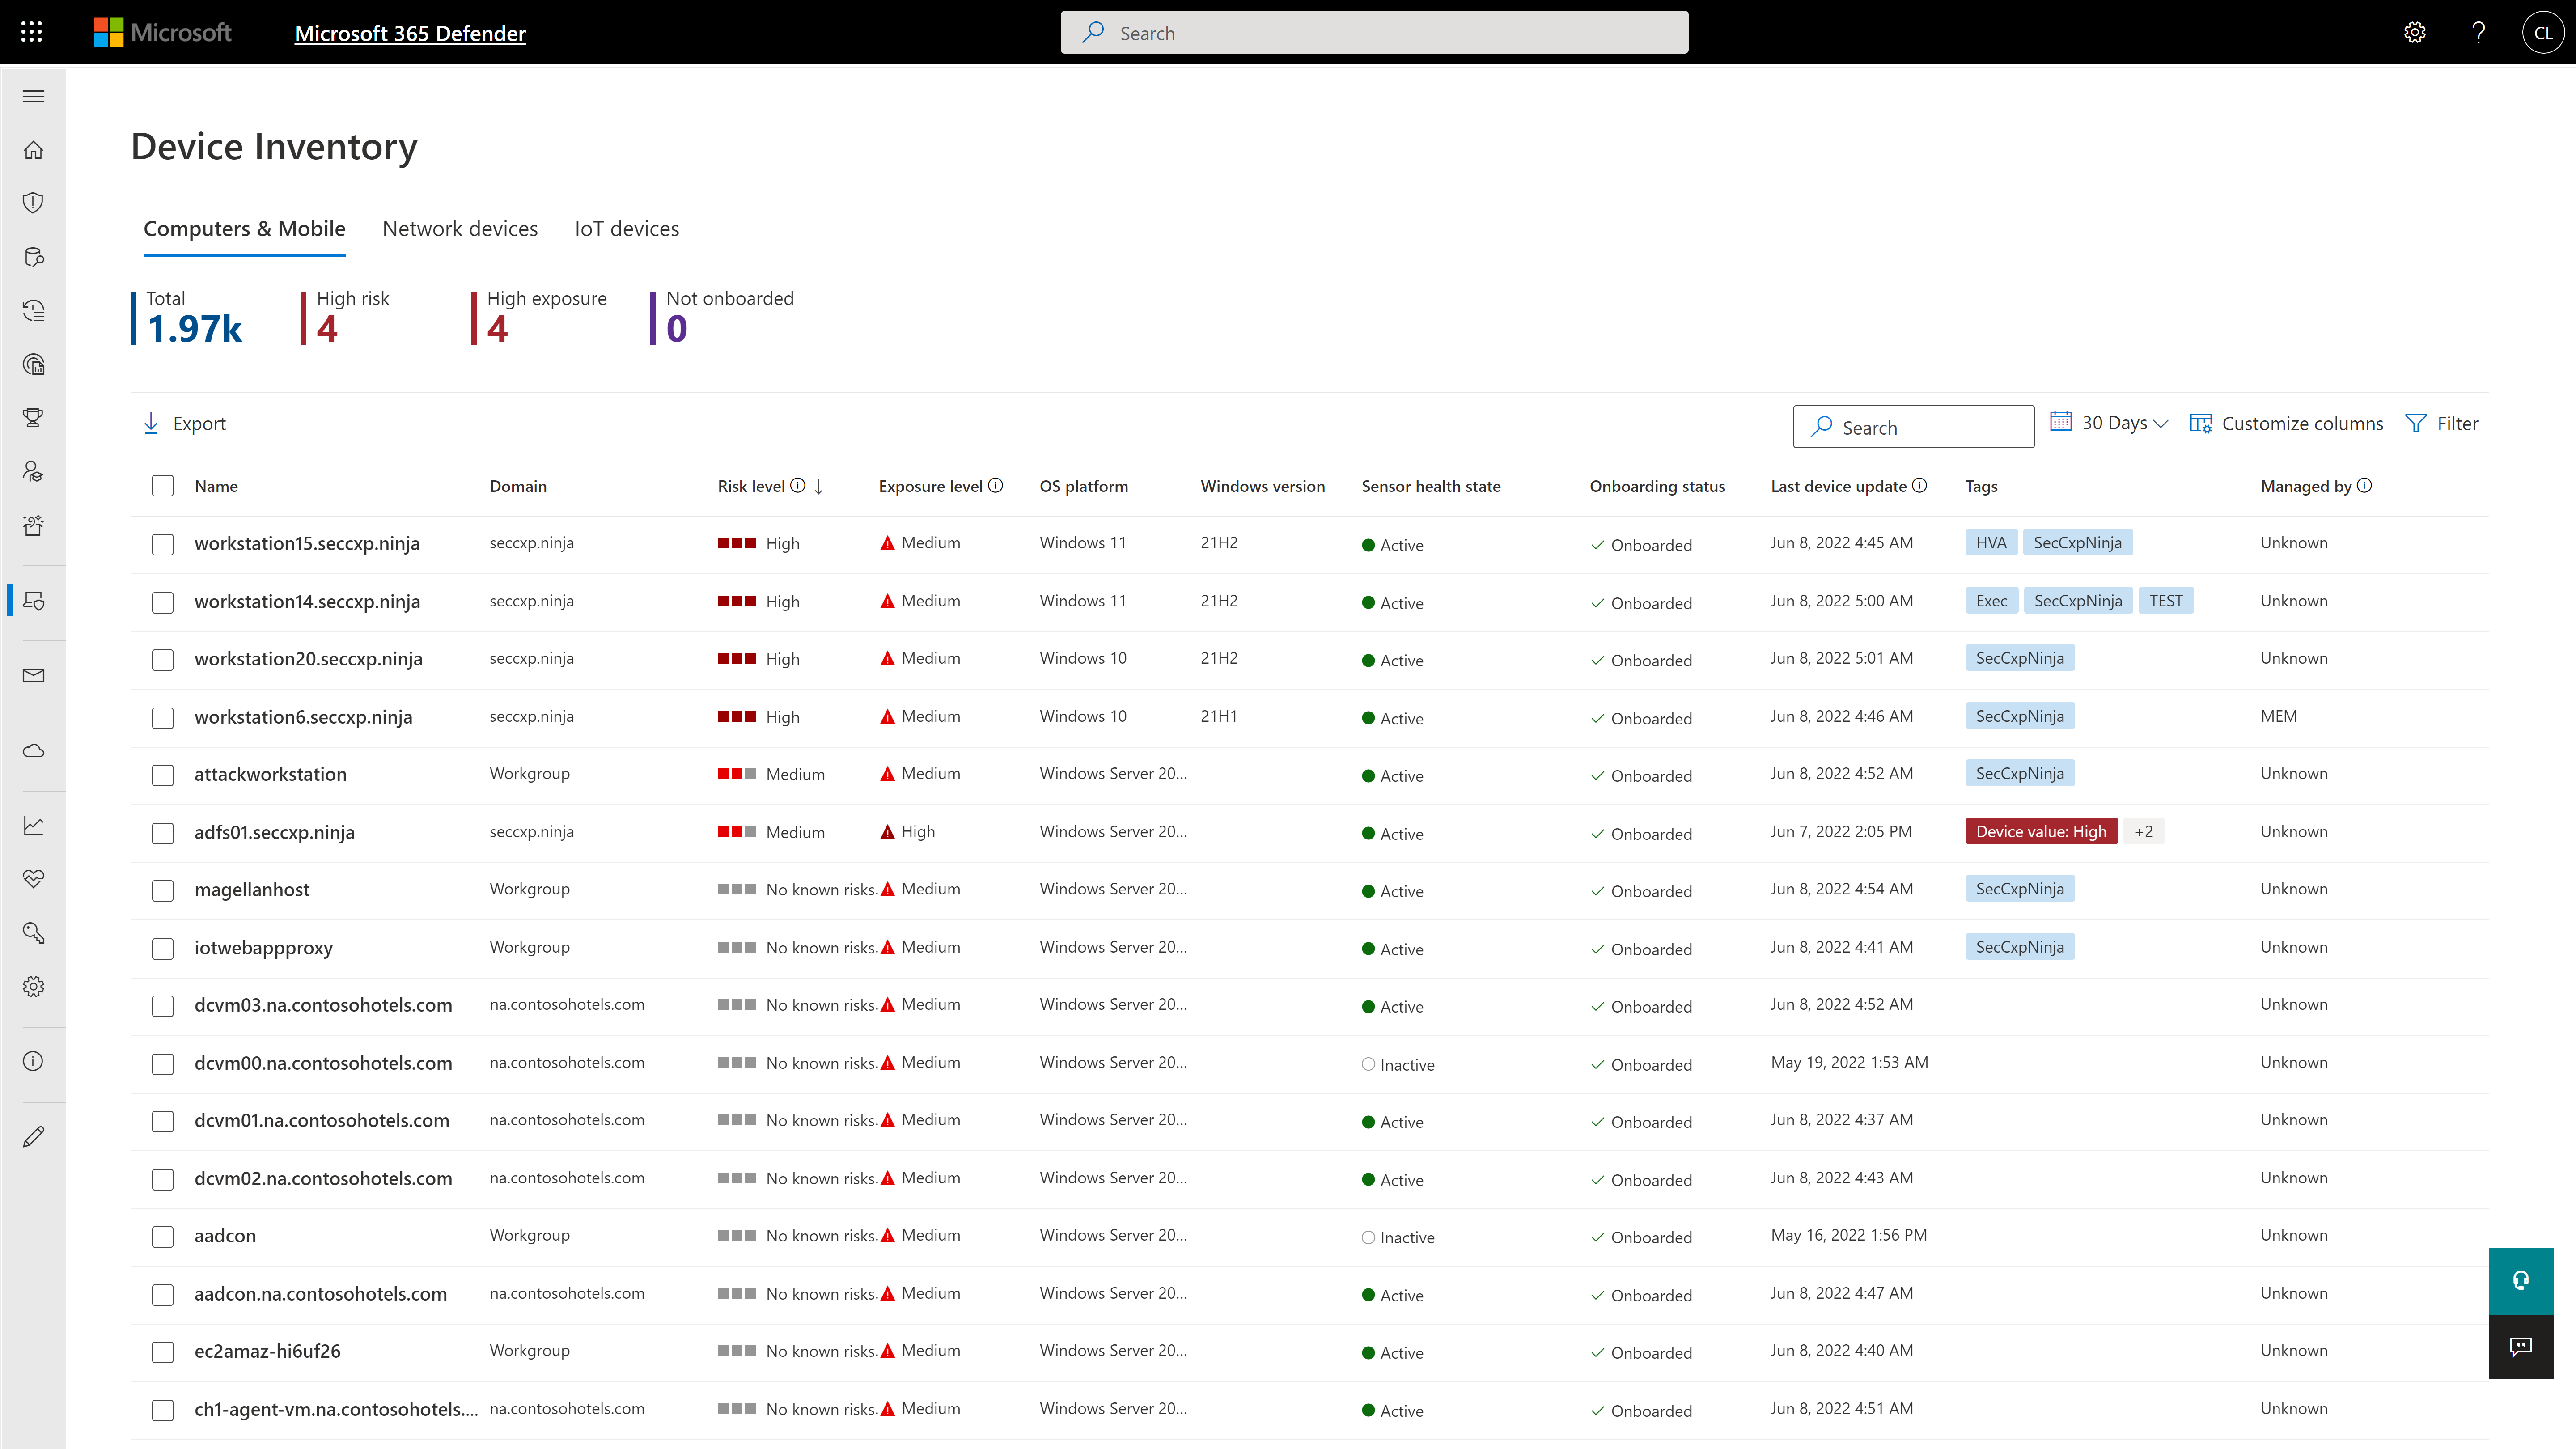
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
Trend Vision One Endpoint Security
Score8.3 out of 10
N/A
The Trend Vision One Endpoint Security platform provides antivirus and malware detection, and endpoint visibility. The product suite can be extended with associated applications that cover mobile endpoint protection, endpoint encryption, as well as network and server vulnerability protection.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender for Endpoint
In my organization we already have E5 license so no need to procured additional license for EDR functionality.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Security Solutions Architect in Information Technology at Tata Communications (Information Technology & Services, 10,001+ employees)
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint is east to deploy, hence safed lot of efforts in implementation and management. When I evaluated CrowdStrike I found that not all threats are identified in it, which was a matter of concern for us. We also had issues with configuration and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Mostly it runs smoothly on host without impacting performance as other AVs like Symantec's impacts performance issue of host. Also because it's still a good product overall price range. Can upgrade to EDR solution with not much difficulty & onboarding on tool is not that …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint is one of the best solutions when the goal is to protect the endpoints of a windows oriented infrastructure. The integrations with the Microsoft services and the unified platform that the analyst can use play a decisive role in the choice and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Before Trend Micro OfficeScan we used Symantec Endpoint Protection and although it was very easy to deploy and to update agents it couldn't find a virus if you pointed it out with a neon sign. We were always getting hit with different viruses but since we migrated to Trend we no longer have that problem. Trend has definitely been preventing those kind of outbreaks successfully.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The product has two important aspects, centralized console and an agent which is typically installed on every machine. When the product is installed on a dedicated server then all computers can readily get updated while in the same network (provided the agent is installed on every machine). This helps the machine to avoid any kind of virus attacks.
Even if the machines are not in the same network where the console is being run it can directly get all updates from the Trend Micro server directly and the machine is still protected. Hence, it is not necessary that users have to visit the office or internal network to get the update, once the agent is installed on the machine then they can get the update from anywhere as long as the machine has access to the Internet.
Once the agent is installed on the machine the users can themselves do a full scan and even check the logs themselves.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Only thing I would have to say that's negative is the reporting aspect. Basic reporting is good but still lacks some details. This is a problem with many of the software vendors I have encountered in the past as well. Reporting is still much better than most.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It is very easy to stick with a vendor year after year, and it is also easy to see the faults in a product and want to change. This is the first time I have renewed with an antiviurs provider as others have been less than ideal and caused issues where there were none before, so while it isn't perfect, it is the best of the bunch currently and I am hopeful that it will continue to improve in future versions.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The dashboard is user-friendly and allows for an IT admin to quickly deploy the software. The users do not even notice the program running in the background. From the dashboard the IT department can monitor all the workstations for issues and maintain good health of the network.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It has been difficult at sometimes, the support people at one point told me that they couldn't tell me information about OfficeScan because it was knowledge that was passed down from engineer to engineer. The issue was that if you used the msi for the install any further installs would require the msi to have the same exact name or else the install fails and corrupts the install. This information is not listed anywhere on trends website. Support kept trying to get me to use the exe for installs instead, but we use SCCM and msi's work better. We had to write a script to come up with a solution so that we could uninstall the software and install the new software. Trend did provide the technical expertise to help with the script and had us work with one of the developers in order to resolve that issue. So they did fix their screw up but it took a while and several complaints.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
For me, Trend Micro Apex One with its low performance is the best option at the time to buy a solution like this, with its flexibility through on-premises or saas deployment options you can choose the option that best fix to you, has an advanced automated threat detection and response against an ever-growing variety of threats.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Since the product is a full suite of protection rolled into a single product, we've seen ROI through cost reduction and simplified management. And while we haven't measured performance, one would logically assume that systems will perform better with a single product installed vs several.
While we haven't measured performance, one would logically assume that systems will perform better with a single product installed vs several.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info