AlienVault OSSIM was an open source Security Information and Event Management (SIEM). AlienVault was acquired by AT&T Cybersecurity, now LevelBlue, and OSSIM is no longer available for sale.
N/A
Microsoft Defender for Endpoint
Score8.8 out of 10
N/A
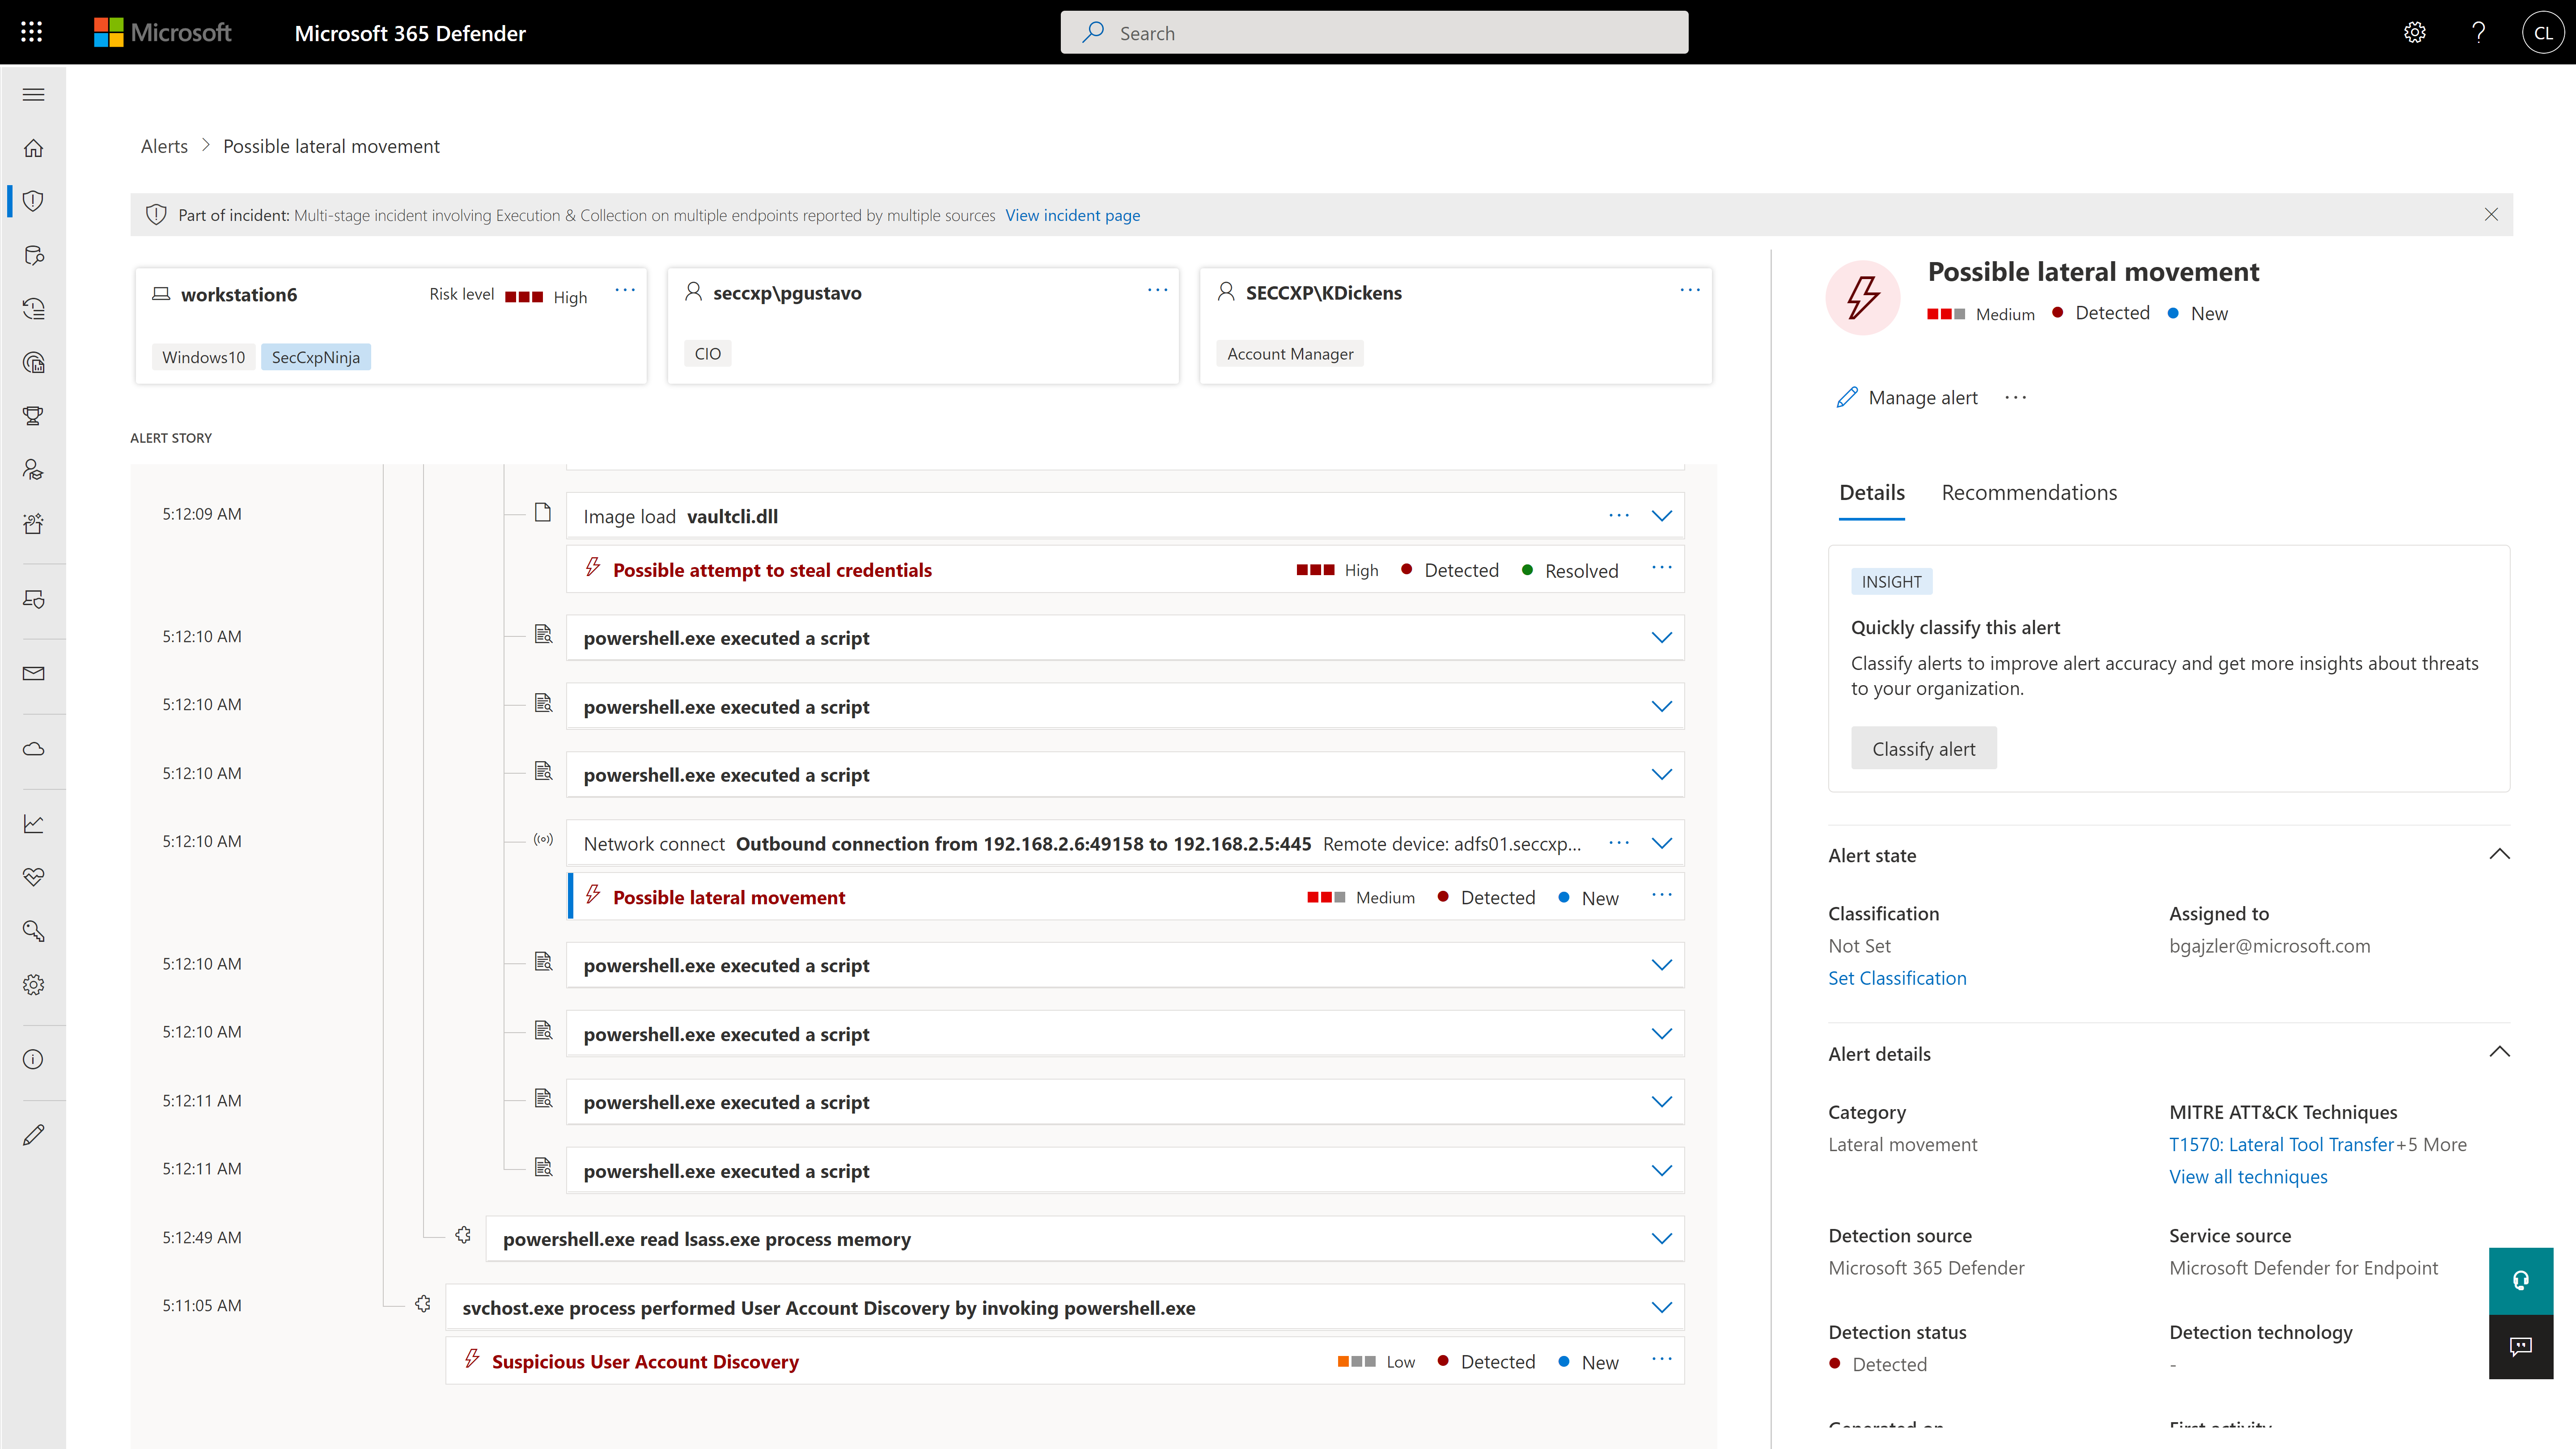
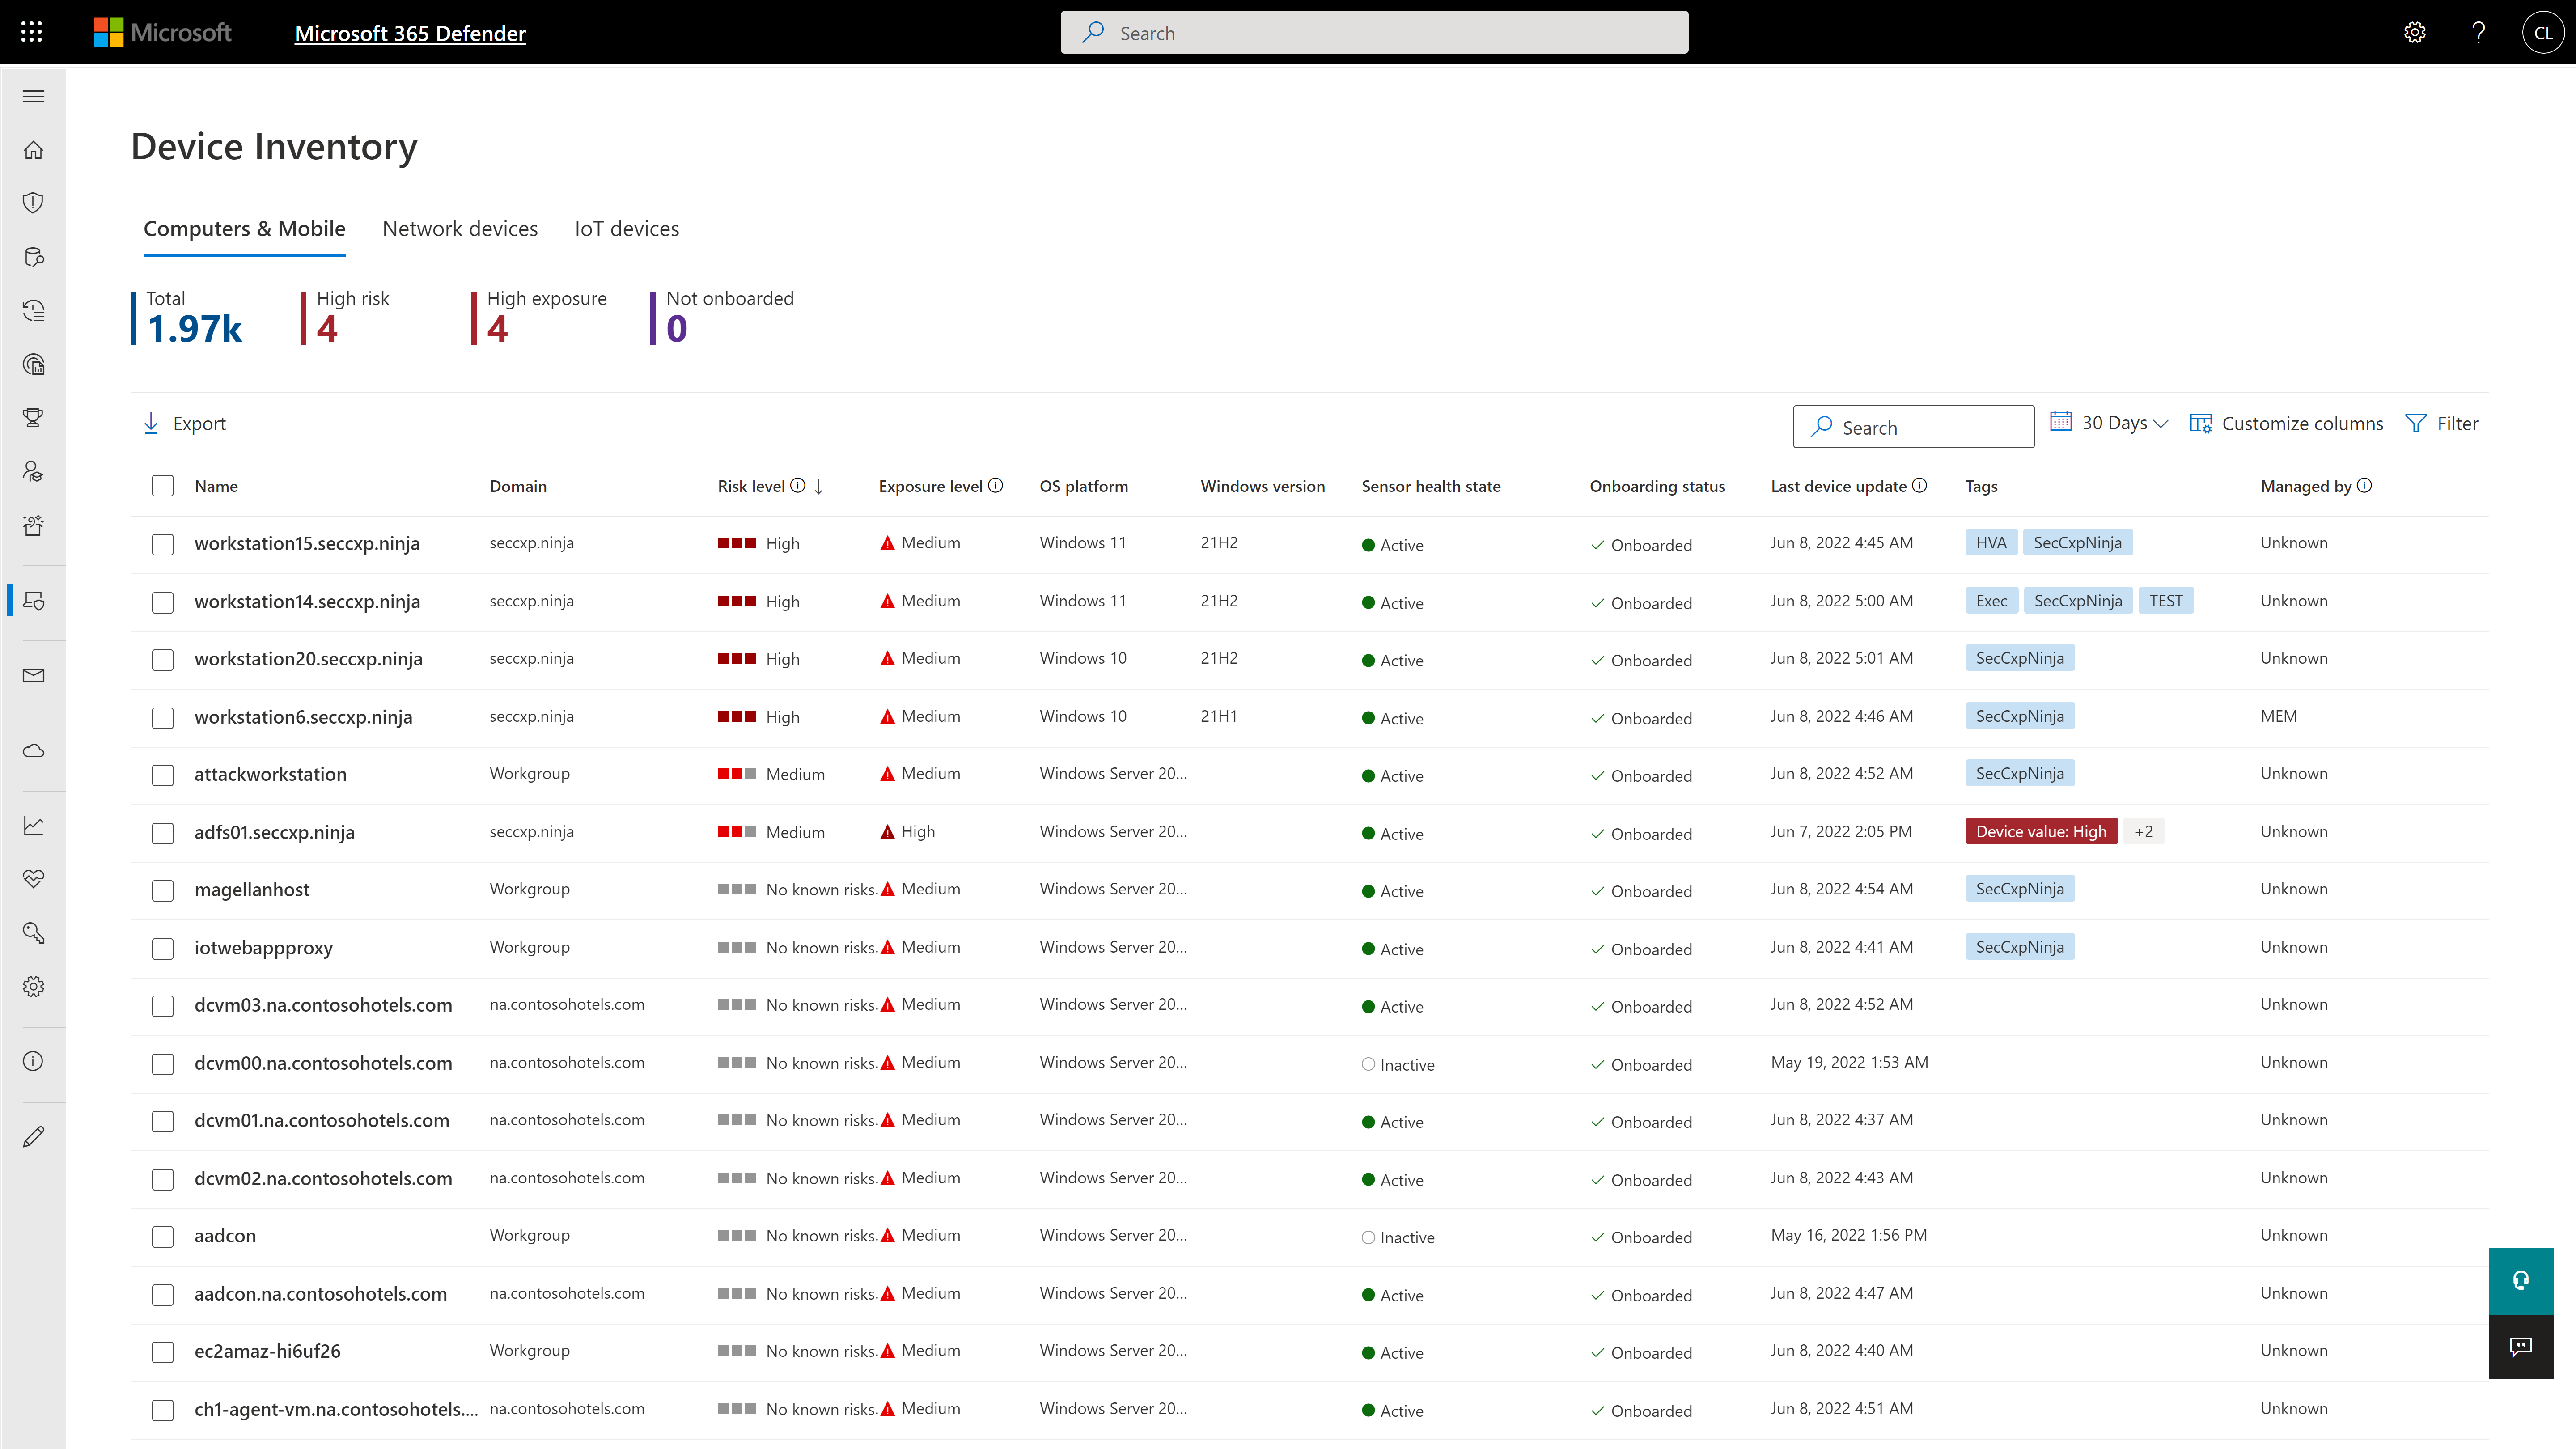
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
If this is your first experience with a SIEM, this one can get you started. Take the time to learn the ins and outs of the product and you'll most likely be satisfied with it if your company is an SMB. If you need compliance reports, OSSIM is too small for you, you'll need to go with USM or USM Anywhere.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Asset discovery. Once installed in a centric, network-accessible server, OSSIM can poll all your endpoints with common protocols (SSH, SNMP, WMI) to detect and discover site-wide assets to monitor. You only need to group them by your own criteria once added to the product.
SIEM Event Correlation. You can define quite complex correlation rules to detect possible suspicious or malicious actions or attempts in your network, in order to categorize them as real threats or as false positives, thus streamlining your risk assessment and management.
Ease of installation. The entire AlienVault OSSIM is self-contained in an ISO file, which can be burned into a DVD or just mounted in your server of choice (physical or virtual) for deployment. The installation process is automated and quote verbosed, with options for static IP, email messaging and others.
Ease of access. Being AlienVault OSSIM a self-contained appliance, it can be accessed via web by any device that supports a web browser, being that desktops, workstation, mobile devices, etc. The OSSIM dashboard and other features are automatically rearranged to adapt to the particular device being in use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
AlienVault OSSIM is far easy to use and manage - provided you know what you're doing. As any SIEM application, there is some background knowledge required in order to take advantage of the product's functionalities, such as the log correlation and analysis. Other than that, the application is quite usable and robust.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Everything is done through MSSP and installation pro services. Once those hours are burned up, then you're on your own without a lot of help. Typically the pro services hours aren't enough to get past 60 days and MSSP are hit and miss. We had a miss for installation helpers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Originally my organization leveraged alien value due to the lower cost of entry and ability to manage it as a service provider. Unfortunately, after several years of working with this tool, it became unwieldy to use as it felt that almost every useful report had to be created by hand. As other tools have come out with the ability to do automated responses such as Stellar Data processor, we have begun to evaluate alternatives.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info