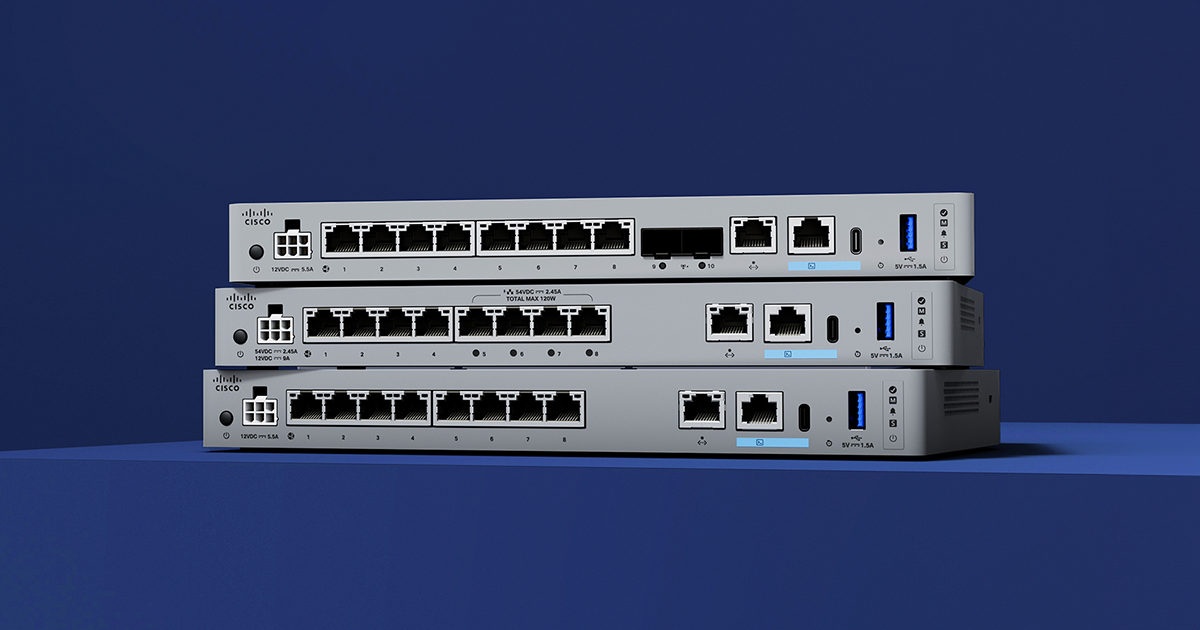
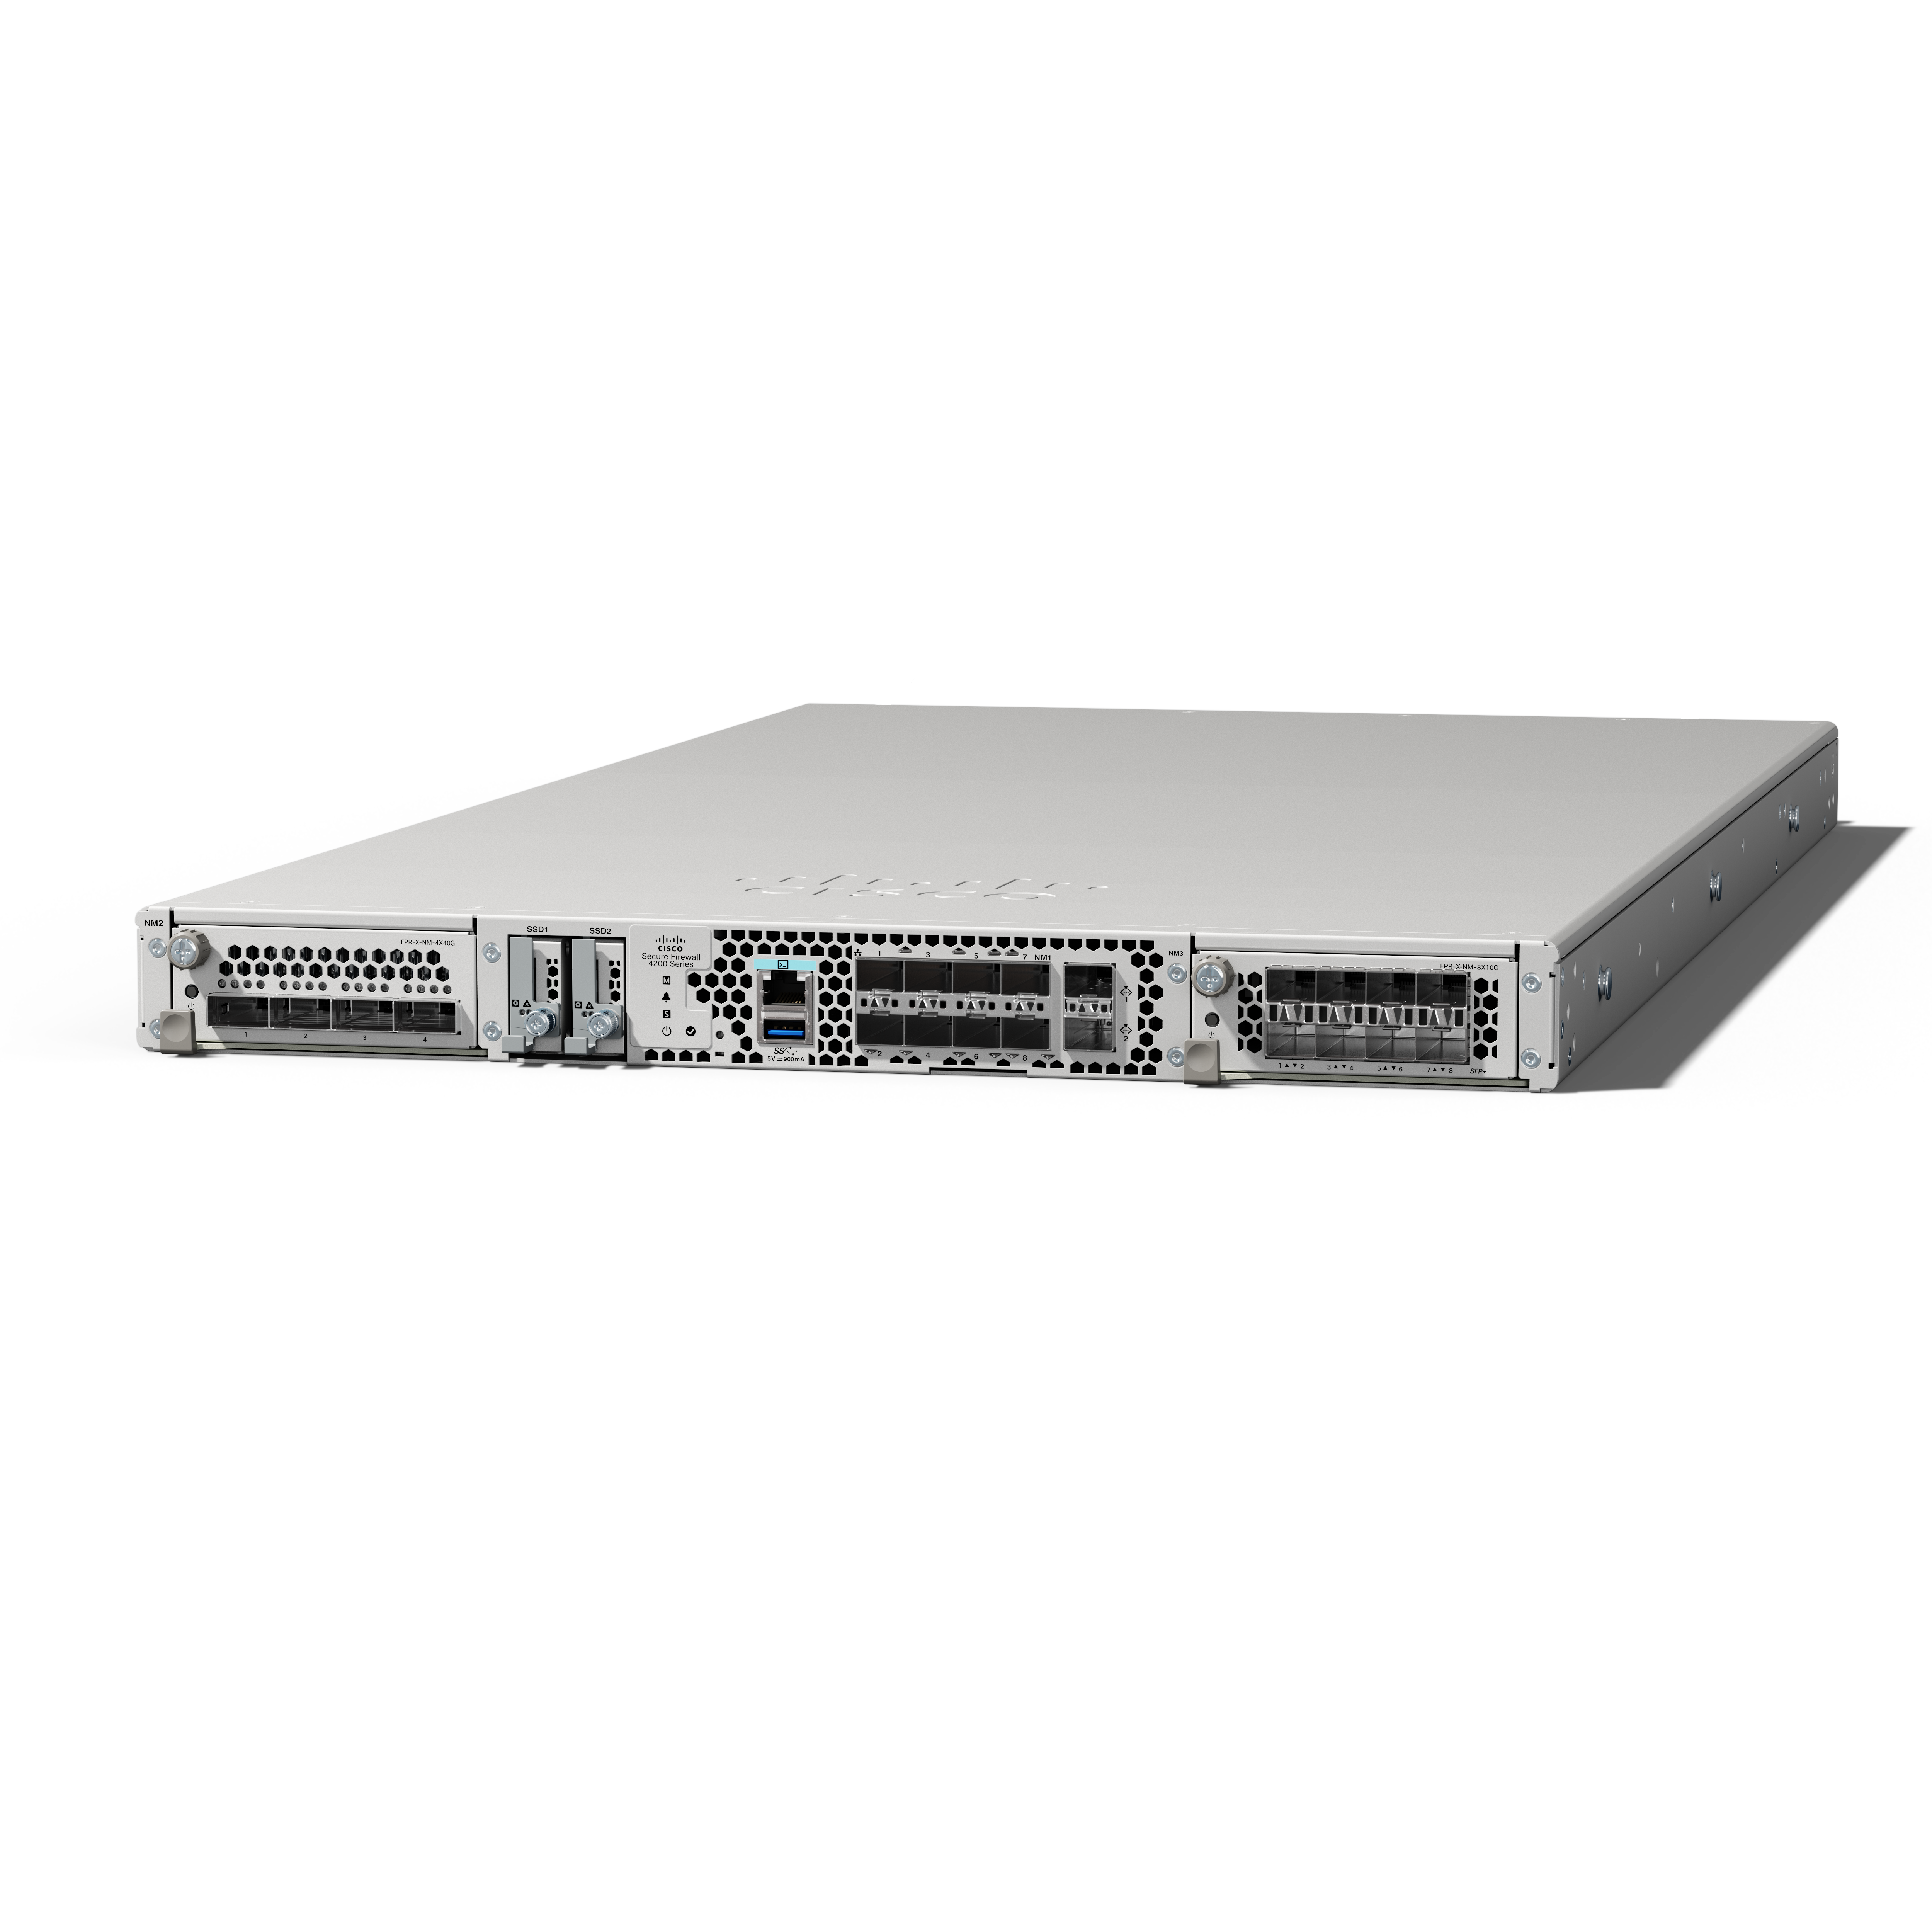
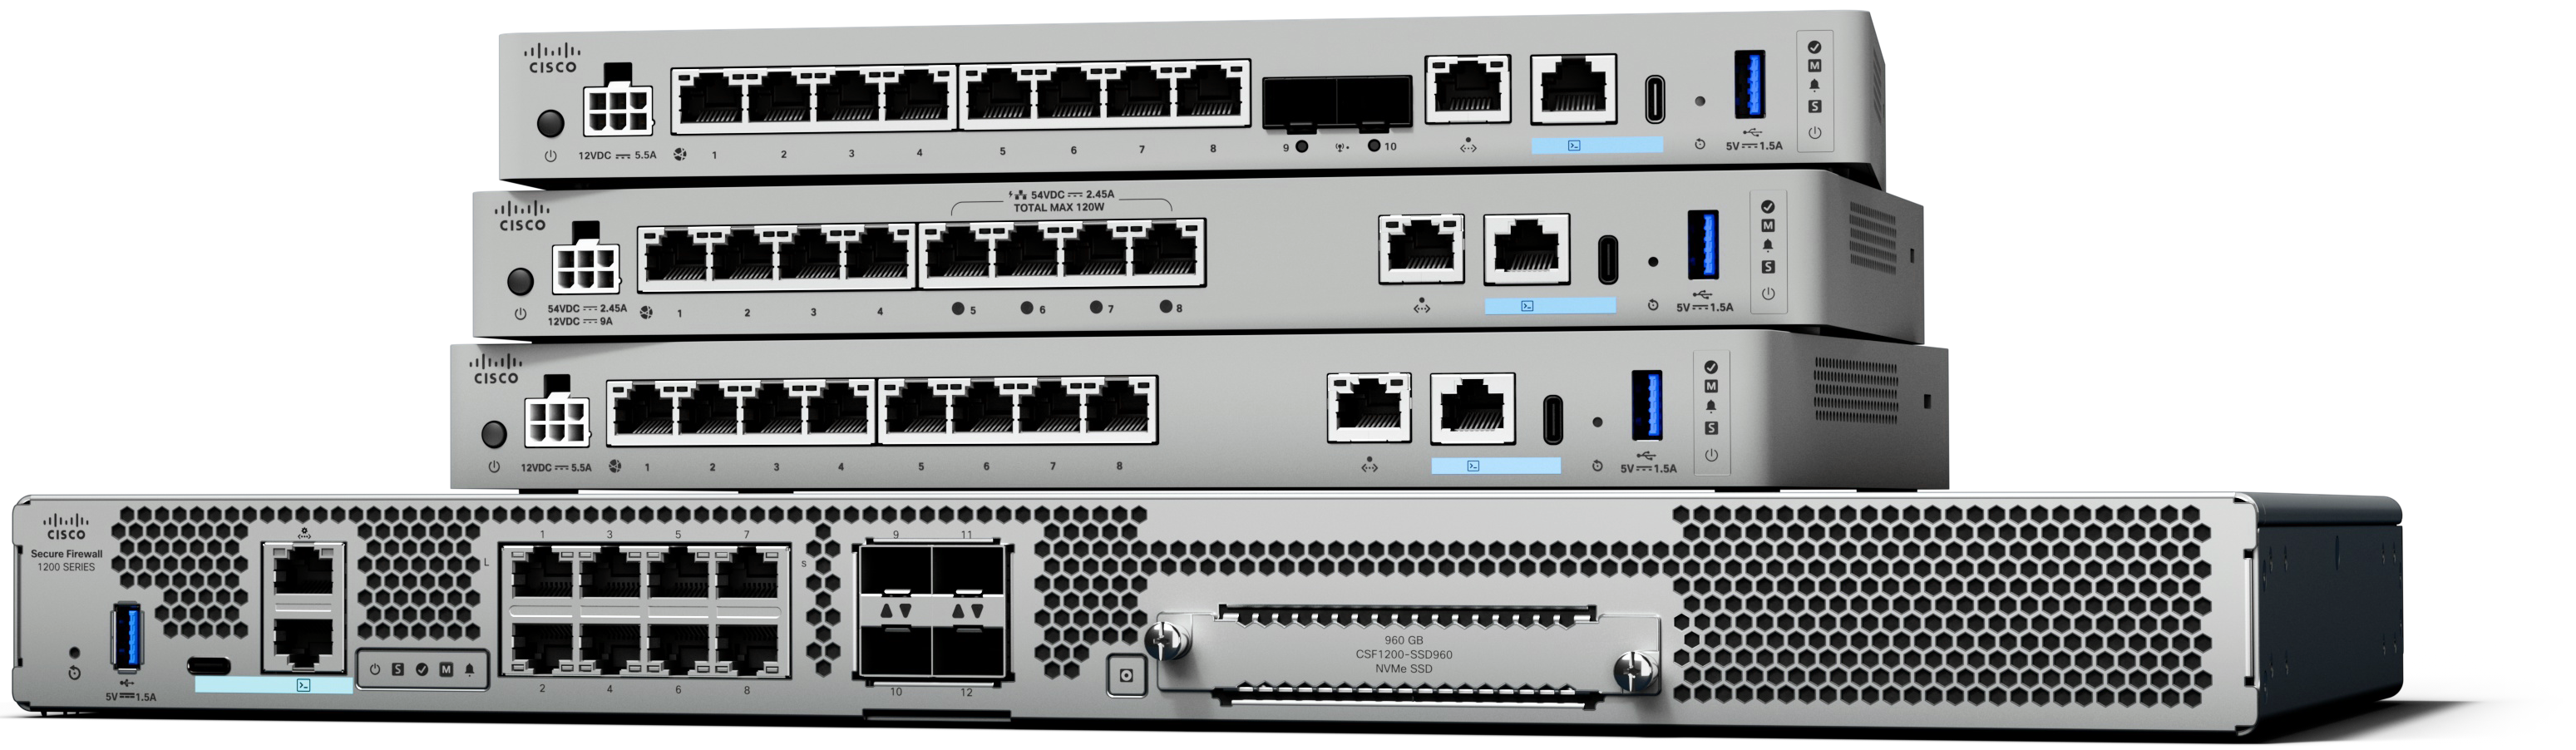
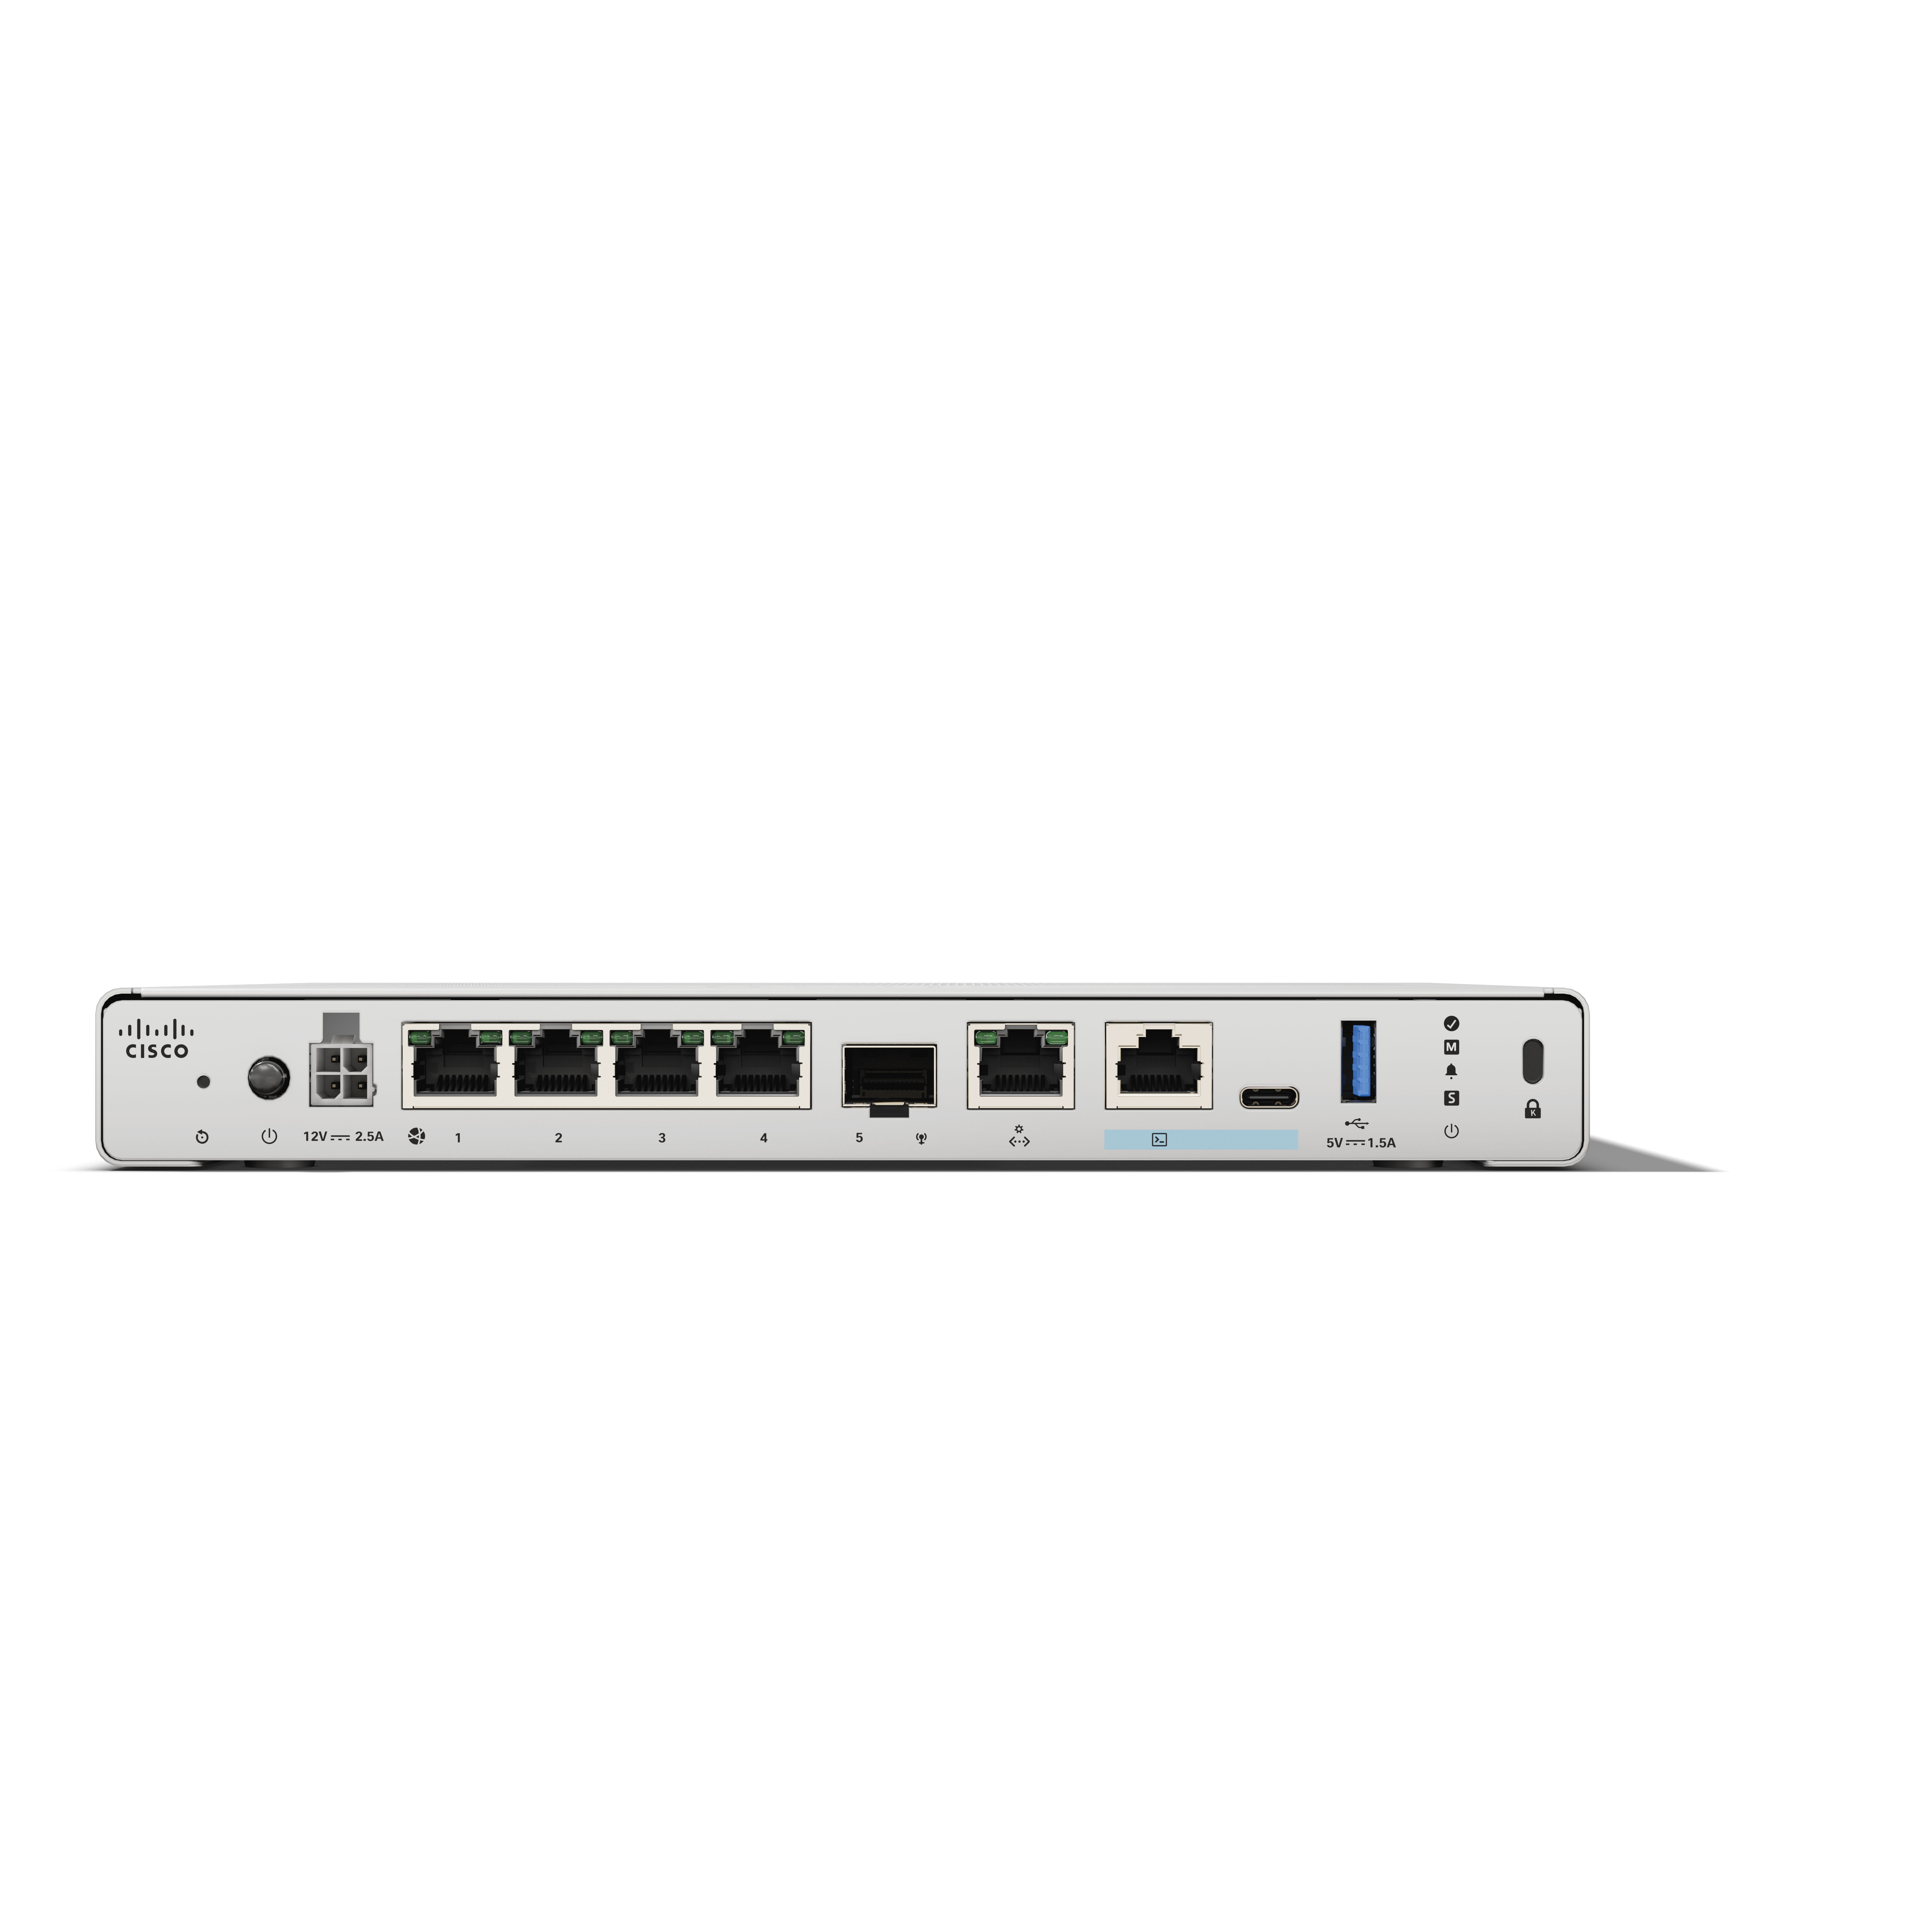
Cisco Secure Firewall delivers comprehensive threat protection for modern, distributed networks. Built to support hybrid workforces and multicloud environments, it enables Zero Trust access, application visibility, and secure remote connectivity. With integration across the Cisco Secure portfolio, including SecureX and Talos threat intelligence, the firewall powers organizations to detect and stop more sophisticated threats. Centralized management simplifies policy enforcement, orchestration,…
N/A
SecureLink Enterprise Access
Score9.1 out of 10
N/A
SecureLink is a platform for remote support in regulated industries. Enterprise software vendors use SecureLink to deliver remote support and services. Hospitals, banks, casinos and other regulated entities use SecureLink to authenticate, control and audit remote access for their vendors, business associates and other 3rd parties.
I can't think of scenarios where it is less appropriate, unless we are talking about real tiny businesses. More businesses will find Cisco Secure Firewall an outstanding tool to use, love, and trust from a reputable Network giant vendor. It is a must for businesses that want to focus on what they are doing, and leaving the network security for the pros.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It does exactly what it needs to. The only times I've had serious issues with rolling out to a vendor is when they have a "contractual agreement" to only use their solution. Almost every vendor that I've worked with and shown this product to has been skeptical for the first 5 minutes and fully converted to liking the ease of use of the product by 10 minutes
Cisco's firewall actually does its job of blocking what it is supposed to block. We had an old Firewall that led to slippages. Cisco catches 97% of malware and vulnerabilities during testing. For Coitiar, that means an engineer who clicks a link with malware is handled quickly.
We actually tested if failovers would affect running sessions. We pulled our primary unit during a certification submission period. The firewall just switched, and the connection kept running.
The AI assistant in policy management is excellent, and for our lean team, it makes the whole process easy and efficient. I don't have to audit 200 policies manually; the AI steps in and does its thing.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I mean I think a lot of the technology with managing them is getting better. There's a few cons to the new firewall management console. You can't sort through routes or I think you can with interfaces now, but there's a few caveats that they haven't really worked out yet, but they're implementing AI into it, so it's getting to be a lot easier to use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Java based. Always an issue. I know they are working on this and it will be Javaless if we need it. I know that Java can cause issues across the board and I understand the need of it, but it does not make it any better when there are Java issues.
Stronger integration with the Active Directory. Currently its only read-only, which is good and bad.
I would love to see an App. I know they are working on this as well.
It works really well. We can do most anything we want or need to with it, and you don’t have to have a doctorate or multiple certs to necessarily figure it out. The thing that would probably have to happen to make us switch would be if we just got priced out - Cisco’s more powerful and higher bandwidth models cost a pretty penny.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
i think overall after ALOT of tac cases it works allright now. But still have alot of issues if you use cloud based mangement. fx, if you open 2 windows of access policys, both of the pages, rules starte to jump form side to side. if you then open one more list, its start to jump even faster. if you close the 2 of them, its back to normal. ALSO the extended access lists for VPN, SUCKS. Its the tiniest window when opening the editor, and you are not able to give the rules names, Which means finding and editing rules SUCKS, its a horrible experience, and eveytime we have to we want to yell :P
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We have not had any performance issues with Cisco Secure Firewall, even with DPI and IPS enabled, we have not seen a performance hit. Emoployes have not complained about any slow network speeds that could have been attributed to the secure firewall it has always been something else within the office network.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I rarely get the support I need in the time I need it. Often, while they are "looking at packet captures and going to get back to me" I fix the problem on my own. If you were to look at my TAC cases over the past year, you would see some very lengthy cases that usually ended with me contacting the TAC person and telling them to just close the case
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The employees at Securelink have always been responsive and seem to be invested in the success of my company. They truly understand what their product means to us so if there is a problem, they are always willing to help. In the rare event that something is found on their end, they will be proactive and reach out to someone to help and get something on calendar for a fix
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
was a good training but questions was answered not so good. Training was "Fundamentals of Cisco Firewall Threat Defense and Intrusion Prevention (SFWIPF)".
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Our initial implementation was aided by Cisco's professional services and was excellent. The engineer was very knowledgeable and helped us work through issues while building out our new internet security edge Part of this involved tools to migrate the firewall configuration from old to new.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco Secure Firewall works better with the Cisco ecosystem when we can utilize it and feels beefy enough when we utilize it in the data center. The Fortinet we have found are great, small cost boxes for remote offices with a better UI then Cisco Secure Firewalls. The feature set included with the firewalls feels similar from a security point of view.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Securelink seems to work better than LogMein for a large enterprise group. Our company has over 10,000 different connections and securelink manages them well.
A solid, realistic rating most people give for Cisco Secure Firewall pricing is 7 or 8 out of 10 (because the product is strong but licensing can be a bit complex)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco Secure Firewall has never given us any trouble, it has stayed up at all times, upgrading the appliance has also become much simpler. We operate the appliance in a HA pair, so 0% downtime within our organisation. During switchover while upgrading, not a single packet seems to get lost, so this has been a very valuable asset to our company.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I've found that Securelink allows me to get a vendor access to an application for support purposes much faster than a provisioned VPN account and the red tape around this. I can set up a vendor to access an application suite in a half hour and it will be more secure than regular provisioning.
The ROI is yet to be seen on this, but it certainly makes Compliance, Internal Audit, and Legal very happy, which helps everybody.
Internally, there is much more push back and it has been problematic. For a tech, to have to log in to a server and navigate to a system is considered cumbersome, when before all they had to do was open up Putty or RDP to a server to get in. The only way to combat this is to force them to use Securelink by removing rights. Near impossible for the domain admins.