Secret Server (originally from Thycotic, now from Delinea since the 2021 Thycotic merger with Centrify) is an enterprise password management application, which is available with either a cloud-based or on-premise deployment which emphasizes fast deployment, scalability, and simplicity.
N/A
IBM Vault
Score9 out of 10
N/A
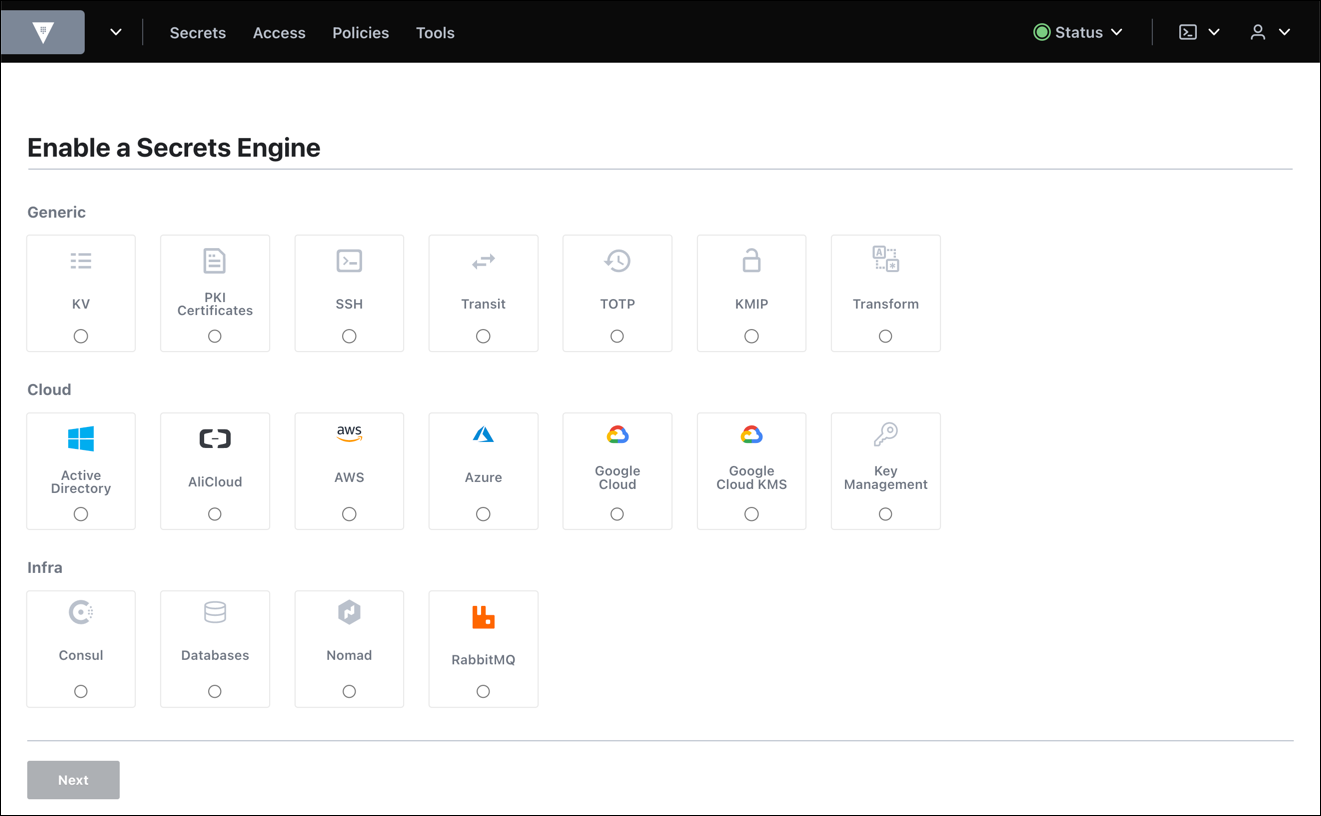
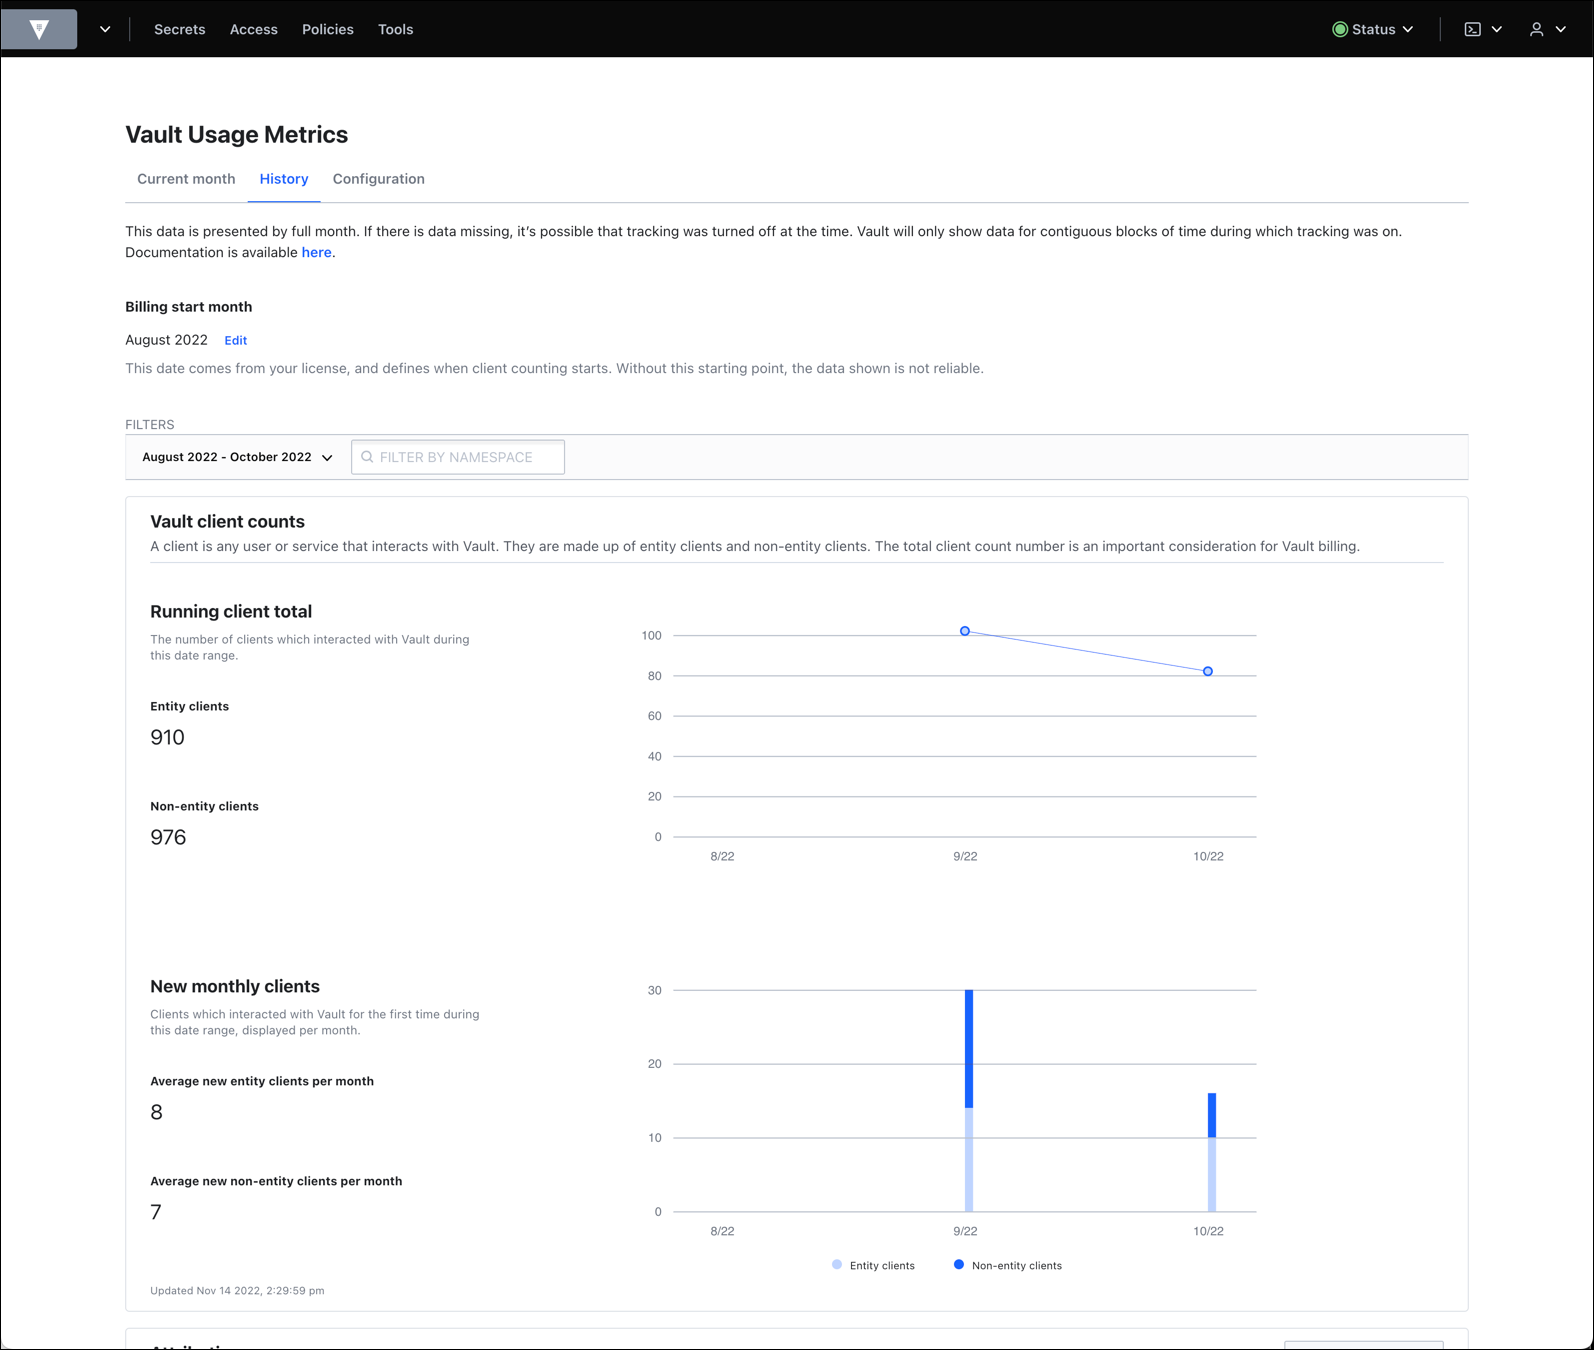
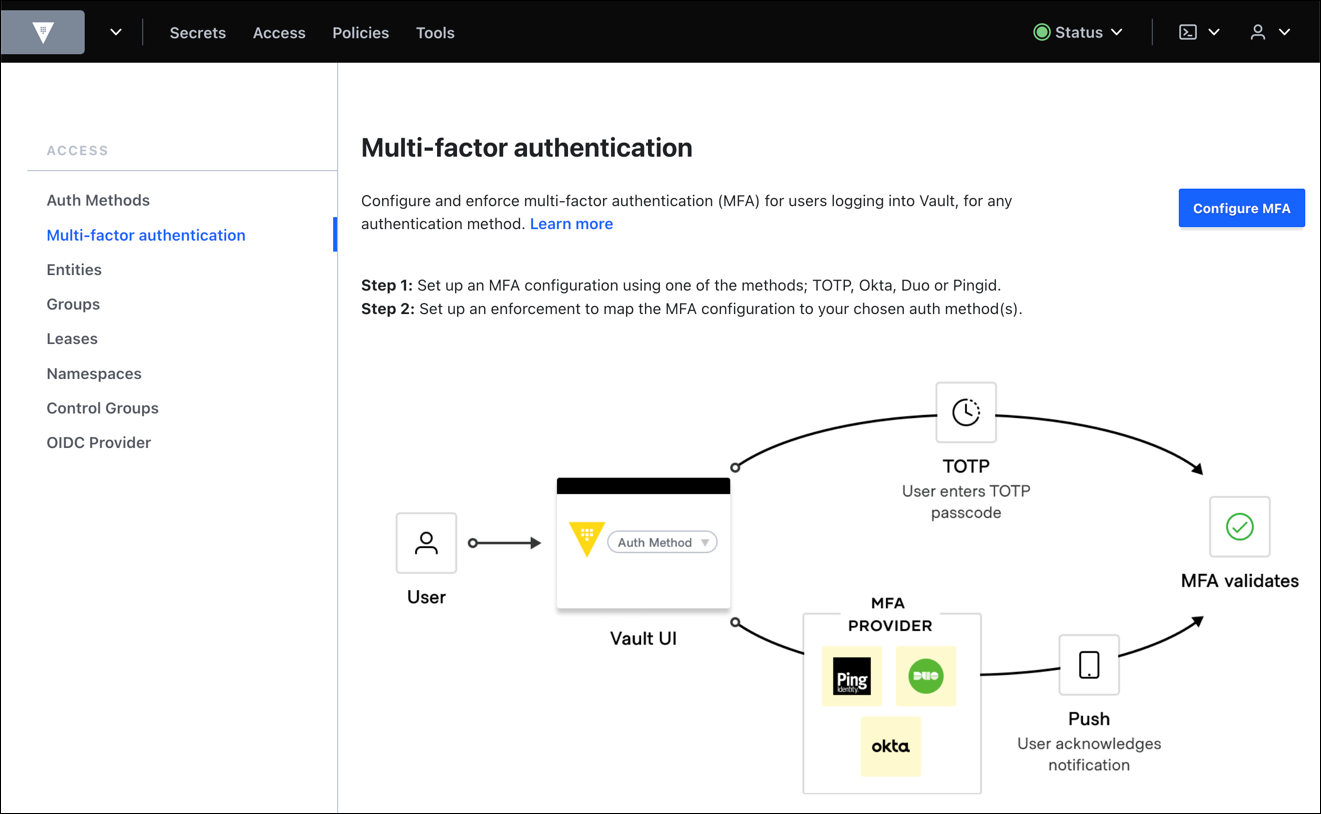
IBM Vault (formerly Hashicorp Vault) is an encryption tool for managing secrets including credentials, passwords and other secrets, providing access control, audit trail, and support for multiple authentication methods. It is available open source, or under an enterprise license.
I would recommend Delinea to any organization or colleague, as I have used it to support our shared services model, as well as a dedicated model for people support to customers, for privileged access management. Delinea has provided us with effective methods for handling unnecessary login attempts to the customer infrastructure. Additionally, the connection thread is available in the audit trail for review, which is a valuable feature to have.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Vault is well-suited for all software application development. It does a great job of ensuring you have full visibility and traceability into your credentials and who checks them out. The integration is the key enabler that makes Vault a differentiator. Some of the new agent capabilities are going to be a good value-add.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Password Management: Its entire purpose, really. Secret Server stores passwords in an incredibly easy to use way. They can be organized in groups, they contain all the information about the site or system the password is used for (including URLs for websites), and even a notes field. You can set up specific policies for expirations and complexity, and Secret Server can even generate strong passwords for you. Using a password is simple, too, since you can just click a button to add it to your clipboard; you don't even have to unmask the password.
Security: The passwords are stored encrypted in a SQL database, and the application requires an authenticated login. This could be local, but we tie it into Active Directory. Each folder of passwords has groups assigned (in our case, again, AD, but you can make them local groups) with different permission levels, so we can compartmentalize passwords. Desktop technicians don't have access to network switch passwords, etc.
Easy Setup: It took me about an hour to get the server running, from spinning up the VM to importing our old password list. It took a little longer to organize the passwords into proper folders, and then assigning groups, but it was easy to do.
Personal Passwords: Each user also gets a personal folder, where they can keep their own, unshared passwords. This is nice for sites or systems with individualized logins (e.g., a firewall, VPN, etc.)
Favorites: Secret Server lets you tag passwords as "favorites" so you can easily find ones you use constantly. The search feature is nice, but this is nicer.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It doesn't have an interface. This isn't entirely bad because of the purpose it serves, but it does make the barrier to entry a little difficult.
Unlike many other HashiCorp products, the documentation feels like it leaves some steps out. Step by step documentation lowers the barriers to entry a little bit, and going through even the installation documentation and setup leaves a little bit of the caveats out.
It needs a fair bit of supporting infrastructure. You cannot just have a Vault instance. Having a HashiCorp Vault instance means also having a consul cluster for the backend.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
HashiCorp Vault is the best there is out there, and it has become critical to our secret management use cases. It would be difficult to find anything that would suit our needs better and that would be beneficial for us to switch over to.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
My rating is purely based on the configurational activities, as feature-wise delineation has all the features that are very beneficial for customers, though the implementation is a bit more manual work, which can be reduced with a low-code platform. Along with that, we can have a better UI to have intuitiveness and can manage the platform for shared customers in a better way. Overall, it is a very good tool for PAM.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Most, if not all companies would have a use for Vault, from basic secret storage and retrieval to dynamic Cloud credentials, database management, etc., and they are all easily configurable to the specific needs/use cases of your specific company. If you can afford it/have it in your budget, Vault is definitely something worth checking out and at least demoing the open-source version.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
As with all other products provided by HashiCorp, the effort and attention that the company has in creating a complete solution ecosystem for the DevOps universe are fully apparent. Several technical lectures about products on YouTube are presented by the company's CEO.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
There were not very many solutions that provided the entire package of taking an account from creation and deactivating it when no longer needed, as well as providing the discovery of unknown service accounts. Other solutions like RoboForm and LastPass did not offer the ability to manage your service accounts and added layers of complication to ensure security.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
HashiCorp Vault integrates with a lot of tools and systems, and the documentation was pretty robust with a lot of community help. Because HashiCorp Vault is also older than other solutions, it is already well developed with a lot of features you need for storing secrets and configuration. HashiCorp Vault is also friendlier towards application build and is focused in providing security and a lot of customization for almost any use case scenario. Bitwarden is more limited to password management of enterprise accounts, but for application usage is not that great or easy to integrate. It does not scale well also. AWS Secrets Manager on the other hand is really good but more limited to AWS applications and vendor lock is problematic as well for such a critical piece of infrastructure.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info