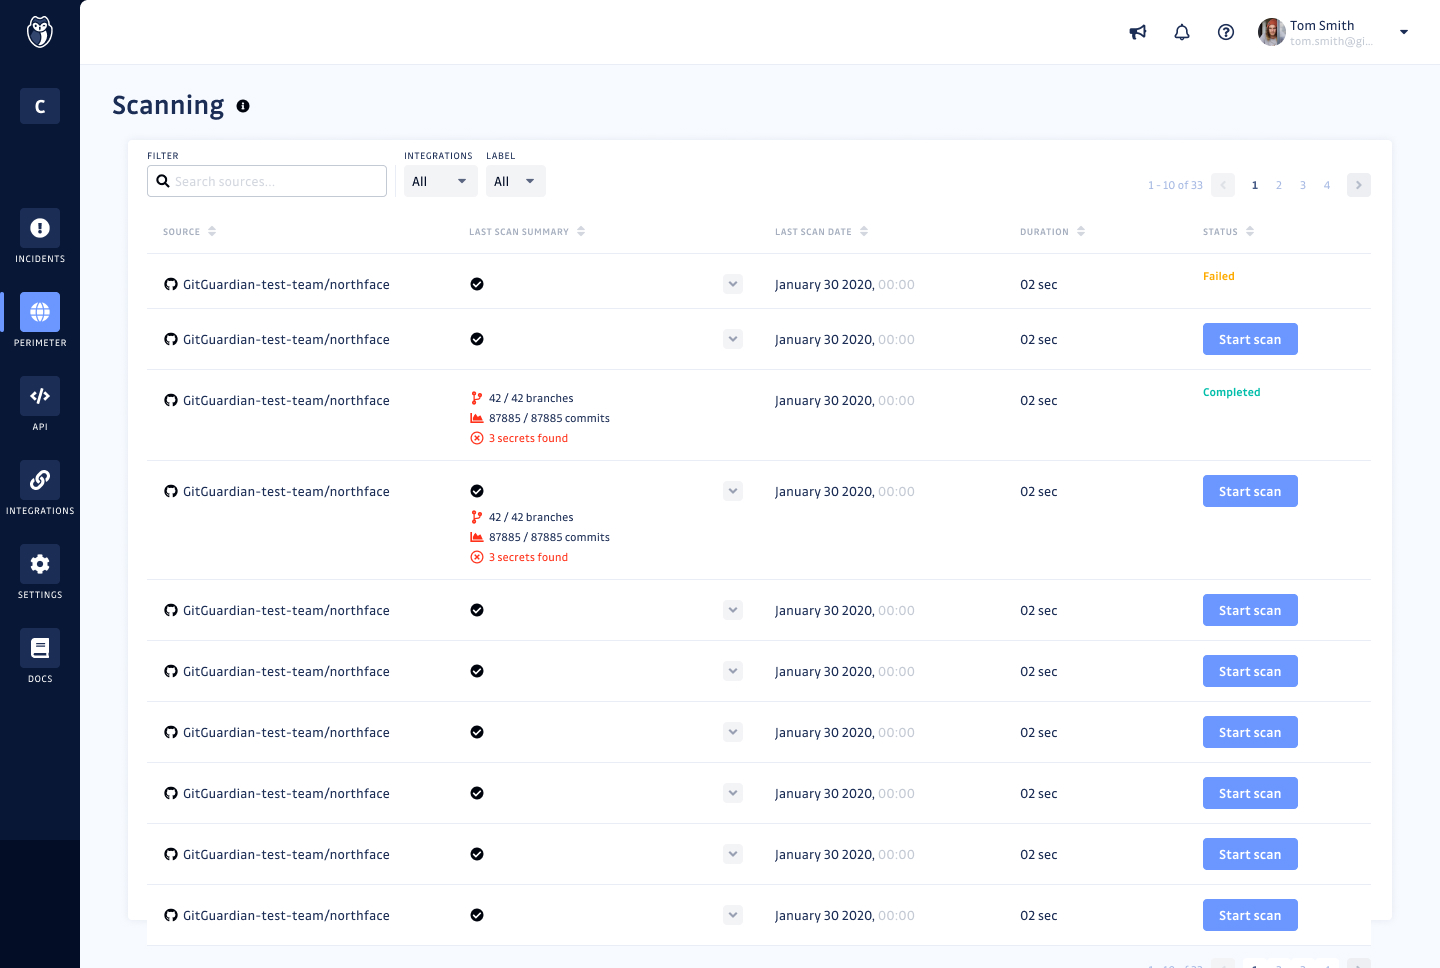
GitGuardian is an end-to-end NHI security platform designed to help organizations strengthen their Non-Human Identity (NHI) security posture and address compliance standards and regulations. As attackers increasingly target NHIs, such as service accounts, service principals, and applications, protecting and managing these critical assets has become paramount. NHIs rely on “secrets” like API keys and certificates for authentication, and their rapid proliferation has led to significant…
$0
(for individuals or up to 25 devs)
Kayako
Score6.8 out of 10
N/A
Kayako is a help desk and customer support platform that helps businesses automate workflows, improve agent productivity, and deliver personalized customer experiences across email, chat, and social media.
I do think it'll absolutely fit everyone who codes integrates with another platform or services. We all forget that one credentials one in a while, and especially those who managed public repository, it is important to keep an eye on accidentally committed credentials. While I think you don't really needs it for personal project, it's a nice to have, you don't want to waie up to 50k USD of sudden surcharge on resources you don't use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
When it works, It's without a doubt a great help desk solution. It is perfect for our usage, and have rolled it out company-wide. It's great if you have multiple departments. We have it set up so most items come through a single desk that then hands out tickets to their proper department. There may be cheaper options for smaller organizations but for one that is as service-driven as ours, we really think Kayako is a great fit.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
GitGuardian monitors every public or private GitHub commit ( that have GitGuardian installed) and event in real-time for secrets and sensitive data. In a leak scenario it immediately notifies us.
It uses sophisticated pattern matching techniques to detect credentials that cannot be strictly defined with a distinctive pattern (like unprefixed credentials)
It covers several API providers, database connection strings, private keys, certificates, usernames and passwords etc
GitGuardian have high True Positive Rate of around 91% and reduces alert fatigue with smart occurrences regrouping
Gives a very good report on an individual level of what is being done for a customer or corporate issue.
Easy to understand who has what, what the tickets are about, how long they have been opened and how many times the customer/employee have gone back and forth with each other.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Improved user interface: It would be beneficial to have a more intuitive and user-friendly interface for Internal Monitoring on GitGuardian. This would make it easier for users to quickly access the data they need and understand the results of their scans.
Automated alerts: It would be helpful to have automated alerts when certain conditions are met, such as when a scan reveals sensitive data or when a new repository is created. This would help users stay informed and take action in a timely manner.
More detailed reports: Currently, Internal Monitoring reports are limited in terms of the depth of information they provide. It would be useful to have more detailed reports that include additional metrics, such as the number of repositories scanned and the types of sensitive data found.
Faster scan times: Scan times can be slow at times, making it difficult to stay on top of changes in repositories quickly. It would be beneficial to have faster scan times so that users can take action quickly when needed.
Departments need a bit of work. Even though you can have multiple departments, the only changes that can be made are globally. If you want independent queues within the departments, you have to do a lot of work that can be very confusing.
Survey system is not up to speed. Kayako really needs to add Net Promoter Score into their system. Also, if a staff user removes their name from an incident ticket, it removes them from the survey so you really can't even get a good estimate of how well your staff is in the eyes of the customer.
Very difficult to implement when you already have a customer base. Setting them up in organizations is difficult. Also, the sign-up for new customers is quirky. If you send an email to Kayako, it will say you are not an authorized user, however, it will store your email address. If you try to send an email a second time, it will go through. This is one of many reasons why we decided to move from Kayako to Oracle Service Cloud.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We are grandfathered in on their old Software-assurance pricing and our continued use costs us only a few hundred dollars a year (excluding hosting expenses)
Our team's processes are now heavily ingrained in the system
We have not been shown a more compelling option that is more cost-effective while still offering all the features we've come to expect
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Three years in we are about as happy with Kayako as we could be. We've had several employee's leave and on-boarding new hires was easier than it has ever been as things are uniform and consistent across the entire application.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I've evaluated quite a few other tools, like git-secrets, Git-leaks, scan, and maybe a few more. They're all great but quite surprisingly none of them detected Github OAuth Secrets for us. A lot of the FOSS tools out there focus on much simpler, generic secrets, which is good in itself but with GitGuardian, it was dead simple from day one. I just connected our Github Account and set up the gg-shield cli and that was all.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We were using Spiceworks for a few years before switching to Kayako but found that it wasn't as customizable or as user friendly for our customers. The SNMP scanning and inventory features with Spiceworks was nice but we needed more of a Help Desk that would allow us to scale our services to more companies.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
GitGuardian Internal Monitoring has had a positive impact on our overall business objectives. By providing visibility into our code repositories and alerting us to potential security risks, we have been able to identify and mitigate security issues before they become a problem. This has allowed us to focus more on developing our product and less on responding to security incidents. We have also seen an increase in customer confidence in our product as a result of using GitGuardian Internal Monitoring, which has led to increased customer loyalty and retention. Overall, the ROI of using GitGuardian Internal Monitoring has been very positive for our business.
We have seen an increase in the security of our codebase, as well as an improvement in the speed and accuracy of our code reviews. This has enabled us to quickly identify and address any potential security issues before they become a problem. Additionally, we have seen an increase in our ROI as a result of using GitGuardian Internal Monitoring, as it has allowed us to save time and money by preventing costly security breaches.
Tickets were definitely responded to faster once we implemented the audible alarm that would go off when new tickets came into the queue. This was possible because of the API.
Since the system was email based we could set our monitoring software up to generate tickets automatically via email for customers when it found something out of the ordinary.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info