ThreatDown (formerly Malwarebytes for Business), combines Malwarebytes' endpoint security capabilities in four bundles. The basic Core tier includes incident response, Next-gen AV, device control, vulnerability assessments, and the ability to block unwanted application.
$345
per year 5 endpoints (minimum)
SonarQube
Score8.7 out of 10
N/A
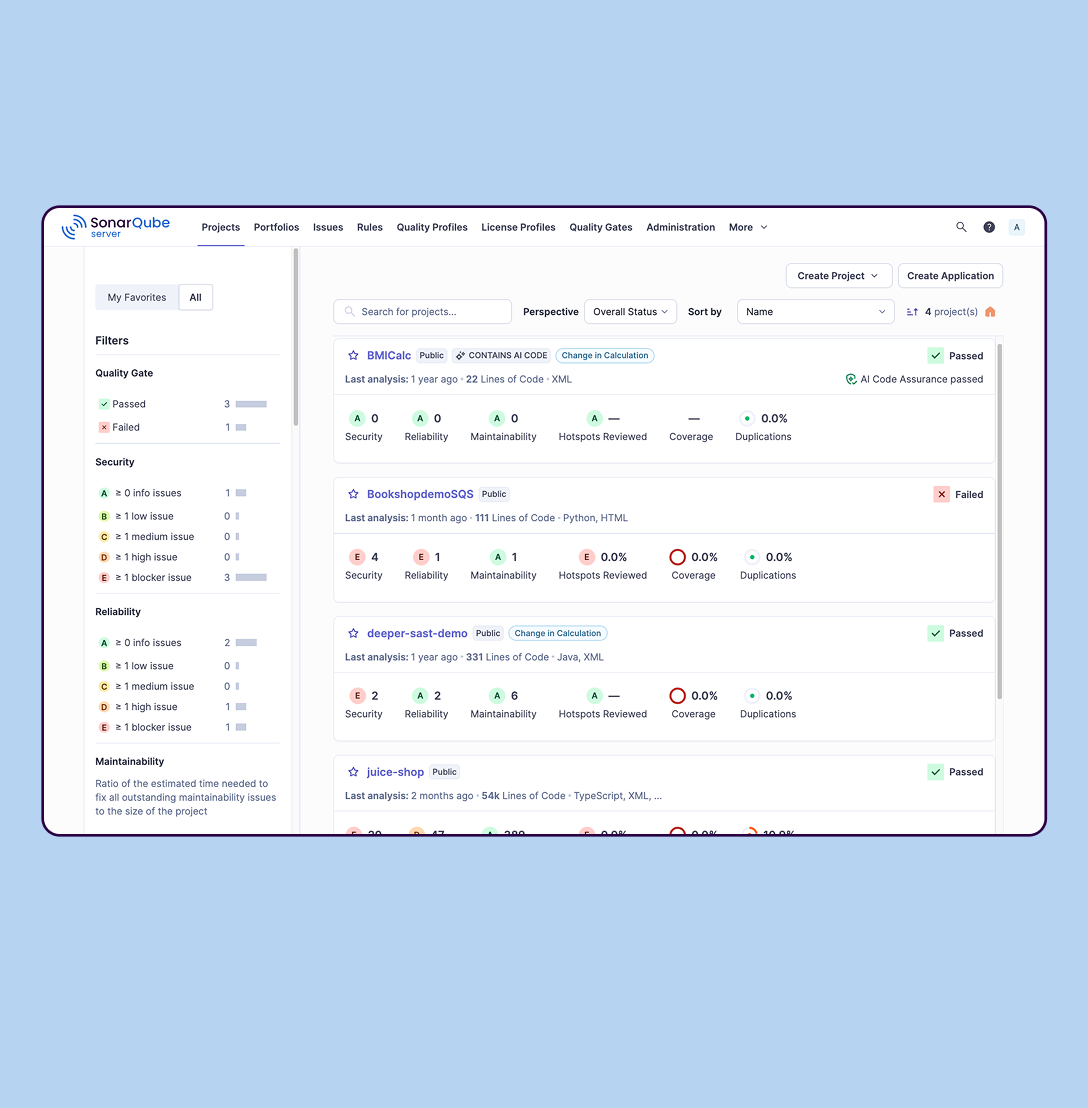
SonarQube is an automated code review solution, serving as the verification layer for code quality and SDLC security. SonarQube is used to ensure that code is secure, reliable, and maintainable. It is available through SaaS or self-managed deployment.
$34
per month Recommended for teams <50 developers
Pricing
ThreatDown, powered by Malwarebytes
SonarQube
Editions & Modules
Core
$345
per year per endpoint (minimum 5)
Advanced
$395
per year per endpoint (minimum 5)
Elite
$495
per year per endpoint (minimum 5)
Ultimate
$595
per year per endpoint (minimum 5)
SonarQube Community Build
$0
(open source)
Self-managed: Developer
Starting at $720 annually
per year per installation
Self-managed: Enterprise
Contact sales for pricing
per year per installation
Cloud-based: Enterprise
Contact sales for pricing
per year per installation
Cloud-based: Teams
Starting at $34 per month
per month per installation
Self-managed: Data Center
Contact sales for pricing
per year per installation
Offerings
Pricing Offerings
ThreatDown, powered by Malwarebytes
SonarQube
Free Trial
Yes
Yes
Free/Freemium Version
No
Yes
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
Optional Add-Ons include server and mobile device protection. Server protection ranges from $129 to $179 per annum depending on service tier. Mobile security is $10 per device, no matter the service tier. A 10% discount is offered for choosing a two-year billing plan.
I think Malwarebytes is the best anti-malware company. I think it is well-suited for any situation and any device. I think Malwarebytes does the best on Windows and on MacOS. Also, Malwarebytes is always improving, and you can tell they are a company that stays on top of cybersecurity trends. If you have a tight budget or looking for the cheapest solution, then Malwarebytes may not be the solution for you. To clarify, I don't think Malwarebytes is that much more expensive compared to its closest competitors.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is excellent if you start using it at the beginning when developing a new system, in this situation you will be able to fix things before they become spread and expensive to correct. It’s a bit less suitable to use on existing code with bad design as it’s usually too expensive to fix everything and only allows you to ensure the situation doesn’t get worse.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Protects against malware - No matter how much training you give end users on social hacking, there is always a breach at some point.
Protects against ransomware - Ransomware could spell disaster for a company...it could literally shut the doors for good.
Centralized administration - Without a terrific centralized method to manage all the systems being protected, it would require an extra position just to maintain all endpoints.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
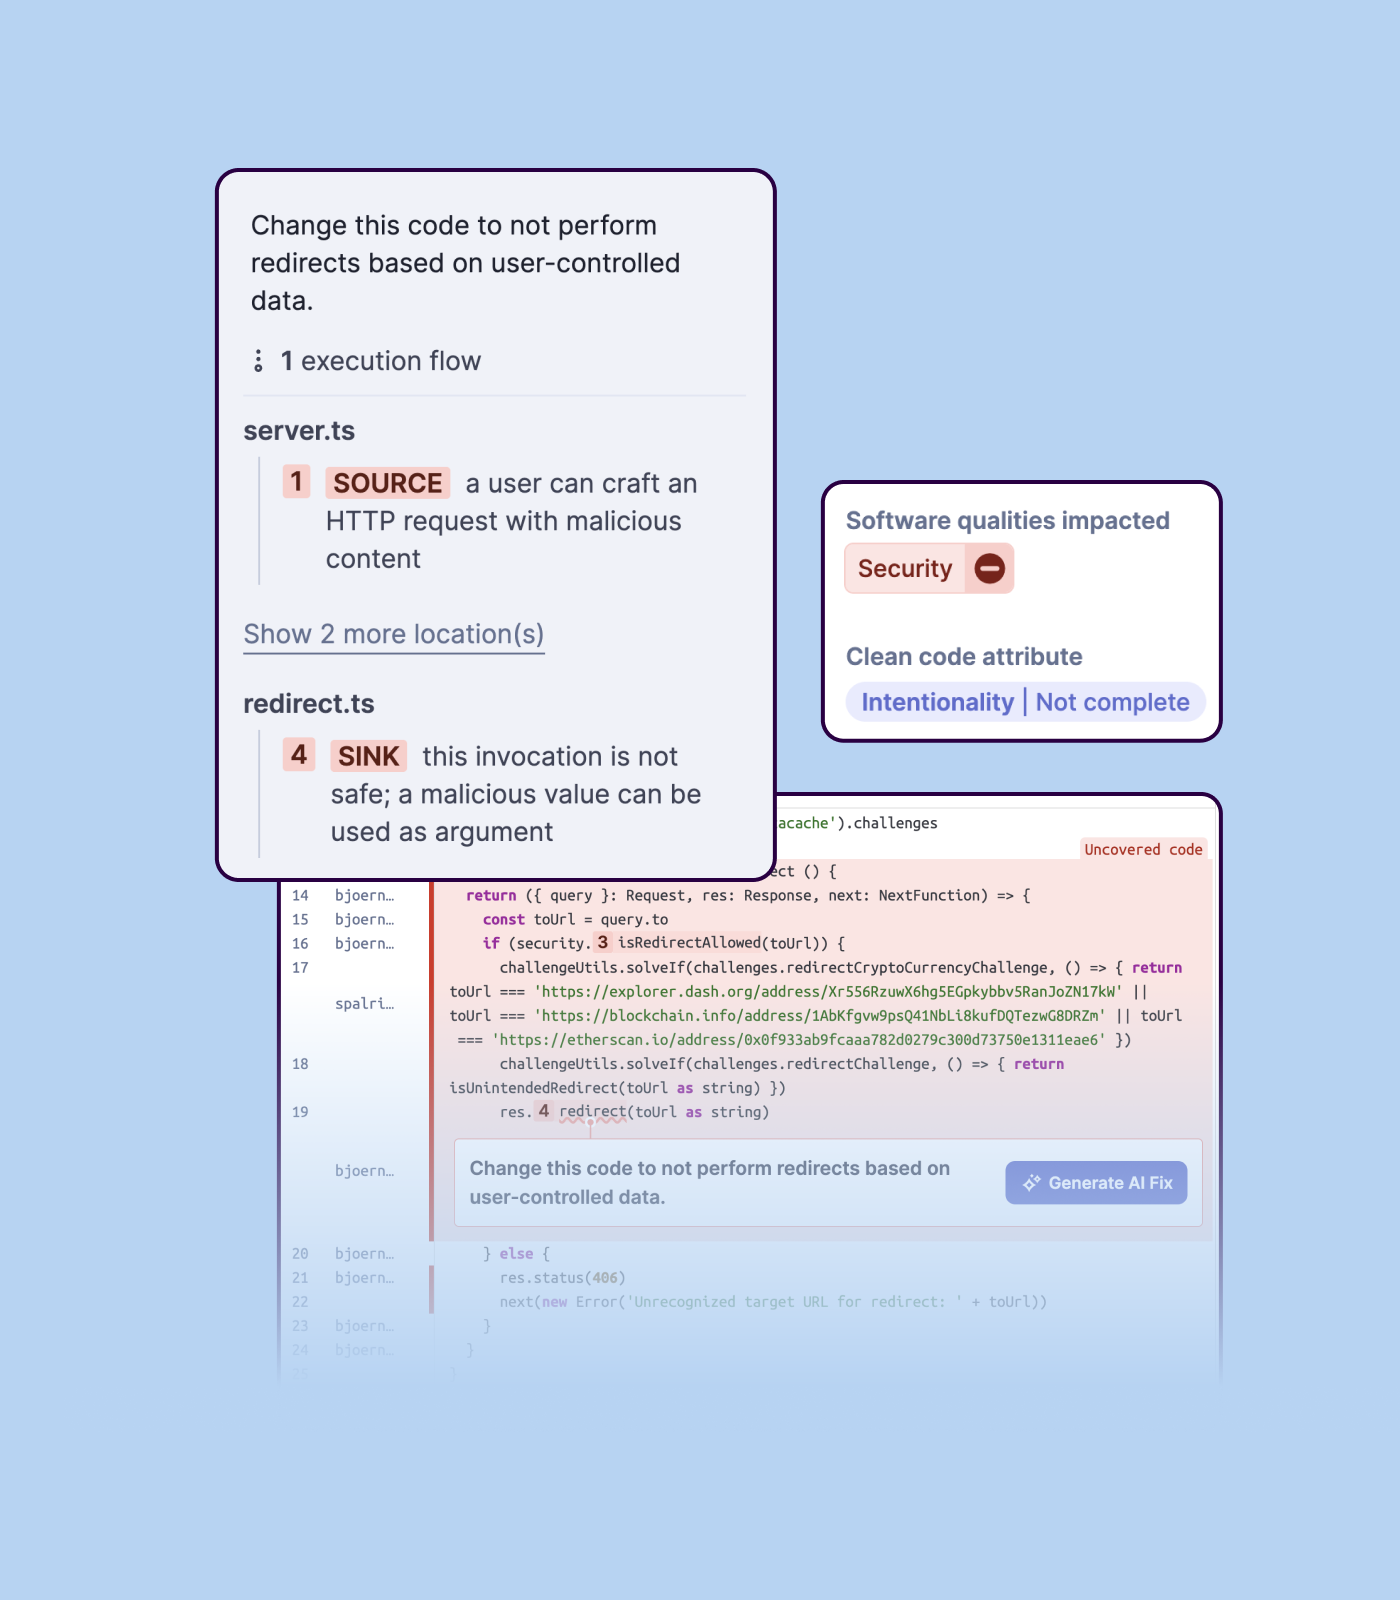
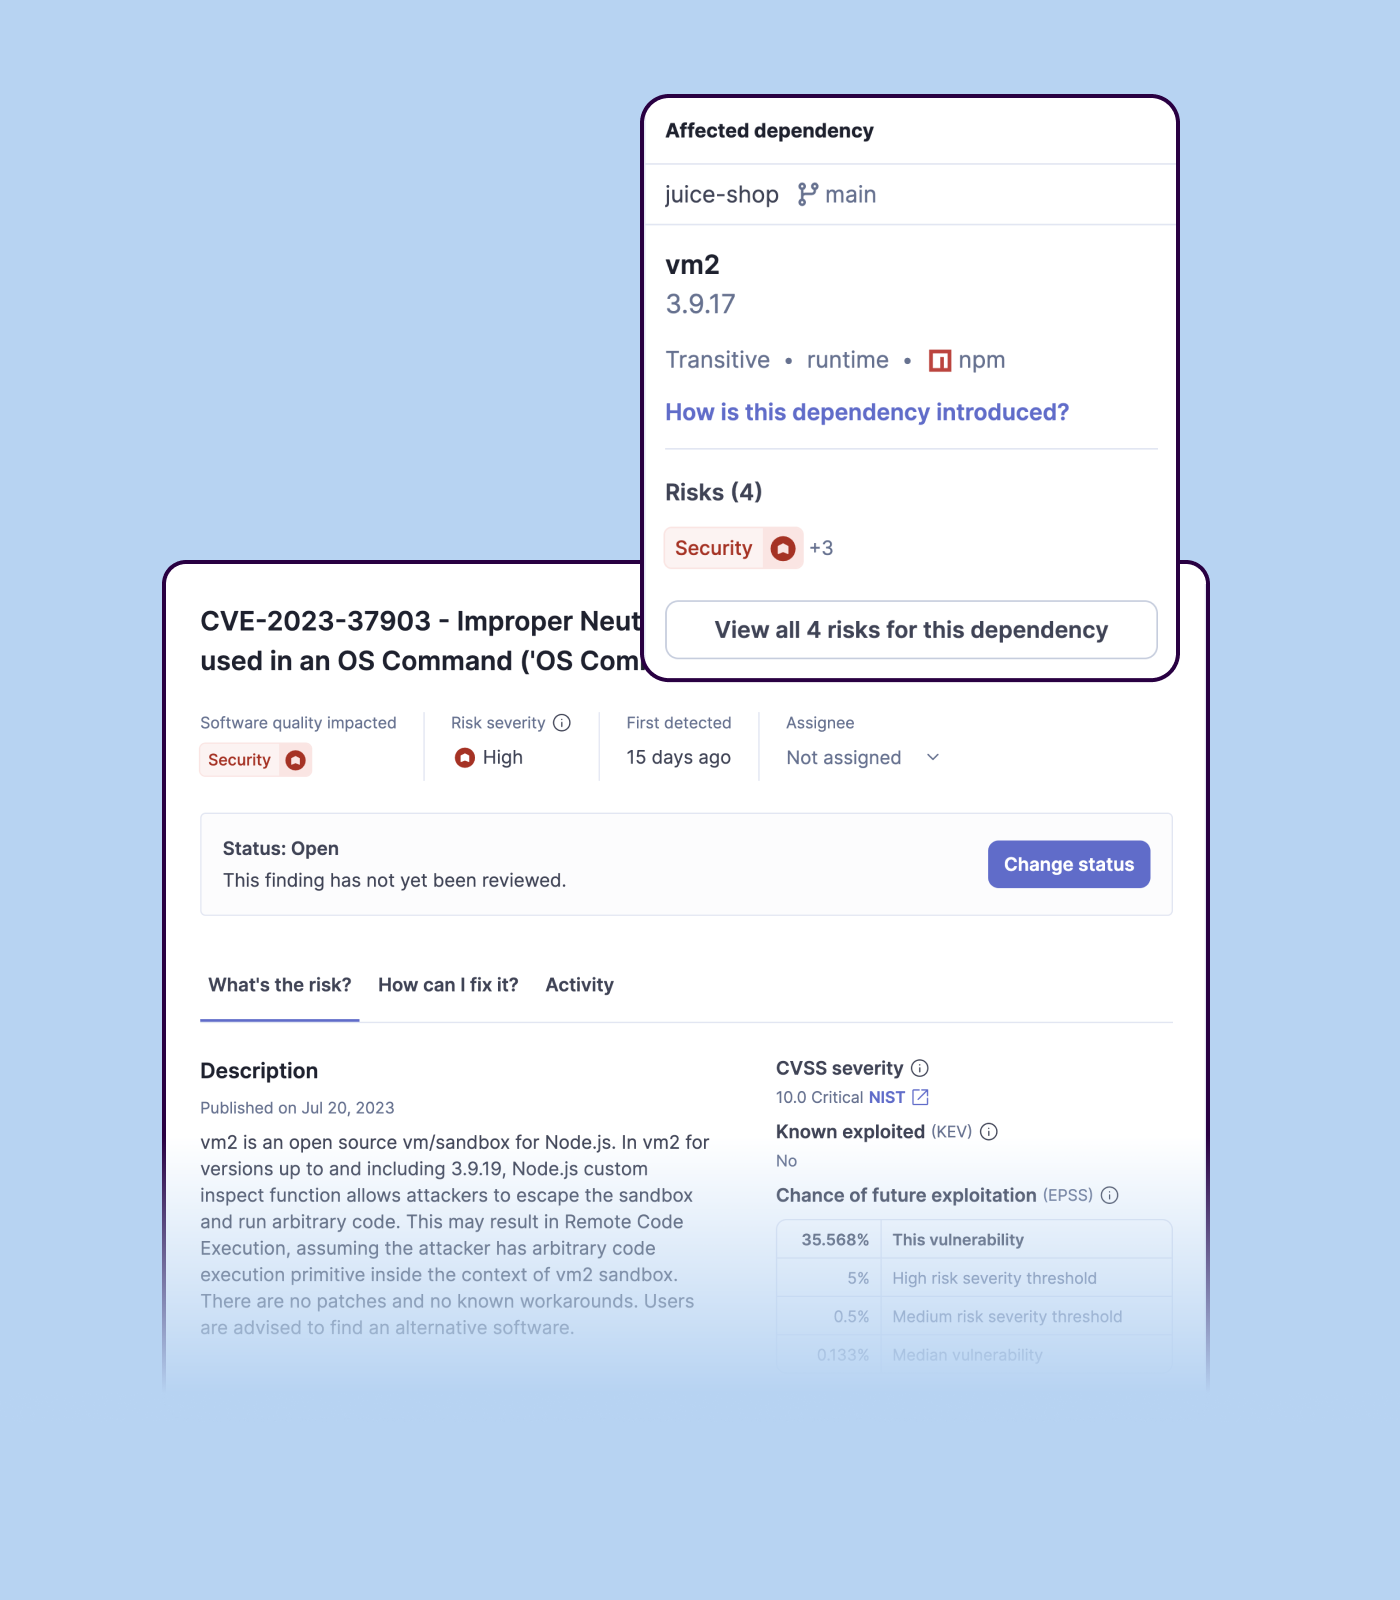
Detecting bugs and vulnerabilities: SonarQube can identify a wide range of bugs and vulnerabilities in code, such as null pointer exceptions, SQL injection, and cross-site scripting (XSS) attacks. It uses static analysis to analyze the code and identify potential issues, and it can also integrate with dynamic analysis tools to provide even more detailed analysis.
Measuring code quality: SonarQube can measure a wide range of code quality metrics, such as cyclomatic complexity, duplicated code, and code coverage. This can help teams understand the quality of their code and identify areas that need improvement.
Providing actionable insights: SonarQube provides detailed information about issues in the code, including the file and line number where the issue occurs and the severity of the issue. This makes it easy for developers to understand and address issues in the code.
Integrating with other tools: SonarQube can be integrated with a wide range of development tools and programming languages, such as Git, Maven, and Java. This allows teams to use SonarQube in their existing development workflow and take advantage of its powerful code analysis capabilities.
Managing technical debt: SonarQube provides metrics and insights on the technical debt on the codebase, enabling teams to better prioritize issues to improve the quality of the code.
Compliance with coding standards: SonarQube can check the code against industry standards like OWASP, CWE and more, making sure the code is compliant with security and coding standards.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Importing a new custom quality profile on SonarQube is a bit tricky, it can be made easier
Every second time when we want to rerun the server, we have to restart the whole system, otherwise, the server stops and closes automatically
When we generate a new report a second time and try to access the report, it shows details of the old report only and takes a lot of time to get updated with the details of the new and fresh report generated
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
When I first used the tool in my home systems MANY years ago, I wished for a Business version. I was once at a focus group for a major antivirus company, and one attendee’s feedback to “what could we do better?” was “buy out MalwareBytes and add it to your tool”. I’ve used the Business version since it first became available, and have continued to be a dedicated user through the many iterations and improvements
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It simply works. It doesn't require the hand-holding and monitoring that some other solutions do. It's simple to deploy and maintain, and adding custom content such as Exceptions require minimal effort. I’ve had to add a few exceptions for internal-use, in-house-developed tools, but it’s quite simple to do so within the online interface
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
As I mentioned, we have only email support. Their phone support was very expensive. If we ever have any issues, we have to email them and wait for their response. In most cases, I have figured out the issue on my own. The software is very stable so we haven't used their support much.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We we easily able to integrate the SonarQube steps into our TFS process via the Microsoft Marektplace, we didn't have the need to call SonarQube support. We've used their online documentation and community forum if we ran into any issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I first implemented this more than 10 years ago, when it required an in-site setup with SQL Server (or SQL Express), and even that was pretty easy. With the move to centralized web management some treats ago, it’s become even easier to deploy
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's no contest. Cisco AMP, Umbrella and Endpoint use vast amounts of resources and provide little protection when compared with Malwarebytes. One client recently replaced Cisco with MWB and found over 7,300 vulnerabilities on 352 endpoints, including 120 listed as Critical and 7,180 listed as High, with CVE's dating back to 2008.
SonarQube is an open-source. It's a scalable product. The costs for this application, for the kind of job it does, are pretty descent. Pipeline scan is more secured in SonarQube. Its a very good tool and its support multiple languages. Its main core competency is of static code analysis and that is why SonarQube exists and it does it exceedingly well. The quality of scan on code convention, best practices, coding standards, unit test coverage etc makes them one of the best competent tool in the market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The ease of remediation has saved our IT team a number of hours manually installing, for example, the free version of Malwarebytes to remove infections, and then cleaning the machine up. Being able to centrally send commands to clean the device is much more efficient.
The centralised management has also alerted us to infections on machines that we might not otherwise have known about, as the existing AV had not detected them, saving us potential data loss, or system damage.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive ROI from the standpoint of flagging several issues that would have otherwise likely been unaddressed and caused more time to be spent closer to launch
Slightly positive ROI from time-saving perspective (it's an automated check which is nice, but depending on the issues it finds, can take developers time to investigate and resolve)