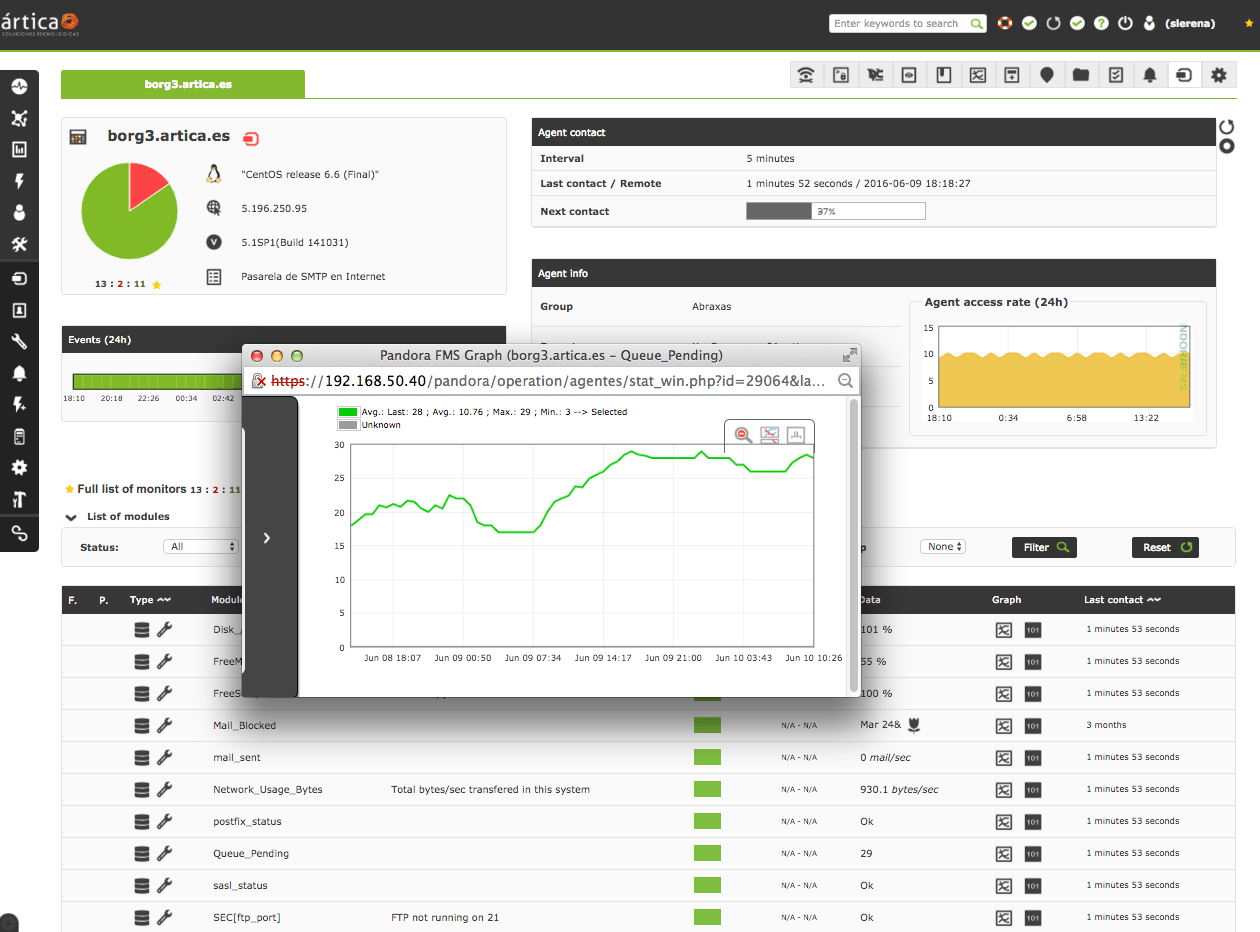
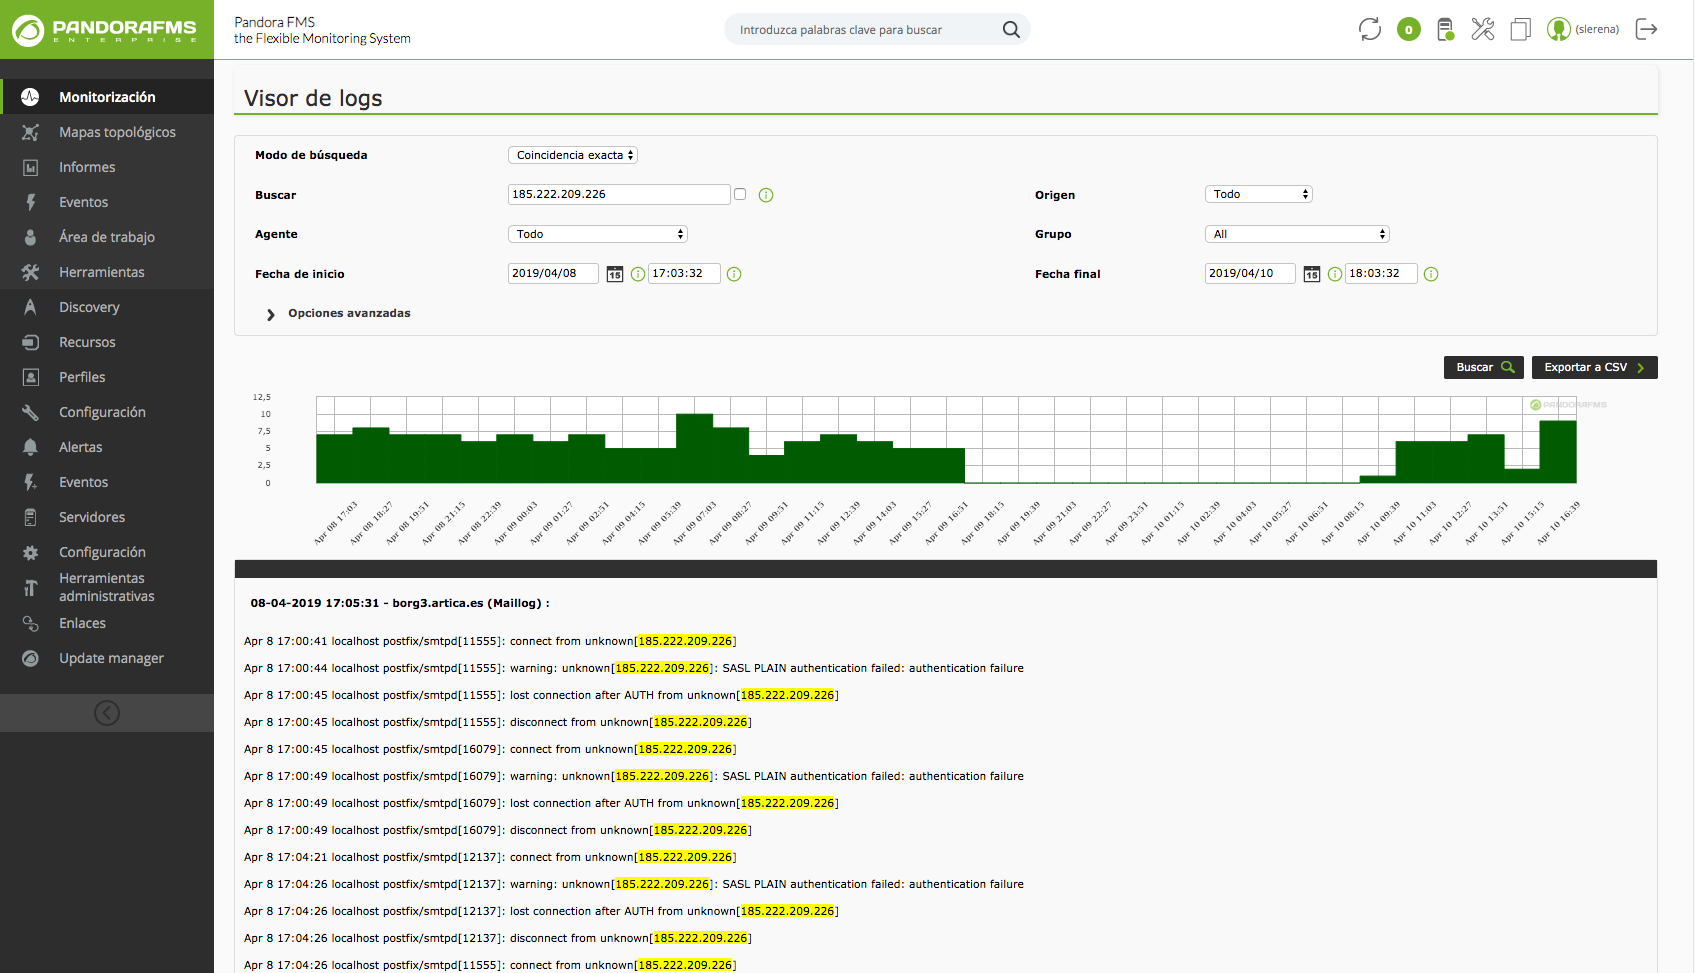
Pandora FMS is a monitoring solution. It is presented as ideal for medium and big-sized environments with at least 100 devices. Users can monitor any device, infrastructure, application, IT as well as business processes and services. It allows business users to obtain information from their concerns in real time, visualizing the data in a direct way. The solution boasts users among companies and organizations in more than 40 countries around the world, who according…
$2,990
100 nodes
Splunk Observability Cloud
Score8.5 out of 10
N/A
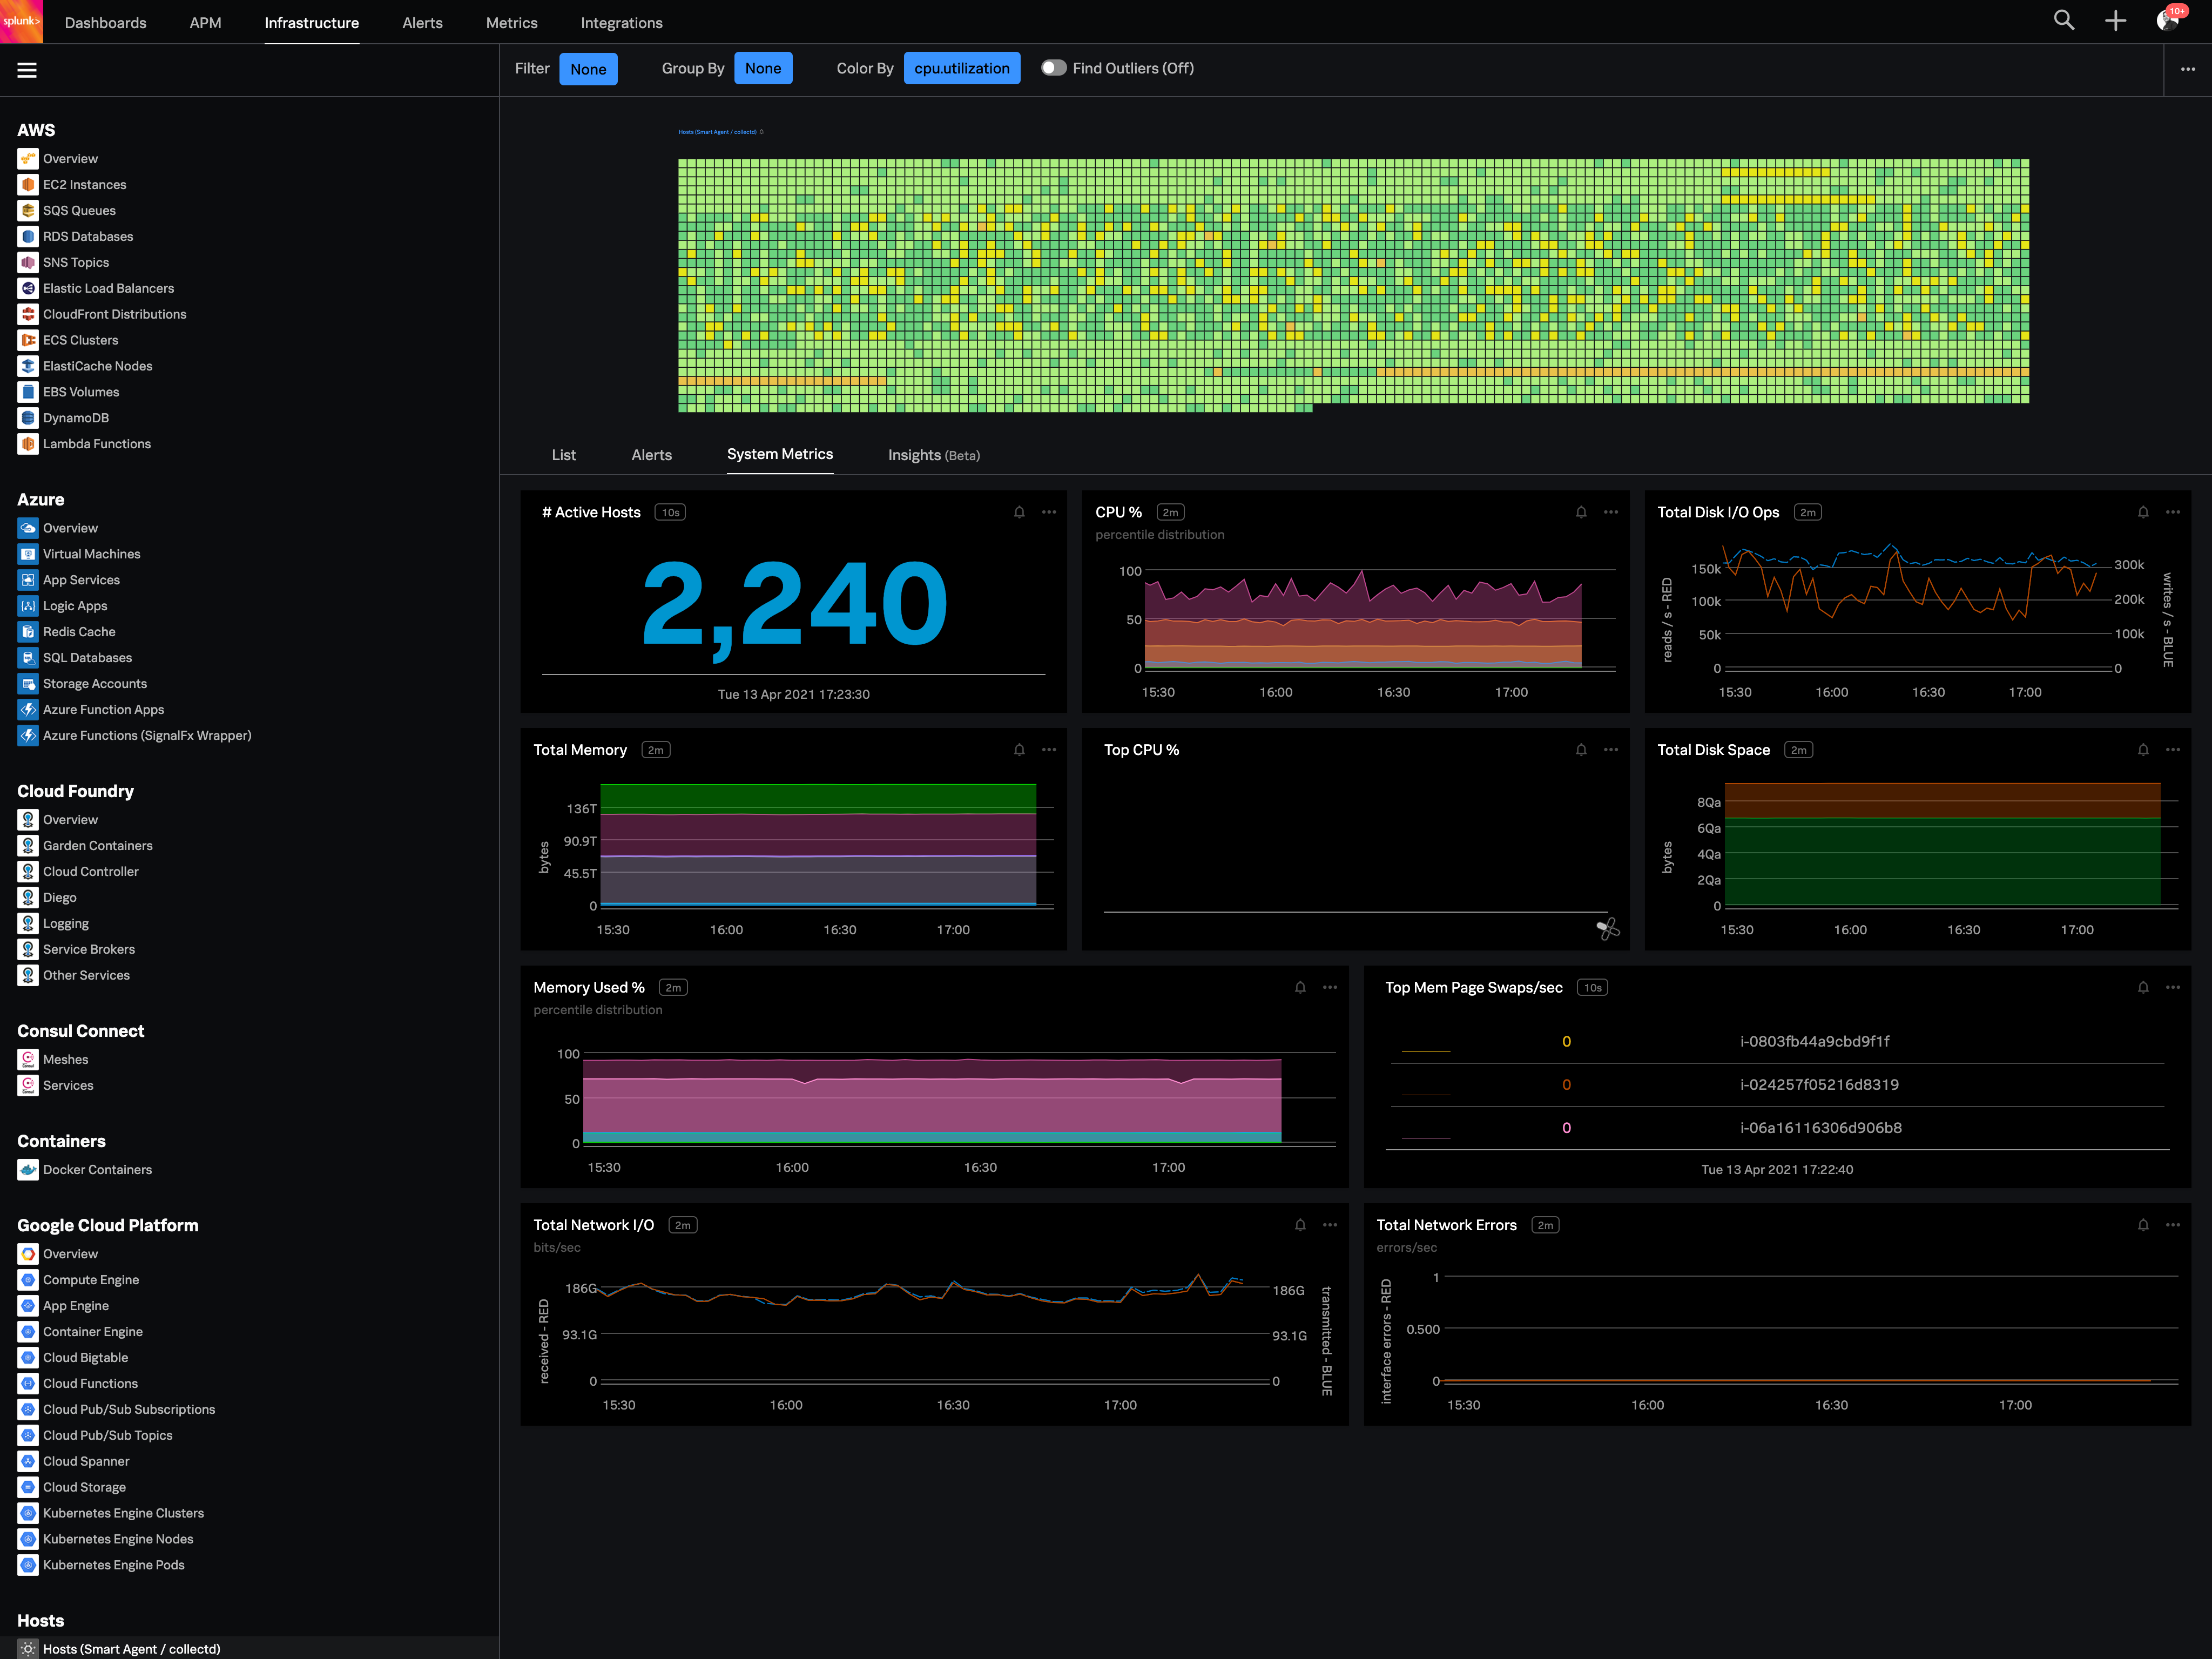
Splunk Observability Cloud aims to enable operational agility and better customer experience through real-time AI-driven streaming analytics allowing accurate alerts in seconds. It is designed to shorten MTTD and MTTR by providing real-time visibility into cloud infrastructure and services.
$180
per year per host
Pricing
Pandora FMS
Splunk Observability Cloud
Editions & Modules
NMS Edition
$2,990
100 nodes
Enterprise Edition
$4,250
100 nodes
Infrastructure
$15
per month (billed annually) per host
App & Infra
$60
per month (billed annually) per host
End-to-End
$75
per month (billed annually) per host
Offerings
Pricing Offerings
Pandora FMS
Splunk Observability Cloud
Free Trial
Yes
Yes
Free/Freemium Version
Yes
No
Premium Consulting/Integration Services
Yes
No
Entry-level Setup Fee
Required
No setup fee
Additional Details
Licensed for individual nodes (agents), starting from 100 nodes.
I believe Pandora FMS is a solution that adapts to any type of scenario; it's useful for small businesses as well as large organizations. It more than meets the need to have a comprehensive monitoring system capable of sending alerts instantly and consulting historical data, logs, and trends. Additionally, for small businesses, the free version will be more than sufficient in most cases. And for those who do not want to deploy the service on-premise, there is an option for MaaS (Monitoring as a Service).
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Its great if you need real-time visibility across complex or regulated environments. Also strong for hybrid or multi-cloud setups where uptime, observability and fast IR are required. It’s probably overkill for smaller teams or environments that don’t have constant changes or compliance reporting needs. It's expensive and has a steep learning curve. Also, in my opinion, do not get yourself into a consumption based model. Costs can certainly get out of control quickly.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The first one is its Kubernetes container monitoring.
I really like this features because as we know how much K8s is vast and to manually monitor each part of the Kubernetes it takes so much time but Splunk Observability Cloud makes it easier. And even once we integrate K8s with Splunk Observability Cloud it gives us some prebuilt dashboards which gives holistic view of our Cluster and its nodes, pods, etc.
The dashbaord feature of Splunk Observability Cloud, it gives us full flexibility to customize our dashboard with a wide range of predefined chart types.
Now it also supports OTEL, which is a plus point for observability. As now everyone is moving towards Otel and in current market there are only few tools who supports OTEL based integrations, Splunk Observability Cloud is one out of them.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
You can use table-like functionality to generate dashboards, but these queries are heavy on the system.
It could be easier to give insight into what type of line parsing is used for specific documents in a company-managed environment and/or show ways to gain the insights needed.
I would like to see ways to anonymize specific data for shared reports without pre-formatting this in a dashboard on which reports could be based.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Good: Stable system with low error rate Easy to use for simple use cases Bad: UI is not very clear for complex usage Mobile view (when logged in from phone) is bad No library for .net
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The solution is very complete, and even includes extras such as IPAM. Deployment can be a bit unintuitive at first, but once you become familiar with the solution and thanks to its automatic deployment options it ends up being easier than it seemed. The power and options of the solution are its greatest virtue.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
When there is an issue, it’s a win if one can easily identify the root cause. To do the same, it should allow the user to dig deep with multiple data points and compare the data and identify the anomaly. In this use case, it’s good to drive from Splunk 011y.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Before using Pandora FMS, tests were carried out with all these tools:
Nagios
Zabbix
System Center Operations Manager (SCOM)
IBM Tivoli
PRTG
SolarWinds
Pandora FMS allows simple customization by making adjustments to text files, developing agent add-ons without the need to be a programmer, there is no scenario where we could not take data and save it in PandoraFMS, IoT, industrial products, and everything that any client needs to monitor.
Splunk Infrastructure Monitoring provides far superior options for anybody using a complex hybrid multi-cloud environment and allows both your SOC and NOC to work together on the same data while driving their own insights. We found other products are still in the old world view of servers and agents residing together within a single data centre, but modern apps are no longer like this.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info