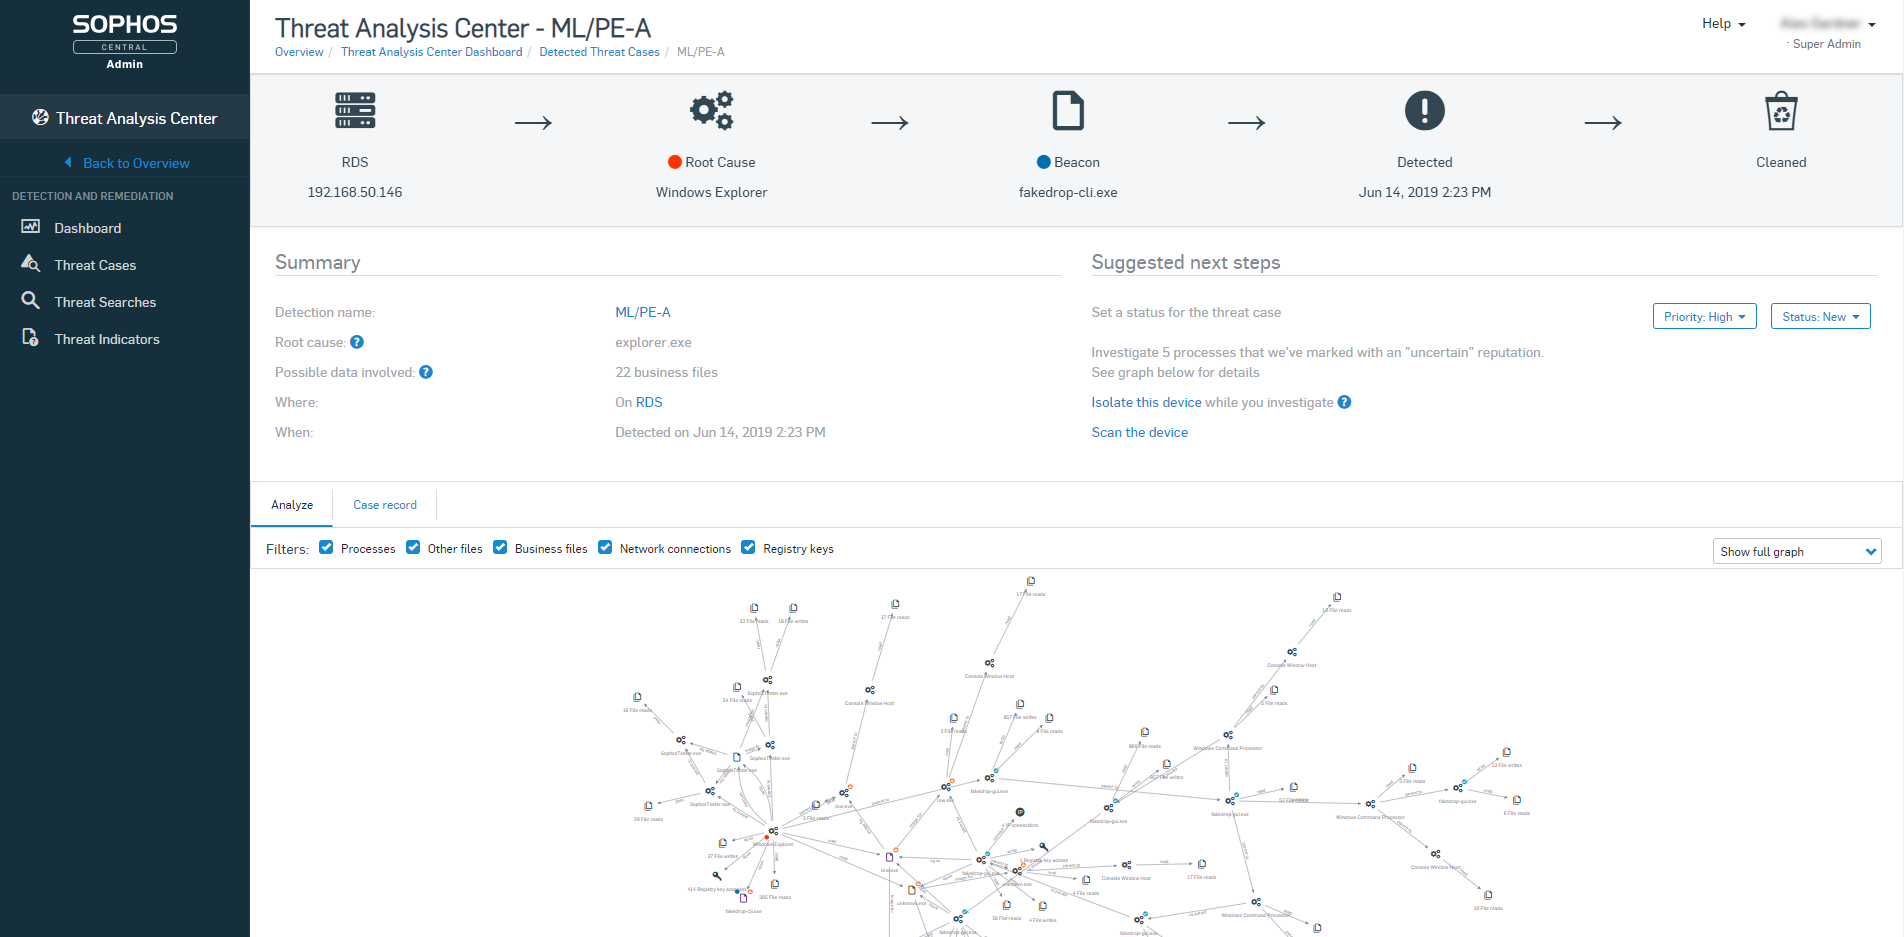
Sophos Endpoint Protection (Sophos EPP) with Intercept X is an endpoint security product providing an antivirus / antimalware solution that when upgraded with Intercept X or Intercept X Advanced provides advanced threat detection and EDR capabilities.
$28
per year per user
Splunk Cloud Platform
Score8 out of 10
N/A
Splunk Cloud Platform is a data platform service thats help users search, analyze, visualize and act on data. The service can go live in as little as two days, and with an IT backend managed by Splunk experts.
N/A
Pricing
Sophos Intercept X
Splunk Cloud Platform
Editions & Modules
Intercept X Advanced
$28
per year per user
Intercept X Advanced with XDR
$48
per year per user
Sophos Managed Threat Response
$79
per year per user
No answers on this topic
Offerings
Pricing Offerings
Sophos Intercept X
Splunk Cloud Platform
Free Trial
No
No
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
Pricing is for a 3-year commitment. Government and Education pricing available.
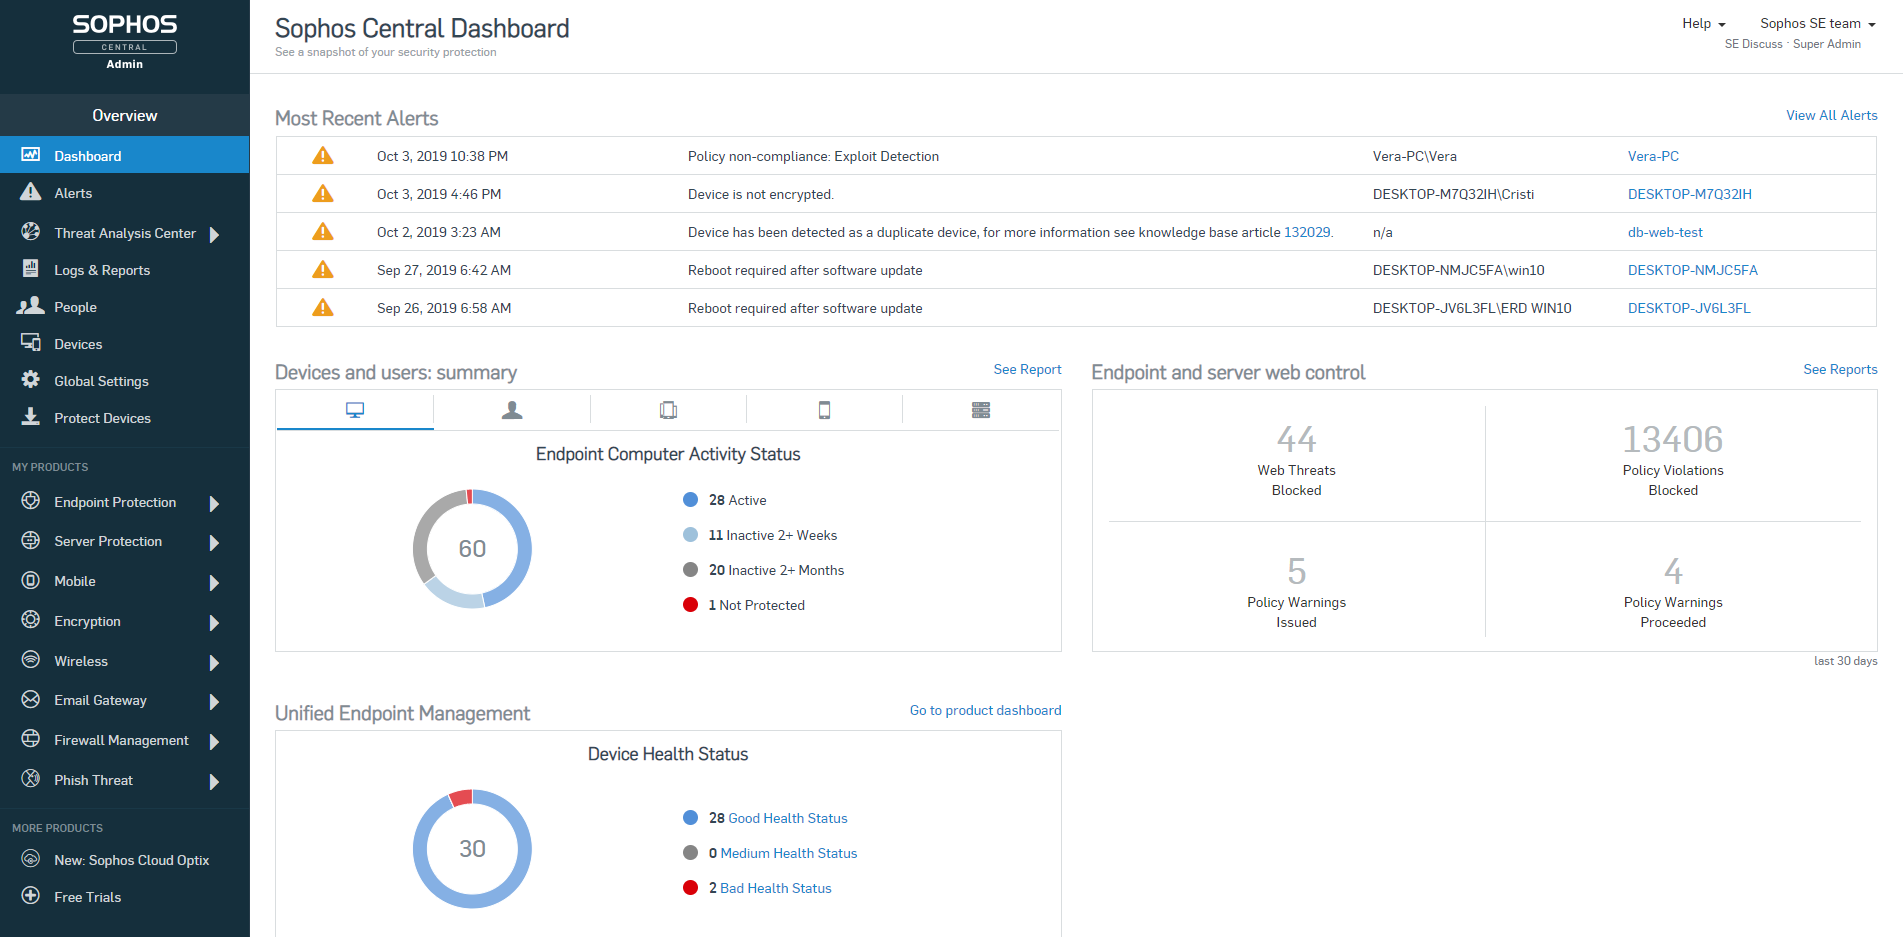
To be frank, this product is fairly expensive. So I would recommend this to companies that are mid-sized or larger to condone the cost of the purchase. It does save me a significant amount of time in my day - being able to glance at the dashboard and see if there are any outstanding issues that require my attention, as not much digging must be done to accomplish this. So for our company, with a short-staffed IT department, it's incredibly helpful to us. We also qualify for Educational pricing which brings the cost down - which helps tremendously
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Splunk is excellent when all your data is in one location. Its ability to correlate all that data is intuitive (once the hurdle of learning the query language is overcome). It is also easy to standardize the presentation of information to the company. When data is siloed/standalone, other systems can be cheaper and faster to implement.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sophos Intercept X is great at preventing malware infections and rolling back their effects. I have seen this happen hundreds of times since we installed it
When combined with Sophos Central, you have an easy to use dashboard where you can manage all installations from a single pane of glass.
It's easy to deploy on machines and stays updated.
Good reporting features including alerts sent to the admin if there's ever something wrong with it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
This SIEM consolidates multiple data points and offers several features and benefits, creating custom dashboards and managing alert workflows.
Splunk Cloud provides a simple way to have a central monitoring and security solution. Though it does not have a huge learning curve, you should spend some time learning the basics.
Splunk Cloud enables me to create and schedule statistical reports on network use for Management.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sophos OOTB policies are very strict and they don't offer anything less strict without you creating new custom policies. I'm sure this is deliberate because the product starts you out in the safest way possible but it means that you will have lots of calls to your tech support desk when you first deploy it unless you do somewhat extensive testing beforehand.
Sophos Intercept X is currently broken (at least the DLP component) by having secure boot turned on in the UEFI/BIOS. If any user wants to be able to write data to a USB drive or floppy from their PC (yes we still have a couple users who need to use floppies) we have to turn off secure boot on their PC, even if the DLP policy for that user/PC combination specifies that the user and PC are allowed to write to USB/floppy. This would be a very serious problem if it weren't for the fact that we have very few users who need to write files to USB. For us it's OK but I bet it would be a deal-breaker for others.
I don't see a whole lot of evidence that Intercept X is any different than any other anti-virus, so maybe their admin alerts just don't clearly identify when they have identified a zero-day threat or maybe we just haven't had any zero-day threats.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The usability has never been a problem. Sophos Intercept X is a program you can install and let protect your company without much intervention. Apart from a few policies, Sophos will keep you protected better than most any product on the market. Sophos Intercept X works quite well when you are looking to "tighten your grip" on user's access to websites, programs, and add-ons.
Splunk AI Assistant for SPL is good tool, as I said, it is really useful for educational purpose, taking in its hands small and simple tasks (ex:small query dashboard,...), but it's not a ten because the contextual memory for complex issues/dashboarding/reports etc can be limited, and can sometime suggets none optimized query which are not always checked by teammates and can cause issue on the long term.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Most of the support reps are fantastic. There have been a few though that have had to be escalated via Account Manager when they haven't followed up but this is a rare instance, and often followed up by the Support Manager for APAC.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Splunk Cloud support is sorely lacking unfortunately. The portal where you submit tickets is not very good and is lacking polish. Tickets are left for days without any updates and when chased it is only sometimes you get a reply back. I get the feeling the support team are very understaffed and have far too much going on. From what I know, Splunk is aware of this and seem to be trying to remedy it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Webroot Endpoint Protection is not even in the same league as Sophos Intercept-X. I have tested and compared both sides by side, run simulations and it's not even close. Plus the Sophos central management is so much better. Easier to view user activities and apply policies and remediate threats. Sophos is the clear winner between these two products.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Vs elastic: - SPL's statistical functions superior to KQL for complex correlations - Better enterprise support, less operational overhead - Splunk Cloud Platform's detection engineering more mature vs Sentinel: - SPL more powerful than KQL for custom analytics - Better cross-platform visibility (non-Azure environments) vs Datadog - SPL enables deeper forensic Investigations - Superior compliance/audit capabilities
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Once our technical and commercial areas got certified, the ROI over the time spent, is great. Actual customers, and/or new ones with other tools, feel safe and advised, once they get in touch with us.
When Sophos EndPoint is being compared against Web Management Tools (competitors), we have failed to deliver, nevertheless, there is a version of Sophos Central (Cloud) which achieves this requirement at 100% and more, since is Cloud Based (on AWS).
We are grateful to be on Sophos "Radar" as a Platinum Partner, and "The Americas" valued partner, we have seen our business grow, thanks to this kind of technology, throughout the years.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info