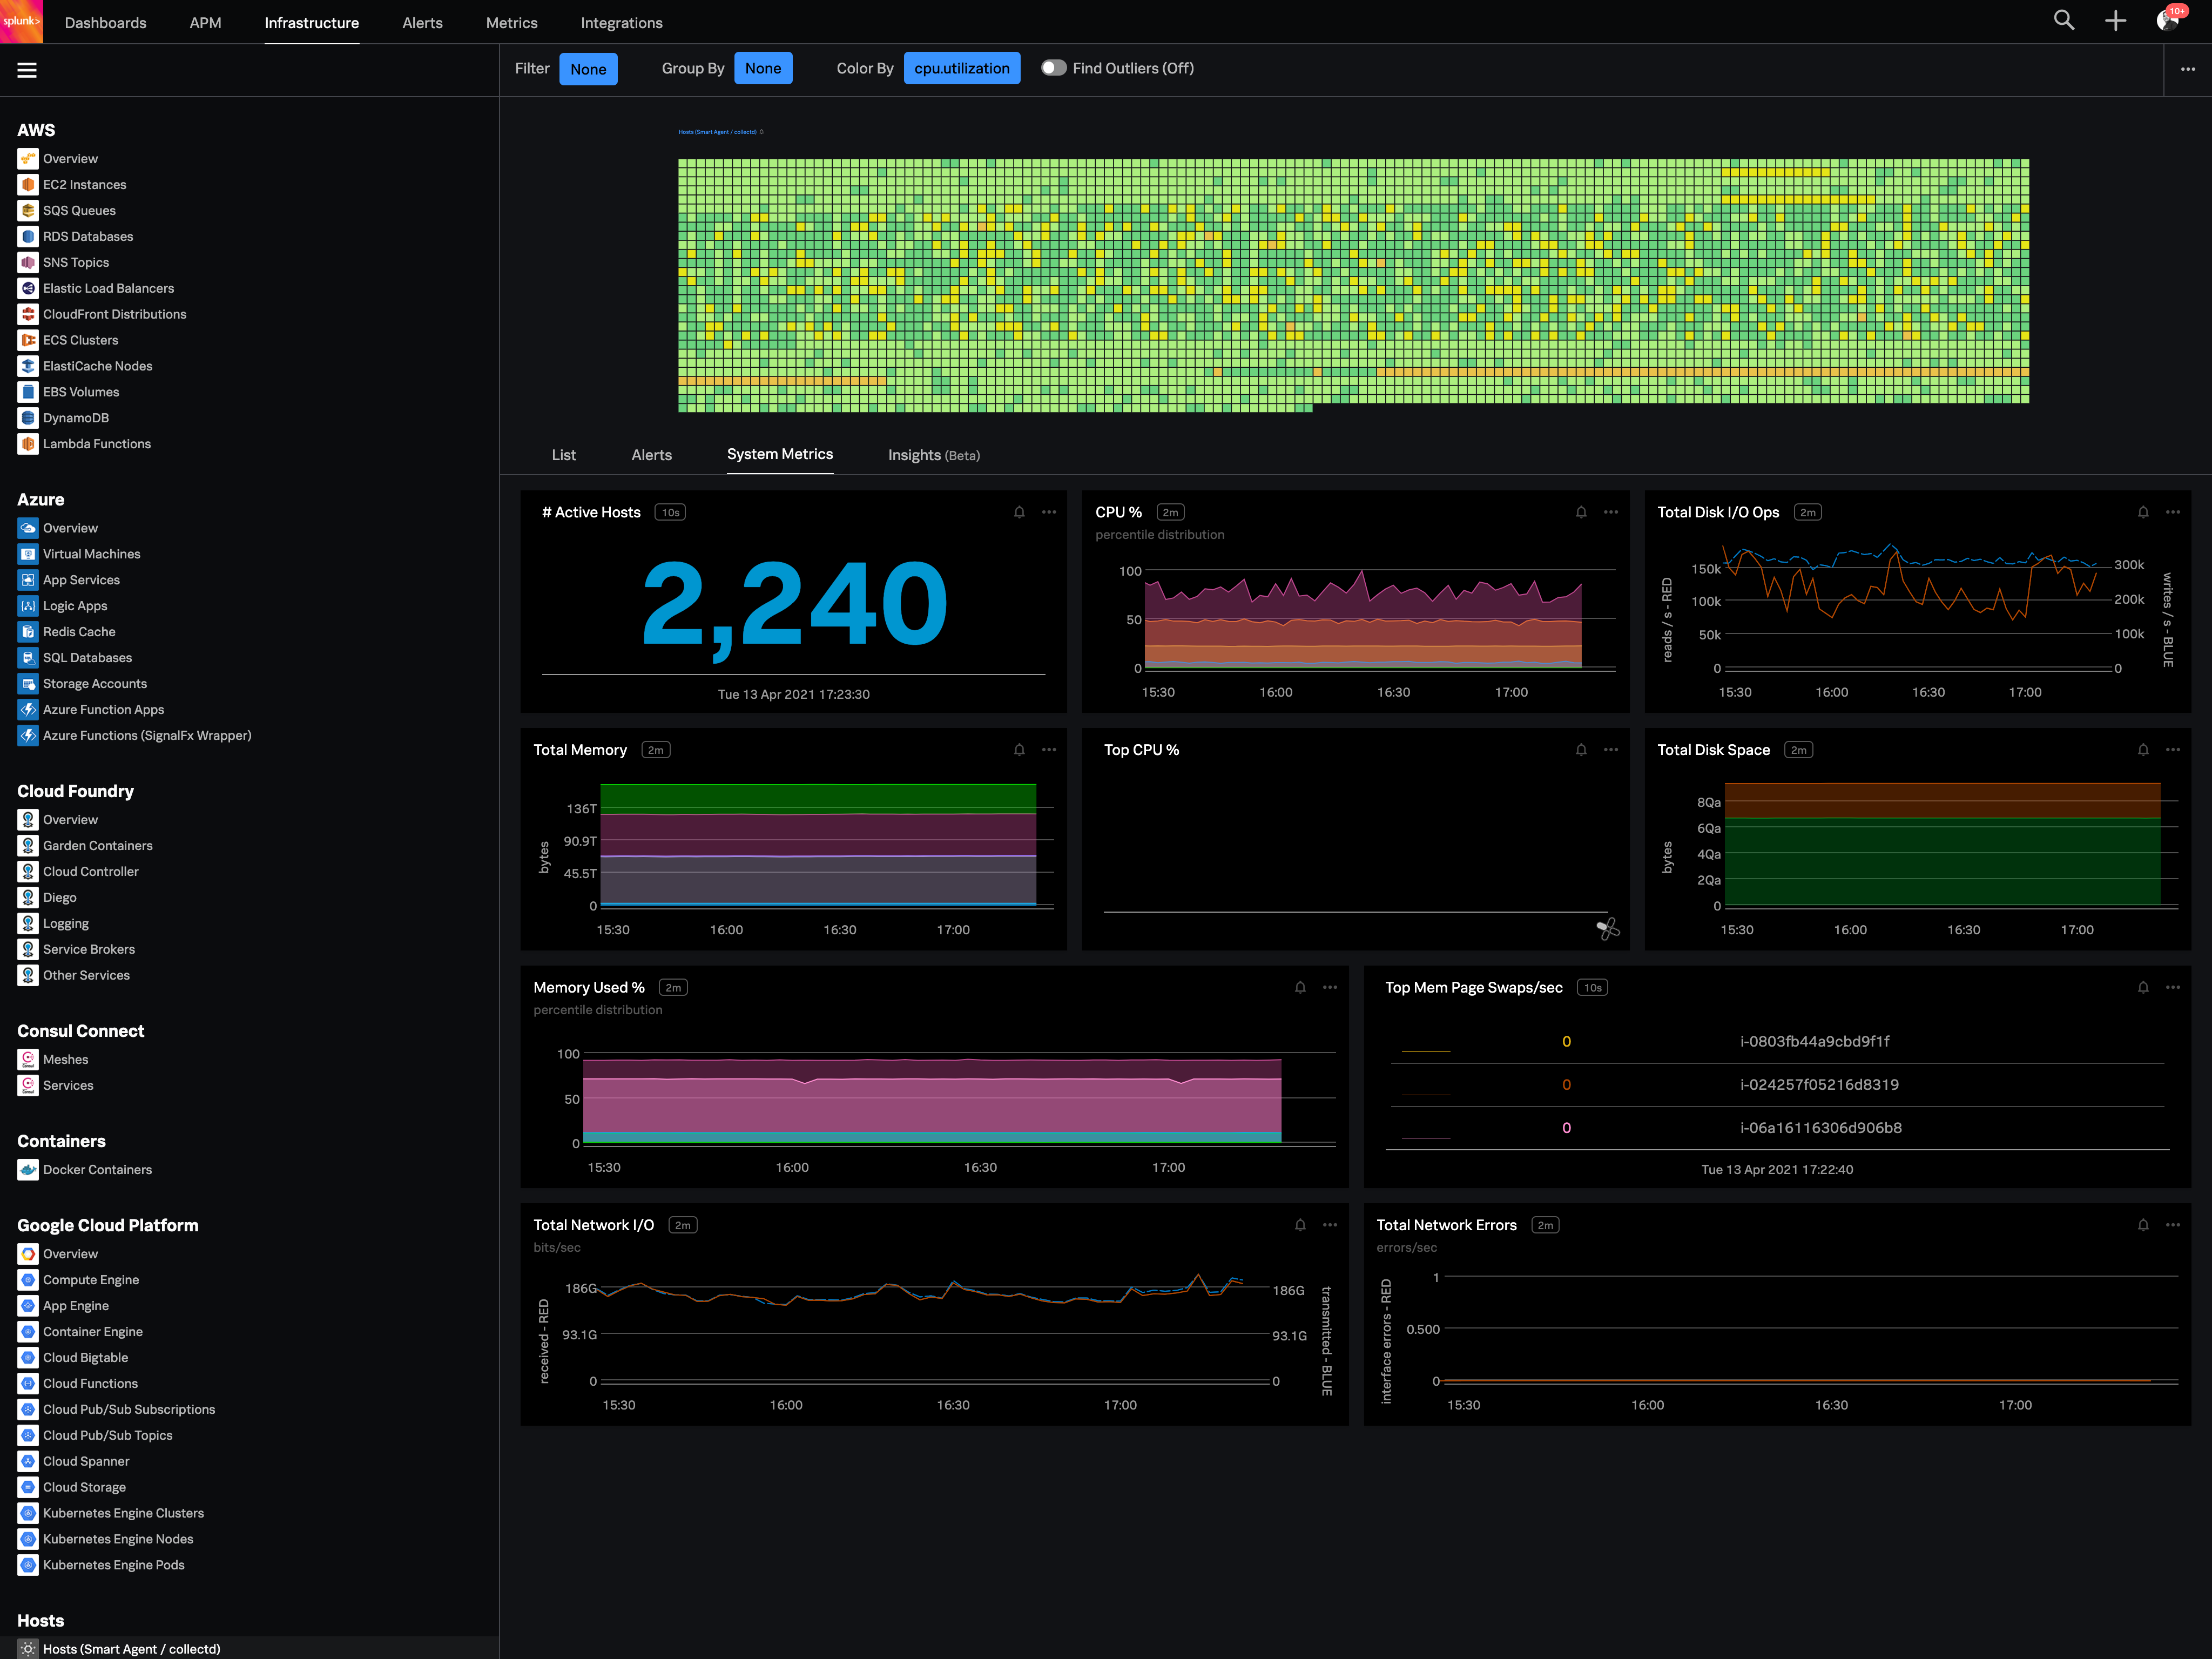
Splunk Observability Cloud aims to enable operational agility and better customer experience through real-time AI-driven streaming analytics allowing accurate alerts in seconds. It is designed to shorten MTTD and MTTR by providing real-time visibility into cloud infrastructure and services.
$180
per year per host
Tenable Nessus
Score8.8 out of 10
N/A
Tenable headquartered in Columbia offers Nessus, a vulnerability scanning and security assessment solution used to analyze an entity's security posture, vulnerability testing, and provide configuration assessments.
Its great if you need real-time visibility across complex or regulated environments. Also strong for hybrid or multi-cloud setups where uptime, observability and fast IR are required. It’s probably overkill for smaller teams or environments that don’t have constant changes or compliance reporting needs. It's expensive and has a steep learning curve. Also, in my opinion, do not get yourself into a consumption based model. Costs can certainly get out of control quickly.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It is an excellent tool for scanning servers, workstations, and network devices to identify missing patches and misconfiguration; we regularly use it to confirm patch effectiveness after the update; it also helps us for preparing audits such as iso 27001, and regulatory requirements, it also helps us to identify open ports and services that violate security.
The first one is its Kubernetes container monitoring.
I really like this features because as we know how much K8s is vast and to manually monitor each part of the Kubernetes it takes so much time but Splunk Observability Cloud makes it easier. And even once we integrate K8s with Splunk Observability Cloud it gives us some prebuilt dashboards which gives holistic view of our Cluster and its nodes, pods, etc.
The dashbaord feature of Splunk Observability Cloud, it gives us full flexibility to customize our dashboard with a wide range of predefined chart types.
Now it also supports OTEL, which is a plus point for observability. As now everyone is moving towards Otel and in current market there are only few tools who supports OTEL based integrations, Splunk Observability Cloud is one out of them.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Nessus is best at performing vulnerability scans, in fact, it gives findings and moreover accurate findings of the assessments. It does not do penetration testing or exploit the vulnerabilities because it is concerned about scanning the systems/applications.
In fact, Nessus has multiple profiles/policies to perform different types of scans such as, scans oriented for PCI-DSS, malware scans, web application scans, bad shell shock detection scan to name a few.
Nessus has the ability to classify the vulnerabilities into risk-based categories from critical to even informational which I think is one of the things that separates Nessus from other vulnerability scanners.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
You can use table-like functionality to generate dashboards, but these queries are heavy on the system.
It could be easier to give insight into what type of line parsing is used for specific documents in a company-managed environment and/or show ways to gain the insights needed.
I would like to see ways to anonymize specific data for shared reports without pre-formatting this in a dashboard on which reports could be based.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The tool has lots of options for setting up before scanning any device, this methodology could be simplified further with default configuration for various devices predefined, anyhow we can use this technique by making use of policies.
For advanced users we cannot disable the plugins inside the plugin groups, we can enable the whole set of plugins at a time, for few hundreds its ok, but thousands of plugins are of waste of resource and time.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Good: Stable system with low error rate Easy to use for simple use cases Bad: UI is not very clear for complex usage Mobile view (when logged in from phone) is bad No library for .net
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Nessus is best and easy to use application for Vulnerabilities finding and reporting, it has multiple platforms and wide scope covering almost all devices for security improvement so far, thus we are very likely to continue its services.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
When there is an issue, it’s a win if one can easily identify the root cause. To do the same, it should allow the user to dig deep with multiple data points and compare the data and identify the anomaly. In this use case, it’s good to drive from Splunk 011y.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Tenable Nessus is a great product and provides a lot of value, but it is difficult to set up and use and the amount of data it generates can be overwhelming. It does help us prioritize based on the severity of the detection, however there are sometimes mitigating factors that we have implemented that Nessus does not account for, which causes lots of noise in the reports.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I haven't needed to contact support yet. But issues are easily solved with a quick internet search which means support and by extension, the larger community are involved and knowledgeable.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Splunk Infrastructure Monitoring provides far superior options for anybody using a complex hybrid multi-cloud environment and allows both your SOC and NOC to work together on the same data while driving their own insights. We found other products are still in the old world view of servers and agents residing together within a single data centre, but modern apps are no longer like this.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sometimes when we identify a vulnerability with Nessus that has an exploit, we made a proof of concept with Metasploit in order to show to the IT managers the importance of the software/hardware hardening.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Nessus certainly has a positive impact while me while performing my job, either as security research, or performing vulnerability assessments for clients. It gives a lot of information about the system/application after performing scans. The number of false positives is also less compared to other vulnerability scanners.
The professional edition is very useful as policy templates available in this edition are very handy and useful even to perform compliance scan like PCI DSS scan.
Also, the ability to export the scan results into reports in formats like HTML, PDF is very useful which could be for performing system/application reviews.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info