TrustRadius: an HG Insights company

What is Identity Rules?

Identity Rules is a unified Identity Threat Detection and Response (ITDR) and Identity Visibility and Intelligence Platform (IVIP) developed for security teams at regulated enterprises. The platform combines real-time detection of identity-based threats with continuous visibility and intelligence across human and non-human identities, spanning Active Directory, Okta, Microsoft Entra ID, AWS IAM, Google Workspace, Oracle Database, and Linux environments.

Read more details.

Media

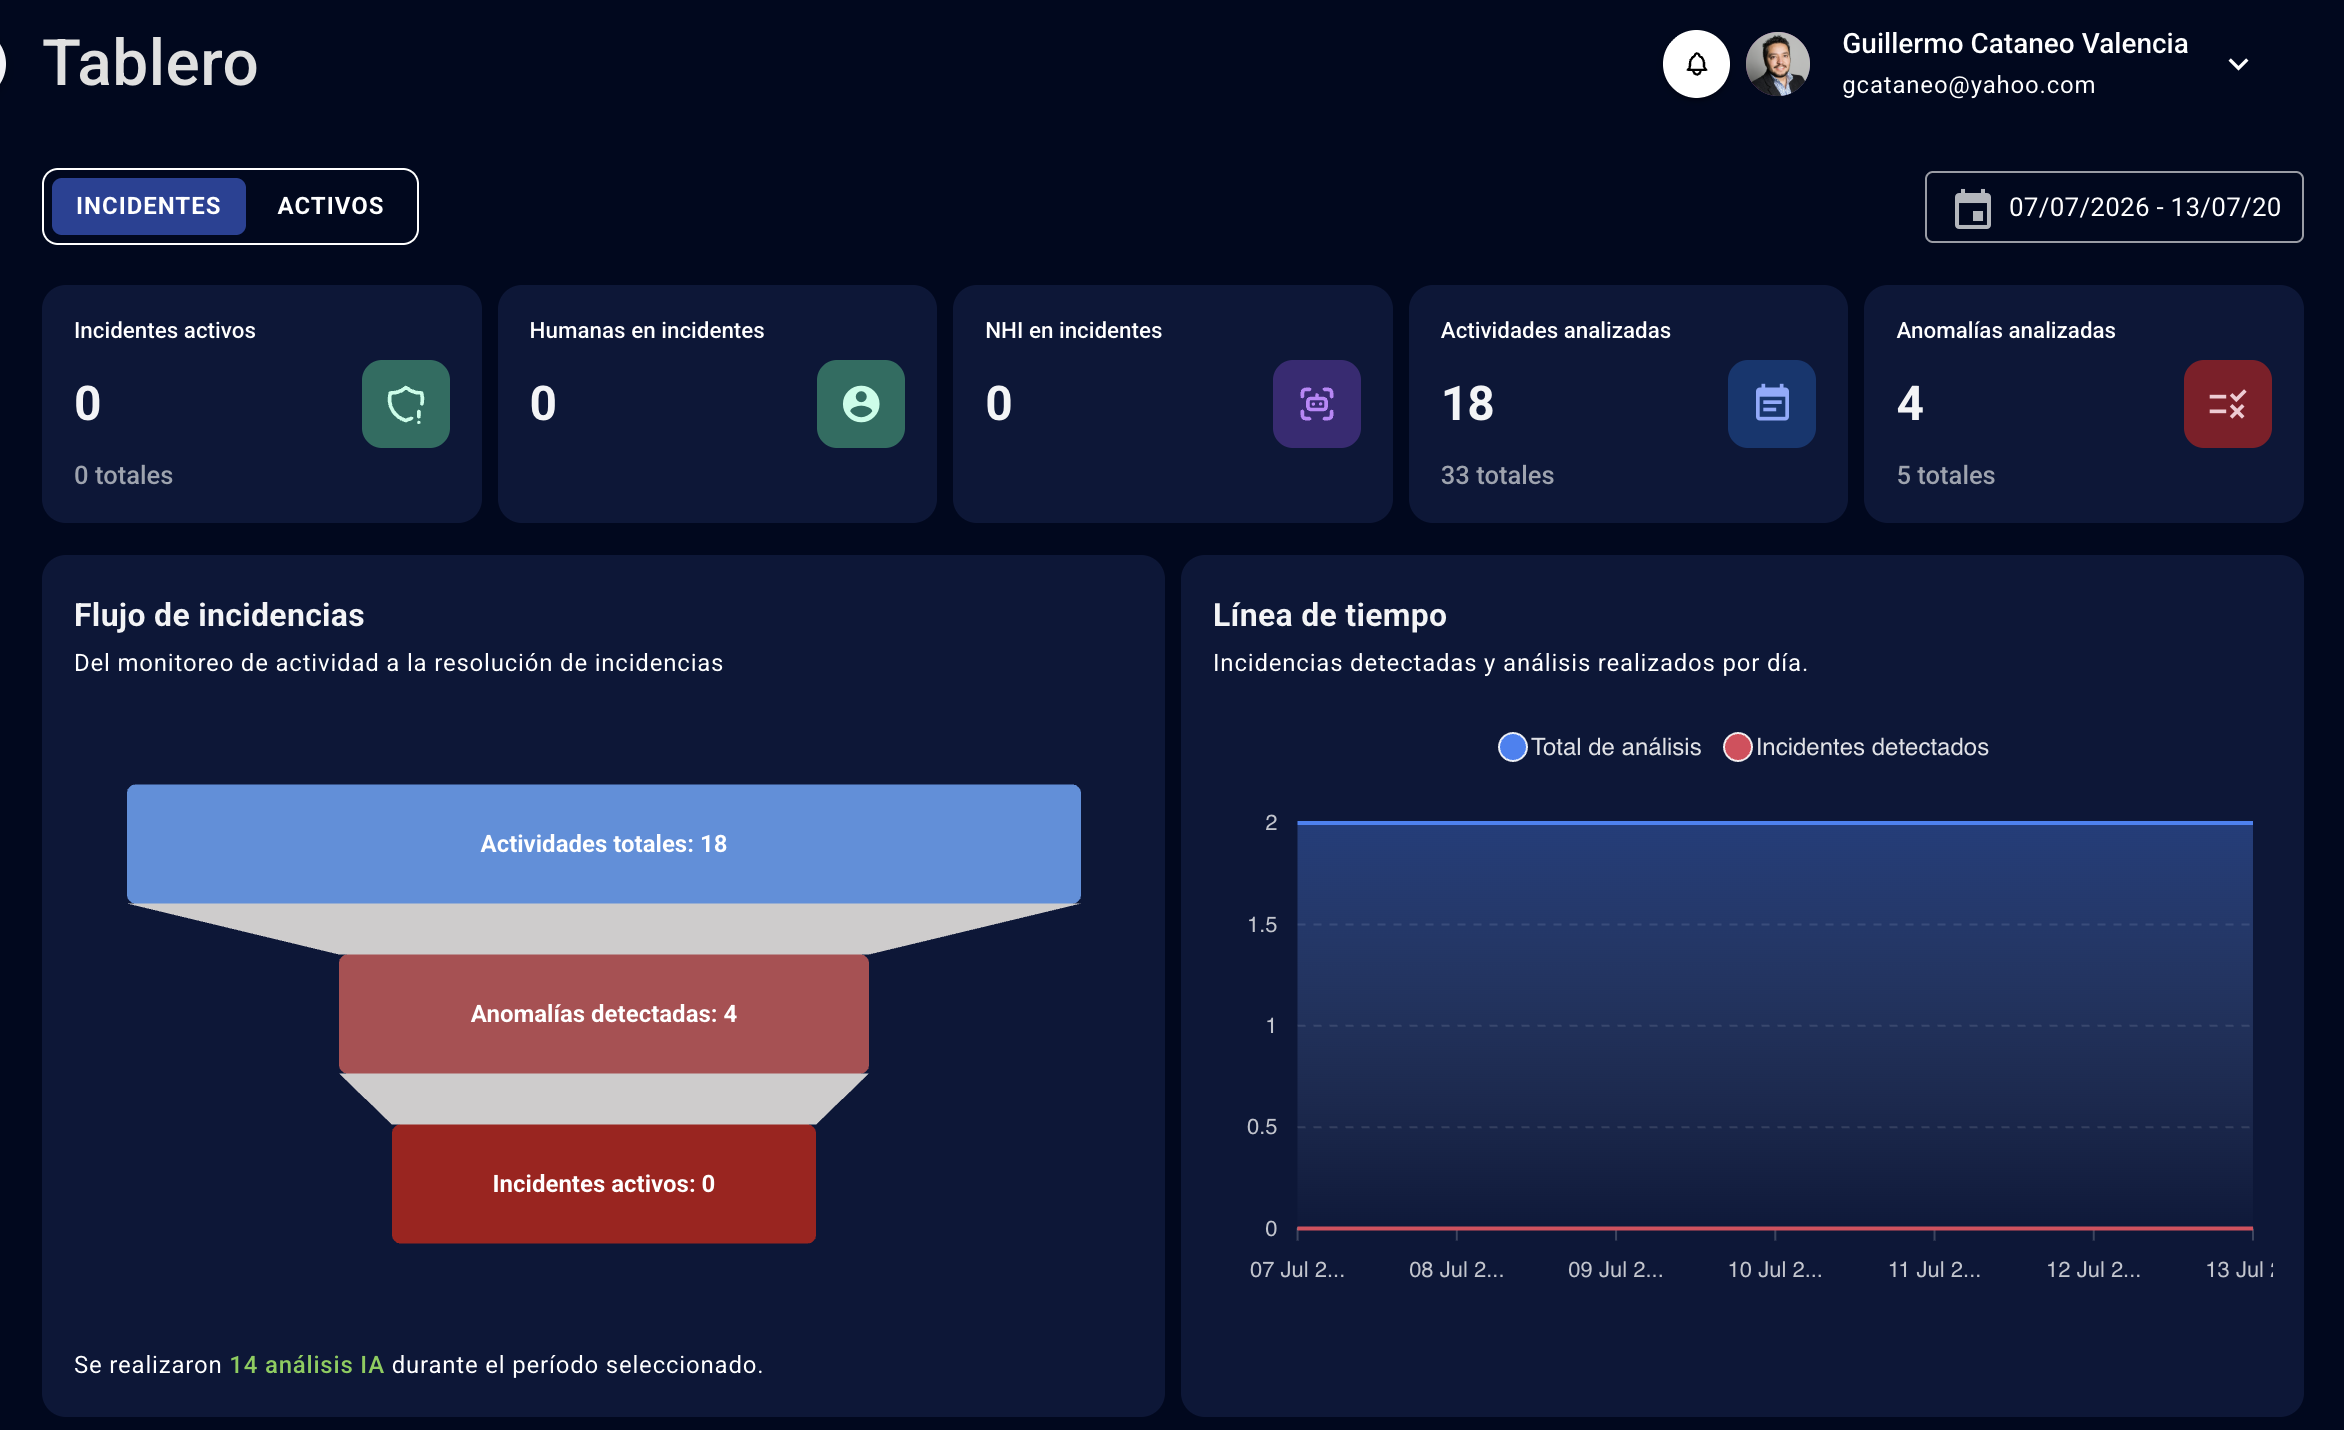
Screenshot of Executive dashboard showing the identity activity funnel — from monitored activities (18) to anomalies detected (4) to active incidents (0) — for a selected date range. Adjacent timeline visualizes incident detection and total AI-driven  analysis events per day, with headline KPIs for active incidents, human vs. non-human identities involved, activities analyzed, and anomalies analyzed.
Screenshot of Assets tab of the executive dashboard, delivering a unified inventory of 17 identities, 116 human accounts, 170 non-human identities (NHI), 599 entitlements, and 728 anomalies. Account risk distribution (Critical, High, Medium, Low) sits alongside behavioral anomaly indicators such as "NHI credential never expires" (169) and "NHI credential not rotated" (164), plus account state breakdown between active, locked, deleted, privileged, and shared accounts.
Screenshot of Security incident management workspace where SOC and IAM teams triage identity threats across all connected systems. Each incident is displayed with source application (Google Workspace shown here), severity (Critical / High / Medium / Low), lifecycle state (New, In Triage, Closed), 
AI-calculated confidence score, and final verdict — including labels like Token Theft, Lateral Movement, Password Spraying, Legitimate Activity, Business Exception, and Insufficient Evidence.
Screenshot of Detailed incident view for a high-severity case: "NHI account without owner and insecure credentials in Google Workspace". The AI Analysis tab maps the finding to MITRE ATT&CK tactic TA0006 (Credential Access) and technique T1556 (Modify Authentication Process) at 80% confidence, showing affected accounts, related activities, and correlated anomalies. An AI-generated Quality Assessment panel surfaces assumptions, evidence gaps, and cross-incident correlations so analysts can act with full context.
Screenshot of Analytics view organizing every identity anomaly by MITRE ATT&CK tactic and technique. isplayed here: TA0006 (Credential Access) with 7 detections across 2 techniques, and TA0003 (Persistence) with 2 detections across 2 techniques. The right-hand panel drills into T1556 (Modify uthentication 
Process) showing each individual detection with application, stage, verdict (Legitimate Activity, Business Exception), severity, and affected accounts — giving SOC teams a native ATT&CK-aligned view of their identity attack surface.
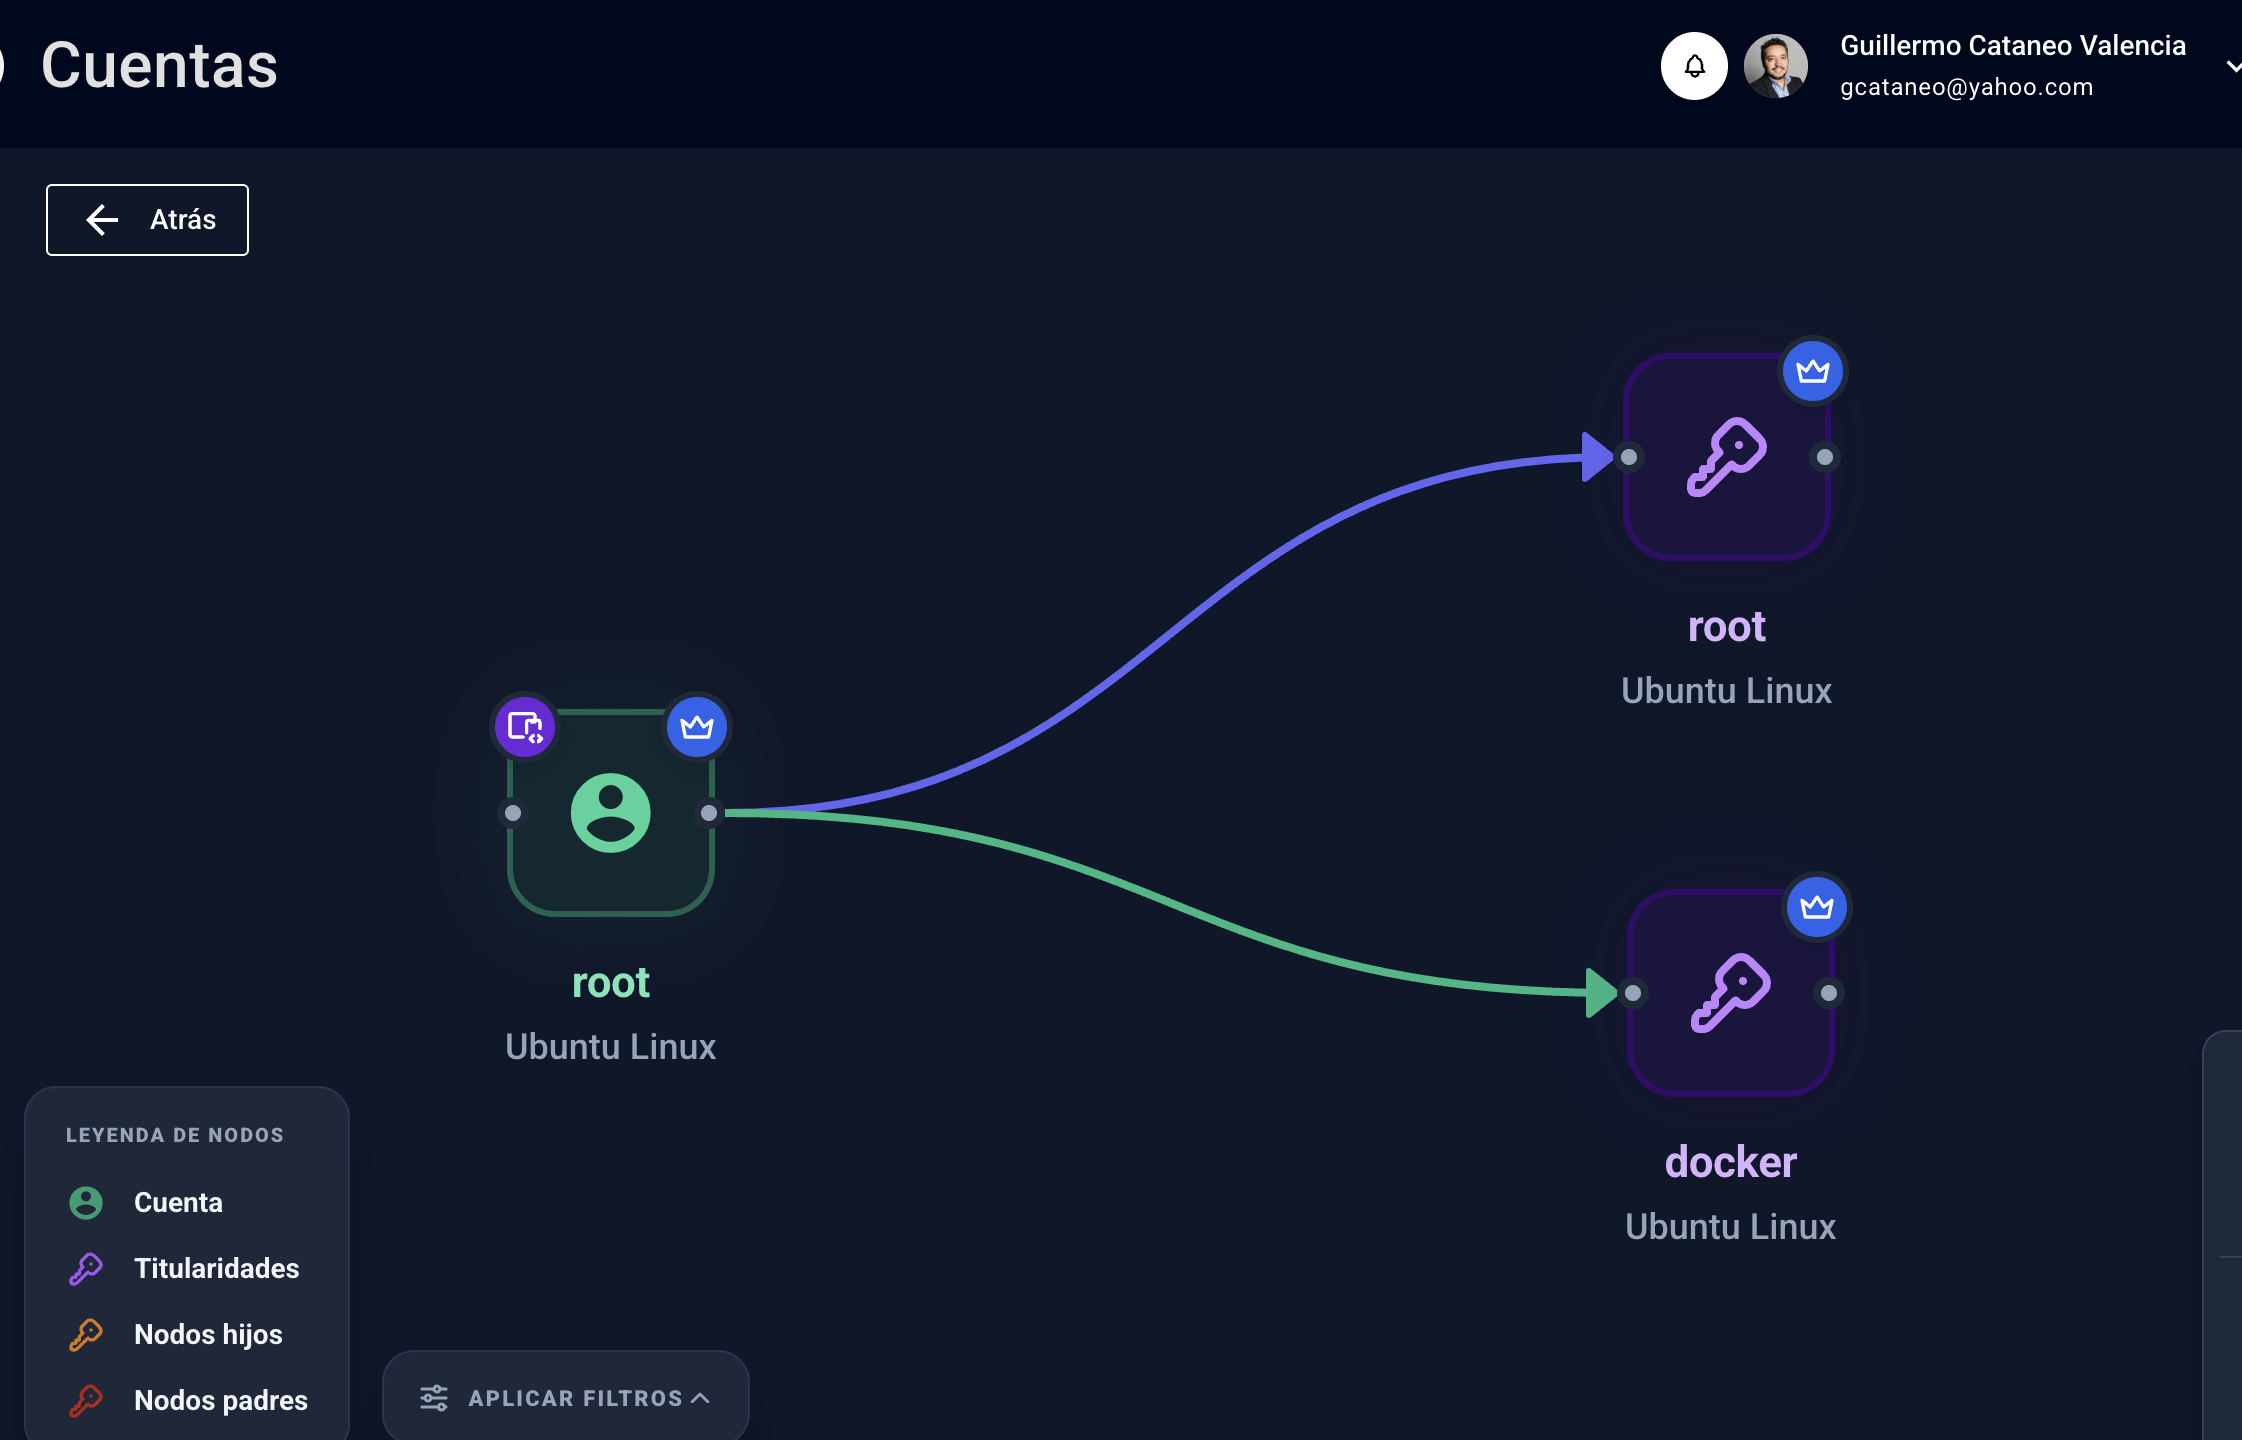
Screenshot of Interactive graph visualization of account relationships. Central node shows a Linux "root" account on Ubuntu, connected via directional edges to its two entitlements — "root" and "docker" privileged access on Ubuntu Linux. The legend explains node types (accounts, entitlements, child nodes, parent nodes), giving IAM and security teams a visual map of how privileges are structured across systems.
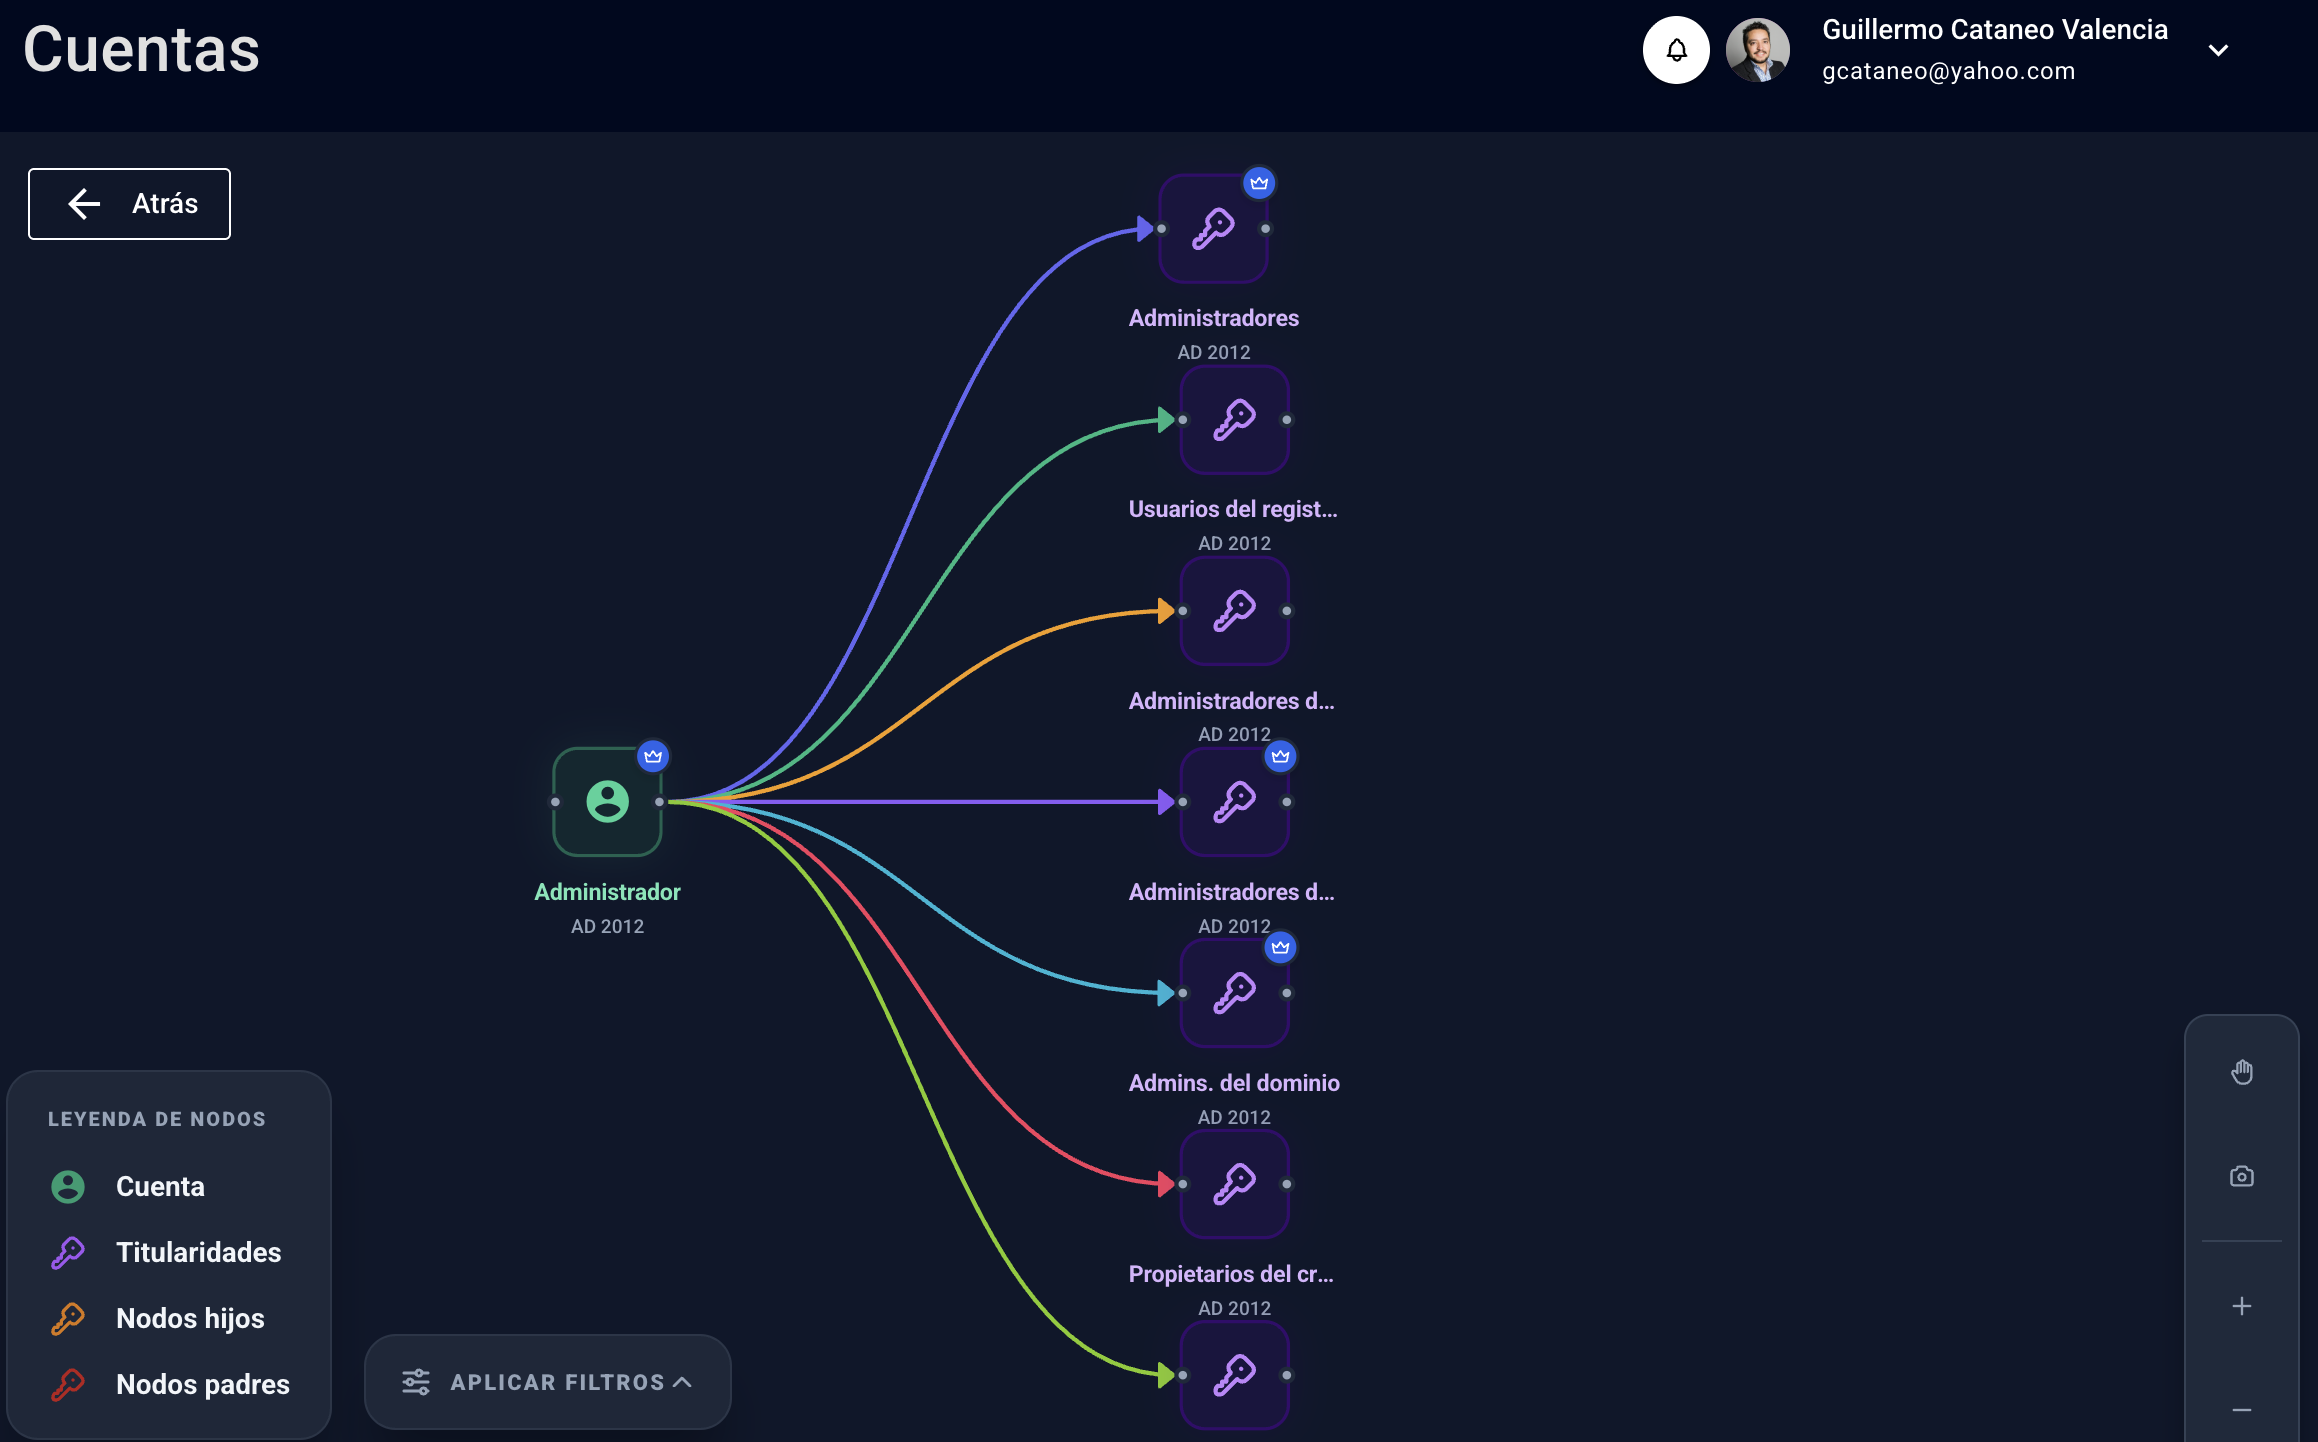
Screenshot of Account graph showing an Active Directory "Administrator" account on Windows Server 2012, with its six group memberships and entitlements: Administrators, Registry Users, Domain Admins, and additional privileged groups. Color-coded edges distinguish entitlement types and privilege levels, making it easy for security teams to spot excessive privileges, unexpected group membership, and identity attack paths crossing multiple Active Directory objects.

1 / 7

Screenshot of Executive dashboard showing the identity activity funnel — from monitored activities (18) to anomalies detected (4) to active incidents (0) — for a selected date range. Adjacent timeline visualizes incident detection and total AI-driven analysis events per day, with headline KPIs for active incidents, human vs. non-human identities involved, activities analyzed, and anomalies analyzed.