AWS Firewall Manager is a security management service which allows users to centrally configure and manage firewall rules across accounts and applications in AWS Organization. As new applications are created, Firewall Manager brings new applications and resources into compliance by enforcing a common set of security rules. Users gain a single service to build firewall rules, create security policies, and enforce them in a consistent, hierarchical manner across the entire infrastructure.
N/A
Cisco Identity Services Engine (ISE)
Score9 out of 10
N/A
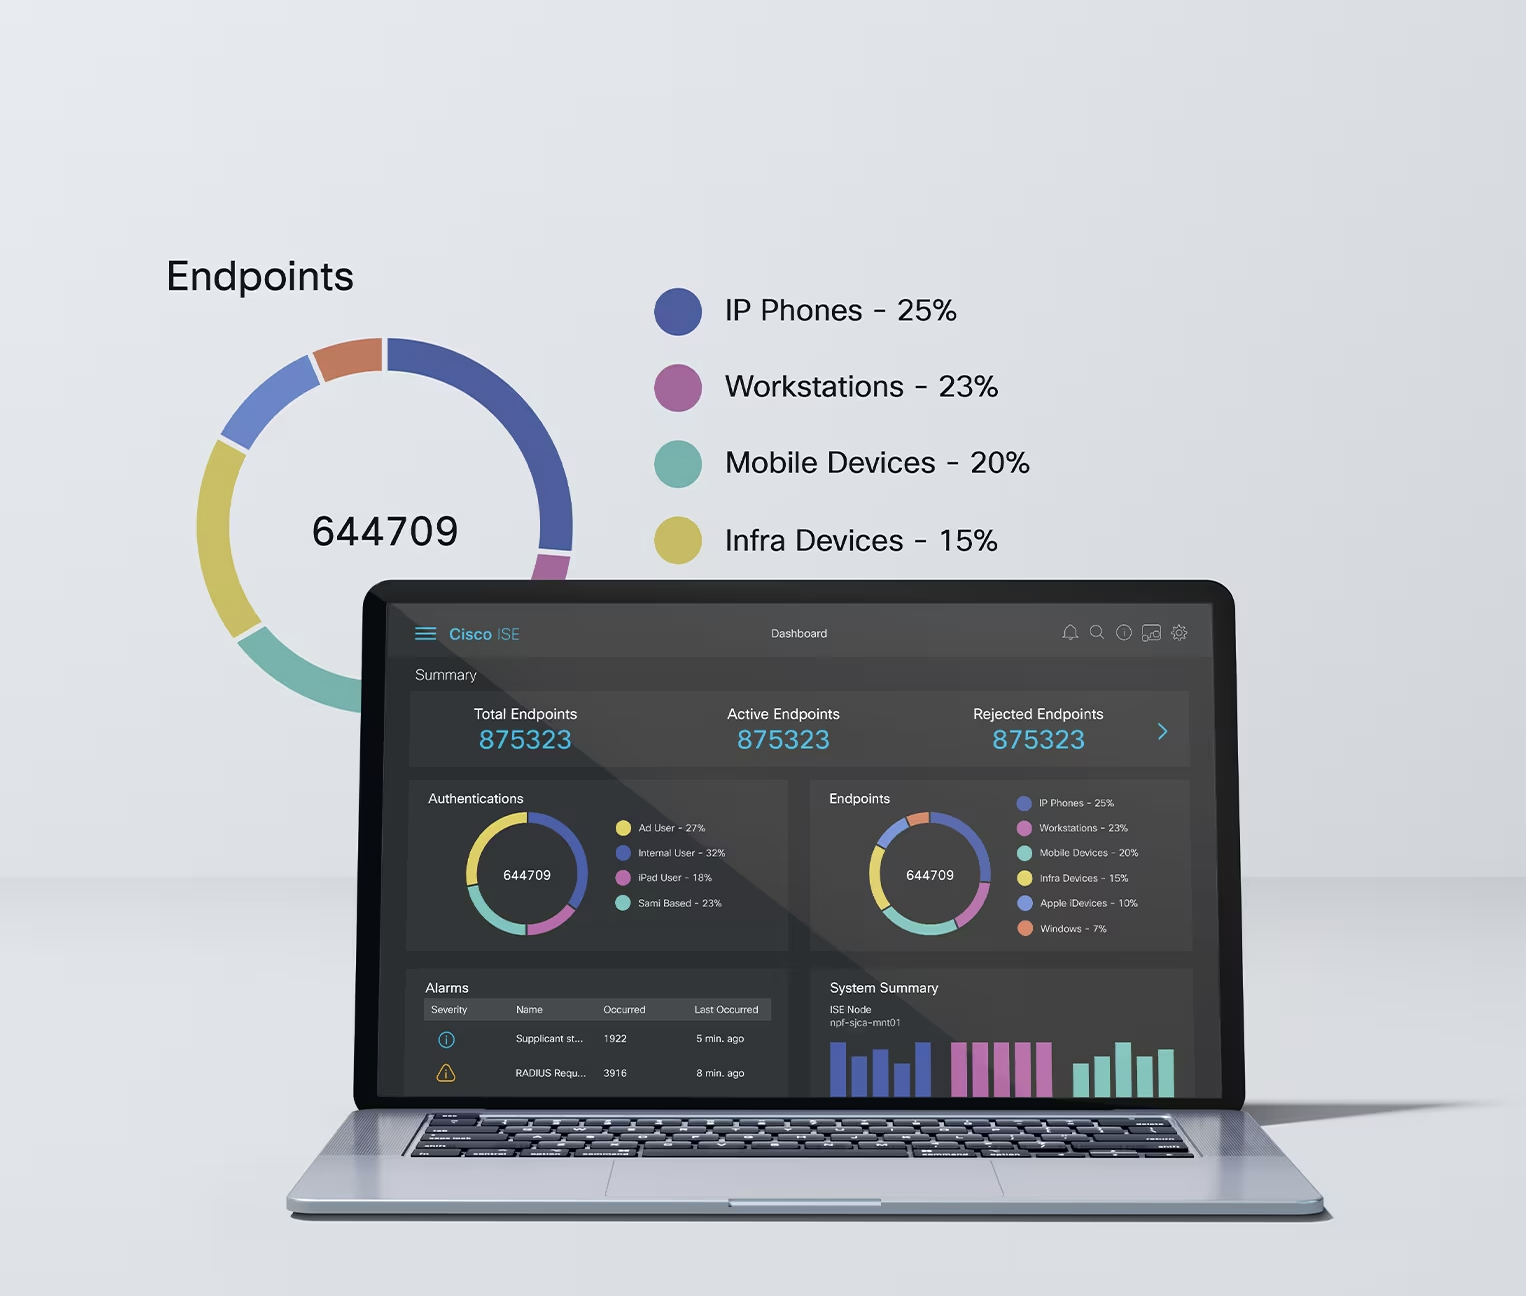
The Cisco Identity Services Engine (ISE) offers a network-based approach for adaptable, trusted access everywhere, based on context. It gives the user intelligent, integrated protection through intent-based policy and compliance solutions.
N/A
FireMon
Score7.9 out of 10
Enterprise companies (1,001+ employees)
FireMon is a real-time security policy management solution built for today’s complex multi-vendor, enterprise environments. Supporting the latest firewall and policy enforcement technologies spanning on-premises networks to the cloud, FireMon delivers visibility and control across the entire IT landscape to automate policy changes, meet compliance standards, to minimize policy-related risk. Since creating their policy management solution in 2004, FireMon states they've helped…
AWS Firewall Manager is well suited for cloud environments that have a lot to manage and maintain. If you have a smaller scale cloud environment or on premise setup this may not be for you.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Well suited... I've used it for both wired and wireless access, and it's perfect for that. In addition to enforcing security on the port, you can also lock down east-west traffic. When you get to the point where you're configuring secure group tags and things like that, you can keep people from getting to places they shouldn't. Basically, you could turn your entire network into a firewall if you wanted to. You can secure access based on the identity of any given user through role-based authentication. For example, if you have salespeople and you don't want them accessing your financial or PCI environment, they authenticate as a salesperson and you can completely stop them from getting to any of that. That's really important, especially for us. Our payment card infrastructure servers are heavily locked down. Granted, in our situation, we firewall all that off anyway, but you still don't want some random individual to be able to even attempt that sort of thing. That's what it's really good for. I'm trying to think of a weakness. I don't know. We don't really struggle with it. There's nothing that I use it for where I wish it were better, at least not that I can think of offhand. I'm sure there are things, I just can't think of anything off the top of my head.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
FireMon is best used in a large environment (for example, I have >100 firewalls in my environment). It's best used when trying to improve security posture and showing changes in firewall security over time. It might not be the best choice for smaller environments or those that aren't concerned about security management.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The shell is locked out and we can't run any general centos commands. The implementation and maintainence of the arch is very complex. Even with the right identifiers on log messages the log collection keeps failing. The warning messages on the device are ambiguous. The log messages on firemon are a bit confusing and don't show the exact issue.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
For us the solution is very easily useable on its own. Perhaps that has to do because we started using ISE in the 1.2 days and have seen it grow during the years. Policy creation, etc. is all very visible and thus easy to use. Deployment of multiple nodes is also incredibly easy and flexible. You can easily add or remove nodes as you wish.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We do have to occasionally reboot the servers when they get low on memory, but we're also a few versions behind. Availability has generally been pretty good though with no major outages in the time that we've had it implemented.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
FireMon has been relatively stable overall. However, there have been a handful of times where we had issues with the console. For example, we couldn't update which devices to include in a security assessment. The initial suggestion from support was to just reboot it. It seems like there weren't many other options available such as to restart services before going to the extreme of a complete reboot.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I'm not sure we have the largest implementation of FireMon out there but we do have a few 1000 devices being probed by FireMon. Overall, the system's performance has been rock solid. The console refreshes quickly and reports are generated within an expected timeframe.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cisco support is second to none, both in terms of how you access support but also the knowledge of the individual support teams. If you focus on one technology and provide "manufacturer support" then you can rest assured that you are accessing Cisco's top individuals. I feel like this is a USP for Cisco support.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
FireMon technical support is awesome! They respond quickly to our requests and they are well trained and very knowledgeable about the tool. Some issues have to be referred to the development team, but technical support largely provides solutions for any issues that we may have.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I think our system integrators lacks some competencies and this has led to an implementation that is still perfectible. (i.e. dedicating an interface for intra-cluster communication)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
For a business that doesn't use any software or applications that will generate high volumes of traffic, AWS Firewall Manager is the ideal choice. The method of creating an initial configuration and user-friendliness is simple. Along with other AWS services, we also created portals for the HR division, with a focus on recruitment. we also created a User Interface and a set of tools. The AWS Firewall Manager is the only thing we need.
I think all give some visibility of device monitoring and management, but Cisco Identity Services Engine gives a good way to manage more details about the device in a centralized way that gives a wider range of monitoring and control than the other softwares individually. I don't think Cisco Identity Services Engine eliminates the need for these other software as of now, but there is potential for Cisco Identity Services Engine to be able to take over more of these roles.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I has worked with AlgoSec and while they are very similar product, I find the FireMon is easier to understand and get rolling with. While both require some learning, FireMon is by far the easier one. Once you have an understanding of how things are arranged and labeled you can easily import firewalls and begin to work on them to improve them
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It's fully customised and comprehensive. only thing is you need to know what you want. Proper research and planning would save lots of time and effort .
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Firemon Is easily scalable and maintainable with any size team. Although it requires some tech debt, it is well worth the time to invest to ensure compliance is visible and reports are accurate. Although our environment is very large we do not fully utilize the scalability of the Firemon product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I don't know about negatives because we haven't seen it right now, but positive impact is one is the roadmap we have. And now since we are going ahead with doing the deployment of Cisco ISE, we see that we are getting closure to, so at the end of the day, we have to make sure that operationally we stay excellent. So that's where operational excellence comes in. Cisco ISE is basically addressing that for us. Right now we are in a situation if there is a WIFI issue or if there is an authentication issue, it gets really difficult to isolate the problem. But with Cisco ISE , this functionality is going to come in. So we believe that it would be a good ROI.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info