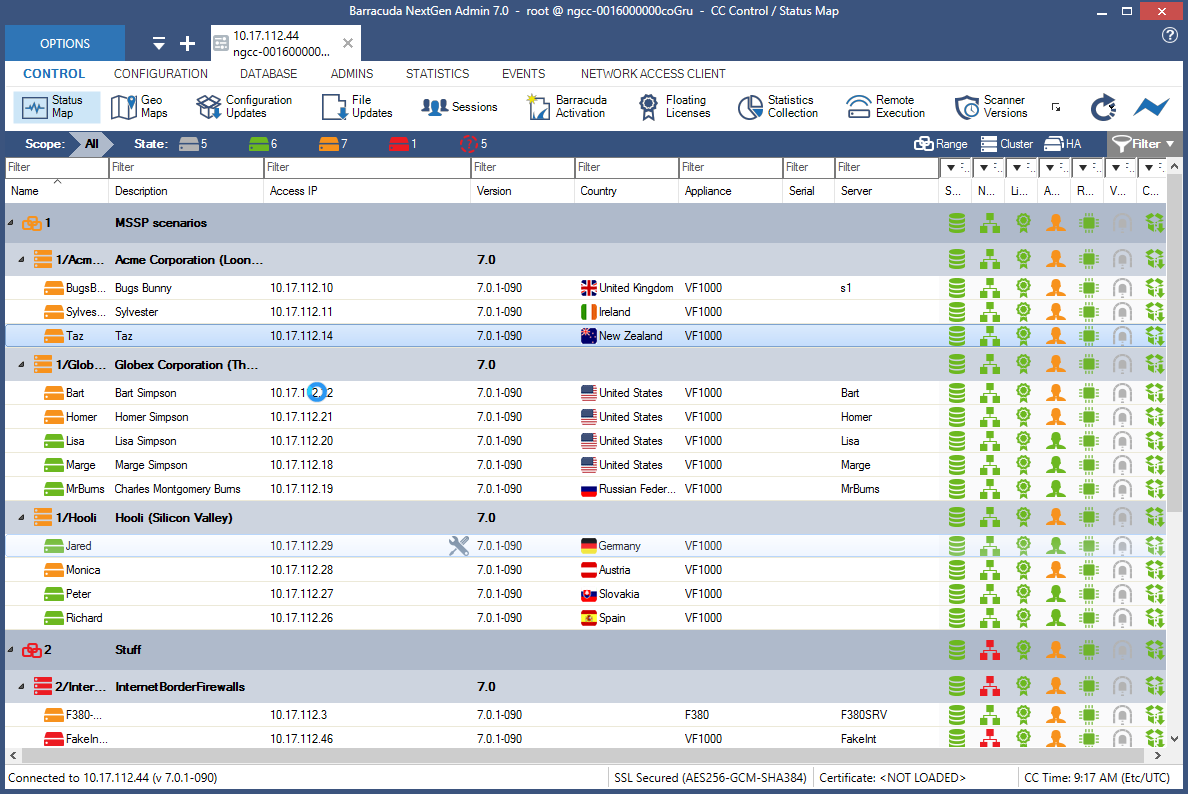
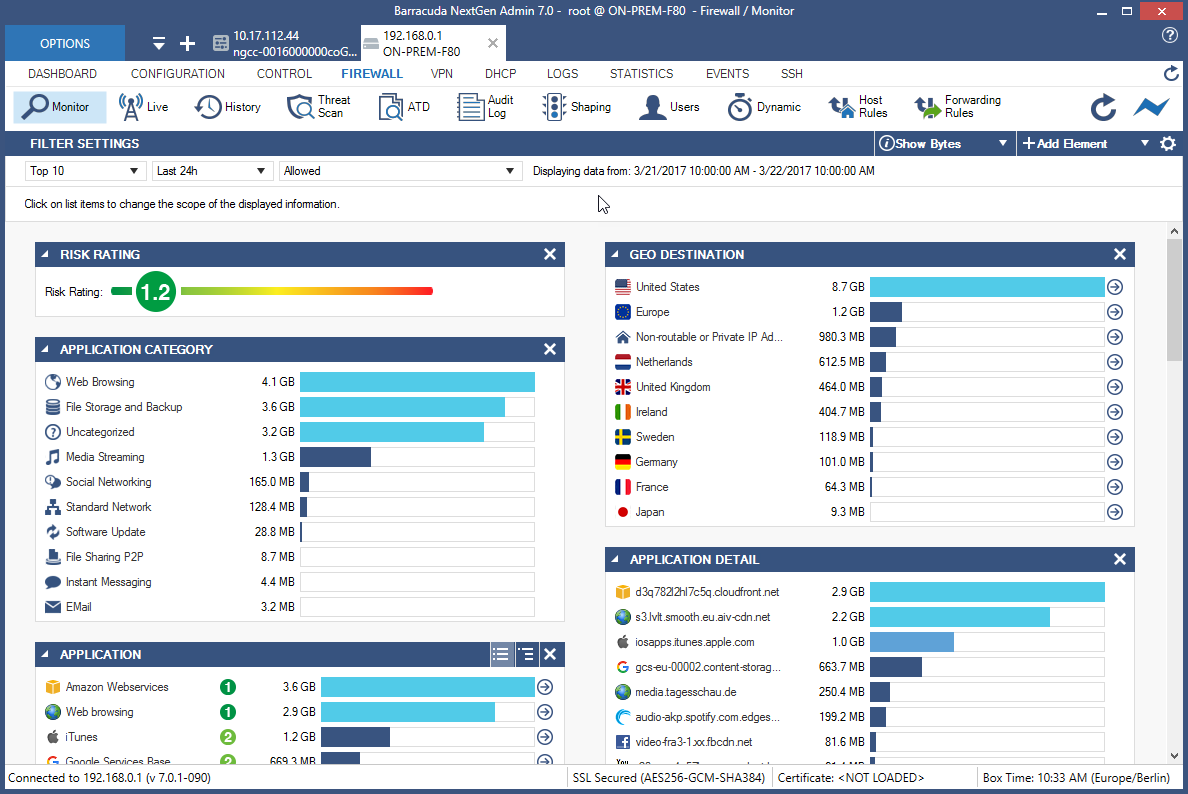
Barracuda Web Application Firewall, from Barracuda Networks in Campbell, California, protects web applications from bots, DDoS attacks, and other advanced threats to enterprise apps.
N/A
Azure Front Door
Score6.8 out of 10
N/A
Azure Front Door is a cloud content delivery network (CDN) service that helps users deliver high performance, scalability, and a secure user experiences for content and applications. It includes a customizable rules engine for advanced routing capabilities. It boasts instant scalability with global HTTP load balancing and failover.
$35
per month
NGINX
Score9.1 out of 10
Mid-Size Companies (51-1,000 employees)
NGINX, a business unit of F5 Networks, powers over 65% of the world's busiest websites and web applications. NGINX started out as an open source web server and reverse proxy, built to be faster and more efficient than Apache. Over the years, NGINX has built a suite of infrastructure software products o tackle some of the biggest challenges in managing high-transaction applications. NGINX offers a suite of products to form the core of what organizations need to create…
N/A
Pricing
Barracuda Web Application Firewall
Azure Front Door
NGINX
Editions & Modules
No answers on this topic
Standard
$35
per month
Premium
$330
per month
No answers on this topic
Offerings
Pricing Offerings
Barracuda Web Application Firewall
Azure Front Door
NGINX
Free Trial
Yes
No
Yes
Free/Freemium Version
No
No
Yes
Premium Consulting/Integration Services
No
No
Yes
Entry-level Setup Fee
Optional
No setup fee
Optional
Additional Details
—
Base fees (Billed hourly and only for number of hours used)
In our organization, we use different solutions depending on if the database is on premise or in the cloud. We went from multiple solutions across different departments towards a more consolidated model to achieve standardization and economies of scale. We’ve mainly moved …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Easy to use and reliable, with very little maintenance required and zero downtime to date. For the education sector, ease of use is hugely important as IT Managers/Technicians are often "Jack of all trades" with a good, broad general knowledge but perhaps lacking specific expertise in certain aspects. Being provided with easy-to-follow tutorials and instructions has been very useful in setting up and configuring the firewall, especially as my background is more in desktop support.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Azure Front Door is very easy and fast to set up and implement, if you are looking for an easy solution that is secure and reliable, Front Door does all that and can be configured in a few hours. AFD is a CDN with WAF, accordingly, it is well suited for any CDN Scenario, other providers such as Akamai or Verizon have a more expensive base price and are harder to manage/configure, Front Door is simple, easy, and provides what's needed when it comes to Web App Security. If you have multiple data centers, have apps in different regions, or targeting a global audience, AFD is an excellent option to get up to speed quickly. If you are looking for more features and capabilities, or planning a very complex setup, Front Door might be sufficient, but other specialized provides such as Imperva, Cloudflare or Akamai are generally a bit more advanced (but harder to set up and maintain). It always depends on the scenario, but for us, Front Door was an excellent option and served us very well with no issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Nginx is well-suited for any web server scenarios, such as web applications, backend or reverse proxy for both application and HTTP requests, and distribution. It is less appropriate for Windows-based applications that run directly on a Windows Server host. In any case, it is very easy to manage, through separate conf files for each application or site you want to host with it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
STM crashes sometimes happen due to unusual traffic pattern
Obfuscation on the client side user credentials which appears in the developer tools of browser
URL Profiles redundancy during the learning of traffic needs to be fixed
Dos Protection should be more granular like escalation period to throw JS challenge, Captcha and rate limit when escalation period hits until the WAF stops the attack
Client Fingerprinting should work as expected when verifying the clients as in rare some scenarios, it creates issues
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Customer support can be strangely condescending, perhaps it's a language issue?
I find it a little weird how the release versions used for Nginx+ aren't the same as for open source version. It can be very confusing to determine the cross-compatibility of modules, etc., because of this.
It seems like some (most?) modules on their own site are ancient and no longer supported, so their documentation in this area needs work.
It's difficult to navigate between nginx.com commercial site and customer support. They need to be integrated together.
I'd love to see more work done on nginx+ monitoring without requiring logging every request. I understand that many statistics can only be derived from logs, but plenty should work without that. Logging is not an option in many environments.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
-User friendly interface for quick learning -Quick deployment for deploying applications -Easy to manage for naive -System components and upgradation of the WAF is very easy go with -Back restoration is very to make it up and ready anytime -Seperate JSON and XmL profiles for each URLs of the application is plus -Amazing and world class support engineer in comparison other vendors and always available to support -Quick resolution on bugs with their patch applying process
This tool is really easy to use and configure. Consumes very less system resources. It is highly modular and configurable. You can easily use it with other tools like certbot for SSLs. You can configure basic security with configuration and headers
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The Barracuda Web Application Firewall is easy to use. Support from Barracuda is great also. Load Balancing of the Web Application Firewall is also nice. This allows you to do maintenance or have large loads for the end-user. Threat monitoring of our network and traffic coming into our services within our cloud solution.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Community support is great, and they've also had a presence at conferences. Overall, there is no shortage of documentation and community support. We're currently using it to serve up some WordPress sites, and configuring NGINX for this purpose is well documented.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have been using their Backup products especially Backup Appliances and legacy products like Intronis. We are also using their Cloud Backup Solutions for O365. This is the reason we opted for this product.
It's generally hard to compare CDNs, each has its features, POP locations, latency, and availability. We have used many other CDNs, including Akamai, Verizon, and Cloudflare. They are all great, but each has its own advantages/disadvantages. From our perspective, all other providers were much harder to configure and maintain and their overall cost was higher than AFD. For example, Verizon was great, performance was excellent, but reporting/logging was not up to our expectations, and we had many issues with its Rules Engine. AFD is great for delivering your web apps globally quickly and easily, the cost is reasonable and comes with very little operational overhead, the logging and reporting capabilities are very good, additionally, its integration with Azure Cloud Services gives it an advantage over other competitors.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I have found that [NGINX] seems to perform better throughout the years with less issues although I've used Apache more. I would definitely recommend [NGINX] for any high volume site and I've seen this to usually be the case from most provided web hosts who will pick [NGINX] over alternatives
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
AFD implementation was approx. 80% cheaper than other providers, from initiation to operation.
It allowed us to minimize backend resources size/processing power, taking all the load from client requests, cutting tens of thousands of dollars monthly on compute, memory, and network bandwidth.
Overall, the ROI of AFD is very quick, it is not an expensive solution, therefore, its ROI goals are easy to calculate and achieve, our overall ROI exceeded 300%.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
By using Nginx, we can host multiple web services on a single server, keeping our infrastructure costs lower.
Nginx maintains our HTTPS connections, allowing us to keep our promise to our customers that their data is safe in transit.
Due to Nginx's extremely low failure rate, our web addresses always return something meaningful, even when individual services go down. In sense, this means we are "always online" and allows us to maintain brand and support our customers even in the face of catastrophe.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info