Carbon Black App Control is an application control product, used to lock down servers and critical systems, prevent unwanted changes and ensure continuous compliance with regulatory mandates.
N/A
HCL BigFix
Score8.3 out of 10
N/A
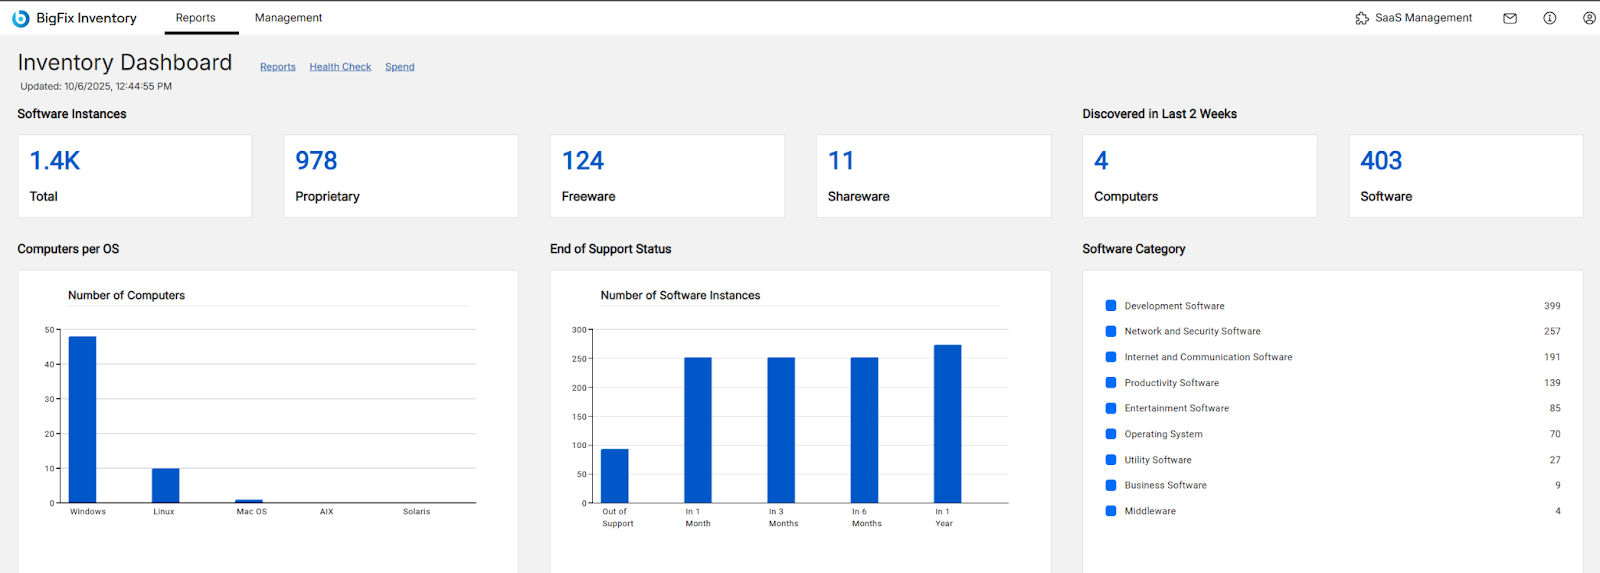
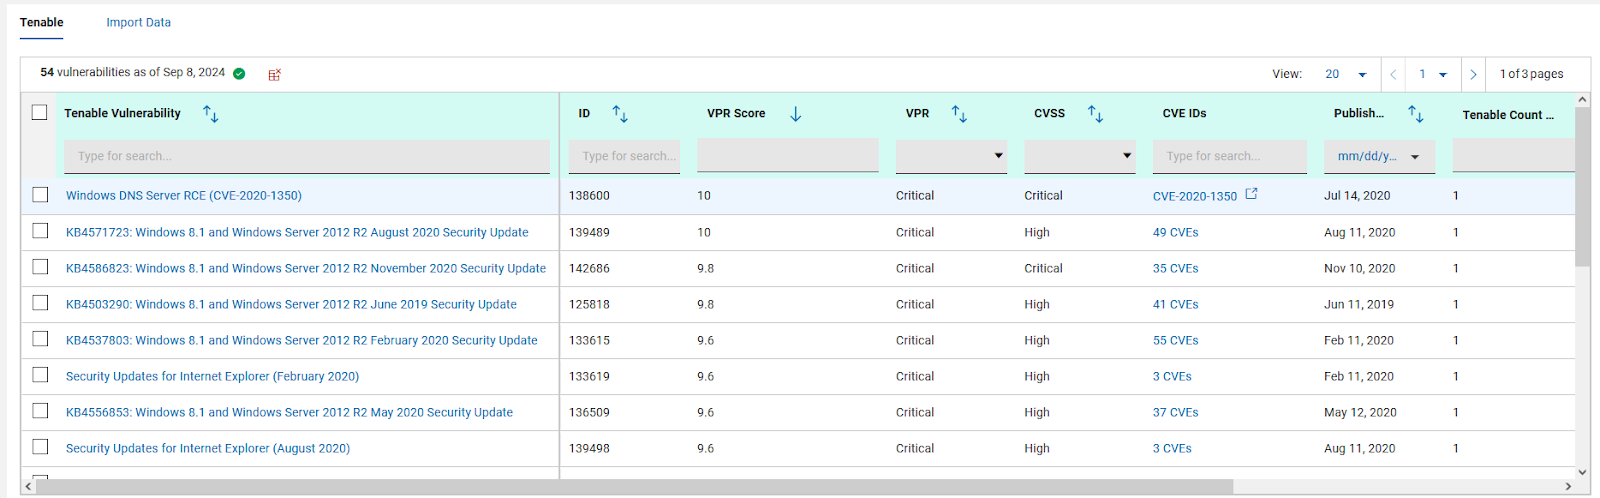
BigFix, now supported by HCL Technologies since the acquisition of BigFix from IBM in 2018, is an endpoint management solution providing endpoint visibility and IT asset discovery, automated endpoint patching (BigFix Lifecycle and BigFix Patch) policy enforcement (BigFix Compliance), and software asset discovery for licensed and unlicensed software (BigFix Inventory).
Cb Protect is best suited somewhere where you want to maximize the lockdown of workstations. So moving past no local admin rights to blocking specific applications and peripherals. The idea would be to have a list of applications you want to run, and then anything else is not able to be used. As stated prior, if you have a very fluid environment where you are having all sorts of new applications installed frequently (I feel for you!!) this is still do-able, but it misses the general idea. I think especially in environments that are more sensitive to new applications, like banks, healthcare systems etc, this is a good fit. The ability to look at application levels, drift, unapproved software etc is very useful.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
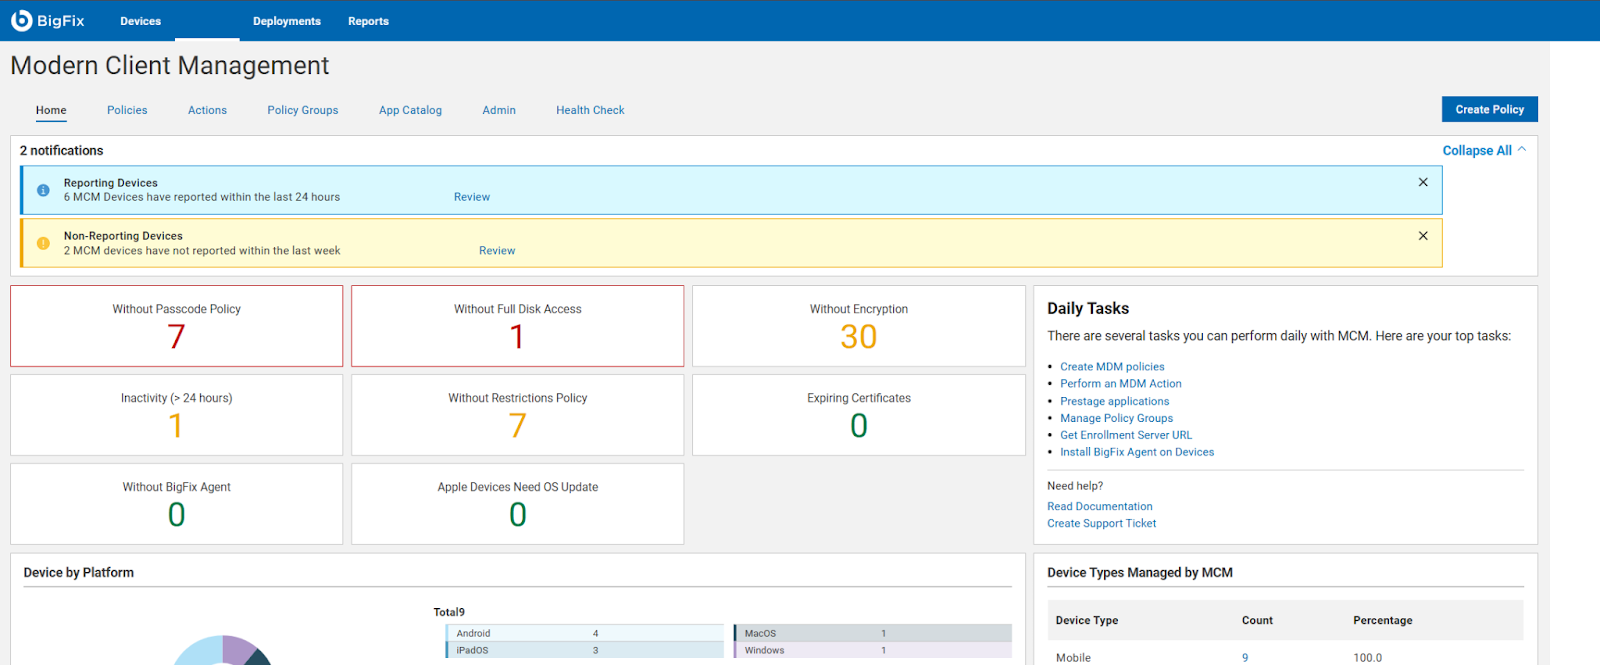
Patch Management for Diverse Devices: HCL BigFix is ideal for organizations with a diverse range of devices, including laptops, desktops, cloud, virtual machines, and mobile devices. Its endpoint management functionality enables seamless patching across various operating systems such as Windows, MacOS, ChromeOS, and Linux.
Comprehensive Patch Management: With HCL BigFix, organizations can achieve comprehensive patch management across their IT infrastructures. It ensures that all endpoints, regardless of the operating system, receive timely and secure patches, reducing vulnerabilities and enhancing overall security.
Troubleshooting and Monitoring: HCL BigFix excels in providing a dashboard that effectively displays problematic and functional machines. This feature allows IT teams to quickly identify and address issues, improving overall troubleshooting efficiency. However, there are some scenarios where HCL BigFix may be less appropriate or areas for improvement: 1. Coverage Expansion: It is important for HCL BigFix to continue expanding its coverage to include all possible resources installed within the IT infrastructure. Ensuring comprehensive coverage can enhance its effectiveness. 2.On-Site and OS Upgrades: Optimizing the process of on-site and operating system upgrades can help streamline the deployment process further. Improvements in this area would contribute to a smoother and more efficient upgrade experience. 3.Communication Speed: Enhancing the speed of communication between the HCL BigFix agent and the server can help improve the overall responsiveness and efficiency of the solution.
Pricing Optimization: Adjusting the pricing of HCL BigFix to be more cost-effective would make it more accessible and attractive to organizations of different sizes and budgets.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big difference between Protect and Barkly/AMP is how exactly it goes about what it's doing. Protect is application whitelisting and program reputation. So the way it's protecting you is using a proprietary reputation service, and hash values to identify applications, and then hitting a list of whitelisted programs to decide if you are able to run that or not, based on the policy you are in. There is a LOT of value in that. We actually are working on transitioning to Cisco Advanced Malware Protection (AMP). The main reason is cost (about the same cost as Cb Protect, but with (most of) the featureset of all 3 Carbon Black products for less than 1/3 of the total spend. AMP works differently, looking at a reputation service powered by Cisco's Talos cloud. You don't really have application whitelisting, but that also reduces how many "requests" you get for applications. So I'll have to find a different way to do whitelisting and USB blocking and the like, but I'm getting more visibility across my network and also built in antivirus (TETRA engine - ClamAV with some work). Barkly is an add that we are looking to put in as it looks at behavior of programs. So specifically it watches for privilege elevation and the like. Thus far all the big name problem children (WannaCry, other ransomware problems) have been caught natively in Barkly day 0.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have significantly enhanced our ability to patch desktops, including laptops, desktop, cloud, virtual machines and other mobile devices used by end-users. BigFix's endpoint management functionality allows us to seamlessly patch a wide range of operating systems, such as Windows, MacOS, ChromeOS, and Linux systems, ensuring comprehensive patch management across IT infrastructures. We have established a track record of delivering secure and hassle-free patching solutions to our clients
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info