Carbon Black App Control is an application control product, used to lock down servers and critical systems, prevent unwanted changes and ensure continuous compliance with regulatory mandates.
N/A
ManageEngine Endpoint Central
Score9 out of 10
N/A
Desktop Central from ManageEngine is a client desktop management with patching, remote control, and configuration.
Cb Protect is best suited somewhere where you want to maximize the lockdown of workstations. So moving past no local admin rights to blocking specific applications and peripherals. The idea would be to have a list of applications you want to run, and then anything else is not able to be used. As stated prior, if you have a very fluid environment where you are having all sorts of new applications installed frequently (I feel for you!!) this is still do-able, but it misses the general idea. I think especially in environments that are more sensitive to new applications, like banks, healthcare systems etc, this is a good fit. The ability to look at application levels, drift, unapproved software etc is very useful.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
For small businesses, it is also free, which, for what it offers, is really helpful. It works better than similar products, such as SCCM, both within and outside the internal network. I do not see scenarios in which it could be less appropriate.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We set alerts when a devices gets low on disk space. That is automatic and creates a ticket in ME SDP. We are then able to Add space to a VM Desktop, and then go thru ManageEngine Endpoint Central to extend the drives so the entire process can be done without interruption to the end user.
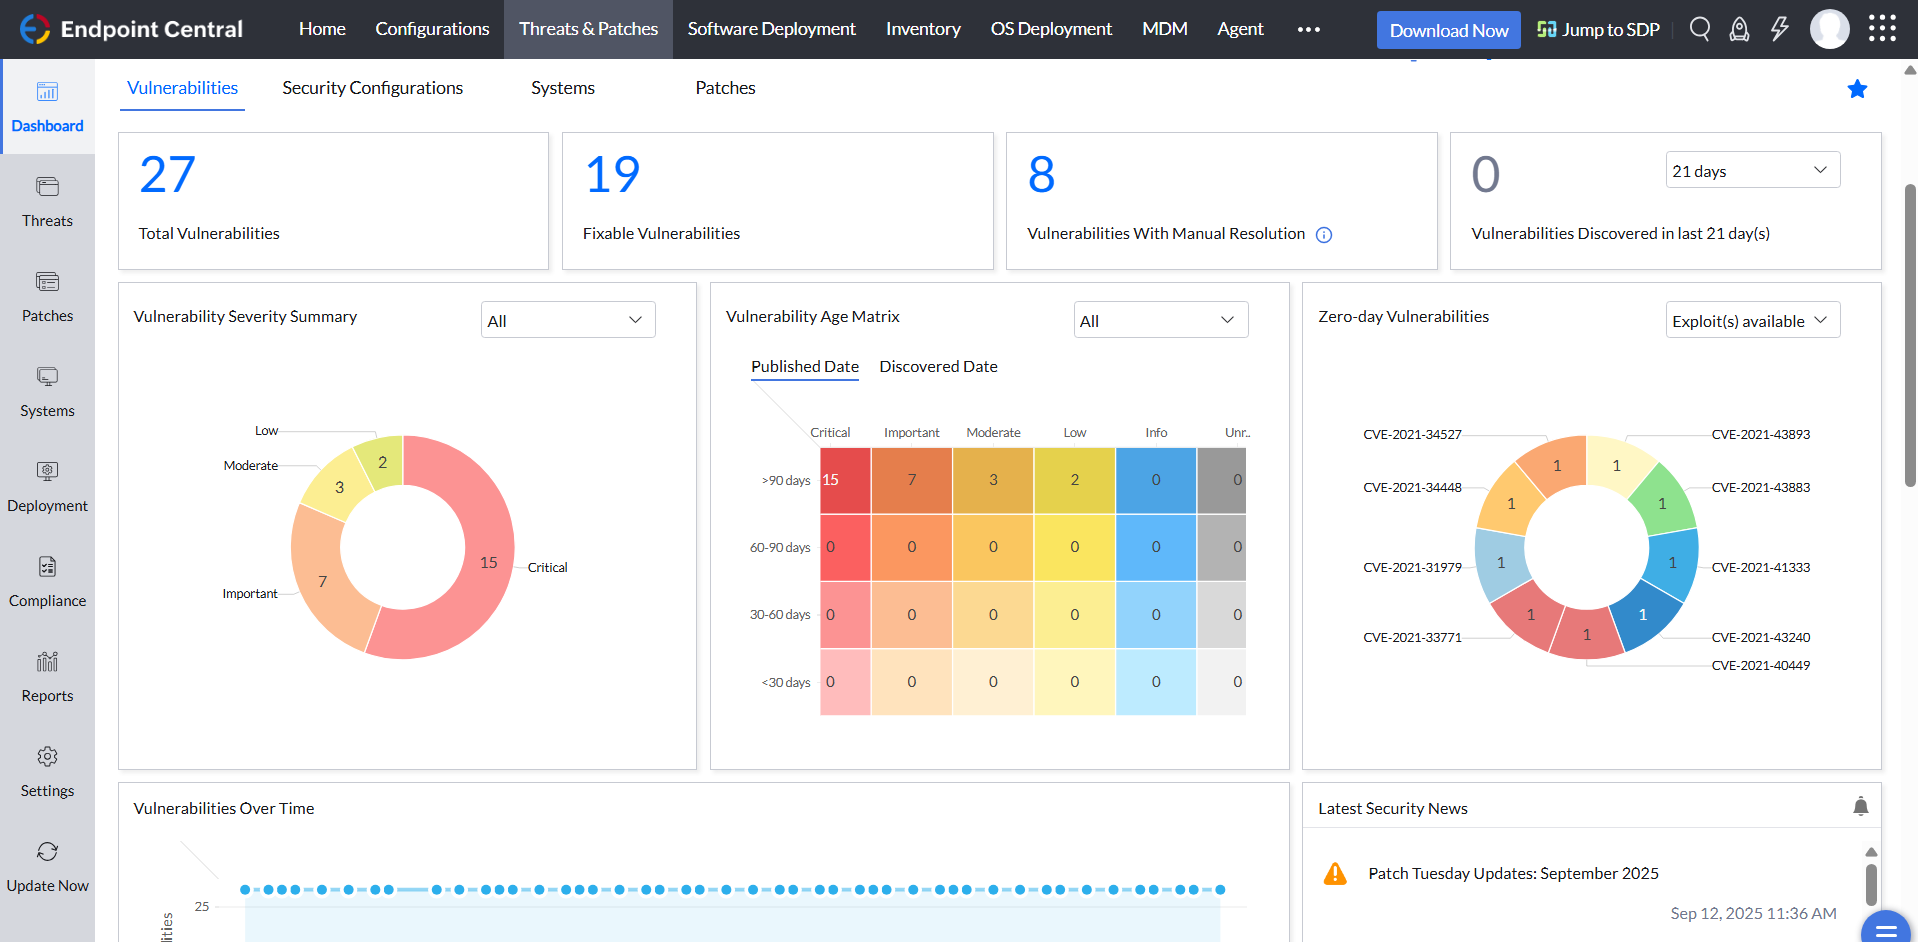
Using the patch scans we can easily see what patches have been installed for all manufacturers not just Microsoft, without having to physically go to the device. It also allows us to choose which patches we want to push out and automate the process so we can be hands off, freeing up out time for other things.
Remote access to devices. This allows us to remotely make changes, not just via remote control but also make registry changes and clean up space without going to the device and without interruption to the end user.
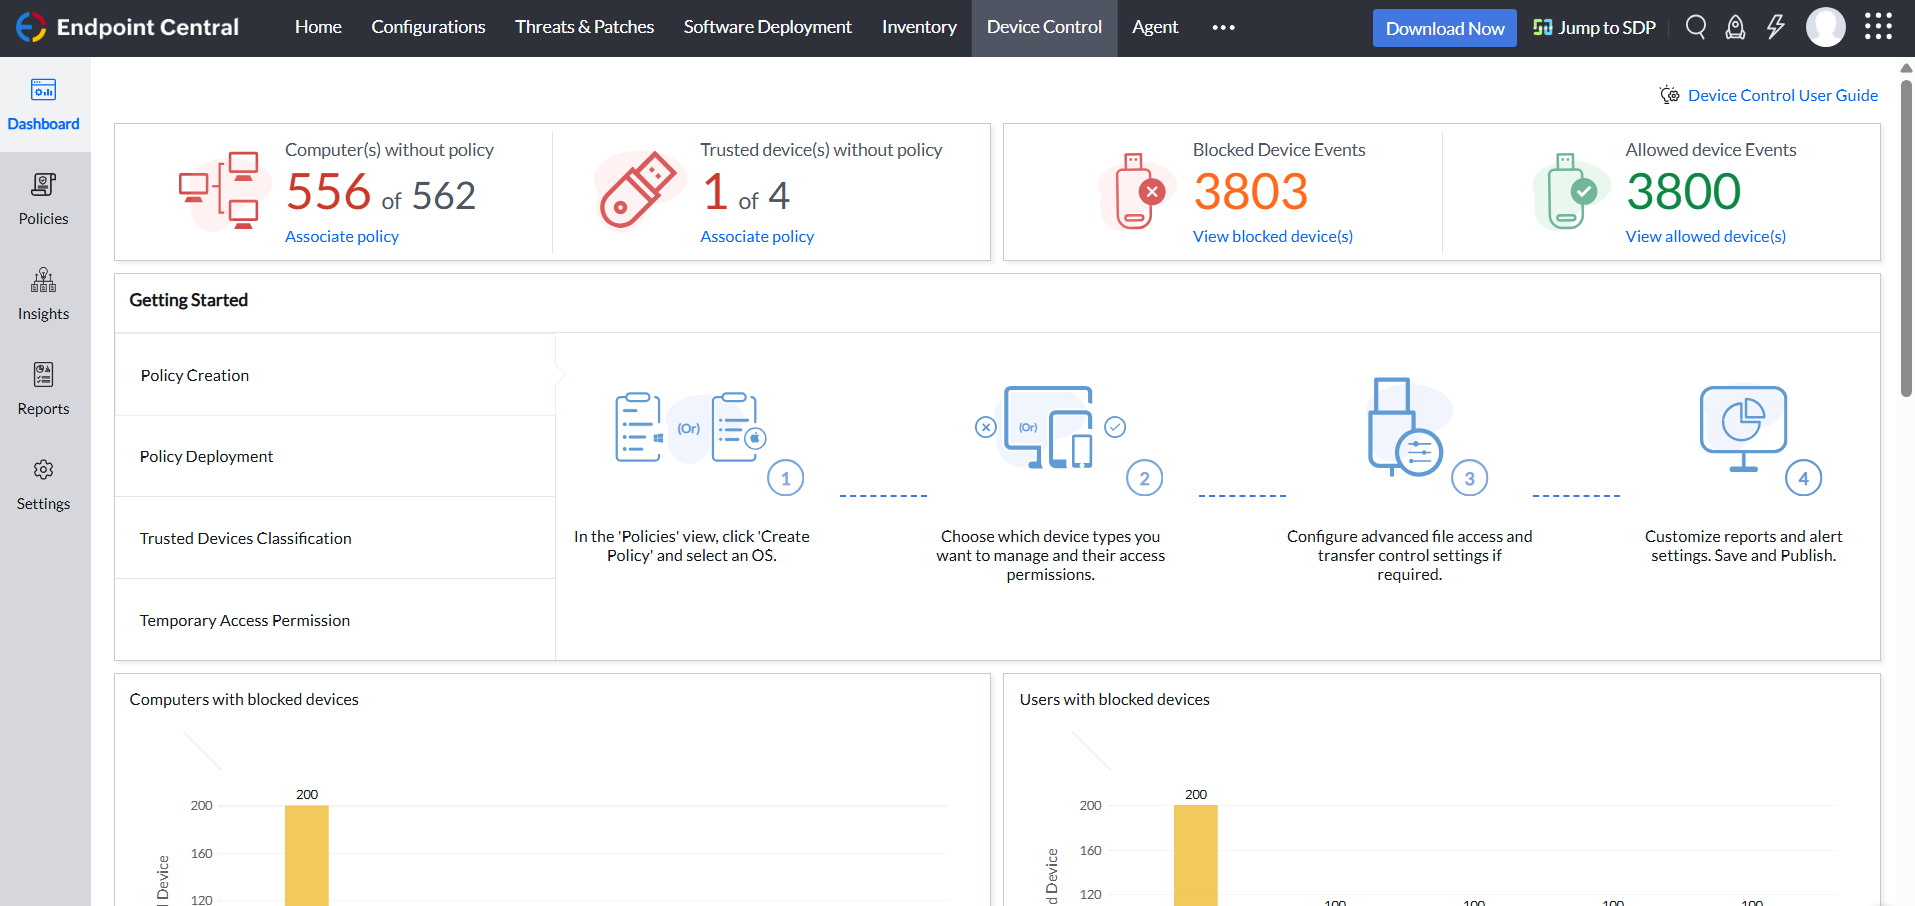
Alerts. We have set up to get email alerts when new hardware is plugged into any computers. This lets us know if someone is bringing in un-authorized equipment (thumb drives, hubs, etc) to better manage what is/is not on our network.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
ManageEngine is considered an excellent product due to its comprehensive suite of solutions for IT management, with ManageEngine Endpoint Central specifically excelling in endpoint management. The platform stands out for its user-friendly interface, robust features, and versatility in addressing diverse IT needs. It offers organizations a centralized solution for endpoint security, patch management, software deployment, and asset management
Not using WNS to communicate with the endpoint console is a big plus. We now use Workspace One, and WNS can be really annoying at times. After deployment, it cleans itself, which is important for us because our current solution leaves the package on the computer and requires maintenance. The remotely script command is a lifesaver.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The immediate chat support is great and very helpful. However, if you need escalated support or have a deeper need that the chat tool can't help with, you will experience significant wait times and slow responses. The time zone difference becomes painful to the point of often just giving up.
It seems that the services offered with the purchase change from what is covered to what is an additional cost. Somethings I thought we had ended up requiring an additional purchase if we wanted to continue using the feature.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big difference between Protect and Barkly/AMP is how exactly it goes about what it's doing. Protect is application whitelisting and program reputation. So the way it's protecting you is using a proprietary reputation service, and hash values to identify applications, and then hitting a list of whitelisted programs to decide if you are able to run that or not, based on the policy you are in. There is a LOT of value in that. We actually are working on transitioning to Cisco Advanced Malware Protection (AMP). The main reason is cost (about the same cost as Cb Protect, but with (most of) the featureset of all 3 Carbon Black products for less than 1/3 of the total spend. AMP works differently, looking at a reputation service powered by Cisco's Talos cloud. You don't really have application whitelisting, but that also reduces how many "requests" you get for applications. So I'll have to find a different way to do whitelisting and USB blocking and the like, but I'm getting more visibility across my network and also built in antivirus (TETRA engine - ClamAV with some work). Barkly is an add that we are looking to put in as it looks at behavior of programs. So specifically it watches for privilege elevation and the like. Thus far all the big name problem children (WannaCry, other ransomware problems) have been caught natively in Barkly day 0.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I was not a part of the initial selection process, but I understand the issue was related to cost per endpoint. As a user of the other solutions I would say that the other solutions do have other strengths that ManageEngine is missing. The remote access tools are superior but at the end of the day you get what you pay for.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info