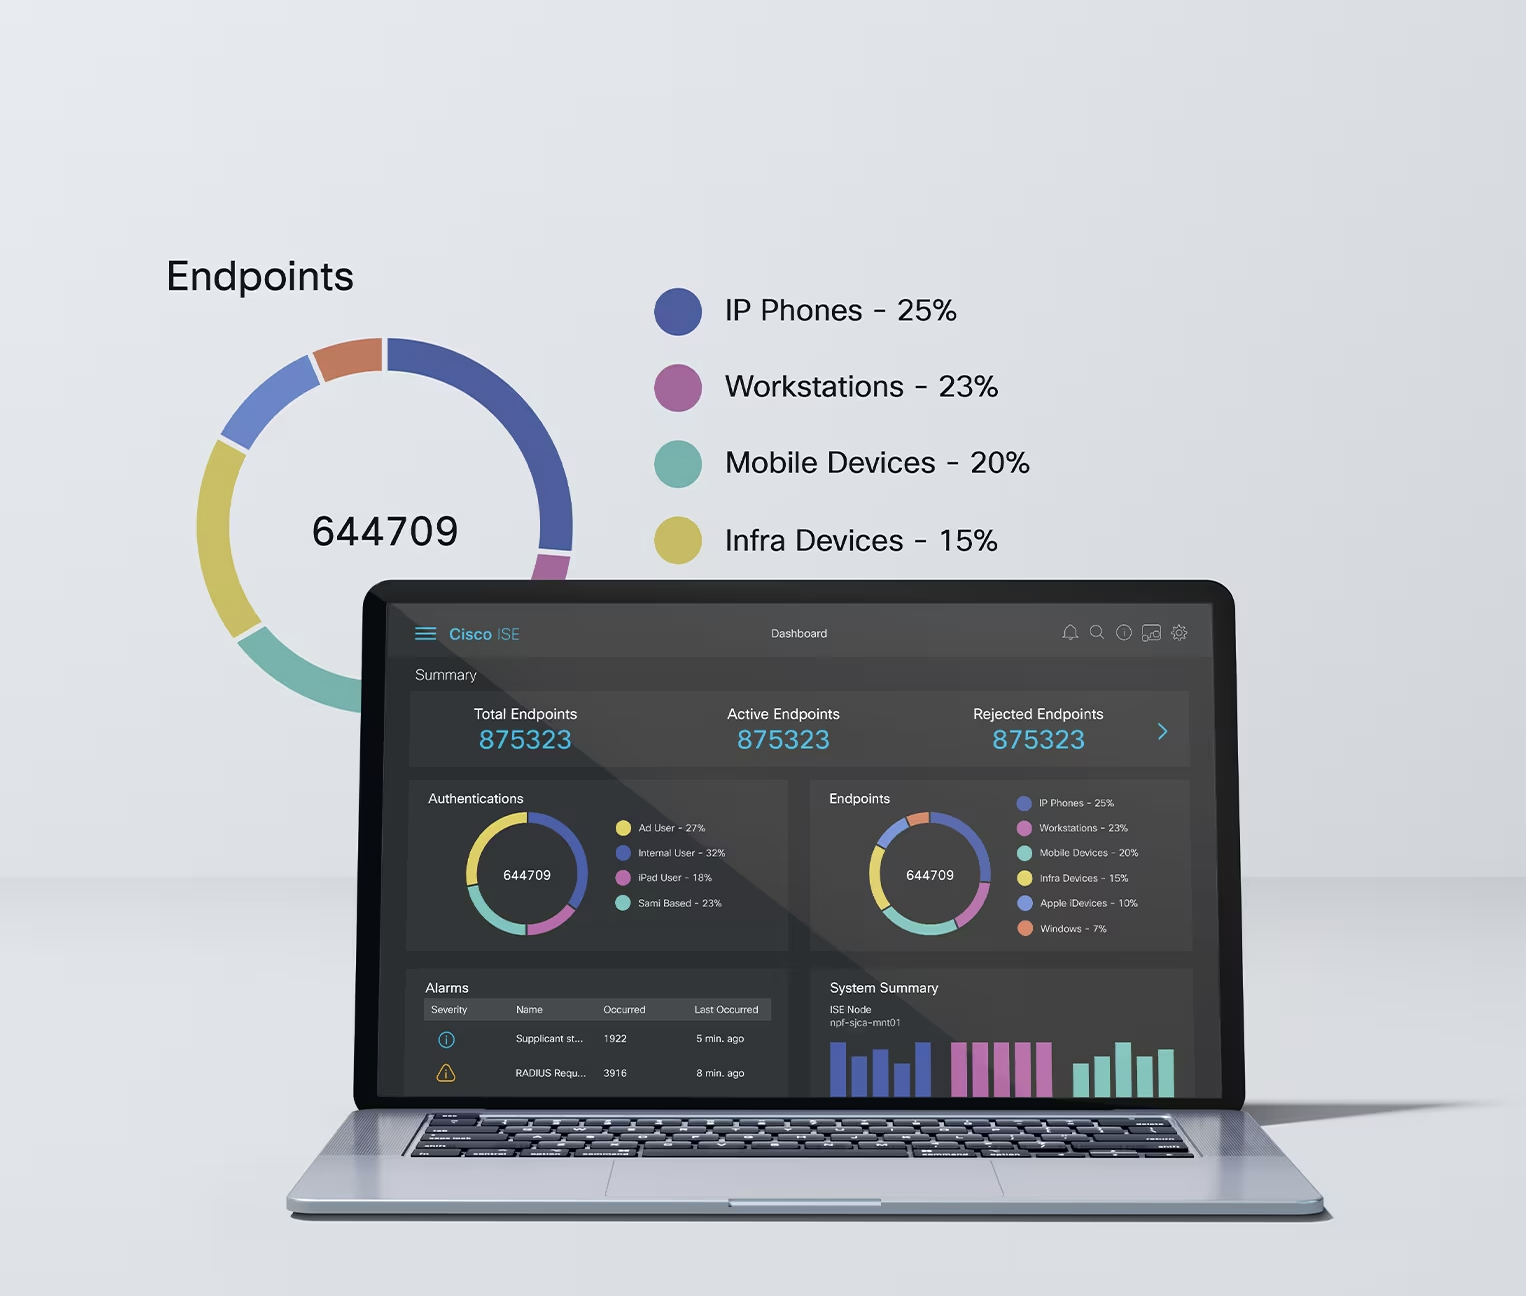
The Cisco Identity Services Engine (ISE) offers a network-based approach for adaptable, trusted access everywhere, based on context. It gives the user intelligent, integrated protection through intent-based policy and compliance solutions.
N/A
ThreatDown, powered by Malwarebytes
Score9.5 out of 10
N/A
ThreatDown (formerly Malwarebytes for Business), combines Malwarebytes' endpoint security capabilities in four bundles. The basic Core tier includes incident response, Next-gen AV, device control, vulnerability assessments, and the ability to block unwanted application.
$345
per year 5 endpoints (minimum)
Pricing
Cisco Identity Services Engine (ISE)
ThreatDown, powered by Malwarebytes
Editions & Modules
No answers on this topic
Core
$345
per year per endpoint (minimum 5)
Advanced
$395
per year per endpoint (minimum 5)
Elite
$495
per year per endpoint (minimum 5)
Ultimate
$595
per year per endpoint (minimum 5)
Offerings
Pricing Offerings
Cisco Identity Services Engine (ISE)
ThreatDown, powered by Malwarebytes
Free Trial
No
Yes
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
—
Optional Add-Ons include server and mobile device protection. Server protection ranges from $129 to $179 per annum depending on service tier. Mobile security is $10 per device, no matter the service tier. A 10% discount is offered for choosing a two-year billing plan.
Well suited... I've used it for both wired and wireless access, and it's perfect for that. In addition to enforcing security on the port, you can also lock down east-west traffic. When you get to the point where you're configuring secure group tags and things like that, you can keep people from getting to places they shouldn't. Basically, you could turn your entire network into a firewall if you wanted to. You can secure access based on the identity of any given user through role-based authentication. For example, if you have salespeople and you don't want them accessing your financial or PCI environment, they authenticate as a salesperson and you can completely stop them from getting to any of that. That's really important, especially for us. Our payment card infrastructure servers are heavily locked down. Granted, in our situation, we firewall all that off anyway, but you still don't want some random individual to be able to even attempt that sort of thing. That's what it's really good for. I'm trying to think of a weakness. I don't know. We don't really struggle with it. There's nothing that I use it for where I wish it were better, at least not that I can think of offhand. I'm sure there are things, I just can't think of anything off the top of my head.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think Malwarebytes is the best anti-malware company. I think it is well-suited for any situation and any device. I think Malwarebytes does the best on Windows and on MacOS. Also, Malwarebytes is always improving, and you can tell they are a company that stays on top of cybersecurity trends. If you have a tight budget or looking for the cheapest solution, then Malwarebytes may not be the solution for you. To clarify, I don't think Malwarebytes is that much more expensive compared to its closest competitors.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Protects against malware - No matter how much training you give end users on social hacking, there is always a breach at some point.
Protects against ransomware - Ransomware could spell disaster for a company...it could literally shut the doors for good.
Centralized administration - Without a terrific centralized method to manage all the systems being protected, it would require an extra position just to maintain all endpoints.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
When I first used the tool in my home systems MANY years ago, I wished for a Business version. I was once at a focus group for a major antivirus company, and one attendee’s feedback to “what could we do better?” was “buy out MalwareBytes and add it to your tool”. I’ve used the Business version since it first became available, and have continued to be a dedicated user through the many iterations and improvements
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
For us the solution is very easily useable on its own. Perhaps that has to do because we started using ISE in the 1.2 days and have seen it grow during the years. Policy creation, etc. is all very visible and thus easy to use. Deployment of multiple nodes is also incredibly easy and flexible. You can easily add or remove nodes as you wish.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It simply works. It doesn't require the hand-holding and monitoring that some other solutions do. It's simple to deploy and maintain, and adding custom content such as Exceptions require minimal effort. I’ve had to add a few exceptions for internal-use, in-house-developed tools, but it’s quite simple to do so within the online interface
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We do have to occasionally reboot the servers when they get low on memory, but we're also a few versions behind. Availability has generally been pretty good though with no major outages in the time that we've had it implemented.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco support is second to none, both in terms of how you access support but also the knowledge of the individual support teams. If you focus on one technology and provide "manufacturer support" then you can rest assured that you are accessing Cisco's top individuals. I feel like this is a USP for Cisco support.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
As I mentioned, we have only email support. Their phone support was very expensive. If we ever have any issues, we have to email them and wait for their response. In most cases, I have figured out the issue on my own. The software is very stable so we haven't used their support much.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I think our system integrators lacks some competencies and this has led to an implementation that is still perfectible. (i.e. dedicating an interface for intra-cluster communication)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I first implemented this more than 10 years ago, when it required an in-site setup with SQL Server (or SQL Express), and even that was pretty easy. With the move to centralized web management some treats ago, it’s become even easier to deploy
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think all give some visibility of device monitoring and management, but Cisco Identity Services Engine gives a good way to manage more details about the device in a centralized way that gives a wider range of monitoring and control than the other softwares individually. I don't think Cisco Identity Services Engine eliminates the need for these other software as of now, but there is potential for Cisco Identity Services Engine to be able to take over more of these roles.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It's no contest. Cisco AMP, Umbrella and Endpoint use vast amounts of resources and provide little protection when compared with Malwarebytes. One client recently replaced Cisco with MWB and found over 7,300 vulnerabilities on 352 endpoints, including 120 listed as Critical and 7,180 listed as High, with CVE's dating back to 2008.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It's fully customised and comprehensive. only thing is you need to know what you want. Proper research and planning would save lots of time and effort .
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I don't know about negatives because we haven't seen it right now, but positive impact is one is the roadmap we have. And now since we are going ahead with doing the deployment of Cisco ISE, we see that we are getting closure to, so at the end of the day, we have to make sure that operationally we stay excellent. So that's where operational excellence comes in. Cisco ISE is basically addressing that for us. Right now we are in a situation if there is a WIFI issue or if there is an authentication issue, it gets really difficult to isolate the problem. But with Cisco ISE , this functionality is going to come in. So we believe that it would be a good ROI.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The ease of remediation has saved our IT team a number of hours manually installing, for example, the free version of Malwarebytes to remove infections, and then cleaning the machine up. Being able to centrally send commands to clean the device is much more efficient.
The centralised management has also alerted us to infections on machines that we might not otherwise have known about, as the existing AV had not detected them, saving us potential data loss, or system damage.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info