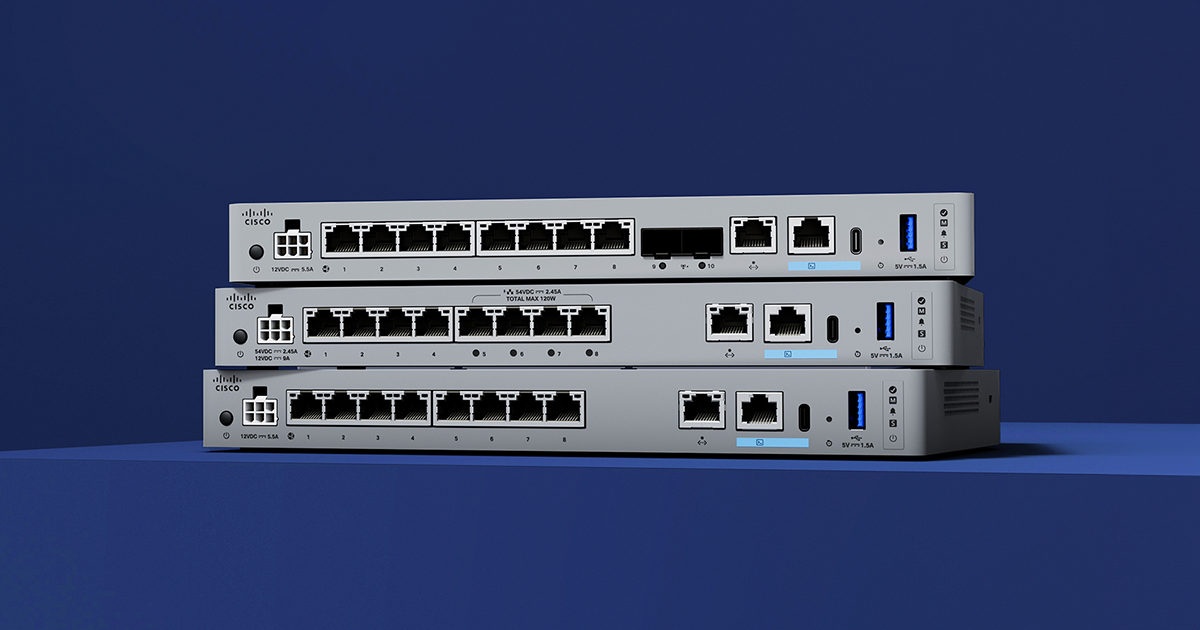
Cisco's Meraki MR Series is a wireless LAN solution.
N/A
Cisco Secure Firewall
Score8.4 out of 10
N/A
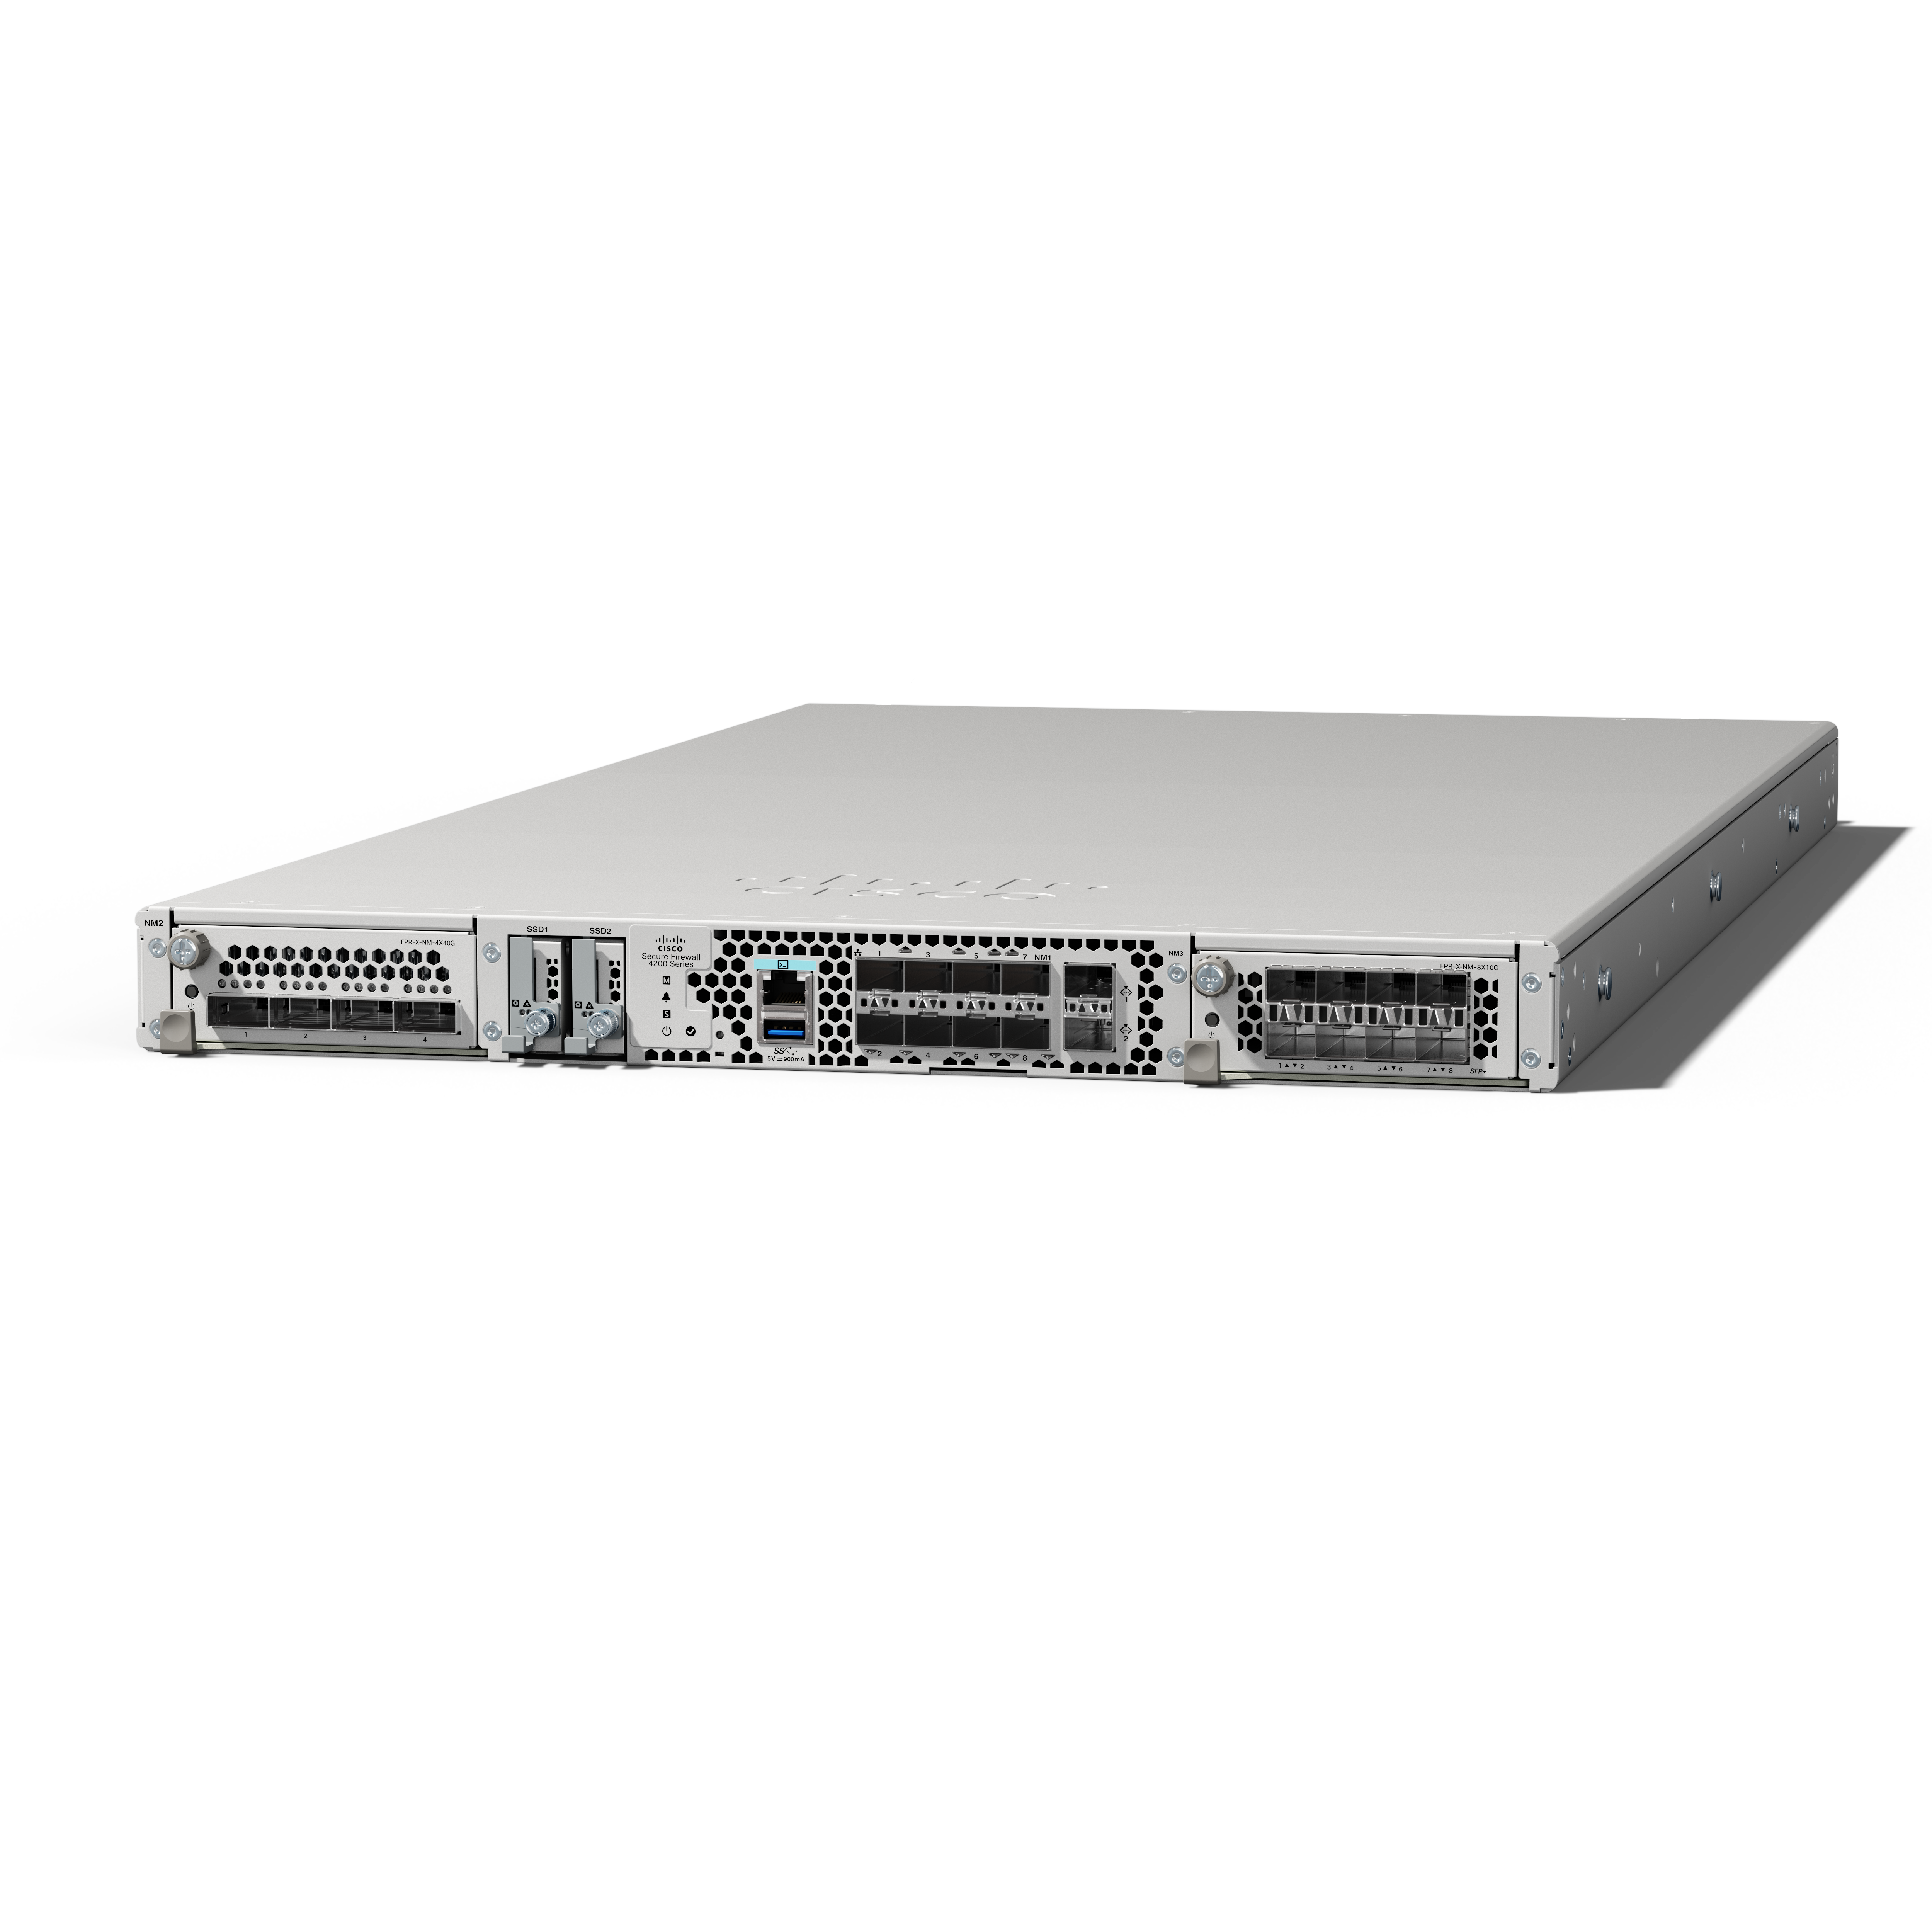
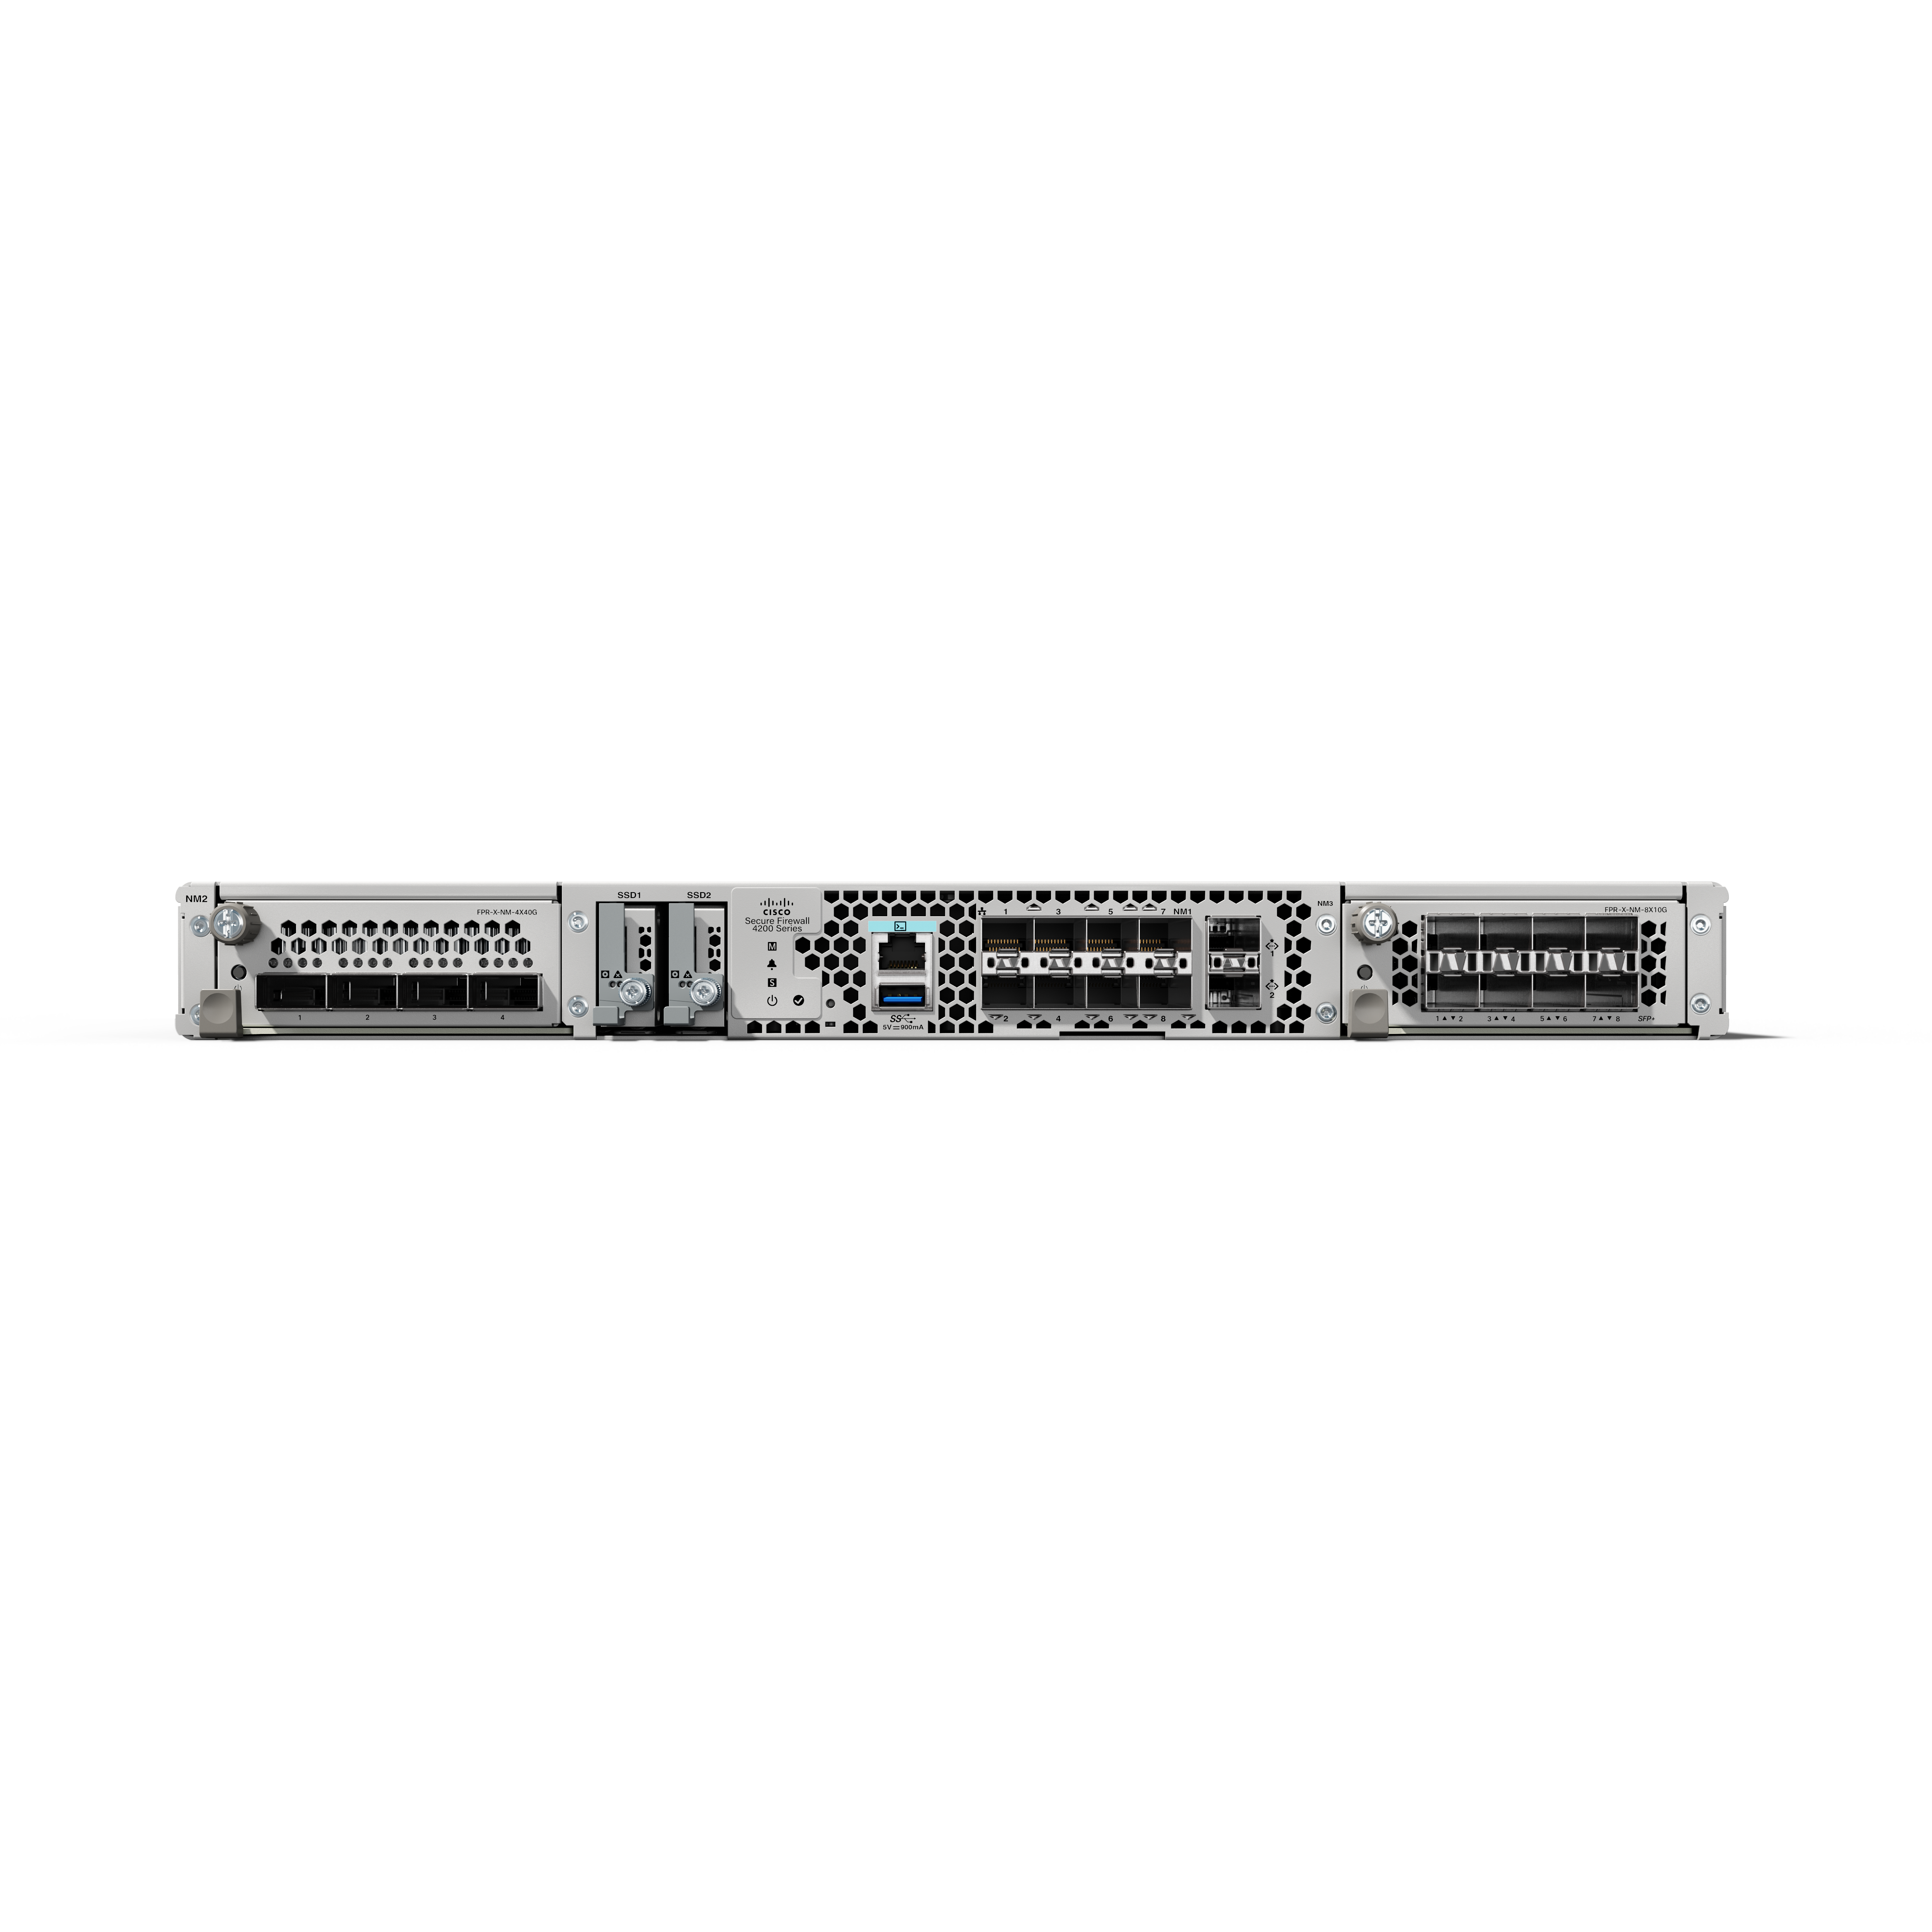
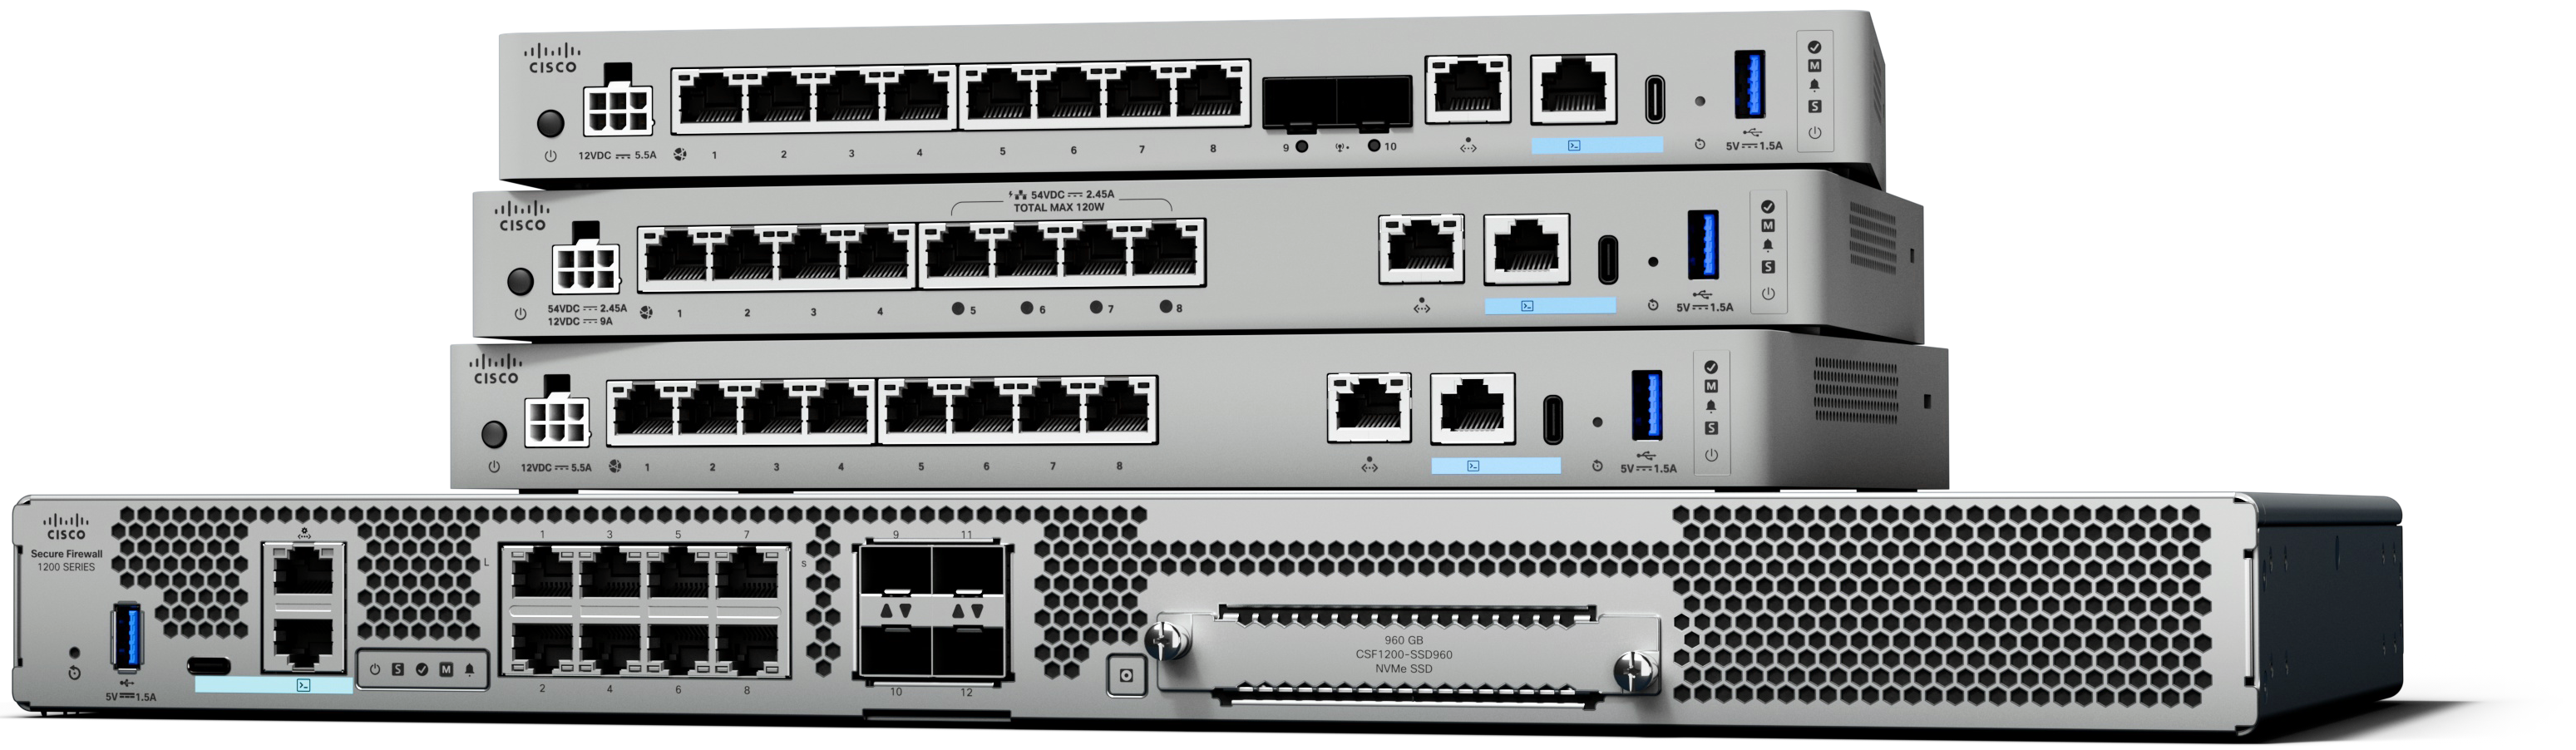
Cisco Secure Firewall delivers comprehensive threat protection for modern, distributed networks. Built to support hybrid workforces and multicloud environments, it enables Zero Trust access, application visibility, and secure remote connectivity. With integration across the Cisco Secure portfolio, including SecureX and Talos threat intelligence, the firewall powers organizations to detect and stop more sophisticated threats. Centralized management simplifies policy enforcement, orchestration,…
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco
Verified User
Chose Cisco Secure Firewall
Cisco Secure Firewall outperforms and the feature set are much better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Cisco Secure Firewall
I really like Cisco FTD with FMC. It is one of the best products out there. Nevertheless, when compared to PaloAlot it has some room for improvements. The PaloAlto firewalls in general are faster easier to use and have better features. Easier to TS and faster to operate. I …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
There is no doubt that these access points are objectively some of the best in the industry. If you need reliability, stability, range, and something to "set and forget" these are an easy choice for those things alone. However, these are most appropriate in high demand, large environments where you can take advantage of the RF tuning, wireless stability, and overall robustness of the platform. Another important note is the SUPPORT as well. There are competitors that I won't mention that simply don't have the level of support and expertise for complex troubleshooting if you ever need it, and that alone counts as significant factor when considering the product too. Merak has that covered.
To wrap up, the cost for large deployment makes far more sense than at a small operation where you need something like 5 APs in a small/medium office for basic Wi-Fi needs. That includes potential cost of time spent troubleshooting future network issues too by IT personnel.
I can't think of scenarios where it is less appropriate, unless we are talking about real tiny businesses. More businesses will find Cisco Secure Firewall an outstanding tool to use, love, and trust from a reputable Network giant vendor. It is a must for businesses that want to focus on what they are doing, and leaving the network security for the pros.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's cloud based, so as long as we have an internet connection, we can access it. Whenever we push a change, it's one stop like a single pane of glass to manage all our equipment. And so that's what I liked about it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco's firewall actually does its job of blocking what it is supposed to block. We had an old Firewall that led to slippages. Cisco catches 97% of malware and vulnerabilities during testing. For Coitiar, that means an engineer who clicks a link with malware is handled quickly.
We actually tested if failovers would affect running sessions. We pulled our primary unit during a certification submission period. The firewall just switched, and the connection kept running.
The AI assistant in policy management is excellent, and for our lean team, it makes the whole process easy and efficient. I don't have to audit 200 policies manually; the AI steps in and does its thing.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Internet connection dependency for management. Management is cloud-based, requiring a strong internet connection. Local management is not possible in the event of network problems or internet outages.
Limited in-depth configuration options. Some more detailed configuration settings are missing or difficult to configure, such as RF tuning and QoS. These are available in some other Cisco products.
License costs: an active license must always be present in the environment, otherwise the product won't work. It's easy to purchase, but if you're going to be expanding regularly, the costs will add up considerably. Ultimately, it's wise to factor this into your purchase.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I mean I think a lot of the technology with managing them is getting better. There's a few cons to the new firewall management console. You can't sort through routes or I think you can with interfaces now, but there's a few caveats that they haven't really worked out yet, but they're implementing AI into it, so it's getting to be a lot easier to use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It is a solution that works very well. It is almost like setup and forget, since the solution works. When issues occur, documentation is available with detailed steps on how to solve this problems you are facing, of course Technical Support is always ready to help. We have had instances where an Access Point fails and within 2 days we have the replacement
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It works really well. We can do most anything we want or need to with it, and you don’t have to have a doctorate or multiple certs to necessarily figure it out. The thing that would probably have to happen to make us switch would be if we just got priced out - Cisco’s more powerful and higher bandwidth models cost a pretty penny.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
To get basic functionality doesn't take long. Set up a new Meraki Dashboard activate the licenses and get internet connection for the APs and you are more or less done. The Dashboard will find your items and you're good to go.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
i think overall after ALOT of tac cases it works allright now. But still have alot of issues if you use cloud based mangement. fx, if you open 2 windows of access policys, both of the pages, rules starte to jump form side to side. if you then open one more list, its start to jump even faster. if you close the 2 of them, its back to normal. ALSO the extended access lists for VPN, SUCKS. Its the tiniest window when opening the editor, and you are not able to give the rules names, Which means finding and editing rules SUCKS, its a horrible experience, and eveytime we have to we want to yell :P
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We have not had any performance issues with Cisco Secure Firewall, even with DPI and IPS enabled, we have not seen a performance hit. Emoployes have not complained about any slow network speeds that could have been attributed to the secure firewall it has always been something else within the office network.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We have not had any issues with the Meraki WiFi Access Point hardware but we did encounter a problem with a Meraki LAN switch that failed to power up. Upon a email into the Meraki Support, they promptly called back and we went over some quick tests to determine a power supply problem. A replacement LAN switch was sent to me the next day.
I rarely get the support I need in the time I need it. Often, while they are "looking at packet captures and going to get back to me" I fix the problem on my own. If you were to look at my TAC cases over the past year, you would see some very lengthy cases that usually ended with me contacting the TAC person and telling them to just close the case
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
was a good training but questions was answered not so good. Training was "Fundamentals of Cisco Firewall Threat Defense and Intrusion Prevention (SFWIPF)".
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
There were documents that detailed how the WiFi Access Point was to be installed and mounted. The only issue was to cable the device, we use a third party for this type of work and typically has to be performed after normal business hours. Other than that, the installation was easy.
Our initial implementation was aided by Cisco's professional services and was excellent. The engineer was very knowledgeable and helped us work through issues while building out our new internet security edge Part of this involved tools to migrate the firewall configuration from old to new.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The Cisco Meraki MR Wireless Access Points fare really well against HPE Aruba AP. The cost difference is minimal on the hardware although things get more expensive on support and subscription cost (on going cost). Speed and throughput seems to be better on Cisco Meraki (user feedback and experience not technically measured). User connectivity is better with HPE Aruba primarily because of the Clearpass solution on top of its generic software management.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco Secure Firewall works better with the Cisco ecosystem when we can utilize it and feels beefy enough when we utilize it in the data center. The Fortinet we have found are great, small cost boxes for remote offices with a better UI then Cisco Secure Firewalls. The feature set included with the firewalls feels similar from a security point of view.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A solid, realistic rating most people give for Cisco Secure Firewall pricing is 7 or 8 out of 10 (because the product is strong but licensing can be a bit complex)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
As far as I know, it's 10. I mean, because like I said, I manage stuff in the south. I have coworkers that manage it in the north. And so the scalability of it to be able to be go in and see the configurations of the ones in the north as well as they can see in the south. So across the board, it works really well for how widespread out it is.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco Secure Firewall has never given us any trouble, it has stayed up at all times, upgrading the appliance has also become much simpler. We operate the appliance in a HA pair, so 0% downtime within our organisation. During switchover while upgrading, not a single packet seems to get lost, so this has been a very valuable asset to our company.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Uptime has improved significantly. The dashboard automatically keeps devices up to date by scheduling upgrades at remote times (say 2am on a Sunday)
Swapping to Cisco Meraki MR Wireless Access Points has reduced the management overhead. No more long controller software hardware upgrades and obviously no more need for beefy central controllers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info