Cisco Nexus Dashboard simplifies data-center networks with automation and analytics. The data-center network helps organizations to meet business demands, and provision reliable data-center networking services as fast as possible, when and where organizations need it. As network infrastructure management is becoming more complex, diverse, and distributed, with multiple configuration points, monitoring tools, and vast amounts of data being generated every second. Cisco Nexus Dashboard is…
N/A
FireMon
Score7.9 out of 10
Enterprise companies (1,001+ employees)
FireMon is a real-time security policy management solution built for today’s complex multi-vendor, enterprise environments. Supporting the latest firewall and policy enforcement technologies spanning on-premises networks to the cloud, FireMon delivers visibility and control across the entire IT landscape to automate policy changes, meet compliance standards, to minimize policy-related risk. Since creating their policy management solution in 2004, FireMon states they've helped…
We used Cisco Nexus Dashboard specifically for automating the creation of networks in our private cloud environment using a VXLAN EVPN multisite environment. It integrates into Infoblox well. It's also very suited in network troubleshooting for past and present issues. Where I don't see it being used much is in the campus but it's nice to know we have the ability to add catalyst if needed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
FireMon is best used in a large environment (for example, I have >100 firewalls in my environment). It's best used when trying to improve security posture and showing changes in firewall security over time. It might not be the best choice for smaller environments or those that aren't concerned about security management.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
With the latest version release of Cisco Nexus Dashboard to version 3.0.1 I can say that most of the features have already improved but one of the wishlists that I want for ND is the possibility of extracting lists of Anomaly.
Include older versions of Firmware in the list of choices when doing the firmware upgrade analysis, currently only the recommended is in the list of choices.
If possible, include all the prechecks in the Firmware pre-upgrade analysis same in the script provided by Cisco.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We observe significant product development with each release, along with substantial expansion of functionality. The program code has been consolidated into a single image, which simplifies installation and routine system update operations. Additionally, it is possible to install it outside the production network, which further enhances the solution’s availability.Additionally, the new graphical interface is very simplified and user-friendly.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The shell is locked out and we can't run any general centos commands. The implementation and maintainence of the arch is very complex. Even with the right identifiers on log messages the log collection keeps failing. The warning messages on the device are ambiguous. The log messages on firemon are a bit confusing and don't show the exact issue.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
For the end user, it is relatively easy to use. However, some training and practice is a must because the NSO is not as straightforward as the traditional router CLI. For the administrator, Cisco Network Service Orchestrator (NSO) is just like another program running on the Linux system--there is no big difference.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
FireMon has been relatively stable overall. However, there have been a handful of times where we had issues with the console. For example, we couldn't update which devices to include in a security assessment. The initial suggestion from support was to just reboot it. It seems like there weren't many other options available such as to restart services before going to the extreme of a complete reboot.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
For us, it's not yet a single pane of glass for the ACI network as Network Assurance Engine is not yet integrated into the [Cisco] Nexus Dashboard. This will be the case after the next update we plan to do. Today it's a tool I use daily to figure out if something unusual or unexpected happened in the SDN part of our network. The legacy network is still monitored with different tools.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'm not sure we have the largest implementation of FireMon out there but we do have a few 1000 devices being probed by FireMon. Overall, the system's performance has been rock solid. The console refreshes quickly and reports are generated within an expected timeframe.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
here was never a need to contact support, as the system includes several commands that allow for self-healing. Even if, after the upgrade process, one of the processes was not running, I was able to quickly find the appropriate sequence of commands that definitively resolved the issue. The entire architecture was designed in such a way as to be resilient to the failure of one node in a three-server setup.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
FireMon technical support is awesome! They respond quickly to our requests and they are well trained and very knowledgeable about the tool. Some issues have to be referred to the development team, but technical support largely provides solutions for any issues that we may have.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Honestly, the product implementation took 1–2 days to comprehensively manage the client’s entire infrastructure. The delivered on-premise solution, provided as physical servers, quickly builds the required environment in which individual data centers are rapidly added. The data collection process takes some time but also depends on the number of devices in the network.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
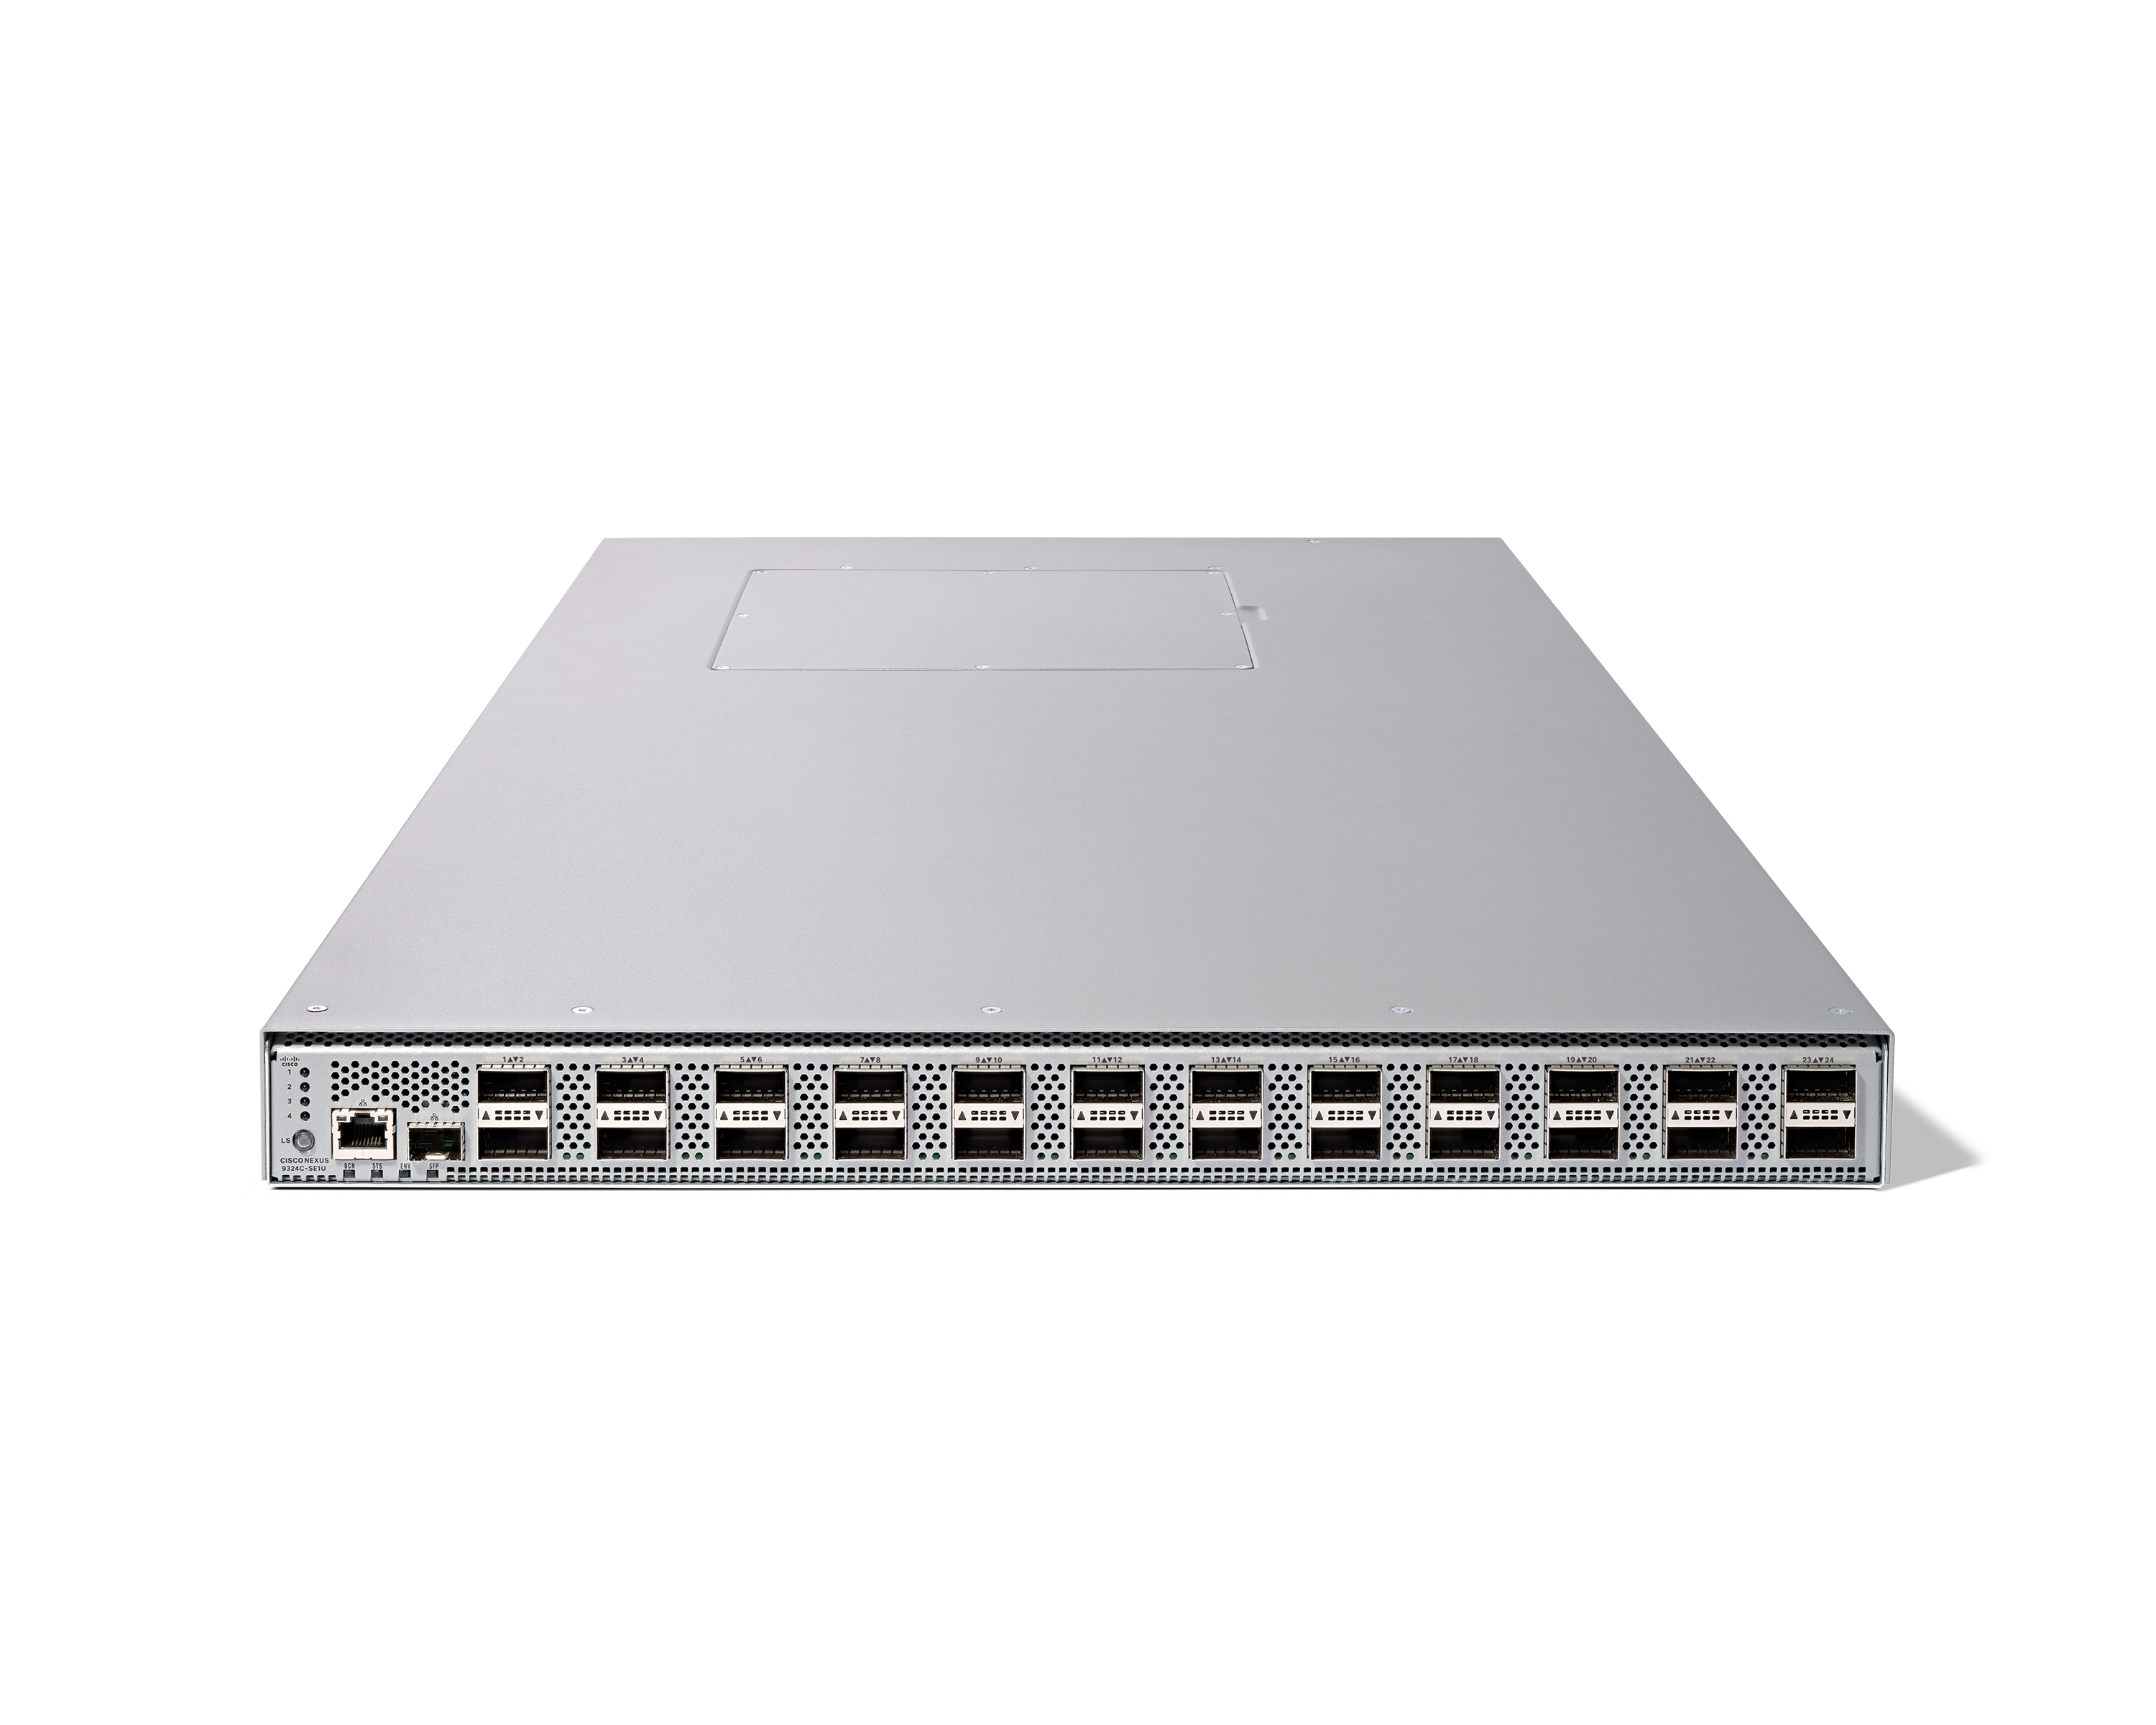
The Cisco Nexus Series switches perform admirably in our blended distributed system. We have been dealing with any of these sorts of switches for over 5 years and have been exceptionally happy with their functionality. Several of our other computer networks in our data rooms have proved effective with Cisco equipment. Because of the simplicity of maintenance and the high quality of technical support provided by Cisco representatives, there is a high level of trust in these switches.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I has worked with AlgoSec and while they are very similar product, I find the FireMon is easier to understand and get rolling with. While both require some learning, FireMon is by far the easier one. Once you have an understanding of how things are arranged and labeled you can easily import firewalls and begin to work on them to improve them
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It's a very secure platform that can manage all the business networks, monitor various network traffic, and is easy project management software. Cisco Nexus Dashboard Fabric Controller can centralize all the network traffic in one room for easy and secure management and threat detection capability and even the secure channels offered are excellent.
Firemon Is easily scalable and maintainable with any size team. Although it requires some tech debt, it is well worth the time to invest to ensure compliance is visible and reports are accurate. Although our environment is very large we do not fully utilize the scalability of the Firemon product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info