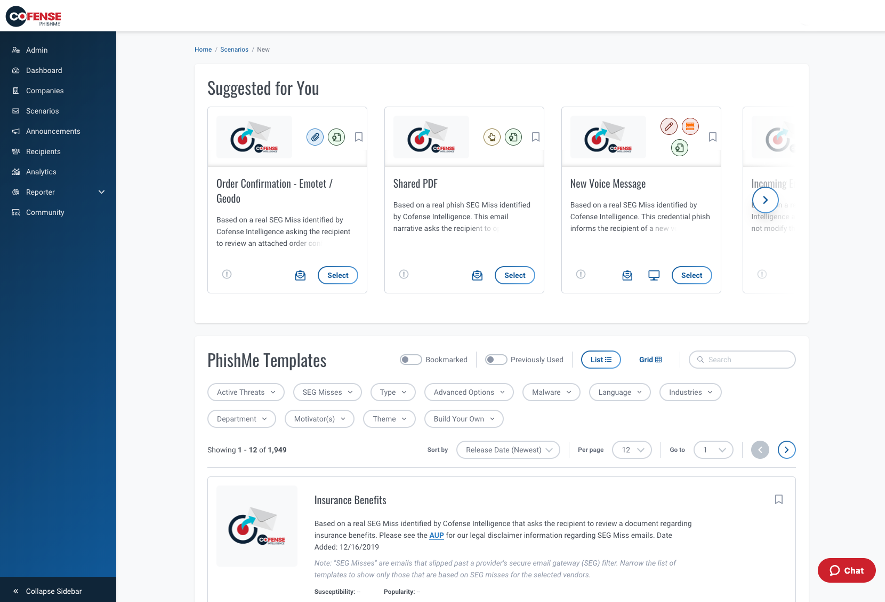
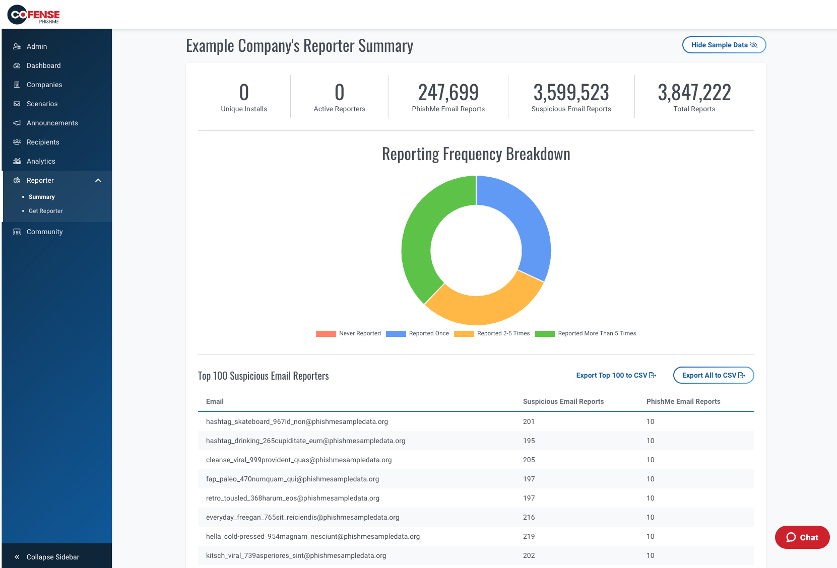
Cofense PhishMe is a cyber threat and phishing simulator meant to be of use in training employees to be wary against threats and also to gain information about general employee threat knowledge and preparedness. A free trial is available for small business.
N/A
FireMon
Score7.9 out of 10
Enterprise companies (1,001+ employees)
FireMon is a real-time security policy management solution built for today’s complex multi-vendor, enterprise environments. Supporting the latest firewall and policy enforcement technologies spanning on-premises networks to the cloud, FireMon delivers visibility and control across the entire IT landscape to automate policy changes, meet compliance standards, to minimize policy-related risk. Since creating their policy management solution in 2004, FireMon states they've helped…
N/A
Pricing
Cofense PhishMe
FireMon
Editions & Modules
No answers on this topic
No answers on this topic
Offerings
Pricing Offerings
Cofense PhishMe
FireMon
Free Trial
Yes
Yes
Free/Freemium Version
No
No
Premium Consulting/Integration Services
Yes
Yes
Entry-level Setup Fee
No setup fee
Optional
Additional Details
—
—
More Pricing Information
Community Pulse
Cofense PhishMe
FireMon
Considered Both Products
Cofense
No answer on this topic
FireMon
Verified User
Chose FireMon
For our use case, only FireMon met our needs with the systems we use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cofense PhishMe is an excellent solution for scenarios where it will be sold as a managed service. I believe that PhishMe is too expensive for many clients and instead would benefit from the economies of scale where an MSSP sells it as part of a whole service, which offers the analysts and reporting included. PhishMe is excellent for training and awareness of Phishing, but shouldn't replace mandatory training for new joiners or yearly refreshers, it should only be used as an additional training option.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
FireMon is best used in a large environment (for example, I have >100 firewalls in my environment). It's best used when trying to improve security posture and showing changes in firewall security over time. It might not be the best choice for smaller environments or those that aren't concerned about security management.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It gives clear-cut segregation of different parts of an email, header, text and HTML body, URL, attachments, HTML preview and some analytical insight like "similar reports." This distinctive approach actually helps reduce data overload during an analysis.
The URLs captured here pass through an automatic reputation check [in our case VirusTotal] and add a tag of the reputation. If it is a well-known bad URL the tag helps us take the decision fast.
For creating automation rules on the reported emails the "Recipes" section is really helpful. We can create easy recipes [or rules ] to handle a huge flow of reports and also we can create more sophisticated rules depending on the Cyber intelligence feed to catch the really bad currently less known attack attempts by malicious emails.
The "Threat Indicators" section is also useful to use as a threat intelligence source to check the URLs for their maliciousness.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The shell is locked out and we can't run any general centos commands. The implementation and maintainence of the arch is very complex. Even with the right identifiers on log messages the log collection keeps failing. The warning messages on the device are ambiguous. The log messages on firemon are a bit confusing and don't show the exact issue.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Its built with UX in mind and is aimed at non-tech people, to ensure that almost everyone can run the campaign. But if we go deeper - sometimes you will need an HTML editor or support in order to figure out some advanced edits you might want to add in your scenarios.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
FireMon has been relatively stable overall. However, there have been a handful of times where we had issues with the console. For example, we couldn't update which devices to include in a security assessment. The initial suggestion from support was to just reboot it. It seems like there weren't many other options available such as to restart services before going to the extreme of a complete reboot.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'm not sure we have the largest implementation of FireMon out there but we do have a few 1000 devices being probed by FireMon. Overall, the system's performance has been rock solid. The console refreshes quickly and reports are generated within an expected timeframe.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I have not had to use their support for pretty much anything. The software works well, and is very intuitive. I would imagine their support would be rather basic as there is not too much that can go wrong with a report phishing button, and if it were I would probably consider a different software.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
FireMon technical support is awesome! They respond quickly to our requests and they are well trained and very knowledgeable about the tool. Some issues have to be referred to the development team, but technical support largely provides solutions for any issues that we may have.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cofense PhishMe was the first choice for us as the user interface as well as their bundle package with Cofense Triage and Vision has helped the organisation to alleviate the overall security awareness posture. The other vendors did not provide a vast range of phishing scenarios as compared to Cofense PhishMe platform.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I has worked with AlgoSec and while they are very similar product, I find the FireMon is easier to understand and get rolling with. While both require some learning, FireMon is by far the easier one. Once you have an understanding of how things are arranged and labeled you can easily import firewalls and begin to work on them to improve them
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Firemon Is easily scalable and maintainable with any size team. Although it requires some tech debt, it is well worth the time to invest to ensure compliance is visible and reports are accurate. Although our environment is very large we do not fully utilize the scalability of the Firemon product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Recipes in the system are capable of handling almost 2x what an analyst does, which cuts down the efforts [of] an analyst and provides more time for accurate strategies.
With roughly 90% false positives coming through, the remaining 10% of true positives need as much attention as they can get for the full investigation and analysis.
1,500 or more phishing messages can come through in a given week and the amount of time/employees required to review this without a tool like Cofense is surely beyond [the] expected/anticipated budget.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info