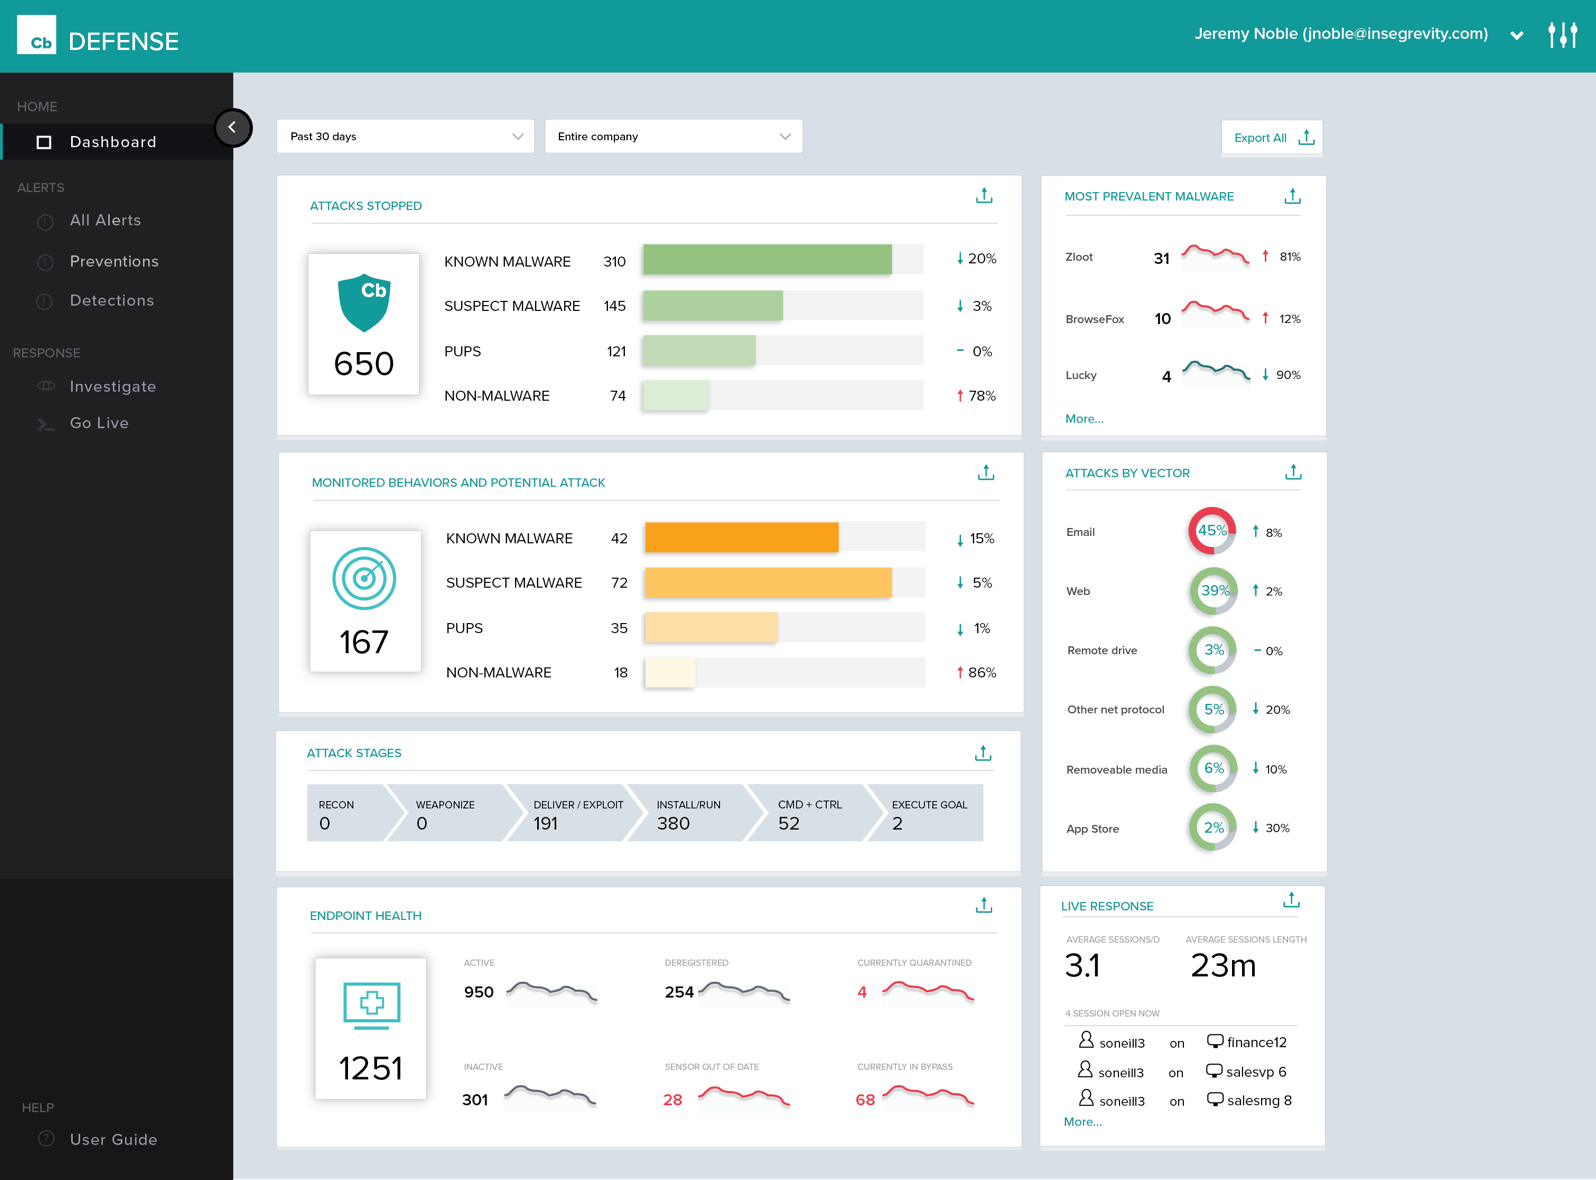
Carbon Black Endpoint is an endpoint security and "next-gen antivirus (NGAV)" that uses machine learning and behavioral models to analyze endpoint data and uncover malicious activity to stop all types of attacks before they reach critical systems.
N/A
CrowdStrike Falcon
Score9 out of 10
N/A
CrowdStrike offers the Falcon Endpoint Protection suite, an antivirus and endpoint protection system emphasizing threat detection, machine learning malware detection, and signature free updating. Additionally the available Falcon Spotlight module delivers vulnerability assessment with no performance impact, no additional agents, hardware, scheduled scans, firewall exceptions or admin credentials.
$59.99
per endpoint/month (minimum number of endpoints applies)
Pricing
Carbon Black Endpoint
CrowdStrike Falcon
Editions & Modules
No answers on this topic
Falcon Go (Small Business)
$59.99
per endpoint/month (minimum number of endpoints applies)
Falcon Go (Small Business)
$59.99
Falcon Pro
$99.99
per endpoint/month (for 5-250 endpoints, billed annually)
Falcon Enterprise
$184.99
per endpoint/month (minimum number of endpoints applies)
Offerings
Pricing Offerings
Carbon Black Endpoint
CrowdStrike Falcon
Free Trial
No
Yes
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
Yes
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
—
—
More Pricing Information
Community Pulse
Carbon Black Endpoint
CrowdStrike Falcon
Considered Both Products
Broadcom
Verified User
Chose Carbon Black Endpoint
We evaluated 3 other competitors and determined that Cb Defense was the best "bang for the buck" when it comes to Next-Generation Anti Virus. Their support (and sales) teams have been very helpful and offered a tremendous level of transparency. Our sales representative went …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
CrowdStrike
Verified User
Chose CrowdStrike Falcon
At the time we evaluated the products, CrowdStrike was clearly leading in this space. It's possible since that time so other products have added additional features and may be equivalent.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose CrowdStrike Falcon
Is better and the ease of use and cost was spot on.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose CrowdStrike Falcon
CrowdStrike Falcon is a far superior endpoint protection product that requires much less upkeep for similar pricing. There was a lot of extra administrative overhead to write detections and keep endpoints updated compared to CrowdStrike Falcon. I was very surprised to learn …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose CrowdStrike Falcon
I think Carbon black is as good a product as CrowdStrike Falcon. We went with CrowdStrike Falcon because it was cheaper at the time and then stuck with it when Dell bought Carbon Black. I find that the logging and information is much better that Microsoft defender, many of …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose CrowdStrike Falcon
It's easier to manage, less time to deploy, has more integrations and better understands the business needs. False positives, visibility, sensors management, device control, detections, preventions are pretty much the differentiators with other rivals. It will have more and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose CrowdStrike Falcon
XDR and Crowdstrike were about even for us. Carbon Black was the agent we were replacing due to failures.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cb Defense has been working very well in our organization. It is giving us much better insight into the applications that people are running on their systems (without authorization). This software is also great because it provides visibility into systems that are remote (off the network but still have Internet access). The out of band feature is great to help ensure that the systems are protected even when a user is traveling.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Crowdstrike is a unified platform for monitoring endpoint devices, whether they're workstations, servers, cloud-native machines, or even mobile devices. It uses AI/ML to monitor anomalies and suspicious behavior, including zero-day attacks. It is suitable for large organizations but may be costlier or less appropriate for smaller organizations, those who want an on-prem EDR setup, and those who need custom scanning based on compliance requirements.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
History of Process Execution, really anything that happens in the system is easily seen within the Dashboard. I can determine if a bad actor has infected the system, be it malware, backdoor, rootkit, Trojan, then from that point, I can put the system into Quarantine.
Being able to quarantine the system from the Dashboard. With these type of tools, pulling the power and running a hard drive image is not needed. Put the system in quarantine, start the analysis. A year ago, the network engineer might move the system into a VLAN that has no access to anything, except the system performing the remote analysis... Now I do not have to rely on anyone to move a system, power it down, pull the drive, or image the drive. I can just start the analysis right from my workstation.
The Live Response, again goes hand in hand with the quarantine feature.
By now, I am sure you see a process. Its simple, and easy and all done from a cloud-based console, called the dashboard. .. deploy the agent, create the policy, and active live response, set up email alerts, and monitor your endpoints... you are now ready to perform a triage in the event of an infection. We have step 1, step 2, step 3... but, just remember, things do happen, nothing is perfect, but this product has its advantages.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Policy management can be cumbersome. It is simple to set up a single policy but you have no way to apply the rules to multiple groups. If you need to set up the same rule to multiple policies, you need to type it over again.
Agent updates can be very slow to deploy. We use a mix of rolling out updates via the web console and our management appliance. It can take several weeks to update all agents.
We can be confused on why a rule will apply to a file. Sometimes something is blocked but we don't understand why.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Crowdstrike has a large suite of tools built for helping the engineers triage and respond to security event whenever identified. The ability to customize the security policies and implement more granular policies to different devices based on the functionality is unmatched. Crowdstrike provides so much of ability in a decent budget which ascertains the value for money or ROI.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The console of the product is very easy to use. It provides great detailed information about all aspects of things occurring on the endpoint. It was easy to deploy and set up. The centralized cloud-based interface has made it easy to add two domains and manage them under a single pane with multiple admins. The only reason I wouldn't give it a higher score is a little bit of lag between updated info from the clients and also the lack of accountability in the deployment process. You set the deployment up for multiple machines and can't easily see if it was successful and/or it takes a while to see if it succeeded or failed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think it is a complete and very trustful XDR platform, with very few False Positives. It is very well supported by highly skilled professionals on all levels: from pre-sales engineers, Customer Account Managers and support engineers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
First, I need to disclose that our support is provided by SecureWorks. We purchased CB Defense from them, and they provide 24x7 monitoring and notification services for the solution and its deployment on our endpoints. To date, we are very pleased with this arrangement
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Any time we need to engage the Crowdstrike Falcon Complete Team, their response is switch, thorough, and they are sure to not close out any request until the customer confirms that they have provided an acceptable resolution. If I ever need anything from the account team related to the product, I also get a response from them within minutes typically to address my question. Top notch customer service!
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
There is limited amount of learning that can be completed in an in-person training available. In my opinion, the self-paced learning provided by Falcon portal is more useful over in-person training. The support from Falcon is great and useful to overcome difficulties, if any.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The training provided by Crowdstrike Falcon is complete in terms of the depth of technical knowledge and teaches the users about going through with the platform. There are lots of jargons for different tools that Crowdstrike Falcon has and this training teaches them all which helps in managing the platform better. Plus, the regular knowledge checks are also very helpful for the end user.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cb is cloud-based and has a more advanced policy management. It also has better forensics information. Cost was similar, but Cb added cost savings in terms of IT management resources. We also have the ability to talk directly with engineers and have input on feature updates.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It was just a legacy AV program onboarded during initial setup days. As the org. As it expanded, its threat landscape also grew, and we needed a next-gen solution to protect against evolving threat vectors. Falcon EDR was the one that solved all these in a single place.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
CrowdStrike Falcon's proactive threat mitigation has significantly reduced the risk of successful cyber attacks, resulting in tangible savings related to potential data breaches or system compromises.
The cloud-native architecture and automated features have improved operational efficiency.
The platform's real-time visibility and threat hunting capabilities have drastically improved incident response times.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info