FireMon is a real-time security policy management solution built for today’s complex multi-vendor, enterprise environments. Supporting the latest firewall and policy enforcement technologies spanning on-premises networks to the cloud, FireMon delivers visibility and control across the entire IT landscape to automate policy changes, meet compliance standards, to minimize policy-related risk. Since creating their policy management solution in 2004, FireMon states they've helped…
N/A
Microsoft Defender for Endpoint
Score8.8 out of 10
N/A
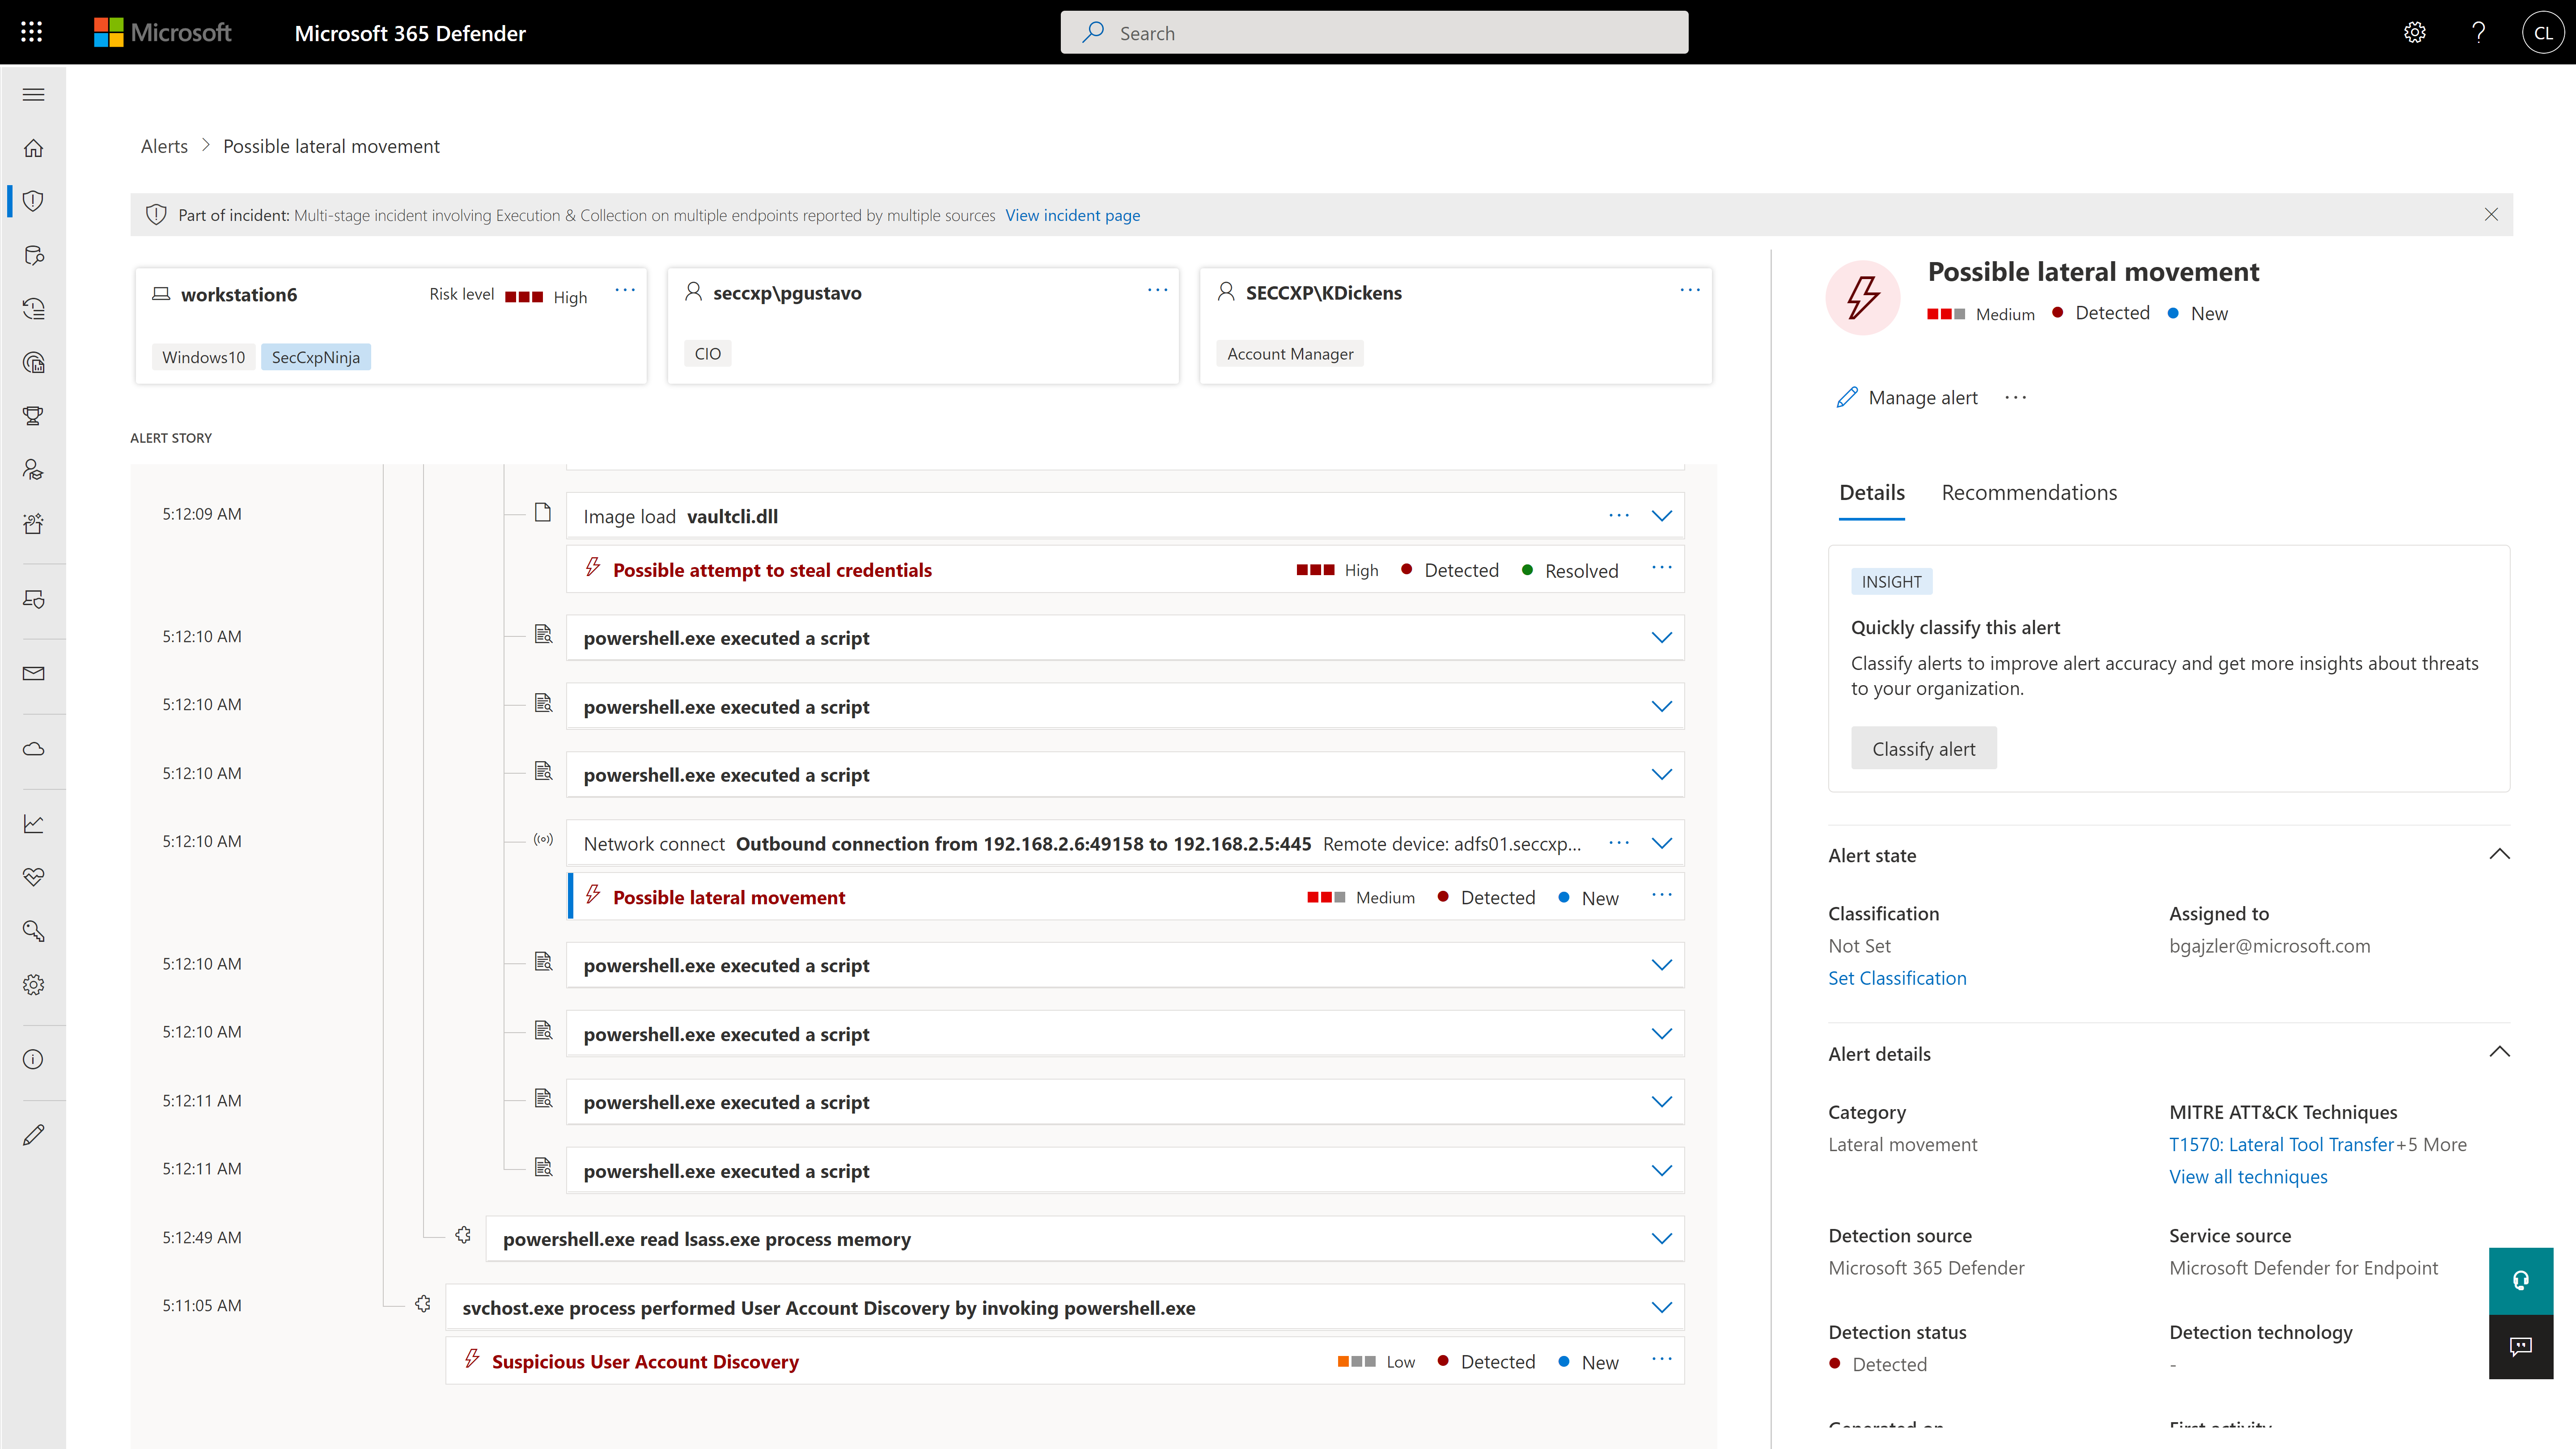
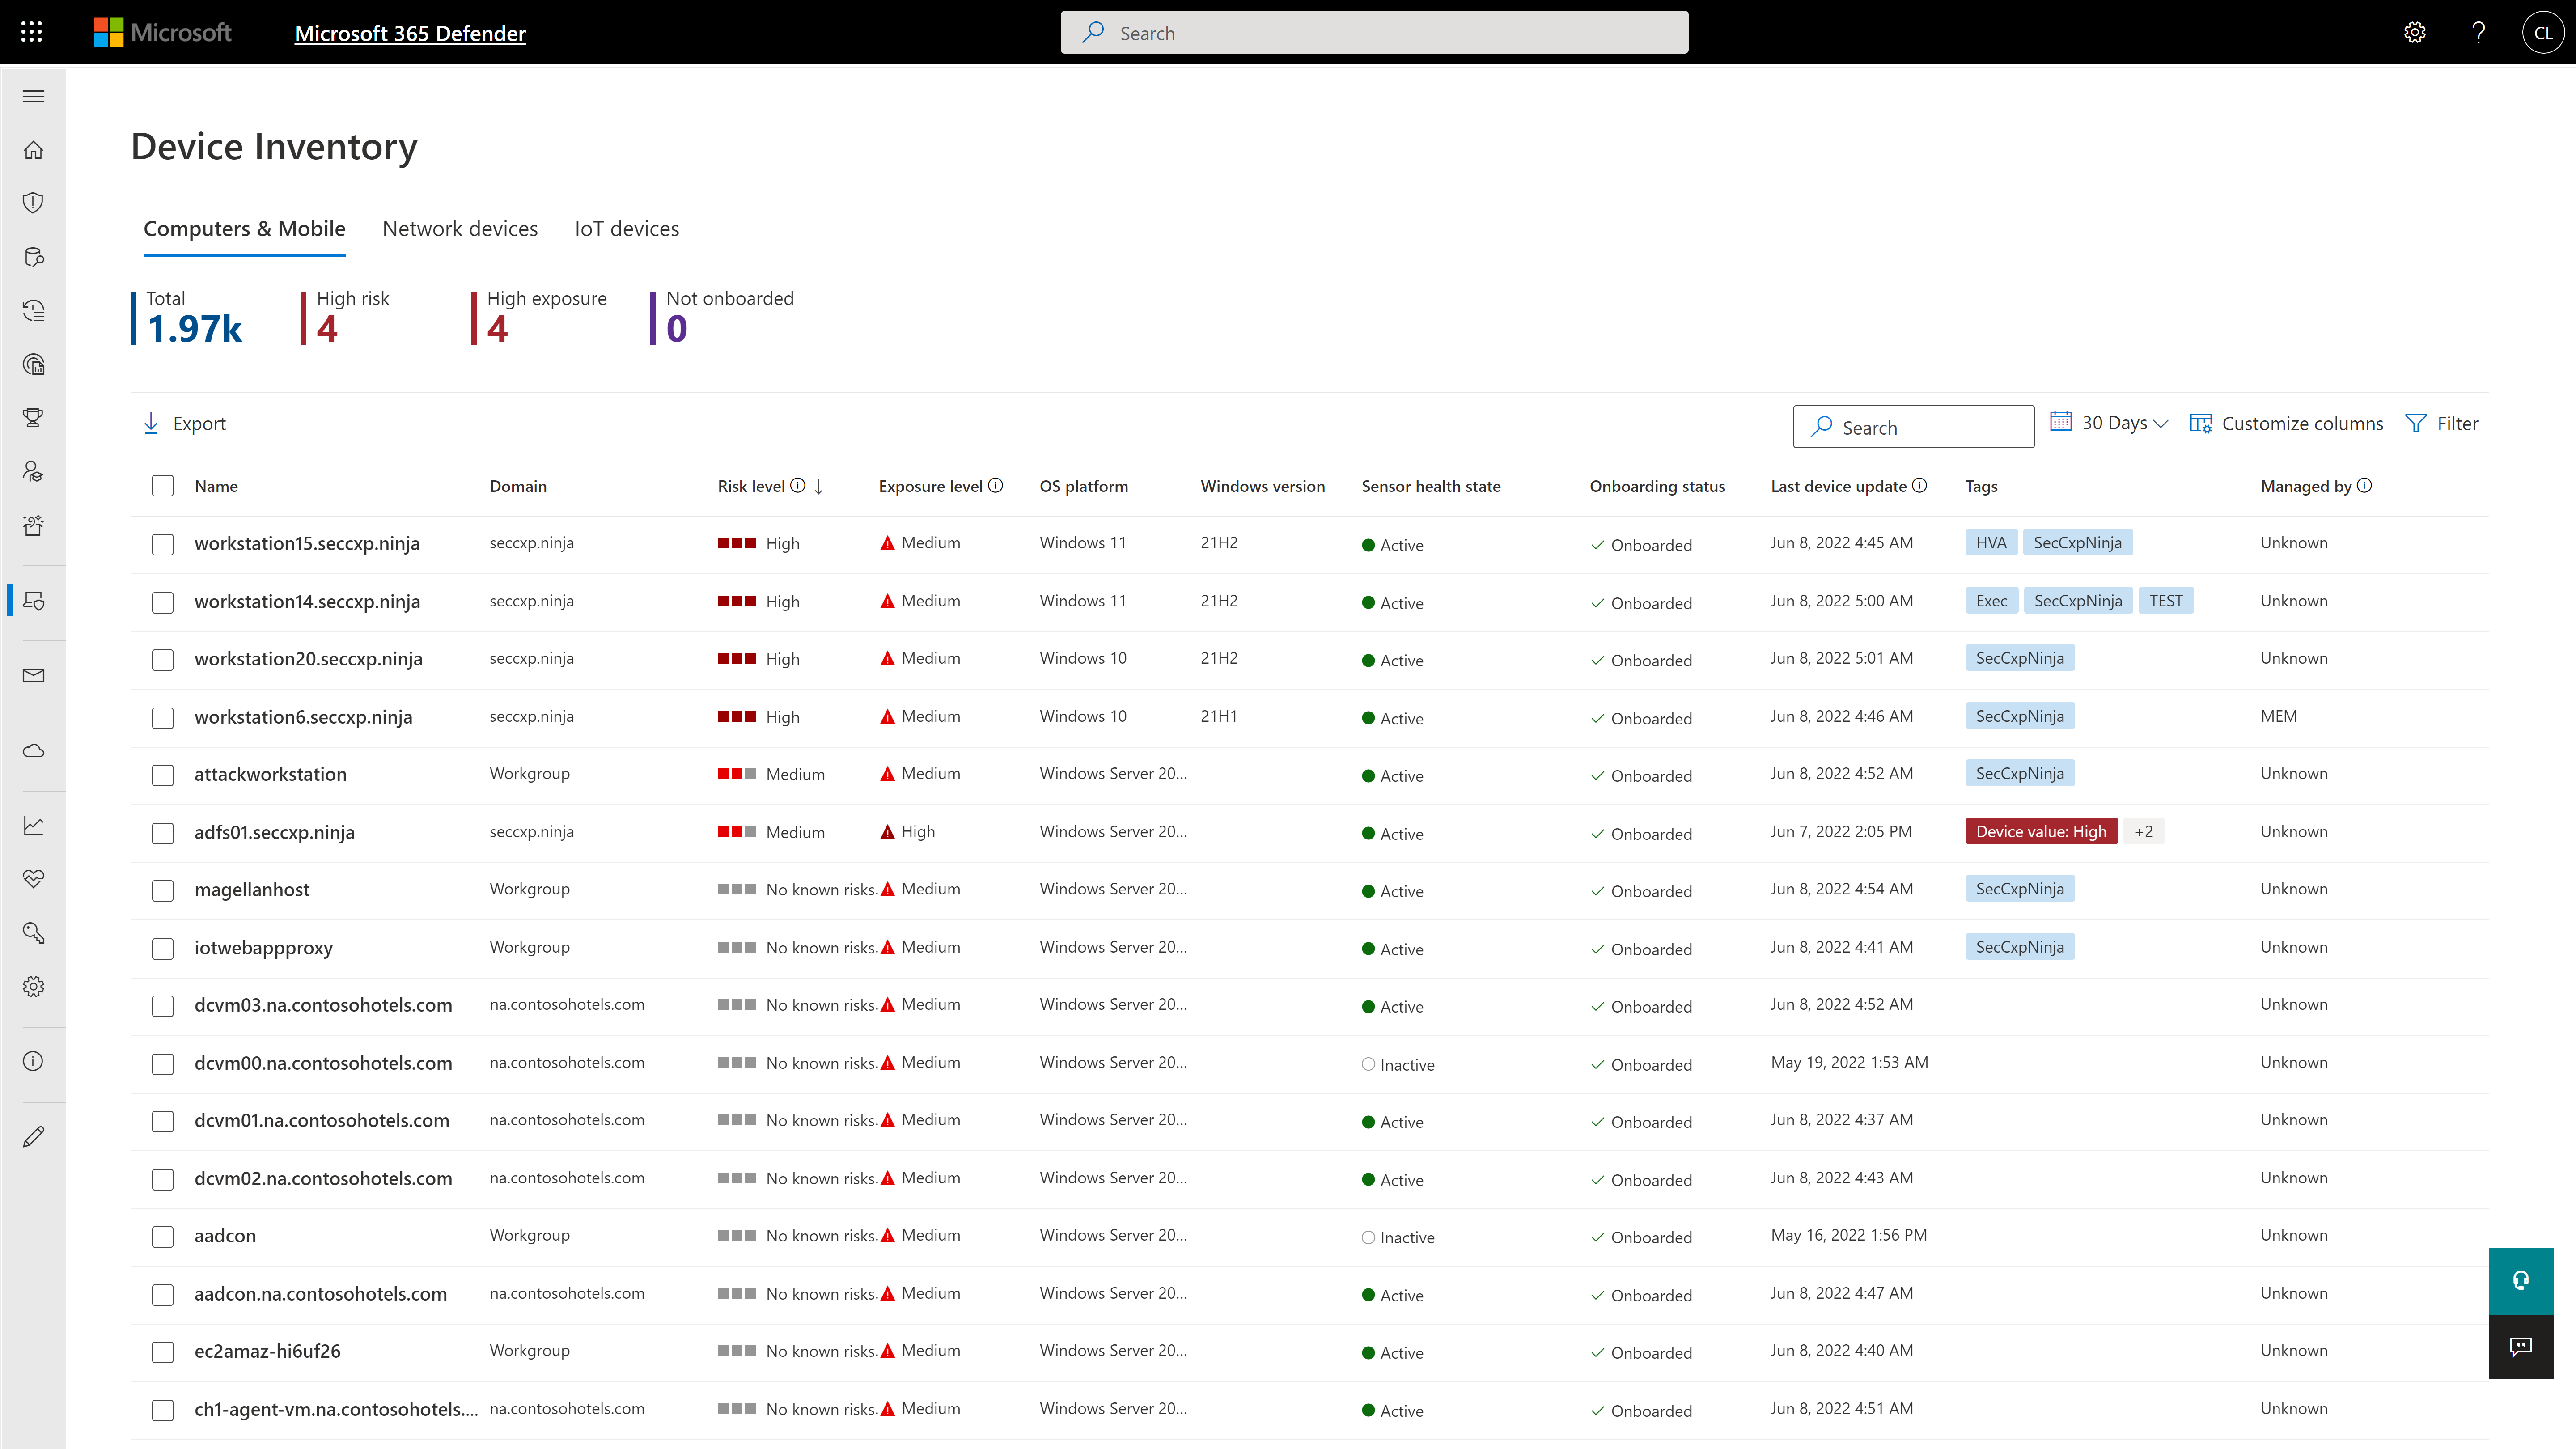
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
FireMon is best used in a large environment (for example, I have >100 firewalls in my environment). It's best used when trying to improve security posture and showing changes in firewall security over time. It might not be the best choice for smaller environments or those that aren't concerned about security management.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The shell is locked out and we can't run any general centos commands. The implementation and maintainence of the arch is very complex. Even with the right identifiers on log messages the log collection keeps failing. The warning messages on the device are ambiguous. The log messages on firemon are a bit confusing and don't show the exact issue.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
FireMon has been relatively stable overall. However, there have been a handful of times where we had issues with the console. For example, we couldn't update which devices to include in a security assessment. The initial suggestion from support was to just reboot it. It seems like there weren't many other options available such as to restart services before going to the extreme of a complete reboot.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'm not sure we have the largest implementation of FireMon out there but we do have a few 1000 devices being probed by FireMon. Overall, the system's performance has been rock solid. The console refreshes quickly and reports are generated within an expected timeframe.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
FireMon technical support is awesome! They respond quickly to our requests and they are well trained and very knowledgeable about the tool. Some issues have to be referred to the development team, but technical support largely provides solutions for any issues that we may have.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I has worked with AlgoSec and while they are very similar product, I find the FireMon is easier to understand and get rolling with. While both require some learning, FireMon is by far the easier one. Once you have an understanding of how things are arranged and labeled you can easily import firewalls and begin to work on them to improve them
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Firemon Is easily scalable and maintainable with any size team. Although it requires some tech debt, it is well worth the time to invest to ensure compliance is visible and reports are accurate. Although our environment is very large we do not fully utilize the scalability of the Firemon product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info