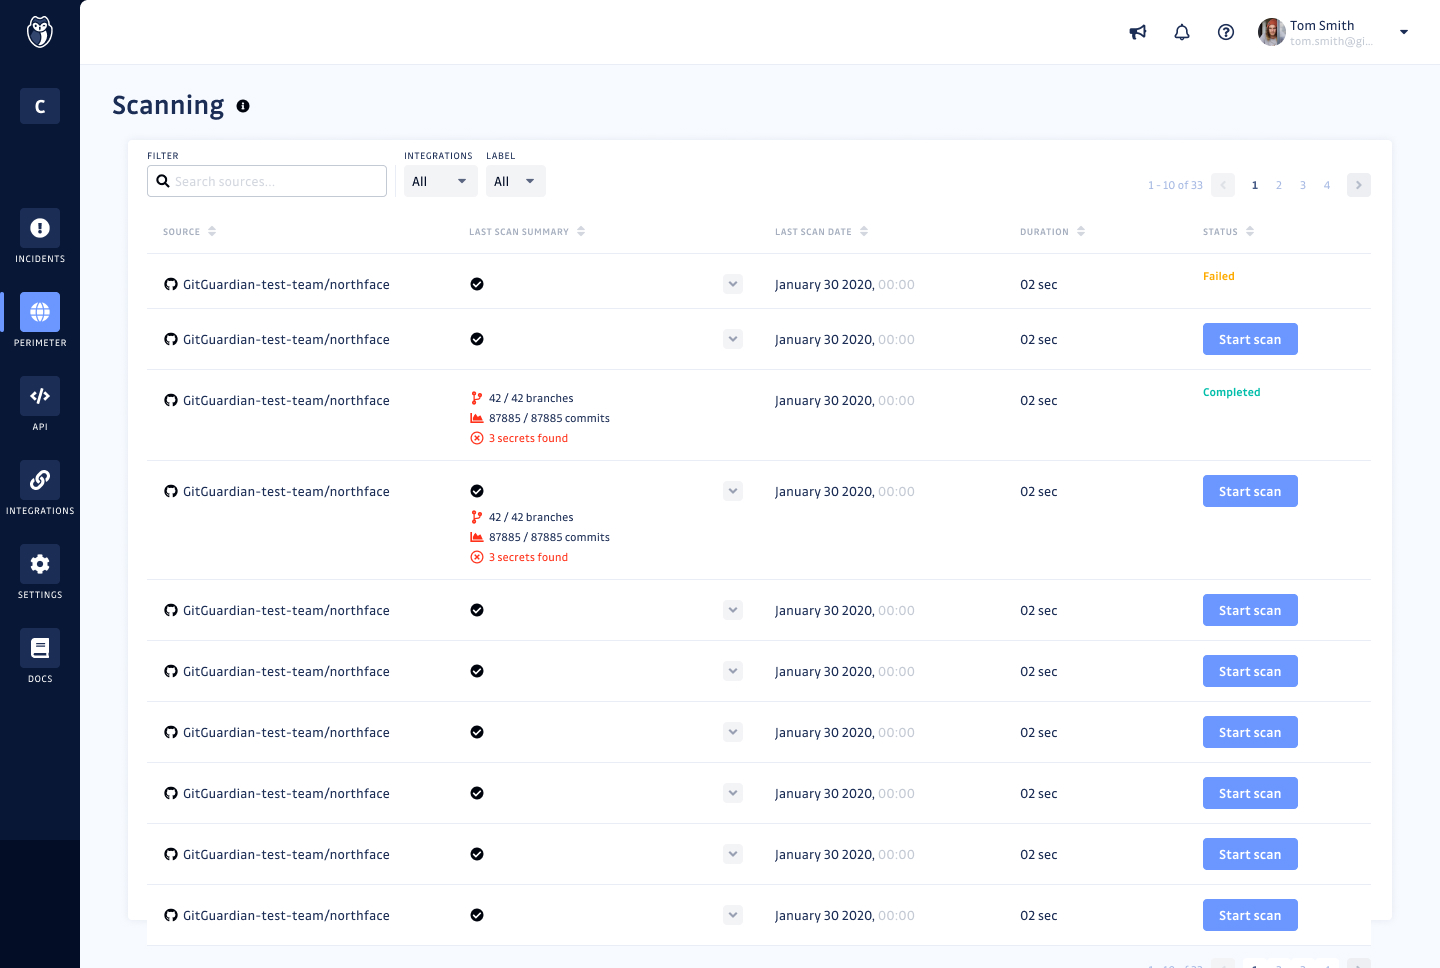
GitGuardian is an end-to-end NHI security platform designed to help organizations strengthen their Non-Human Identity (NHI) security posture and address compliance standards and regulations. As attackers increasingly target NHIs, such as service accounts, service principals, and applications, protecting and managing these critical assets has become paramount. NHIs rely on “secrets” like API keys and certificates for authentication, and their rapid proliferation has led to significant…
$0
(for individuals or up to 25 devs)
SailPoint Identity Security Cloud
Score8.1 out of 10
N/A
SailPoint Identity Security for the cloud enterprise manages risk from the explosion of technology access. The solution gives businesses visibility while automating and accelerating the management of all user identities, entitlements, systems, data and cloud services.
I do think it'll absolutely fit everyone who codes integrates with another platform or services. We all forget that one credentials one in a while, and especially those who managed public repository, it is important to keep an eye on accidentally committed credentials. While I think you don't really needs it for personal project, it's a nice to have, you don't want to waie up to 50k USD of sudden surcharge on resources you don't use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
As discussed in previous sections, it does integrate well with other systems, and basic JML works well; it's very powerful and customizable in these areas (though also complex). The downsides are in areas like access reviews, where it's less customizable (no way to automatically send a review to the owner for a set of access items; each review needs an individual to be selected for it).
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
GitGuardian monitors every public or private GitHub commit ( that have GitGuardian installed) and event in real-time for secrets and sensitive data. In a leak scenario it immediately notifies us.
It uses sophisticated pattern matching techniques to detect credentials that cannot be strictly defined with a distinctive pattern (like unprefixed credentials)
It covers several API providers, database connection strings, private keys, certificates, usernames and passwords etc
GitGuardian have high True Positive Rate of around 91% and reduces alert fatigue with smart occurrences regrouping
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Improved user interface: It would be beneficial to have a more intuitive and user-friendly interface for Internal Monitoring on GitGuardian. This would make it easier for users to quickly access the data they need and understand the results of their scans.
Automated alerts: It would be helpful to have automated alerts when certain conditions are met, such as when a scan reveals sensitive data or when a new repository is created. This would help users stay informed and take action in a timely manner.
More detailed reports: Currently, Internal Monitoring reports are limited in terms of the depth of information they provide. It would be useful to have more detailed reports that include additional metrics, such as the number of repositories scanned and the types of sensitive data found.
Faster scan times: Scan times can be slow at times, making it difficult to stay on top of changes in repositories quickly. It would be beneficial to have faster scan times so that users can take action quickly when needed.
The user interface is not very intuitive. It is hard for the occasional user to navigate through the request process. There are no instructions on the screen to help the user to know what to do. It is left up to the user to figure out what to click on and how to navigate through the process.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Its a best tool for a CISO, works very well, easy to use, great connectors and integrations, great reports, automated reviews, full compliance, great support to a JML (Joiners, Movers and Leavers) project;
Always improving the UI, so it's getting better. Some areas are fully featured, but others, such as Separation of Duties reporting and policies, are very weak.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first journey isn't easy because you need to win your internal process and problem concern and Sailpoint have many experience to support this phase, and make the real difference into the client experience;
I've evaluated quite a few other tools, like git-secrets, Git-leaks, scan, and maybe a few more. They're all great but quite surprisingly none of them detected Github OAuth Secrets for us. A lot of the FOSS tools out there focus on much simpler, generic secrets, which is good in itself but with GitGuardian, it was dead simple from day one. I just connected our Github Account and set up the gg-shield cli and that was all.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The on-prem SailPoint IdentityIQ platform provides the necessary customization that is required in our dynamic environment. Although we may look at a cloud-based Identity Management service again in the future, (there are many advantages), our identity management, authentication, and application assignment processes cannot be quickly consolidated to a single cloud-based service at this time.
GitGuardian Internal Monitoring has had a positive impact on our overall business objectives. By providing visibility into our code repositories and alerting us to potential security risks, we have been able to identify and mitigate security issues before they become a problem. This has allowed us to focus more on developing our product and less on responding to security incidents. We have also seen an increase in customer confidence in our product as a result of using GitGuardian Internal Monitoring, which has led to increased customer loyalty and retention. Overall, the ROI of using GitGuardian Internal Monitoring has been very positive for our business.
We have seen an increase in the security of our codebase, as well as an improvement in the speed and accuracy of our code reviews. This has enabled us to quickly identify and address any potential security issues before they become a problem. Additionally, we have seen an increase in our ROI as a result of using GitGuardian Internal Monitoring, as it has allowed us to save time and money by preventing costly security breaches.
Over 300,000 password change/reset calls avoided to the helpdesk annually.
1,000 plus accounts with proper accesses provisioned via automated birthright processes weekly versus 1-2 days of manual provisioning and approvals. With a call center population that churns many people per week, this brings many dollars of efficiency to the operations teams.
Flexibility on terminations to manage accounts and access for target applications based on regulatory or business rules to ensure compliance and avoid fines for non-compliance.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info