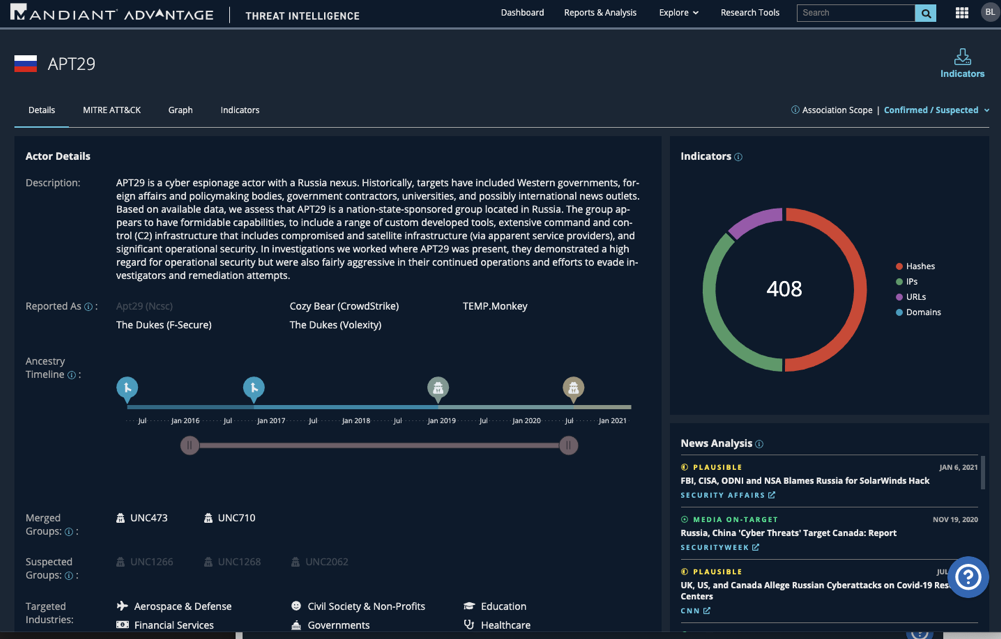
Google Threat Intelligence, based on the expertise and service of Mandiant, aims to accelerate security and risk decision making – operational as well as strategic – and to enable security teams to focus on threats that matter to them.
N/A
Huntress
Score9.5 out of 10
N/A
Huntress is a security platform that surfaces hidden threats, vulnerabilities, and exploits.
The platform helps IT resellers protect their customers from persistent footholds, ransomware and other attacks.
Usually SOC leverages Intel from mutiple sources. The scenarios are: 1.Suitable: In large scale SOC where more than 5000 devices are being monitored and the tech stack is wide, Mandiant will play an excellent role in that scenario. 2.Not Suitable: In small scale SOCs wherein limited devices belonging to the same tech stack is being used then the analysts can rely on OSINT and it is not useful to buy the solution.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Huntress is great for a managed service provider to provide a better cybersecurity stack to their endpoints/customers. Some smaller clients cannot afford high-priced SOC services but require SOC-level protection. Along with a couple of other layers of security, Huntress provides peace of mind for the MSP that if a threat were to arise, they would be notified with specific instructions for dealing with that threat.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Using the latest industry knowledge of threats that have been ongoing, but not previously known and projecting it back in time against their installed endpoints to identify machines that are vulnerable or breached and when it these events occurred
Very quiet. If they alert, it is a thing.
Very good at remediation.
They communicate extremely well when it matters.
While there are the most extensive products more often than not they are the first to alert us to a threat.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Mandiant Advantage Threat Intelligence has a very usable platform, with well-differentiated sections for the analyst, as well as the possibility of cross-searching to obtain the desired results. All this is presented with an interface that is easy on the eye and not very messy, which increases productivity and the speed with which work is done.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We dropped SentinelOne in favor of Huntress because the UI was much more simplistic for the tier 1 techs to maintain. It beats the old web design model of three clicks to where you want to go. It is very intuitive. No one needs training to figure out how to navigate its console.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It gives more ways to analyze threats and options to fixed it. This device gives more visibility on vulnerability detection and its analysis. It provides detailed reports to have more information of all malwares which help us to increase overall security of our current organization
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Firstly from a business model, [VMware] Carbon Black [Cloud Managed Detection] was not outfitted for the MSP where Huntress is very MSP-friendly from an affordably easy point to entry to value for money licensing. Carbon Black TS is not bad in anyway, well, that we found, but Huntress is a new layer of security that fits between the OS and AV layers to provide additional information, monitoring, and detection. With Huntress backing the MSP, [it] sure does help as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info