Huntress is a security platform that surfaces hidden threats, vulnerabilities, and exploits.
The platform helps IT resellers protect their customers from persistent footholds, ransomware and other attacks.
N/A
Microsoft Defender for Endpoint
Score8.9 out of 10
N/A
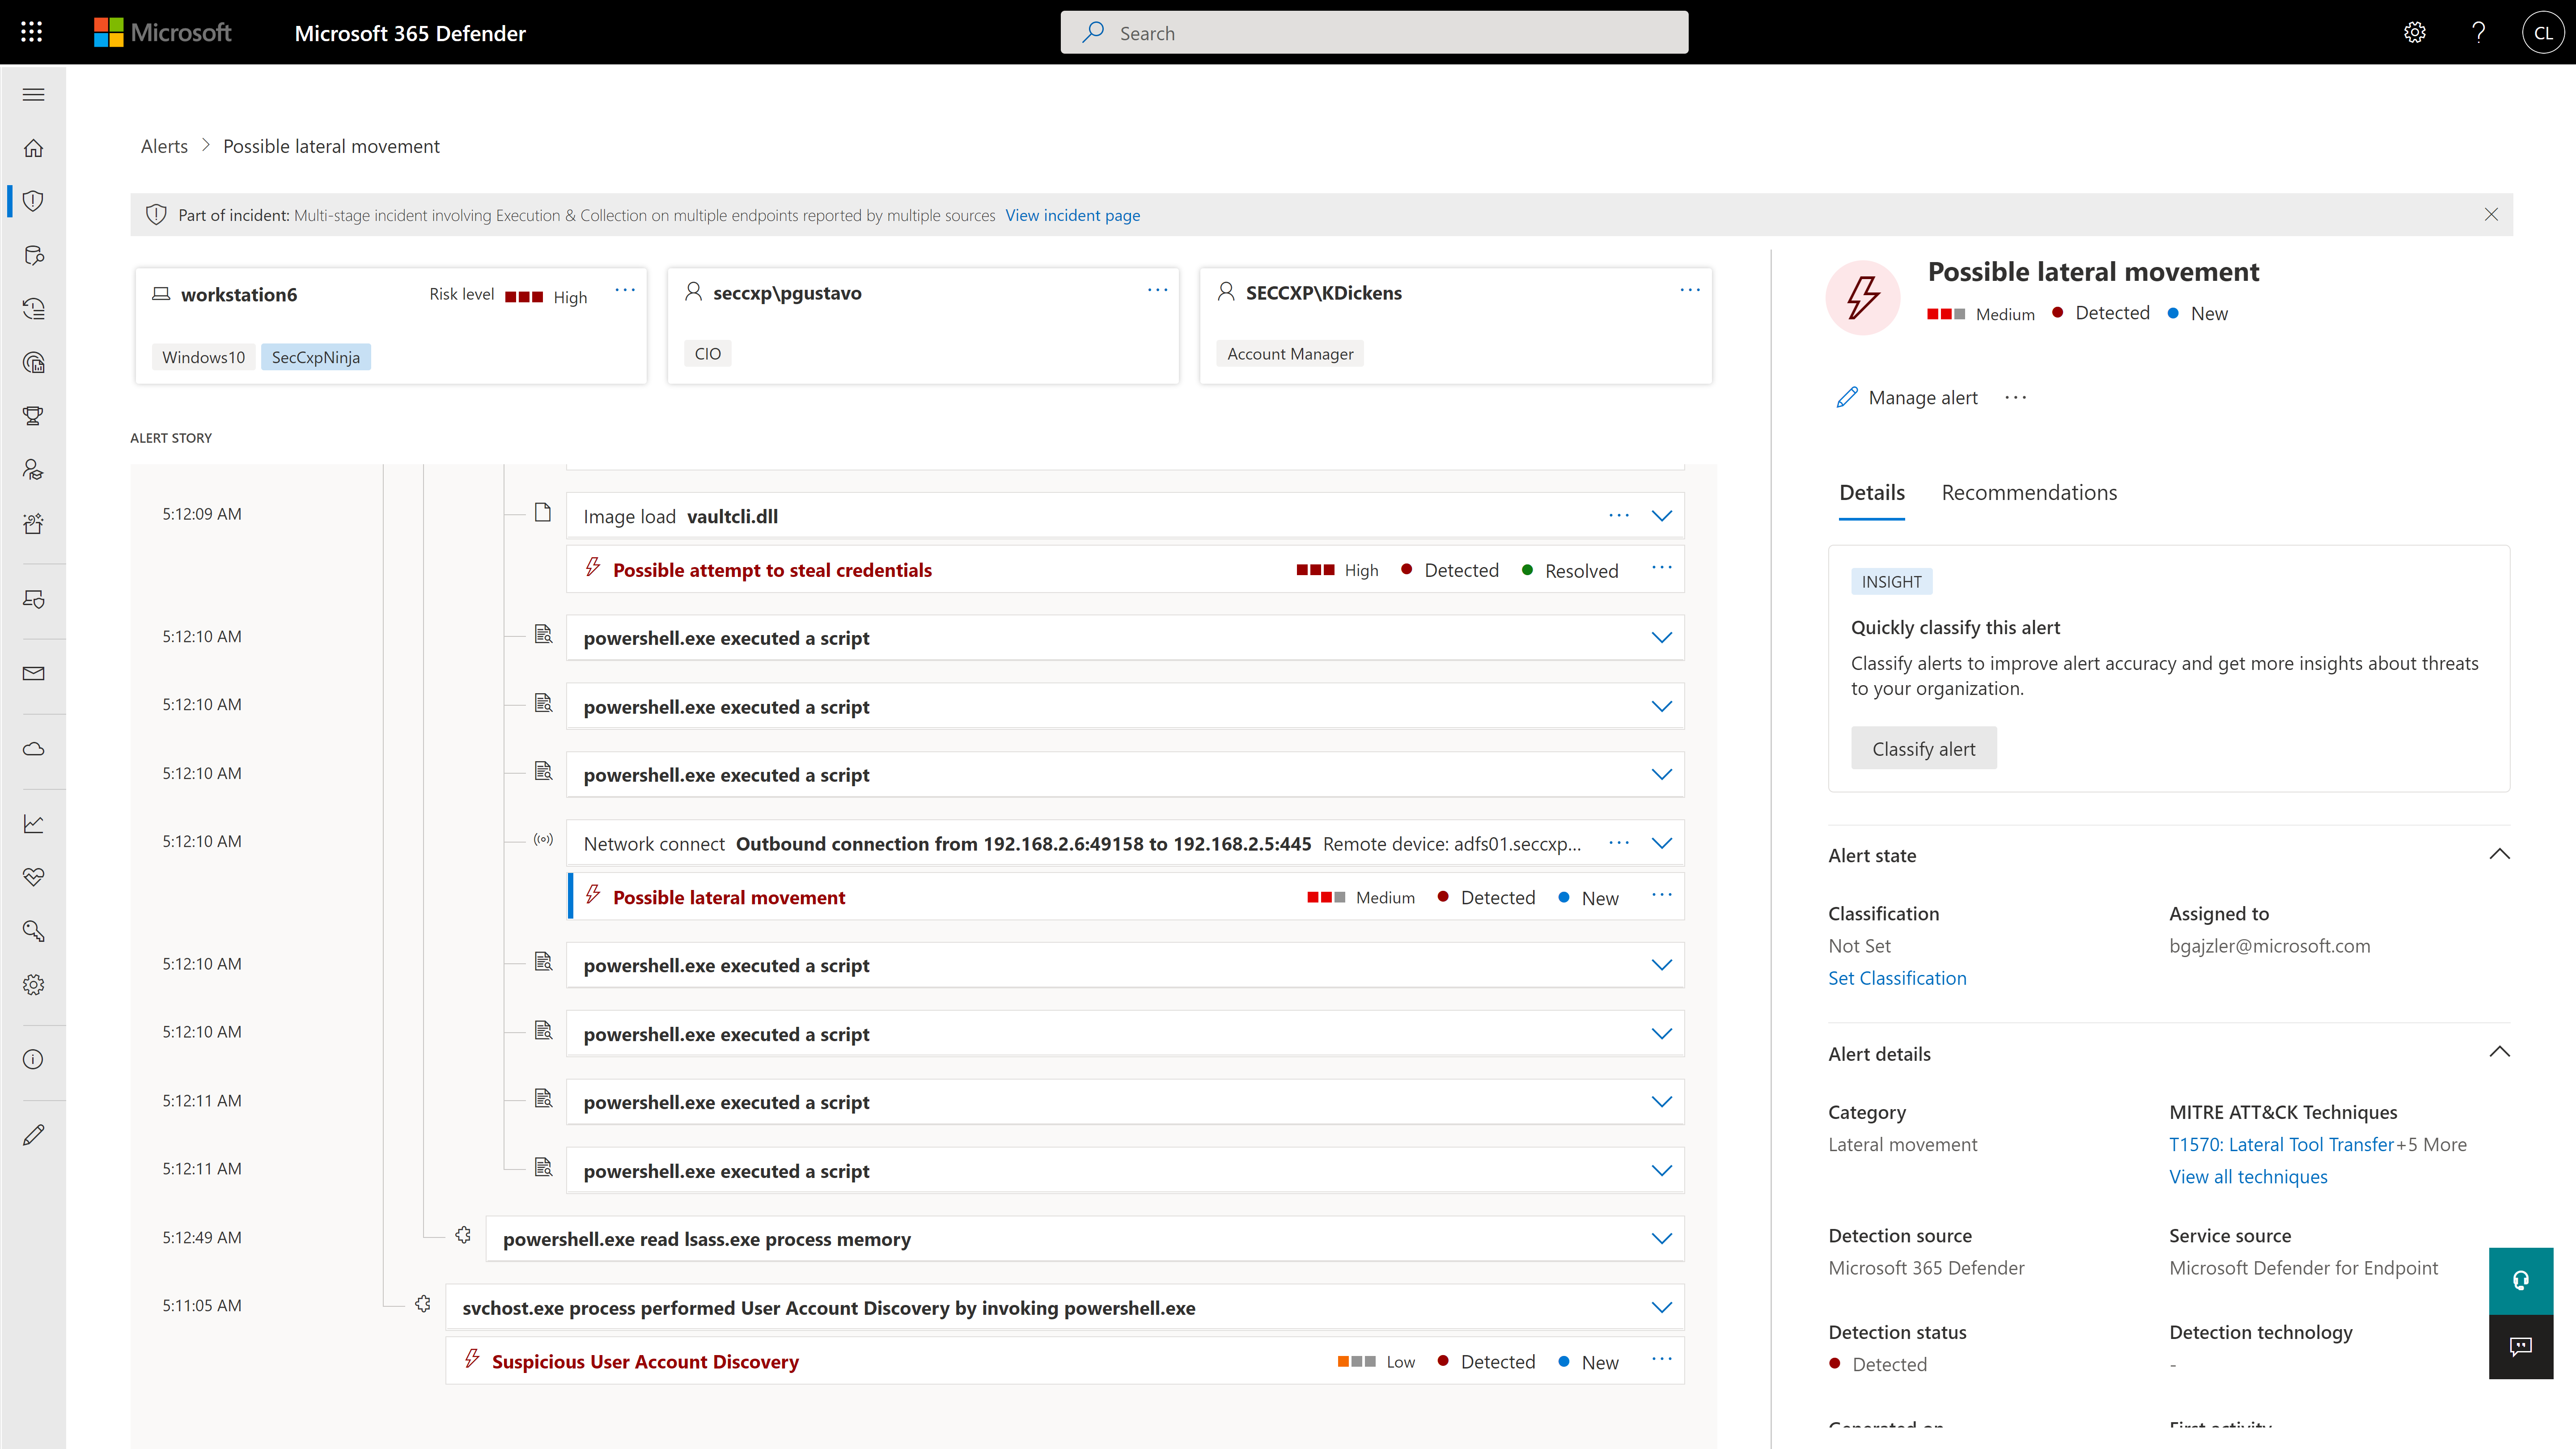
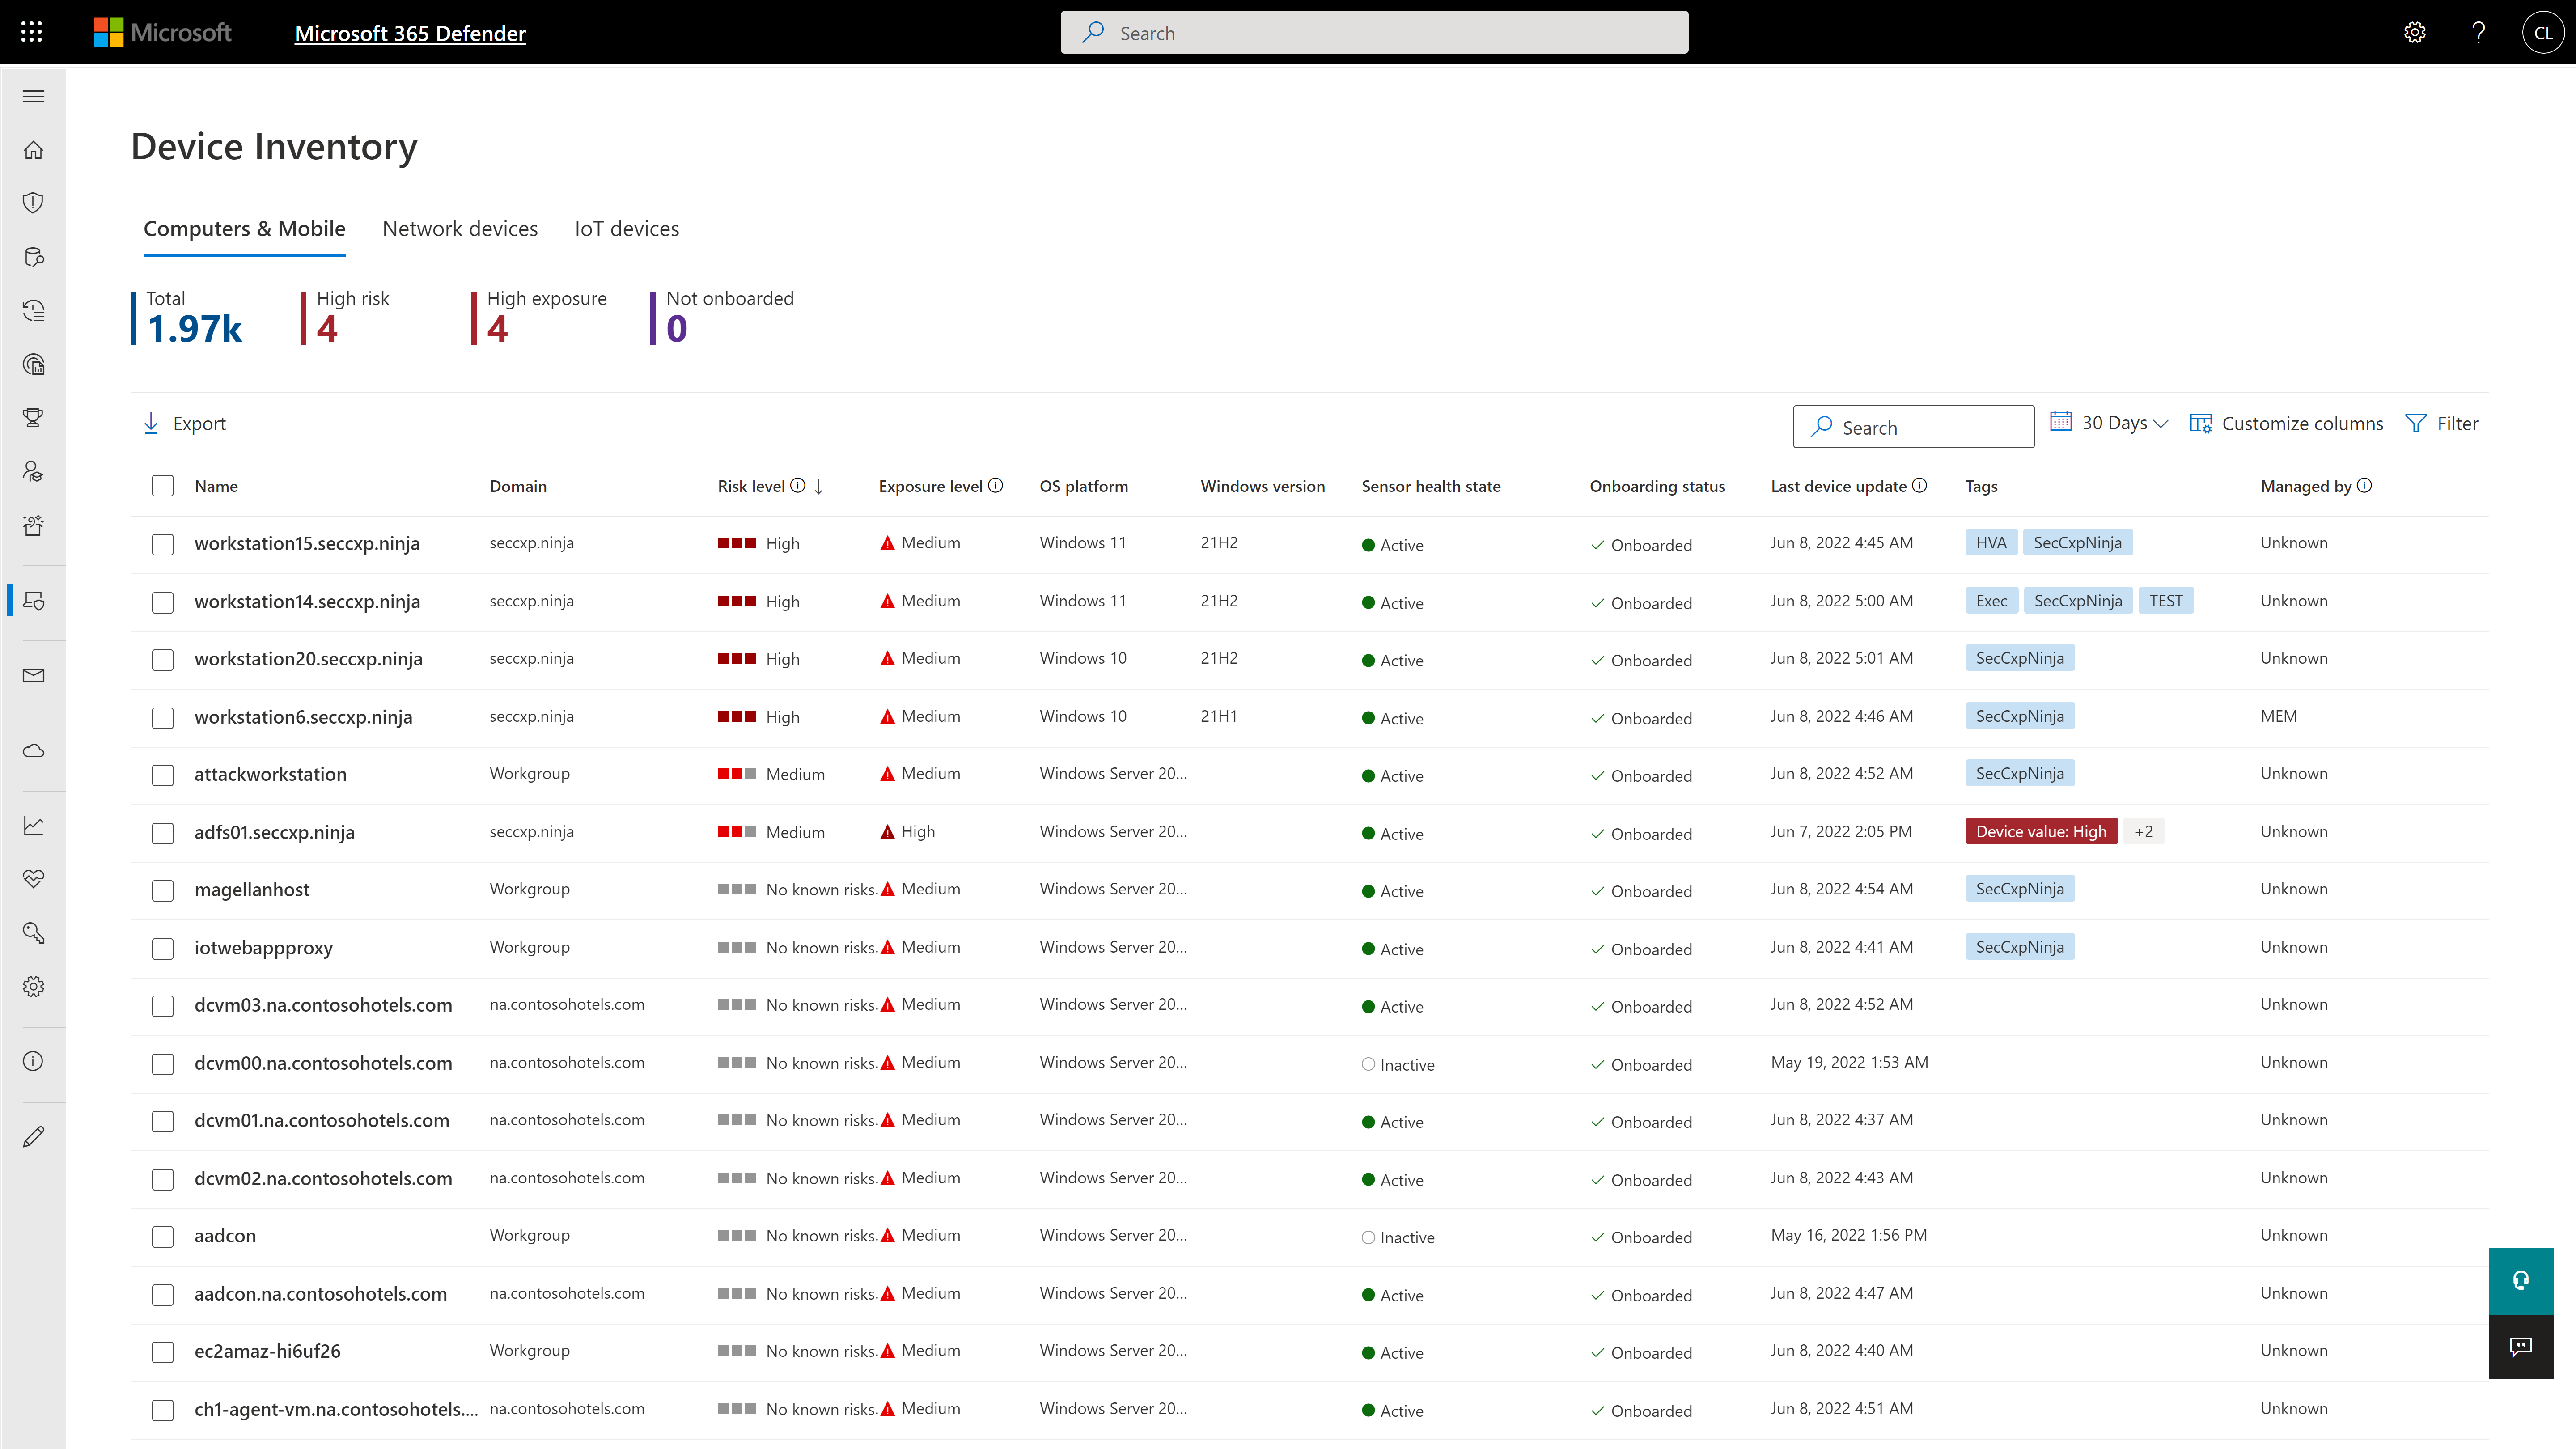
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
In my opinion, Microsoft Defender for Endpoint is inferior to the competition. Combined with Huntress it is good (they are designed to integrate), but in my opinion, no need to use the paid version of Microsoft Defender for Endpoint when combining with Huntress, so not really …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
SentinelOne, Hunters. There's been some other ones. I can't remember. Those are the most recent ones, though. CrowdStrike is the other one. For what I use it for right now, it's been fine. I haven't had anything I've needed more advanced than that. CrowdStrike and some of …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
NetSuite Administrator in Information Technology at Powertex Group (Marketing & Advertising, 51-200 employees)
Chose Microsoft Defender for Endpoint
We choose Microsoft Defender for Endpoint as an additional solution to fill gaps and also to keep more of our solutions under one pane of glass (Microsoft 365).
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Their managed endpoint platforms wouldn't be suitable for a company that hasn't received investment or has any employees just yet, because the platform is designed to manage company device endpoints for businesses with multiple users across enterprise software and mobile work devices such as laptops, tablets, or phones. If you are building a startup and you need educational guidance on how to protect yourself from scams either before or during your investment phase, then the security awareness training sessions are key for SME's that are pre-investment, and the product lab sessions are highly technical deep dives on the platform's capabilities, and these are also mixed in with a bit of craic and interaction from the podcast hosts too, which helps to keep the sessions engaging.
I think for your average user's experience, it's perfectly fine. I think when you're dealing with more advanced people within the cybersecurity space, where they may deal with applications or tooling, other situations like that, or malicious-type files, that might be problematic for them to use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Using the latest industry knowledge of threats that have been ongoing, but not previously known and projecting it back in time against their installed endpoints to identify machines that are vulnerable or breached and when it these events occurred
Very quiet. If they alert, it is a thing.
Very good at remediation.
They communicate extremely well when it matters.
While there are the most extensive products more often than not they are the first to alert us to a threat.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We dropped SentinelOne in favor of Huntress because the UI was much more simplistic for the tier 1 techs to maintain. It beats the old web design model of three clicks to where you want to go. It is very intuitive. No one needs training to figure out how to navigate its console.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It just works. It's easy. I mean, even if you didn't have much background in it, you could figure out what you need to do to get the information that you need. The dashboards are comprehensive. The information that it aggregates on the screen, your first initial screen, is very comprehensive and telling. So, usability.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Huntress may not be a complete SOC such as Blackpoint, but the level of protection is close. Huntress provides a set of human eyes always hunting for persistent threats on your endpoints. Huntress also seems less noisy with no false positives, so no time is wasted reviewing alerts.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Falcon. I will say this: Falcon was way easier to deploy. We deployed 36,000 endpoints in about 40 hours. It took us two years to get Microsoft Defender for Endpoint deployed. So deployment was a pain. Falcon, what else we've got? Trellix or McAfee Endpoint. And that's about it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info