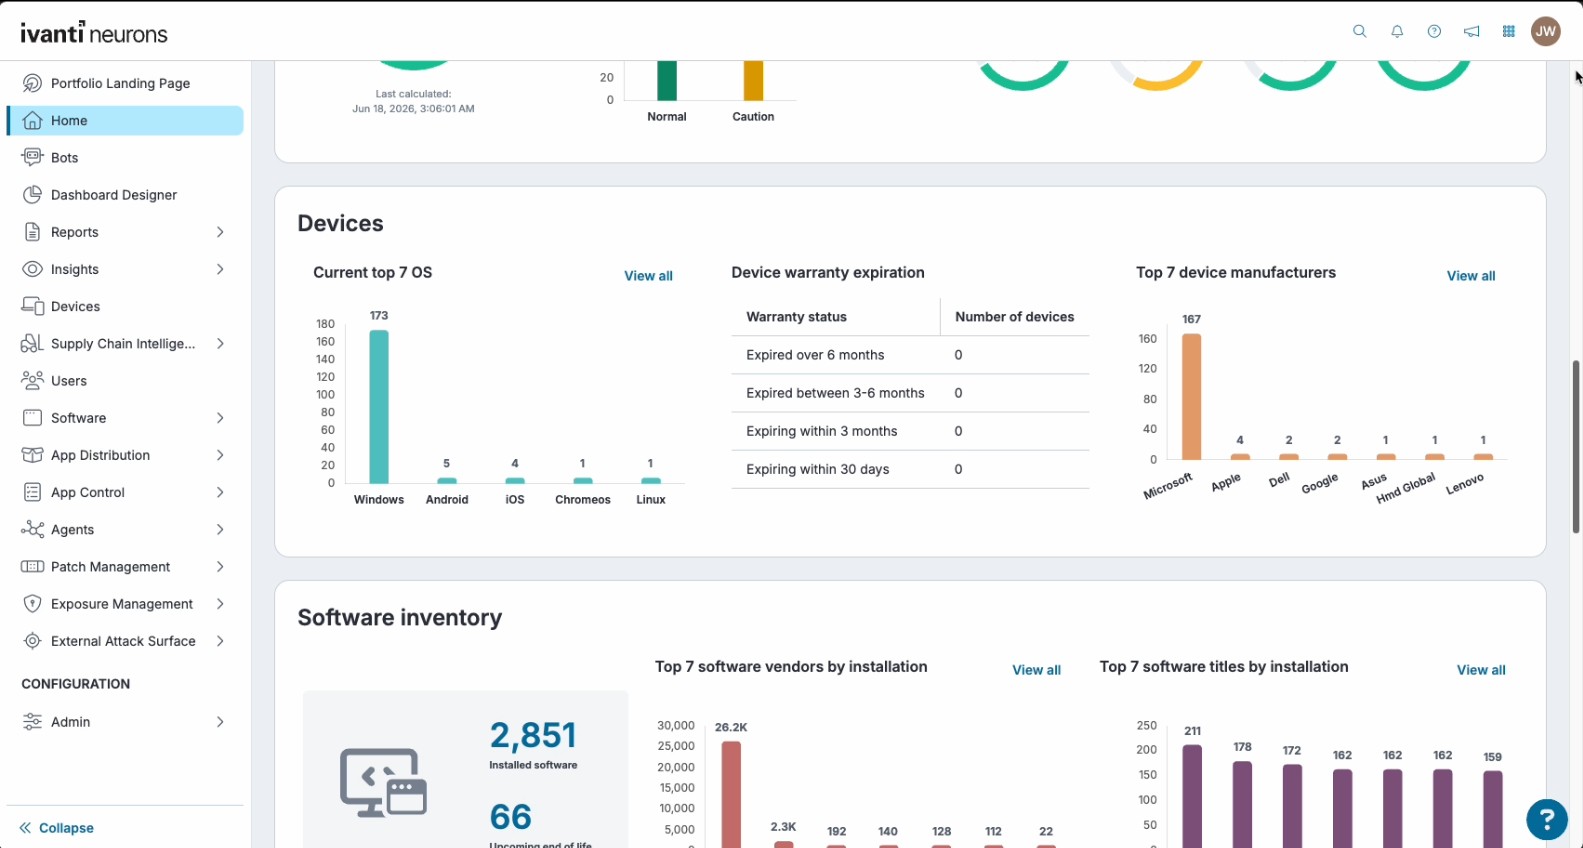
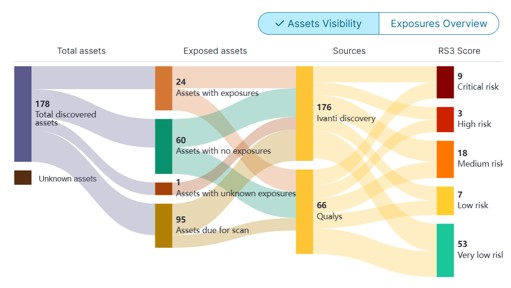
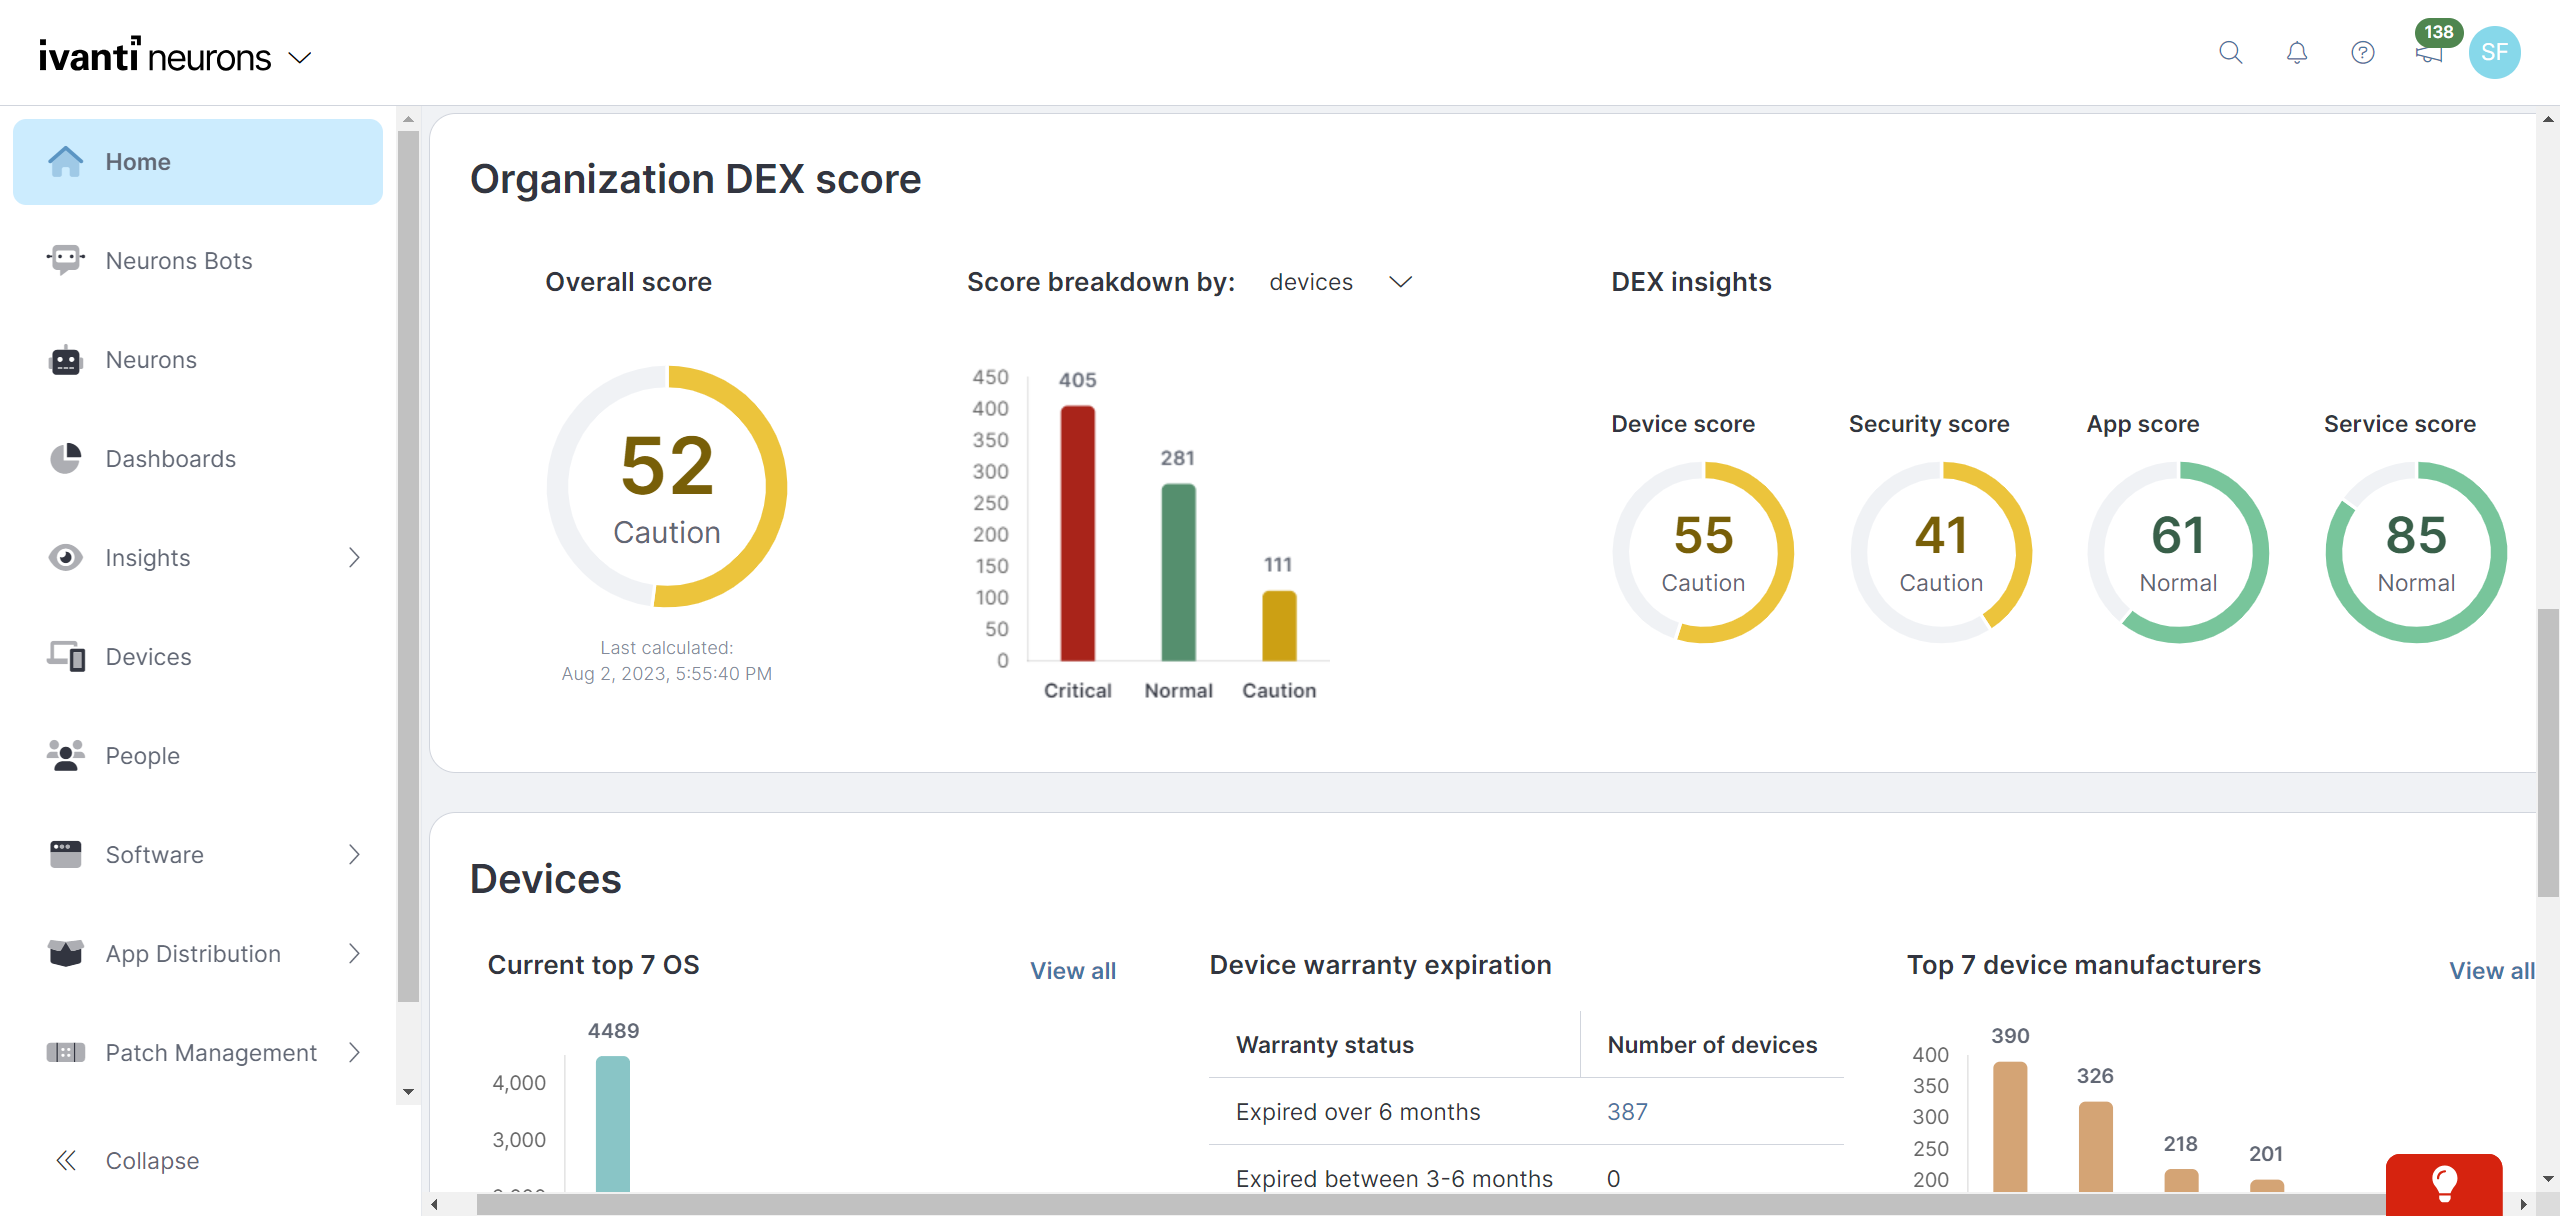
Ivanti Autonomous Endpoint Management (AEM) is an enterprise endpoint-operations solution built on the Ivanti Neurons platform. It combines unified endpoint management (UEM)—centralized management of desktops, mobile devices, and other endpoints—with digital employee experience monitoring, asset discovery, security controls, and automated remediation. Ivanti positions AEM as a broader solution layer that brings UEM, digital employee experience, and security capabilities together rather than as a…
N/A
Microsoft Defender for Cloud Apps
Score7.8 out of 10
N/A
Microsoft Defender for Cloud Apps (formerly Microsoft Cloud App Security) is a multimode cloud access security broker.
I think that Ivanti Autonomous Endpoint Management can be well suited to most scenarios for patch management. The different options with Ring Deployments allow for rolling out patches in any number of circumstances. Typical monthly, weekly, daily, zero day response, etc. There is some lack of control over how to wrap up a deployment. What I mean is that in a scenario where we need extremely controlled rollouts, some of the features do not align well. For our organization, we would ideally evaluate patches that come out each Patch Tuesday. Select those patches for deployment, deploy those to our test servers over 3 days, wait 2 days, then deploy to production for 3 days. While we have plenty of control over the initial deployment, we have no clean way to say "after these 3 days, no longer deploy the patch". In our specific scenario, we sacrifice process to align with the tool's capabilities.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Microsoft Defender for Cloud Apps is well suited when working with other Microsoft Applications. For example, if you are working with Microsoft Office 365 it works very well when implementing CASB features. It works when implementing monitoring or blocks on Sanctioned applications however customizing the message to users is not that great.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Ivanti Autonomous Endpoint Management is light weight and easy to install
Ivanti Autonomous Endpoint Management allows the user to defer a required restart. Allowing them to restart their machine at a time that's more convenient for them.
Comparatively, Ivanti Autonomous Endpoint Management is a budget friendly solution.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The integration to Microsoft Entra ID is seamless, which allows Conditional Access to redirect the session to Microsoft Defender for Cloud App for it to take actions (Block or Monitor).
Tracker users' activity is very good when troubleshooting or running an investigate.
Detecting risky users through tight integration with Microsoft Entra ID is a very good feature.
Detecting mass downloads and blocking the download of files from non-manage company devices is a very good feature as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
MDM has fallen a bit flat, however, with the recent acquisition of MobileIron I believe this will change but as of now there is some of this still built into the product
The antivirus portion of the product hasn't had much love and could use a bump. It is not bad at all but I would like to see it hit that next level.
Data Analytics is the most powerful tool inside this platform but it is so hard for people to figure it out that it often goes unused. It needs a good redesign.
It takes some time to scan and apply the policies when there is some sensitive information.
After it applies the policies, it works, but there is a delay.
It doesn't provide any way to scan Microsoft Teams when an external exchange of images is happening. You can always do the filtering on the documents during the chat, but if there is an image, then some kind of OCR capability is required to detect it. At present, there is no way [Microsoft Cloud App Security] can go and detect those kinds of images and alert us
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
MobileIron is a constantly evolving platform that stays current with industry trends. iOS updates? No problem, they're supported almost immediately after a new iOS version comes out. If you are a Core (on-prem) customer there is ample support and assistance to migrate to the Cloud version of MobileIron (although I've yet to convince my department head to approve the request). The platform is very robust and extremely configurable. Management roles can be delegated effectively to other staff without compromising security. These in alone are important, but even more important is the company itself - they are great to work with, from support to sales. We have never had a situation where MobileIron left us on our own, and many times support has gone way beyond what is simply required in order to educate us or extend the usefulness of the product
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Importing devices and setting up patch deployment was very simple. The real star here is the automation built into Neurons though. Neurons is able to set up custom Bots commands which can automate troublesome servers which have custom start up and shut down commands that must be followed. User and SAML setup was also incredibly easy
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The interface is pretty simple and easy to use; however, you will need to do a lot of investigative research on your own to get comfortable with it. Originally, many of the Microsoft security tools had their own seperate consoles. Overtime, they have blended into one interface which is the ideal state. In some cases it is clear Microsoft had to pick which console a certain feature or setting was going to reside in and this leads to some confusion. For example, DLP is managed through Defender for Cloud Apps but you will also need to jump into Purview. For things like reverse proxy on your M365 tenant, you will need to go into Azure and setup conditional access rules. Not a big problem and I can understand why the settings are located where they are but for someone just starting out with Defender for Cloud Apps, it will take some time to figure out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
TRM\TAM support has been generally very good. Getting reported bug fixes, design changes, UX problems resolved has been a pain. It is often difficult to get problems escalated beyond the TRM\TAM level. Support is fantastic when you can get it, getting it can often require more work than it should, and that is probably our biggest issue.
I have not utilized actual support but the Sales and Product teams have been super helpful in moving our implementation forward and showing us the best practices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
it was clear and understandable for me which is why i have a good hang of it the training material is also great which was provided by them. The help community and documentation is also great. all the questions were clearly answered and the person for clear and patient with it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is online based, after learning content you can take a test and if you don't pass you get two other chances to pass. Once you pass the test you can print out your certification or save it
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Better in most all categories. On-prem was not an issue for my organization. MS SCCM was lacking features. Airwatch required increasing tiers of service in order to match [Ivanti Unified Endpoint Manager (formerly LANDESK Management Suite)] features, and lacked the robust inventory data we needed. Meraki was very simple to use, but did not meet our needs. I would say that most Airwatch customers aren't using all the features they are paying for, and could save lots of money by using Meraki instead.
More flexible and more features with easy integration with cloud services like Microsoft Azure and other cloud services. Overall both gives similar features but we prefer Microsoft cloud app security due to its high threat detection rate. mostly we have been able to stop the threat in very very less time.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The installation of MobileIron was for security compliance so we could containerize email on BYOD devices and also control who got email on company phones (to prevent hourly workers from working on emails after hours). MobileIron met this need nicely.
MobileIron allowed us to utilize device certificates to prevent unauthorized devices from joining wireless networks in our company.
MobileIron allows our sales staff to get emails on the road and many users rely on the functionality and ease of the phone for general mail communication.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cloud App Security saves us thousands of dollars finding and rectifying apps security issues
Identity Security Posture helps the organization identity stay in shape, saving thousands of dollars on security consultations
The cost of suffering a breach cannot be quantified, CAS helps minimize the chances of the attackers succeeding, with excellent historical logging for most operations
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info