TrustRadius: an HG Insights company

SolarWinds Kiwi Syslog Server vs. Splunk Observability Cloud

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    SolarWinds Kiwi Syslog Server

    Score8.1 out of 10
    N/ASolarwinds® Kiwi Syslog® Server is a syslog management tool for network and systems engineers. It receives syslog messages and SNMP traps from network devices (routers, switches, firewalls, etc.), and Linux®/Unix® hosts. Users can filter and view these messages based on time, hostname, severity, etc., and set up custom alerts. Kiwi Syslog Server has built-in actions to react appropriately to syslog messages. There are also log archival and clean-up features to help comply with security policies.

    $319

    Per Instance

    Splunk Observability Cloud

    Score8.5 out of 10
    N/ASplunk Observability Cloud aims to enable operational agility and better customer experience through real-time AI-driven streaming analytics allowing accurate alerts in seconds. It is designed to shorten MTTD and MTTR by providing real-time visibility into cloud infrastructure and services.

    $180

    per year per host

    Pricing
    SolarWinds Kiwi Syslog ServerSplunk Observability Cloud
    Editions & Modules
    One Time Price
    $319.00
    Per Instance
    Infrastructure
    $15
    per month (billed annually) per host
    App & Infra
    $60
    per month (billed annually) per host
    End-to-End
    $75
    per month (billed annually) per host
    Offerings
    Pricing Offerings
    SolarWinds Kiwi Syslog ServerSplunk Observability Cloud
    Free Trial
    YesYes
    Free/Freemium Version
    YesNo
    Premium Consulting/Integration Services
    NoNo
    Entry-level Setup FeeNo setup feeNo setup fee
    Additional Details——
    More Pricing Information
    Community Pulse
    SolarWinds Kiwi Syslog ServerSplunk Observability Cloud
    Considered Both Products
    SolarWinds
    No answer on this topic
    Cisco
    No answer on this topic
    Key User Insights
    Would buy again
    100%
    Would buy again
    5 Answers
    95%
    Would buy again
    55 Answers
    Delivers good value for the price
    100%
    Delivers good value for the price
    5 Answers
    94%
    Delivers good value for the price
    48 Answers
    Happy with the feature set
    100%
    Happy with the feature set
    5 Answers
    98%
    Happy with the feature set
    57 Answers
    Lived up to sales and marketing promises
    100%
    Lived up to sales and marketing promises
    5 Answers
    97%
    Lived up to sales and marketing promises
    31 Answers
    Implementation went as expected
    100%
    Implementation went as expected
    5 Answers
    98%
    Implementation went as expected
    45 Answers
    Best Alternatives
    SolarWinds Kiwi Syslog ServerSplunk Observability Cloud
    Small Businesses
    SolarWinds Papertrail
    Score8.9 out of 10
    Amazon CloudWatch
    Score7.8 out of 10
    Medium-sized Companies
    SolarWinds Papertrail
    Score8.9 out of 10
    LogicMonitor
    Score8.9 out of 10
    Enterprises
    SolarWinds Loggly
    Score7.7 out of 10
    ManageEngine Site24x7
    Score10 out of 10
    All AlternativesView all alternativesView all alternatives
    User Ratings
    SolarWinds Kiwi Syslog ServerSplunk Observability Cloud
    Likelihood to Recommend
    8.0
    (7 ratings)
    7.9
    (59 ratings)
    Likelihood to Renew
    -
    (0 ratings)
    9.0
    (3 ratings)
    Usability
    10.0
    (1 ratings)
    7.6
    (18 ratings)
    Support Rating
    9.9
    (3 ratings)
    10.0
    (1 ratings)
    Implementation Rating
    -
    (0 ratings)
    10.0
    (1 ratings)
    User Testimonials
    SolarWinds Kiwi Syslog ServerSplunk Observability Cloud
    Likelihood to Recommend
    SolarWinds
    To monitor syslog events Kiwi syslog much helpful and needed .Its saving human efforts and cost.Easy to check on GUI panel flow and status of server ,start and stop services we can do them from GUI panel it self . Recent version also no need C++ libraries to install .We can store the ingested events and archive based on our threshold criteria .We can import and export INI file which contain everything what we have configured
    Read full review
    Cisco
    Its great if you need real-time visibility across complex or regulated environments. Also strong for hybrid or multi-cloud setups where uptime, observability and fast IR are required. It’s probably overkill for smaller teams or environments that don’t have constant changes or compliance reporting needs. It's expensive and has a steep learning curve. Also, in my opinion, do not get yourself into a consumption based model. Costs can certainly get out of control quickly.
    Incentivized
    Read full review
    Pros
    SolarWinds
    • Collection of SNMP traps a reliable and stable collection server for these is crucial to troubleshooting and time to ROS. Kiwi excels at this.
    • Easy to install set up and train users on.
    • The free version is a good free tool and handy to use for personal labs and other smalle use cases.
    • SNMP traps to user readable format is great, sometimes syslog and smnp messages can be hard to interpret and read with out a knowledge of how to do this.
    Incentivized
    Read full review
    Cisco
    • The first one is its Kubernetes container monitoring.
    • I really like this features because as we know how much K8s is vast and to manually monitor each part of the Kubernetes it takes so much time but Splunk Observability Cloud makes it easier. And even once we integrate K8s with Splunk Observability Cloud it gives us some prebuilt dashboards which gives holistic view of our Cluster and its nodes, pods, etc.
    • The dashbaord feature of Splunk Observability Cloud, it gives us full flexibility to customize our dashboard with a wide range of predefined chart types.
    • Now it also supports OTEL, which is a plus point for observability. As now everyone is moving towards Otel and in current market there are only few tools who supports OTEL based integrations, Splunk Observability Cloud is one out of them.
    Incentivized
    Read full review
    Cons
    SolarWinds
    • Minimalistic; If you're looking for something with analysis features look elsewhere.
    • Operating System support is Windows only.
    • Some management features cannot be configured via web interface.
    Incentivized
    Read full review
    Cisco
    • You can use table-like functionality to generate dashboards, but these queries are heavy on the system.
    • It could be easier to give insight into what type of line parsing is used for specific documents in a company-managed environment and/or show ways to gain the insights needed.
    • I would like to see ways to anonymize specific data for shared reports without pre-formatting this in a dashboard on which reports could be based.
    Incentivized
    Read full review
    Likelihood to Renew
    SolarWinds
    No answers on this topic
    Cisco
    Good: Stable system with low error rate Easy to use for simple use cases Bad: UI is not very clear for complex usage Mobile view (when logged in from phone) is bad No library for .net
    Incentivized
    Read full review
    Usability
    SolarWinds
    Kiwi Syslog has the best usability of any syslog server. While not being able to offer the most features, the ones it does have are intuitive and easy to work with. Everything that it has is where you think it should be. If you can't find it in the menus, it doesn't exist.
    Incentivized
    Read full review
    Cisco
    When there is an issue, it’s a win if one can easily identify the root cause. To do the same, it should allow the user to dig deep with multiple data points and compare the data and identify the anomaly. In this use case, it’s good to drive from Splunk 011y.
    Incentivized
    Read full review
    Support Rating
    SolarWinds
    Because the solution is so simple to use and implement, support wasn't very necessary. The one time I did call them to better understand where logs were stored, they were very helpful and friendly. Kiwi has been around for some time and not a lot has changed over the years, so support for it is pretty straightforward and quick.
    Incentivized
    Read full review
    Cisco
    Splunk support is very quick and efficient. Pre-sale specialists are very skilled and available.
    Incentivized
    Read full review
    Implementation Rating
    SolarWinds
    No answers on this topic
    Cisco
    Follow a training before starting.
    Incentivized
    Read full review
    Alternatives Considered
    SolarWinds
    PRTG is a great package and very useful, but the jump from the free 100 sensor price model to the first tier of the paid model is WAY too expensive. SolarWinds Kiwi Syslog Server is very inexpensive and provides us with the results we needed for log monitoring.
    Incentivized
    Read full review
    Cisco
    Splunk Infrastructure Monitoring provides far superior options for anybody using a complex hybrid multi-cloud environment and allows both your SOC and NOC to work together on the same data while driving their own insights. We found other products are still in the old world view of servers and agents residing together within a single data centre, but modern apps are no longer like this.
    Incentivized
    Read full review
    Return on Investment
    SolarWinds
    • Its provides centralized console for Server and Network devices log collection, reducing need of two separate Log collectors.
    • It reduces cost
    Incentivized
    Read full review
    Cisco
    • Significantly reduced the MTTR (Mean Time To Recovery), which in turn has improved the end-user experience tremendously.
    • Meets compliance requirements of security policies, audit, regulation, and forensics.
    • Helps us to track/manage the resource usage on our cloud instances which has a direct implication on the recurring cost.
    Incentivized
    Read full review
    ScreenShots

    SolarWinds Kiwi Syslog Server Screenshots

    Screenshot of Manage syslog messages and SNMP traps from network devices, including Linux, UNIX, and Windows systems from a single console.Screenshot of Trigger email alerts, run scripts, log to file or ODBC database, forward messages, and more.Screenshot of Schedule automated log archival and cleanup to help you comply with SOX, HIPAA, PCI DSS, etc.Screenshot of View graphs of syslog statistics over specific time periods.Screenshot of Filter and monitor log messages on an intuitive syslog viewer web console with multiple custom views.Screenshot of Perform advanced message filtering by host name, host IP address, priority, or time of day.

    Splunk Observability Cloud Screenshots

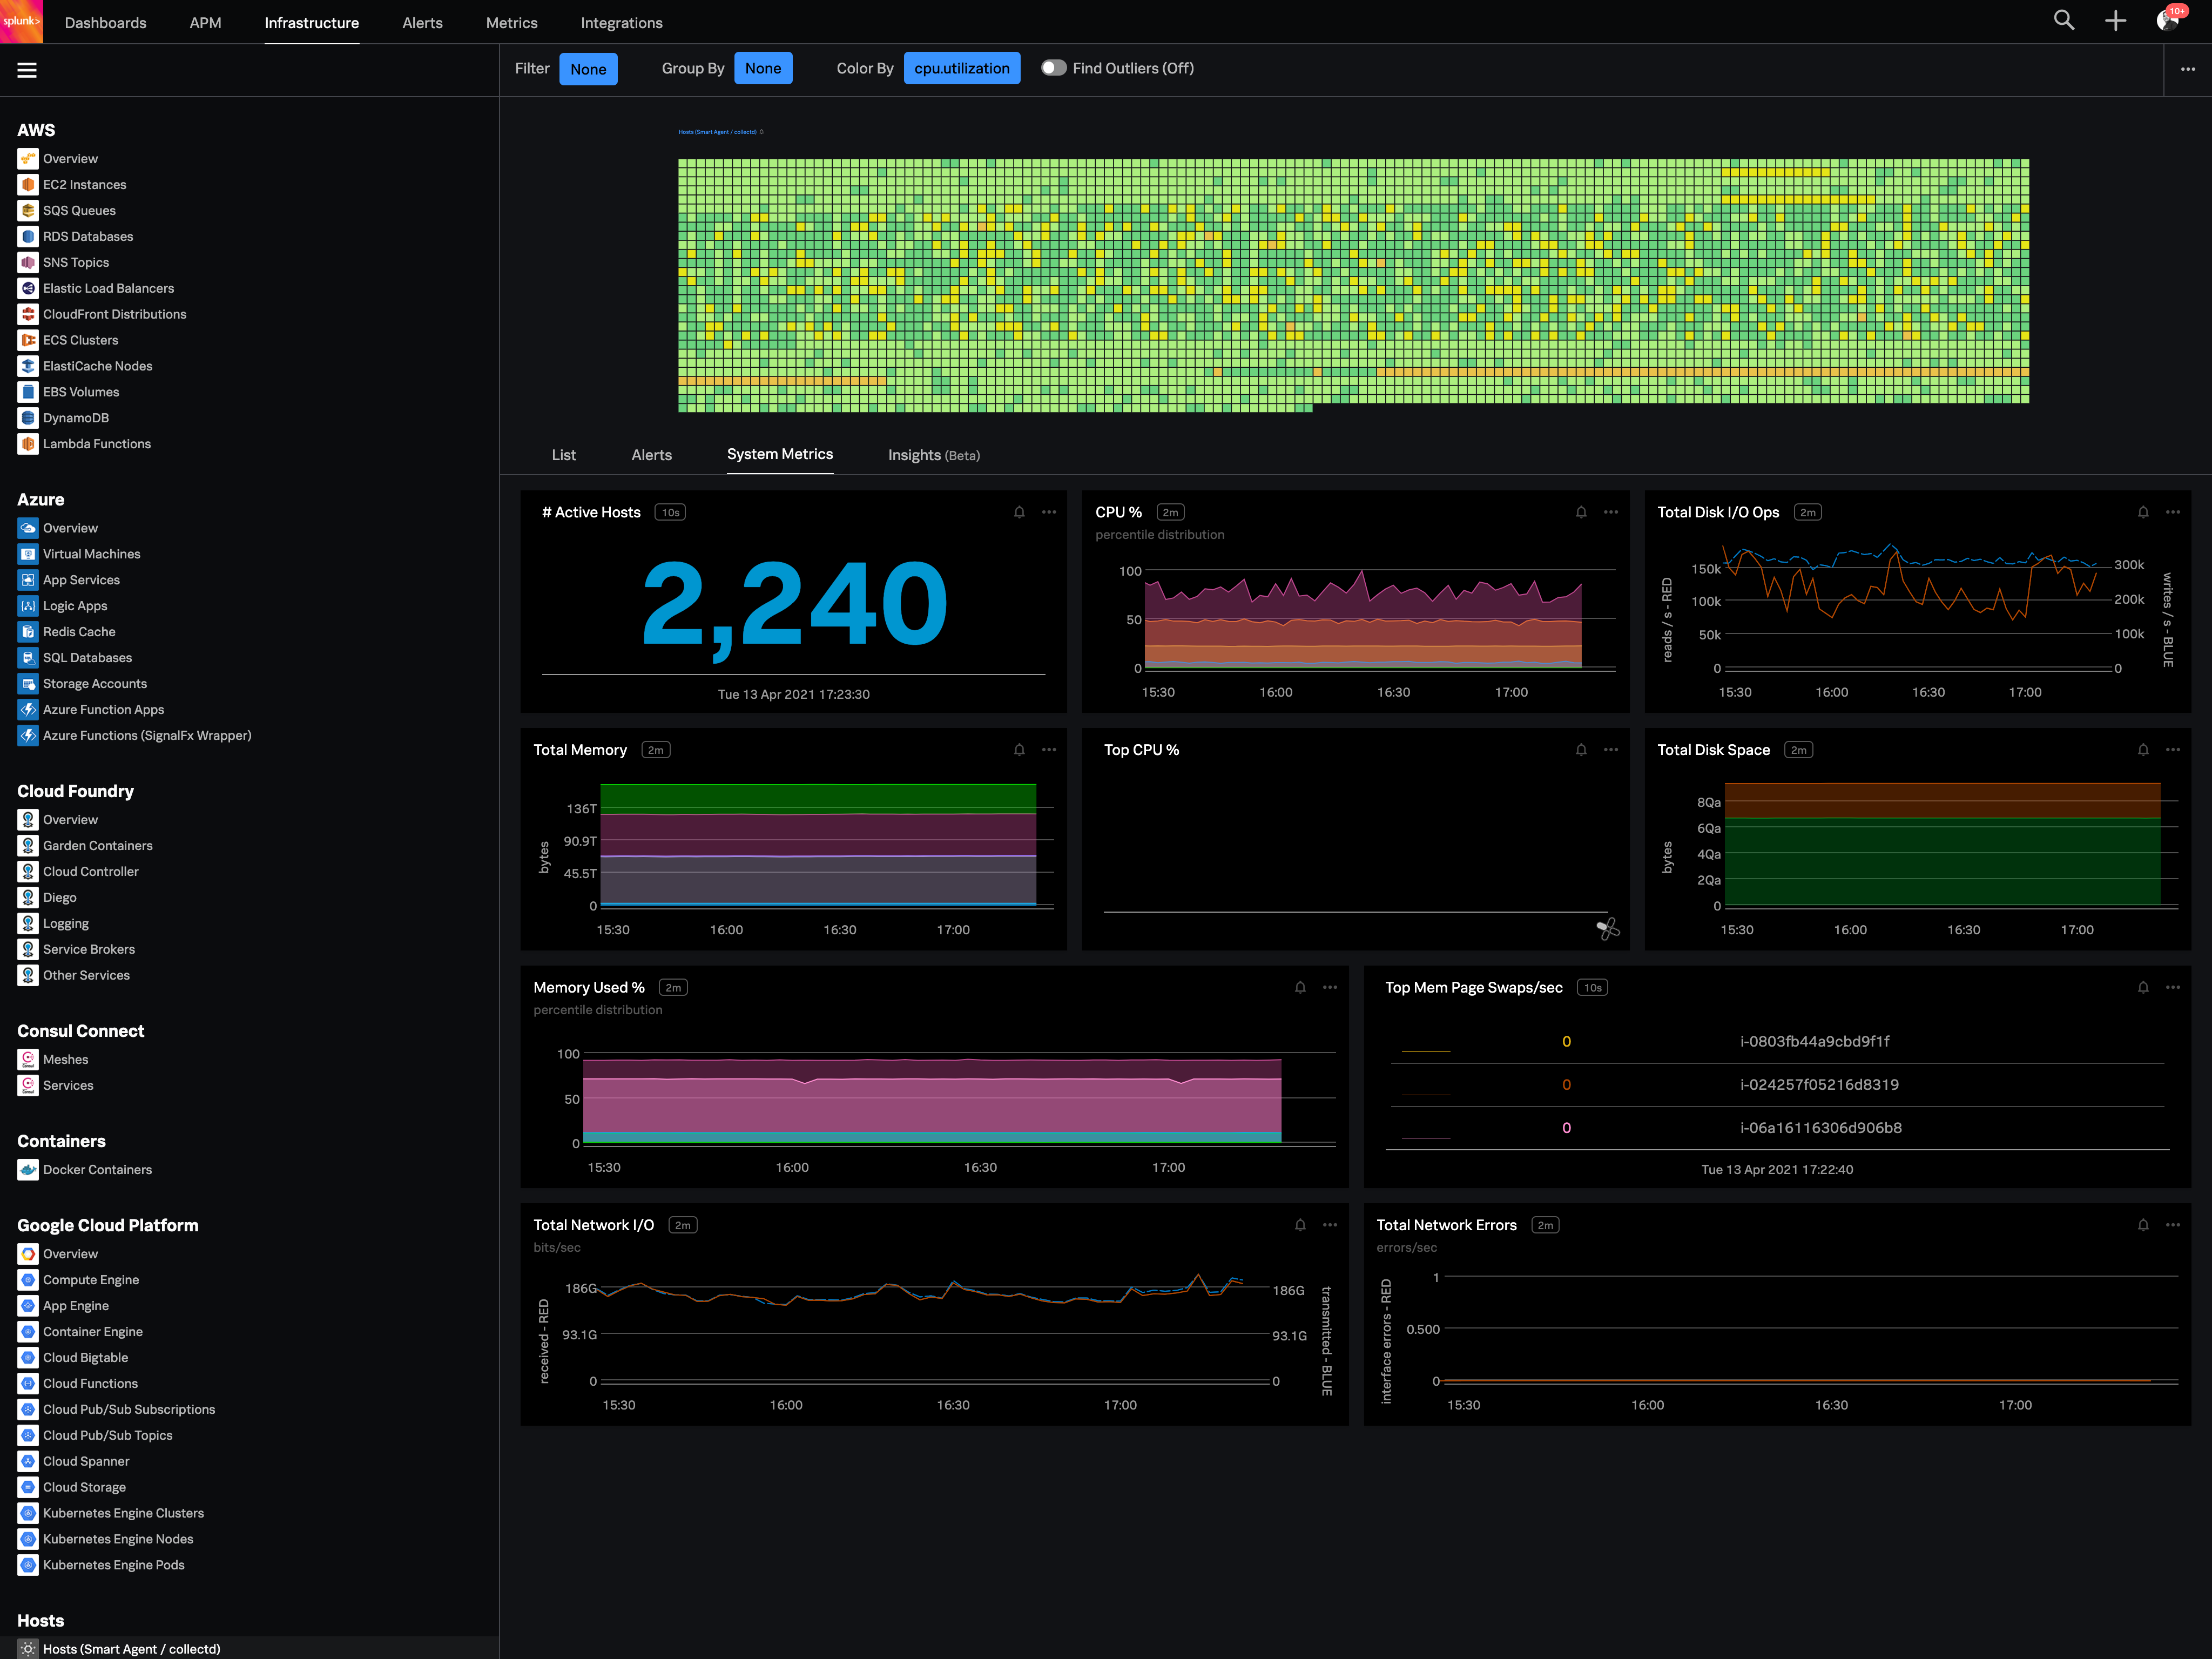
    Screenshot of Real-time monitoring for public, private and hybrid cloud