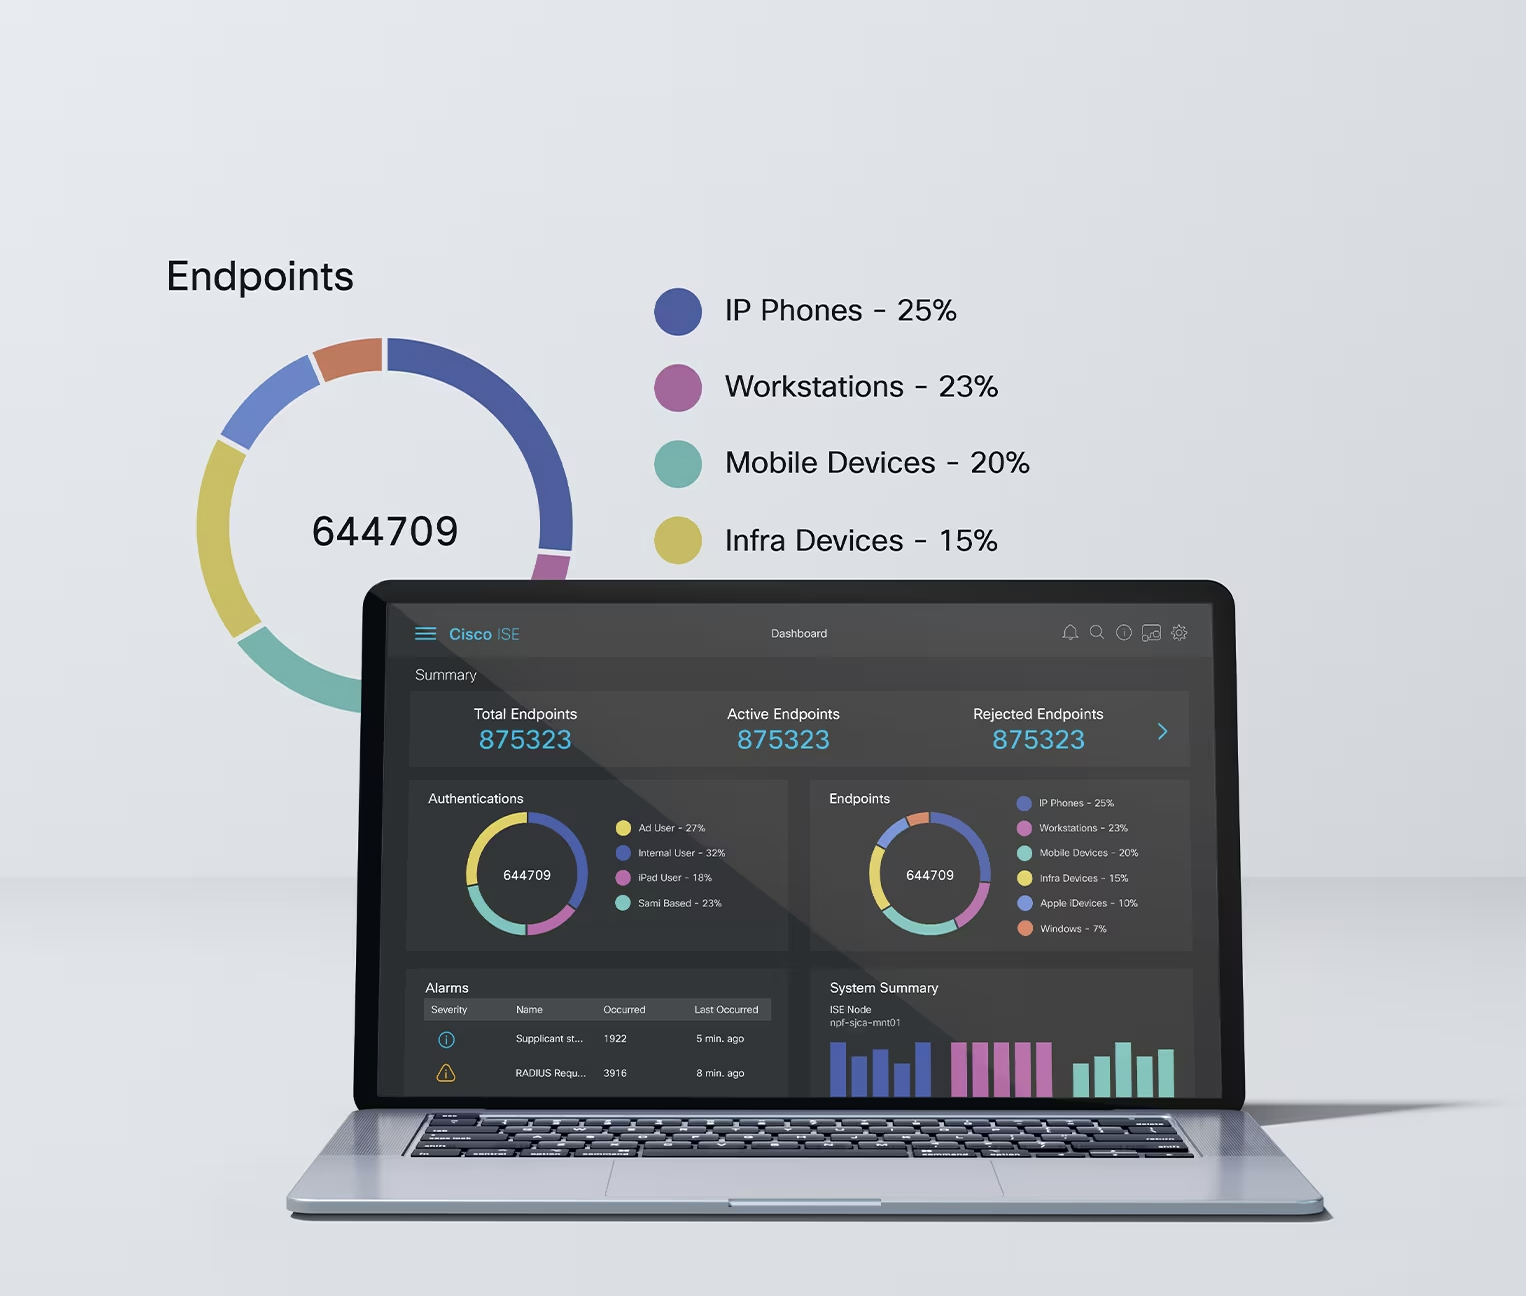
The Cisco Identity Services Engine (ISE) offers a network-based approach for adaptable, trusted access everywhere, based on context. It gives the user intelligent, integrated protection through intent-based policy and compliance solutions.
N/A
SecureLink Enterprise Access
Score9.1 out of 10
N/A
SecureLink is a platform for remote support in regulated industries. Enterprise software vendors use SecureLink to deliver remote support and services. Hospitals, banks, casinos and other regulated entities use SecureLink to authenticate, control and audit remote access for their vendors, business associates and other 3rd parties.
N/A
Zscaler Private Access
Score9.4 out of 10
N/A
Zscaler Private Access™ (ZPA) gives users secure access to private apps and OT devices while enabling zero trust connectivity for workloads.
Well suited... I've used it for both wired and wireless access, and it's perfect for that. In addition to enforcing security on the port, you can also lock down east-west traffic. When you get to the point where you're configuring secure group tags and things like that, you can keep people from getting to places they shouldn't. Basically, you could turn your entire network into a firewall if you wanted to. You can secure access based on the identity of any given user through role-based authentication. For example, if you have salespeople and you don't want them accessing your financial or PCI environment, they authenticate as a salesperson and you can completely stop them from getting to any of that. That's really important, especially for us. Our payment card infrastructure servers are heavily locked down. Granted, in our situation, we firewall all that off anyway, but you still don't want some random individual to be able to even attempt that sort of thing. That's what it's really good for. I'm trying to think of a weakness. I don't know. We don't really struggle with it. There's nothing that I use it for where I wish it were better, at least not that I can think of offhand. I'm sure there are things, I just can't think of anything off the top of my head.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It does exactly what it needs to. The only times I've had serious issues with rolling out to a vendor is when they have a "contractual agreement" to only use their solution. Almost every vendor that I've worked with and shown this product to has been skeptical for the first 5 minutes and fully converted to liking the ease of use of the product by 10 minutes
Zscaler Private Access works really well in environments setup for FQDNs and where you know what users should/shouldn't be accessing on what ports. You can use Zscaler Private Access to figure out these kinds of features but that doesn't always mean you'll be correct. It also provides a consistent experience for users as they can access their materials anywhere. It also makes the user the last line of defense. If a user's account is compromised then the attacker has access to everything they already did. It doesn't work great in OT environments or Server based environments. Flows have to be initiated from the client and not the server for stuff to behave properly.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Connecting users remotely with a secure connection. I am a service desk agent who works with end users, and if there is an issue due to ZPA, it's most likely due to configuration. A really good service.
Logging, I believe, works well as I troubleshoot end users and can gather extra details for my network admin. IP.zscaler.com, and the debug logs are nice. Additionally, I like how it shows the App policy assigned to the user's machine ECT.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Java based. Always an issue. I know they are working on this and it will be Javaless if we need it. I know that Java can cause issues across the board and I understand the need of it, but it does not make it any better when there are Java issues.
Stronger integration with the Active Directory. Currently its only read-only, which is good and bad.
I would love to see an App. I know they are working on this as well.
Needs an interface for Support Desk/Help Desk to more easily understand that the problem is a lack of an FQDN or access is not allowed due to policy, not because of a technical shortcoming in ZPA.
Documentation of the BC solution is not well-detailed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
For us the solution is very easily useable on its own. Perhaps that has to do because we started using ISE in the 1.2 days and have seen it grow during the years. Policy creation, etc. is all very visible and thus easy to use. Deployment of multiple nodes is also incredibly easy and flexible. You can easily add or remove nodes as you wish.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The environment feels more secure, and we are seeing that users are adapting to it fast. The fact that we have tools to assist the users with their day-to-day access helps, as we can hand it off to the helpdesk without any escalations to the Network team. It is a work in progress for our agency, but we are seeing the benefits from the solution.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We do have to occasionally reboot the servers when they get low on memory, but we're also a few versions behind. Availability has generally been pretty good though with no major outages in the time that we've had it implemented.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco support is second to none, both in terms of how you access support but also the knowledge of the individual support teams. If you focus on one technology and provide "manufacturer support" then you can rest assured that you are accessing Cisco's top individuals. I feel like this is a USP for Cisco support.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The employees at Securelink have always been responsive and seem to be invested in the success of my company. They truly understand what their product means to us so if there is a problem, they are always willing to help. In the rare event that something is found on their end, they will be proactive and reach out to someone to help and get something on calendar for a fix
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I think our system integrators lacks some competencies and this has led to an implementation that is still perfectible. (i.e. dedicating an interface for intra-cluster communication)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think all give some visibility of device monitoring and management, but Cisco Identity Services Engine gives a good way to manage more details about the device in a centralized way that gives a wider range of monitoring and control than the other softwares individually. I don't think Cisco Identity Services Engine eliminates the need for these other software as of now, but there is potential for Cisco Identity Services Engine to be able to take over more of these roles.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Securelink seems to work better than LogMein for a large enterprise group. Our company has over 10,000 different connections and securelink manages them well.
ZPA is where the bulk of zero-trust access is found. While the functionality for ZIA is excellent, the policy we implement for internet access is more focused on threat prevention and not narrowly scoped access.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It's fully customised and comprehensive. only thing is you need to know what you want. Proper research and planning would save lots of time and effort .
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I don't know about negatives because we haven't seen it right now, but positive impact is one is the roadmap we have. And now since we are going ahead with doing the deployment of Cisco ISE, we see that we are getting closure to, so at the end of the day, we have to make sure that operationally we stay excellent. So that's where operational excellence comes in. Cisco ISE is basically addressing that for us. Right now we are in a situation if there is a WIFI issue or if there is an authentication issue, it gets really difficult to isolate the problem. But with Cisco ISE , this functionality is going to come in. So we believe that it would be a good ROI.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I've found that Securelink allows me to get a vendor access to an application for support purposes much faster than a provisioned VPN account and the red tape around this. I can set up a vendor to access an application suite in a half hour and it will be more secure than regular provisioning.
The ROI is yet to be seen on this, but it certainly makes Compliance, Internal Audit, and Legal very happy, which helps everybody.
Internally, there is much more push back and it has been problematic. For a tech, to have to log in to a server and navigate to a system is considered cumbersome, when before all they had to do was open up Putty or RDP to a server to get in. The only way to combat this is to force them to use Securelink by removing rights. Near impossible for the domain admins.
We used to get anywhere from 30 to 50 tickets surrounding our previous VPN solution every month. We now average 3-5 tickets regarding remote connectivity, and of those, only 1 or 2 are actual issues with ZPA.
Using ZPA Access Policies, we can now block endpoints that have outdated security software from ever connecting to our environment. This was simply not possible with our previous solution.
Some of our employee base skews older and had a harder time understanding the change from VPN to Zscaler.
There is significantly less downtime with ZPA when compared to other VPN solutions.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info