Cisco ThousandEyes empowers organizations to assure every digital experience across every network, everywhere, every time.
N/A
Microsoft Defender for Endpoint
Score8.8 out of 10
N/A
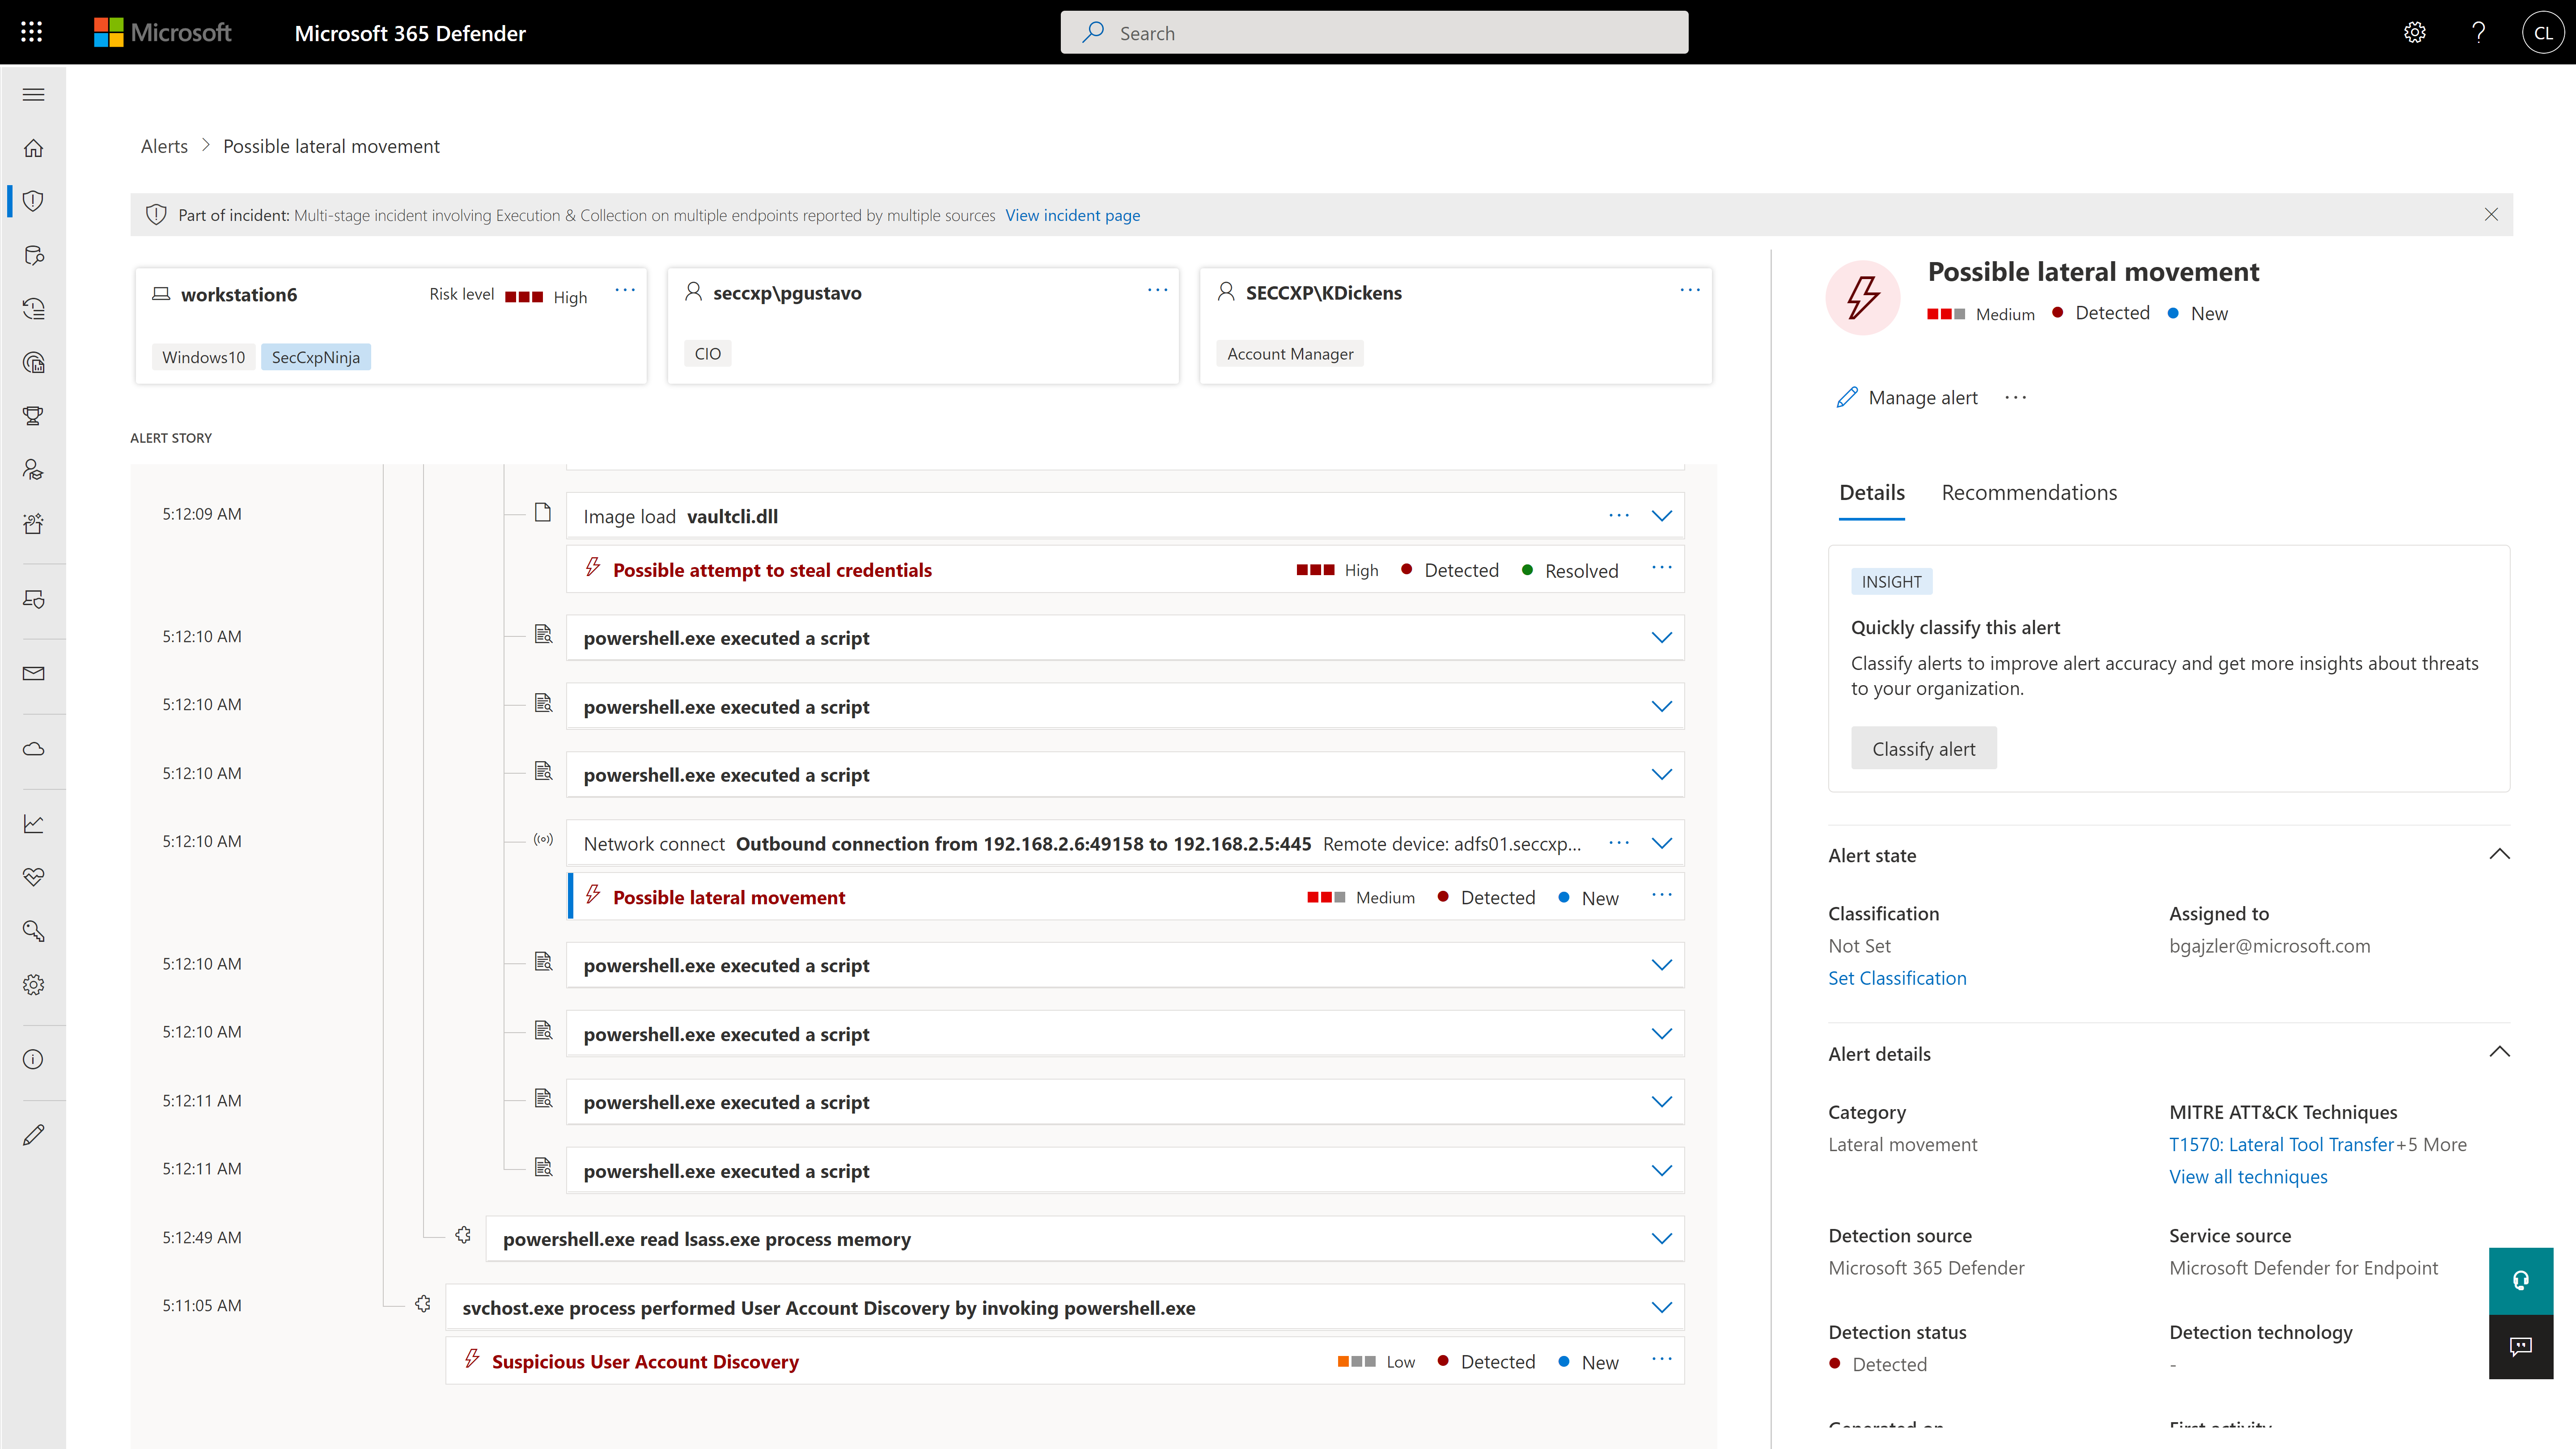
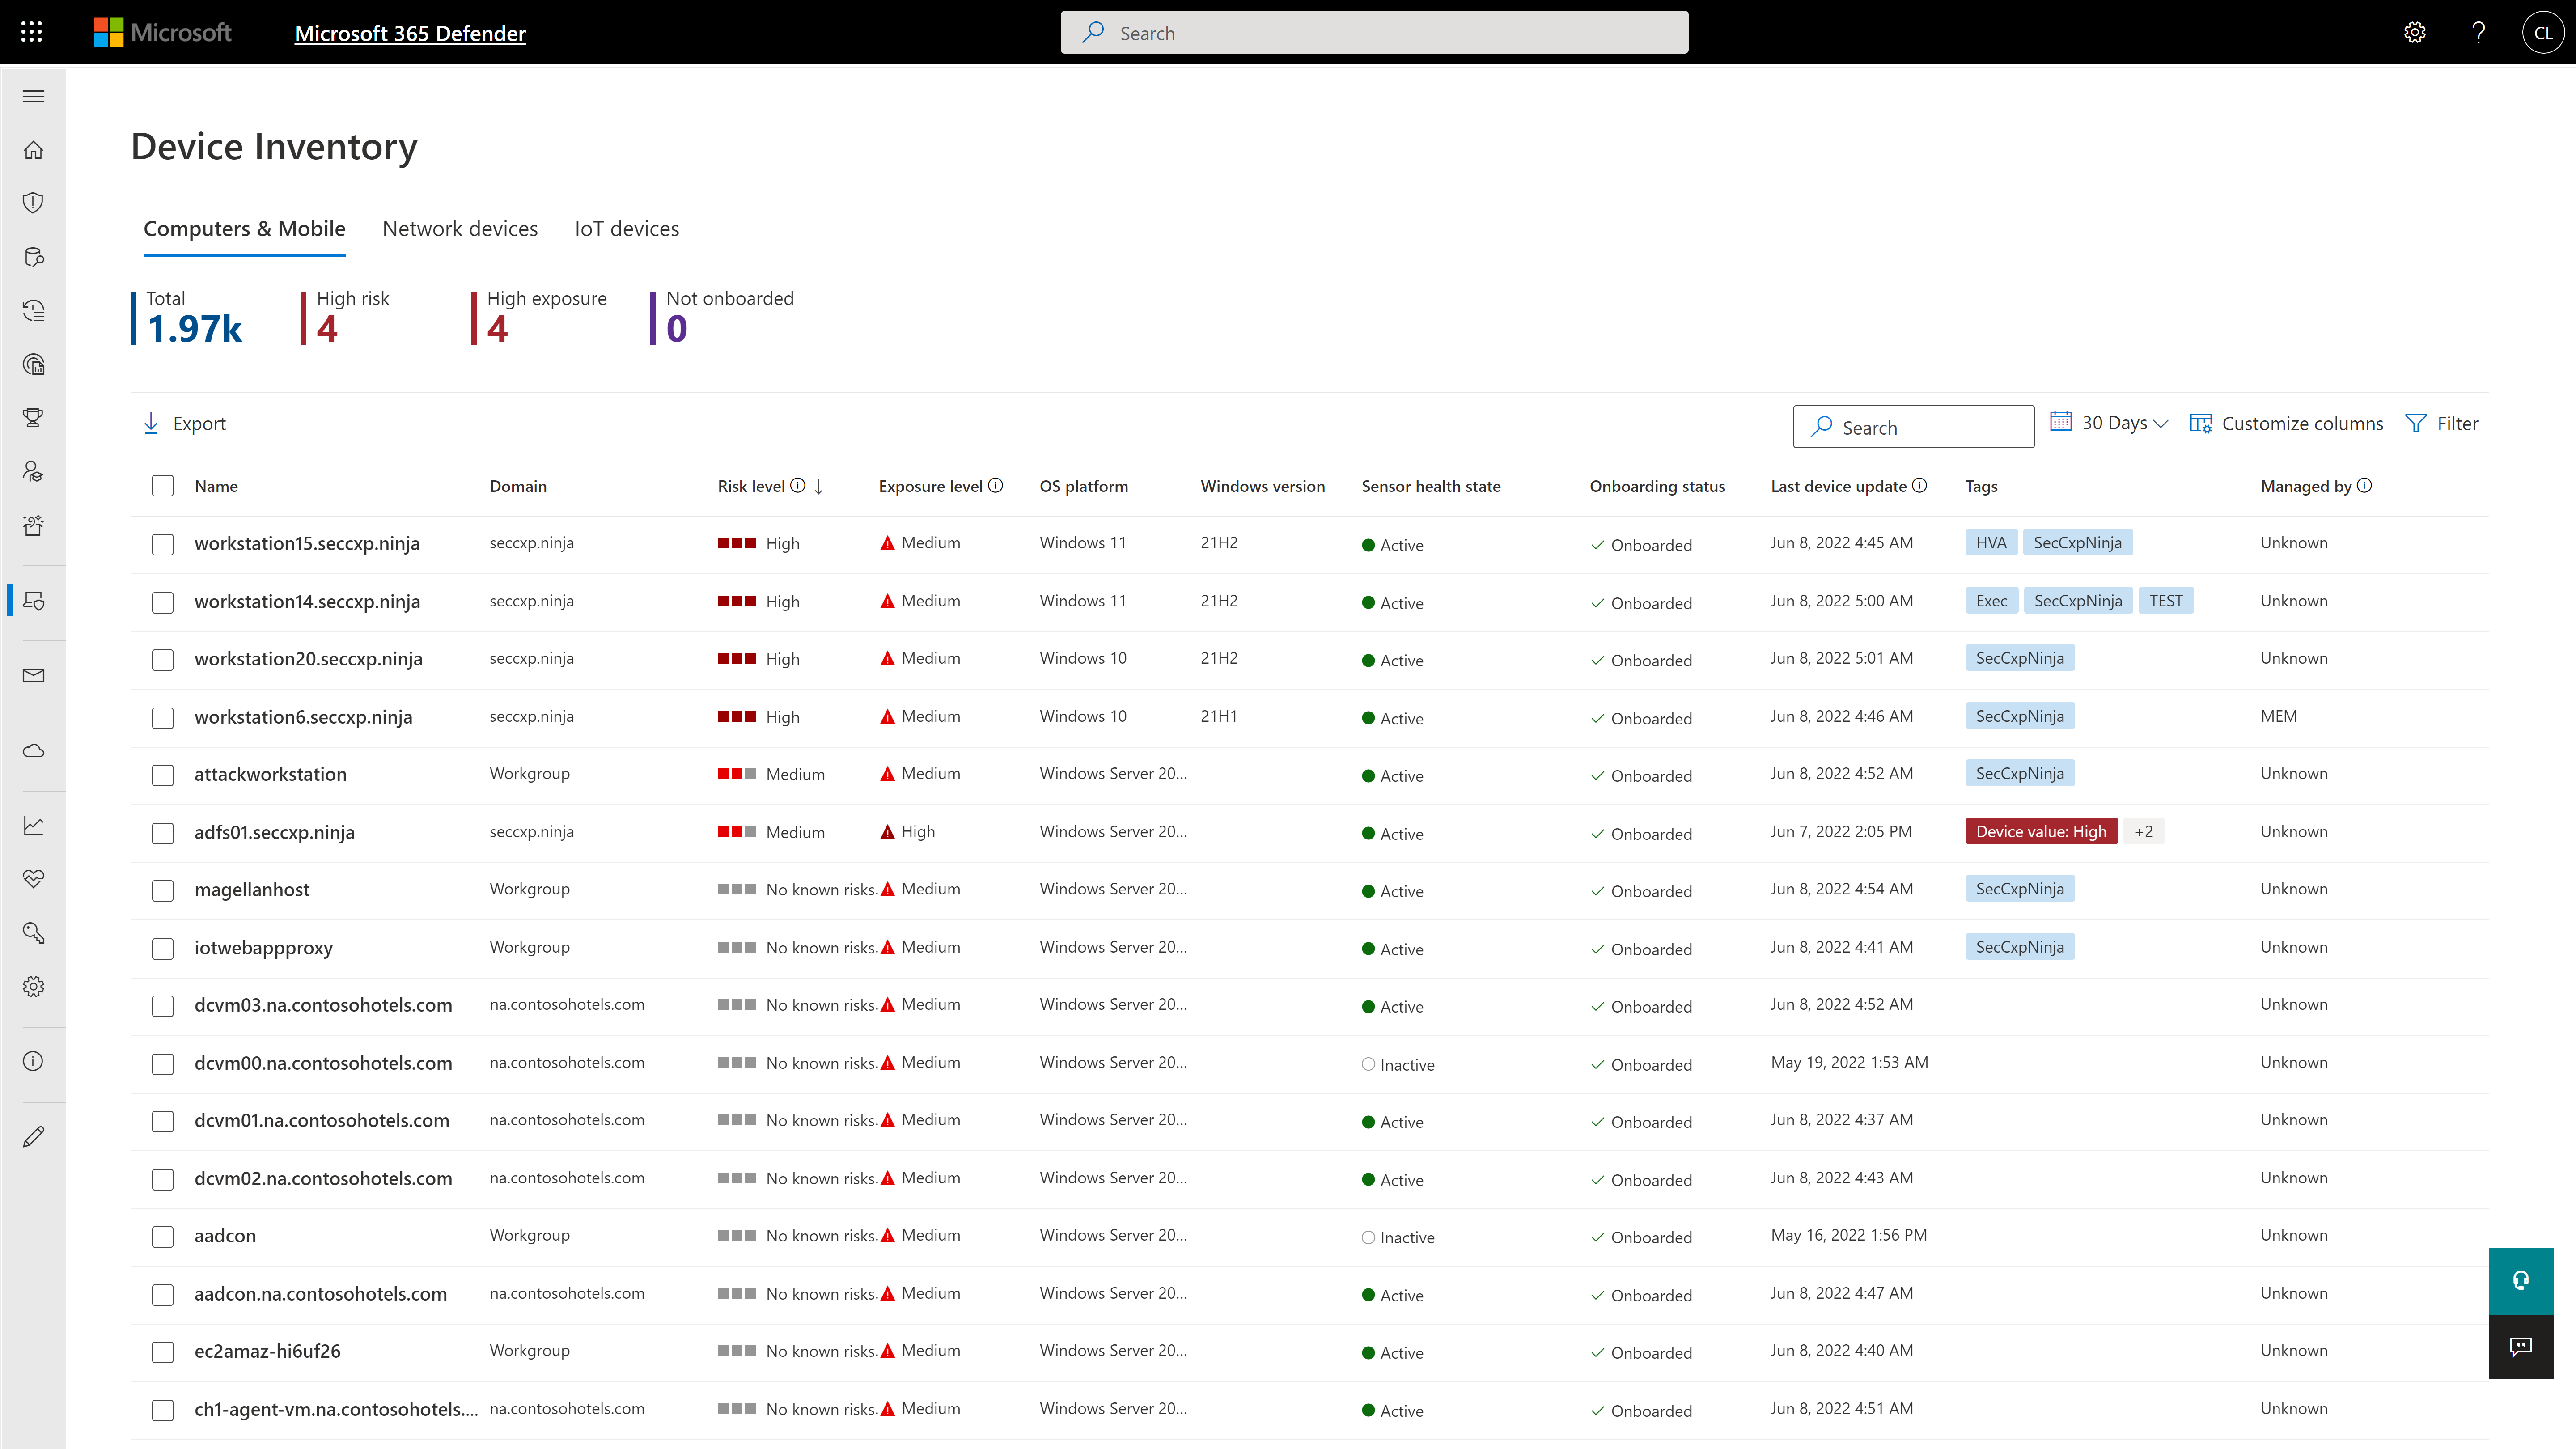
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
Unified communications real-time analysis is one of the biggest points of the solution. You can see your traffic path and find issues before, during and after the calls. This is very useful for analyzing VoIP and video conferencing problems like in WebEx, Microsoft Teams and Zoom. It helps to see network issues like packet loss, jitter, or latency that can make call quality bad. Another good use case is checking cloud apps and SaaS services. Many companies use external platforms like Microsoft Azure, 365, Salesforce, or AWS. It lets Networking teams see the network path from users to these services so they can find if problems come from the company network, the internet provider, or the cloud service. Also, it is good for companies using mix of on-prem and cloud. It shows how traffic moves between different parts of the network, so IT teams can see where a problem happens and fix it faster. There are different types of agents that we can use in Cisco ThousandEyes. Enterprise agents can be use for a relative big amount of synthetic test. Endpoint agents are install in user PC or MAC laptops to check network quality from the client side. WebEx devices also have built-in agents that help to see performance problems in meetings, making it easy to find what is causing a bad call. Maybe it's not the best solution if what you want to measure is not HTTPs based or hasn't an API. Also if your scenario is Zoom Rooms, you won't have the same level of integration that it has for WebEx and Microsoft solutions.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco ThousandEyes does the holistic discovery of the end components, the network components, and it's really fast at identifying where the issue is, which is not normally identified by the classic monitoring tools. So it's quite a fast identifying the issue of the networks and Cisco ThousandEyes also provides a very good real user end user monitoring experience for the end customers. So those are the two real life and also very good examples for Cisco ThousandEyes.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The elephant in the room is going to be cost. ThousandEyes is a great tool, but you will pay for it. There are other services that do a good job at providing a smaller subset of features compared to ThousandEyes. If all you need is that particular subset of features, ThousandEyes may not make fiscal sense for your organization.
As a subset of the cost issue, within the last 18 months or so the pricing on enterprise (local) agents has been modified in a way that seems not to benefit the customer. Previously enterprise agents had a flat monthly cost associated with them with unlimited test usage (the only limit on test usage was based on concurrent tests running at any given point in time). This meant that instead of using a cloud agent and paying per-test, you had the option of spinning up an cheap Digital Ocean droplet and creating your own cloud agent for external testing without using Cloud Agents. When the change was made they eliminated the flat per-agent cost and instead treated the pricing the same as that of the cloud agents but cutting the number of "cloud units" per test in half for tests run from enterprise agents. For organizations with under-utilized enterprise agents, this may be helpful financially, but for organizations that push their local agents to the limit, the cost skyrocketed.
BGP monitor peering sessions have been less than reliable. The data doesn't seem to be an issue, but the sessions seem to bounce or fail altogether on a fairly consistent basis. The routers or servers with which your routers peer sit behind some firewalls that have caused issues in the past.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The software does it's job extremely well and the system makes it very user friendly to get into. When looking for software I prefer to not need a PHD to operate it. Having a great UI and simple setup makes it easy to include more members of our team to get more value out of the platform.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
There is definitely a learning curve to ThousandEyes, but once you understand how the client deployment works and how to set up monitoring, things go pretty smoothly. I think the initial setting up of clients on endpoints can be a little tricky though.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
You have online support from the tool itself 24/7 and they are very responsive. We also have a specific account manager and specific engineer assigned to help us with very specific questions for our environment. The level of response to our requirements is always super high. We have requested specific features to be added and these have been developed and introduced very quick tot he product (within weeks). Their DevOps and agile approach seems to pay off.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Our Cisco reps actually had someone teach us a few things about the functionality of ThousandEyes, and it helped a lot. The training was good and we had follow-up assistance as well when we had questions about the monitoring and reporting functions. Overall, we were satisfied with the training and support.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Our implementation was pretty straightforward, with some issues loading clients on endpoints. We didn't have any notable issues, and I don't really have any additional insights.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
No one is better than the other. I can get different data and sometimes similar data, it's important to compare values and verify the data between the tools. Additionally, there are other functionalities that ThousandEyes has that the others don't, but it is also the other way around. I will always recommend to have available not 1 or 2, all possible available for your job.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think this product would be infinitely scalable since it's all cloud hosted and can support thousands of endpoints if needed. We are only using it for a limited number of endpoints, so we never really considered scalability.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Building the trust from our Merchants is core when you come to renewal time. Trust builds partnerships, builds stickiness and allows for easier upsells or contract renewals.
Having a champion in IT that touts your service is important to the business, it removes a large portion of friction in the business to get services implemented and working to its peak.
Flexibility in pricing can be better. How they measure the number of agents being used can get thorny. When you build and tear down virtual servers a lot it can appear there are more agents running than there are. Once we understood how they measure we were able to better utilize the product efficiently.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info