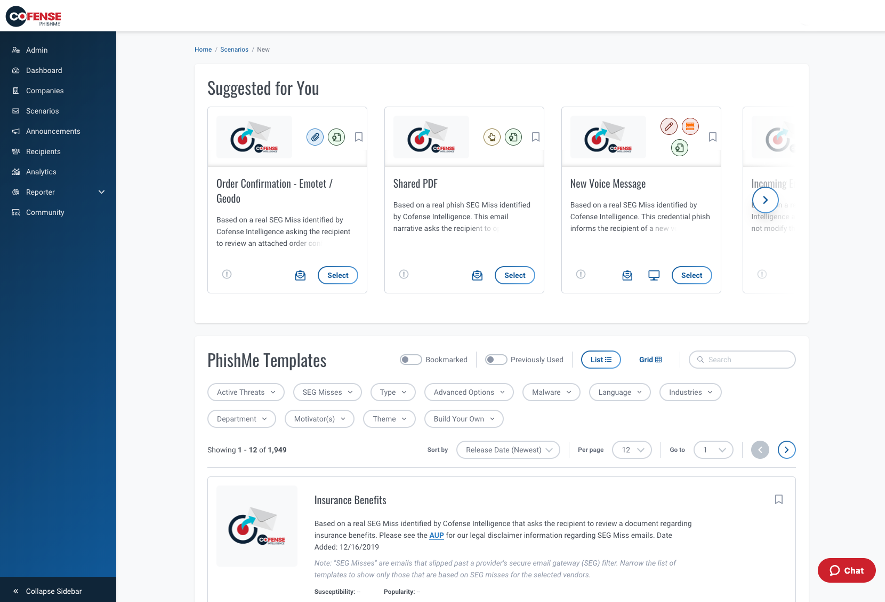
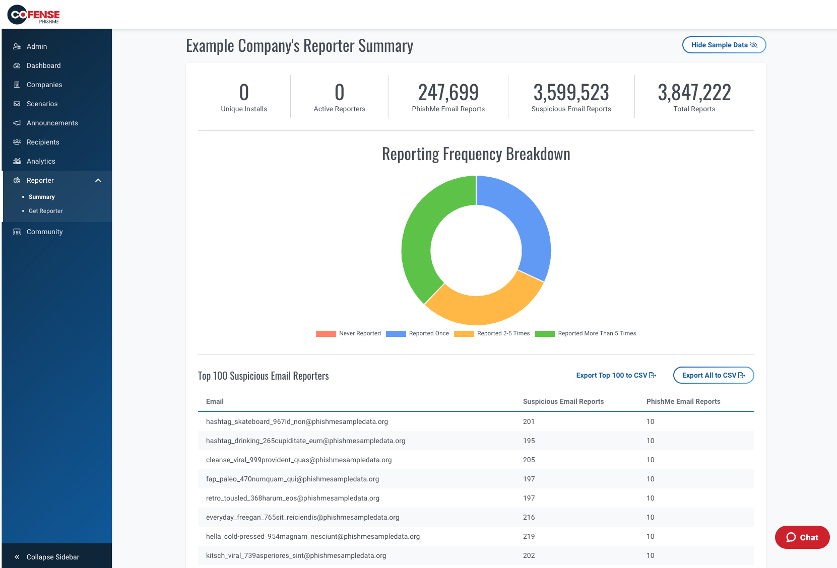
Cofense PhishMe is a cyber threat and phishing simulator meant to be of use in training employees to be wary against threats and also to gain information about general employee threat knowledge and preparedness. A free trial is available for small business.
N/A
Darktrace
Score8.3 out of 10
N/A
Darktrace AI interrupts in-progress cyber-attacks, including ransomware, email phishing, and threats to cloud environments. It's able to detect and establish baselines for your organization so it can make the distinction between what is and what isn't normal network activity for your organization. This allows it to tackle complex cyber-attacks as they happen and prevent future cyber-attacks from happening.
N/A
SolarWinds NetFlow Traffic Analyzer (NTA)
Score8.5 out of 10
N/A
SolarWinds Netflow Traffic Analyzer is a network monitoring tool within the broader SolarWinds ecosystem. It includes core traffic monitoring features, as well as customizable traffic reports and alerts.
Cofense PhishMe is an excellent solution for scenarios where it will be sold as a managed service. I believe that PhishMe is too expensive for many clients and instead would benefit from the economies of scale where an MSSP sells it as part of a whole service, which offers the analysts and reporting included. PhishMe is excellent for training and awareness of Phishing, but shouldn't replace mandatory training for new joiners or yearly refreshers, it should only be used as an additional training option.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Darktrace is a product well suited for the vast majority of infrastructures and helps monitoring and responding to threats based on the network in a very elastic way. This is a product based on on-premise infrastructures that hosts its machines locally, of course it can be technically difficult to monitor an entire On-Cloud infrastructure but even there there's room for sensors and monitoring, not to mention the SaaS and mail integration that completes the product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We use and depend on it for status state of our network gear, switches and routers. It does an excellent job of getting you the details you need to confirm all devices and products are working at the level needed. At times, it does tend to flag network switch ports and/or switches themselves as exceeding their rated capacity when frequently it was a quick blip of high traffic due to downloads, or uploads causing the max'ing of the device. Again, you can adjust the settings but then you adjust it too high and miss real activity. It can become nuisance alerting when you tend to then ignore
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It gives clear-cut segregation of different parts of an email, header, text and HTML body, URL, attachments, HTML preview and some analytical insight like "similar reports." This distinctive approach actually helps reduce data overload during an analysis.
The URLs captured here pass through an automatic reputation check [in our case VirusTotal] and add a tag of the reputation. If it is a well-known bad URL the tag helps us take the decision fast.
For creating automation rules on the reported emails the "Recipes" section is really helpful. We can create easy recipes [or rules ] to handle a huge flow of reports and also we can create more sophisticated rules depending on the Cyber intelligence feed to catch the really bad currently less known attack attempts by malicious emails.
The "Threat Indicators" section is also useful to use as a threat intelligence source to check the URLs for their maliciousness.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Uses it Al model UEBA to detect anomalies in the behaviour of not only the users in a corporate network but also the routers, servers, and endpoints in that network.
Provides a visualisation of both egress and outbound network traffics flowing in and out of the organisation.
Darktrace comes with it autonomous AI model detection and responses capabilities.
Darktrace as an AI next generation NDR solution, prevents ,contains and quarantines malicious traffics from and into the corporate network.
The level of customization possible with Network Bandwidth Analyzer is very valuable. Rather than being stuck with a "one-size-fits-all" presentation, an administrator can easily create customized views, reports, and alerts so that users can have a more tailored view of the data provided by Network Bandwidth Analyzer. This has the effect of making the tool more attractive to the end user.
The NetFlow Traffic Analyzer piece of Network Bandwidth Analyzer provides the details on bandwidth usage on the network. More than knowing how much bandwidth is being used, one is provided with detailed information on how that bandwidth is being used. This provides invaluable information for capacity planning and even certain forensic tasks faced by the network engineer.
The ability to produce network maps provides an easy way to create an attractive and functional NOC/SOC view of the entire network. Both technician and the occasional passerby can quickly determine if there are issues to be addressed. The ability to customize a map with background images and custom icons and stencils can make these maps really pop.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
There are few areas that I would say need to be improved; their customer support portal allows you to log tickets with any suggestions or things you feel the product is missing, and they will generally show you how to achieve what you want, or in some cases, introduce it as a feature in a later update.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The ability to intuitively and quickly serve up specified information up to a dashboard for general “public” consumption, that cycles through several pages of information.
The ability to intuitively set up alerting on bandwidth levels, instead of having to dig through all types of alerts available to find the one needed.
Provide a pricing model based on different support levels: if I want only available update installations, don’t make me pay the same amount as those wanting full support.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Its built with UX in mind and is aimed at non-tech people, to ensure that almost everyone can run the campaign. But if we go deeper - sometimes you will need an HTML editor or support in order to figure out some advanced edits you might want to add in your scenarios.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The Darktrace toolset is very expansive, allowing it to handle many different tasks, but this leads to a user interface that is sometimes not at all intuitive. Icons don't always make sense visually, and the associated tool tips do not always provide enough detail on what action the button performs
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
As far as rating for usability is concerned I would give 10/10 as NTA is very easy to use. All you need to do is install that module and ask network Team to configure the Netflow towards Server IP. [The] rest is pre-configured and reports are pre-built. Moment you receive the flows from Network all you will have is information about traffic.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I have not had to use their support for pretty much anything. The software works well, and is very intuitive. I would imagine their support would be rather basic as there is not too much that can go wrong with a report phishing button, and if it were I would probably consider a different software.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Darktrace support is excellent in my experience. They send a competent engineer on-site to provide on-boarding training. They were also very responsive in responding to questions and concerns. Having an individual point of contact who is a competent network and security engineer is not a common experience, at least for me.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I know we could probably pay for it, but it would be nice if we could get to a tier 2 technician faster. Spending a couple of hours on the phone with the level 1 technician, when we have already tried the troubleshooting they are walking us through, is just a waste of time.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The training offered by SolarWinds is some of the best out there. They have several different videos that go into great detail from initial setup to advanced configurations. In addition to the view at your own pace video, they also have live training for customers that focus on a single product and you can ask questions with the folks who develop the software. I have had good success with their live sessions and getting questions answered.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cofense PhishMe was the first choice for us as the user interface as well as their bundle package with Cofense Triage and Vision has helped the organisation to alleviate the overall security awareness posture. The other vendors did not provide a vast range of phishing scenarios as compared to Cofense PhishMe platform.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We did NOT select Darktrace. OSSIM/AlienVault is a more mature product and it provided better intelligence and reporting. The end user interface is much easier to use - and you can tell built form engineers who have had to do the work. My suggestion for anyone considering Darktrace, is to get the price upfront; do a 30/60 onsite trail; and do the same thing, at the same time, with AlienVault. AlientVault will win every time. I say that because that's exactly what I did.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SolarWinds NetFlow Traffic Analyzer compared to Wireshark and PRTG Network Monitor beats it by just the simple interface. Though all are manual setup, NTA takes it a step further with graphs and reports that analyze the data for you. In comparing to Extrahop from a bandwidth comparison, Extrahop wins but Extrahop is a lot more than just a bandwidth monitoring and cost.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Recipes in the system are capable of handling almost 2x what an analyst does, which cuts down the efforts [of] an analyst and provides more time for accurate strategies.
With roughly 90% false positives coming through, the remaining 10% of true positives need as much attention as they can get for the full investigation and analysis.
1,500 or more phishing messages can come through in a given week and the amount of time/employees required to review this without a tool like Cofense is surely beyond [the] expected/anticipated budget.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One big positive is how it helps us with the security assessments that clients have done on us. They are looking to see if we know how we might have unusual/malicious traffic running on the network.
If you have a small network and only need 1 appliance, it can be a good ROI and peace of mind.
You could go down a hole in trying to spend time looking at all of your traffic with this software. You need to focus only on what it is showing as potential bad traffic.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Be prepared to answer lots of questions. When people see the data in NTA they are going to want to know why App A is talking to App B. Be ready to explain!
Hand the keys to the NTA kingdom to the network team. They will thank you. Everyone wants to have friends on the network team, right?
Be prepared to invest in some significant compute and storage performance to keep up with your NTA monitoring
Running the latest firmware for your network gear is (often) required to take advantage of all the flow-monitoring. You upgrade regularly, right??
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info