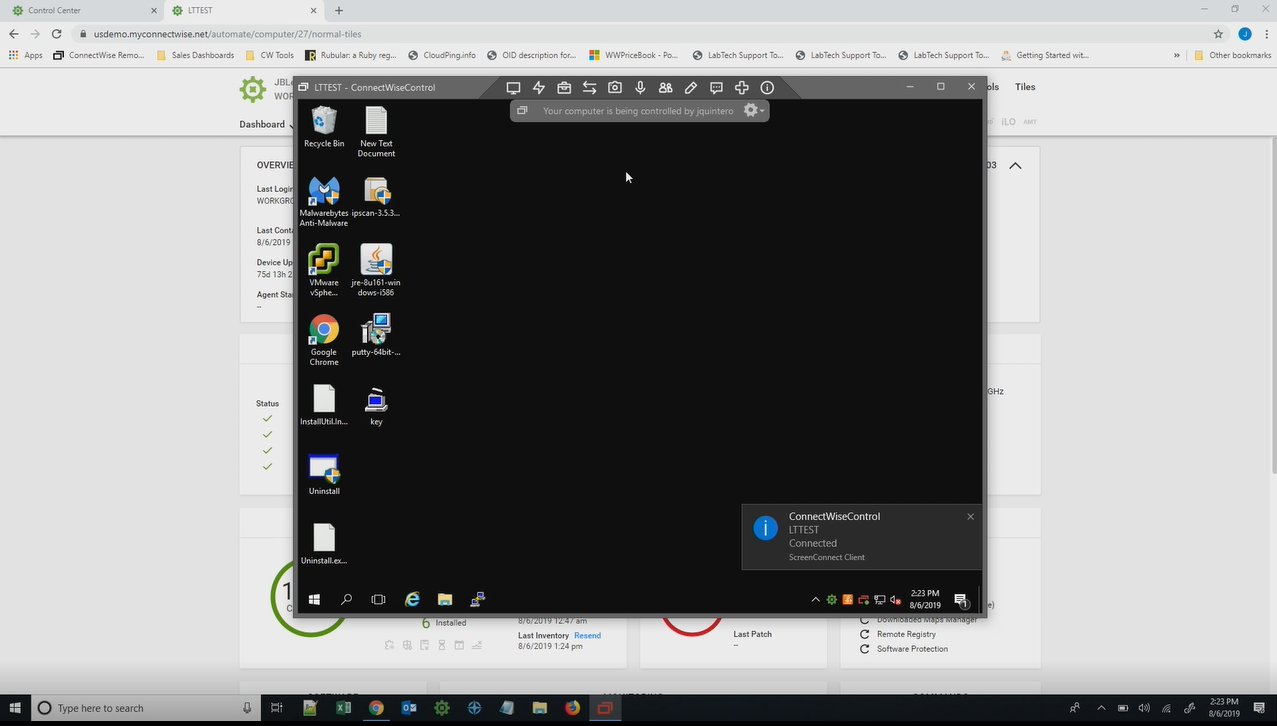
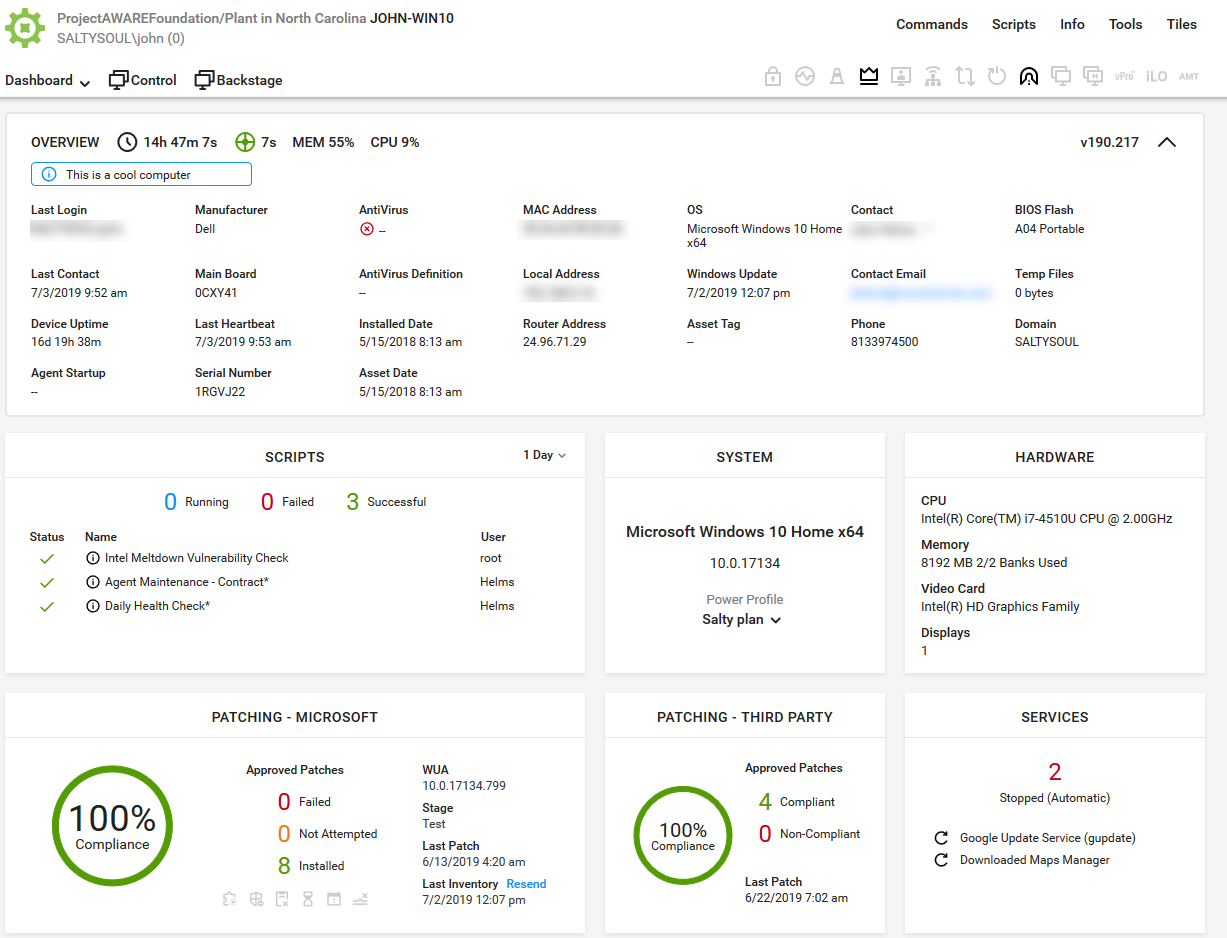
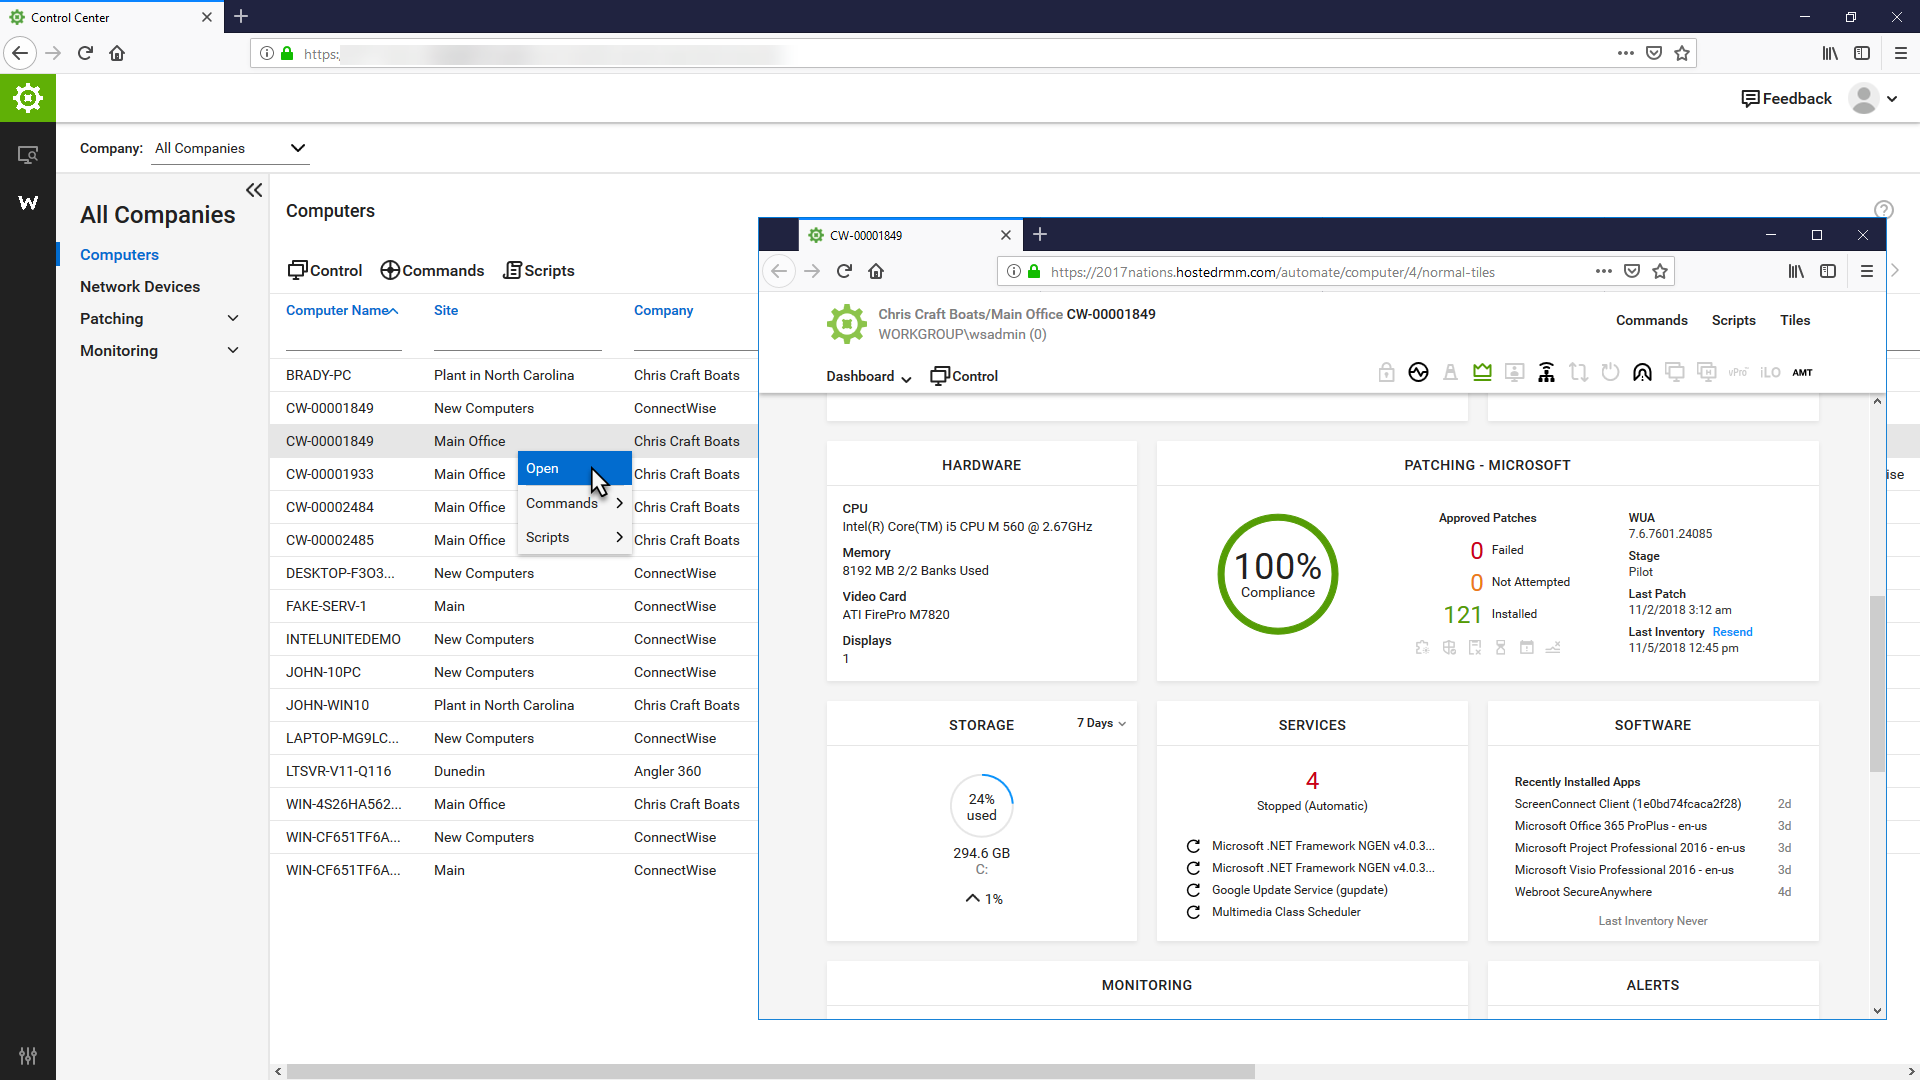
ConnectWise Automate, formerly LabTech, is a remote monitoring and management (RMM) platform. It provides powerful automation to discover and manage devices, monitor for problems, and scripts repetitive action.
$700
Microsoft Defender External Attack Surface Management
Score 9.7 out of 10
N/A
Microsoft Defender External Attack Surface Management is a service available on Microsoft's Azure, that provides insights into vulnerabilities, risks, and exposures for web-based resources. It defines an organization’s unique internet-exposed attack surface and discovers unknown resources to help users proactively manage security posture.
$0.01
per day per asset
Pricing
ConnectWise Automate
Microsoft Defender External Attack Surface Management
Editions & Modules
Agents
$1.00-$6.00
per month/per agent
Implementation Fee
$700
No answers on this topic
Offerings
Pricing Offerings
ConnectWise Automate
Microsoft Defender External Attack Surface Management
Free Trial
Yes
No
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
—
—
More Pricing Information
Community Pulse
ConnectWise Automate
Microsoft Defender External Attack Surface Management
Features
ConnectWise Automate
Microsoft Defender External Attack Surface Management
Application Performance Management
Comparison of Application Performance Management features of Product A and Product B
ConnectWise Automate
8.5
1 Ratings
18% above category average
Microsoft Defender External Attack Surface Management
-
Ratings
Virtualization monitoring
8.01 Ratings
00 Ratings
IT Asset Discovery
9.01 Ratings
00 Ratings
Monitoring Tasks
Comparison of Monitoring Tasks features of Product A and Product B
ConnectWise Automate
7.4
22 Ratings
4% above category average
Microsoft Defender External Attack Surface Management
-
Ratings
Remote monitoring
10.022 Ratings
00 Ratings
Network device monitoring
8.021 Ratings
00 Ratings
Activity Monitoring
8.01 Ratings
00 Ratings
Management Tasks
Comparison of Management Tasks features of Product A and Product B
ConnectWise Automate
7.8
22 Ratings
14% above category average
Microsoft Defender External Attack Surface Management
-
Ratings
Patch Management
10.021 Ratings
00 Ratings
Policy-based automation
9.022 Ratings
00 Ratings
Remote Access
Comparison of Remote Access features of Product A and Product B
ConnectWise Automate
8.0
1 Ratings
13% above category average
Microsoft Defender External Attack Surface Management
-
Ratings
Attended device access
10.01 Ratings
00 Ratings
Unattended device access
8.01 Ratings
00 Ratings
Mobile device access
5.01 Ratings
00 Ratings
Virtual device access
8.01 Ratings
00 Ratings
Multiple-display support
9.01 Ratings
00 Ratings
Multiple concurrent sessions
8.01 Ratings
00 Ratings
Threat Intelligence
Comparison of Threat Intelligence features of Product A and Product B
ConnectWise Automate
-
Ratings
Microsoft Defender External Attack Surface Management
9.7
1 Ratings
18% above category average
Network Analytics
00 Ratings
9.01 Ratings
Threat Recognition
00 Ratings
10.01 Ratings
Vulnerability Classification
00 Ratings
10.01 Ratings
Automated Alerts and Reporting
00 Ratings
10.01 Ratings
Threat Analysis
00 Ratings
10.01 Ratings
Threat Intelligence Reporting
00 Ratings
9.01 Ratings
Automated Threat Identification
00 Ratings
10.01 Ratings
Vulnerability Management Tools
Comparison of Vulnerability Management Tools features of Product A and Product B
ConnectWise Automate
-
Ratings
Microsoft Defender External Attack Surface Management
9.4
1 Ratings
12% above category average
IT Asset Realization
00 Ratings
8.01 Ratings
Authentication
00 Ratings
9.01 Ratings
Configuration Monitoring
00 Ratings
10.01 Ratings
Web Scanning
00 Ratings
10.01 Ratings
Vulnerability Intelligence
00 Ratings
10.01 Ratings
Best Alternatives
ConnectWise Automate
Microsoft Defender External Attack Surface Management
Microsoft Defender External Attack Surface Management
Likelihood to Recommend
ConnectWise
I recommend it to all IT colleagues; regardless of the size of the PCs with which you work most of the time, the application allows connection stability between computers that make it possible to continue working or taking care of the infrastructure from afar.
Microsoft Defender External Attack Surface Management is particularly well-suited for discovering, inventorying, and continuously monitoring the external attack surface, especially in environments with heavy Microsoft adoption. It is less suitable as a standalone solution for internal scanning, real-time attack detection, automated remediation, or advanced application testing. Microsoft Defender External Attack Surface Management es especialmente adecuado para descubrir, inventariar y monitorear continuamente la superficie de ataque externa, sobre todo en entornos con fuerte adopción de Microsoft. Es menos adecuado como solución única para escaneo interno, detección de ataques en tiempo real, remediación automática o pruebas avanzadas de aplicaciones. Parts of this review were originally written in Spanish and have been translated into English using a third-party translation tool. While we strive for accuracy, some nuances or meanings may not be perfectly captured.
They have conflicting scheduling paradigms. When scheduling patching for clients, the 1st Friday is interpreted as the very first Friday of the month, even if this is the 1st of the month. For scripting, the 1st Friday of the month is interpreted as the 1st Friday of the 1st FULL WEEK of the month. This makes no sense to have two different interpretations, and makes it unreliable to schedule recurring scripts to fall when recurring maintenance does. The scripts need to be done manually because of this.
There is no way to dictate reboot orders for patch policies. This tied directly in with my first point. We have some clients that require reboot orders. This is not possible without having different patch policies for each server and specifying a time this way. But, there aren't small enough increments of time to make this reliable, plus patching duration might vary. Excluding reboots with patching and scheduling reboot scripts fixes this. However, this can't be done once on a recurring schedule due to the different scheduling paradigms already discussed. We have to schedule these manually each month.
The primary reason for this rating is that ConnectWise Automate is currently so integral to our operations that moving away would involve more man hours than we would realistically have to invest. However, ConnectWise Automate is also completely capable of meeting all of our business needs and customizable to the point where if something is not meeting those needs out of the box, it can be modified to do what we want. From only installing software on machines if a different software package exists, to push a new version of that software is available, to check if credentials for user/machine have been updated to our new standards and then updating them if they have not, ConnectWise Automate is capable of doing everything we ask of it.
Basic use of the product is fairly easy. Information about the machines you manage can be found in customizable dashboards, which can be unique for each user, and, therefore, properly suited to the users' needs/job function. This is not a 10 because some of the interfaces are very clunky (Patch Management), and some features are not intuitive and not well documented (reporting). Scripting and Patch Management have a fairly steep learning curve (For structure in patch management and syntax in scripting), but once learned, they work well.
We rate Microsoft Defender External Attack Surface Management’s overall usability as 10 out of 10 because it delivers a strong balance between depth of capability and ease of use, particularly within organizations already operating in the Microsoft security ecosystem.
It used to be great, but then they broke reporting, speed and responsiveness with version 11 and the new Patch Manager. It's really bad and their support people are way behind on fixing so many bugs. They have really gone downhill. If they don't get it together soon, we'll start looking around.
ConnectWise Automate lets you manage more endpoints, with enhanced productivity and improved service, all without increasing expenses. It can manage patches and updates across thousands of computers. We also use it for customized monitoring and alerting on workstations and servers. Monitoring is really robust and granular. It does a great job of gathering a TON of data about the network, and that data is searchable. There are a bunch of different reports built in. Integrates with Manage, Control, and other applications. It does a ton of stuff out of the box, and has endless customization options.
The Online training has been re-done and needs a lot more work. When you look at training in different roles, it shows a lot of the same topics but no explanation to what is different about them. Several times that topics are the exact same, but they make you re-take the same information for a different topic, instead of marking that you have already completed that portion of training.
Start small and learn the in's and out's before making policies and rolling things out company wide. Ask the questions of why if you don't agree with something or your company does things a different way. Usually they are done a certain way for a reason. Start simple with roll out and slowly enable or add on the functionality that is needed.
I believe the monitoring and alerts in Continuum command is better, but [ConnectWise Automate (formerly LabTech)] does have stronger scripting, and perhaps a better interface. N-Central is inferior on all fronts to both. I did not make the purchasing decision. I would myself likely pick Continuum if I had to make a on the spot choice.
Because Microsoft Defender External Attack Surface Management is part of the broader Microsoft Defender family (including Defender XDR, Entra ID, Azure Security, Sentinel, etc.), it: Shares identity, endpoint, and threat context across tools Reduces the need for custom integrations or connectors Works in a “single pane of glass” experience for SOC analysts Why it matters: Organizations already invested in Microsoft security tools gain greater contextual insight and lower operational overhead.
We found we were able to provide good monitoring of our customers sites which was an objective. However, that came at a significant time investment that never seemed to be finished.
We were able to negotiate a price that worked for us for an up-front purchase which was nice.
We found the pricing to be very competitive.
Bottom line for us was despite the pros of the product, we found other RMM solutions to be a better overall "value" due to not having to dedicate technicians to maintaining the product.