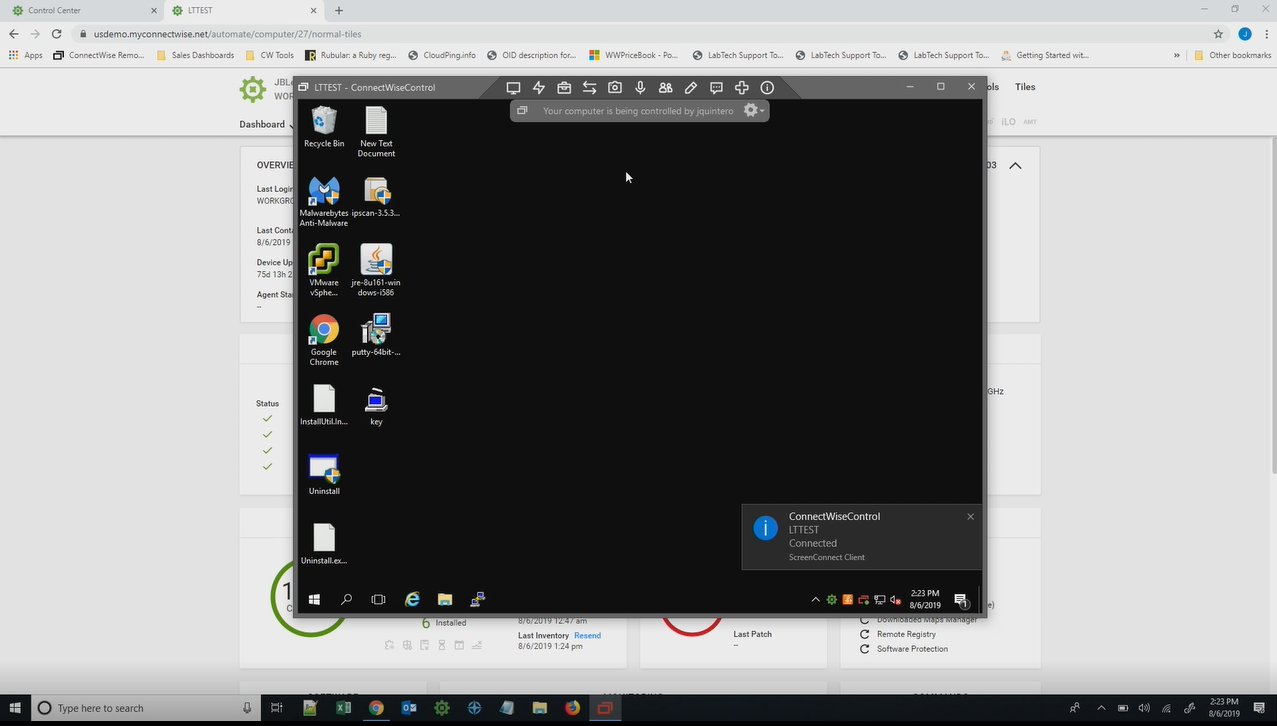
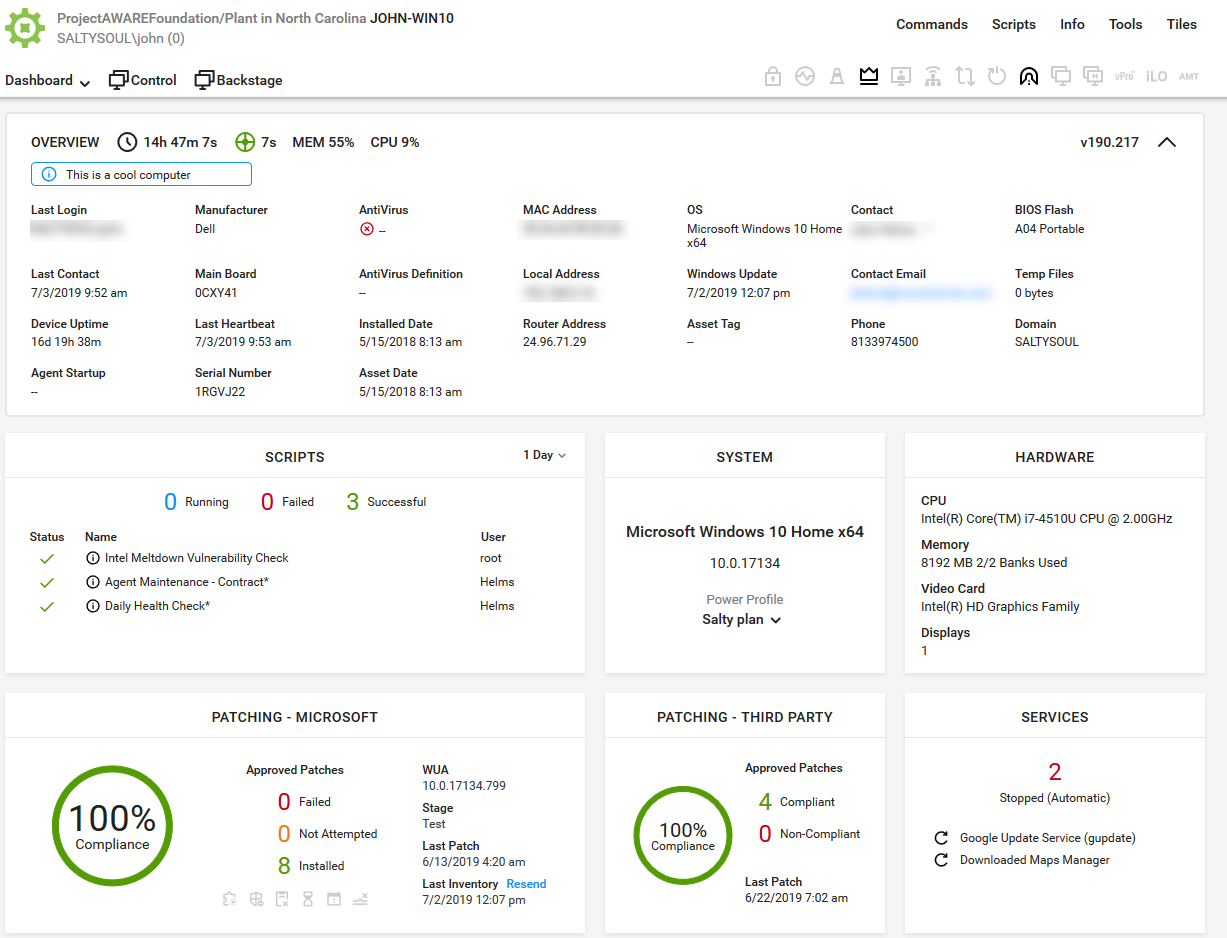
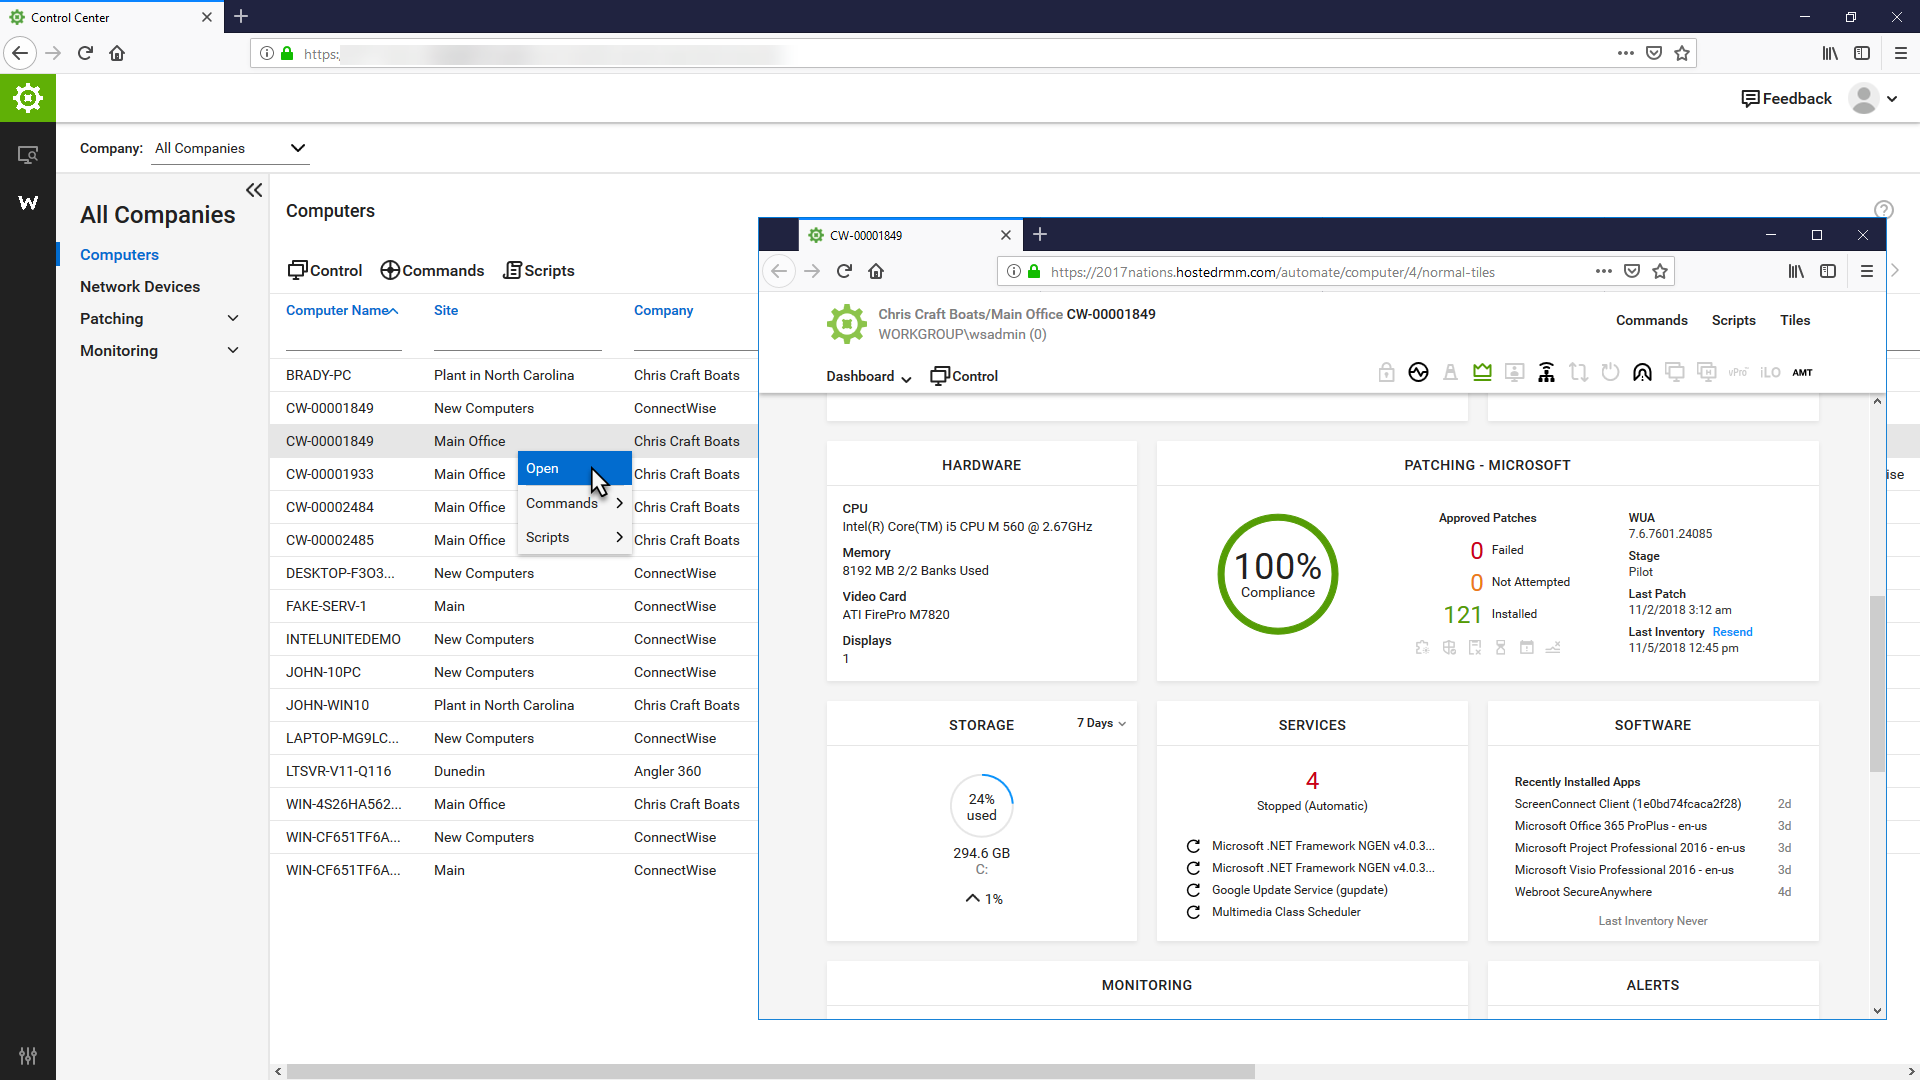
ConnectWise Automate, formerly LabTech, is a remote monitoring and management (RMM) platform. It provides powerful automation to discover and manage devices, monitor for problems, and scripts repetitive action.
$700
Microsoft Defender for Endpoint
Score8.8 out of 10
N/A
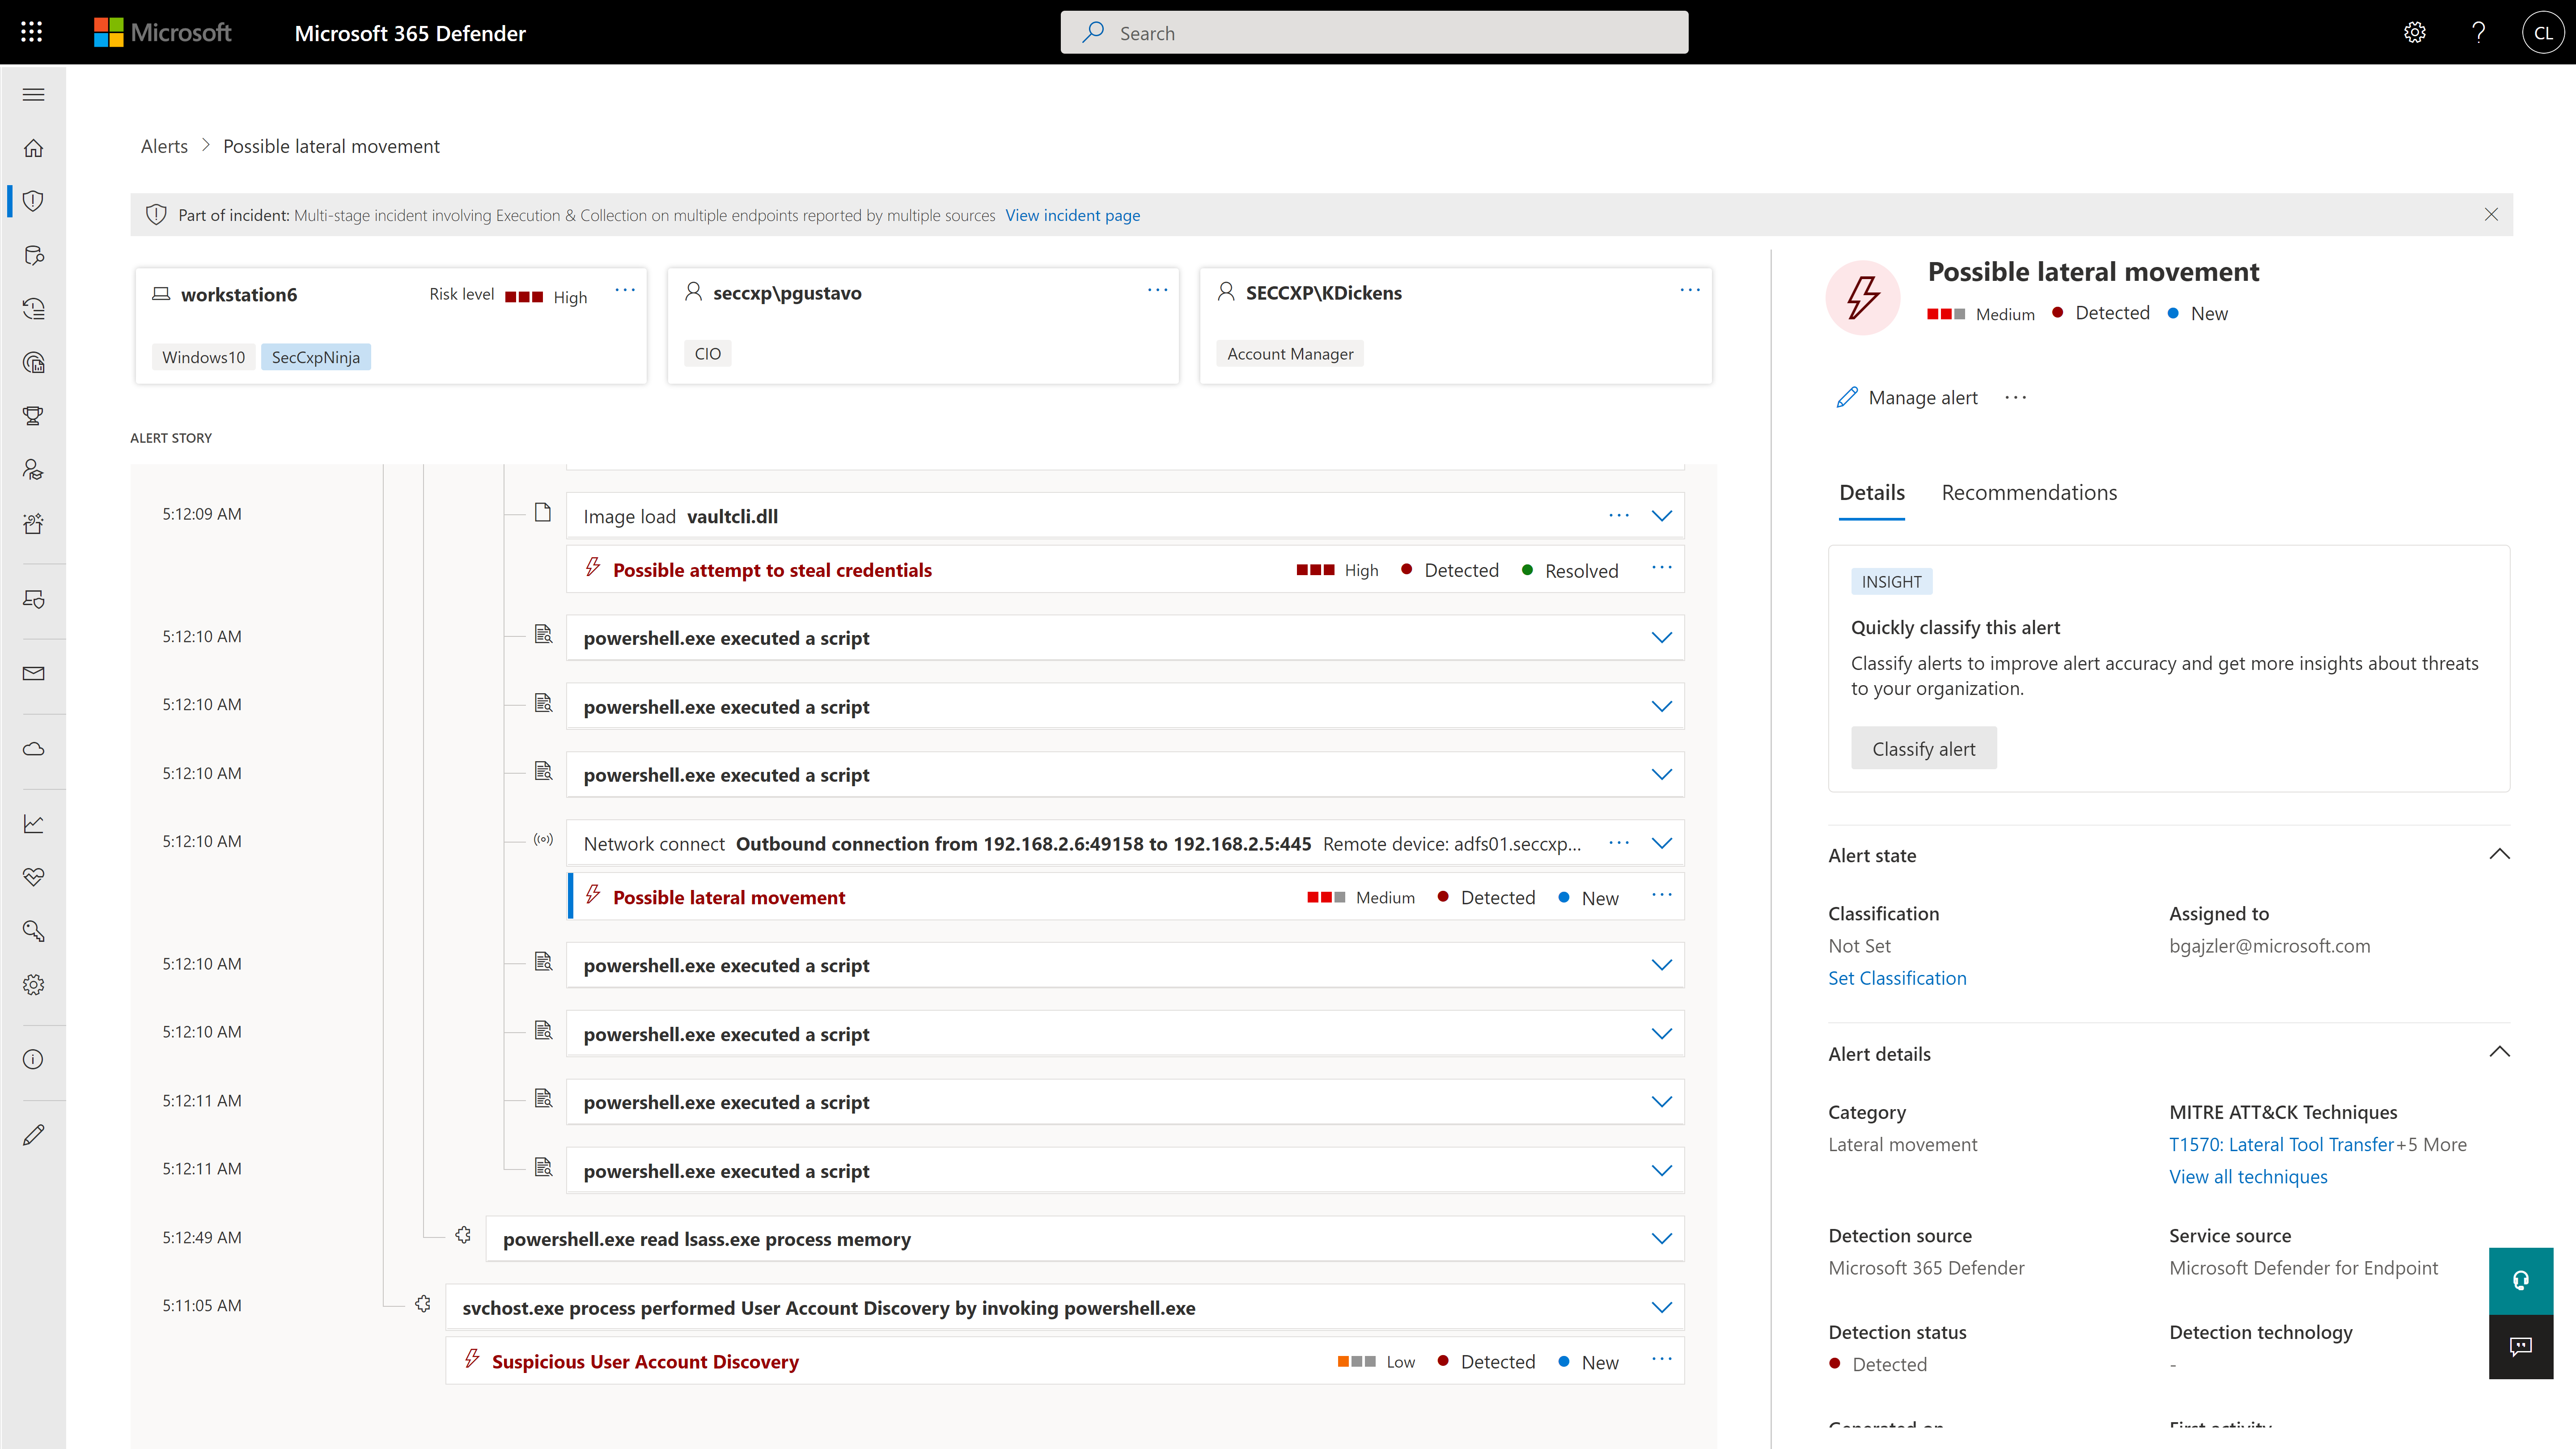
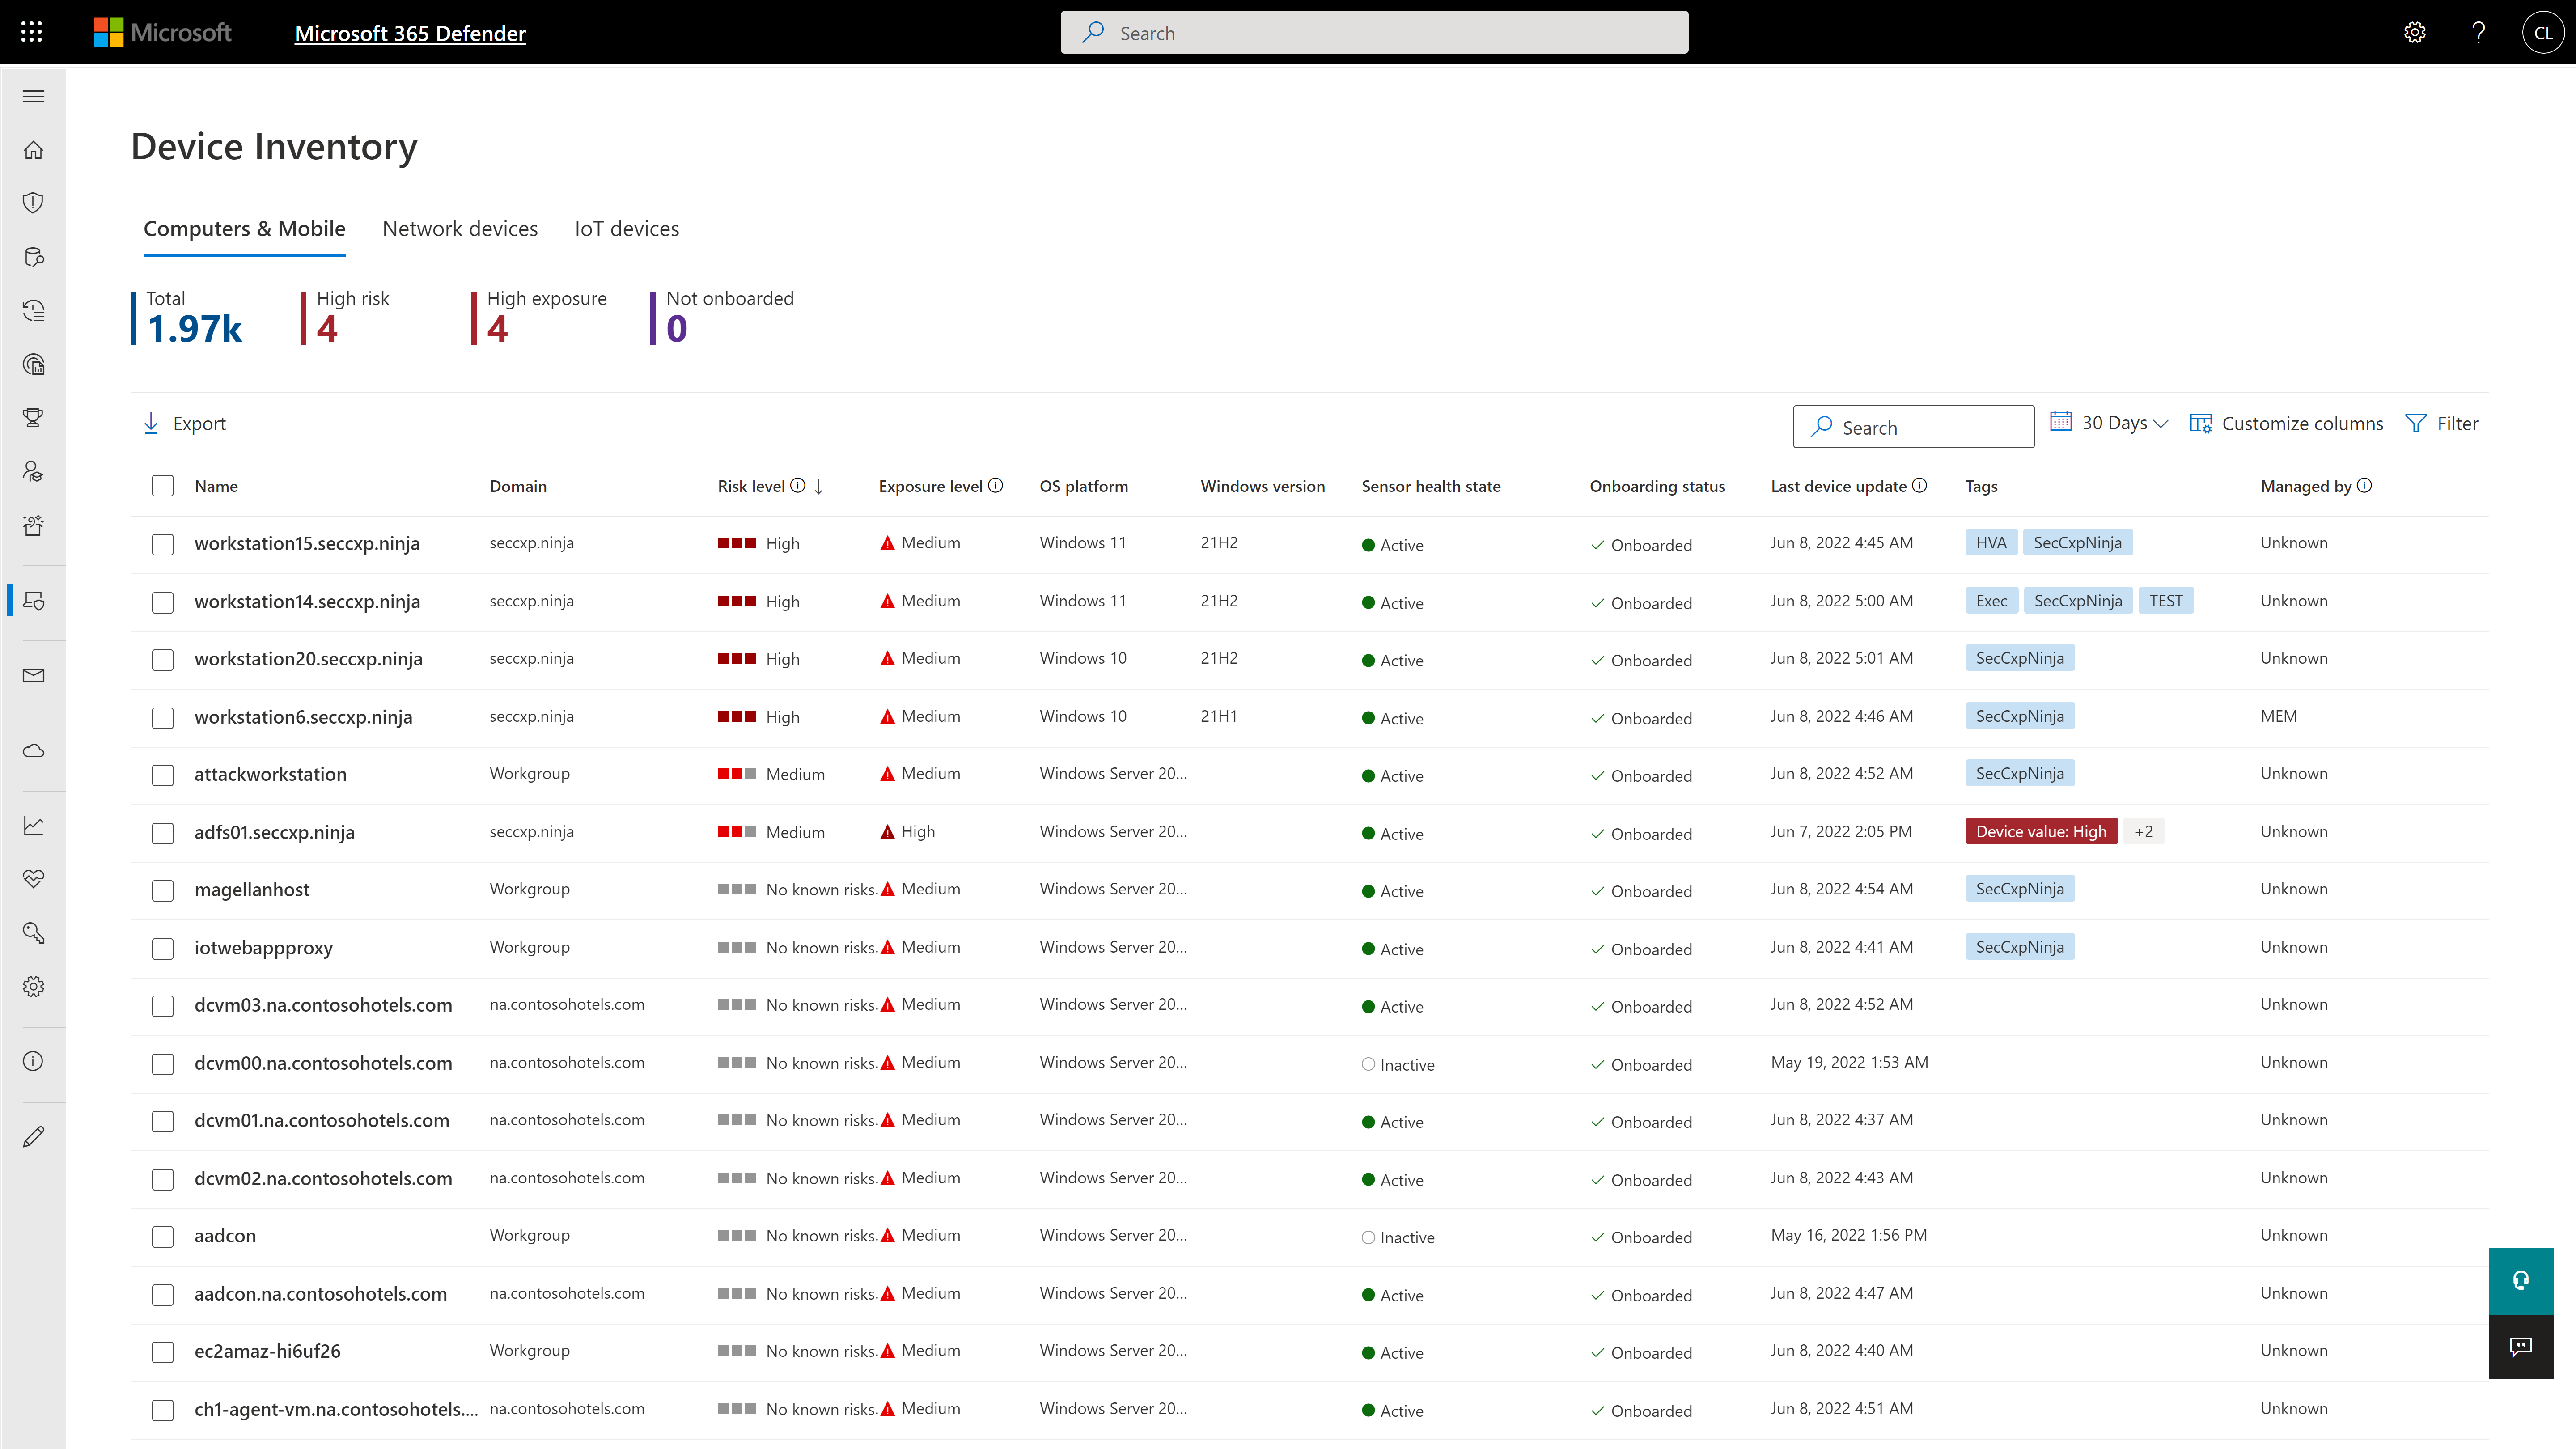
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
I recommend it to all IT colleagues; regardless of the size of the PCs with which you work most of the time, the application allows connection stability between computers that make it possible to continue working or taking care of the infrastructure from afar.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
They have conflicting scheduling paradigms. When scheduling patching for clients, the 1st Friday is interpreted as the very first Friday of the month, even if this is the 1st of the month. For scripting, the 1st Friday of the month is interpreted as the 1st Friday of the 1st FULL WEEK of the month. This makes no sense to have two different interpretations, and makes it unreliable to schedule recurring scripts to fall when recurring maintenance does. The scripts need to be done manually because of this.
There is no way to dictate reboot orders for patch policies. This tied directly in with my first point. We have some clients that require reboot orders. This is not possible without having different patch policies for each server and specifying a time this way. But, there aren't small enough increments of time to make this reliable, plus patching duration might vary. Excluding reboots with patching and scheduling reboot scripts fixes this. However, this can't be done once on a recurring schedule due to the different scheduling paradigms already discussed. We have to schedule these manually each month.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The primary reason for this rating is that ConnectWise Automate is currently so integral to our operations that moving away would involve more man hours than we would realistically have to invest. However, ConnectWise Automate is also completely capable of meeting all of our business needs and customizable to the point where if something is not meeting those needs out of the box, it can be modified to do what we want. From only installing software on machines if a different software package exists, to push a new version of that software is available, to check if credentials for user/machine have been updated to our new standards and then updating them if they have not, ConnectWise Automate is capable of doing everything we ask of it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Basic use of the product is fairly easy. Information about the machines you manage can be found in customizable dashboards, which can be unique for each user, and, therefore, properly suited to the users' needs/job function. This is not a 10 because some of the interfaces are very clunky (Patch Management), and some features are not intuitive and not well documented (reporting). Scripting and Patch Management have a fairly steep learning curve (For structure in patch management and syntax in scripting), but once learned, they work well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It used to be great, but then they broke reporting, speed and responsiveness with version 11 and the new Patch Manager. It's really bad and their support people are way behind on fixing so many bugs. They have really gone downhill. If they don't get it together soon, we'll start looking around.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
ConnectWise Automate lets you manage more endpoints, with enhanced productivity and improved service, all without increasing expenses. It can manage patches and updates across thousands of computers. We also use it for customized monitoring and alerting on workstations and servers. Monitoring is really robust and granular. It does a great job of gathering a TON of data about the network, and that data is searchable. There are a bunch of different reports built in. Integrates with Manage, Control, and other applications. It does a ton of stuff out of the box, and has endless customization options.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The Online training has been re-done and needs a lot more work. When you look at training in different roles, it shows a lot of the same topics but no explanation to what is different about them. Several times that topics are the exact same, but they make you re-take the same information for a different topic, instead of marking that you have already completed that portion of training.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Start small and learn the in's and out's before making policies and rolling things out company wide. Ask the questions of why if you don't agree with something or your company does things a different way. Usually they are done a certain way for a reason. Start simple with roll out and slowly enable or add on the functionality that is needed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I believe the monitoring and alerts in Continuum command is better, but [ConnectWise Automate (formerly LabTech)] does have stronger scripting, and perhaps a better interface. N-Central is inferior on all fronts to both. I did not make the purchasing decision. I would myself likely pick Continuum if I had to make a on the spot choice.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We found we were able to provide good monitoring of our customers sites which was an objective. However, that came at a significant time investment that never seemed to be finished.
We were able to negotiate a price that worked for us for an up-front purchase which was nice.
We found the pricing to be very competitive.
Bottom line for us was despite the pros of the product, we found other RMM solutions to be a better overall "value" due to not having to dedicate technicians to maintaining the product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info